Reported Documents (810 total)
Documents published alongside news reporting on the Snowden disclosures.
Sort: Title
Documents
-
Partner Cables [pdf]
A classified table mapping which GCHQ cable interception programs had access to specific undersea fiber optic cables worldwide, revealing the codenames and access types — either Direct Cable Order or Indefeasible Right of Use/Landing Capacity — of seven surveillance programs across dozens of international cable systems, with Cable & Wireless (GERONTIC) providing access to the largest number.
“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
Pay attention to that man behind the curtain: Discovering aliens on CNE infrastructure [pdf]
CSEC briefing from 2010 outlines Canada’s counter–computer network exploitation efforts to detect, analyze, and pursue foreign and friendly cyber actors operating on shared CNE infrastructure. It details tools, methods, and a case study showing how hidden implants and overlapping state-sponsored operations were uncovered and attributed.
Programs: SNOWGLOBE · WARRIORPRIDE · DAREDEVIL · SLIPSTREAM · CHORDFLIER · NAMEDROPPER · WORMWOOD · REPLICANTFARM · OBELIX · SHEPHERD · CARBON · ALOOFNESS · REGBACKUP · DOGHOUSE · WALKER · CHOCOPOP · BLAZINGANGEL · WINDO · QUIVERINGSQUAB · DIESELRATTLE · CYDLL · CIVETCAT · WIDOWKEY · LASEX · PULLEDPORK · MAKERSMARK · FANNER · SEEDSPHERE · BYZANTINE · VOYEUR · SUPERDRAKE · GOSSIPGIRL · WATERMARK · DOURMAGNUM -
Peeling Back the Layers of TOR with EGOTISTICALGIRAFFE [pdf]
An NSA Tailored Access Operations presentation describing EGOTISTICALGIRAFFE and EGOTISTICALGOAT — Firefox browser exploits targeting Tor Browser Bundle users — covering fingerprinting Tor users via the TorButton BuildID, the EGOTISTICALGOAT type confusion vulnerability in Firefox's E4X implementation enabling remote code execution, and the FINKDIFFERENT/FUNNELOUT callback infrastructure used to exfiltrate data from exploited targets.
Programs: EGOTISTICALGIRAFFE · EGOTISTICALGOAT · ERRONEOUSINGENUITY · ERIN · EGGO · FINKDIFFERENT · FIDI · EGGI · FUNNELOUT -
Perseverance Pays Off: Eight-Year SIGINT Effort Culminates in Arrest of Elusive Colombian Terrorist SIDtoday [pdf]
In 2008, SIGINT from NSA Texas led to the arrest of Doris Adriana, a key FARC member, after eight years of surveillance. NSA's actionable intelligence provided Colombian authorities with crucial details about her border crossing from Venezuela, resulting in her capture and subsequent prosecution for cocaine trafficking and kidnapping U.S. citizens.
-
Persistence and Collaboration Thwart Criminals on the High Seas SIDtoday [pdf]
This SIDtoday document describes a successful operation in which NSA Hawaii's Maritime Analysis Support Team (HMAST) and other agencies helped track and interdict the illegal fishing vessel Da Cheng (formerly Shun Li No. 6), which was engaged in high seas drift net (HSDN) fishing, a practice harmful to marine ecosystems. The coordinated effort, involving the U.S. Coast Guard and SIGINT support, led to the vessel's boarding and the discovery of illegal catch, though the document emphasizes that ongoing efforts are necessary to combat this illegal activity.
-
PGP encrypted email can't be decrypted by the NSA [pdf]
Two intercepted Yahoo email messages collected under FAA counterterrorism authority through PRISM (SIGAD US-984XN), both containing PGP-encrypted content that NSA was unable to decrypt — published by Der Spiegel as direct evidence that PGP encryption defeated NSA collection at the time of interception in January 2012.
Programs: PRISM -
PHANTOM PARROT [pdf]
This document discusses PHANTOM PARROT, a GTAC tool used for querying mobile phone data collected from individuals stopped at UK ports as part of the ITT Op WILDWAY initiative. The tool allows intelligence analysts to access phonebook, SMS, and call log data from these stops, which can be used for counter-terrorism efforts. Data is obtained under the Terrorism Act 2000, and the tool is part of a broader intelligence-gathering effort, eventually to be integrated into the LUCKY STRIKE project.
Programs: PHANTOM PARROT · WILDWAY · RANNOCH MOOR · LUCKY STRIKE · LOOKING GLASS · DISHFIRE · CORINTH · MOONRAKER · RUSSETT -
Phone Number Extractor [pdf]
A top secret XKEYSCORE training document from October 2009 describing the Phone Number Extractor capability, which automatically identifies and extracts telephone numbers from intercepted internet traffic including website content, email signature blocks, HTTP GET requests from mobile devices, HTTP POST submissions, and converged DNR/DNI collection — with operational examples targeting Iran, Lebanon, and Pakistan.
-
Pine Gap classification guide [pdf]
This document is a classification guide for NSA/CSS activities at the Joint Defense Facility Pine Gap (JDFPG) in Australia, outlining which information about the site, its SIGINT missions, organizational structure, and training is classified and at what level. It specifies that sensitive details, including the site’s SIGINT mission, Producer Designator Digraph, SIGAD, and support to military operations, are protected to safeguard national security and allied interests.
-
PINWALE: Transnational DNI Training [pdf]
This presentation is a classified NSA training guide on PINWALE, a SIGINT database used for the storage, retrieval, and analysis of intercepted digital network intelligence (DNI) communications. It outlines system capabilities, query creation, search tools, and interfaces such as NEXUS, UIS, and AGILITY, explaining how analysts search, retrieve, and analyze both content and metadata — including FISA-partitioned data — within the Five Eyes intelligence framework.
-
POISONNUT [pdf]
NSA Wiki page describing POISONNUT — also known as the VPN Attack Orchestrator (VAO) — a LONGHAUL cryptologic exploitation service for IPSec VPN decryption that has existed in various forms since 2003, serving clients including TURMOIL, WEALTHYCLUSTER and the Transform Engine emulator via ISLANDTRANSPORT with ISLANDHIDEAWAY encryption.
Programs: POISONNUT · TURMOIL · WEALTHYCLUSTER · ISLANDTRANSPORT · ISLANDHIDEAWAY · LONGHAUL · OAKLEY · SCARLETFEVER · PICARESQUE · VALIANTSURF -
PRC Information Warfare & Huawei [pdf]
This NSA intelligence briefing on Huawei analyzes Huawei’s global telecommunications presence and its potential links to the People’s Liberation Army (PLA) and Chinese government intelligence activities. It highlights concerns that Huawei’s international market expansion — including its subcontracted 2008 upgrade of the TAT-14 transatlantic cable carrying U.S. and defense communications — could be exploited by China for signals intelligence (SIGINT) purposes.
People: Chávez, Hugo -
Presentation on the spying program PRISM and ECC's participation [pdf]
This presentation provides statistics on the PRISM surveillance program, detailing intelligence reporting and target tasking across various NSA units and partners from 2011 to 2013. The data reveals that while not the top producer by volume, the European Cryptologic Center (ECC) was the most proportionally reliant on PRISM, which constituted over half of its intelligence output.
-
Presidential Policy Directive/PPD-20 [pdf]
Eighteen-page presidential memo reveals how Barack Obama has ordered intelligence officials to draw up a list of potential overseas targets for US cyber attacks.
-
PRESTON Architecture [pdf]
The PRESTON architecture, centered on GCHQ’s PRESTON Processing system, is detailed across multiple views showing how the agency intercepts, processes, and stores communications. It outlines a sophisticated surveillance framework that integrates lawful interception, data processing, and analyst access, emphasizing covert monitoring and management of intercepted data.
Programs: PRESTON · FAST GROK · BOXSTER · MARMION · GENTIAN · TERRAIN · BLACKNIGHT · CORINTH · FARNDALE · SAMDYCE · B3M · VSLT · SAMBOK · HAUSTORIUM · FUNFAIR · Cheltenham · SALAMANCA · IIB · LOCHNVAR · MONACO · HOTLINE · Benhall · GDR · CE · BRIGHTON · ARSENIDE · SPQR · TACHO · TRAFFIC MASTER · KEYCARD · XKEYSCORE · COURIERSKILL · MONKEYPUZZLE · PILBEAM · GREENHEART · CCDF · GTE · CADENCE · TERRAINS · GCNET · HENCE -
PRESTON Business Processes [pdf]
The PRESTON Business Processes document outlines GCHQ’s internal workflows for authorizing, enabling, managing, and terminating communications interception, as well as producing intelligence from intercepted data. It defines the roles, responsibilities, and technical processes that support lawful interception operations within the PRESTON system.
-
PRESTON Study [pdf]
This GCHQ document details the PRESTON surveillance program, revealing that over a six-month period, 97% of intercepted communications—including calls, texts, and internet data—were not viewed by analysts despite being fully warranted, highlighting systemic challenges in processing and exploiting the vast volume of collected intelligence. It underscores the reliance on traditional PRESTON sources for events like the London G20, while noting gaps in data feeds from other repositories, reflecting both operational scale and limitations in effective oversight.
-
PRIMARY FORNSAT COLLECTION OPERATIONS [pdf]
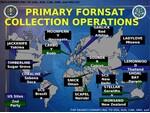
This document is a TOP SECRET NSA/CSS slide mapping the global locations of primary FORNSAT (foreign satellite) collection operations, showing U.S. and second-party ground stations used to intercept satellite communications worldwide. It illustrates the geographic spread and allied integration of NSA satellite surveillance infrastructure rather than specific technical capabilities.
-
PRISM (US-984XN) expanded its impact [pdf]
FY2012 figures for PRISM: 24,096 end-product reports (up 27 percent), the most-cited SIGAD in first-party reporting at 15.1 percent, 1,477 reports cited in the President's Daily Brief, tasked selectors up 32 percent to 45,406, and taskable e-mail domains expanded from 40 to 22,000.
Programs: PRISM -
PRISM Olympic Option [pdf]
A May 2012 NSA operational highlight revealing that Britain's GCHQ was given access to the NSA's PRISM surveillance system during the London Olympics, with 100 trained British operatives secretly monitoring 256 targets and intercepting over 11,000 communications in a single week.