Reported Documents (810 total)
Documents published alongside news reporting on the Snowden disclosures.
Sort: Title
Documents
-
OAKSTAR Travel Hanbook: A Guide for Traveling [pdf]
This document is a NSA OAKSTAR Travel Handbook, providing detailed guidance for personnel traveling on OAKSTAR-related missions, including MONKEYROCKET. It covers travel preparation, clearance requirements, coordination with partner organizations, operational security measures, conduct during visits, reporting obligations, and expense documentation to ensure sensitive intelligence operations are protected while engaging with private-sector partners.
Programs: OAKSTAR · STEELKNIGHT · SILVERZEPHYR · YACHTSTOP · SHIFTINGSHADOW · MONKEYROCKET · COBALTFALCON · BLUEZEPHYR · ORANGECRUSH · ORANGEBLOSSOM · PRIMECANE · TRANSPORTORO · THUNDERLISLAND · WHIPGENIE · SSO · THUNDERISLAND · YACHTSHOP -
OAKSTAR Weekly Update - Program Highlights Week of: March 16-22, 2013 [pdf]
The document is a NSA weekly operations update from March 16-22, 2013, detailing technical issues, maintenance, and intelligence activities within the OAKSTAR and MONKEYROCKET programs—surveillance systems used for data collection. It notes collection outages, system adjustments, and that analysts were using MONKEYROCKET access to track Bitcoin transactions and investigate organized crime and cyber targets using e-currency for money laundering.
Programs: OAKSTAR · PRIMECANE · MONKEYROCKET · NIAGARAFILES · TRANSPORTORO · XKEYSCORE · REMEDY · MARINA · CLOUDRUNNER -
OAKSTAR Weekly Update - Program Highlights Week of: March 2-8, 2013 [pdf]
The document is a NSA weekly operations update from March 2-8, 2013, detailing technical issues, maintenance, and intelligence activities within the OAKSTAR and MONKEYROCKET programs—surveillance systems used for data collection. It notes collection outages, system adjustments, and that analysts were using MONKEYROCKET access to track Bitcoin transactions and investigate organized crime and cyber targets using e-currency for money laundering.
-
OAKSTAR Weekly Update - Program Highlights Week of: March 23-29, 2013 [pdf]
The document is a NSA weekly operations update from March 23-29, 2013, it details equipment handoffs, script tweaks to improve data flow, metadata collection metrics, and ongoing MONKEYROCKET use for tracking Bitcoin-related targets, including sharing detailed user and session data with analysts for intelligence purposes.
-
OAKSTAR Weekly Update - Program Highlights Week of: March 30 - April 5, 2013 [pdf]
The document is a NSA weekly operations update from March 30 - April 5, 2013, reporting hardware failures and server issues with XKeyscore, efforts to reroute data and replace components, ongoing metadata collection metrics, and continued intelligence production, with OAKSTAR's 2013 serialized product totals at 430 reports and 2,641 GISTs (MONKEYROCKET: 1 report).
-
OAKSTAR Weekly Update - Program Highlights Week of: March 9-15, 2013 [pdf]
The document is a NSA weekly operations update from March 9-15, 2013, detailing technical issues, maintenance, and intelligence activities within the OAKSTAR and MONKEYROCKET programs—surveillance systems used for data collection. It notes collection outages, system adjustments, and that analysts were using MONKEYROCKET access to track Bitcoin transactions and investigate organized crime and cyber targets using e-currency for money laundering.
-
Offsensive Session: the Boundaries and Against Hacktivism [pdf]
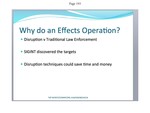
GCHQ slides on “effects” operations against hacktivists: disruption in place of traditional law enforcement, denial-of-service attacks on key communications outlets during Op WEALTH in summer 2011, and a disruption playbook of infiltration, ruse, set-piece, false-flag, false-rescue, disruption and sting operations.
-
One Fish, Two Fish, My Fish, Your Fish! SIDtoday [pdf]
This SIDtoday document discusses the challenges faced by the U.S. and its partners in monitoring foreign fishing fleets, particularly Chinese vessels, in exclusive economic zones (EEZ). It highlights issues with the Automatic Identification System (AIS) used by fishing boats, where Chinese vessels were broadcasting inaccurate positional data, either due to technical errors or intentional misuse of the system, complicating monitoring efforts and posing risks to maritime safety and security.
Programs: SCQAWK -
One-Year Anniversary for SUSLAG [pdf]
The document commemorates the one-year anniversary of the Special US Liaison Activity Germany (SUSLAG) at its new facility in Mangfall Kaserne, Bad Aibling, highlighting its transition from Bad Aibling Station. It discusses SUSLAG's ongoing role as a SIGINT liaison with the German intelligence service BND and showcases its collaborations, such as the Joint Analysis Center (JAC) and the Joint SIGINT Activity (JSA).
-
OP HIGHLAND FLING - Event Log [pdf]
A TOP SECRET operational event log from GCHQ's GCWiki documenting a January 2011 operation targeting Gemalto employees in France, Poland and elsewhere, using MUTANT BROTH cookie analysis, Facebook credentials, LinkedIn profiles and Computer Network Exploitation to identify and implant targets as part of the operation to steal SIM card encryption keys.
-
Op MULLENIZE and beyond - Staining machines 10/10/12 [pdf]
This 2012 report from the NSA's British counterpart, the GCHQ, describes a method of "staining" electronic traffic to distinguish otherwise anonymous users. It is used to unmask Tor users and devices on networks in which many computers share the same Internet address. The method relies on planting code in a web browser to change the "user agent," which is the way the browser identifies itself on the web. In a two month period, the report says, GCHQ managed to implant about 200 computers with uniquely identifying stains.
-
Op-ed: Leave Bright Pebbles, Not Breadcrumbs, for Those Coming After You SIDtoday [pdf]
A 2010 NSA SIDtoday op-ed by a Chinese language analyst urging analysts to actively document and share their target knowledge through available tools rather than hoarding expertise in personal files or spreadsheets, arguing that the agency's increasing reliance on short tours and rotating assignments makes institutional knowledge-sharing an operational necessity.
-
Operational Engineering November 2010 [pdf]
This internal GCHQ briefing from late 2010 documents the Events Product Centre's suite of bulk internet and communications surveillance tools — including IMMINGLE, SALAMANCA, SOCIAL ANTHROPOID, MUTANT BROTH, KARMA POLICE, SAMUEL PEPYS and GUIDING LIGHT — covering scaling targets, new data sources, and operational capabilities across telephony, webmail, instant messaging, social media, GPRS and VoIP collection.
Programs: EVENTS · IMMINGLE · SALAMANCA · GUIDINGLIGHT · B3M · HARDASSOC · MAINWAY · THUGGEE · FASCIA · HAUSTORIUM · FIRESTORM · TERRAIN · SHAREOWN · ESCHAR · BRIO · INFINITEMONKEY · KARMAPOLICE · MARBLEDGECKO · MEMORYHOLE · MUTANTBROTH · SAMUELPEPYS · SOCIALANIMAL · SOCIALANTHROPOID · HEARTBEAT · SANTHROPOID · LEAKYGATEWAYS · GTPTUNNEL · LUSTRE · GLASSBACK · COLLATERAL · HRMAP · SWORDPLAY · BROADOAK · REFORMER · ARTEMIS · MERLOT · CONTRAOCTAVE · CRYINGFOWL · CULTWEAVE · SAMDYCE · GCQUERY · BLAZZINGSADDLES · EREPO · JTRIG · SOUNDER -
Operational Legalities – GCHQ Powerpoint Presentation [pdf]
GCHQ’s “Operational Legalities” deck is an internal compliance playbook that translates the UK’s surveillance laws into day‑to‑day SIGINT procedure—drilling staff on authorisation, necessity, and proportionality, and walking through warrants, targeting justifications, database queries, dissemination, and oversight. Half slides and half speaker notes, it shows how analysts are trained to document, audit, and defend operations under ISA, RIPA, HRA, and WTA while navigating edge cases like location, nationality, second‑party constraints, and “indirect targeting.”
-
OPULENT PUP Encryption Attack [pdf]
"OPULENT PUP encryption attack (GCHQ)" is a 2009 technical planning document from the British intelligence agency GCHQ. It outlines a "proof-of-concept demonstrator" for a new capability to intercept and decrypt GSM communications protected by the A5/3 algorithm, requiring a complete overhaul of the existing processing chain used for the older A5/1 standard.
Programs: OPULENTPUP -
ORANGECRUSH, part of the OAKSTAR program [pdf]
An SSO item reporting that ORANGECRUSH — the OAKSTAR access at a third-party partner site in Poland, known to the Poles only as BUFFALOGREEN — began forwarding metadata to NSA on 3 March and content on 25 March, with collection shared to Second Parties through TICKETWINDOW.
-
OSINT FUSION PROJECT [pdf]
A TOP SECRET//COMINT//REL TO USA, FVEY presentation by Lockheed Martin's Intelligence and Global Solutions division describing the OSINT Fusion Project — a programme to collect and weaponise open source intelligence from hacker forums, malicious email traffic, botnet data and commercial threat feeds to generate XKEYSCORE fingerprints for CNE targeting and fourth party collection.
-
OTR encrypted messages can't be decrypted by the NSA [pdf]
Three intercepted chat sessions from 16 March 2012 collected under PRISM, showing a target switching mid-conversation from unencrypted to OTR-encrypted messaging — with NSA able to collect the session metadata and unencrypted portions but unable to decrypt the OTR messages, each annotated "No decrypt available for this OTR encrypted message."
Programs: PRISM -
-
Pages From Denial and Deception Except Redacted [pdf]
This document is a TOP SECRET X1 NSA report listing unauthorized disclosures of signals intelligence over the previous three years, noting that some—including coverage of the 1967 Israeli attack on the USS Liberty—had potential operational impacts but did not change targeting or intelligence priorities. It highlights that such leaks can harm U.S. intelligence capabilities and details one specific instance involving a 2000 Wall Street Journal letter discussing the incident.