Reported Documents (810 total)
Documents published alongside news reporting on the Snowden disclosures.
Sort: Title
Documents
-
How the NSA verifies a target's location [pdf]
This is an excerpt from a transcript of National Security Agency training videos that describe how to verify the location of a targeted device. It explains how the NSA monitors different types of mobile signaling information known as HLR and VLR registrations in order to locate individuals. It also makes clear that the agency is able to use location tracking to ascertain whether a target is in the United States.
-
How to configure category throttling in XKEYSCORE [pdf]
An NSA technical guide explains how to configure "category throttling" in XKEYSCORE—a feature that automatically stops forwarding intercepted communications once analyst-defined collection targets hit predetermined data volume or session count limits, allowing the surveillance system to continue processing but prevent overflow from high-volume targets.
-
How to tell if a target is 'foreign' [pdf]
The document describes a human intelligence (HUMINT) report indicating that a specific intelligence target, identified by a Foreign Source ID, is located outside the U.S., including details such as email, telephone number, and mobile network type, with checks confirming no U.S. roaming over a 60-day period. It illustrates the use of HUMINT to corroborate foreign location data for surveillance purposes.
-
HR DIETMAR B - Director SIGINT Analysis and Production German Federal Intelligence Service, 30 April - 1 May 2013 [pdf]
This draft agenda outlines scheduled meetings and presentations for a collaboration event between the German Federal Intelligence Service (BND) and the NSA, held from April 30 to May 1, 2013. The agenda details various discussions on SIGINT analysis, data acquisition, and counterterrorism efforts, showcasing the active engagement between the two intelligence communities.
Programs: SSOPeople: Alexander, Keith B. -
HRA auditing [pdf]
This GCHQ internal wiki page provides detailed procedural guidance for conducting Human Rights Act (HRA) compliance audits of analyst activities using surveillance databases like BROAD OAK and Events, establishing quarterly and six-monthly random sampling schedules, defining compliance metrics (Red <75%, Amber 75-94%, Green ≥95%), and specifying the responsibilities of analysts, auditors, and business unit heads to demonstrate that targeting, tasking, and examination of intercept content or metadata meet legal requirements for necessity and proportionality.
Marking: UK CONFIDENTIAL -
HTTP Activity in XKEYSCORE [pdf]
This training presentation from March 2009 provides NSA and Five Eyes analysts with detailed instructions on exploiting HTTP web browsing activity collected by XKEYSCORE, explaining how to differentiate client-to-server requests (GET/POST) from server-to-client responses, extract metadata like search terms, URLs, cookies, language, and browser types, and use this data to discover new surveillance targets, track individuals' online behavior, and conduct "pattern of life" analysis.
-
HTTP Activity vs User Activity [pdf]
This NSA training document from June 2009 explains the distinction between HTTP Activity (general web browsing data) and User Activity (communications metadata from specific protocols like webmail and chat) within the XKEYSCORE surveillance system, demonstrating through Iranian examples how analysts combine both search types to develop comprehensive intelligence on targets.
Programs: XKEYSCORE · MARINA · FOXTRAIL · DECODEORDAIN · YACHTSHOP · BRUTUS · WINDCHASER · NKB · UIS · STARPROC -
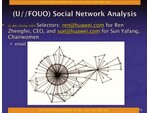
Huawei - Social Network Analysis [pdf]
This document describes Social Network Analysis targeting top leadership at Huawei. By tracking the email selectors of CEO Ren Zhengfei and Chairwoman Sun Yafang, the agency mapped their professional and personal connections.
“NSA: Imperiale Visionen” - Der Spiegel ↗ (2014-03-23) · Rosenbach, Marcel · Stark, Holger · Zand, Bernhard -
I hunt sys admins [pdf]
These internal documents outline the NSA’s strategy for identifying and targeting foreign system administrators to gain "keys to the kingdom" access to global network infrastructure. By correlating disparate datasets—such as passive telnet/SSH metadata and personal social media/webmail logins—the agency identifies personal accounts to facilitate QUANTUM-based hacking operations and network "pwnage."
-
ICREACH Black Budget Extracts [pdf]
This document provides fiscal and strategic justifications for the continued expansion of ICREACH, detailing its role as a primary vehicle for disseminating both telephony and Digital Network Intelligence (DNI) metadata across the Intelligence Community. It outlines the platform's transition to the NSA/CSS cloud architecture, a move intended to enhance data enrichment services and ensure the system remains responsive to the evolving requirements of the National Intelligence Priorities Framework (NIPF).
Programs: ICREACH -
ICREACH Wholesale Sharing (2007) [pdf]
This document serves as an official submission by the SID Technical Director detailing the leadership and collaborative efforts required to transition ICREACH from a conceptual framework into the Intelligence Community's first wholesale metadata-sharing platform. This document emphasizes the role of the SID team in securing critical legal and policy approvals through the NSA's Office of the General Counsel and coordinating with Five Eyes partners to ensure international participation in the system.
Programs: ICREACH -
ICREACH: Sharing SIGINT Comms Metadata with the Intel Community SIDtoday [pdf]
This document serves as an internal announcement marking the 2007 operational launch of ICREACH, a massive signals intelligence (SIGINT) metadata-sharing platform designed to provide real-time access to raw communication records for authorized analysts across the U.S. Intelligence Community. By consolidating telephony, cellular, and satellite data into a "one-stop shop" similar to the NSA’s internal GLOBALREACH tool, the program aimed to fulfill post-9/11 mandates for increased inter-agency collaboration and enhanced target development.
-
ICTR Cloud Efforts [pdf]
A GCHQ presentation details how the agency developed cloud-based big data analytics to achieve "population scale" surveillance—processing trillions of internet events to build geographic and behavioral profiles on every online identifier worldwide, enabling discovery of unknown targets through pattern analysis rather than traditional keyword searches.
Programs: EVERYASSOC · PROBABILITYCLOUD · SILVERLINING · CULTWEAVE · KARMAPOLICE · EVERYPOLICE · AWKWARDTURTLE · GORDIANKNOT · SANDIA · BLOODHOUND · FIVEALIVE · NGE · MAPREDUCE -
Identity Intelligence: Image Is Everything [pdf]
This document is a highly classified NSA/CSS briefing detailing Identity Intelligence (i2), a comprehensive methodology for exploiting unique fragments of information to track, identify, and exploit targets of interest. It outlines an expansive architecture for data collection that spans Biometric/Biologic, Biographic, and Contextual/Behavioral domains, essentially mapping every conceivable data point of an individual's physical existence and digital/social footprint.
-
In-Flight GSM [pdf]
This NSA presentation outlines how the agency is reacting to the growth of mobile phone services on board commercial aircraft.
-
India: Support to Terrorist Attacks in Mumbai [pdf]
A top secret NSA intelligence report on GCHQ's surveillance of Lashkar-e-Taiba technology chief Zarrar Shah before and during the November 2008 Mumbai attacks, documenting how analysis of his internet browsing and viewing habits revealed reconnaissance activity and operational planning against Mumbai targets including the Taj Hotel.
People: Shah, Zarrar“In 2008 Mumbai Attacks, Piles of Spy Data, but an Uncompleted Puzzle” - The New York Times ↗ (2014-12-21) · “In 2008 Mumbai Attacks, Piles of Spy Data, But an Uncompleted Puzzle” - ProPublica ↗ (2014-12-21) · “In 2008 Mumbai Attacks, Piles of Spy Data, but an Uncompleted Puzzle” - PBS ↗ (2014-12-21) · Glanz, James · Rotella, Sebastian · Sanger, David E. · Jennings, Tom · Peevey, Anna Belle · Nieling, Michael -
Industrial-Scale Exploitation [pdf]
This top-secret NSA document details the operational philosophy behind the TURBINE system's transition to "industrial-scale exploitation." By integrating with both active and passive sensors, TURBINE automates the delivery of malware and the maintenance of network implants, specifically targeting routers and server-side code execution.
-
Innov8 Experiment Profile Template [pdf]
A TOP SECRET STRAP1 joint NSA/GCHQ experiment profile documenting a 2010-2011 Joint Capability Experiment to test hardware-accelerated bulk decryption of common internet encryption technologies at scale, integrating TURMOIL's passive collection with NSA's LONGHAUL key recovery service via the ISLANDTRANSPORT messaging system, as part of the broader BULLRUN assault on internet encryption.
“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Ball, James · Borger, Julian · Greenwald, Glenn -
Innov8 Voice Analytics Experiment Profile [pdf]
This document outlines Phase 1 of a Voice Analytics experiment conducted by GCHQ in partnership with the NSA, testing the ingestion and processing of voice data through the DISTILLERY platform on GHOSTMACHINE hardware. The experiments evaluate independent, parallel, and linked analytics (SAD, GID, LID), as well as dynamic resource management, to ensure accurate, scalable, and compliant voice processing in a Joint Collaboration Environment.
Marking: TOP SECRET -
Instability creates opportunity against counter-terrorism targets SIDtoday [pdf]
This document reveals how the NSA’s collaboration with Ethiopia during and after the 2006 Ethiopian invasion of Somalia was leveraged to advance U.S. counterterrorism objectives, using SIGINT tools and shared intelligence to track and eliminate al-Qaida targets across the Horn of Africa.