Publisher: The Washington Post 27 documents
Search documents matching “The Washington Post” →Who published each document. Mostly a news outlet, but sometimes a book. A partner outlet that reported the story without publishing the documents keeps its byline and its article, but is not a publisher here.
Showing the documents The Washington Post itself published in 2013 - all years.
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
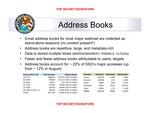
Bulk collection of webmail address books and emerging protocols [pdf]
TOP SECRET NSA document details the large-scale collection of email address books and contact lists from major webmail and social media providers, emphasizing their metadata value despite low attribution rates to known targets. It also highlights ongoing efforts to identify and analyze emerging communication protocols, such as those used by Hotmail Messenger.
-
Content Acquisition Optimization PowerPoint Slides [pdf]
An NSA presentation on content acquisition optimisation — describing how incidental bulk collection from Yahoo Webmessenger, email address books, buddy lists and webmail inboxes was generating massive unintended collection volumes.
-
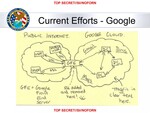
Current Efforts - Google [pdf]
The famous NSA slide from the MUSCULAR program showing where Google's encryption is stripped away — a hand-drawn diagram of Google's cloud architecture annotated with "SSL Added and removed here!" beside a smiley face, marking the exact point where NSA and GCHQ intercepted Google user data flowing unencrypted between Google's data centers.
-
Email from GCHQ to NSA about targeting realms in MONKEY PUZZLE [pdf]
Email from GCHQ's MONKEY PUZZLE development team to NSA clarifying that the system only supports deploying targeting for four specific selector realms: emailAddr, google, msnpassport, and yahoo, while still accepting other realms into the system pool.
Marking: SECRET -
FAA Certification Renewals with Caveats [pdf]
This NSA document shows that after the FISA Court found NSA’s upstream internet collection unconstitutional and illegal, the agency’s response was less about reform and more about finding technical and procedural workarounds to keep surveillance running as usual. While the court ordered changes within 30 days, NSA officials planned to sequester and filter “higher-risk” data to appease the judge—not halt collection—revealing a mindset focused on preserving operations rather than addressing legal violations.
-
FASCIA: The NSA's huge trove of location records [pdf]
FASCIA is the National Security Agency's enormous database containing trillions of metadata records, many with device locations, that are collected from a variety of sources. This document shows the volume and types of device-location data collected by the agency.
“NSA tracking cellphone locations worldwide, Snowden documents show” - The Washington Post ↗ (2013-12-04) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Gellman, Barton · Soltani, Ashkan · Greenwald, Glenn -
FY 2013 Congressional Budget Justification, Volume I, National Intelligence Program Summary, February 2012 [pdf]
This document outlines the $52.6 billion “black budget,” detailing the structure, priorities, successes, and shortcomings of the 16 U.S. intelligence agencies. It reveals unprecedented insight into funding allocations, operations, and intelligence gaps—including the CIA’s dominant role, expanding cyber operations, and persistent challenges in areas such as North Korea and counterterrorism—while emphasizing the tension between secrecy and public accountability.
-
How the NSA Pinpoints a Mobile Device [pdf]
This document is an internal National Security Agency classification guide outlining the agency's abilities to intercept cellular communications.
Programs: ARCVIEW -
How the NSA verifies a target's location [pdf]
This is an excerpt from a transcript of National Security Agency training videos that describe how to verify the location of a targeted device. It explains how the NSA monitors different types of mobile signaling information known as HLR and VLR registrations in order to locate individuals. It also makes clear that the agency is able to use location tracking to ascertain whether a target is in the United States.
-
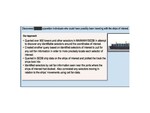
How to tell if a target is 'foreign' [pdf]
The document describes a human intelligence (HUMINT) report indicating that a specific intelligence target, identified by a Foreign Source ID, is located outside the U.S., including details such as email, telephone number, and mobile network type, with checks confirming no U.S. roaming over a 60-day period. It illustrates the use of HUMINT to corroborate foreign location data for surveillance purposes.
-
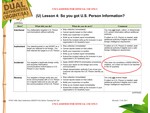
Lesson 4: So you got U.S. Person Information? [pdf]
This slide is used in a training course for NSA intelligence collectors and analysts. It tells the trainees what to do if they collect communications "to, from or about" a U.S. citizen, green card holder or company. The slide's revision date is nearly one month after the Foreign Intelligence Surveillance Court ruled on Oct. 3, 2011 that the NSA's handling of some "U.S. Persons" data was unlawful. The highlighted portion of the slide is notable because it shows that "incidentally" acquired U.S. communications, which may account for the highest volume of American content collected, are not purged from NSA databases. Analysts do not need to report "incidental" collection to the NSA Inspector General because it is not deemed a violation of rules. They may use the data routinely in "minimized" form, with identities masked, and with supervisory permission they may unmask the identities of U.S. persons in reports if the "customer set" requires them.
-
Location Cookies [pdf]
These slides contain excerpts from an April 2013 National Security Agency presentation detailing signal surveillance techniques and successes. They reveal that the NSA and its British counterpart, Government Communications Headquarters (GCHQ), use a Google-specific tracking cookie to pinpoint targets for hacking.
-
NSA/CSS Mission: PROVIDE AND PROTECT VITAL INFORMATION FOR THE NATION [pdf]
These slides, from an internal presentation in the first week of October 2001, show how critical the NSA sees electronic eavesdropping.
-
Op MULLENIZE and beyond - Staining machines 10/10/12 [pdf]
This 2012 report from the NSA's British counterpart, the GCHQ, describes a method of "staining" electronic traffic to distinguish otherwise anonymous users. It is used to unmask Tor users and devices on networks in which many computers share the same Internet address. The method relies on planting code in a web browser to change the "user agent," which is the way the browser identifies itself on the web. In a two month period, the report says, GCHQ managed to implant about 200 computers with uniquely identifying stains.
-
PRISM/US-984XN Overview [pdf]
A 2013 NSA training presentation revealing that major U.S. tech companies — including Google, Facebook, Apple, Microsoft, and Skype — secretly gave the NSA direct access to their servers, allowing the agency to collect users' emails, chats, photos, and files in real time, with the FBI acting as intermediary.
Programs: PRISM · FAIRVIEW · STORMBREW · BLARNEY · OAKSTAR · UTT · PRINTAURA · PINWALE · NUCLEON · TRAFFICTHIEF · SCISSORS · MARINA · MAINWAY · FALLOUT · CONVEYANCE · REPRISMFISA · SSO“U.S., British intelligence mining data from nine U.S. Internet companies in broad secret program” - The Washington Post ↗ (2013-06-06) · “NSA Prism program taps in to user data of Apple, Google and others” - The Guardian ↗ (2013-06-07) · “L'ampleur de l'espionnage mondial par la NSA” - Le Monde ↗ (2013-10-21) · “NSA files decoded: Edward Snowden's surveillance revelations explained” - The Guardian ↗ (2013-11-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “Dark Mirror: Edward Snowden and the American Surveillance State” - Penguin Press ↗ (2020-05-19) · Gellman, Barton · Poitras, Laura · Greenwald, Glenn · MacAskill, Ewen · Untersinger, Martin · Dance, Gabriel -
Roger Dingledine at NSA NOV 2007 [pdf]
An NSA internal wiki page summarising a talk given at NSA on 1 November 2007 by Roger Dingledine, one of Tor's inventors, covering who Tor's users are, anonymity system design concepts, and Tor's weaknesses.
People: Dingledine, Roger -
SID Oversight and Compliance [pdf]
Signals Intelligence Directorate (SID) oversight and compliance. A 2012 quarterly audit of the NSA's surveillance activities, which describes 865 violations by the NSA of the surveillance laws and its internal rules and regulations.
-
Special Source Operations - The Cryptologic Provider of Intelligence from Global High-Capacity Telecommunications Systems [pdf]
The document outlines NSA special source operations for accessing global telecommunications data, detailing corporate and foreign cable interception programs. It highlights the MUSCULAR program (DS-200B), a joint NSA–GCHQ operation in the UK that taps into high-capacity fiber-optic links to collect and process large volumes of data from private networks.
-
SSO Collection Optimization [pdf]
This is another presentation on problems with the National Security Agency's overcollection of address books and buddy lists and its efforts to weed out useless content. See also EFF_-_20131104-wapo-optimization_google
-
SSO Collection Optimization [pdf]
The documents reveal that the NSA, in collaboration with GCHQ, accessed private internal networks of Google and Yahoo by intercepting data in transit between their data centers, without breaking into user accounts or servers. This involved analyzing proprietary formats and protocols, such as Google’s Gaia authentication system, using specialized tools to extract intelligence while operating primarily under foreign jurisdiction with fewer legal restrictions.