Publication year: 2014 283 documents
Search documents matching “2014” →When a publisher first published each document. If a document is published multiple times, only the oldest one is used here.
Graphs
By document date (12 years)
By published date (6 years)
Sort: Title
Documents
-
CLASSIFICATION GUIDE FOR THE NSA/CSS TARGET EXPLOITATION (TAREX) PROGRAM [pdf]
A 2012 NSA/CSS classification guide for the TAREX program — the agency's clandestine human intelligence and close-access signals intelligence unit — establishing what information about TAREX's operations, locations, methodologies, and interagency relationships must be protected, revealing forward-based presences in Germany, South Korea, and Beijing, and confirming that TAREX personnel operate undercover at U.S. embassies worldwide.
Programs: TAREXPeople: Shea, Teresa H. -
CNE EndPoint Project Load [pdf]
The CNE EndPoint Project Load document lists multiple GCHQ exploitation projects, with “PFENNING ALPHA” targeting Flag Telecom’s network. It notes automated pulls of router monitoring webpages, collection of performance statistics, and ongoing efforts to gain further access points within Reliance’s infrastructure, while other projects and targets remain redacted.
Programs: PFENNING ALPHA · BURRITO ALPHA · GLADDY IOTA · HEADRESS IOTA · HEADRESS KAPPA · HEADRESS NU · HEADRESS OMICRON · GLADDY CHI · EREPO · RELIANCE · GTE“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
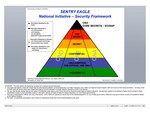
CNO Core Secrets Security Structure [pdf]
A 3-slide NSA presentation outlining the classification architecture of Sentry Eagle, a national cyber operations initiative, showing how its most sensitive components — covering network hacking, encryption sabotage, and covert industry relationships — are locked behind ECI and SAP designations accessible only to a tiny circle of government officials.
Programs: SENTRYEAGLE · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL -
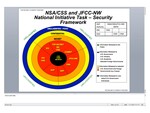
CNO Core Secrets Slide Slices [pdf]
This document outlines the Security Framework for a joint national initiative between the NSA/CSS and JFCC-NW, detailing the highly compartmented structure used to protect cyber and intelligence secrets. It utilizes a concentric security framework diagram to visualize the layers of sensitivity, placing the most critical technical capabilities at the absolute center of the intelligence community's protection.
Programs: SENTRY-EAGLE · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL -
Collaboration in Overdrive: A CNE Success SIDtoday [pdf]
A collaboration between several NSA departments achieved, for the first time, Computer Network Exploitation against "Turkish leadership."
Programs: CMAP“Turkey Is 'Partner and Target' for the NSA” - Der Spiegel ↗ (2014-08-31) · “How the NSA Helped Turkey Kill Kurdish Rebels” - The Intercept ↗ (2014-08-31) · The Intercept ↗ (2019-05-29) · Poitras, Laura · Rosenbach, Marcel · Sontheimer, Michael · Stark, Holger -
Computer Network Exploitation (CNE) Classification Guide / 2-59 [pdf]
A NSA/TAO classification guide establishing the precise classification level for 41 categories of information about computer network exploitation operations — covering remote and physical subversion methods, CNE tools and techniques, supply chain operations, hardware implants, off-net field operations, zero-day vulnerabilities, and cryptographic material acquired through CNE.
“Core Secrets: NSA Saboteurs in China and Germany” - The Intercept ↗ (2014-10-10) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Maass, Peter · Poitras, Laura · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
Content Extraction Enhancements For Target Analytics: SMS Text Messages: A Goldmine to Exploit (9 June 2011) [pdf]
The document describes the NSA’s Dishfire program, which collects hundreds of millions of global SMS messages daily, and the PREFER system, which extracts detailed metadata—including contacts, geolocation, travel, and financial information—from these messages for analytic purposes. It highlights the scale, operational processes, and types of data exploited to support intelligence and target analysis.
-
Converged Analysis of Smartphone Devices [pdf]
This 2010 document outlines NSA methods for identifying, processing, and exploiting data from smartphones by targeting both telephony and digital network intelligence (DNI). It details how analysts use tools like XKEYSCORE and metadata extraction to collect geolocation, app data, call logs, unique identifiers, and user activity from popular mobile apps and services (e.g., Google Maps, Facebook, Flickr), emphasizing the intelligence potential of smartphones as rich surveillance targets.
People: Kuruc, Paula -
Cooperation between the NSA and BND [pdf]
Comprehensive internal summary of the history and current state of cooperation between the NSA and BND
Programs: RT-RGPeople: Schindler, Gerhard -
CRISSCROSS/PROTON Point Paper [pdf]
Originating as a CIA/DEA joint venture in the 1990s, CRISSCROSS/PROTON is a centralized repository used by five U.S. agencies (CIA, DEA, NSA, DIA, FBI) for massive link analysis and contact chaining. The document details how the NSA provides billions of telephony records to the system to assist in capturing High Value Individuals (HVIs) but recommends transitioning to an NSA-led architecture using the GLOBALREACH federated query service.
-
Crypt Discovery Joint Collaboration Activity 20 January 2011 [pdf]
A TOP SECRET NSA/GCHQ joint collaboration activity plan from January 2011 describing a research programme to understand and mitigate the threat that rising encryption adoption poses to target discovery and development — measuring encryption prevalence across SIGINT collection, assessing the impact on metadata-based targeting tradecraft, and developing new techniques for identifying targets behind encrypted traffic using a joint cloud environment fed by MUTANT BROTH, BEARDED PIGGY, KARMA POLICE, MEMORY HOLE, MARBLED GECKO, SOCIAL ANIMAL and ASDF metadata.
Marking: TOP SECRETPrograms: TICKETWINDOW · MUTANTBROTH · BEARDEDPIGGY · KARMAPOLICE · MEMORYHOLE · MARBLEDGECKO · SOCIALANIMAL · XKEYSCORE · ASDF“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “Profiled: From Radio to Porn, British Spies Track Web Users' Online Identities” - The Intercept ↗ (2015-09-25) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Gallagher, Ryan -
Crypt Ops Data Store User Guide [pdf]
A SECRET GCHQ user guide for the Crypt Ops Data Store — the internal task management system used by GCHQ's cryptanalytic operations division to receive, triage, assign and track decryption and cryptanalytic requests — notable for its category list which maps task types to operational programmes including BULLRUN, BEARDED PIGGY and VPN exploitation.
Marking: SECRET -
Cryptographic Modernization (CryptoMod) Classification Guide 3-9 [pdf]
A partial NSA/CSS classification guide for the Cryptographic Modernisation (CryptoMod) programme — establishing classification levels for information about NSA's transition of US cryptographic products to modern algorithms, Positive Access Control parameters, software signing, and the association of specific algorithms with critical year and life-of-use assessments.
-
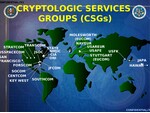
CRYPTOLOGIC SERVICES GROUPS (CSGs) [pdf]
Worldwide locations of the Cryptologic Services Groups (CSGs). The visual is a world map annotated with the locations of CSGs embedded in or supporting major U.S. combatant commands and agencies. These groups act as NSA’s cryptologic arms inside military commands. Cryptologic operations are co-located with military command authority and signals intelligence is structurally tied to every major U.S. warfighting domain.
-
CSEC Surveillance of Travellers Through Airport Wi-Fi Tracking [pdf]
The leaked 2012 top secret CSEC presentation details a trial program that used airport Wi-Fi metadata to identify and track travellers’ devices across Canada and internationally, developing advanced “IP profiling” techniques to map movements through hotels, airports, and public hotspots. The program, conducted with NSA support, aimed to build powerful analytic tools for surveillance and real-time alerts within the Five Eyes intelligence network.
Marking: TOP SECRET -
Cyber Integration [pdf]
The leaked 2012 GCHQ JTRIG presentation detail a wide range of offensive cyber and influence operations designed to “deny, disrupt, degrade, and deceive” targets, including hackers, foreign governments, companies, and individuals. Tactics include hacking, DDOS attacks, disinformation, honey traps, credential harvesting, and psychological operations, reflecting a shift from traditional surveillance to active disruption and manipulation campaigns.
“Exclusive: Snowden Docs Show British Spies Used Sex and 'Dirty Tricks'” - NBC News ↗ (2014-02-07) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Cole, Matthew · Esposito, Richard · Schone, Mark · Greenwald, Glenn -
DEA - The "Other" Warfighter SIDtoday [pdf]
NSA SIGINT helped the Drug Enforcement Administration achieve "major successes" in the war on drugs. This role is little known. Examples are provided.
People: Hinojosa, Gonzalo“The NSA Is Recording Every Cell Phone Call in the Bahamas” - The Intercept ↗ (2014-05-19) · The Intercept ↗ (2016-12-07) · Devereaux, Ryan · Greenwald, Glenn · Poitras, Laura -
Decision Memorandum for the DNI on ICREACH [pdf]
This 2006 memorandum from the Director of the NSA, Keith B. Alexander, requests that the Director of National Intelligence authorize the NSA to create ICREACH, a new Intelligence Community-wide system for sharing communications metadata. The proposal designates the NSA as the executive agent for this new structure, which would replace the older, less scalable PROTON program and grant unprecedented data access to partner agencies.
People: Alexander, Keith B. -
Denmark DDIS partnership with NSA (2013) [pdf]
This document provides classified talking points and administrative guidance for the Director of the NSA (DIRNSA) regarding the DENUSA conference and the agency’s strategic partnership with the Danish Defence Intelligence Service (DDIS). It highlights the long-standing collaboration between the two nations on specialized cable access programs and reaffirms the NSA’s commitment to maintaining and expanding access to high-capacity international fiber-optic cables transiting Danish territory.
“How Secret Partners Expand NSA’s Surveillance Dragnet” - The Intercept ↗ (2014-06-18) · “NSA ‘third party’ partners tap the Internet backbone in global surveillance program” - Dagbladet Information ↗ (2014-06-19) · Gallagher, Ryan · Geist, Anton · Gjerding, Sebastian · Moltke, Henrik · Poitras, Laura -
Discovery SIGINT Targeting Scenarios and Compliance [pdf]
This document is a top-secret NSA guidance manual detailing SIGINT targeting scenarios, compliance procedures, and legal guidance for querying foreign actors, malware, and potentially U.S.-linked systems, including considerations for minimizing incidental collection of U.S. persons’ communications. It outlines specific rules, approvals, and exceptions for using SIGINT tools, foreign intelligence tasks, and cases involving ambiguous or dual-use selectors like WikiLeaks, The Pirate Bay, and foreign actors operating through U.S. infrastructure.