Document year: 2011-01 21 documents
Search documents matching “2011-01” →When each document was written, from its own dateline. Undated documents don't appear here.
Sort: Title
Documents
-
AURORAGOLD – Project Overview [pdf]
A technical briefing document outlining an NSA SIGINT initiative designed to map, monitor, and forecast the evolution of global mobile networks. It details the project's infrastructure, which aggregates both unclassified commercial data and classified intelligence intercepted from international roaming agreements to identify technical trends and exploitation opportunities.
-
AURORAGOLD – Target Technology Trends Center support to WPMO [pdf]
This briefing details the technical architecture and data pipeline used to process global cellular network information. It specifically highlights the synergy between data gathering on GSM/UMTS networks and the implementation of "Auto-Minimization" to ensure the resulting SIGINT reporting complies with NSA legal and policy requirements.
-
Automated NOC detection [pdf]
This slide deck lays out how GCHQ and Canada’s CSEC systematically identified and penetrated Network Operations Centers—most notably Belgacom—by automating NOC discovery and weaponizing that mapping for QUANTUM INSERT attacks. It reads like a blueprint for turning router configs, metadata, and bulk scans into cookie-based targeting against telecom engineers inside core networks.
Programs: SURGE · NOCTURNALSURGE · RT · NACSHACK · CHAINGUARD · TIDALSURGE · GLOBALSURGE · PENTAHO · OLYMPIA · HYPERION · TERMINALSURGE · HACIENDA · QUANTUMINSERT · MUTANTBROTH · OPSOCIALIST · SAMUEL PEPYS · GEOFUSION · FIVEALIVE · NRTA · RADIUS“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
Crypt Discovery Joint Collaboration Activity 20 January 2011 [pdf]
A TOP SECRET NSA/GCHQ joint collaboration activity plan from January 2011 describing a research programme to understand and mitigate the threat that rising encryption adoption poses to target discovery and development — measuring encryption prevalence across SIGINT collection, assessing the impact on metadata-based targeting tradecraft, and developing new techniques for identifying targets behind encrypted traffic using a joint cloud environment fed by MUTANT BROTH, BEARDED PIGGY, KARMA POLICE, MEMORY HOLE, MARBLED GECKO, SOCIAL ANIMAL and ASDF metadata.
Marking: TOP SECRETPrograms: TICKETWINDOW · MUTANTBROTH · BEARDEDPIGGY · KARMAPOLICE · MEMORYHOLE · MARBLEDGECKO · SOCIALANIMAL · XKEYSCORE · ASDF“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “Profiled: From Radio to Porn, British Spies Track Web Users' Online Identities” - The Intercept ↗ (2015-09-25) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Gallagher, Ryan -
DoD 2011 Strategy for Operating in Cyberspace – Supply Chain Excerpts [pdf]
The classified 2011 Department of Defense strategy warns that U.S. reliance on foreign manufacturing—especially from countries like China—creates major cybersecurity risks, including the potential insertion of malicious hardware or software into critical systems. It outlines a government-wide plan to mitigate these supply chain vulnerabilities through coordinated policies, risk management strategies, and collaboration with industry.
-
Fourth Party Opportunities [pdf]
This presentation document explains how NSA identifies, prioritizes, and exploits “fourth party” opportunities by passively or actively leveraging foreign computer network exploitation operations, including victim stealing and tool repurposing, to collect intelligence without initiating original intrusions.
Programs: VOYEUR · UIS · PINWALE · YNKE · TUNINGFORK · DIRTSHED · SEEKER · CLOUD · ABR · SILVERBOLT · DEADSEA · XKEYSCORE · BYZANTINERAPTOR · HAWALA · ZEBEDEE · DATAFLURRY · ECLECTICPLOT · HAPPYFOOT · BLUESMOKE · CROSSBONES2 · CYBERQUEST · VICDB · PLAIDDIANA · TRANSGRESSION -
GCHQ – Making network sense of the encryption problem (2011) [pdf]
GCHQ’s Network Analysis Centre convened a 2011 roundtable on “making network sense” of encryption, pushing a metadata-first strategy to triage SSL/TLS, IKE, OpenVPN, and SSH flows, pivot from “seed” indicators, and zero in on targets and subnets worth decrypting. The playbook leans on enrichment, AS-level scoping (explicitly citing Belgacom AS6774 GRX VPNs), and “access optimisation” to collect data pre‑encryption—passively or actively.
Programs: SQUEAL · BEARDEDPIGGY · CLOUD · IRASCIBLEHARE · IRASCIBLERABBIT · IRASCIBLEMOOSE · IRASCIBLEEMITT“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
Hackers are Humans too - Cyber leads to CI leads [pdf]
This document from Canada’s Communications Security Establishment (CSE) analyzes the Russian hacking team MAKERSMARK, highlighting how its operators misused technically sophisticated but poorly secured infrastructure, mixing personal and operational activity, which made them traceable despite their advanced tools. It details CSE’s methods for attributing cyber intrusions, monitoring malware-infected systems, and exploiting operational security lapses to gain intelligence on Russian cyber operations.
-
New Contact-Chaining Procedures to Allow Better, Faster Analysis SIDtoday [pdf]
The SIGINT Management Directive 424 briefing (Jan 2011) announces a major procedural shift at the NSA, allowing analysts to conduct contact chaining and large-scale metadata analysis from any selector, regardless of nationality or location. This change removes prior restrictions on U.S. data, enabling more powerful social network mapping for foreign intelligence purposes.
Programs: GATEKEEPER -
NSA target package [pdf]
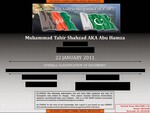
This 2011 target package focuses on Muhammad Tahir Shahzad (alias Abu Hamza), a Pakistan-based bomb builder and Al-Qaeda facilitator. The document was produced by the Counter IED Analysis Integration Cell (CAIC) at the NSA. Notably, the document credits the tracking of Shahzad’s 60+ digital selectors with the eventual capture of high-value targets, including himself and Bali bombing suspect Umar Patek. The accompanying Washington Post investigation uses this specific case to highlight the massive scale of "incidental collection." While Shahzad was a valid foreign target under Section 702 of the FISA Amendments Act (FAA), the investigation revealed that for every legitimate target like him, the NSA intercepted nine "non-targeted" users—many of whom were Americans—capturing deeply personal photos, medical records, and private correspondence.
-
NWP NSA [pdf]
A January 2011 internal NSA newsletter from Yakima Research Station (YRS) covering the station's early history as the West Coast ECHELON/FROSTING satellite interception facility established in 1966 to collect INTELSAT communications, and its more recent expansion into cloud-based cyber threat discovery using FORNSAT and Special Source Operations data.
Programs: EARLYBIRD · FROSTING · TRANSIENT · ECHELON · JACKKNIFE · SAFEGUARD · STEAMS · CYBERQUEST · GINPENNANT · RUMBUCKET · CROSSBONES · SSO -
Project SANDSTORM [pdf]
This document shortly describes Project SANDSTORM, part of the Active Sigint Enabling Passive Geolocation (ASEPG) program at Menwith Hill, which uses Wi-Fi signal characterization and satellite-based Overhead capabilities to geolocate high-value targets, with geolocations of under 100 meters expected even for low-power signals in denied areas. It focuses on actively enabling SIGINT to track targets via 802.11 wireless networks.
-
RAMPART-A Sites [pdf]
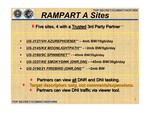
This document specifies the data throughput and operational constraints of five key RAMPART-A interception sites, including the implementation of the "DNI Throttle" to manage data volume. It also defines the "Support Hub" model for managing signals tasking and explains the role of the REDHARVEST compartment in restricting which analysts can view specific digital network categories.
Programs: RAMPART-A · AZUREPHOENIX · MOONLIGHTPATH · SPINNERET · SMOKYSINK · FIREBIRD · XKEYSCORE · PINWALE · REDHARVEST · CADENCE“How Secret Partners Expand NSA’s Surveillance Dragnet” - The Intercept ↗ (2014-06-18) · “NSA ‘third party’ partners tap the Internet backbone in global surveillance program” - Dagbladet Information ↗ (2014-06-19) · Gallagher, Ryan · Geist, Anton · Gjerding, Sebastian · Moltke, Henrik · Poitras, Laura -
Report about Operation Doody - The Child of the Neighbor Shot By Accident [pdf]
This Dynamic Target Storyboard documents a 7 Feb 2011 UK AH‑64 engagement (Op STEN TAKAY) against “Obj DOODY” (Mullah Niaz Muhammed, IS3673), a JPEL mid‑level Taliban commander, which culminated in an AGM‑114 miss that may have killed a local child and wounded another civilian, and a follow‑on 30mm strafing run that wounded the target.
People: Muhammed, Mullah Niaz -
Secure key extraction by physical de-processing of Apple's A4 processor [pdf]
An abstract from the CIA Trusted Computing Base Jamboree describing a physical chip decapping and de-processing attack on Apple's A4 processor to extract the embedded Global ID cryptographic key, which if successful would enable decryption of boot firmware across all A4-based Apple devices including the iPhone 4, iPod Touch and iPad.
“The CIA Campaign to Steal Apple's Secrets” - The Intercept ↗ (2015-03-10) · Scahill, Jeremy · Begley, Josh -
Special Source Operations [pdf]
This document provides an overview of the NSA’s Special Source Operations (SSO), characterizing the division as the premier "Cryptologic Provider" for intelligence derived from global high-capacity telecommunications. It outlines a three-tiered access portfolio—Corporate, Foreign, and Unilateral—designed to manage the "incredible challenge" of intercepting target communications across undersea fiber-optic cables that carry millions of simultaneous sessions.
Programs: RAMPART-A · WINDSTOP · BLARNEY · FAIRVIEW · STORMBREW · OAKSTAR · PRISM · RAMPART-I · RAMPART-T · SSO · RAMPART-X · ClanSIG · MYSTIC · LOPERS · WEALTHYCLUSTER-2 · DEEPDIVE · TURMOIL · FASCIA · PINWALE · MARINA · TRAFFICTHIEF · TWISTEDPATH · BLACKPEARL · ACS“How Secret Partners Expand NSA’s Surveillance Dragnet” - The Intercept ↗ (2014-06-18) · “NSA ‘third party’ partners tap the Internet backbone in global surveillance program” - Dagbladet Information ↗ (2014-06-19) · Gallagher, Ryan · Geist, Anton · Gjerding, Sebastian · Moltke, Henrik · Poitras, Laura -
SSO news excerpts [pdf]
These SSO news exceprts describe the successful deployment of QUANTUMTHEORY and QUANTUMINSERT capabilities by the NSA’s Tailored Access Operations (TAO) team, in collaboration with Special Source Operations (SSO), to exploit high-value targets, including key figures in the Haqqani network. Using a combination of signal case notations and real-time exploitation via QUANTUMHAND, TAO was able to implant malicious software on the target's computer, enabling further intelligence collection and exploitation.
Programs: QUANTUMTHEORY · QUANTUM · QUANTUMINSERT · FOXACID · DANCINGOASIS · FOXCONTACT · VALIDATOR · SARATOGA · TURMOIL · QUANTUMHAND · SSOPeople: Haqqani, Badruddin -
The SIGINT Philosopher: Too Many Choices SIDtoday [pdf]
The inaugural 2011 NSA SIDtoday "SIGINT Philosopher" column by a Russian language analyst, using the everyday paralysis of grocery shopping to introduce the concept of "analysis paralysis" and argue that the SIGINT enterprise's greatest challenge is not a lack of access or information but the cognitive difficulty of prioritizing among an overwhelming abundance of choices.
People: Simon, Herbert -
TREASUREMAP Announces a New Release SIDtoday [pdf]
A January 2011 NSA SIDtoday announcement from NTOC's Office of Technology Development detailing a new release of TREASURE MAP — the global internet mapping system — and confirming it is accessible to all NSANet, JWICS, and SIPRNet users with valid PKI certificates, with new features including router configuration exports, traceroute improvements, wireless access point visualization, and enhanced target identification tools.
Programs: TREASUREMAP -
TUTELAGE 411 [pdf]
TUTELAGE is a SIGINT-driven cyber defense and counterintelligence platform that enables NSA to observe, intercept, redirect, block, and manipulate adversary network activity at DoD gateways, transforming intrusion response from post-incident reporting into real-time mitigation and intelligence generation.
Programs: TUTELAGE · CYBERQUEST · XKEYSCORE · GNOMEVISION · POPQUIZ · BISHOPKNIGHT · BLACKENERGY · BLINDMARKSMEN · BYZANTINEFOOTHOLD · BYZANTINEVIKING · CARBONPEPTIDE · CONFICKER · DANCING PANDA · DISCOVERY · GNOMEFISHER · MAKERSMARK · MAVERICKCHURCH · NATIVEDANCER · WEASELWAGGLE · SUBTLESNOW · WIDOWKEY · ZEUS · GHOSTMACHINE · PANDORASMAYHEM · TURBINE · QUANTUM · BYZANTINEHADES · AMULETSTELLAR · TURNABOUT