TUTELAGE 411
Open PDFDocument date: 2011-01-01
Pages: 30
Genre: slides
Banner: TOP SECRET//COMINT//REL TO USA, FVEY
Classification: TOP SECRET COMINT
Dissemination: REL TO USA, FVEY
TUTELAGE is a SIGINT-driven cyber defense and counterintelligence platform that enables NSA to observe, intercept, redirect, block, and manipulate adversary network activity at DoD gateways, transforming intrusion response from post-incident reporting into real-time mitigation and intelligence generation.
My notes
TOP SECRET//COMINT//REL TO USA, FVEY
TUTELAGE
4 1 1
SPECIAL PROJECTS
NSA/CSS THREAT OPERATIONS CENTER
TOP SECRET//COMINT//REL TO USA,
TOP SECRET//COMINT//REL TO USA, FVEY
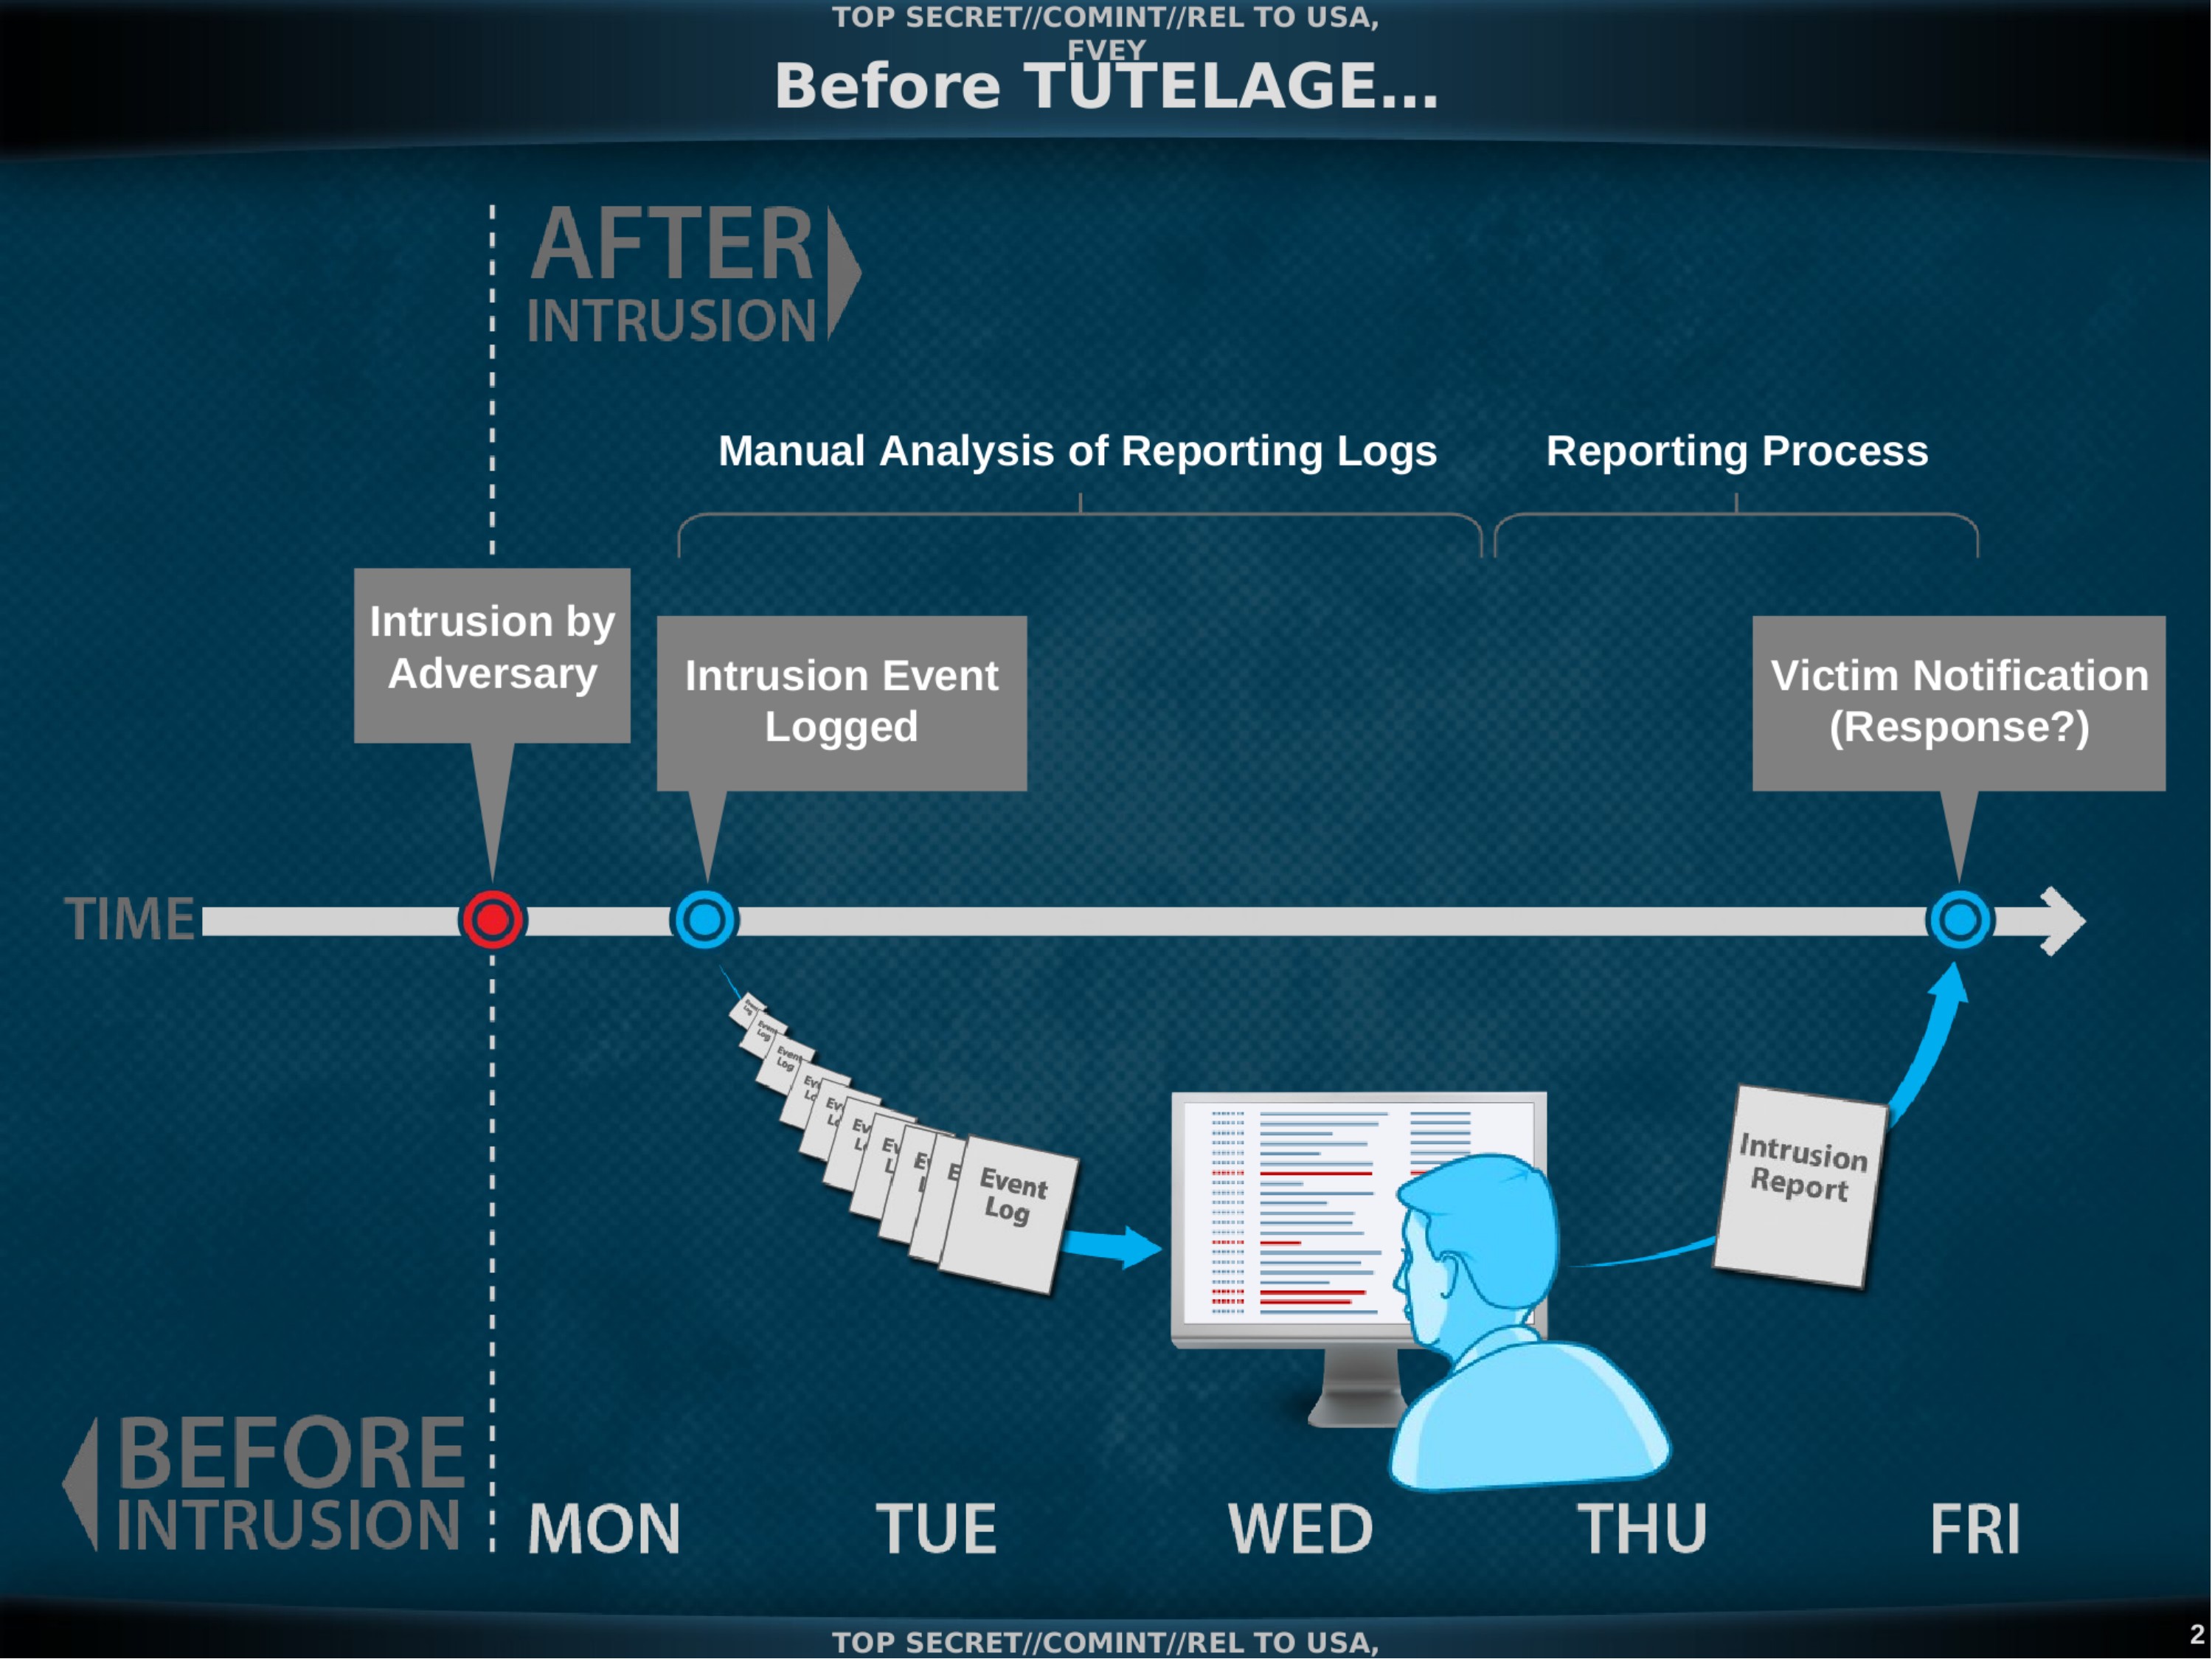
Before TUTELAGE...
AFTER INTRUSION
Manual Analysis of Reporting Logs
Reporting Process
TIME
- Intrusion by Adversary
- Intrusion Event Logged
- Event Log
- Intrusion Report
- Victim Notification (Response?)
BEFORE INTRUSION
MON TUE WED THU FRI
TOP SECRET//COMINT//REL TO USA,
2
TOP SECRET//COMINT//REL TO USA, FVEY
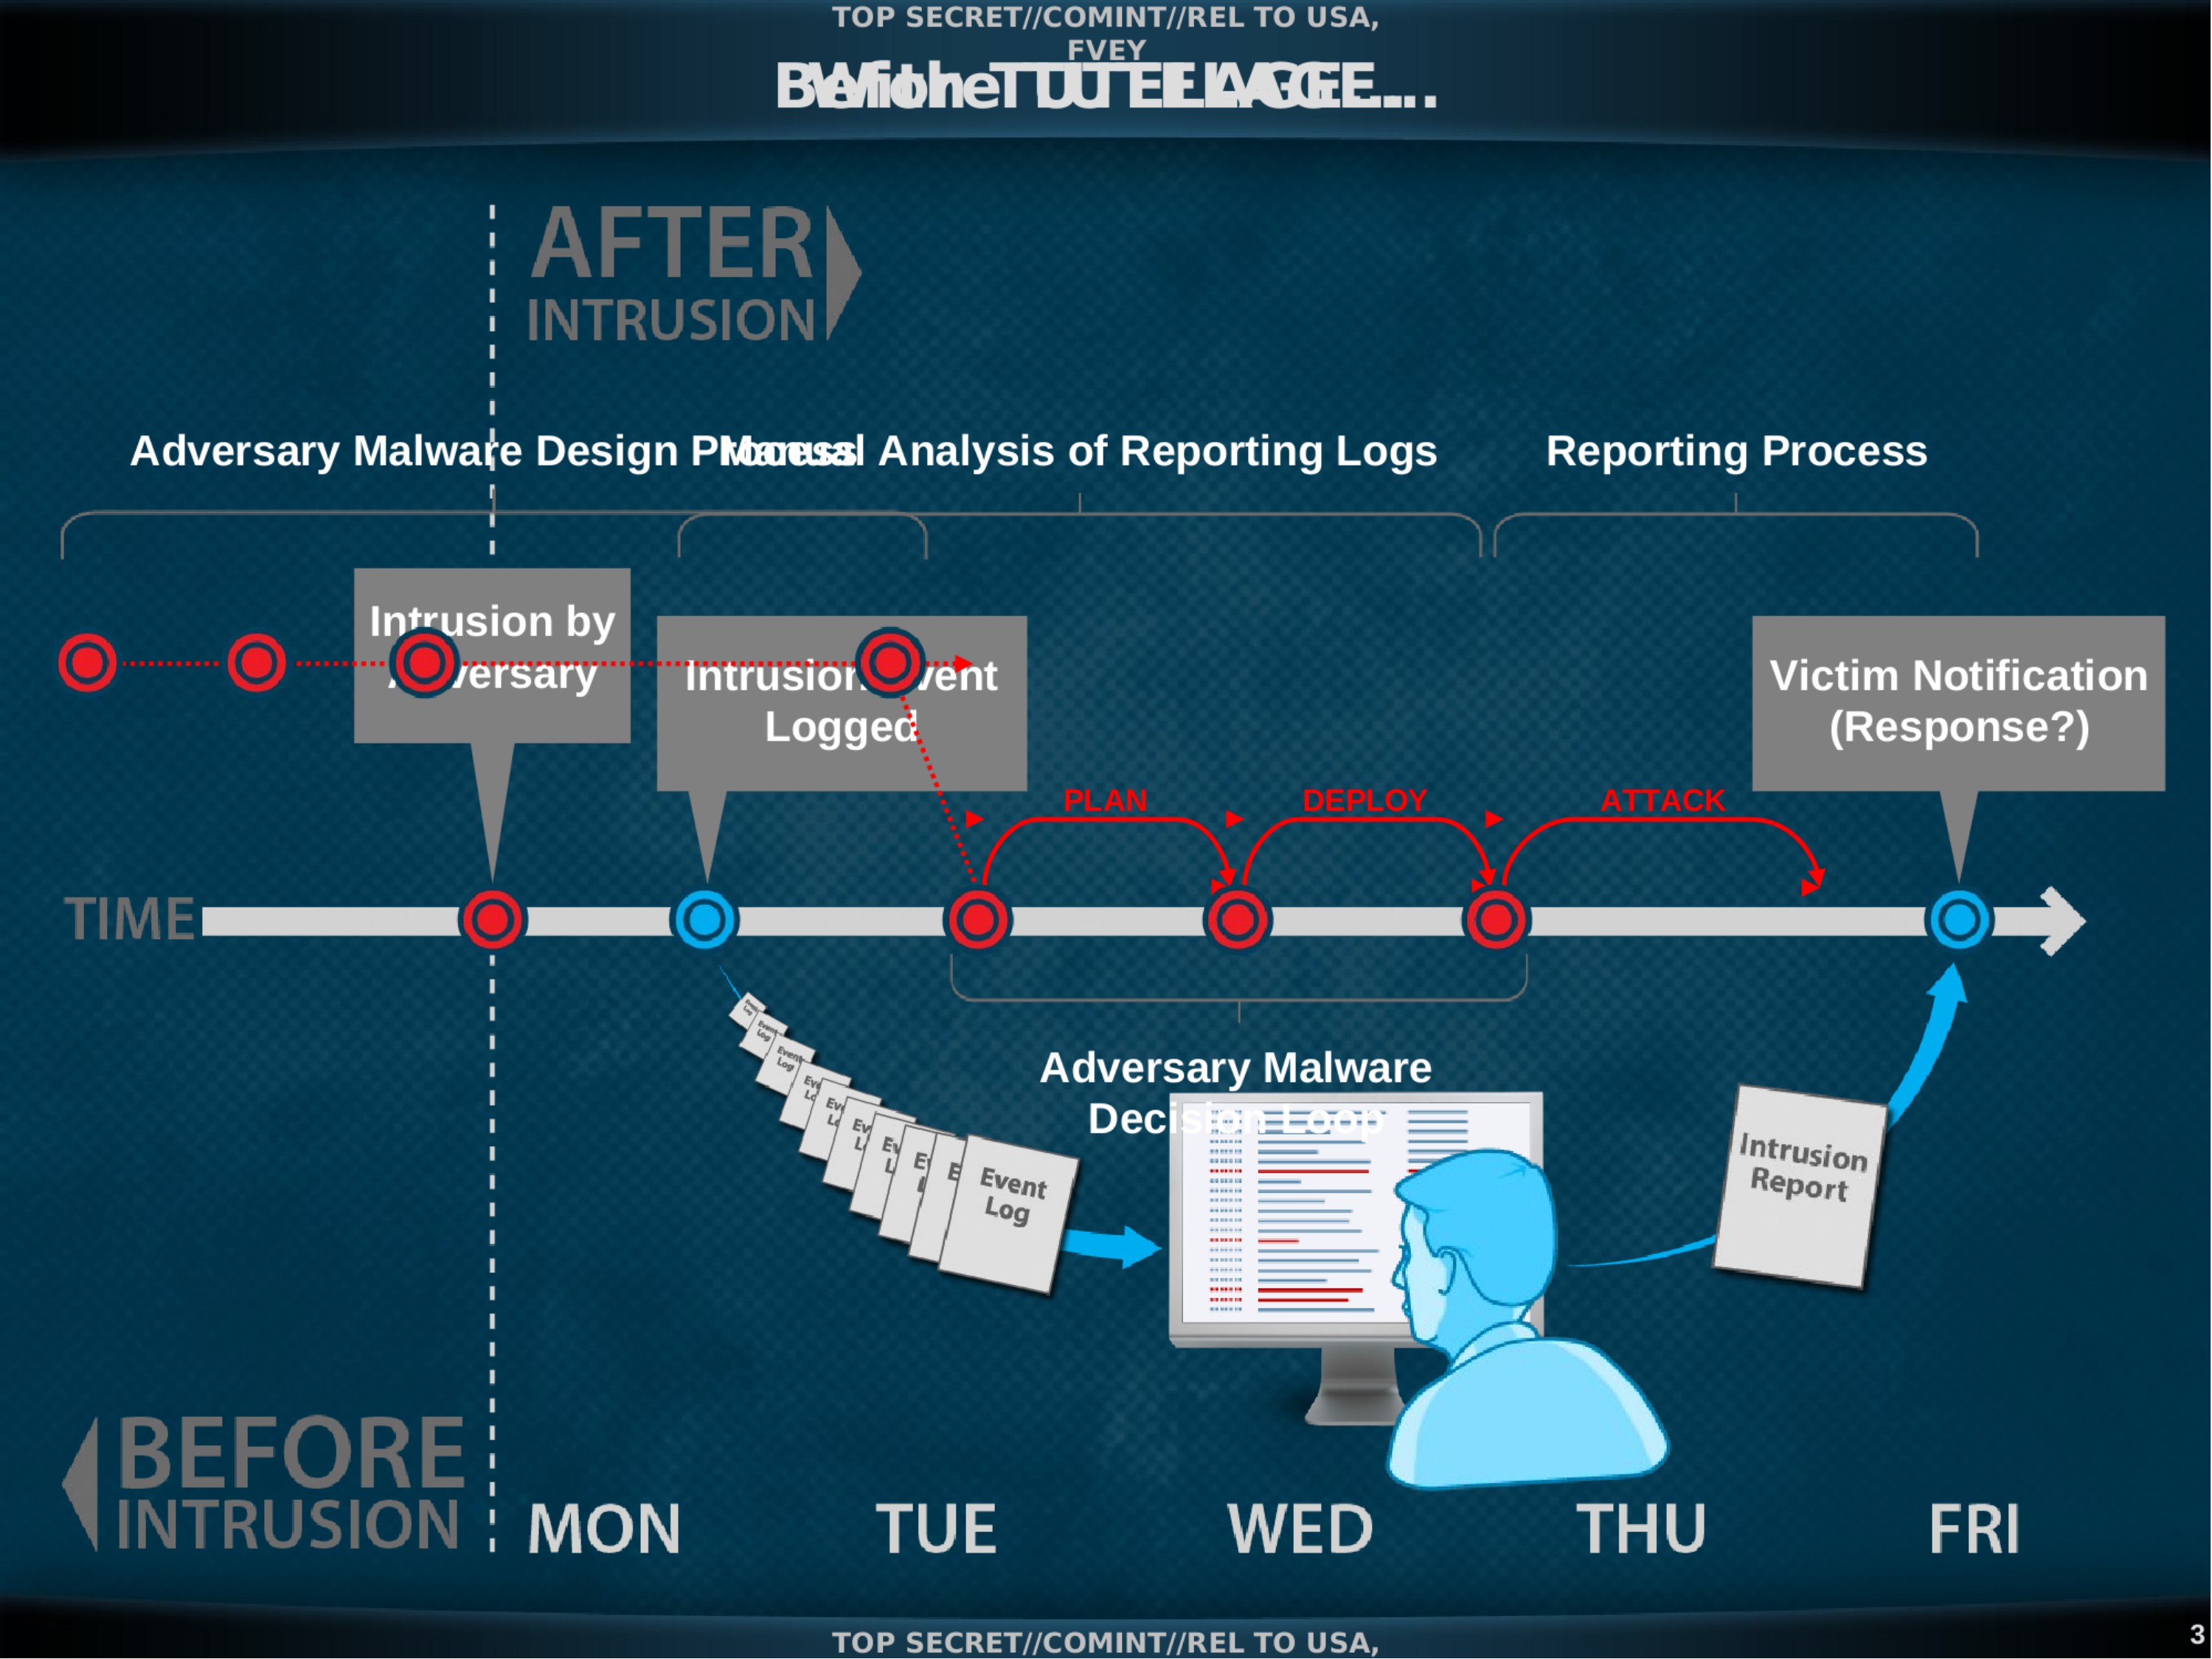
Before TUTELAGE...
AFTER INTRUSION
Adversary Malware Design Process
Manual Analysis of Reporting Logs
Reporting Process
TIME
- Intrusion by Adversary
- Intrusion Event Logged
- PLAN
- DEPLOY
- ATTACK
- Event Log
- Adversary Malware Decision
- Intrusion Report
- Victim Notification (Response?)
BEFORE INTRUSION
MON TUE WED THU FRI
TOP SECRET//COMINT//REL TO USA,
3
TOP SECRET//COMINT//REL TO USA, FVEY
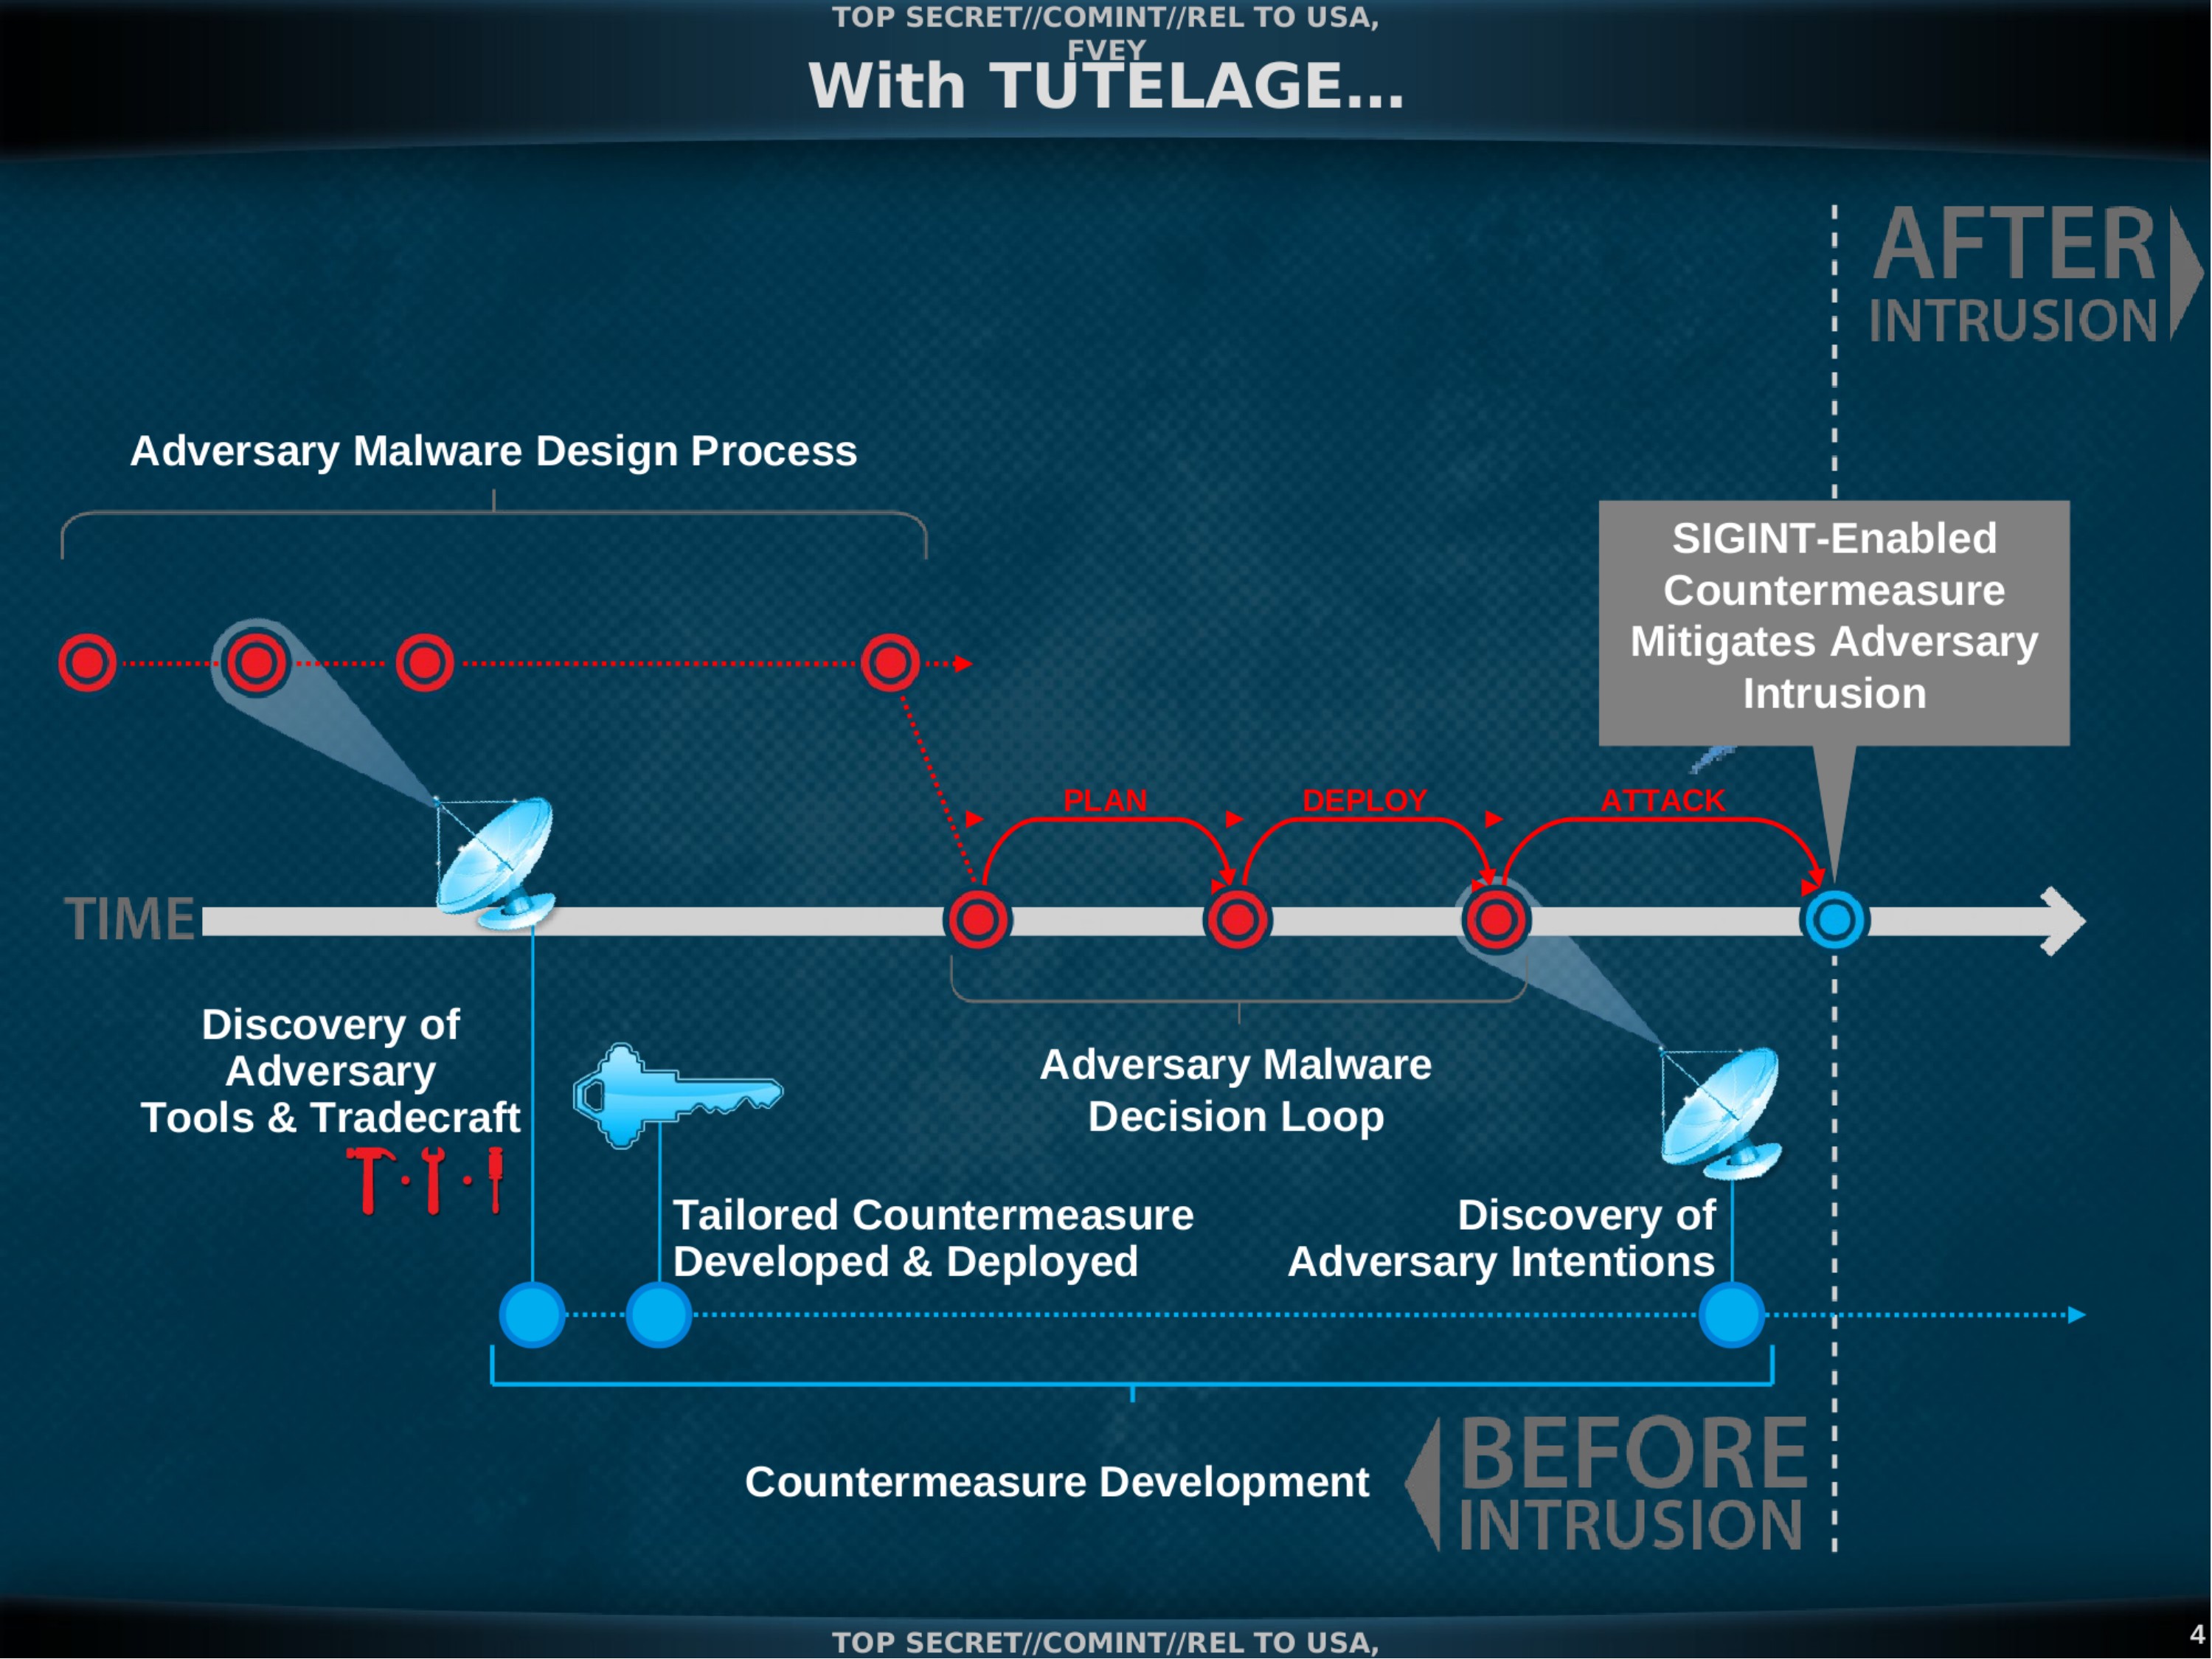
With TUTELAGE...
AFTER INTRUSION
Adversary Malware Design Process
- Discovery of Adversary Tools & Tradecraft
- Tailored Countermeasure Developed & Deployed
- Discovery of Adversary Intentions
- Adversary Malware Decision Loop
- PLAN
- DEPLOY
- ATTACK
- SIGINT-Enabled Countermeasure Mitigates Adversary Intrusion
TIME
Countermeasure Development
BEFORE INTRUSION
TOP SECRET//COMINT//REL TO USA,
4
TOP SECRET//COMINT//REL TO USA, FVEY
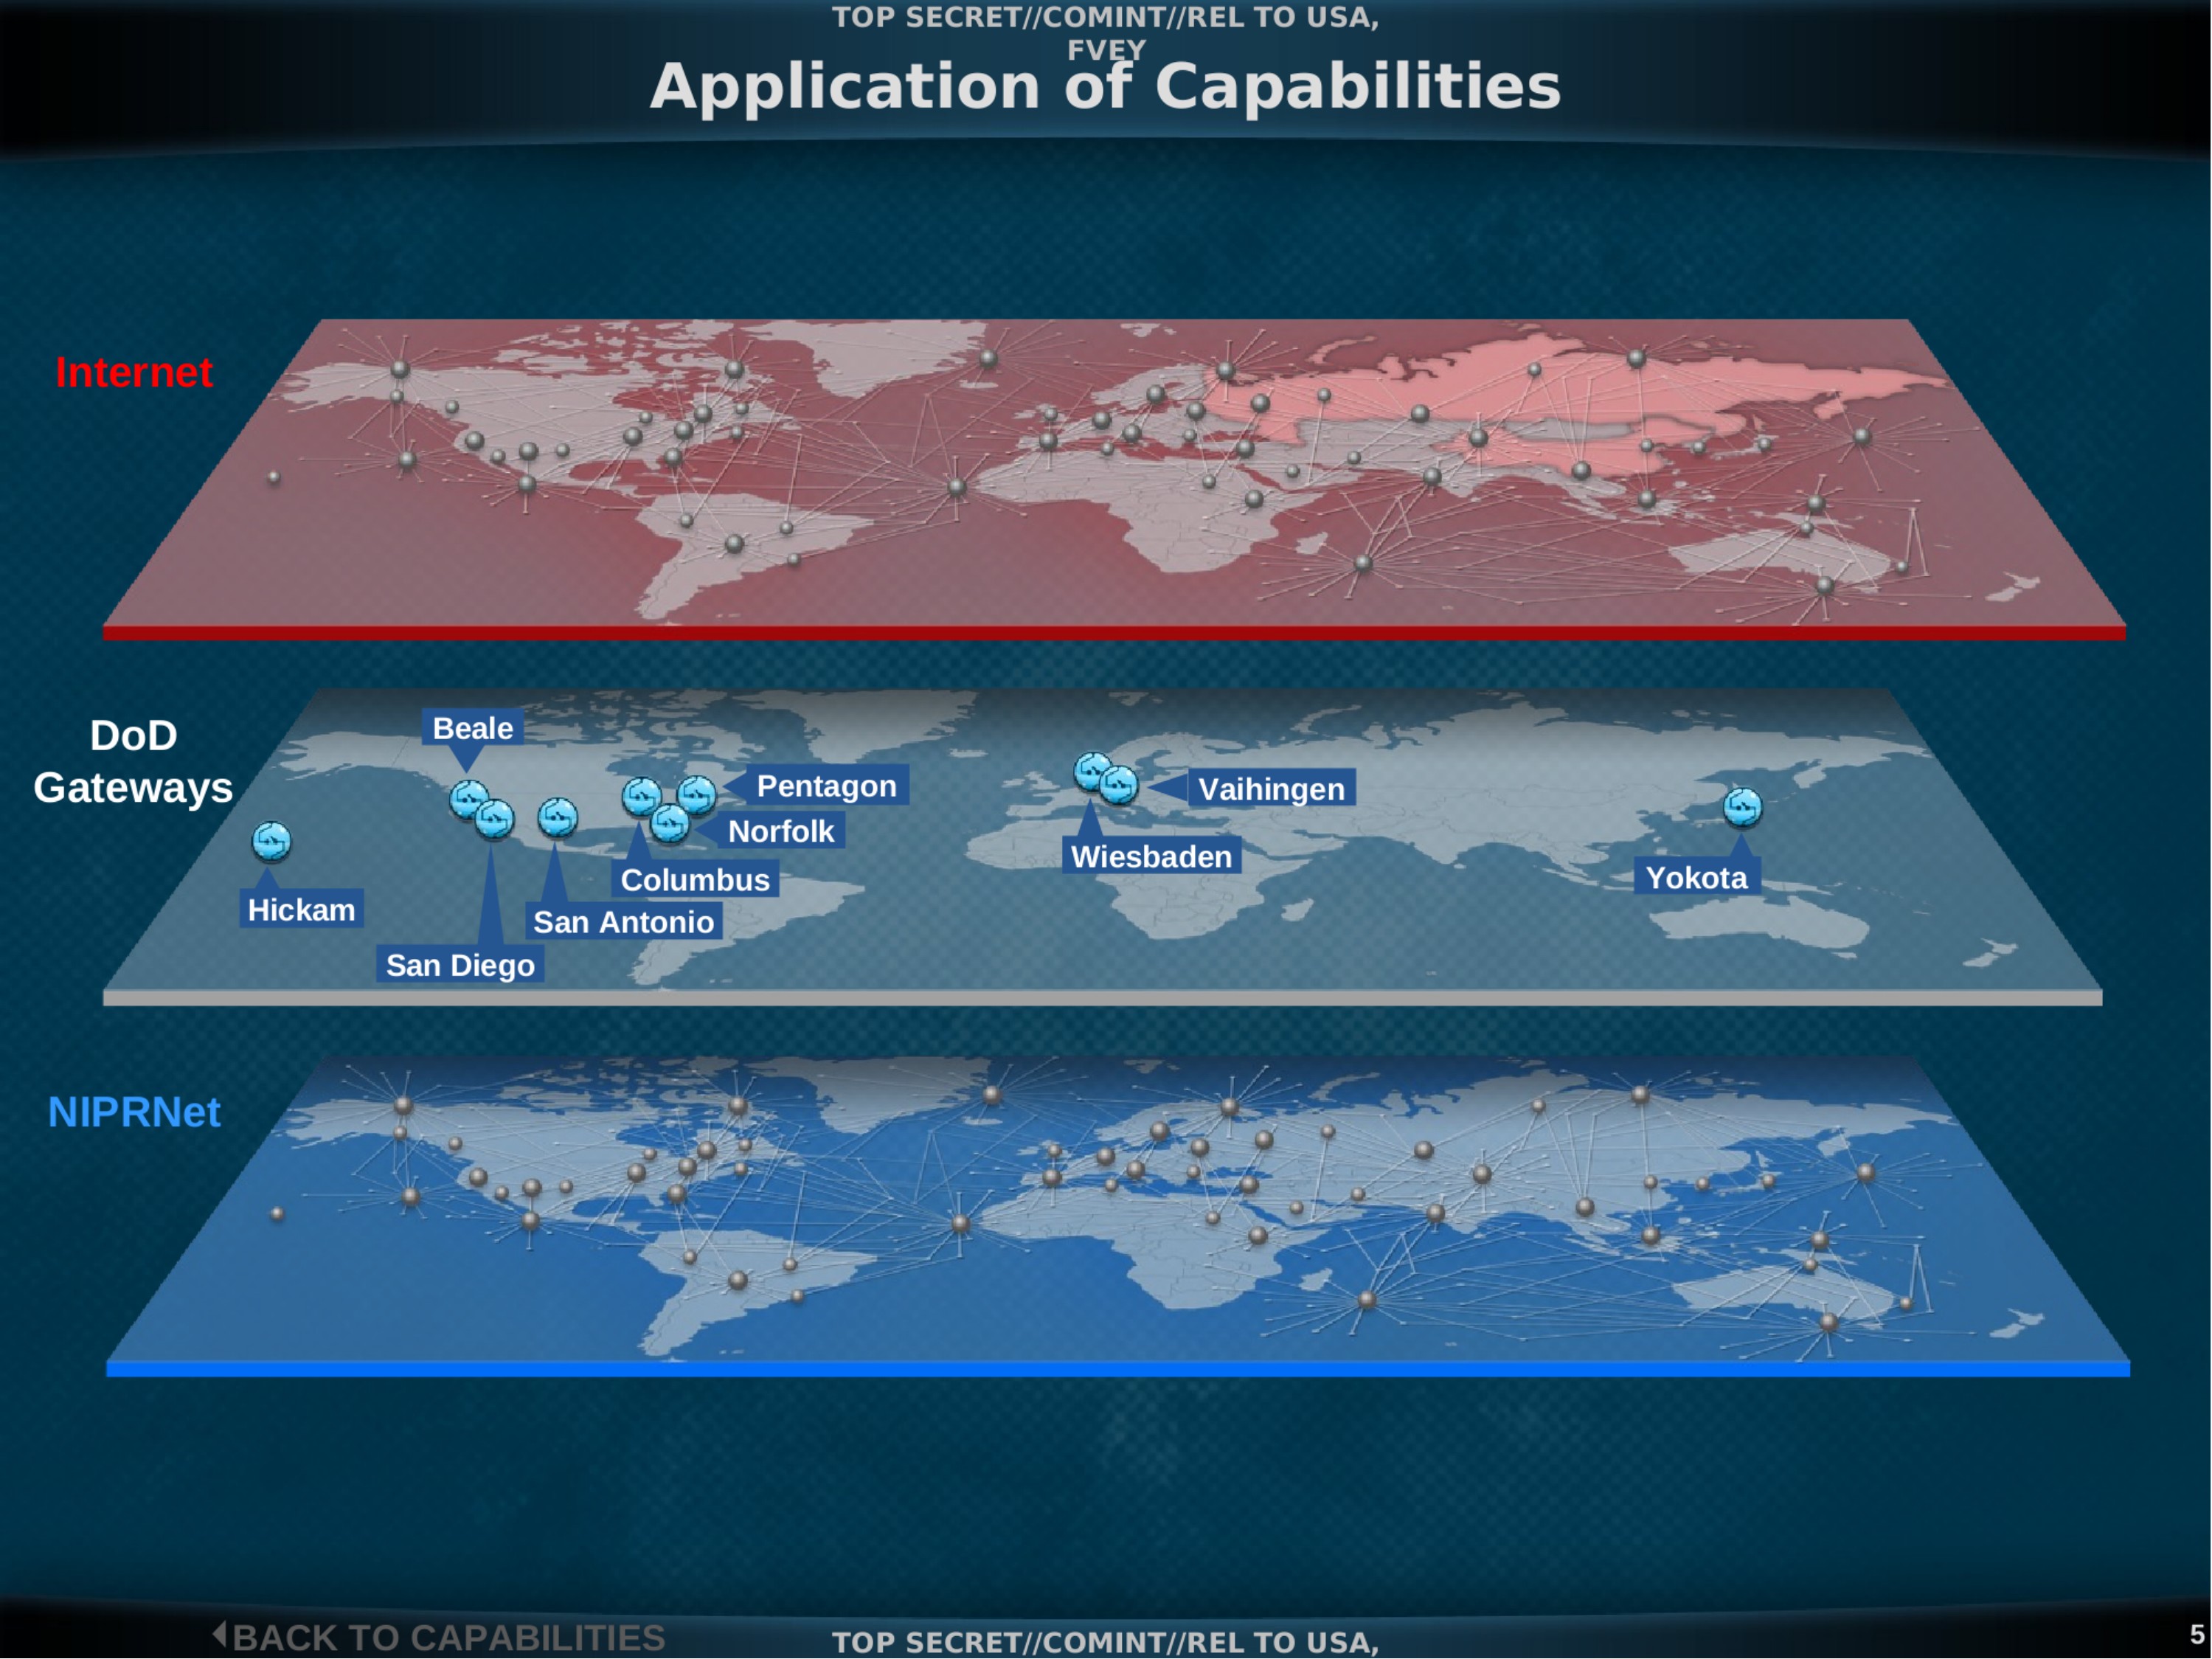
Application of Capabilities
Internet
DoD Gateways
- Beale
- Pentagon
- Norfolk
- Columbus
- San Antonio
- Hickam
- San Diego
- Vaihingen
- Wiesbaden
- Yokota
NIPRNet
BACK TO CAPABILITIES
TOP SECRET//COMINT//REL TO USA,
5
SECRET//COMINT//REL TO USA, FVEY
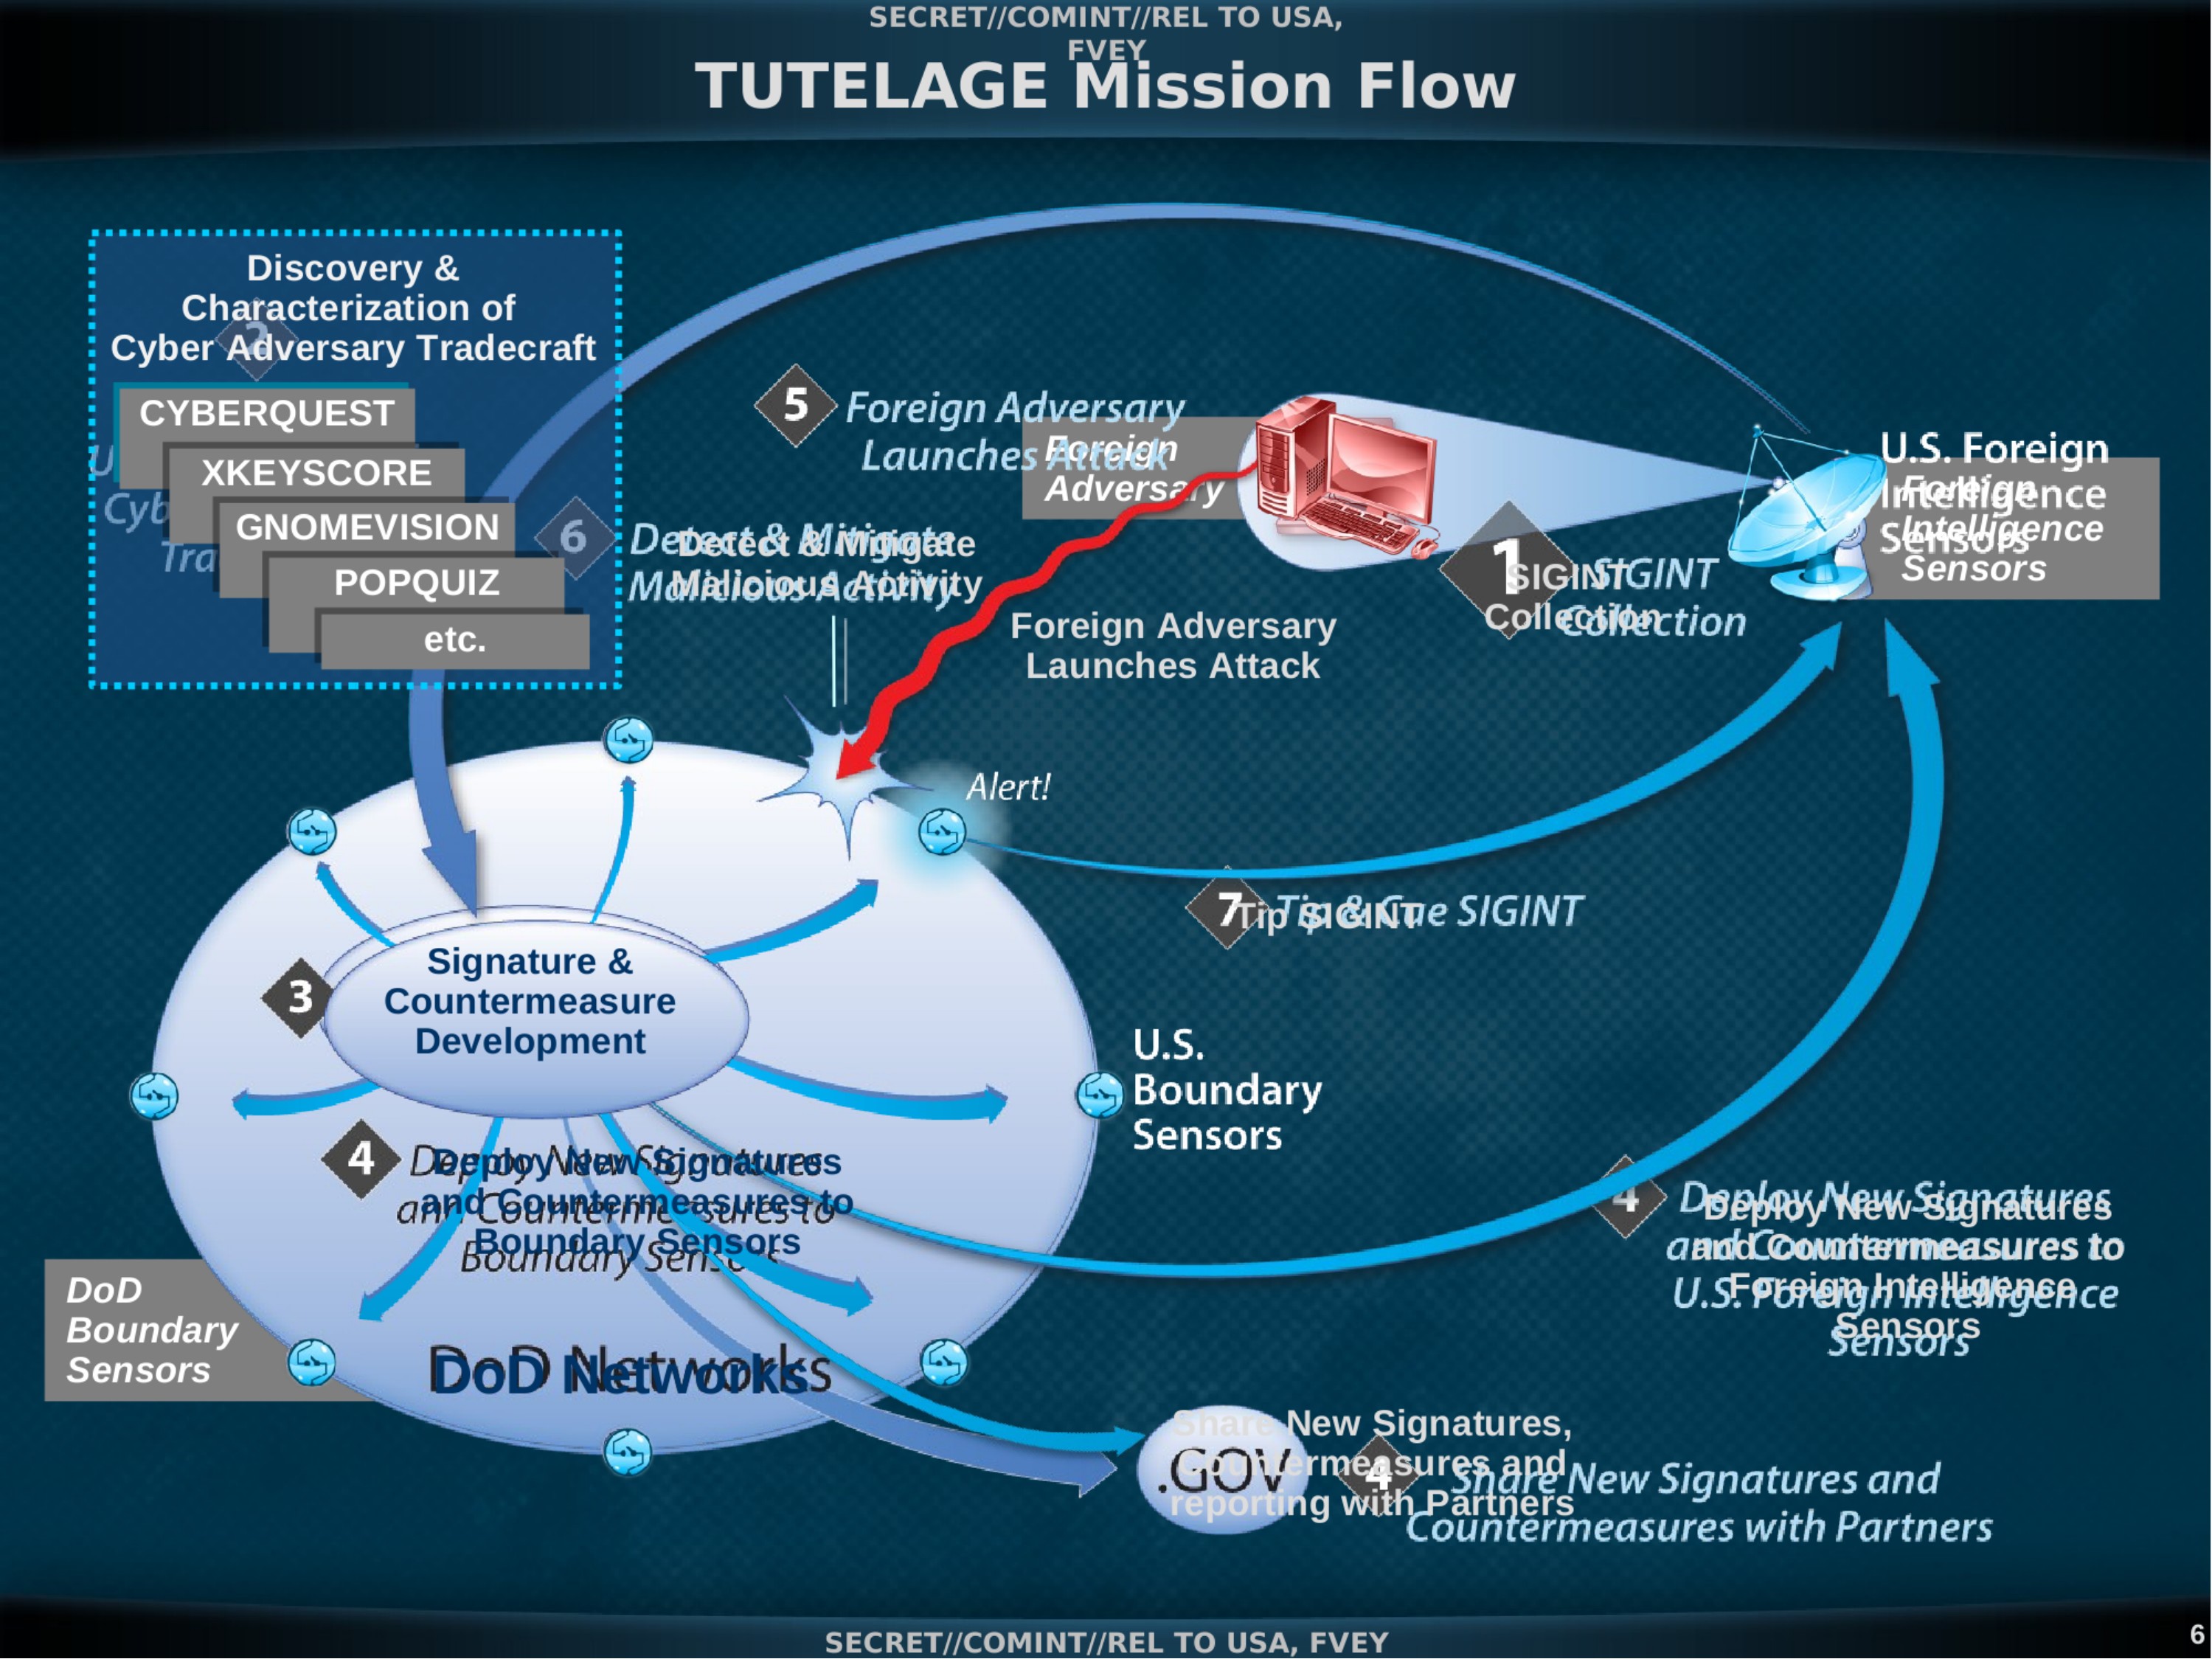
TUTELAGE Mission Flow
Discovery & Characterization of Cyber Adversary Tradecraft
- CYBERQUEST
- XKEYSCORE
- GNOMEVISION
- POPQUIZ
- etc.
- SIGINT Collection
- Signature & Countermeasure Development
- Deploy New Signatures and Countermeasures to Boundary Sensors
- Share New Signatures, Countermeasures and reporting with Partners
- Deploy New Signatures and Countermeasures to Foreign Intelligence Sensors
- Foreign Adversary Launches Attack
- Detect & Mitigate Malicious Activity
- Tip & Cue SIGINT
Foreign Adversary
Alert!
DoD Networks
DoD Boundary Sensors
U.S. Foreign Intelligence Sensors
U.S. Boundary Sensors
.GOV
- Foreign Adversary Launches Foreign Adversary
- Detect & Mitigate Malicious Activity
- Foreign Adversary Launches Attack
- SIGINT Collection
- U.S. Foreign Intelligence Sensors
- Alert!
- Tips & New SIGINT
- Signature & Countermeasure Development
- Deploy New Signatures and Countermeasures to Boundary Sensors
- DoD Boundary Sensors
- DoD Networks
- U.S. Boundary Sensors
- Share New Signatures, measures and New Signatures and Countermeasures with Partners
- Deploy New Signatures and Countermeasures to U.S. Foreign Intelligence Sensors
- GOV reporting with Partners
SECRET//COMINT//REL TO USA, FVEY
6
UNCLASSIFIED//FOUO
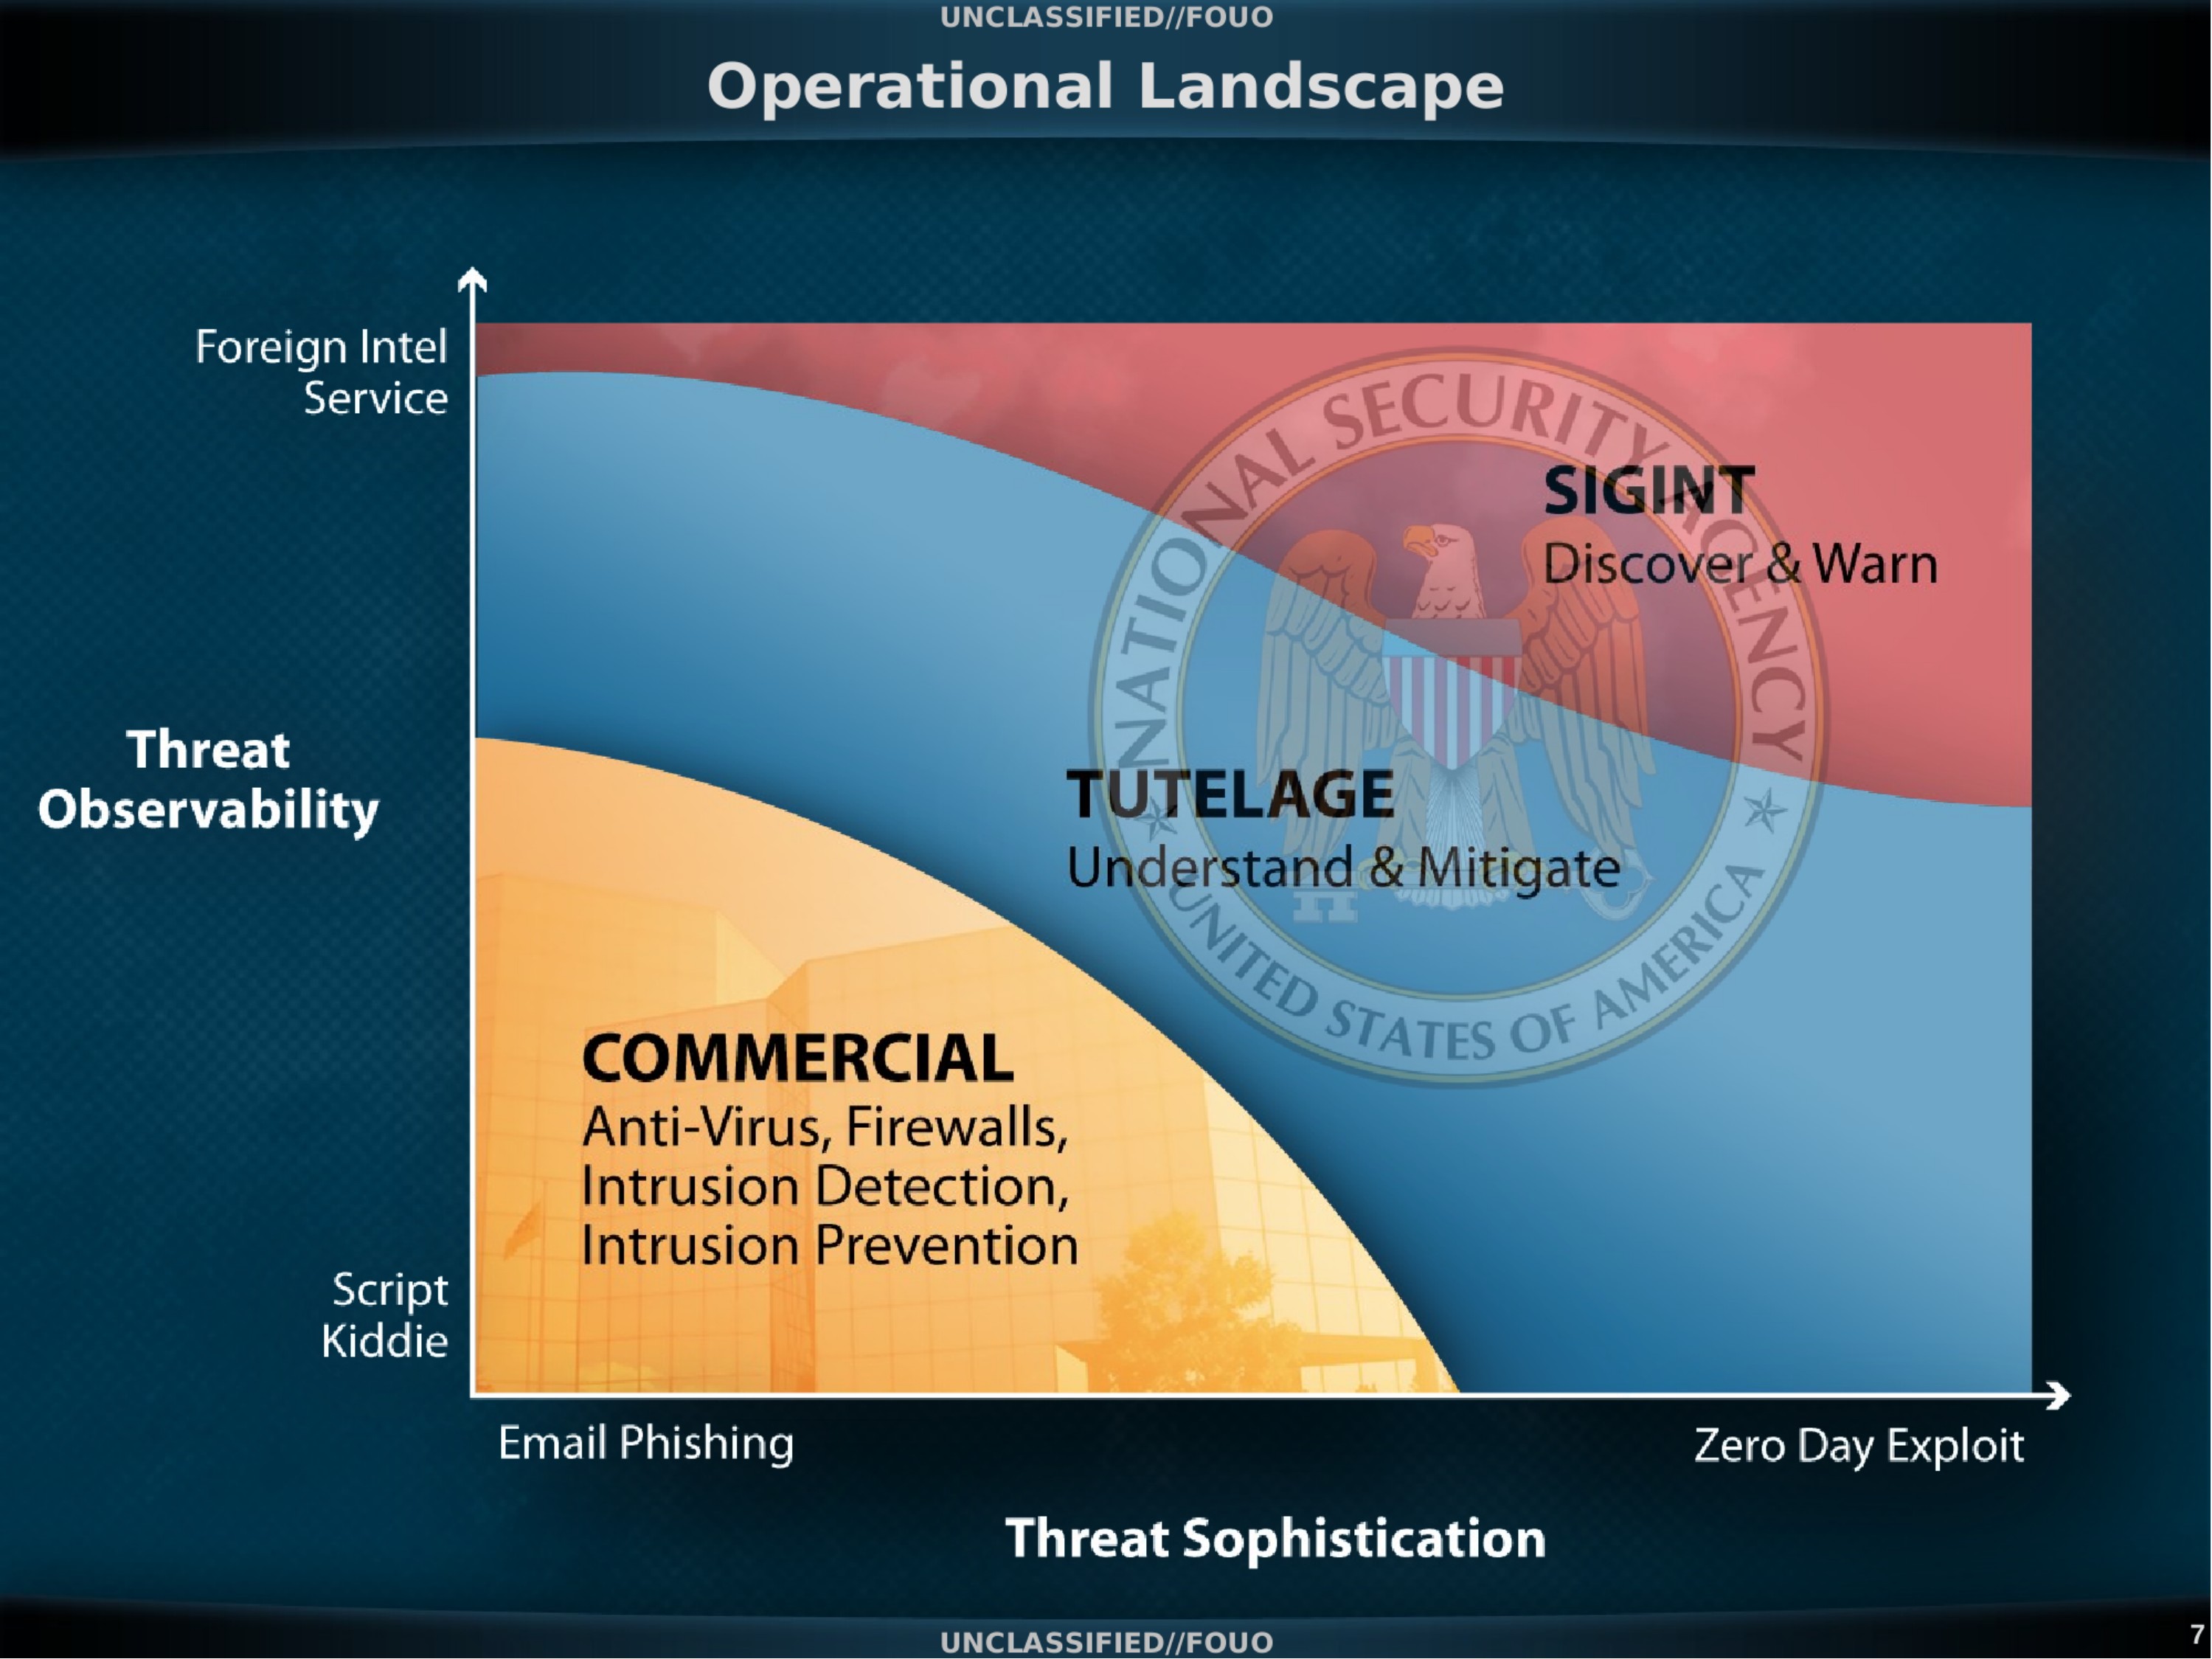
Operational Landscape
Foreign Intel Service
Threat Observability
Script Kiddie
- SIGINT
- Discover & Warn
- TUTELAGE
- Understand & Mitigate
- COMMERCIAL
- Anti-Virus, Firewalls, Intrusion Detection, Intrusion Prevention
Email Phishing
Zero Day Exploit
Threat Sophistication
UNCLASSIFIED//FOUO
7
SECRET//COMINT//REL TO USA, FVEY
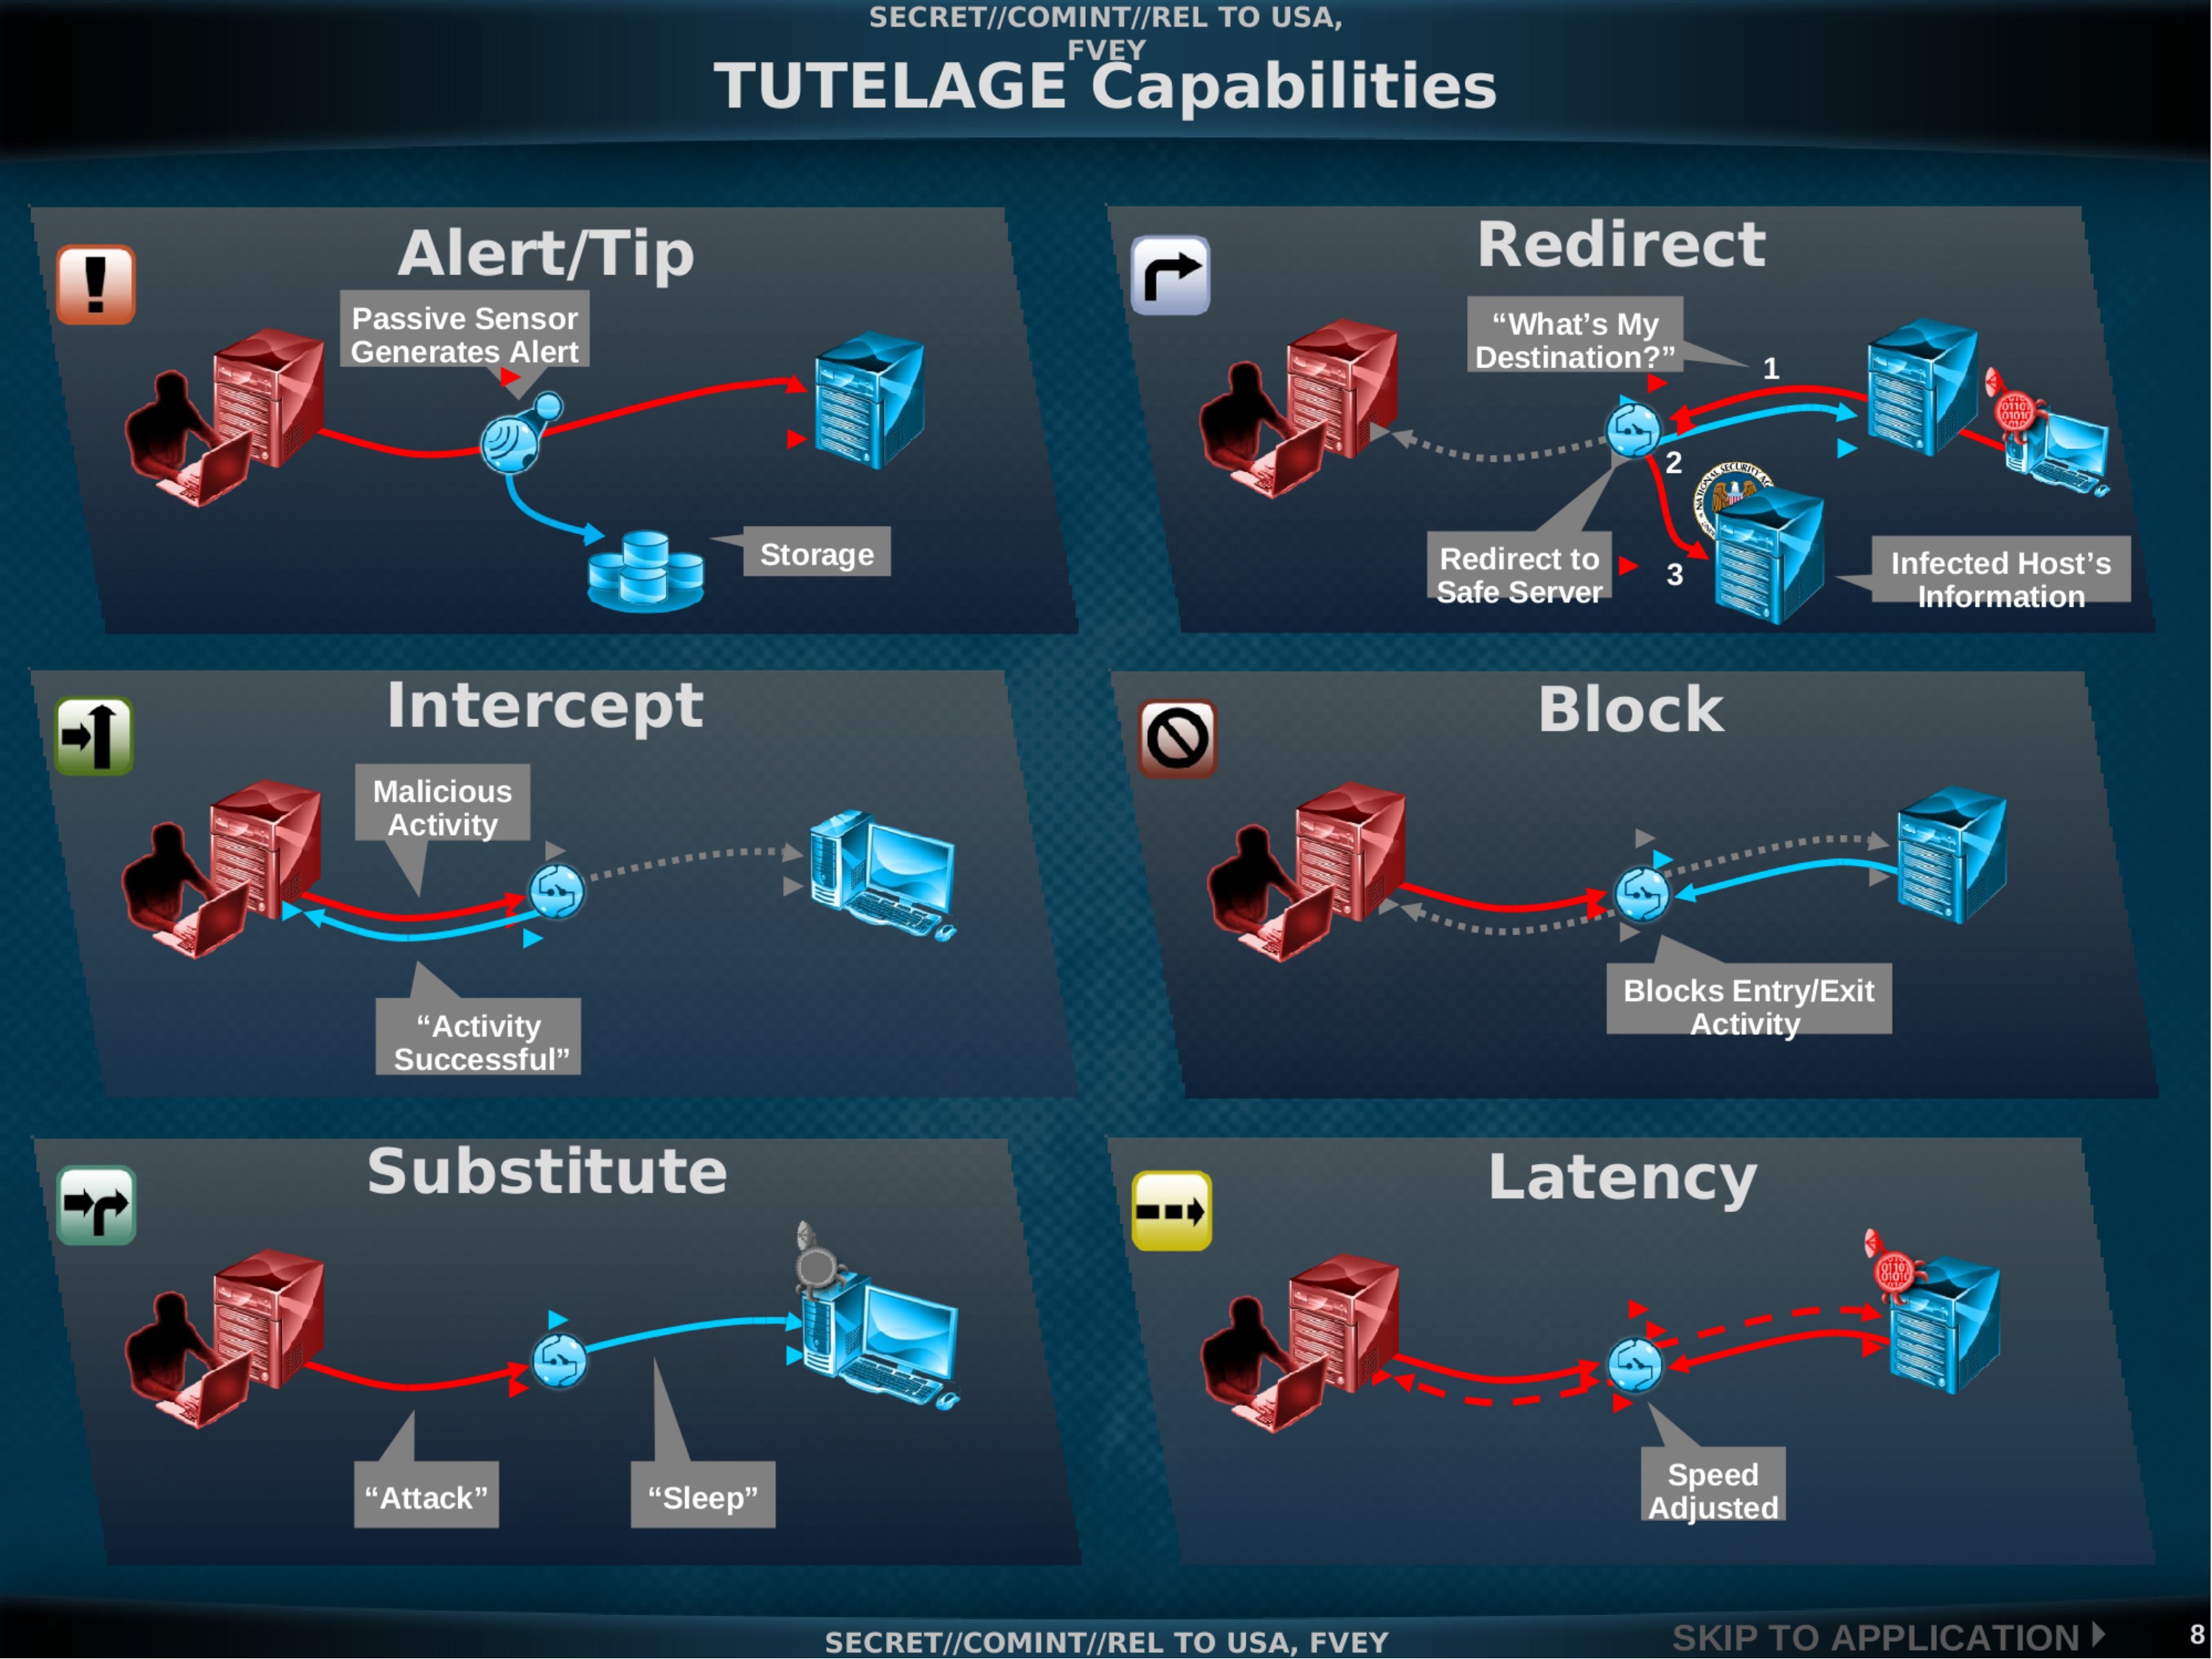
TUTELAGE Capabilities
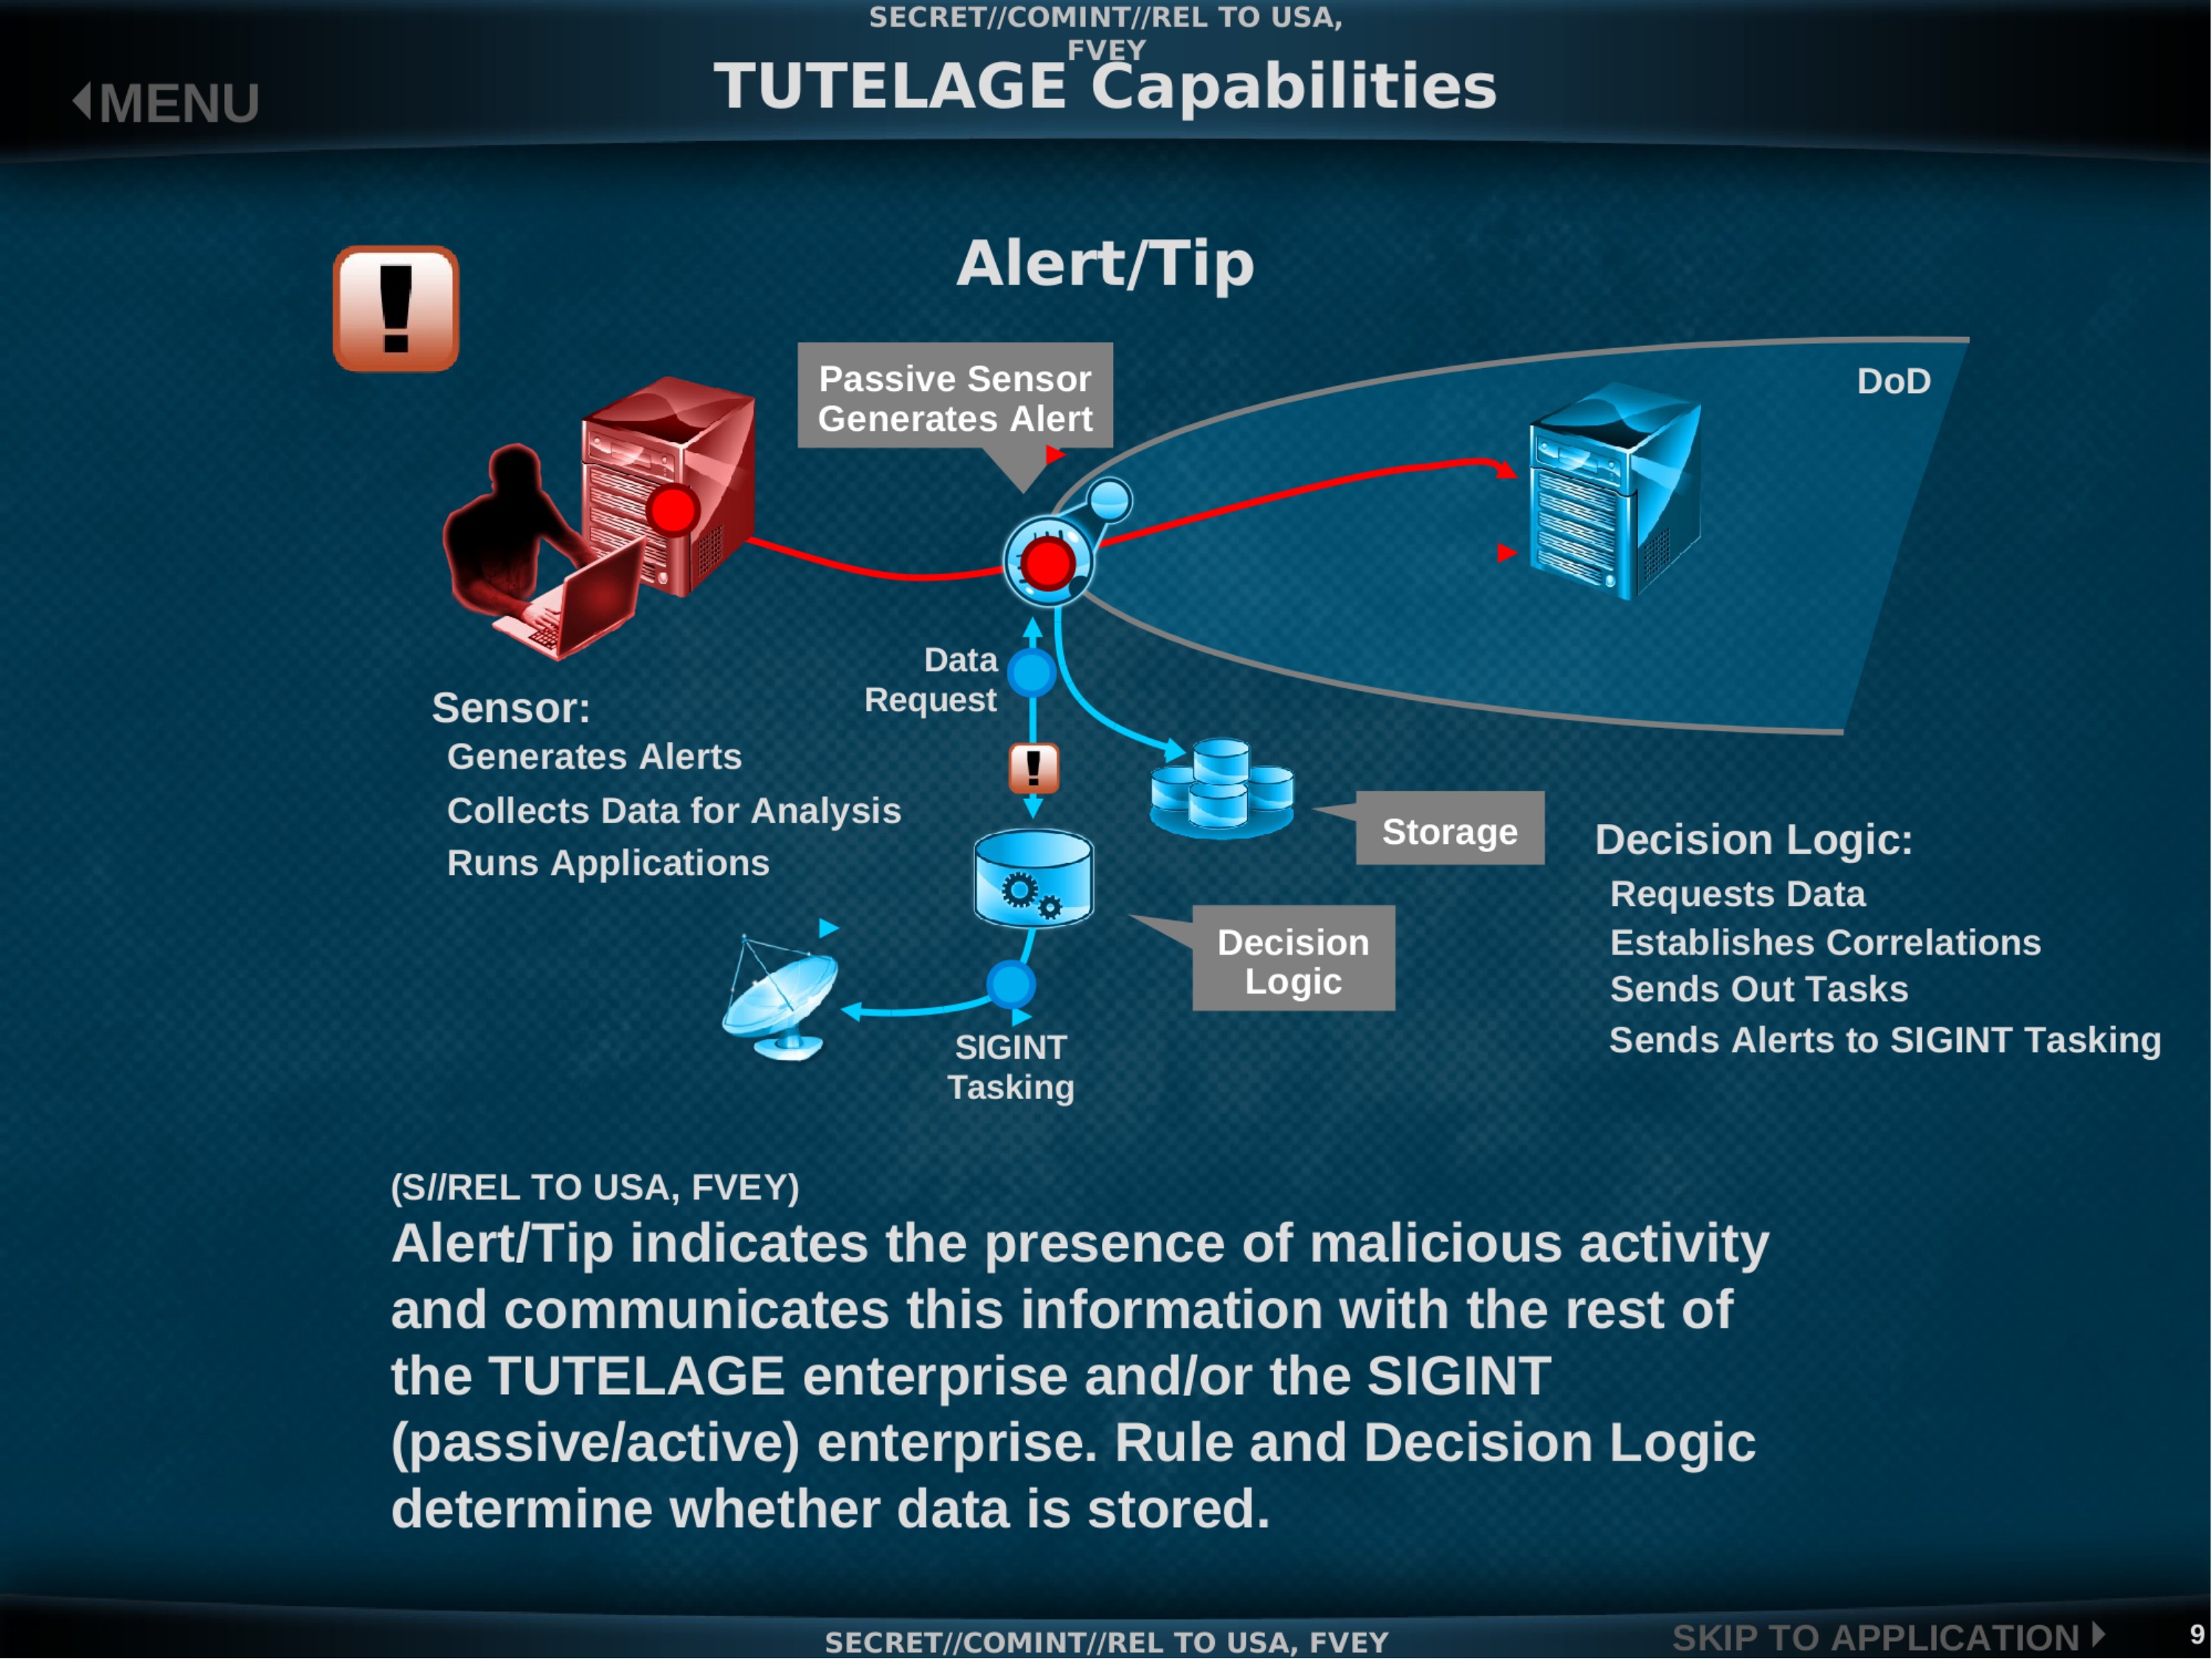
Alert/Tip
- Passive Sensor Generates Alert
- Storage
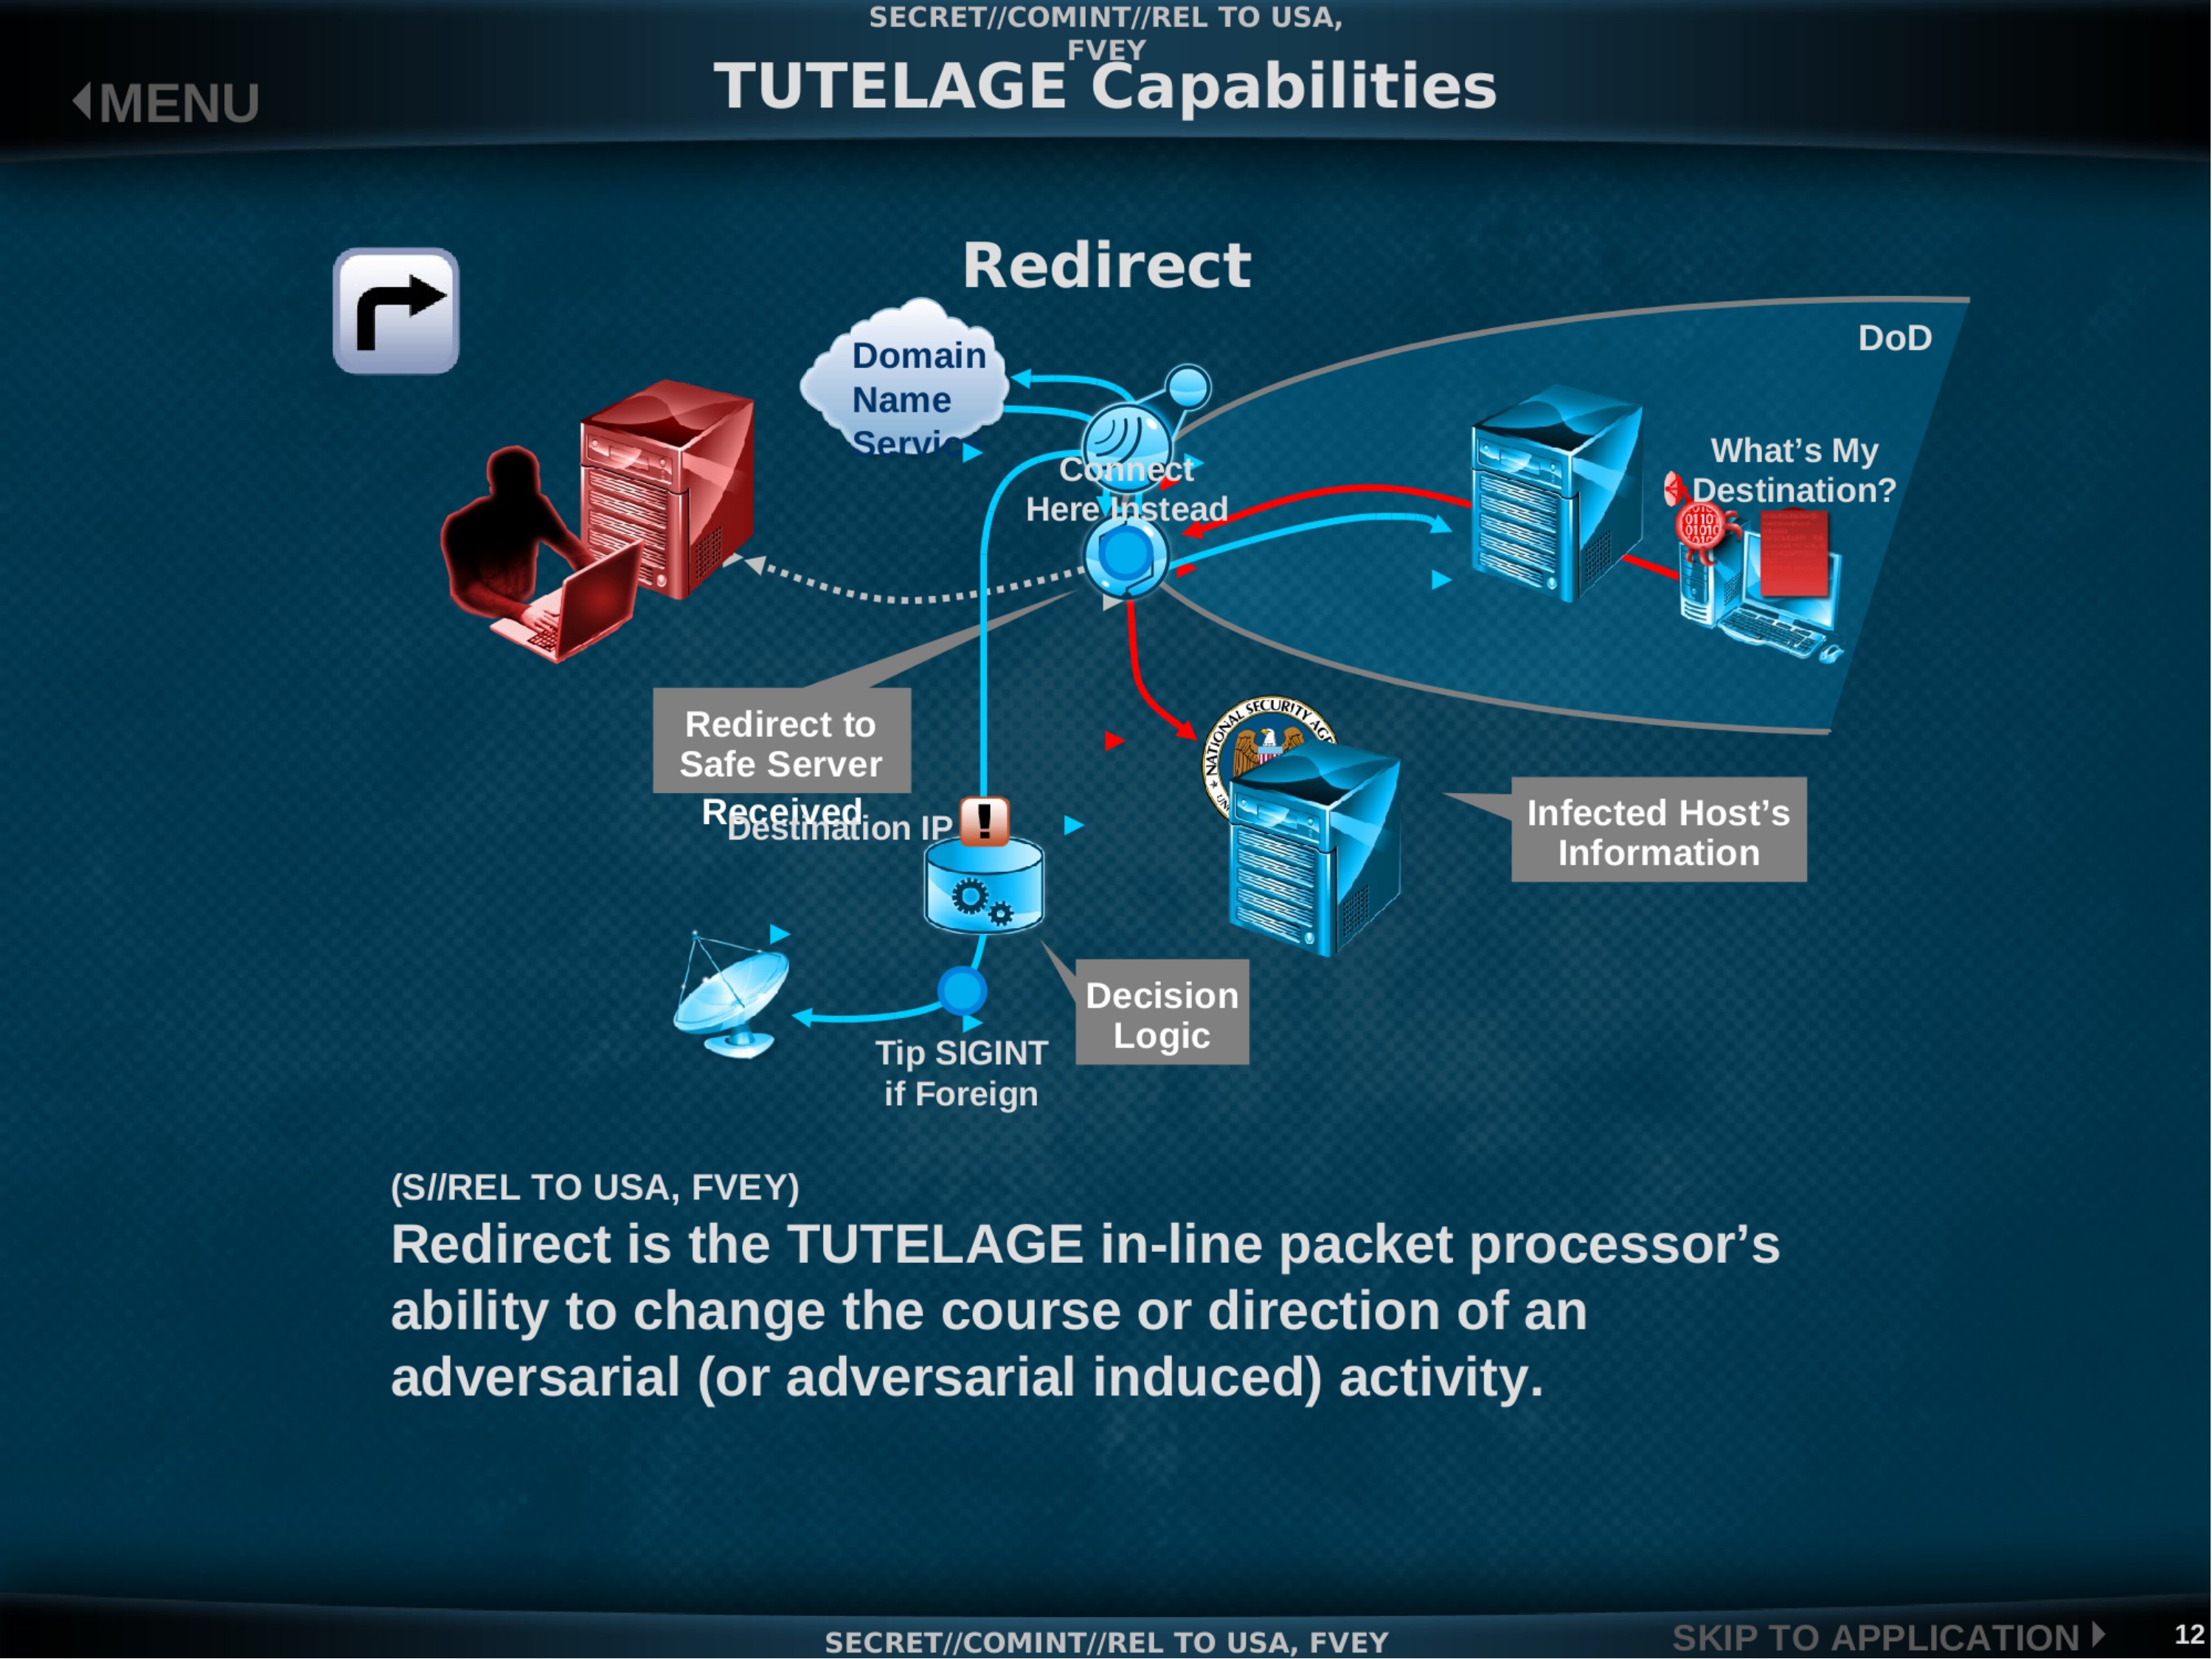
Redirect
- "What's My Destination?"
- Redirect to Safe Server
- Infected Host's Information
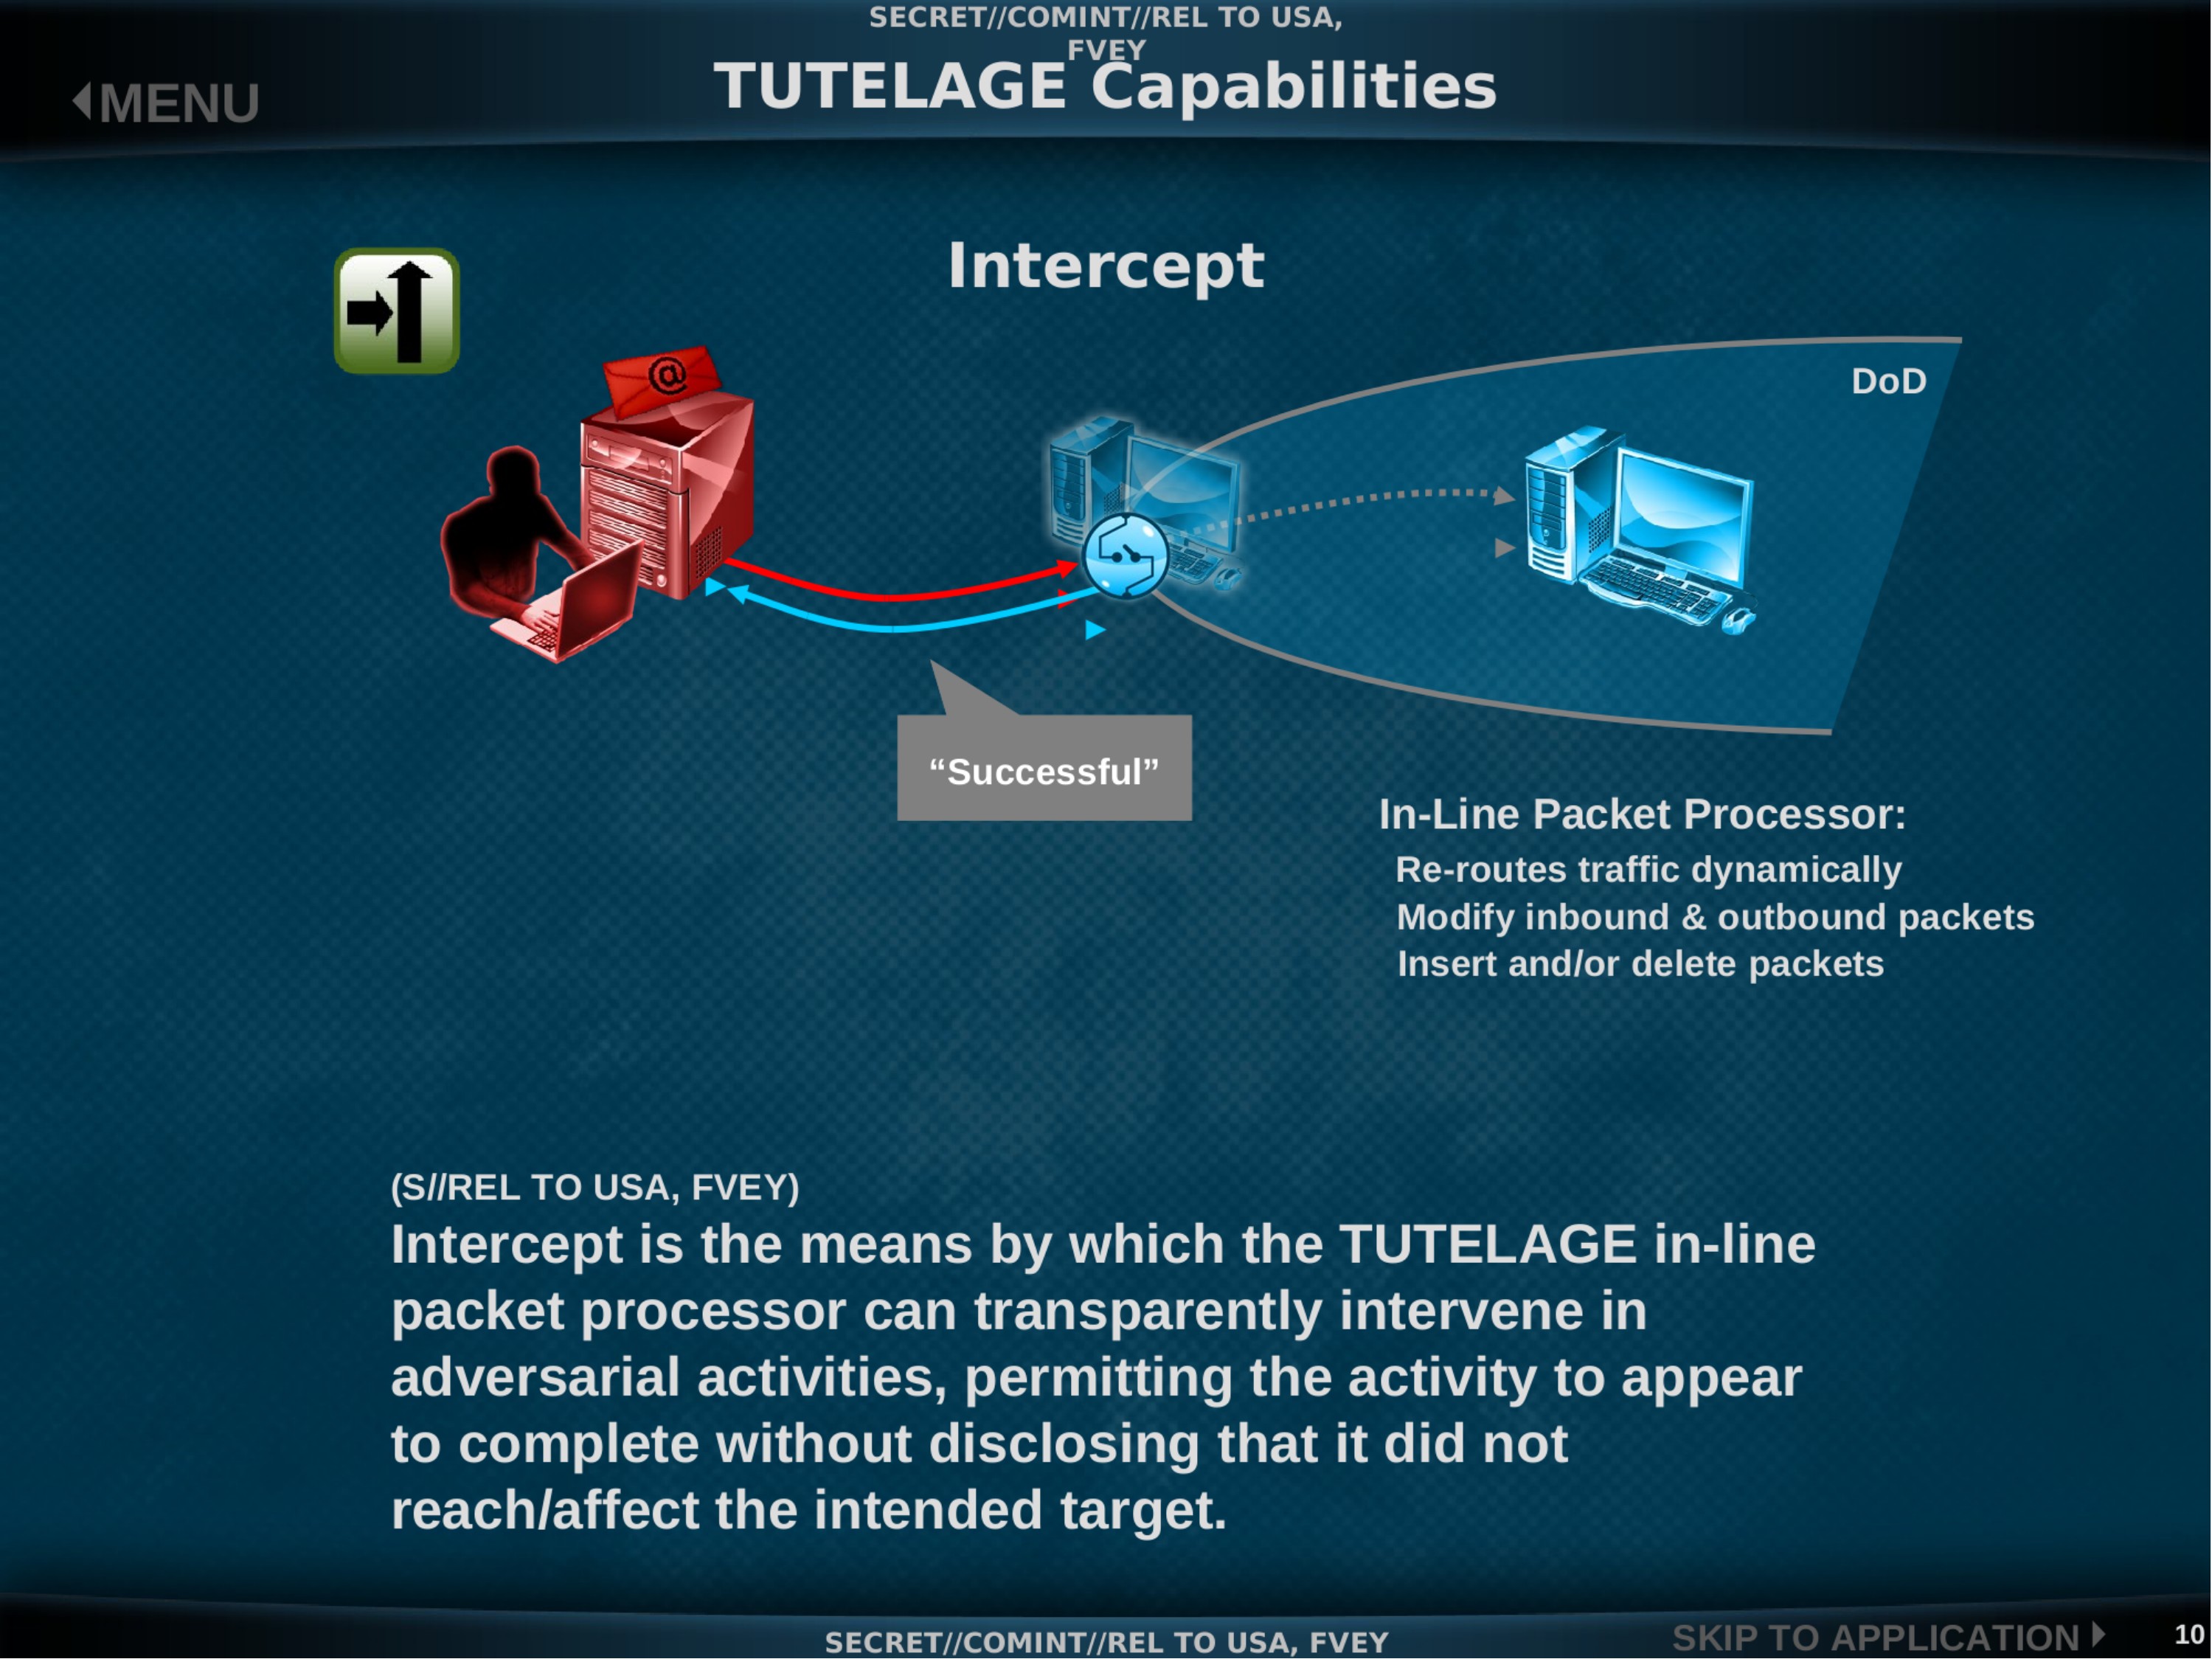
Intercept
- Malicious Activity
- "Activity Successful"
Block
- Blocks Entry/Exit Activity
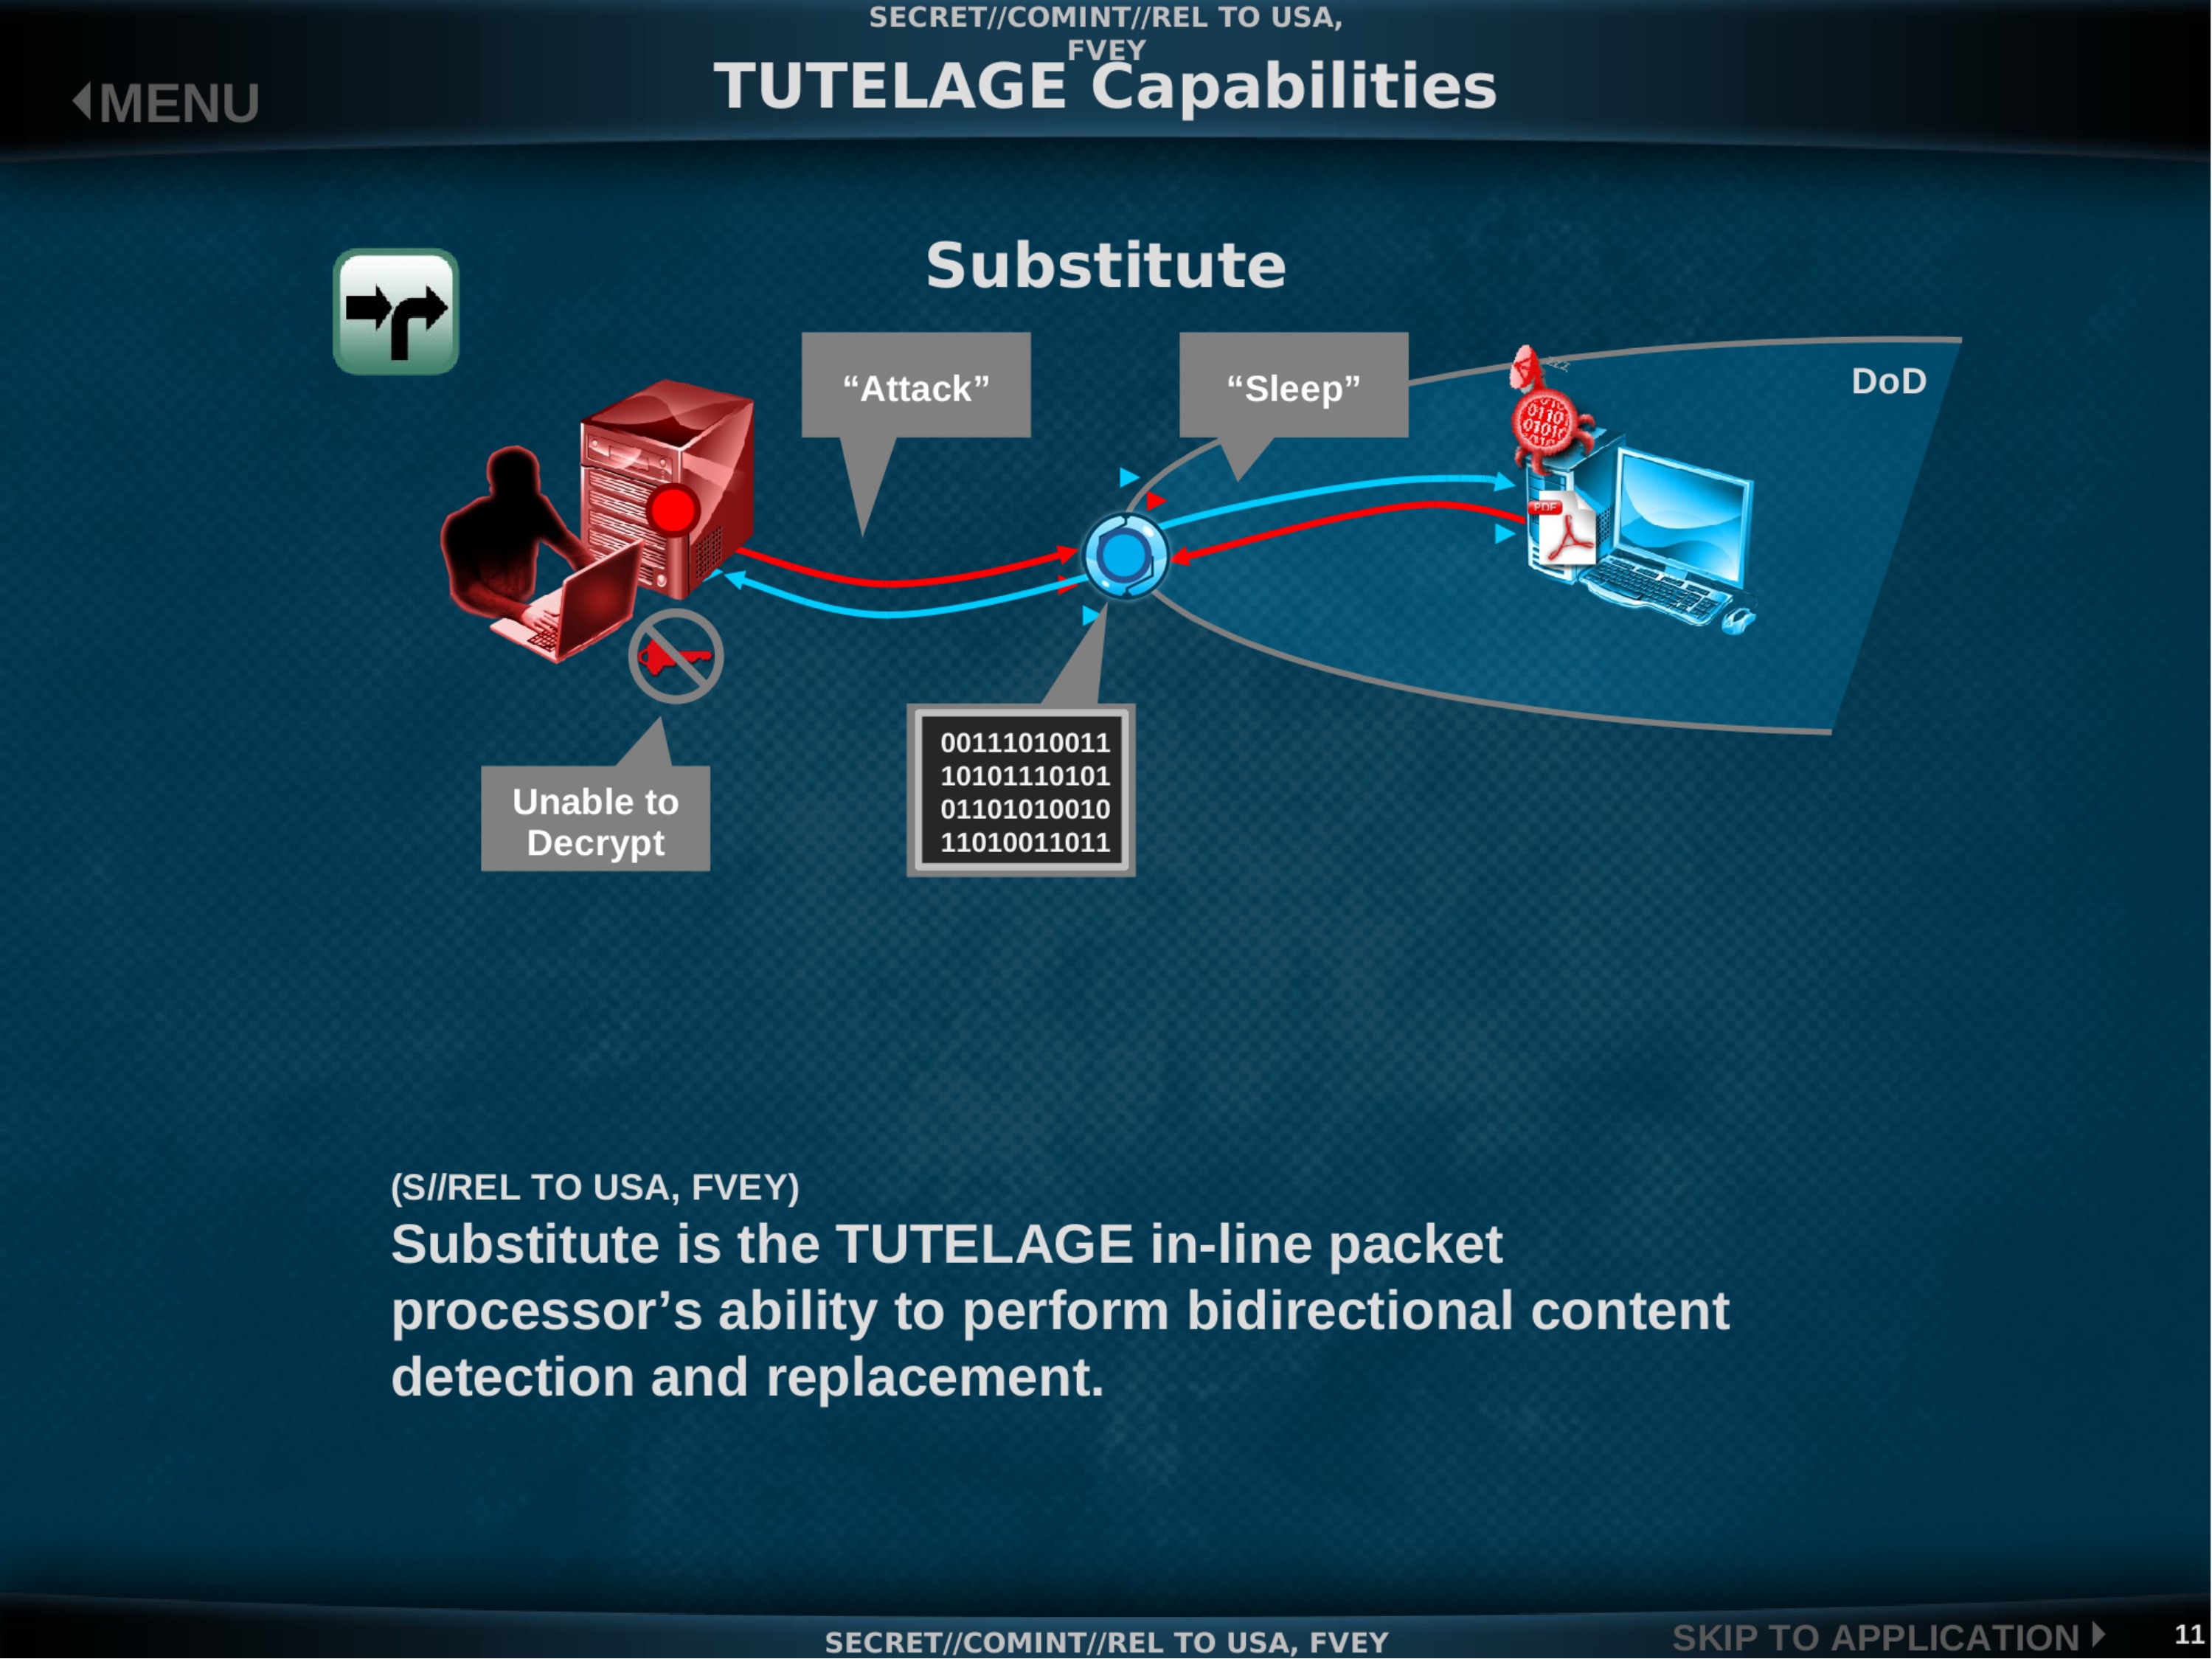
Substitute
- "Attack"
- "Sleep"
Latency
- Speed Adjusted
SKIP TO APPLICATION
SECRET//COMINT//REL TO USA, FVEY
8
SECRET//COMINT//REL TO USA, FVEY
TUTELAGE Capabilities
MENU
Alert/Tip
- Passive Sensor Generates Alert
- Sensor:
- Generates Alerts
- Collects Data for Analysis
- Runs Applications
- Data Request
- Storage
- Decision Logic
- SIGINT Tasking
- Decision Logic:
- Requests Data
- Establishes Correlations
- Sends Out Tasks
- Sends Alerts to SIGINT Tasking
- DoD
(S//REL TO USA, FVEY)
Alert/Tip indicates the presence of malicious activity and communicates this information with the rest of the TUTELAGE enterprise and/or the SIGINT (passive/active) enterprise. Rule and Decision Logic determine whether data is stored.
SKIP TO APPLICATION
SECRET//COMINT//REL TO USA, FVEY
9
SECRET//COMINT//REL TO USA, FVEY
TUTELAGE Capabilities
MENU
Intercept
- DoD
- "Successful"
- In-Line Packet Processor:
- Re-routes traffic dynamically
- Modify inbound & outbound packets
- Insert and/or delete packets
(S//REL TO USA, FVEY)
Intercept is the means by which the TUTELAGE in-line packet processor can transparently intervene in adversarial activities, permitting the activity to appear to complete without disclosing that it did not reach/affect the intended target.
SKIP TO APPLICATION
SECRET//COMINT//REL TO USA, FVEY
10
SECRET//COMINT//REL TO USA, FVEY
TUTELAGE Capabilities
MENU
Substitute
- "Attack"
- "Sleep"
- Unable to Decrypt
- 00111010011101011101010110101001011010011011
- DoD
(S//REL TO USA, FVEY)
Substitute is the TUTELAGE in-line packet processor's ability to perform bidirectional content detection and replacement.
SKIP TO APPLICATION
SECRET//COMINT//REL TO USA, FVEY
11
SECRET//COMINT//REL TO USA, FVEY
TUTELAGE Capabilities
MENU
Redirect
Domain Name Servi
Connect Here Instead
Redirect to Safe Server
Received Destination IP
What's My Destination?
Infected Host's Information
Tip SIGINT if Foreign
Decision Logic
DoD
(S//REL TO USA, FVEY)
Redirect is the TUTELAGE in-line packet processor's ability to change the course or direction of an adversarial (or adversarial induced) activity.
SKIP TO APPLICATION
SECRET//COMINT//REL TO USA, FVEY
12
SECRET//COMINT//REL TO USA, FVEY
TUTELAGE Capabilities
MENU
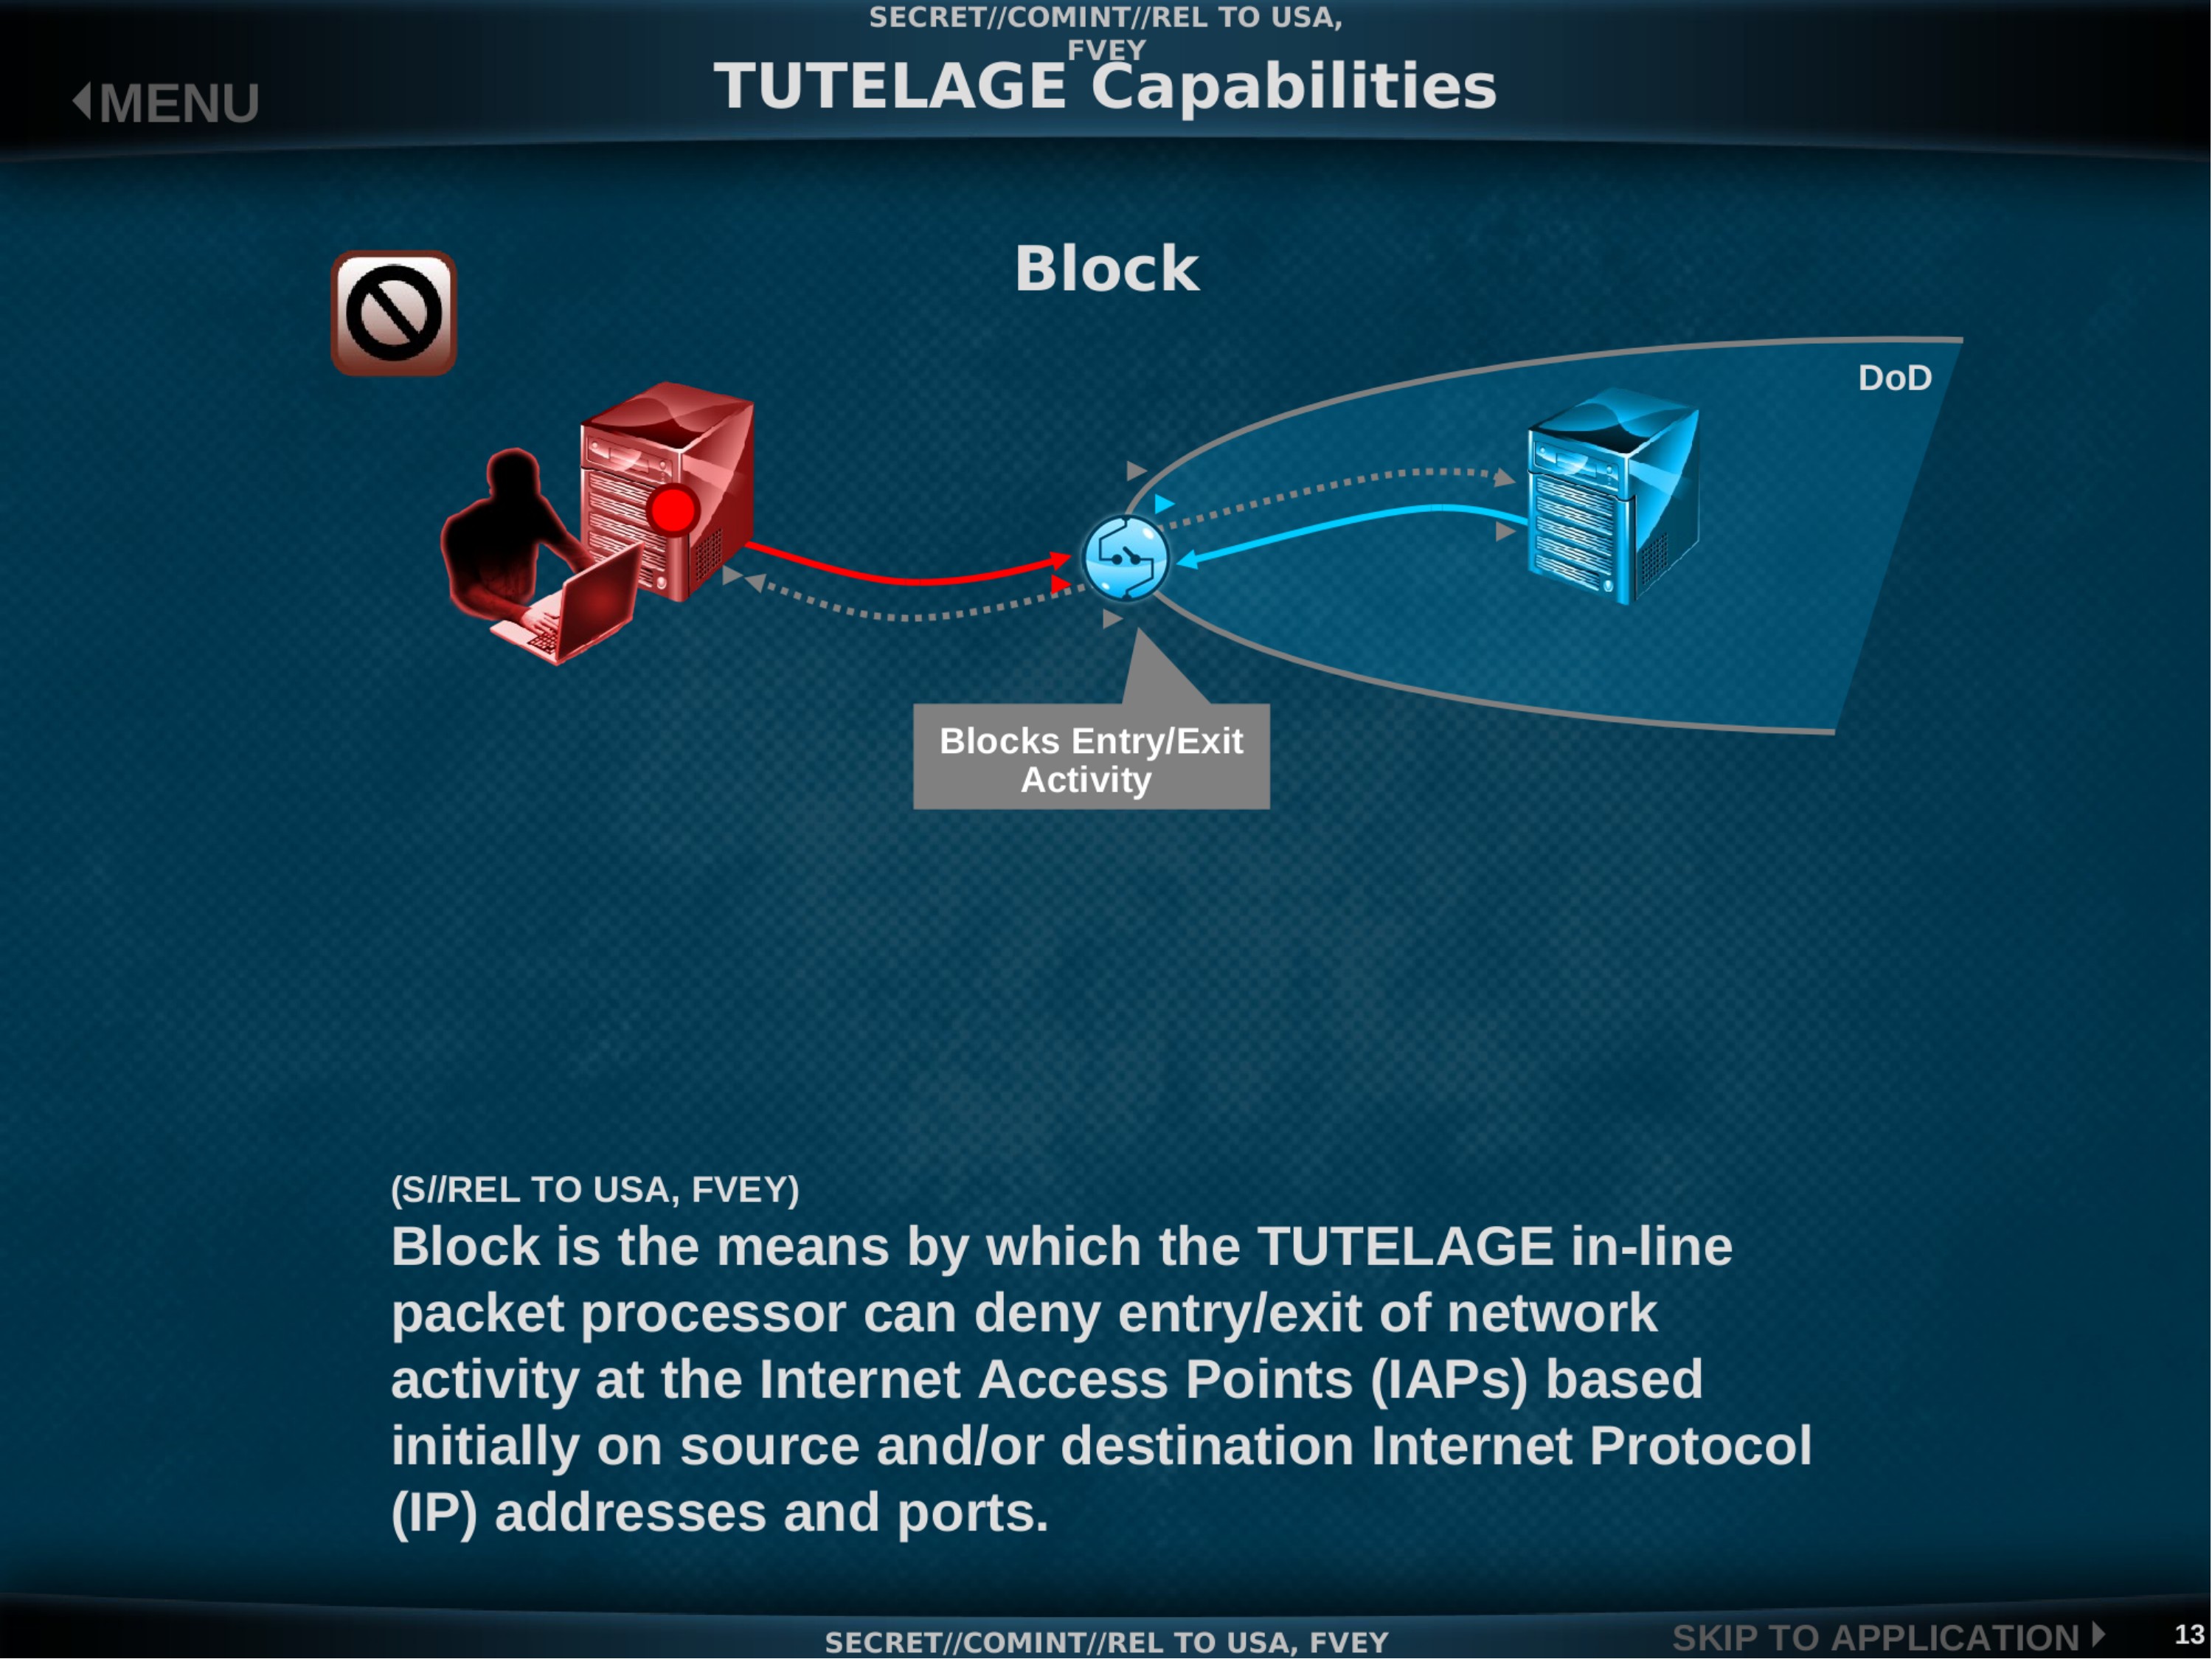
Block
- Blocks Entry/Exit Activity
- DoD
(S//REL TO USA, FVEY)
Block is the means by which the TUTELAGE in-line packet processor can deny entry/exit of network activity at the Internet Access Points (IAPs) based initially on source and/or destination Internet Protocol (IP) addresses and ports.
SKIP TO APPLICATION
SECRET//COMINT//REL TO USA, FVEY
13
SECRET//COMINT//REL TO USA, FVEY
TUTELAGE Capabilities
MENU
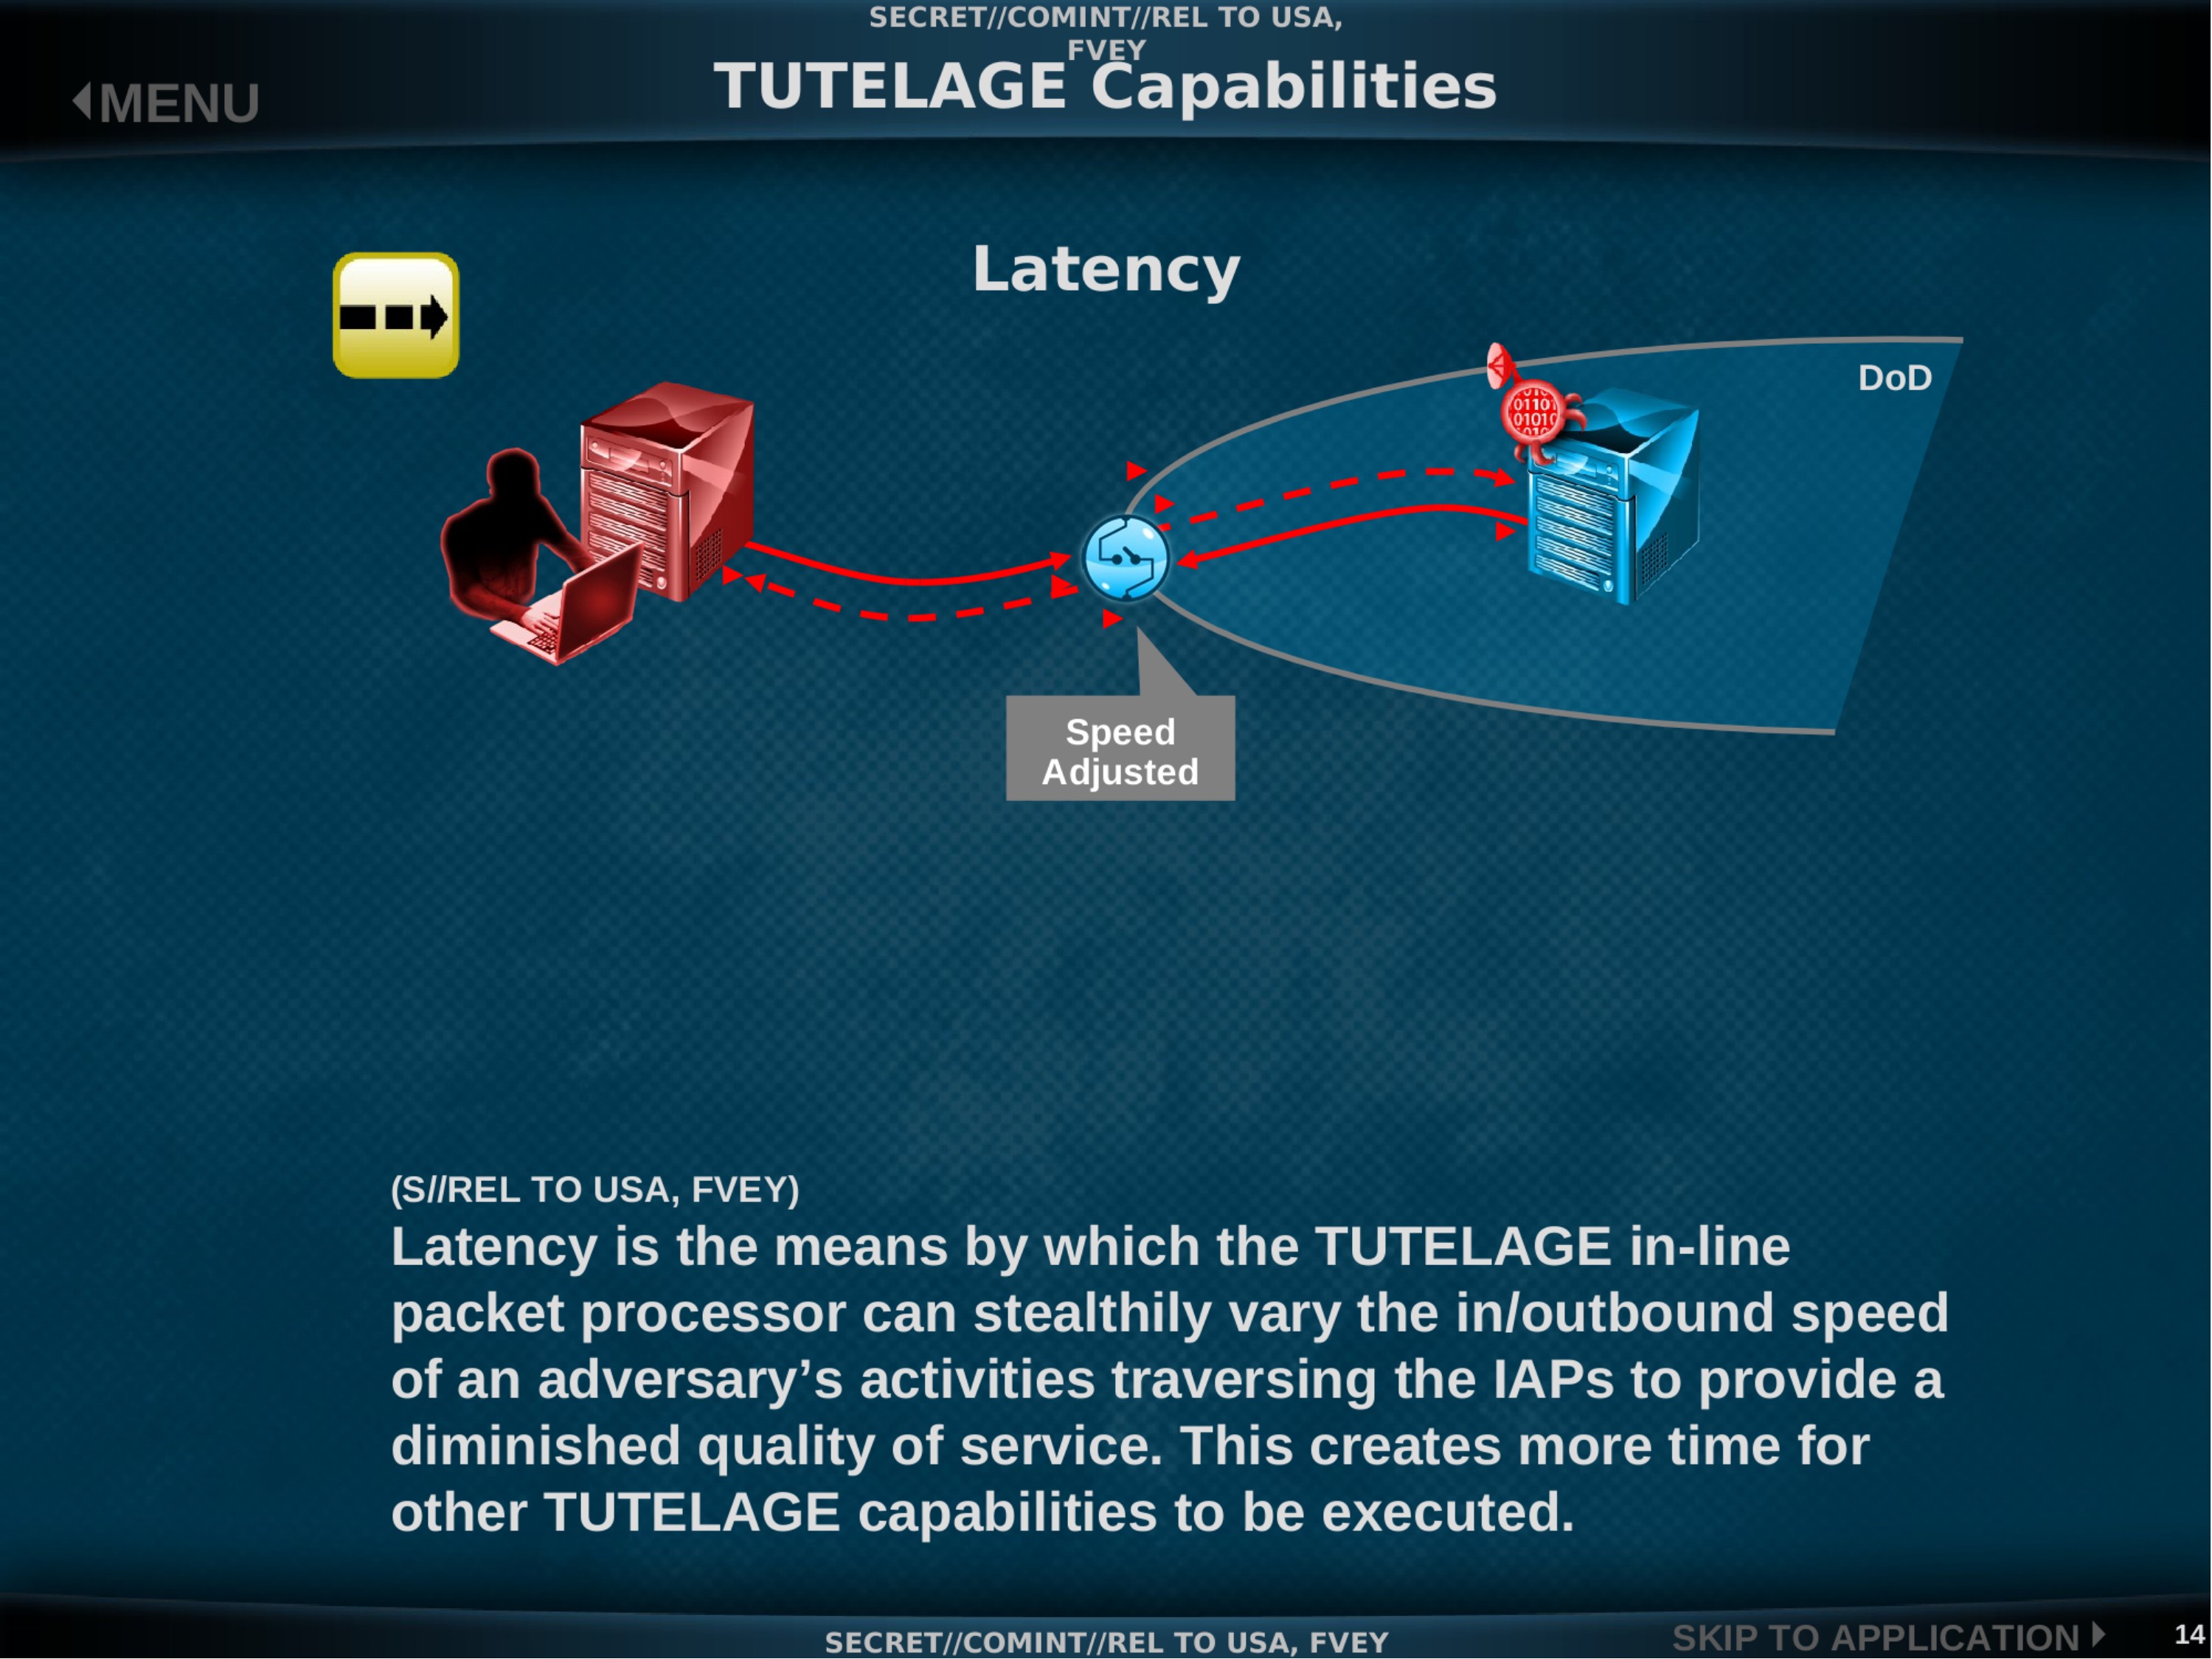
Latency
- Speed Adjusted
- DoD
(S//REL TO USA, FVEY)
Latency is the means by which the TUTELAGE in-line packet processor can stealthily vary the in/outbound speed of an adversary's activities traversing the IAPs to provide a diminished quality of service. This creates more time for other TUTELAGE capabilities to be executed.
SKIP TO APPLICATION
SECRET//COMINT//REL TO USA, FVEY
14
TOP SECRET//COMINT//REL TO USA, FVEY
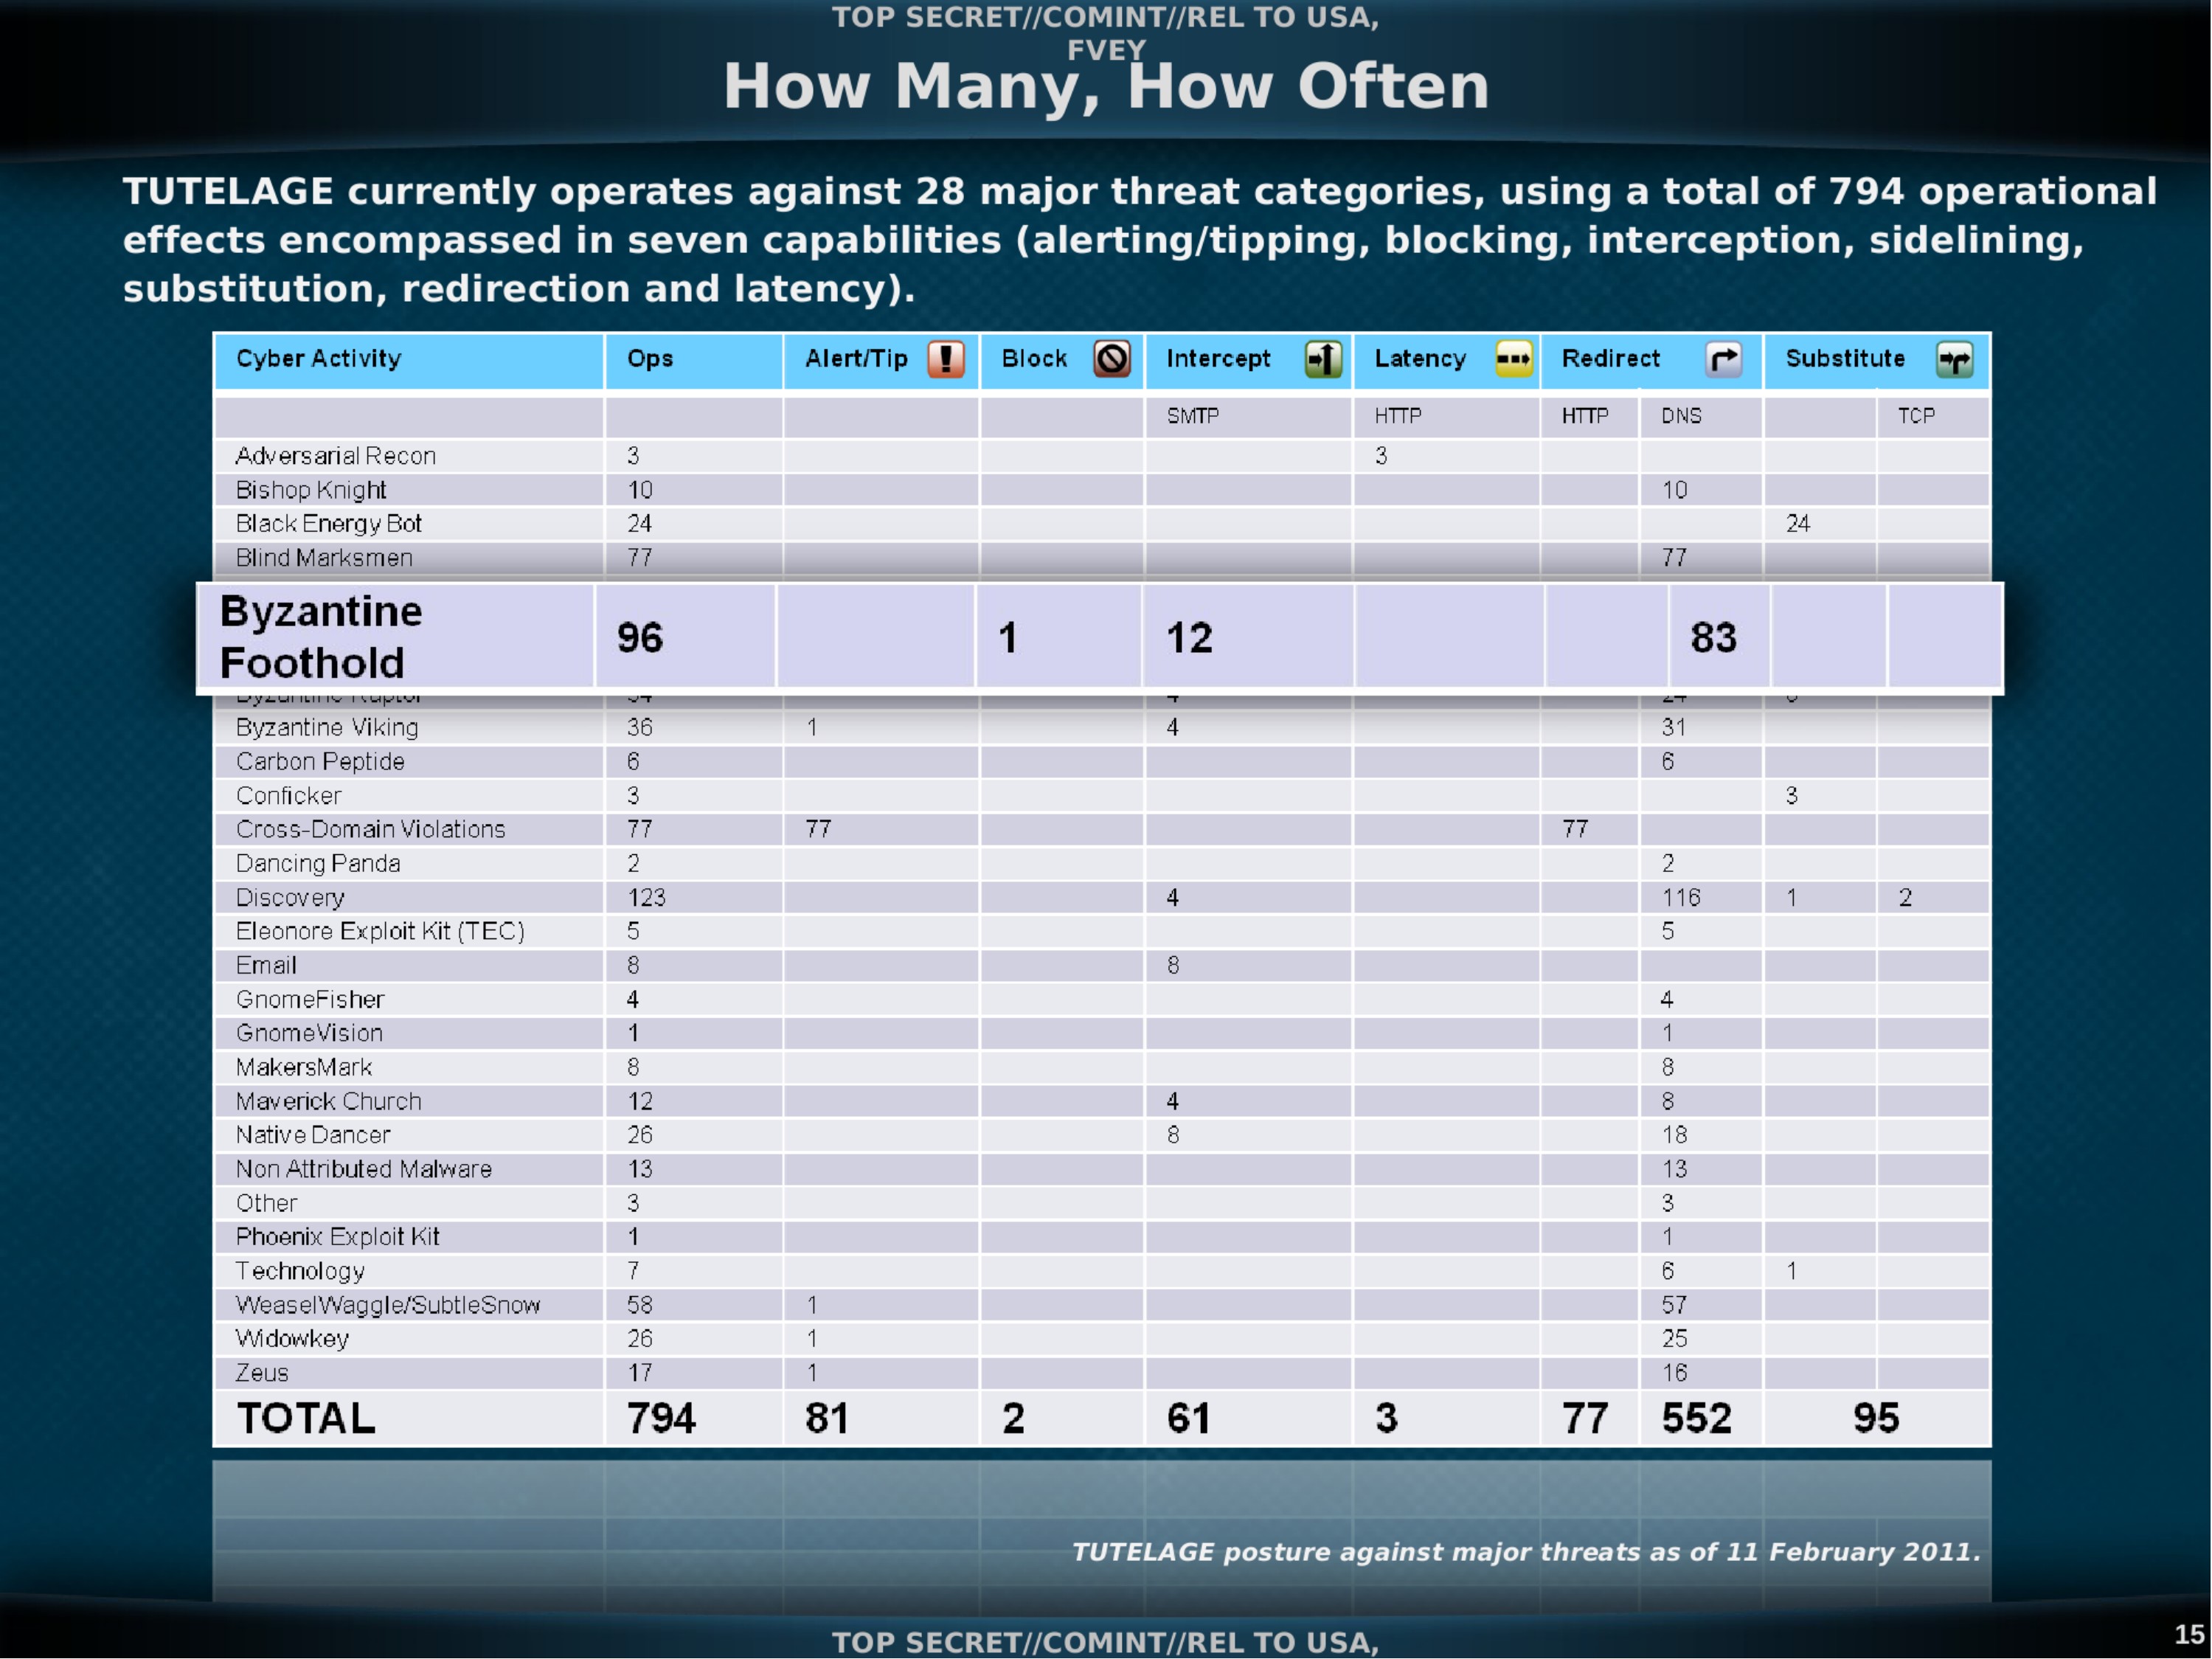
How Many, How Often
TUTELAGE currently operates against 28 major threat categories, using a total of 794 operational effects encompassed in seven capabilities (alerting/tipping, blocking, interception, sidelining, substitution, redirection and latency).
| Cyber Activity | Ops | Alert/Tip | Block | Intercept | Latency | Redirect | Substitute | ||
|---|---|---|---|---|---|---|---|---|---|
| SMTP | HTTP | HTTP | DNS | TCP | |||||
| Adversarial Recon | 3 | 3 | |||||||
| Bishop Knight | 10 | 10 | |||||||
| Black Energy Bot | 24 | 24 | |||||||
| Blind Marksmen | 77 | 77 | |||||||
| Byzantine Foothold | 96 | 1 | 12 | 83 | |||||
| Byzantine Viking | 36 | 1 | 4 | 31 | |||||
| Carbon Peptide | 6 | 6 | |||||||
| Conficker | 3 | 3 | |||||||
| Cross-Domain Violations | 77 | 77 | 77 | ||||||
| Dancing Panda | 2 | 2 | |||||||
| Discovery | 123 | 4 | 116 | 1 | 2 | ||||
| Eleonore Exploit Kit (TEC) | 5 | 5 | |||||||
| 8 | 8 | ||||||||
| GnomeFisher | 4 | 4 | |||||||
| GnomeVision | 1 | 1 | |||||||
| MakersMark | 8 | 8 | |||||||
| Maverick Church | 12 | 4 | 8 | ||||||
| Native Dancer | 26 | 8 | 18 | ||||||
| Non Attributed Malware | 13 | 13 | |||||||
| Other | 3 | 3 | |||||||
| Phoenix Exploit Kit | 1 | 1 | |||||||
| Technology | 7 | 6 | 1 | ||||||
| WeaselWaggle/SubtleSnow | 58 | 1 | 57 | ||||||
| Widowkey | 26 | 1 | 25 | ||||||
| Zeus | 17 | 1 | 16 | ||||||
| TOTAL | 794 | 81 | 2 | 61 | 3 | 77 | 552 | 95 |
TUTELAGE posture against major threats as of 11 February 2011.
TOP SECRET//COMINT//REL TO USA,
15
UNCLASSIFIED//FOUO
FUTURE CAPABILITIES
UNCLASSIFIED//FOUO
16
SECRET//COMINT//REL TO USA, FVEY
Upgrades & What They Mean
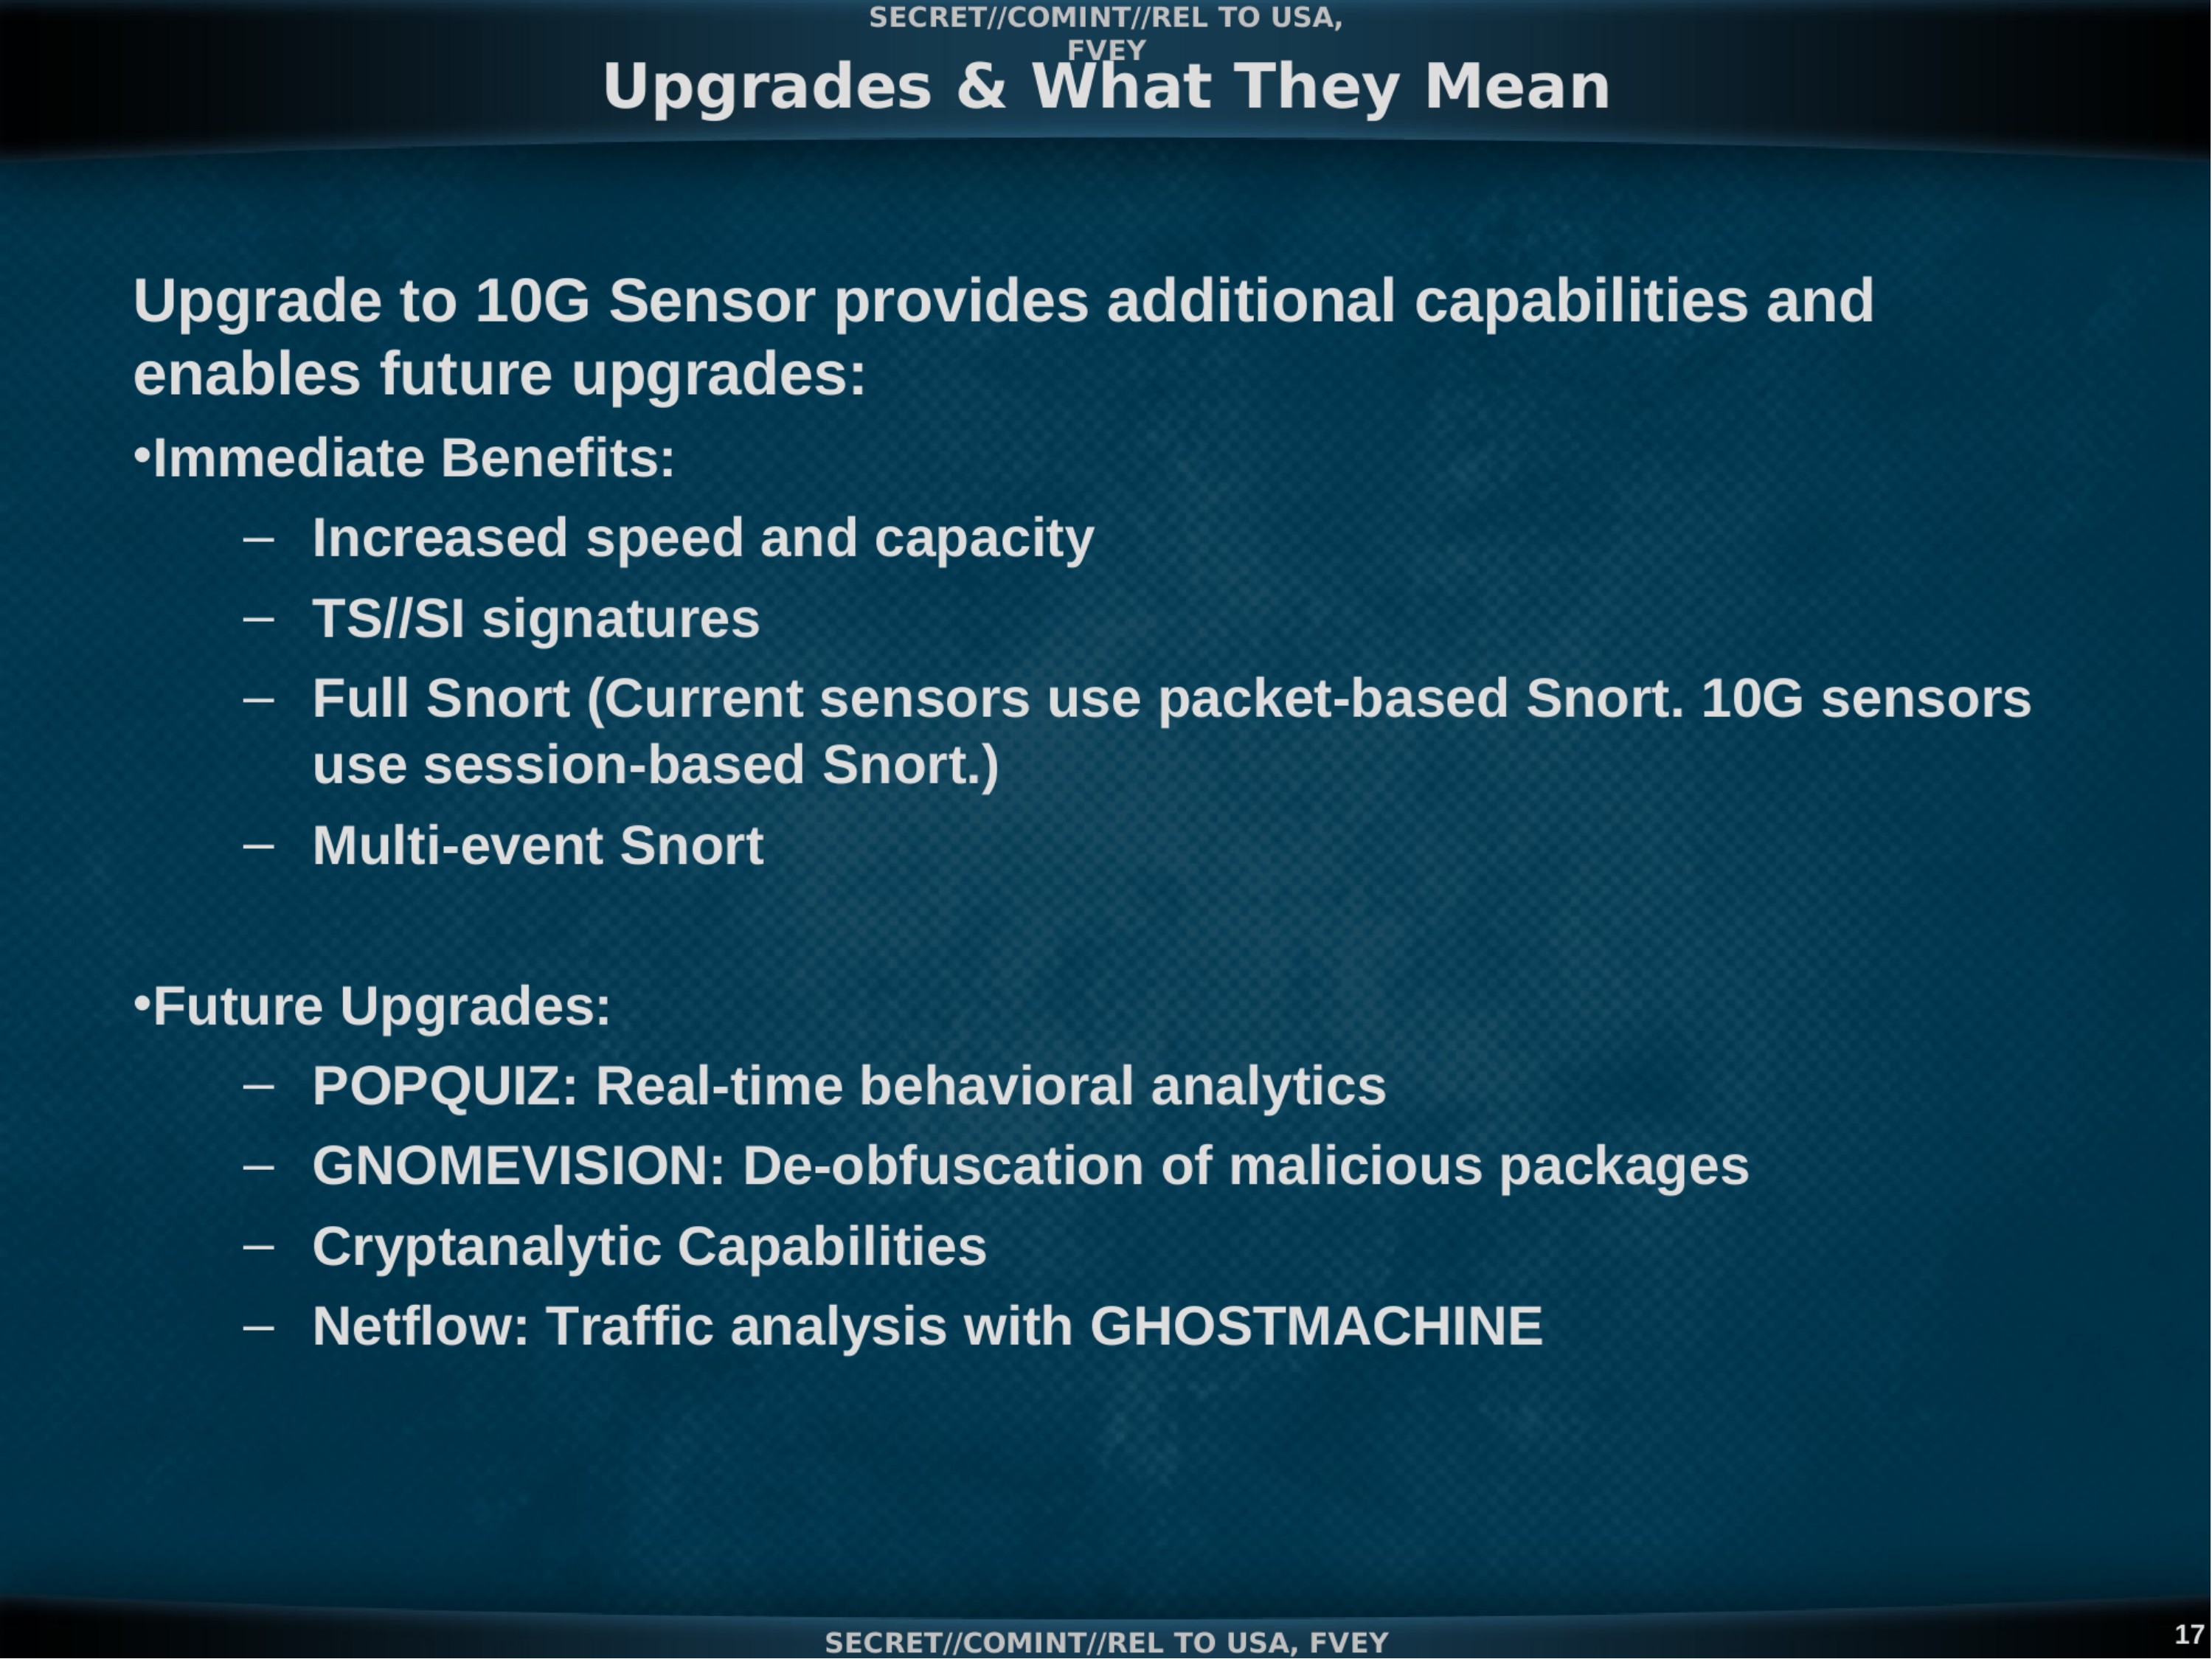
Upgrade to 10G Sensor provides additional capabilities and enables future upgrades:
- Immediate Benefits:
- Increased speed and capacity
- TS//SI signatures
- Full Snort (Current sensors use packet-based Snort. 10G sensors use session-based Snort.)
- Multi-event Snort
- Future Upgrades:
- POPQUIZ: Real-time behavioral analytics
- GNOMEVISION: De-obfuscation of malicious packages
- Cryptanalytic Capabilities
- Netflow: Traffic analysis with GHOSTMACHINE
SECRET//COMINT//REL TO USA, FVEY
17
SECRET//COMINT//REL TO USA, FVEY
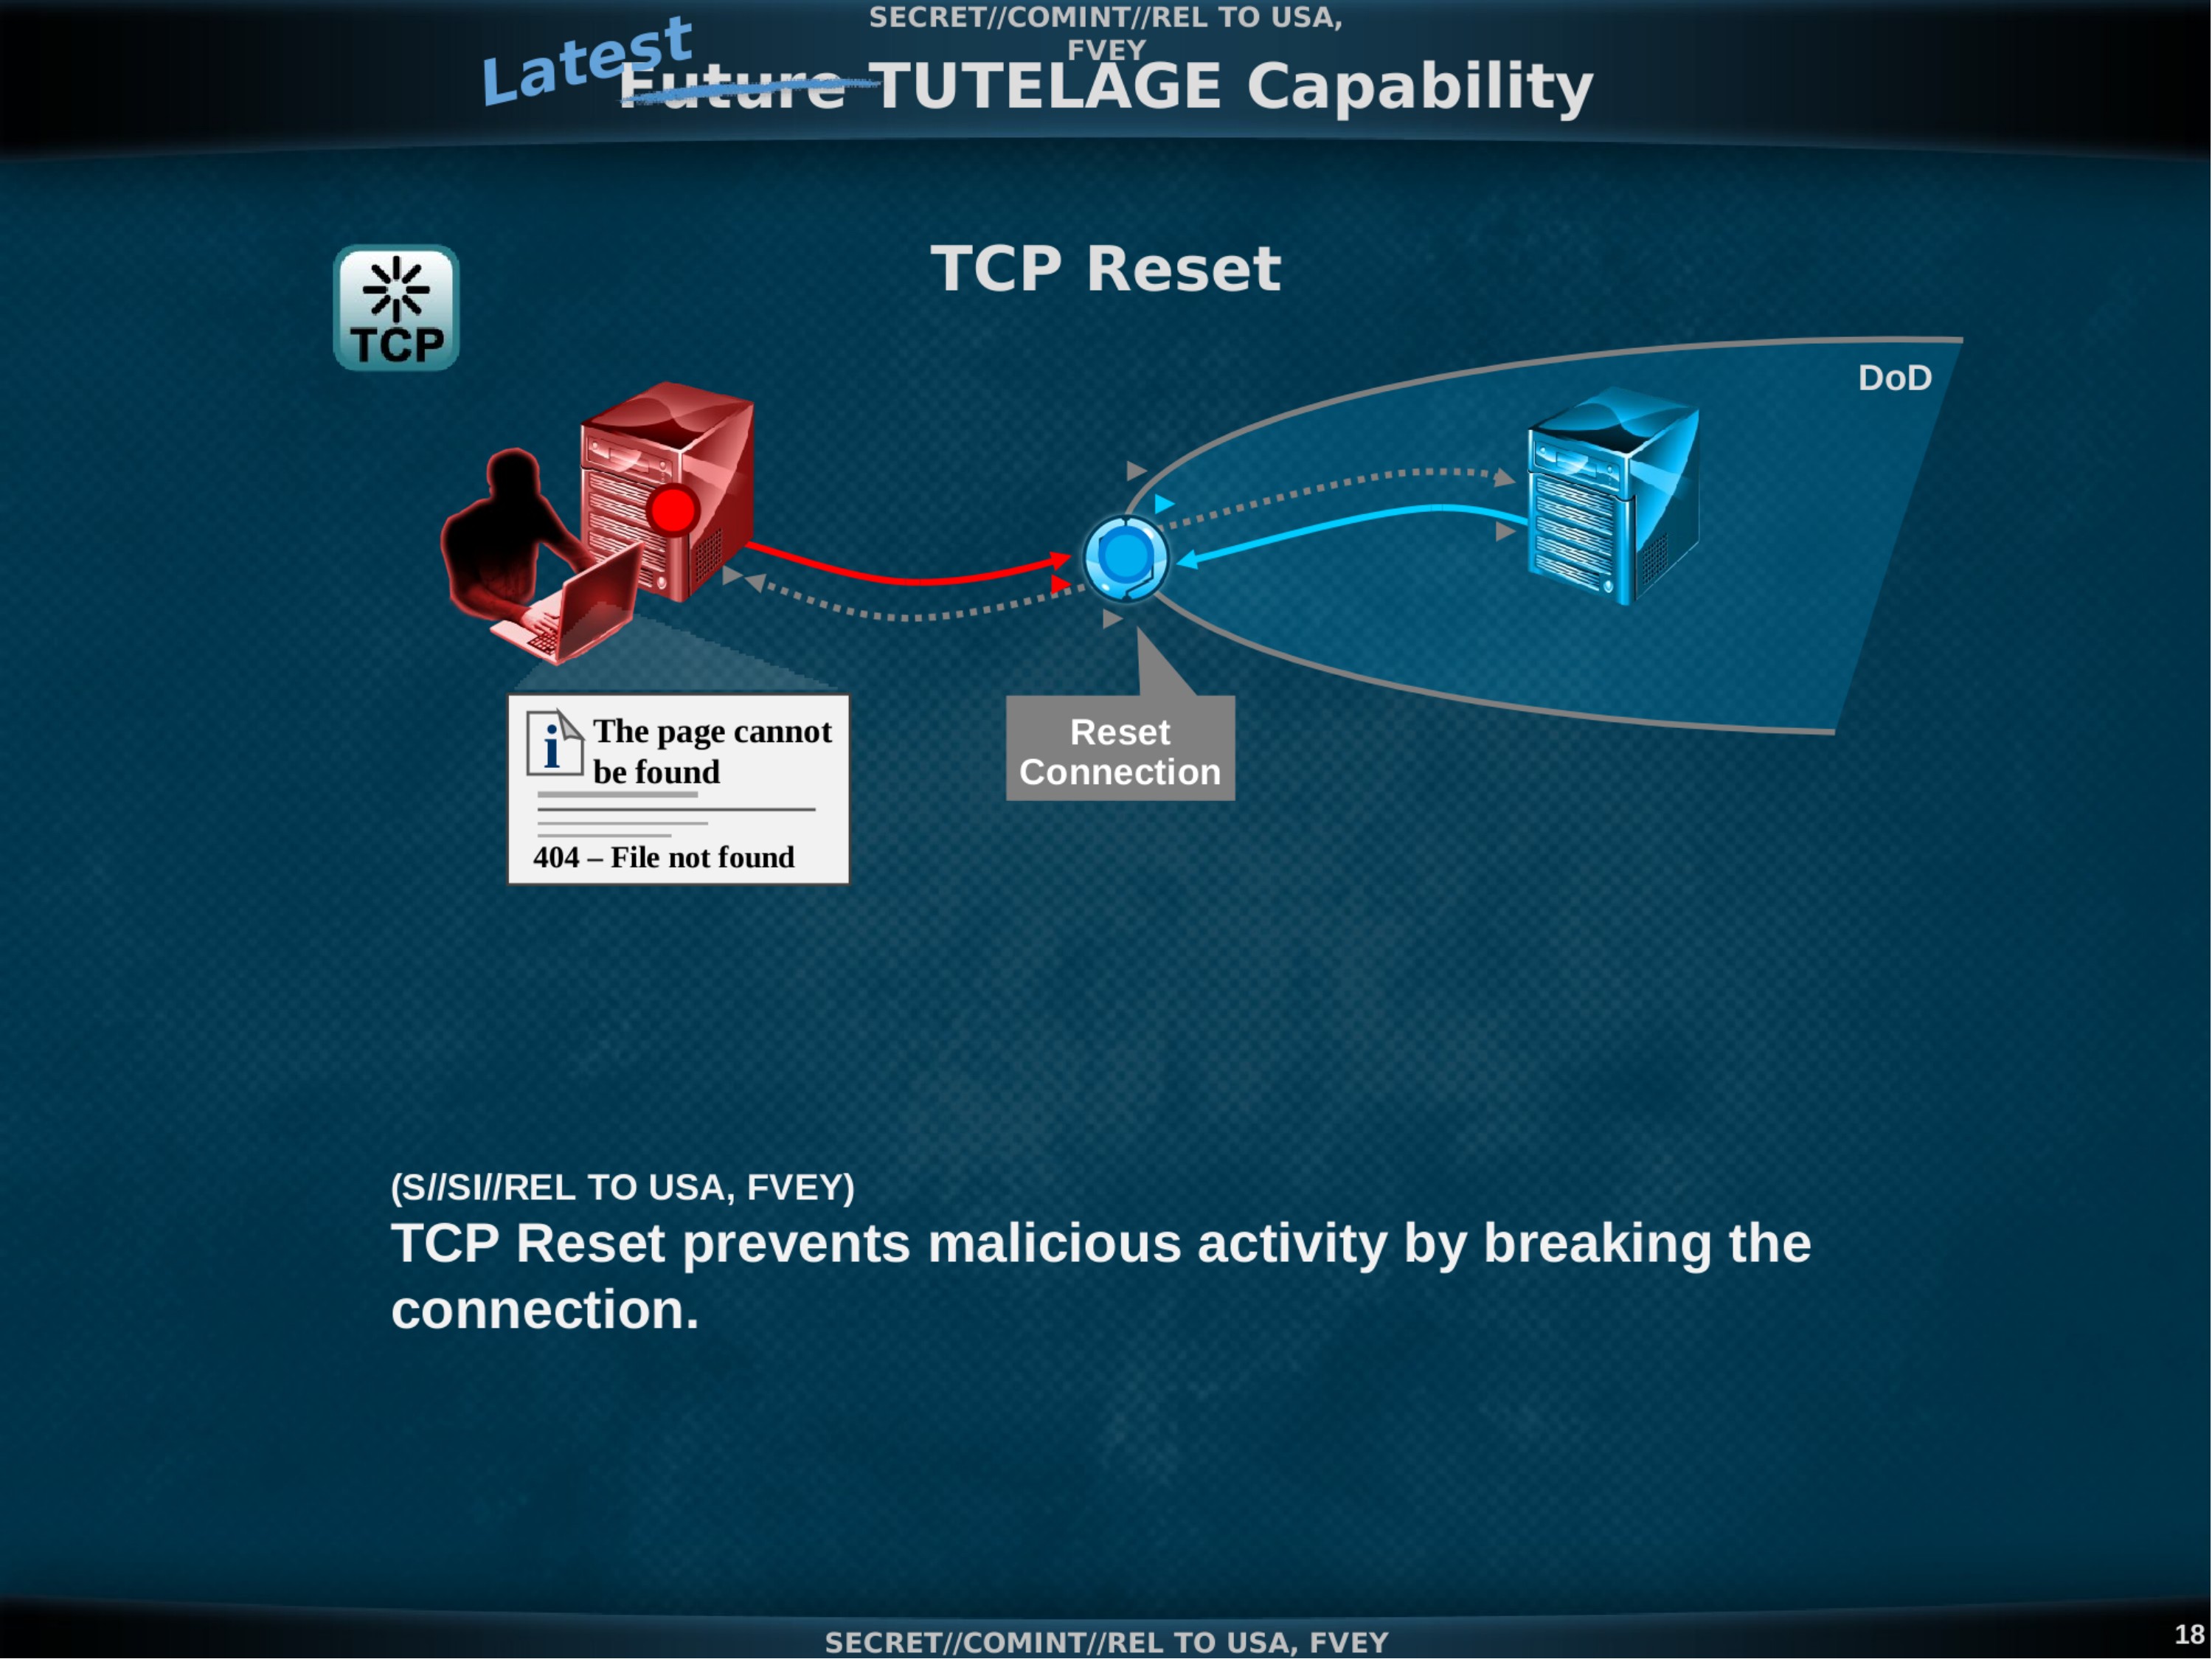
Latest ~Future~ TUTELAGE Capability
TCP Reset
- TCP
- The page cannot be found 404 - File not found
- Reset Connection
- DoD
(S//SI//REL TO USA, FVEY)
TCP Reset prevents malicious activity by breaking the connection.
SECRET//COMINT//REL TO USA, FVEY
18
SECRET//COMINT//REL TO USA, FVEY
Future TUTELAGE Capabilities
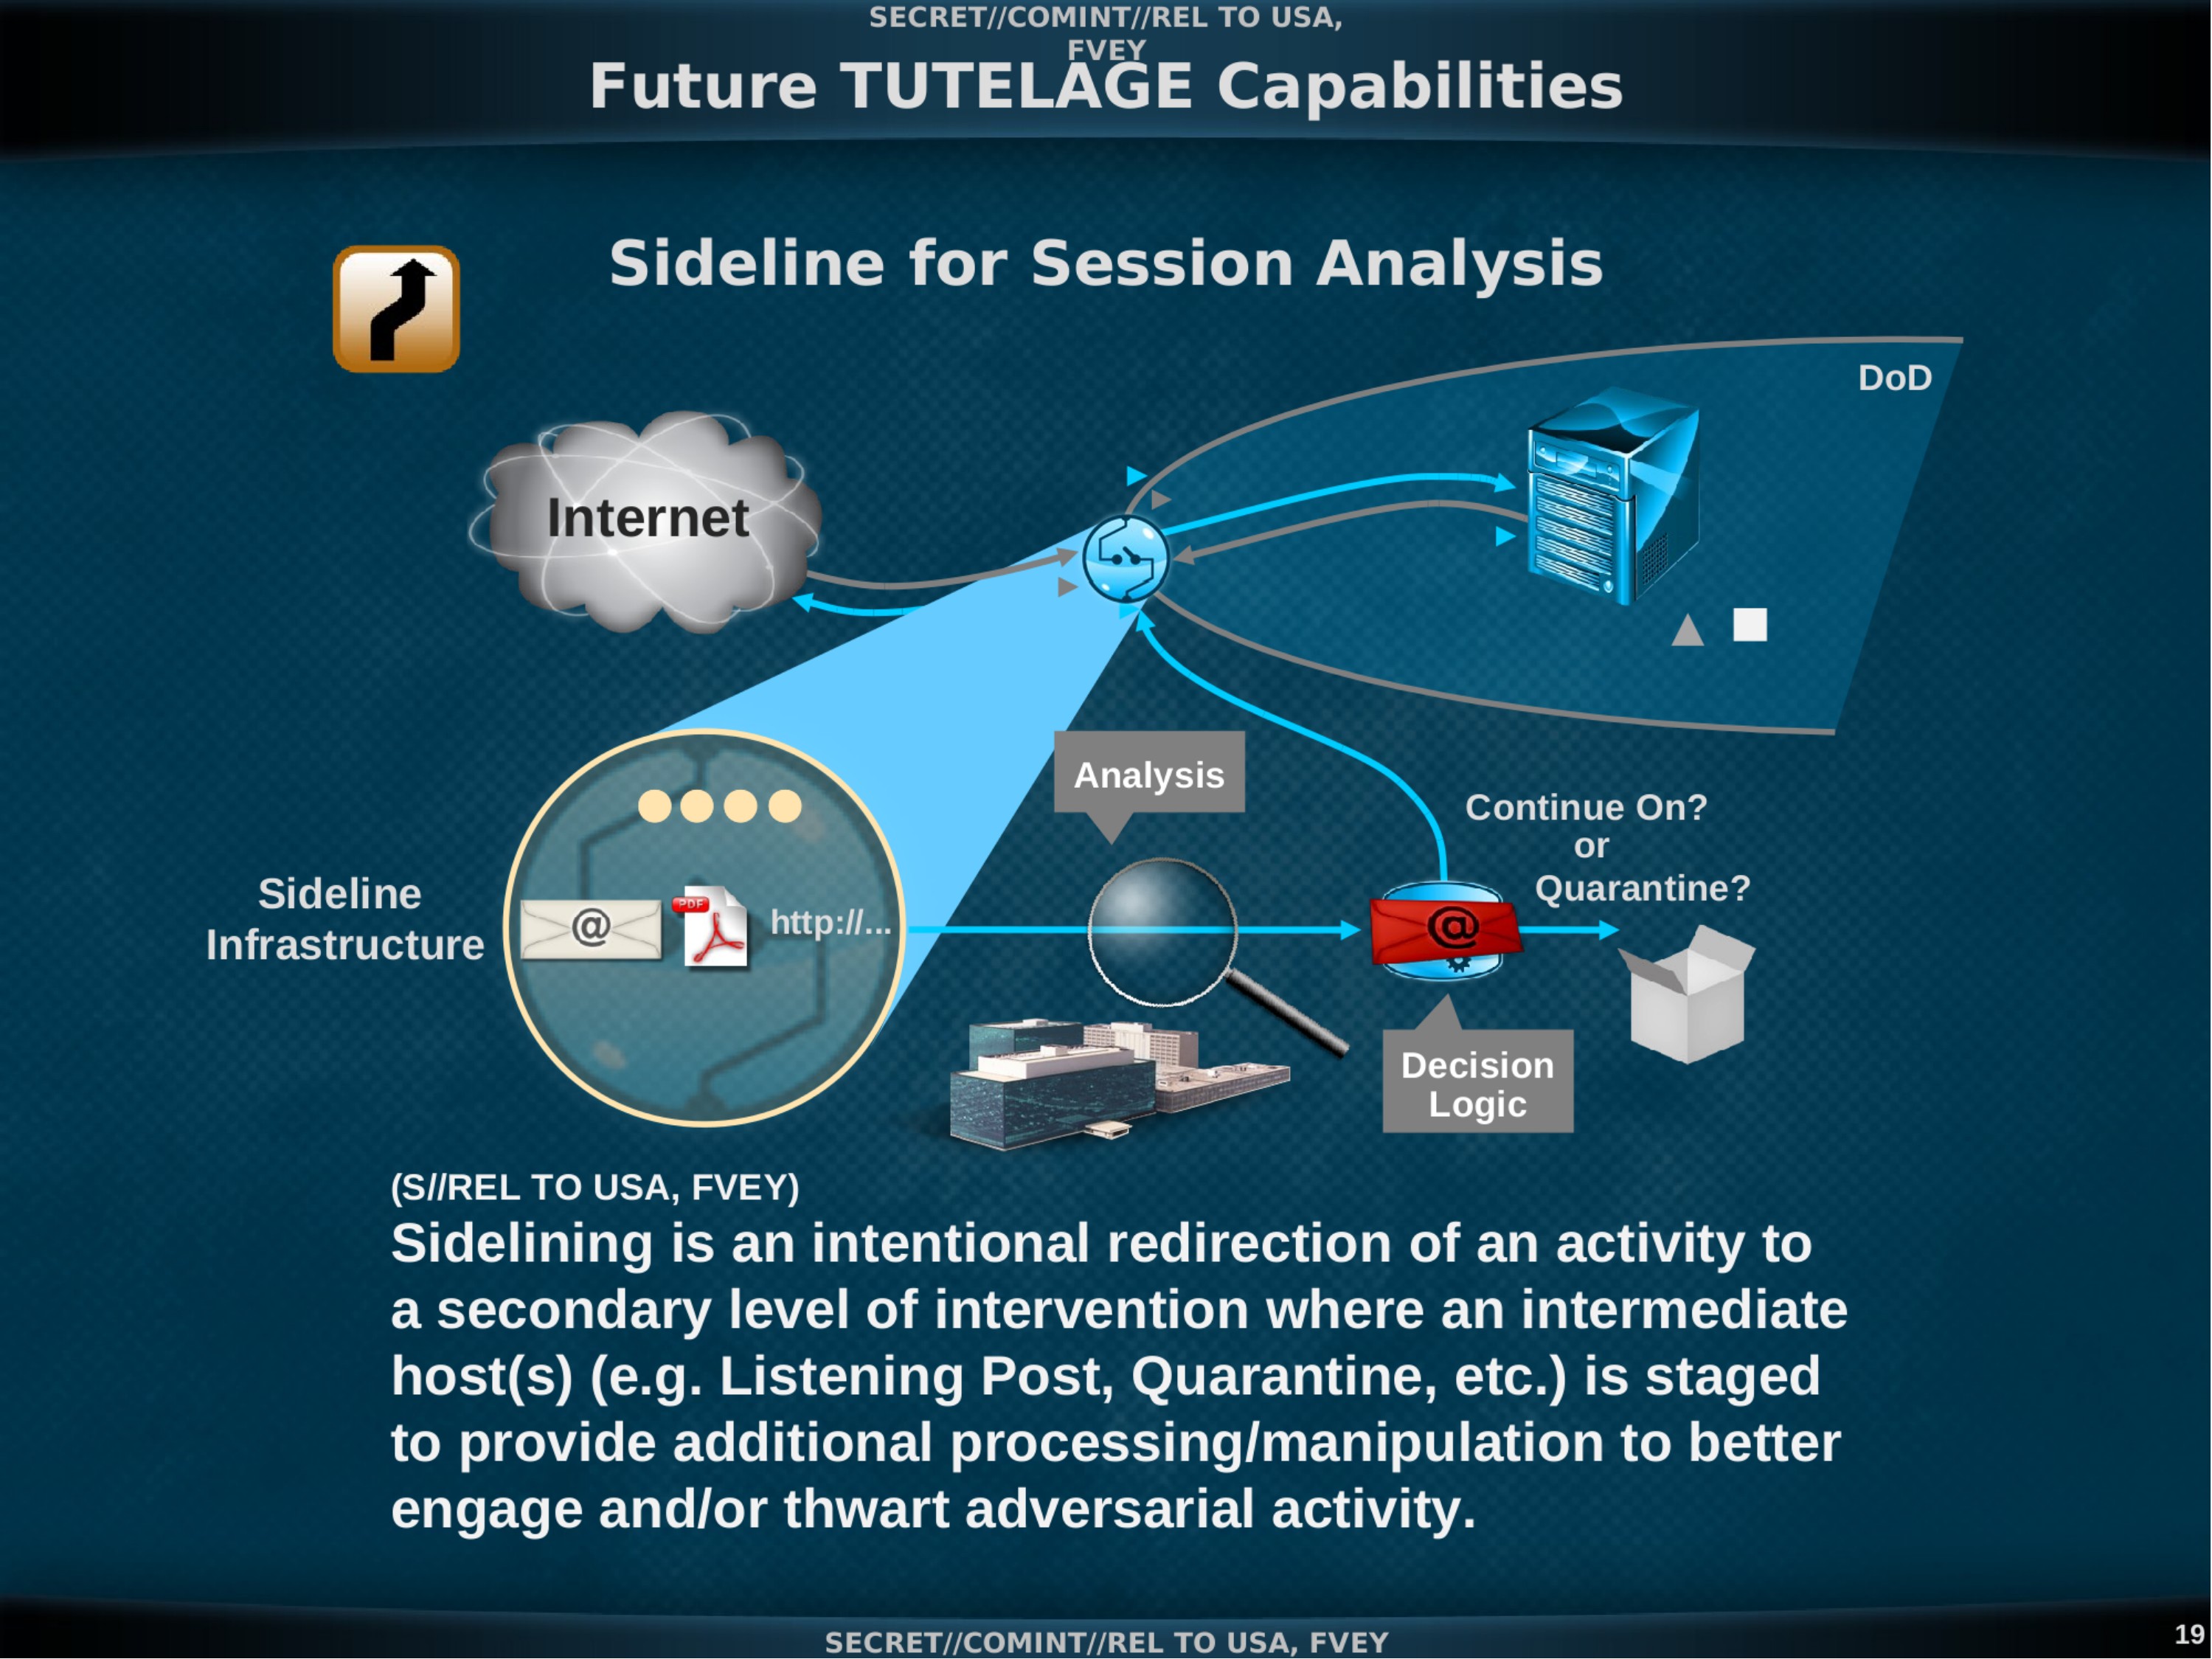
Sideline for Session Analysis
- Internet
- Sideline Infrastructure
- Analysis
- http://...
- Continue On? or Quarantine?
- Decision Logic
- DoD
(S//REL TO USA, FVEY)
Sidelining is an intentional redirection of an activity to a secondary level of intervention where an intermediate host(s) (e.g. Listening Post, Quarantine, etc.) is staged to provide additional processing/manipulation to better engage and/or thwart adversarial activity.
SECRET//COMINT//REL TO USA, FVEY
19
SECRET//COMINT//REL TO USA, FVEY
Future TUTELAGE Capabilities
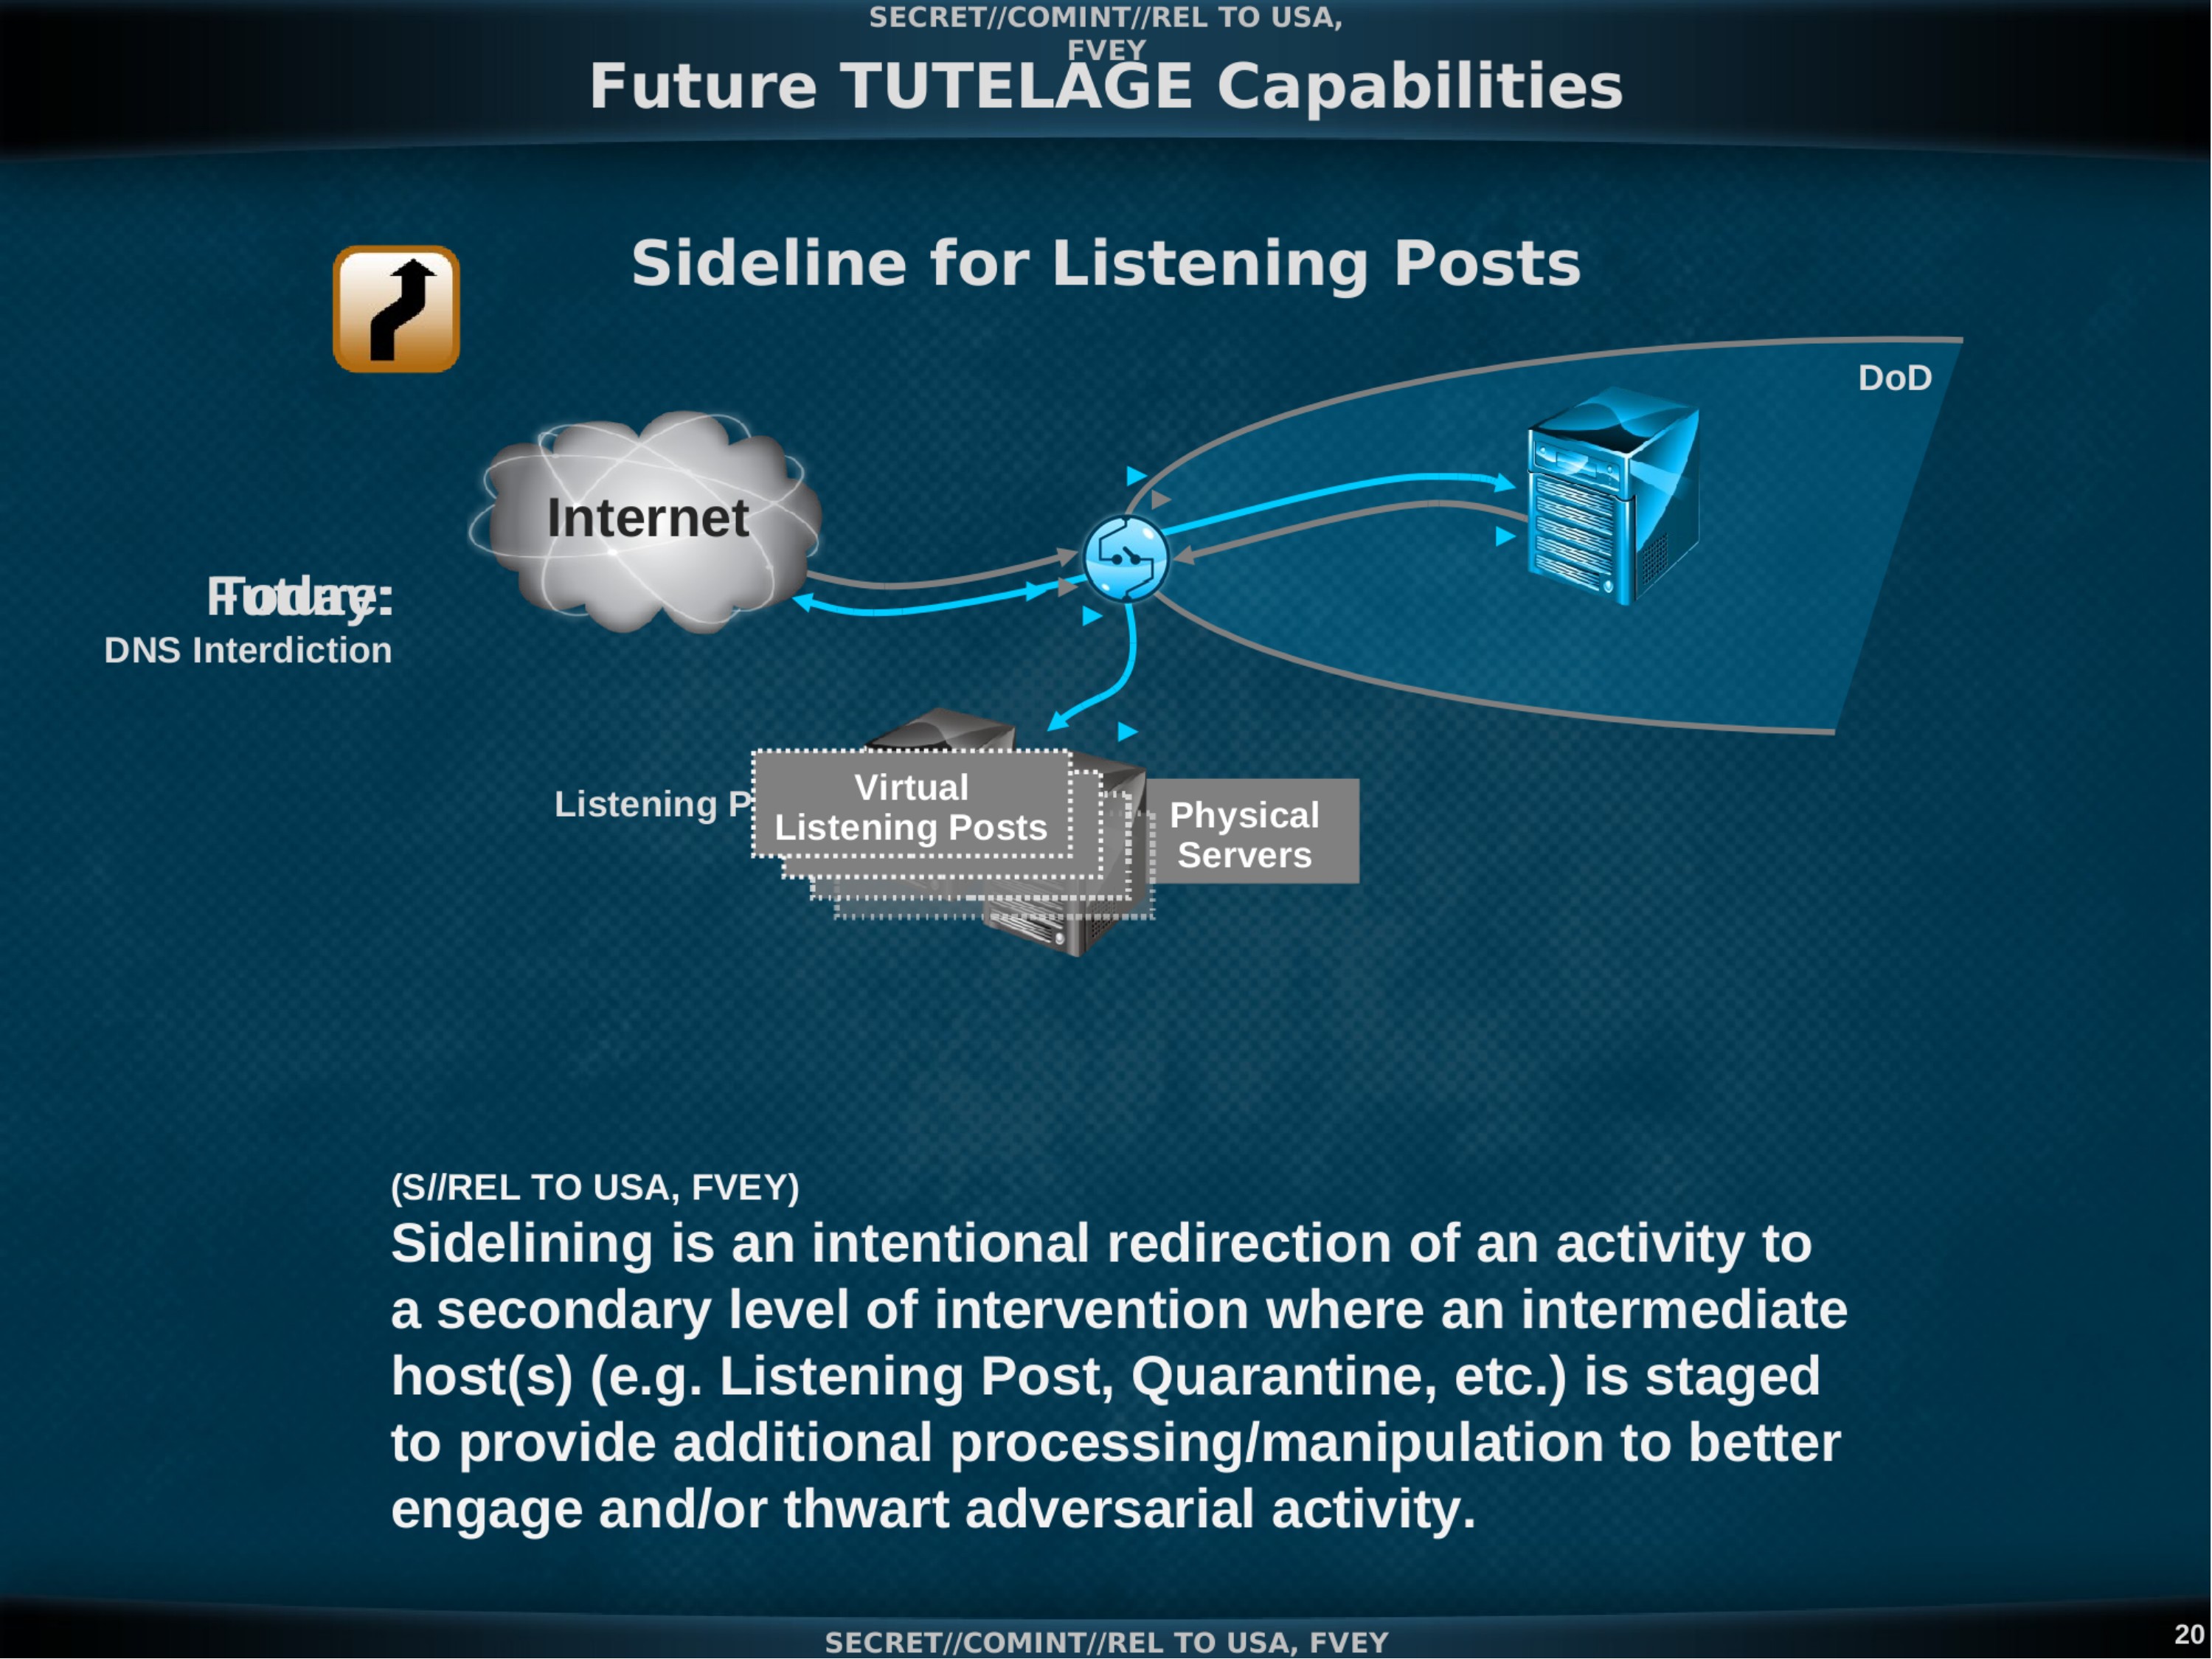
Sideline for Listening Posts
- Internet
- Today: DNS Interdiction
- Listening Post
- Virtual Listening Posts
- Physical Servers
- DoD
(S//REL TO USA, FVEY)
Sidelining is an intentional redirection of an activity to a secondary level of intervention where an intermediate host(s) (e.g. Listening Post, Quarantine, etc.) is staged to provide additional processing/manipulation to better engage and/or thwart adversarial activity.
SECRET//COMINT//REL TO USA, FVEY
20
SECRET//COMINT//REL TO USA, FVEY
Future TUTELAGE Capabilities
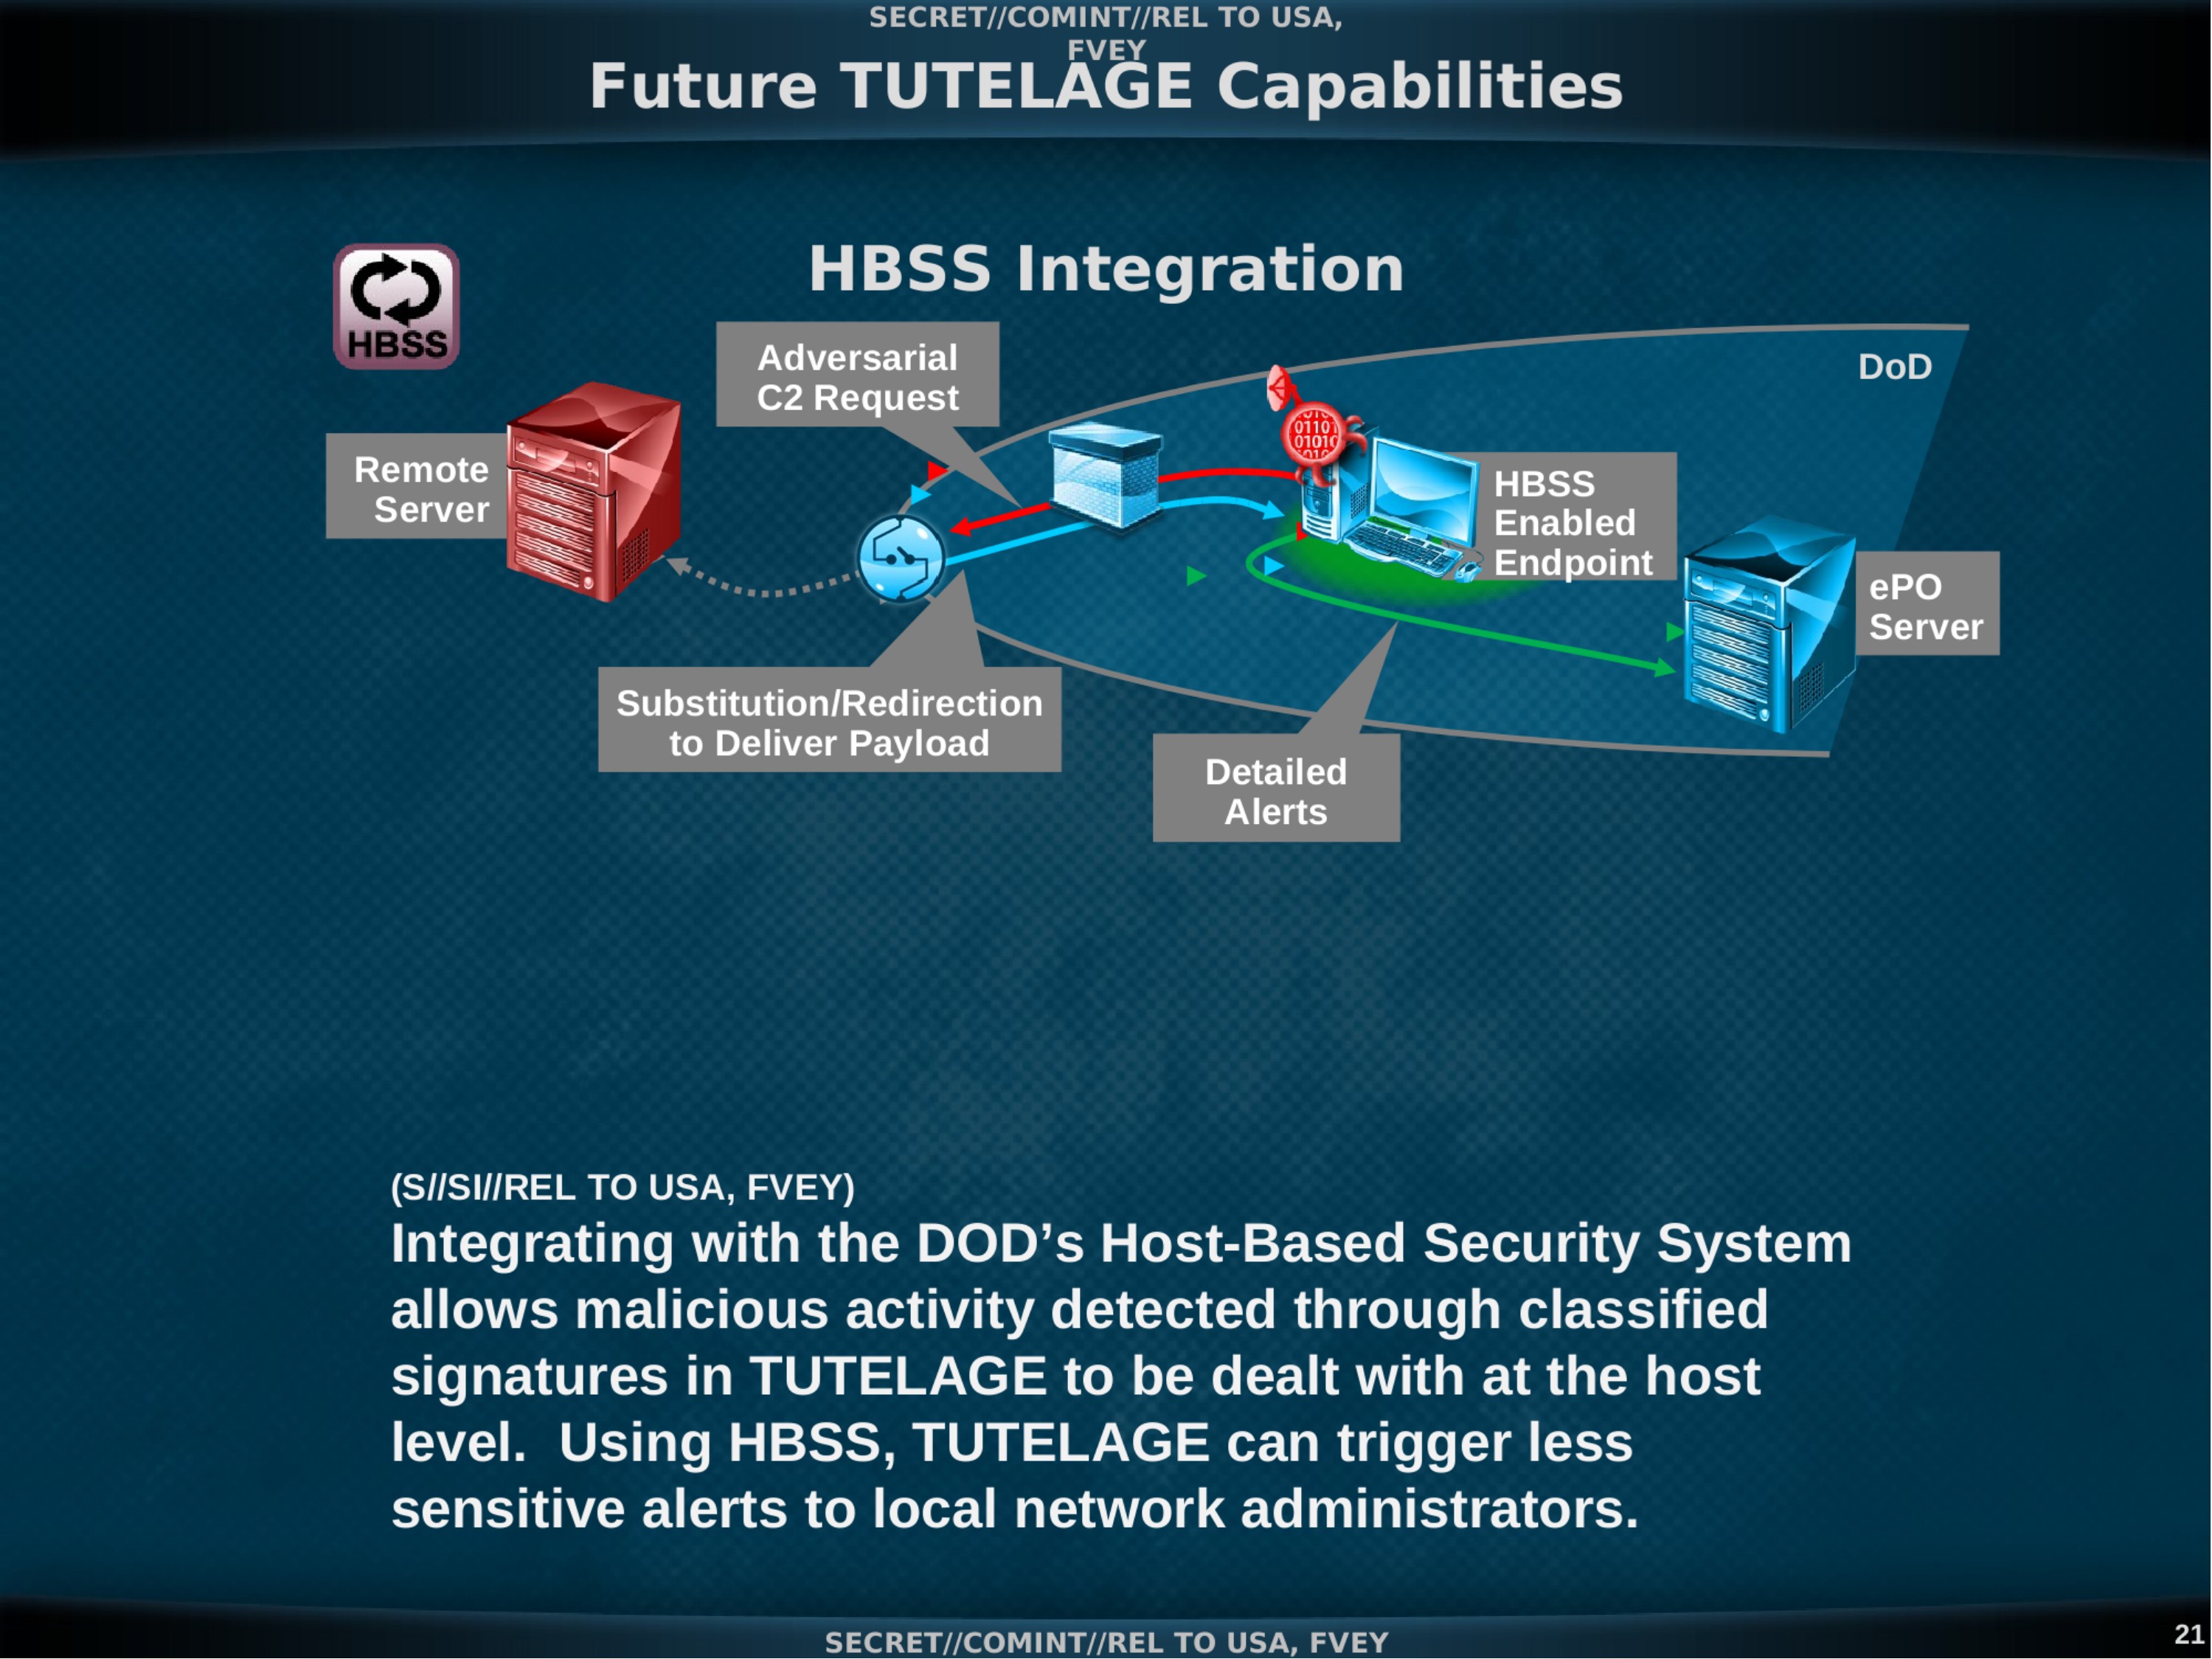
HBSS Integration
- HBSS
- Adversarial C2 Request
- Remote Server
- HBSS Enabled Endpoint
- ePO Server
- Substitution/Redirection to Deliver Payload
- Detailed Alerts
- DoD
(S//SI//REL TO USA, FVEY)
Integrating with the DOD's Host-Based Security System allows malicious activity detected through classified signatures in TUTELAGE to be dealt with at the host level. Using HBSS, TUTELAGE can trigger less sensitive alerts to local network administrators.
SECRET//COMINT//REL TO USA, FVEY
21
TOP SECRET//COMINT//REL TO USA, FVEY
Future TUTELAGE Capabilities
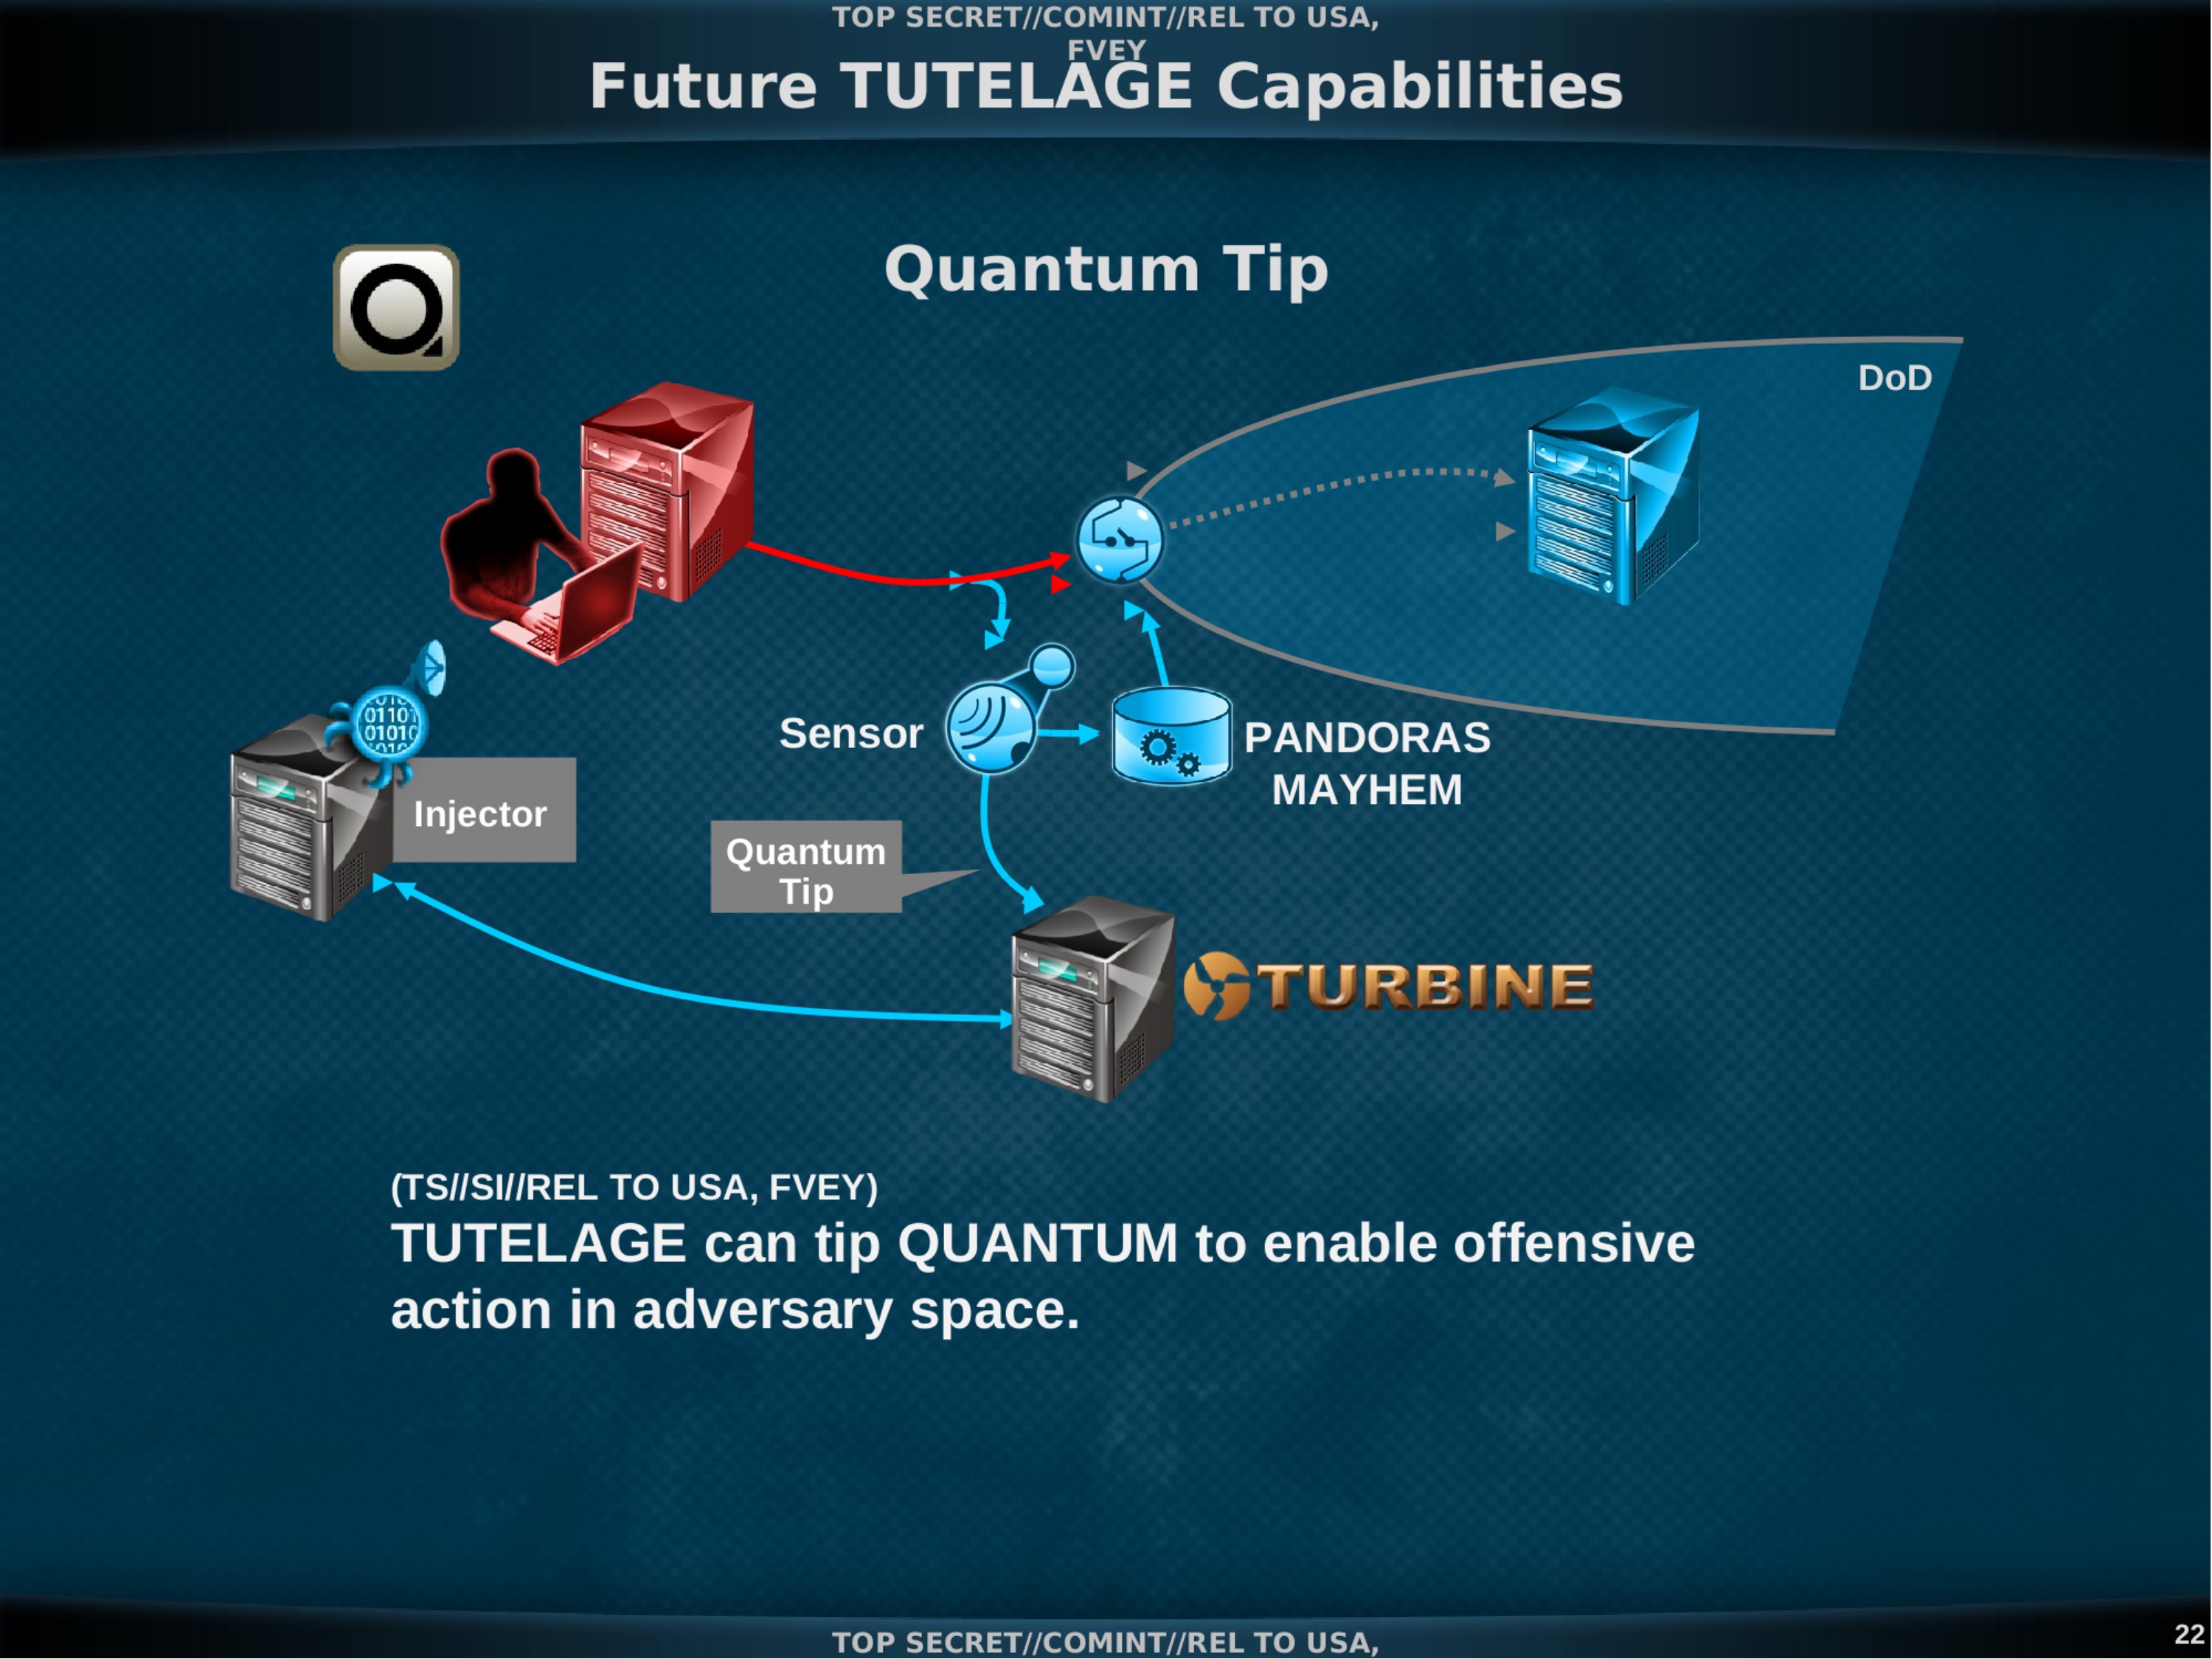
Quantum Tip
- Sensor
- PANDORAS MAYHEM
- Injector
- Quantum Tip
- TURBINE
- DoD
(TS//SI//REL TO USA, FVEY)
TUTELAGE can tip QUANTUM to enable offensive action in adversary space.
TOP SECRET//COMINT//REL TO USA,
22
TOP SECRET//COMINT//REL TO USA, FVEY
Future TUTELAGE Capabilities
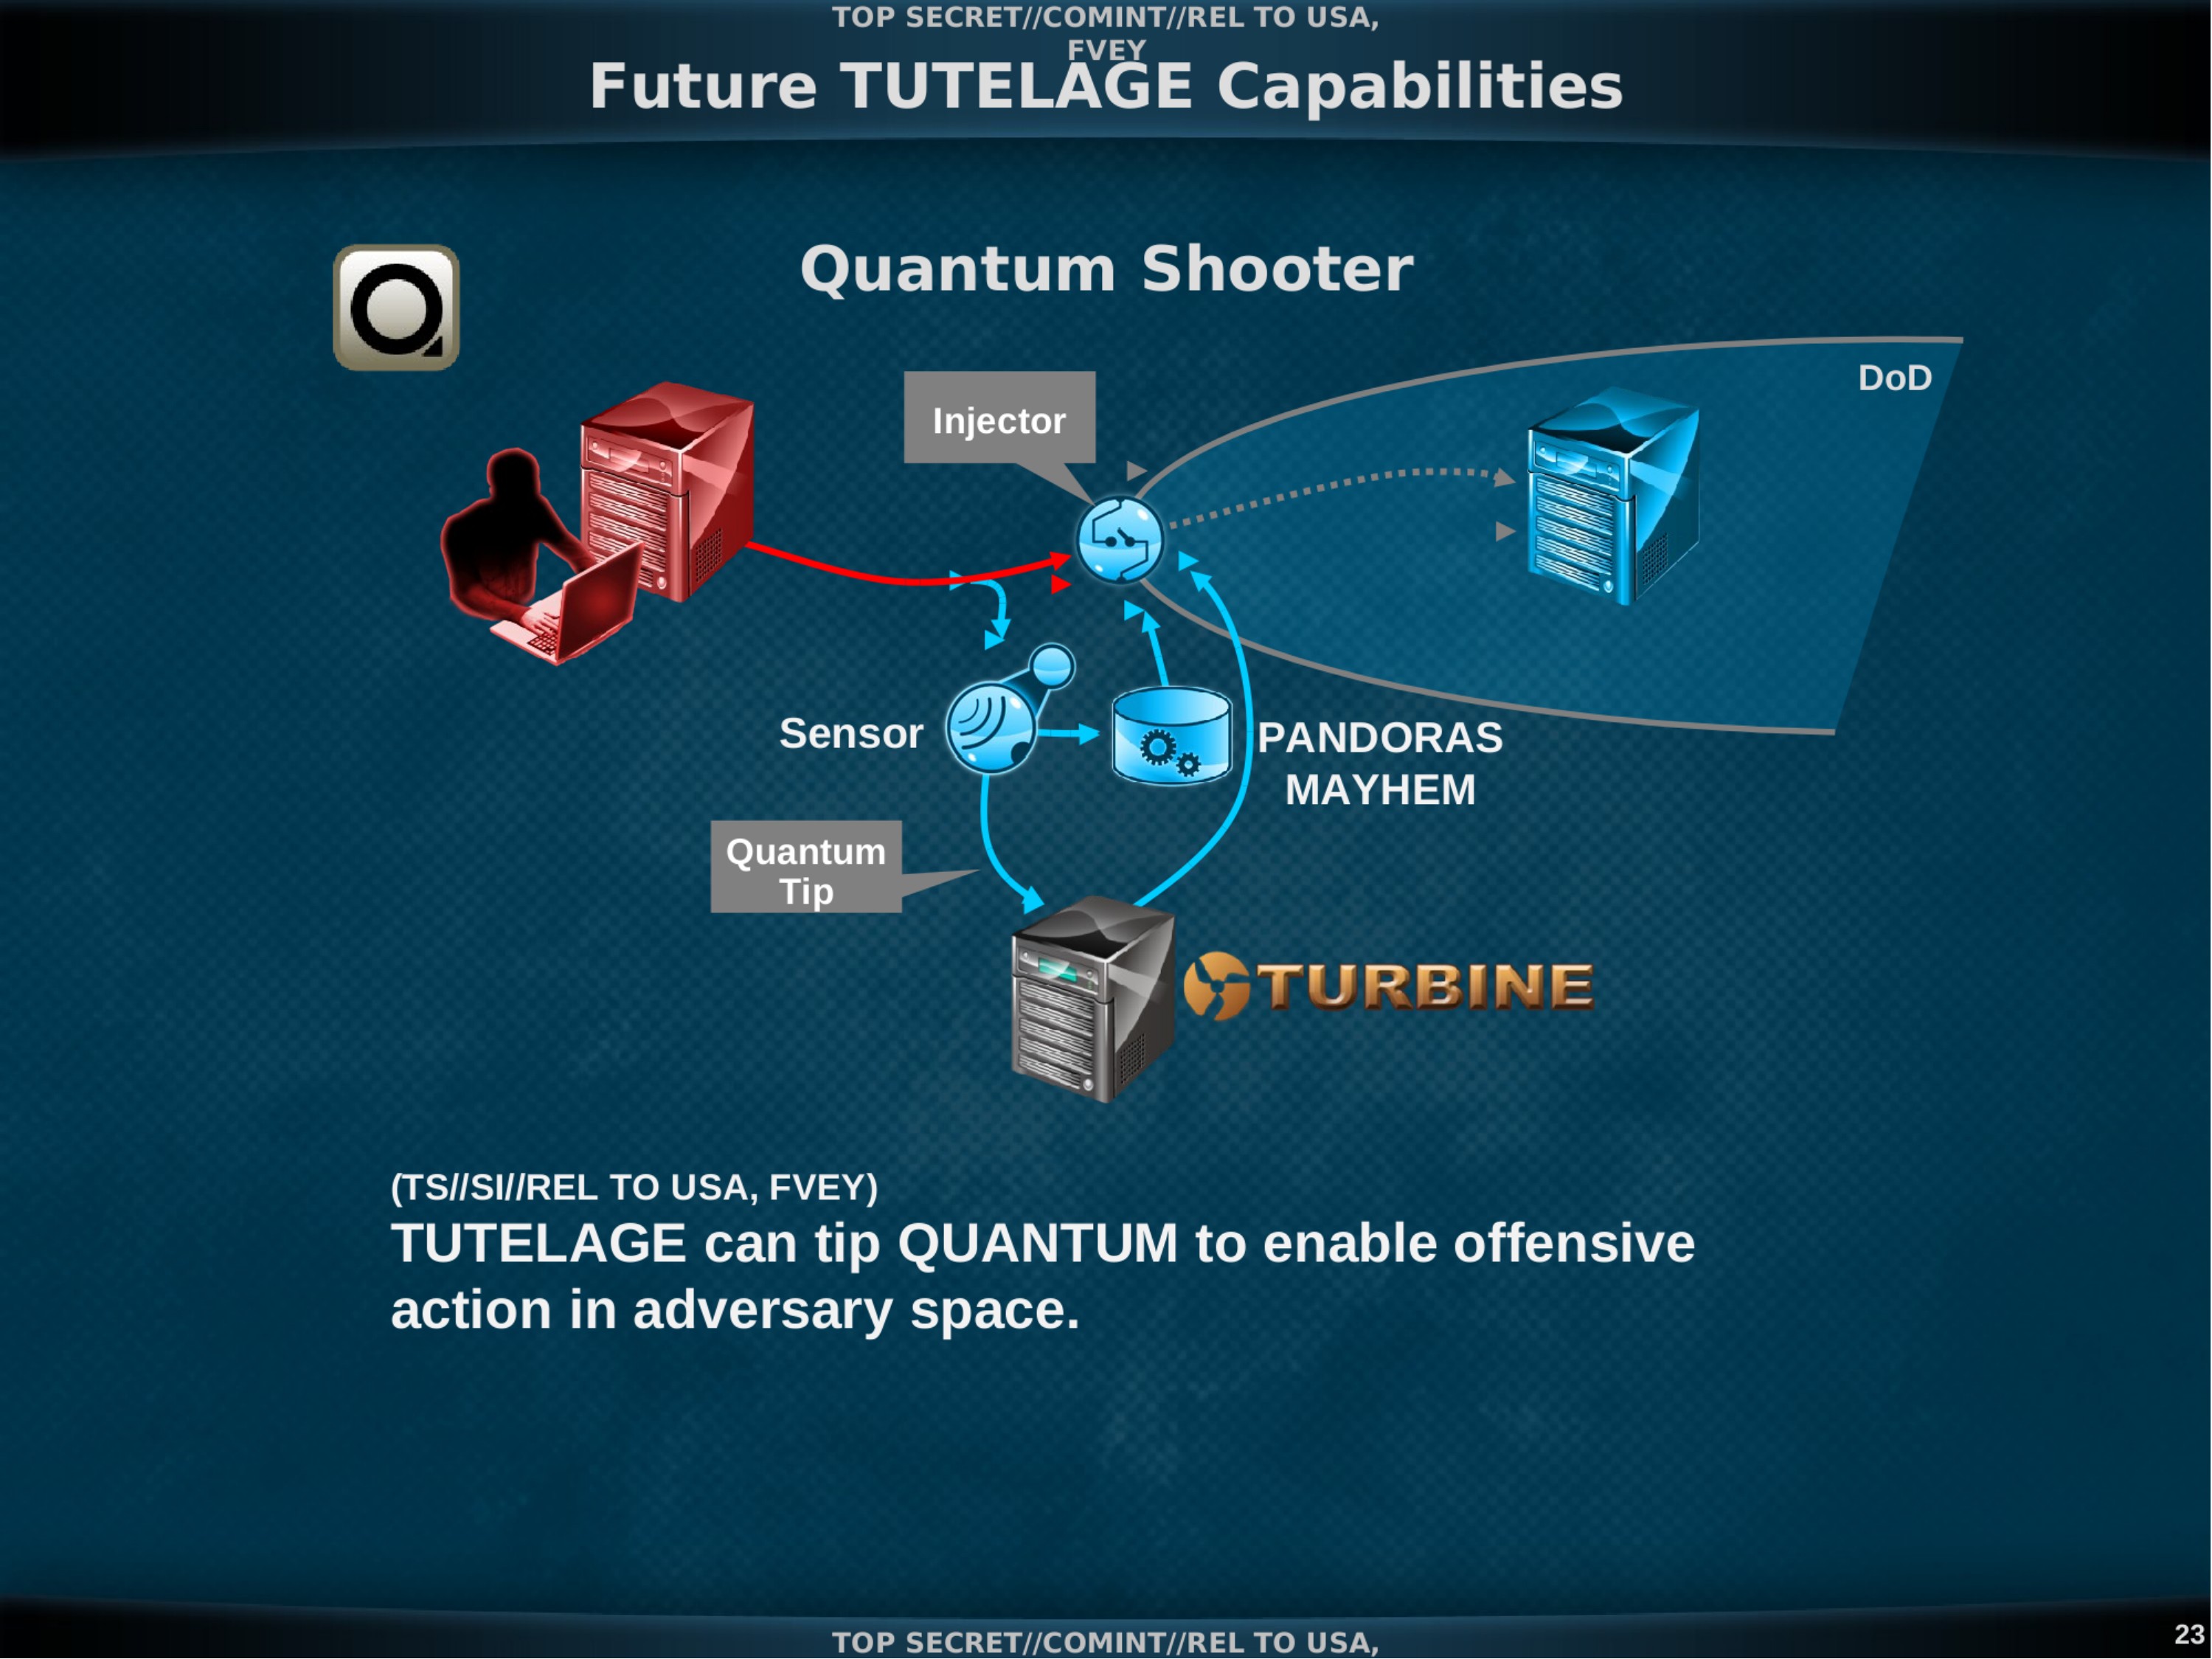
Quantum Shooter
- Injector
- Sensor
- PANDORAS MAYHEM
- Quantum Tip
- TURBINE
- DoD
(TS//SI//REL TO USA, FVEY)
TUTELAGE can tip QUANTUM to enable offensive action in adversary space.
TOP SECRET//COMINT//REL TO USA,
23
TOP SECRET//COMINT//REL TO USA, FVEY
Future TUTELAGE Capabilities
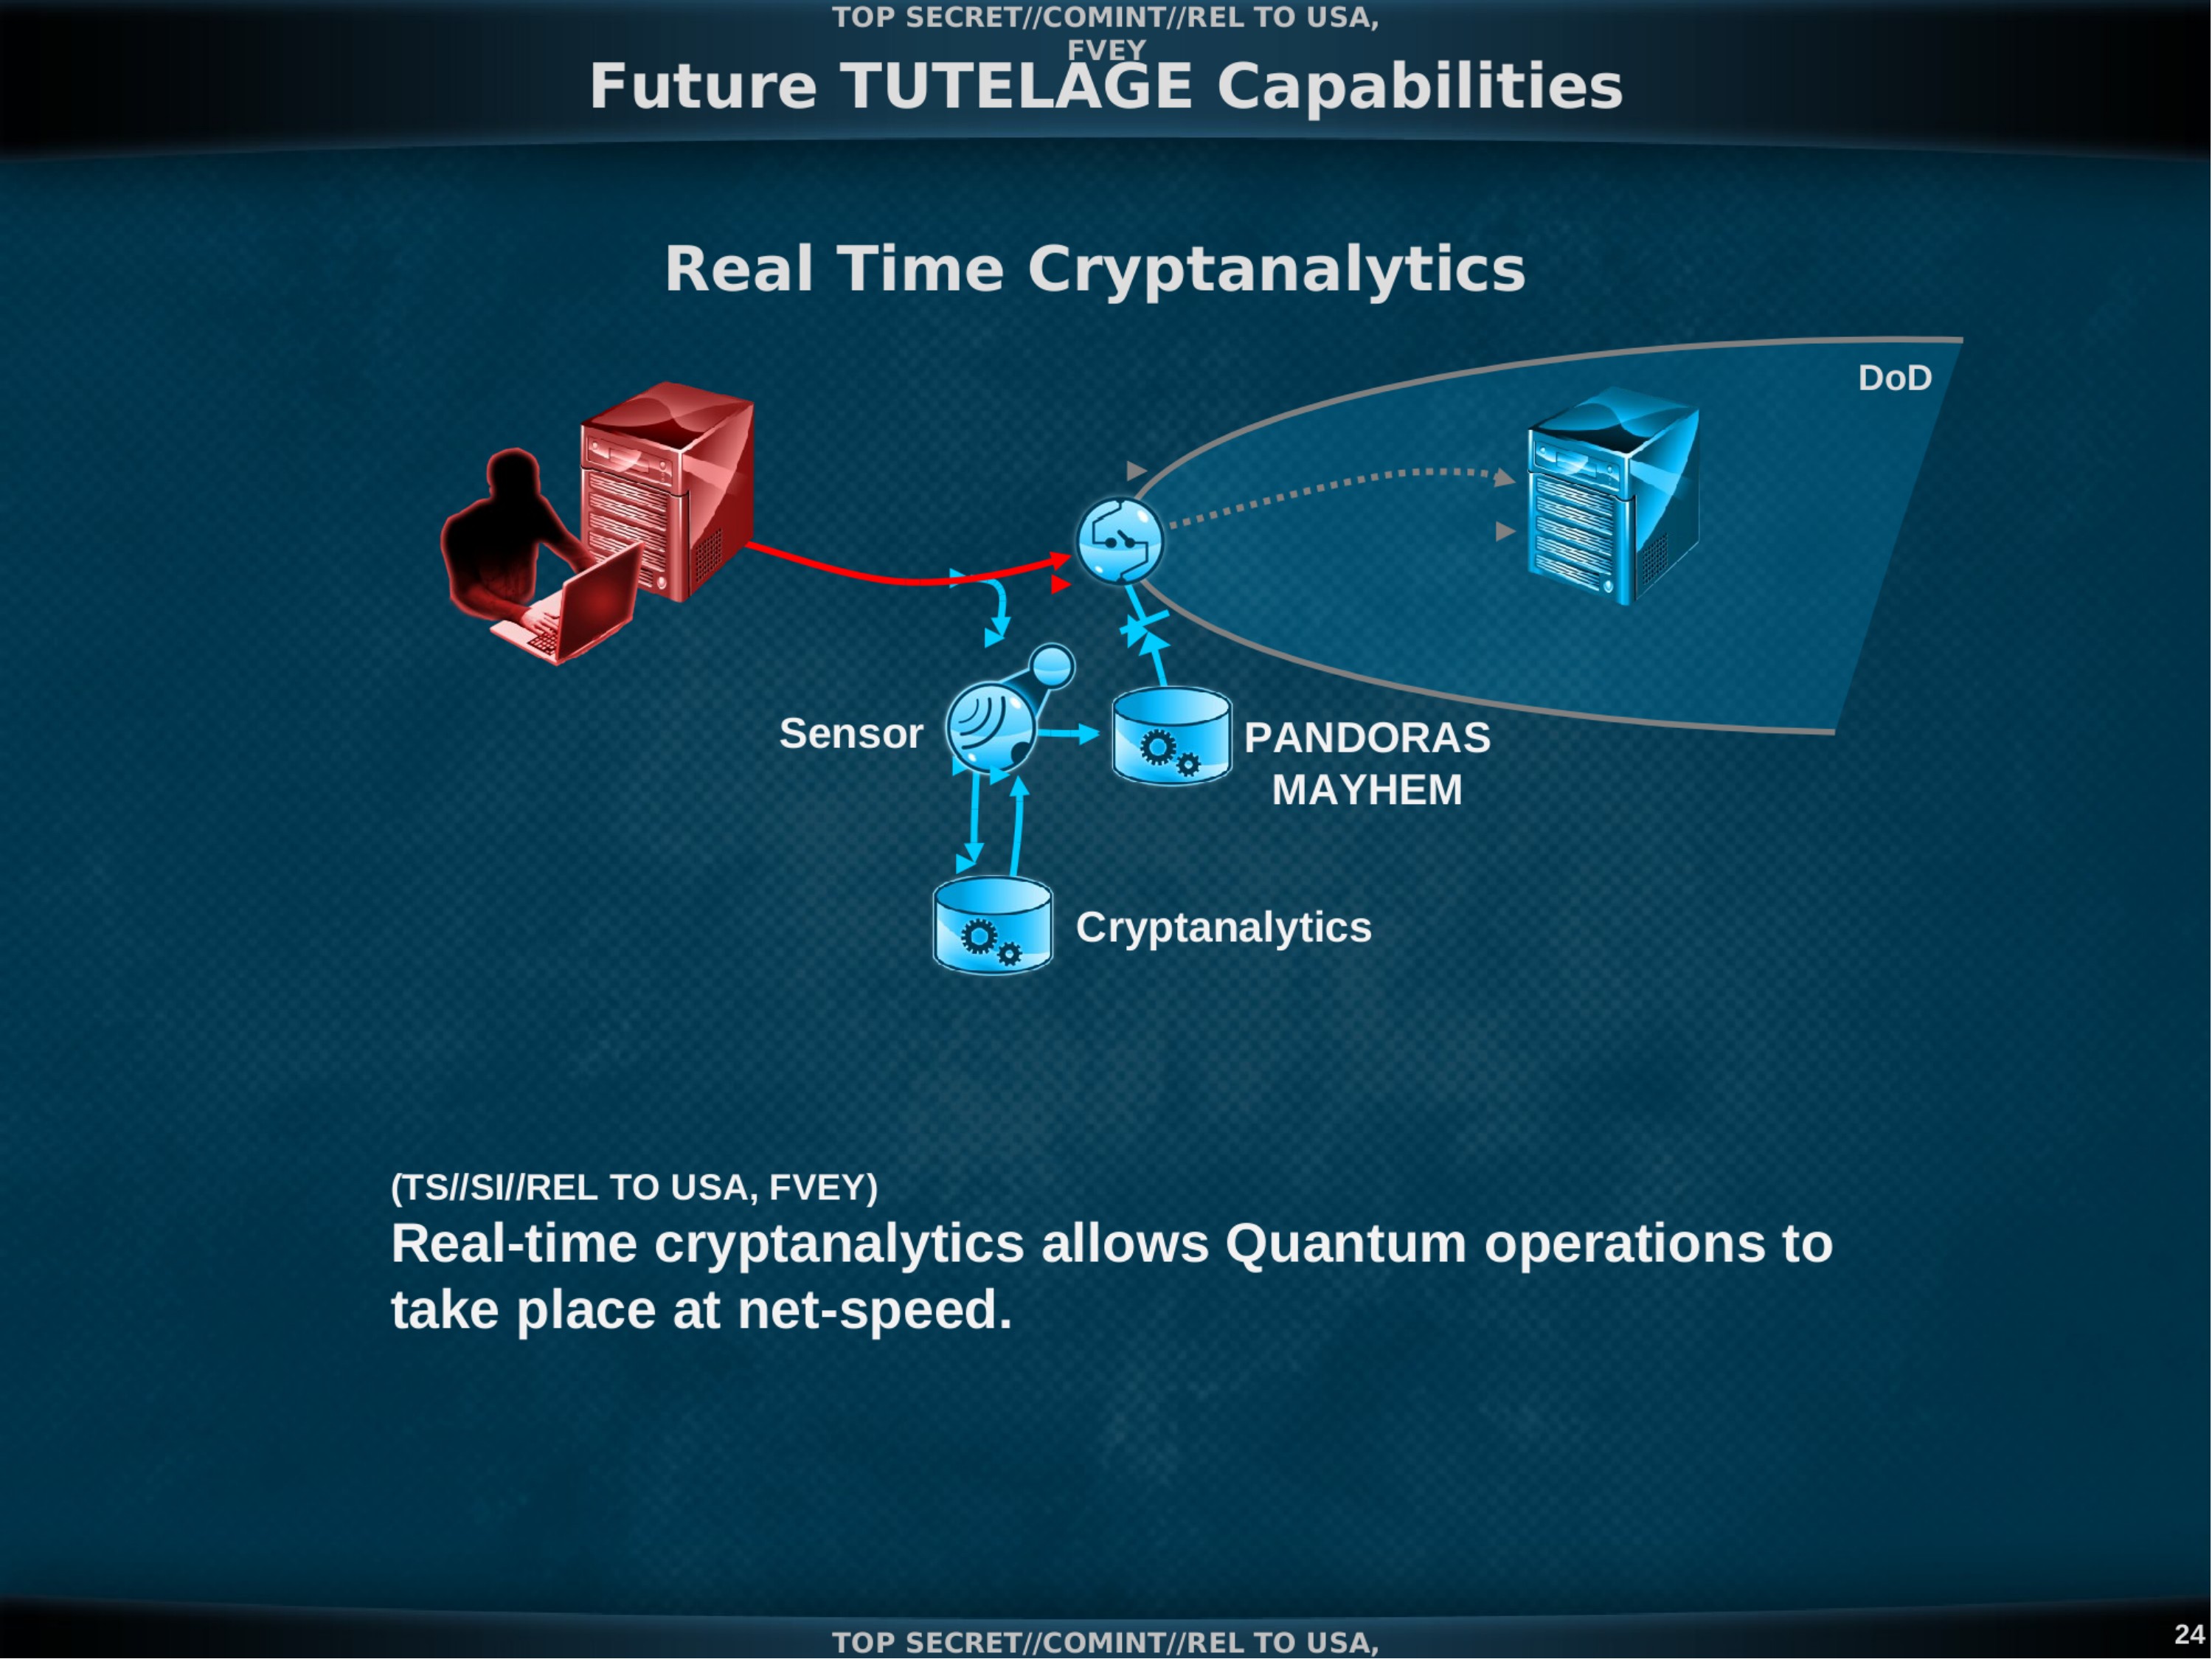
Real Time Cryptanalytics
- Sensor
- PANDORAS MAYHEM
- Cryptanalytics
- DoD
(TS//SI//REL TO USA, FVEY)
Real-time cryptanalytics allows Quantum operations to take place at net-speed.
TOP SECRET//COMINT//REL TO USA,
24
UNCLASSIFIED//FOUO
OPS SUCCESS STORIES
UNCLASSIFIED//FOUO
25
SECRET//REL TO USA, FVEY
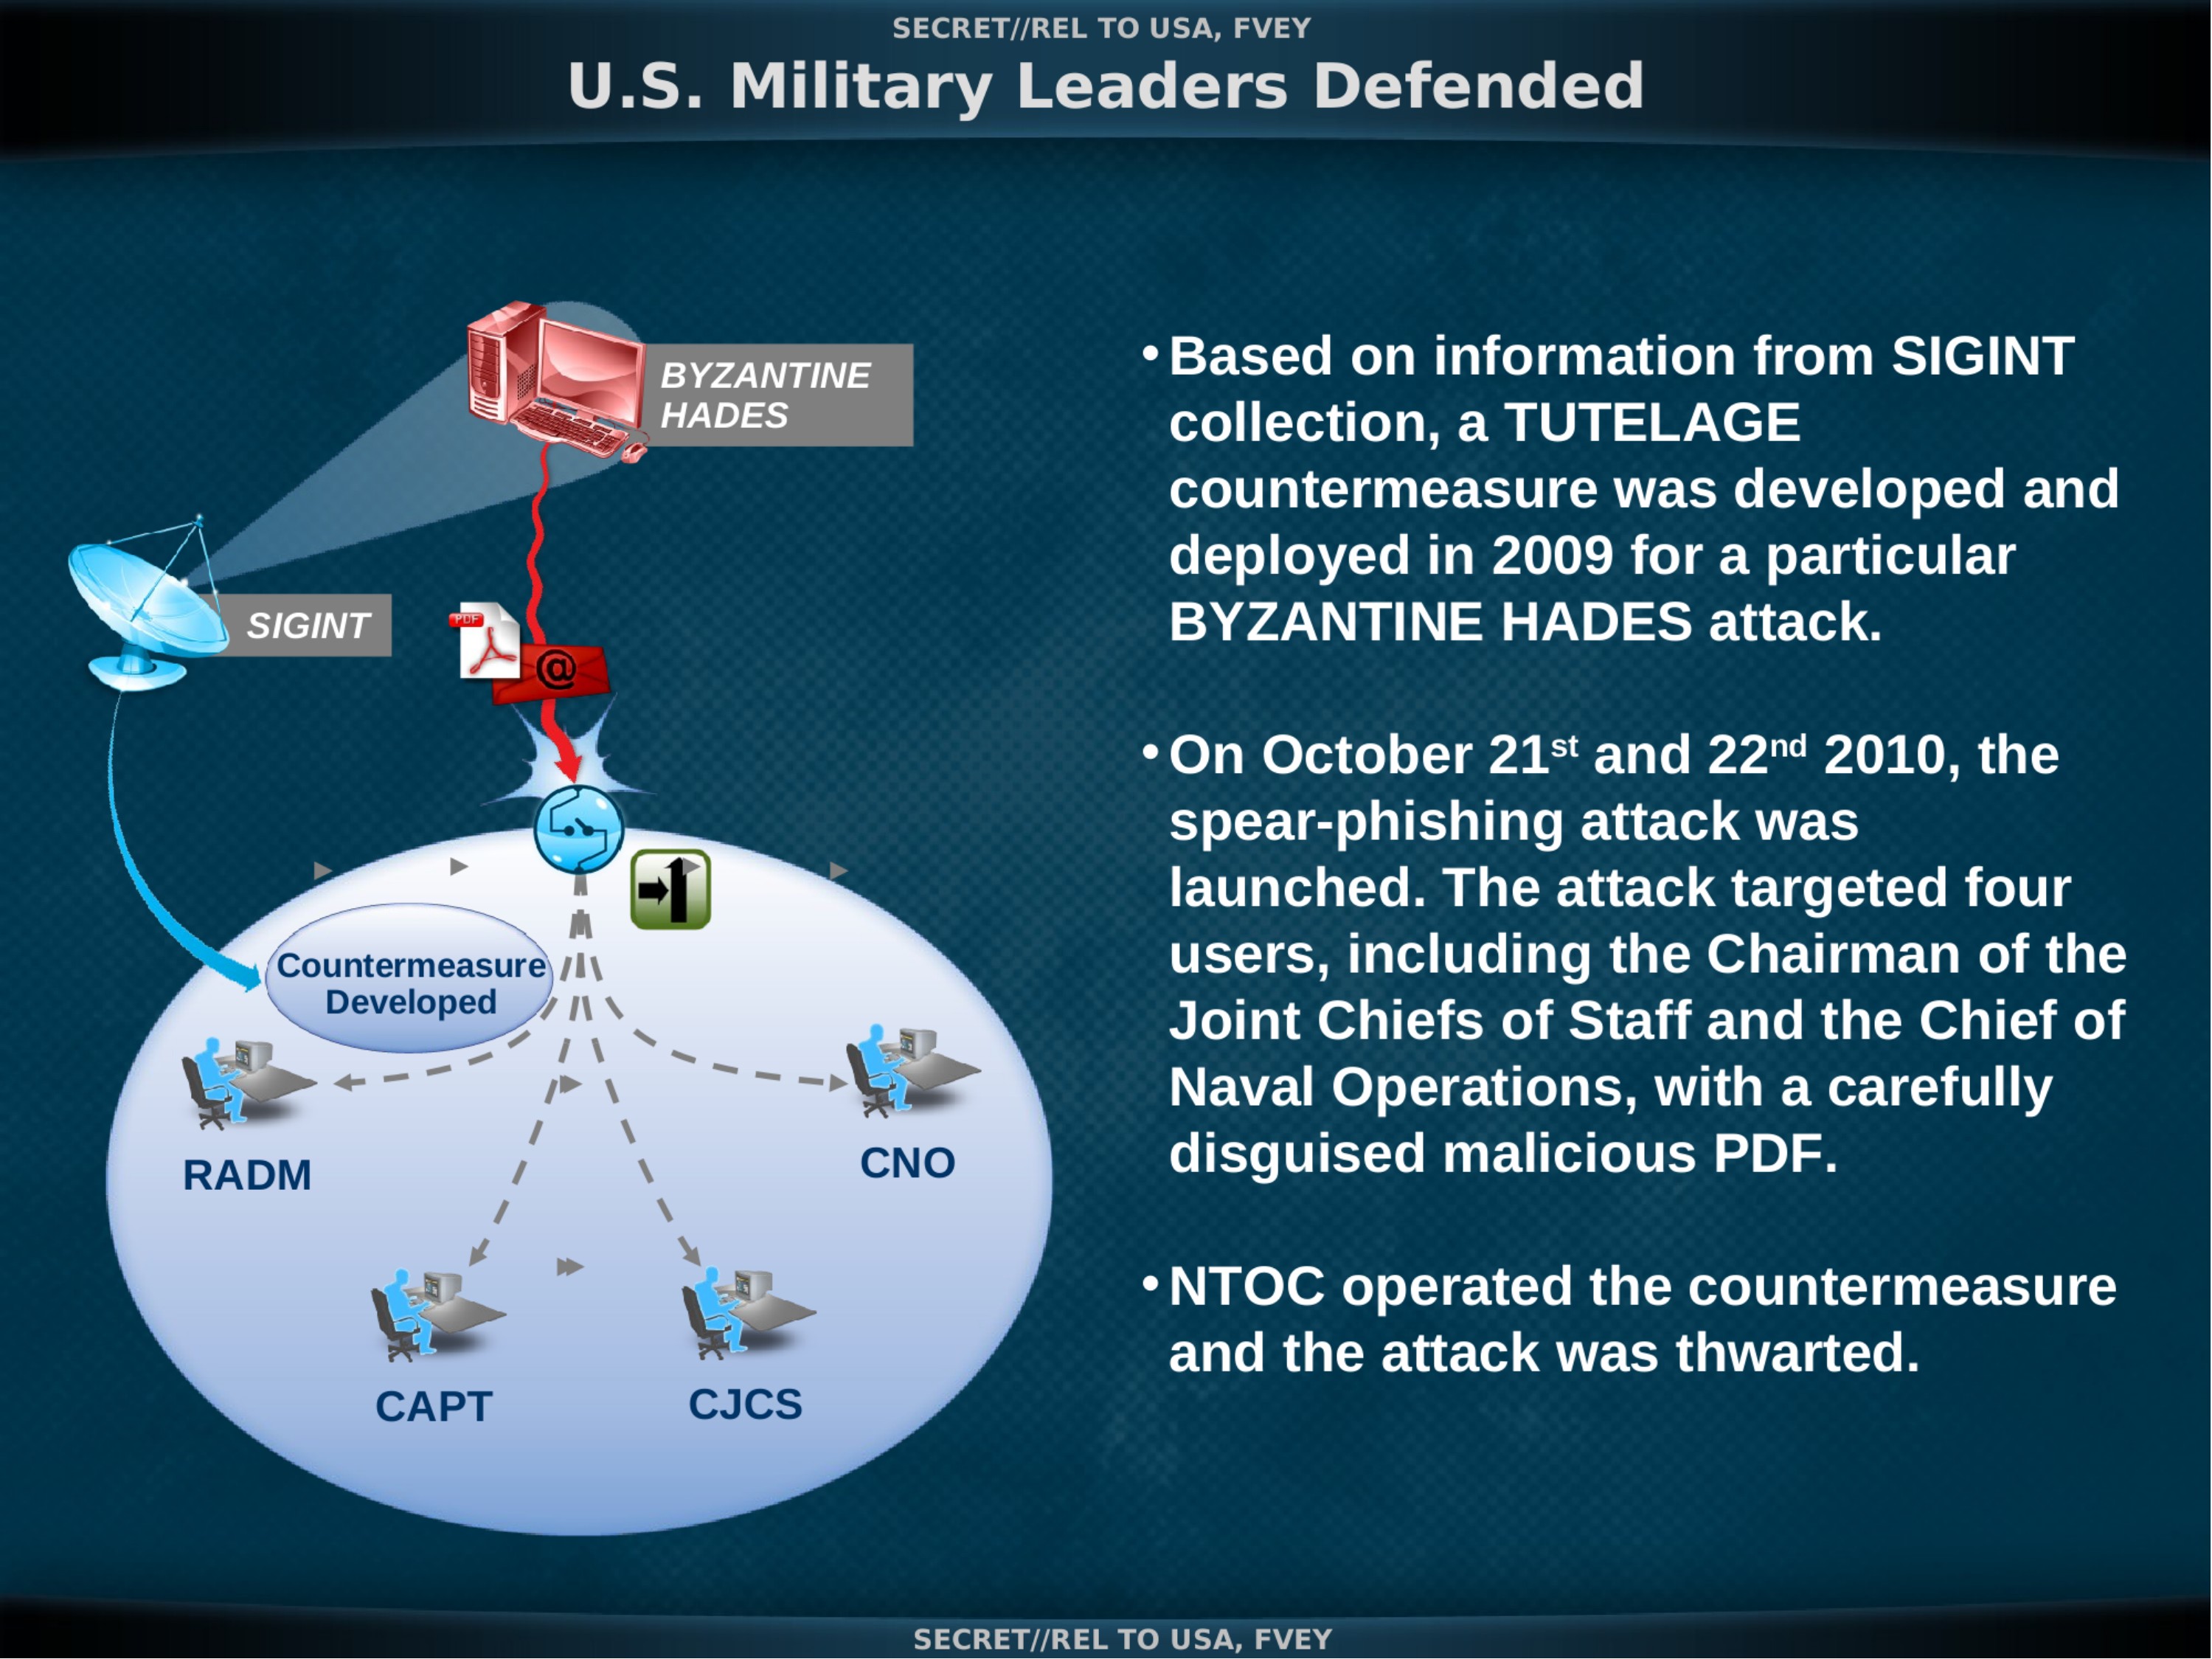
U.S. Military Leaders Defended
- SIGINT
- BYZANTINE HADES
- Countermeasure Developed
- RADM
- CAPT
- CJCS
- CNO
- Based on information from SIGINT collection, a TUTELAGE countermeasure was developed and deployed in 2009 for a particular BYZANTINE HADES attack.
- On October 21st and 22nd 2010, the spear-phishing attack was launched. The attack targeted four users, including the Chairman of the Joint Chiefs of Staff and the Chief of Naval Operations, with a carefully disguised malicious PDF.
- NTOC operated the countermeasure and the attack was thwarted.
SECRET//REL TO USA, FVEY
SECRET//REL TO USA, FVEY
WAG Attempts to Deliver Holiday Present to DoD
23 December
- NTOC-TX calls ops center advising of phishing campaign with “Merry Christmas” subject associated with WAG actors
- WAG actors attempted to use ZEUS malware to exfiltrate documents
- NTOC-TX did malware analysis and identified 2 new callback domains
- In < 3 hours, received CyberCommand approval and placed domains on DNS interdiction
30 December
- NTOC-TX notices new spike in WAG mail signature
- NTOC-TX discovers new callback domain
- In < 20 minutes, received approval and placed domain on DNS interdiction
- NTOC-W confirmed same malware from Xmas themed event
SECRET//REL TO USA, FVEY
27
TOP SECRET//COMINT//REL TO USA, FVEY
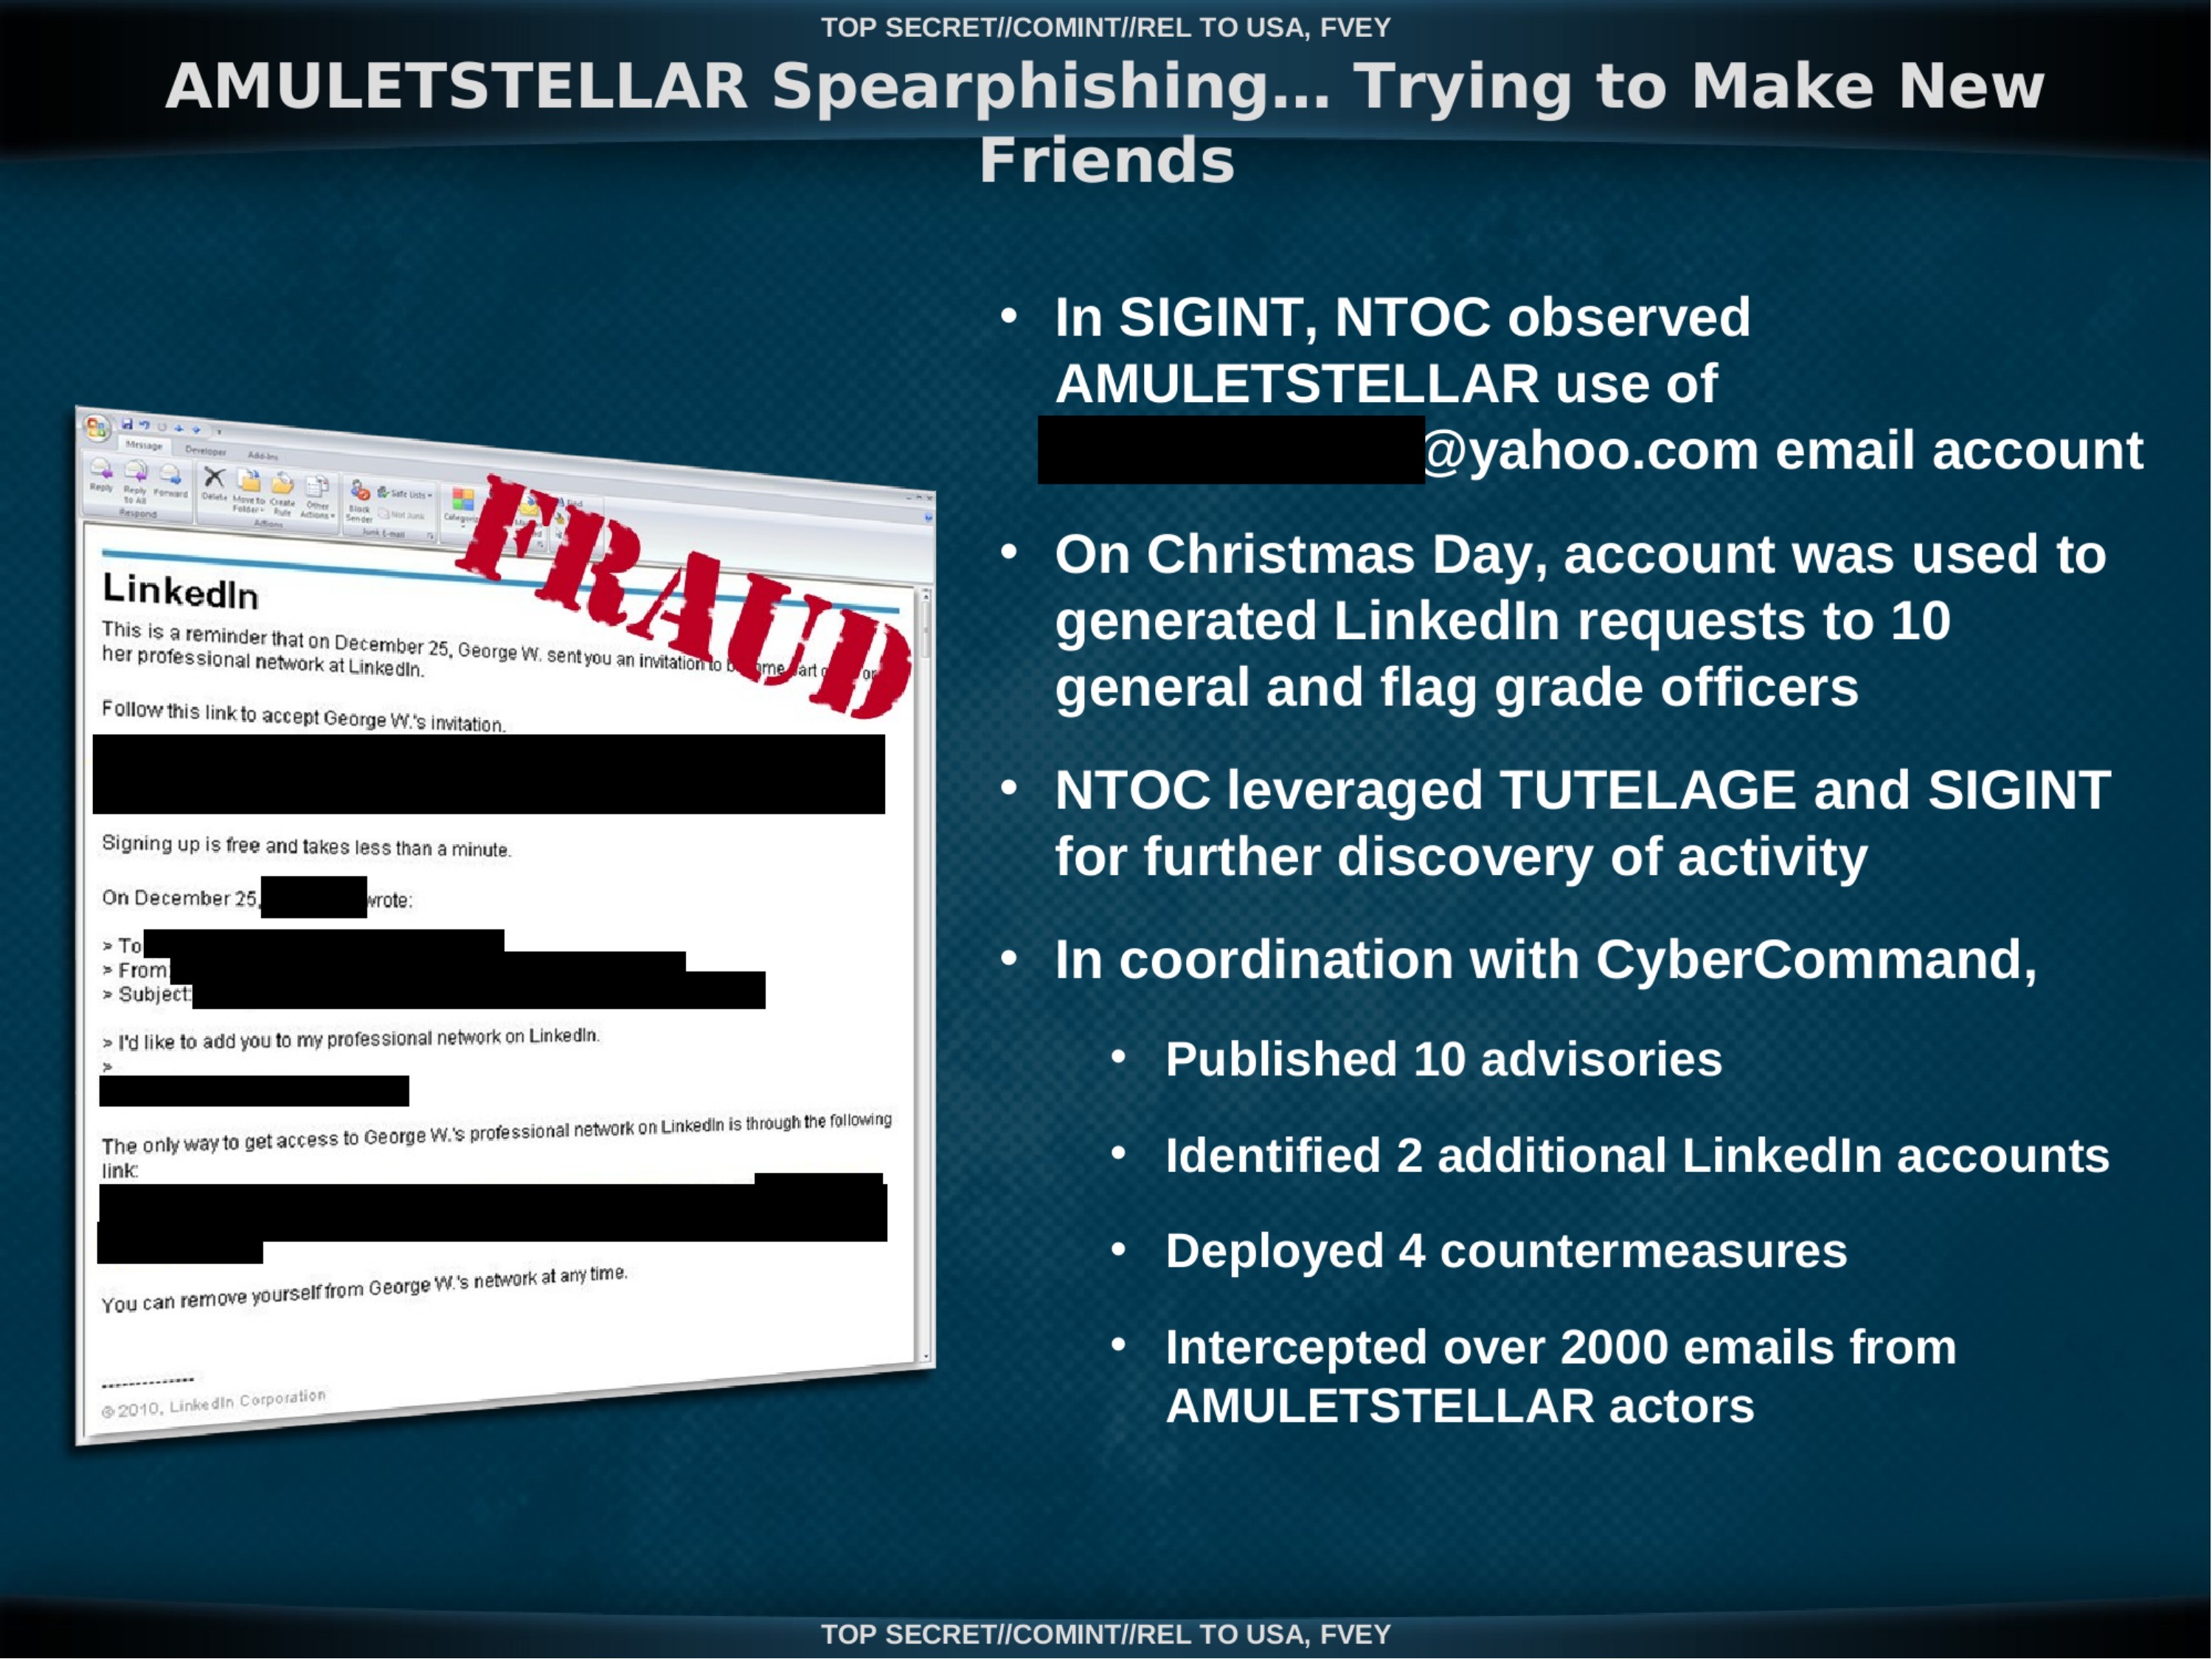
AMULETSTELLAR Spearphishing... Trying to Make New Friends
FRAUD
LinkedIn
This is a reminder that on December 25, George W. sent you an invitation to be her professional network at LinkedIn.
Follow this link to accept George W.'s invitation.
[REDACTED]
Signing up is free and takes less than a minute.
On December 25, [REDACTED] wrote:
> To[REDACTED]
> From[REDACTED]
> Subject:[REDACTED]
> I'd like to add you to my professional network on LinkedIn.
>
[REDACTED]

The only way to get access to George W.'s professional network on LinkedIn is through the following link:

[REDACTED]

You can remove yourself from George W.'s network at any time.
© 2010, LinkedIn Corporation
- In SIGINT, NTOC observed AMULETSTELLAR use of [REDACTED]@yahoo.com email account
- On Christmas Day, account was used to generated LinkedIn requests to 10 general and flag grade officers
- NTOC leveraged TUTELAGE and SIGINT for further discovery of activity
- In coordination with CyberCommand,
- Published 10 advisories
- Identified 2 additional LinkedIn accounts
- Deployed 4 countermeasures
- Intercepted over 2000 emails from AMULETSTELLAR actors
TOP SECRET//COMINT//REL TO USA, FVEY
SECRET//REL TO USA, FVEY
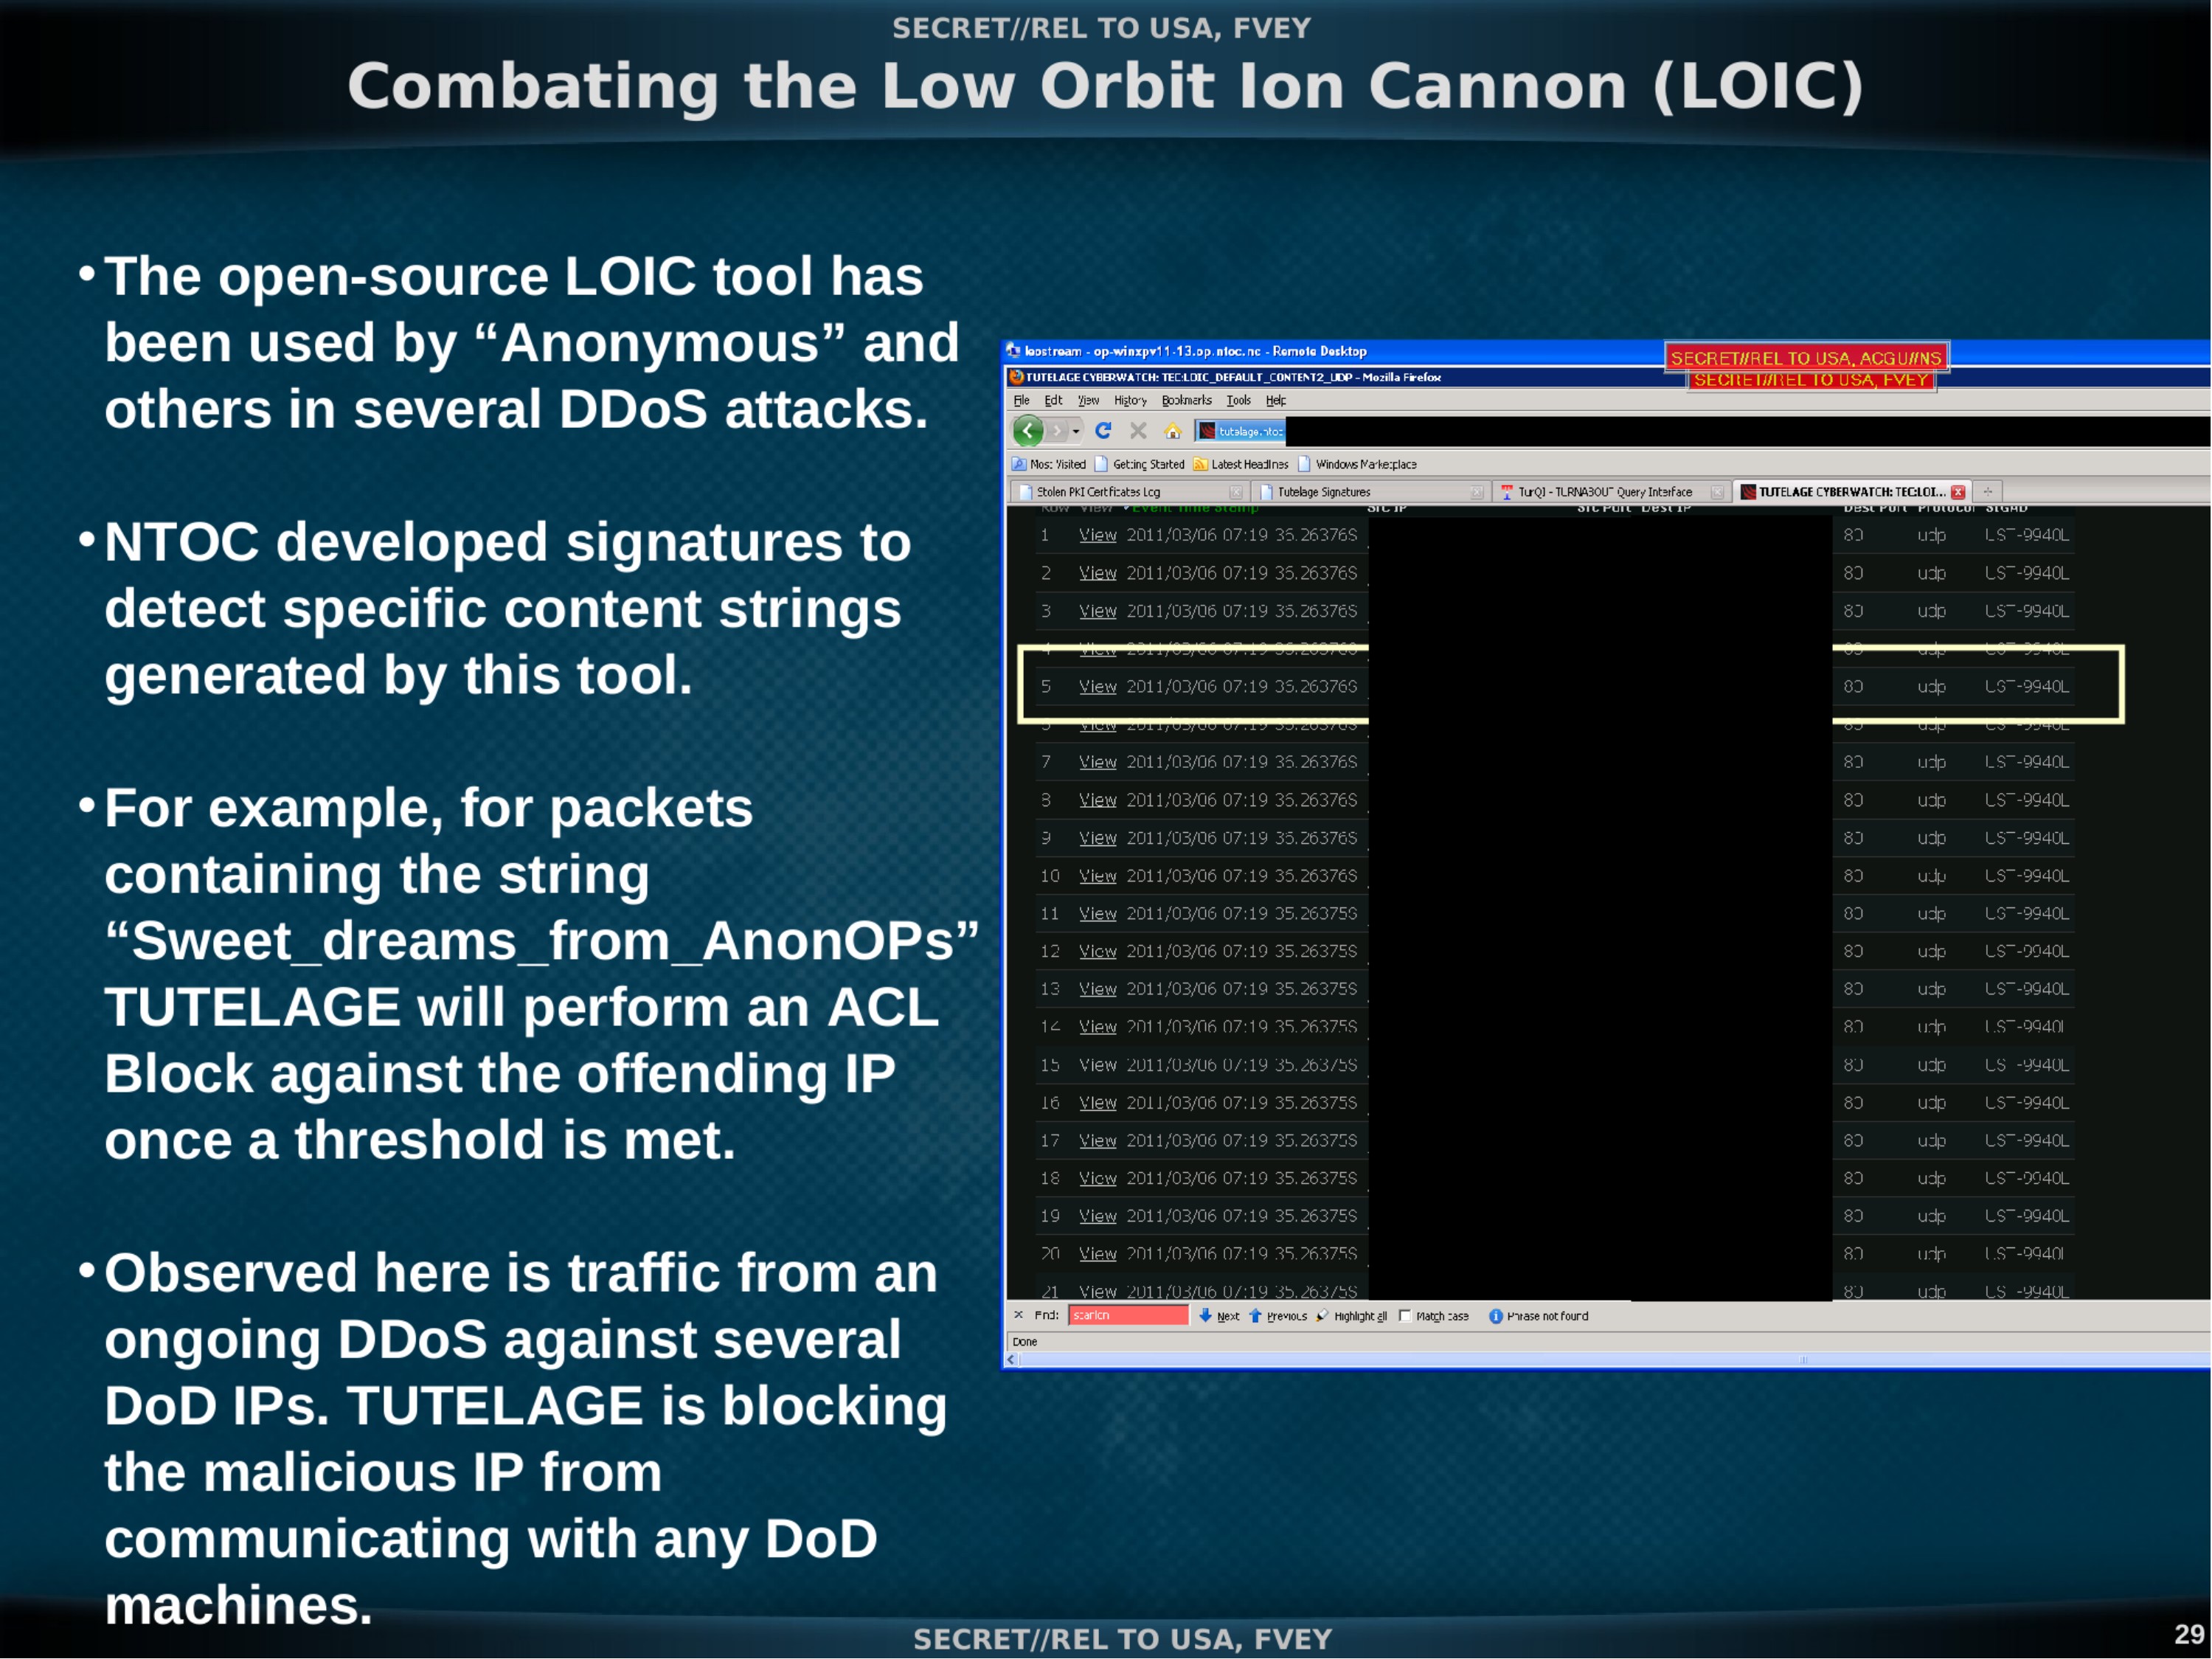
Combating the Low Orbit Ion Cannon (LOIC)
- The open-source LOIC tool has been used by “Anonymous” and others in several DDoS attacks.
- NTOC developed signatures to detect specific content strings generated by this tool.
- For example, for packets containing the string “Sweet_dreams_from_AnonOPs” TUTELAGE will perform an ACL Block against the offending IP once a threshold is met.
- Observed here is traffic from an ongoing DDoS against several DoD IPs. TUTELAGE is blocking the malicious IP from communicating with any DoD machines.
leostream - op-winxpv11-13.op.ntoc.nc - Remote Desktop

SECRET//REL TO USA, ACGU/NS

TUTELAGE CYBERWATCH: TEC:LOIC_DEFAULT_CONTENT2_UDP - Mozilla Firefox

SECRET//REL TO USA, FVEY

File Edit View History Bookmarks Tools Help

tutelage.ntoc[REDACTED]

Most Visited Getting Started Latest Headlines Windows Marketplace

Stolen PKI Certificates Log | Tutelage Signatures | TurQI - TURNABOUT Query Interface | TUTELAGE CYBERWATCH: TEC:LOI...

Row  View Event time stamp           SRC IP     SRC PORT    Dest IP   Dest Port Protocol SIGAD
1    View 2011/03/06 07:19 35.26376S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
2    View 2011/03/06 07:19 35.26376S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
3    View 2011/03/06 07:19 35.26376S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
4    View 2011/03/06 07:19 35.26376S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
5    View 2011/03/06 07:19 35.26376S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
6    View 2011/03/06 07:19 35.26376S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
7    View 2011/03/06 07:19 35.26376S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
8    View 2011/03/06 07:19 35.26376S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
9    View 2011/03/06 07:19 35.26376S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
10   View 2011/03/06 07:19 35.26376S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
11   View 2011/03/06 07:19 35.26375S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
12   View 2011/03/06 07:19 35.26375S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
13   View 2011/03/06 07:19 35.26375S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
14   View 2011/03/06 07:19 35.26375S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
15   View 2011/03/06 07:19 35.26375S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
16   View 2011/03/06 07:19 35.26375S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
17   View 2011/03/06 07:19 35.26375S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
18   View 2011/03/06 07:19 35.26375S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
19   View 2011/03/06 07:19 35.26375S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
20   View 2011/03/06 07:19 35.26375S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L
21   View 2011/03/06 07:19 35.26375S [REDACTED] [REDACTED] [REDACTED] 80        udp  USF-9940L

Find: scarlon Next Previous Highlight All Match Phrase not found
Done
SECRET//REL TO USA, FVEY
29
UNCLASSIFIED//FOUO
QUESTIONS?
UNCLASSIFIED//FOUO
30
Published in the Same Report
(10 of 34 documents)
-
Expanding Endpoint Operations SIDtoday [pdf]
Tailored Access Operations, NSA's elite hackers, are expanding their endpoint operations -- hacking directly into computers to steal information -- and are establishing the new endpoint operations remote operations center, scheduled to come online in the summer of 2005, that "is capable of managing and conducting endpoint operations on a scale that will dramatically expand collection." The physical office space of this new center will allow TAO to "grow from the current average of 20-25 of these operations per day to over 100 per day," and will allow TAO to increase the number of "active implants," or actively monitored pieces of malware, from 100-150 to thousands.
“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · The Intercept ↗ (2017-04-24) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
The ROC: NSA's Epicenter for Computer Network Operations SIDtoday [pdf]
The Remote Operations Center (ROC) conducts computer network operations against U.S. adversaries and foreign governments. Its motto is: "Your data is our data, your equipment is our equipment, anytime, any place, by any legal means."
The Intercept ↗ (2019-05-29) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
CSEC SIGINT Cyber Discovery: Summary of the current effort [pdf]
This document provides a overview of the Communications Security Establishment Canada (CSEC) cyber operations, detailing its SIGINT, CNE (Computer Network Exploitation), and cyber counterintelligence programs, including tools like WARRIORPRIDE, REPLICANTFARM, and EONBLUE for threat detection, anomaly discovery, and metadata production. It outlines operational procedures, analytic methodologies, and collaborative frameworks with domestic and Five Eyes partners for sharing intelligence, tipping/cueing, and integrating cyber and traditional counterintelligence efforts.
Programs: REPLICANTFARM · SLIPSTREAM · WARRIORPRIDE · DAREDEVIL · CHORDFLIER · NAMEDROPPER · WORMWOOD · OBELIX · SHEPHERD · CARBON · REGBACKUP · DOGHOUSE · WALKER · ALOOFNESS · BLAZINGANGEL · TINYWEB · QUIVERINGSQUAB · WINDO · DIESELRATTLE · WIDOWKEY · CIVETCAT · WINBEE · SSLINST · PULLEDPORK · EONBLUE · SNIFFLE · QUANTUM · XKEYSCORE · HALTERHITCH · FASTFLUX · DEADSEA · NSPACES · PPF · SSO · TKB“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “Communication Security Establishment's cyberwarfare toolbox revealed” - CBC News ↗ (2015-03-23) · “Documents Reveal Canada’s Secret Hacking Tactics” - The Intercept ↗ (2015-03-23) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Seglins, Dave · Hildebrandt, Amber · Pereira, Michael · Greenwald, Glenn · Gallagher, Ryan -
CNE End Point Requirements [pdf]
This NSA/GCHQ document outlines comprehensive requirements for an endpoint surveillance systems that enables analysts to systematically identify intelligence collection needs and discover appropriate tools for data extraction from compromised computers. The framework covers capabilities for remote data collection, cross-platform intelligence integration, query functions, tasking procedures, and visualization tools across implanted networks.
Programs: STARGATE · LOOKING GLASS · QUANTUM · GOLDENEYE · XKEYSCORE · MARINA · JTRIG · BROADOAK · UTT · GLOBALREACH · GLOBALSURGE · THUGGEE · EREPO · DANCINGBEAR · HAUSTORIUM · SHAREOWN · MUTANTBROTH · MOONRAKER · CARBONROD · RUFFLE · ROCKOPERA · QUINCEY · ECLIPSE · MUGSHOT · HIGHNOTE · UDAQ2 · EKB · TURBINE · ACNO · FLAMECARPET · FUMECUPBOARD · JACKPOT · SLIPSTREAM · B13B · PSC · QUINCY · DAREDEVIL · ROADBED -
QUANTUMTHEORY (2010 SIGINT Development Conference) [pdf]
This 2010 NSA presentation reveals QUANTUMTHEORY, a suite of "man-on-the-side" network attack technologies that enable real-time injection and manipulation of TCP/IP connections through passive surveillance infrastructure. The system encompasses multiple specialized attack techniques including HTML redirection, DNS hijacking, botnet takeover, and database injection, deployed at Five Eyes surveillance sites worldwide.
Programs: QUANTUMTHEORY · TRAFFICTHIEF · TURMOIL · TURBINE · QUANTUM · NINJANIC · ISLANDTRANSPORT · SURPLUSHANGER · DAREDEVIL · STRAIGHTBIZARRE · QUANTUMINSERT · QUANTUMSKY · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMDNS · QUANTUMBOT2 · QUANTUMCOPPER · QUANTUMMUSH · HUFFMUSH · QUANTUMSPIM · QUANTUMSQUEEL · QUANTUMSQUIRREL · INCENSOR · SMOKEYSINK · SARATOGA · QUANTUMDEFENSE · TURBULENCE“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
-
TURBULENCE - APEX - Active/passive Exfiltration [pdf]
This 2009 NSA presentation details APEX (Active/Passive Exfiltration), a TURBULENCE program component that combines passive collection infrastructure with active TAO implants to exfiltrate VPN and VoIP traffic from deep within target networks back to NSA collection systems. The system uses the FASHIONCLEFT protocol to tunnel captured packets through compromised routers and network devices, enabling decryption of VPN tunnels and collection of voice communications that would otherwise be invisible to passive surveillance.
Programs: TURBULENCE · TURMOIL · HAMMERSTEIN · HAMMERCHANT · FASHIONCLEFT · TUTELAGE · TURBINE · TRAFFICTHIEF · XKEYSCORE · ANALYTICS · PRESSUREWAVE · TOYGRIPPE · POISONNUT · FLAXENPRECEPT · FOGYNULL · FUNNELAPS · SHELLGREY · METROTUBE · VINYLSEAT · OLYMPUS · UNITEDRAKE · FIGBUILD · SURPASSPIN · ROOTKNOT · OPTICPINCH · SEAGULFARO · TREBLECLEF · CONVEY · PINWALE · SWEEPFORWARD · QUANTUM · KEYCARD · ASDF · TUBE · PUZZLECUBE · WEALTHYCLUSTER2 · COALSHOVEL · HAMMERMILL · ISLANDTRANSPORT · FASCIA · TURBINIE · APEX · PPF · AEG · FIP · SSO · PICARESQUE · PSP · IVE · PSC · CHIMNEYPOOL · CORESSC · FLASHHANDLE · IBRIDGE · CORALREEF · VAO · NUCLEON · PIQBLADE“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Gallagher, Ryan · Greenwald, Glenn -
Analytic Challenges from Active-Passive Integration [pdf]
This NSA presentation examines metadata attribution challenges arising when active TAO implants exfiltrate traffic through passive TURMOIL collection infrastructure, creating conflicts where intercepted data carries dual classification markings, case notations, and legal authorities from both collection systems. The briefing highlights how existing databases and analytic tools were not designed to handle traffic with two simultaneous sets of metadata parameters, requiring enterprise-wide solutions to consistently attribute and track actively-shaped intelligence collection.
Programs: BRAVENICKEL · HAMMERMILL · APEX · MARINA · TURMOIL · PRESSUREWAVE · METROTUBE · TOYGRIPPE · HAMMERSTEIN · HAMMERSTONE · METAWAVE · TURBULENCE · SSO -
The FASHIONCLEFT Protocol [pdf]
This October 2008 NSA technical specification details FASHIONCLEFT, the encryption and exfiltration protocol used by TAO implants to securely tunnel captured network packets from compromised devices back to the NSA's Common Data Receptor using layered RSA and RC6 encryption with authentication. The document addresses technical integration challenges of implementing FASHIONCLEFT packet reception within TURMOIL's passive collection infrastructure, particularly cache buffering requirements and metadata handling for exfiltrated traffic.
Programs: FASHIONCLEFT · FOGYNULL · FUNNELAPS · SHELLGREY · TURMOIL · SURPASSPIN · PUZZLECUBE · FLASHHANDLE · HAMMERCHANT · AEG · PPF · ISLANDTRANSPORT -
Moving Data Through Disconnected Networks - Delay-Tolerant Networking and the IC [pdf]
This June 2012 NSA Laboratory for Telecommunications Sciences presentation details Delay-Tolerant Networking (DTN) applications for surveillance operations, including covert communications in denied areas, data exfiltration from isolated networks, unwitting data mules, and integration with TAO's CHIMNEYPOOL implant framework. The document reveals R4 development of FUZZYLINT, an ultra-lightweight DTN implementation designed to enable multi-hop exfiltration from implants without requiring direct physical access.
People: Vahdat, Amin · Becker, David · Juang, Philo · Oki, Hidekazu · Wang, Yong · Martonosi, Margaret · Peh, Li-Shiuan · Rubenstein, Daniel · Grossglauser, Matthias · Tse, David N. C. · Fall, Kevin · Shah, Rahul C. · Roy, Sumit · Jain, Sushant · Brunette, Waylon · Lindgren, Anders · Doria, Avri · Schelen, Olov · Small, Tara · Haas, Zygmunt J. · Zhao, Wenrui · Ammar, Mostafa · Zegura, Ellen · Ginzboorg, Philip · Kärkkäinen, Teemu · Nagata, Akira · Lenders, Vincent · Legendre, Franck · May, Martin · Karlsson, Gunnar · Du, Bowei · Demmer, Michael · Brewer, Eric · Ott, Jörg · Pitkänen, Mikko Juhani · Han, Bo · Hui, Pan





Related Documents
-
BYZANTINE HADES: An Evolution of Collection [pdf]
A classified NSA SIGINT briefing from 2010 describes “BYZANTINE HADES,” a collection of Chinese computer network exploitation activities, with a focus on the BYZANTINE CANDOR actor set and U.S. efforts to analyze, attribute, and counter those intrusions. The document details targeting patterns, technical tradecraft, and a TAO-led counterintelligence operation that successfully penetrated the attackers’ infrastructure and personal systems.
Programs: BYZANTINEHADES · BYZANTINECANDOR · BYZANTINERAPTOR · BYZANTINEANCHOR · BISHOPKNIGHT · BYZANTINEVIKING · MAVERICKCHURCH · BISHOP · BYZANTINETRACE · DIESELRATTLE · BYZANTINEFOOTHOLD · BYZANTINEPRAIRIE · SEEDSPHERE · CARBONPEPTIDE · TITANRAIN · PINWALE · XKEYSCORE · CROSSBONES · TUNINGFORK · ARROWECLIPSE · CUTEBOY · POPROCKS · BYZANTINE -
TRANSGRESSION Overview for Pod58 [pdf]
The TRANSGRESSION overview describes an NSA capability focused on discovering, decrypting, and exploiting foreign computer network exploitation activity to support fourth-party collection, TAO cyber operations, and network defense missions across NSA and FVEY partners.
Programs: TRANSGRESSION · MAKERSMARK · BYZANTINEHADES · VOYEUR · WALKERBLACK · WALKERRED · CROWNROYAL · CROWNPRINCE · SHEPHERD · ZEBEDEE · MAVERICK CHURCH · POPROCKS · GHOSTRECON · NIGHTTRAIN · SHADOWDRAGON · RECORDER · PLAIDDIANA · INCAADAM · TWEEZERS · SNOWGLOBE · WIDOWKEY · SUPERDRAKE · XKEYSCORE · POLARSTARKEY · TUNINGFORK · SCISSORS · PINWALE · CLOUD · BYZANTINEFOOTHOLD · ADJUTANTVENTURE · RAPTORROLEX · RAPTORJOY · RAPTORSAD · BYZANTINERAPTOR -
HIDDENSALAMANDER - Alerting and Characterization of Botnet Activity in TURMOIL [pdf]
This NSA briefing describes HIDDENSALAMANDER, a TURMOIL component that detects, tracks, and characterizes botnet command-and-control traffic on passive collection sensors worldwide, generating enriched metadata about bot herders, infected machines, attack commands, and malware families while providing low-latency defensive alerts when botnet activity involves high-value targets or protected networks. The system extends beyond traditional signature matching by decrypting Zeus RC4-encrypted traffic, extracting payload details like target IPs and DDoS commands, tracking C2 servers across multiple sessions, and categorizing botnet lifecycle stages (configuration, infection, reconnaissance, C&C communication, attack, exfiltration) to support both offensive attribution and defensive response.
Programs: HIDDENSALAMANDER · TURMOIL · CLOUDSHIELD · NETEZZA · TUTELAGE · GMPLACE · RONIN · CYBERCLOUD · MARINA · GHOSTMACHINE · QBOT · ASDF · MARIPOSA · XKEYSCORE · GOGADGET · TURQI · TRAFFICTHIEF · FALLOUT · POUNDSAND · BLUESMOKE · AEG · TURNABOUT · QUANTUMBOT -
TURBULENCE - APEX - Active/passive Exfiltration [pdf]
This 2009 NSA presentation details APEX (Active/Passive Exfiltration), a TURBULENCE program component that combines passive collection infrastructure with active TAO implants to exfiltrate VPN and VoIP traffic from deep within target networks back to NSA collection systems. The system uses the FASHIONCLEFT protocol to tunnel captured packets through compromised routers and network devices, enabling decryption of VPN tunnels and collection of voice communications that would otherwise be invisible to passive surveillance.
Programs: TURBULENCE · TURMOIL · HAMMERSTEIN · HAMMERCHANT · FASHIONCLEFT · TUTELAGE · TURBINE · TRAFFICTHIEF · XKEYSCORE · ANALYTICS · PRESSUREWAVE · TOYGRIPPE · POISONNUT · FLAXENPRECEPT · FOGYNULL · FUNNELAPS · SHELLGREY · METROTUBE · VINYLSEAT · OLYMPUS · UNITEDRAKE · FIGBUILD · SURPASSPIN · ROOTKNOT · OPTICPINCH · SEAGULFARO · TREBLECLEF · CONVEY · PINWALE · SWEEPFORWARD · QUANTUM · KEYCARD · ASDF · TUBE · PUZZLECUBE · WEALTHYCLUSTER2 · COALSHOVEL · HAMMERMILL · ISLANDTRANSPORT · FASCIA · TURBINIE · APEX · PPF · AEG · FIP · SSO · PICARESQUE · PSP · IVE · PSC · CHIMNEYPOOL · CORESSC · FLASHHANDLE · IBRIDGE · CORALREEF · VAO · NUCLEON · PIQBLADE“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Gallagher, Ryan · Greenwald, Glenn -
Fourth Party Opportunities [pdf]
This presentation document explains how NSA identifies, prioritizes, and exploits “fourth party” opportunities by passively or actively leveraging foreign computer network exploitation operations, including victim stealing and tool repurposing, to collect intelligence without initiating original intrusions.
Programs: VOYEUR · UIS · PINWALE · YNKE · TUNINGFORK · DIRTSHED · SEEKER · CLOUD · ABR · SILVERBOLT · DEADSEA · XKEYSCORE · BYZANTINERAPTOR · HAWALA · ZEBEDEE · DATAFLURRY · ECLECTICPLOT · HAPPYFOOT · BLUESMOKE · CROSSBONES2 · CYBERQUEST · VICDB · PLAIDDIANA · TRANSGRESSION



