Classification: TOP SECRET 823 documents
Search documents matching “TOP SECRET” →Each document's classification level, as component values. If a document contains multiple classifications, the highest is used here.
Graphs
By document date (14 years)
By published date (9 years)
By Banner
Refine (combine with another filter, via search)
Sort: Title
Documents
-
International Incident Avoided, Thanks to Intelligence SIDtoday [pdf]
Israel was concerned that a North Korean ship was carrying missile-related cargo for Syria or Iran. The U.S. arranged for Egyptians to inspect the cargo and convinced Israel that the ship wasn’t worth boarding, averting a “politically sensitive incident.”
The Intercept ↗ (2018-08-15) -
Internet Anonymity 2011 [pdf]
A TOP SECRET NSA presentation from 2011 providing a comprehensive survey of Internet Anonymity Technologies (IAT) — covering HTTP proxies, VPN anonymity providers, multi-hop networks including Tor and JAP, anonymous remailers and circumvention tools — alongside NSA's capabilities and limitations against each, including XKEYSCORE fingerprints for VPN identification, the PARTNERSNIPPET Tor deanonymisation team, GOLDENFORTIN Netflow data, and a candid assessment that Tor offers "no passive exploitation."
Programs: FOXTRAIL · NKB · NACIRONIN · PONTENTPOTABLES · RONIN · XKEYSCORE · PARTNERSNIPPET · GOLDENFORTIN · SNAPEPeople: Heap, Austin -
Interns Now Contributing from Day One SIDtoday [pdf]
An intelligence analysis intern recounts how, due to high volumes of data, he was thrown right into “prosecuting critical targets within weeks of arriving” and learned that the Signals Intelligence Directorate is “not quite satellites, but not really Dilbert either.”
Marking: TOP SECRETPrograms: FOLLOWTHEMONEYThe Intercept ↗ (2018-08-15) -
Interview with... Fran Fleisch, China & Korea (S2B) Production Manager SIDtoday [pdf]
A 24-year NSA veteran describes her career as an analyst on missions involving the Soviet Union, Korea, and China.
The Intercept ↗ (2016-12-07) -
INTOLERANT – Who Else Is Targeting Your Target? Collecting Data Stolen by Hackers – SIDtoday SIDtoday [pdf]
A TOP SECRET SIDToday article from Menwith Hill Station describing how NSA and CSEC discovered and began exploiting INTOLERANT — a sophisticated email-stealing hacking operation targeting Indian diplomats, Central Asian diplomats, Chinese human rights defenders, Tibetan pro-democracy activists, Uighur activists and European officials — by intercepting the stolen emails as they transited satellite links, a technique internally called "fourth party collection" or "outsourcing SIGINT."
Programs: INTOLERANT -
Intro to the VPN Exploitation Process [pdf]
NSA introduction to the VPN exploitation process from September 2010, presented by the OTP VPN Exploitation Team, covering the full workflow from initial collection through to sustained decryption of IPSec, PPTP, SSL and SSH traffic, with named exploitation successes including airlines, diplomatic missions, banks and intelligence services across Iran, Jordan, Russia, Turkey, Pakistan, Afghanistan, Somalia, Indonesia and Mexico.
Programs: BLEAKINQUIRY · TOYGRIPPE · XKEYSCORE · MAILORDER · CORALREEF · VULCANDEATHGRIP · SCISSORS · TURTLEPOWER · PINWALE · FOURSCORE · CADENCE · UTT · VULCANMINDMELD · CAPRIOS · AGILITY · NKB · FOLLOWTHEMONEY -
Introduction to BADDECISION [pdf]
This presentation details the use of the NSA program BADDECISION, which is a computer network exploitation tool (CNE) that uses a frame injection technique to redirect the target client to a FOXACID server.
-
Introduction to Context Sensitive Scanning with X-KEYSCORE Fingerprints [pdf]
This May 2010 NSA training document introduces XKEYSCORE's context-sensitive scanning capabilities using "fingerprints"—customizable detection rules that allow analysts to surgically target specific types of Internet traffic without needing prior knowledge of email addresses or other strong selectors, using over 70 unique contexts to identify patterns in communications and behaviors.
-
Introduction to WLAN / 802.11 Active CNE Operations [pdf]
This NSA powerpoint introduces computer network exploitation (CNE) criteria and assesment as well as active CNE operations. It also introduces the FOXACID program, which is a program to deliver content based exploits to web browsers.
-
Introduction to XKS Application IDs and Fingerprints [pdf]
This August 2009 NSA training document introduces XKEYSCORE's Application IDs (AppIDs) and Fingerprints system, explaining how metadata tags are automatically applied to intercepted sessions to identify and categorize different types of Internet traffic, applications, and behaviors, evolving through four generations from simple keyword matching to sophisticated code-based metadata extraction.
-
iPhone target analysis and exploitation with unique device identifiers [pdf]
A GCHQ technical paper from November 2010 describing iPhone target analysis and exploitation using the QUANTUM system — covering UDID-based target tracking and correlation across MUTANT BROTH and AUTOASSOC, a Safari PDF exploit delivering WARRIORPRIDE implants to target iPhones via QUANTUM redirection, and a confirmed successful exploitation of a jailbroken target phone yielding address book, SMS, call logs, notes, WiFi logs, browser history and images.
Programs: QUANTUM · DEBITCARD · AUTOASSOC · HARDASSOC · MUTANTBROTH · BROKER · HANDEX · WARRIORPRIDE · ABSOLINEEPILSON · BROADOAK · SOLARSHOCK · BLACKHOLE · SHORTSHEET · XKEYSCORE · MARINA · LOOKINGGLASS · OVERLIT · SLIDE · SEP · PRESTON · WHIPSAW · CROWNPRINCE · CORINTH · MVR · SOCIALANTHROPOID -
IR.21 – A Technology Warning Mechanism [pdf]
This 2010 TOP SECRET NSA briefing defines the IR.21 roaming document as a critical tool for "horizon scanning" and "forecasting" global telecommunications shifts. The document outlines how the NSA uses these technical files to proactively identify emerging 3G and 4G technologies, pinpointing vulnerabilities for exploitation before new systems are even fully deployed.
-
Iran Day - Aiming for High-Hanging Iranian 'Fruit' SIDtoday [pdf]
A one-day conference on Iran, identified as one of the NSA’s four missions “warranting a specific Mission Manager,” touched on Iran’s view of itself as the leader of Shia Islam, its nuclear proliferation, and its support to terrorism.
The Intercept ↗ (2018-08-15) -
Iran – Current Topics, Interaction with GCHQ [pdf]
This NOFORN top secret April 2013 NSA document, shows how Iran significantly improved its offensive cyber capabilities by learning from cyberattacks against it, such as the April 2012 attack on its own oil industry, subsequently launching its own destructive attacks against Saudi Aramco and U.S. financial institutions.
-
Iraqis Vote for First Permanent Parliament -- A Report from Baghdad SIDtoday [pdf]
A report from the first Iraqi parliamentary election, which — in addition to extensive, U.S.-backed logistics and security support — received 24/7 signals intelligence coverage from a dedicated NSA team.
People: Hussein, SaddamThe Intercept ↗ (2018-08-15) -
Is It the End of the SIGINT World as We Have Come to Know It? [pdf]
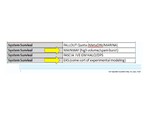
Two excerpts from a 2012 NSA presentation titled "Is It the End of the SIGINT World as We Have Come to Know It?" prepared by a member of the Large-Access Exploitation Group. The table excerpt lists MAINWAY among the systems at highest risk of being overwhelmed by the volume of data the agency was ingesting. The diagram excerpt shows MAINWAY feeding into the Graph-in-Memory (alongside WESTERNSTAR), illustrating how MAINWAY's continuous contact-chaining pushed its precomputed results into the in-memory graph database that analysts actually queried.
Programs: FALLOUT · METADNI · MARINA · MAINWAY · FASCIA · GMHALO · DPS · EKS · WESTERNSTAR · GRAPH-IN-MEMORY -
Is NSA Going Deaf? What Is 'Golf Cart Reporting'? -- An Interview With REDACTED SIDtoday [pdf]
SIDtoday interviews the deputy chief of the Middle East and North Africa product line. His team faces a personnel shortage and has to creatively onboard new staff who receive little training. He believes that new communications technology presents an advantage to the NSA, as the agency can spy on more intimate, firsthand communications from targets.
Programs: VOICESAILThe Intercept ↗ (2018-03-01) -
Is there "fifth party" collection? [pdf]
This NSA internal Q&A forum discussion reveals "fifth party collection"—where the NSA passively intercepts data from one intelligence service (South Korea) that has compromised another service's (North Korea) computer network exploitation operations, creating a three-layer chain where NSA exploits Actor One's access to Actor Two's CNE activities against shared targets. The thread provides concrete examples including NSA leveraging South Korean implants on North Korean officials' computers (who themselves were conducting CNE operations) and stealing zero-day exploits from unidentified foreign intelligence services by passively monitoring their successful attacks.
-
Israel targets the U.S. government for invasive electronic surveillance [pdf]
Israel targets the U.S. government for invasive electronic surveillance, and does so more aggressively and threateningly than almost any other country in the world. Indeed, so concerted and aggressive are Israeli efforts against the U.S. that some key U.S. government documents — including the top secret 2013 intelligence budget — list Israel among the U.S.’s most threatening cyber-adversaries and as a “hostile” foreign intelligence service.
-
Israel targets US [pdf]
2 p.An NSA assessment noting that France targets the US Department of Defense and that Israel, while an extraordinarily good SIGINT partner, also targets the United States — ranked by a National Intelligence Estimate as the third most aggressive intelligence service against the US — and that the exchange has tilted heavily toward Israeli needs.