Tag: CES 22 documents
Search documents matching “CES” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Tor - 2006 CES Summer Program [pdf]
The following document is a 2006 research paper produced for the NSA's "Cryptanalysis and Exploitation Services" office. It lays out the technical features of Tor and proposes a number of theoretical and practical attacks, some of which the NSA developed and used in subsequent years. Among other things, the paper describes an NSA-written adaptation of Tor, "indistinguishable from an original Tor client," which enables the NSA to gather intelligence inside the network. It also describes two kinds of "denial of service" attacks against Tor, code-named Coil and Flower, which are used to divert would-be anonymous communications into open channels.
Programs: MJOLNIR -
A potential technique to deanonymise users of the TOR network [pdf]
The GCHQ technical report documenting the entry-exit traffic correlation attack against Tor — providing the complete mathematical specification, test methodology, experimental results and software reference implementation, with distribution to NSA R1, NSA R4, NSA CES, CSE, DSD, SEQUOIA, ICTR, JTRIG, TEA, GTE and multiple OPC divisions.
-
Black Budget: Cryptanalysis & Exploitation Services – Analysis of Target Systems [pdf]
This document is a budget justification for the NSA's Cryptanalysis & Exploitation Services project, which develops capabilities to defeat commercial encryption systems, exploit emerging communications technologies, and conduct vulnerability analysis against both foreign and domestic security products.
“The CIA Campaign to Steal Apple's Secrets” - The Intercept ↗ (2015-03-10) · Scahill, Jeremy · Begley, Josh -
CLASSIFICATION GUIDE FOR CRYPTANALYSIS, 2-12 [pdf]
An NSA/CSS classification guide for cryptanalysis establishing the precise classification level for each type of information about NSA's capabilities to exploit commercial and indigenous encryption systems — from the unclassified acknowledgement that NSA exploits cryptographic devices, through to the Top Secret protection of cryptographic modifications made to commercial products to render them exploitable and industry relationships used to obtain cryptographic details.
“Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · “Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · Ball, James · Borger, Julian · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian -
CLASSIFICATION GUIDE FOR ECI PAWLEYS (PAW) [pdf]
This 2006 NSA classification guide outlines the protocols for ECI PAWLEYS (PAW). PAWLEYS is an Exceptionally Compartmented Information (ECI) category designed to protect clandestine operations—both physical (HUMINT) and digital (CNE)—specifically aimed at acquiring foreign cryptographic information and material. The document confirms that the NSA actively seeks to circumvent encryption through clandestine HUMINT and computer network access aimed at cryptographic information and material, rather than relying solely on traditional codebreaking.
Programs: PAWLEYS -
Innov8 Experiment Profile Template [pdf]
A TOP SECRET STRAP1 joint NSA/GCHQ experiment profile documenting a 2010-2011 Joint Capability Experiment to test hardware-accelerated bulk decryption of common internet encryption technologies at scale, integrating TURMOIL's passive collection with NSA's LONGHAUL key recovery service via the ISLANDTRANSPORT messaging system, as part of the broader BULLRUN assault on internet encryption.
“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Ball, James · Borger, Julian · Greenwald, Glenn -
Intro to the VPN Exploitation Process [pdf]
NSA introduction to the VPN exploitation process from September 2010, presented by the OTP VPN Exploitation Team, covering the full workflow from initial collection through to sustained decryption of IPSec, PPTP, SSL and SSH traffic, with named exploitation successes including airlines, diplomatic missions, banks and intelligence services across Iran, Jordan, Russia, Turkey, Pakistan, Afghanistan, Somalia, Indonesia and Mexico.
Programs: BLEAKINQUIRY · TOYGRIPPE · XKEYSCORE · MAILORDER · CORALREEF · VULCANDEATHGRIP · SCISSORS · TURTLEPOWER · PINWALE · FOURSCORE · CADENCE · UTT · VULCANMINDMELD · CAPRIOS · AGILITY · NKB · FOLLOWTHEMONEY -
LONGHAUL [pdf]
An NSA WikiInfo page for LONGHAUL — the centralised end-to-end attack orchestration and key recovery service that sits at the heart of NSA's capability to break encrypted internet traffic, receiving cryptanalytic data from field collection systems, coordinating attacks against VPN and SSL/TLS encryption through child projects POISONNUT and SCARLETFEVER, and returning recovered keys to deployed CA Servers at collection sites worldwide.
Programs: LONGHAUL · MAILORDER · CASPORT · GECC · VIVIDDREAM · TURMOIL · WEALTHYCLUSTER · TUTELAGE · EINSTEIN · ISLANDTRANSPORT · HADOOP · NINJACOVE · JST · CST · VMM · VDG · ORDC · SCB · ISLANDHIDEAWAY · TURBULENCE · POISONNUT · SCARLETFEVER · HEROICSAND · PLATINUMRING · GALLANTWAVE · JEDIMINDTRICK · CHAOTICSTORMTROOPER · CORALREEF · SCUBADIVER2 · TERRACOTTA · HBASE · SCALA · MAPREDUCE · COALCAR · STOCKCAR · BEACHHEAD · MIDRIFT · WOLVERINESTAKE · NSP · PURGE · SURGE · C2DP · DOORS · HUDSON -
N.S.A. Memo Expands Access to FISA Information [pdf]
In 2006, the National Security Agency sought to expand access to Foreign Intelligence Surveillance Act information — previously limited to its headquarters in Fort Meade, Md. — to its code-breakers in Georgia, Texas and Hawaii. Part of the deliberations focused on a problem that raised the possibility that the agency had violated rules the surveillance court established for handling the information.
-
NSA Intelligence Relationship with Norway [pdf]
This document details the long-standing SIGINT partnership between the NSA and Norway’s NIS, formalized under the NORUSA agreement in 1954, highlighting collaboration on intelligence collection, analysis, and technology modernization, particularly against Russian, counterterrorism, and counter-proliferation targets. It emphasizes mutual contributions, including SIGINT, geolocation data, FORNSAT metadata, and computer network exploitation, with Norway recognized as a top NSA partner and significant contributor to coalition intelligence efforts in Afghanistan.
“Norway Used NSA Technology for Potentially Illegal Spying” - The Intercept ↗ (2018-03-01) · “Norway´s secret surveillance of Russian politics for the NSA” - Dagbladet ↗ (2013-12-17) · “The antennas that collect data on Norwegian citizens” - NRK ↗ (2018-03-01) · Moltke, Henrik · Halvorsen, Arne · Blindheim, Anne Marte · Klungtveit, Harald S. · Sørenes, Kjetil Magne · Bergsaker, Tore · Hultgreen, Gunnar · Skille, Øyvind Bye · Hansen, Ståle Ellingsgard · Døvik, Olav · Lied, Henrik · Jansson, Harald K. -
POISONNUT [pdf]
NSA Wiki page describing POISONNUT — also known as the VPN Attack Orchestrator (VAO) — a LONGHAUL cryptologic exploitation service for IPSec VPN decryption that has existed in various forms since 2003, serving clients including TURMOIL, WEALTHYCLUSTER and the Transform Engine emulator via ISLANDTRANSPORT with ISLANDHIDEAWAY encryption.
Programs: POISONNUT · TURMOIL · WEALTHYCLUSTER · ISLANDTRANSPORT · ISLANDHIDEAWAY · LONGHAUL · OAKLEY · SCARLETFEVER · PICARESQUE · VALIANTSURF -
SIGINT Strategy Threads 4 and 7 SIDtoday [pdf]
A TOP SECRET SIDToday article from September 2011 describing SIGINT Strategy Threads 4 and 7 — NSA's two classified programmes addressing the challenge of ubiquitous internet encryption — directing cleared analysts to BULLRUN-protected content covering capabilities against commercial webmail encryption used by CT targets and VPN traffic exploitation, with access requiring BULLRUN Community of Interest indoctrination.
-
SPIN 15 VPN Story [pdf]
A TOP SECRET planning document describing two parallel workstreams in SPIN 15: the deployment of VPN decryption capabilities to SMOKYSINK (US-3237), a unilateral NSA RAMPART-T cable tap site operating without a third-party partner, and a risk reduction benchmarking activity measuring TURMOIL's VPN and SSL exploitation performance against the Net-Centric Capabilities (NCC) programme's Key Performance Parameters — which targeted 100,000 VPN decrypt requests per hour by the end of fiscal year 2011, and 10 million SSL sessions per day by the end of fiscal year 2012.
Programs: TURMOIL · SMOKYSINK · ISLANDHIDEAWAY · PICARESQUE · KEYCARD · XKEYSCORE · PRESSUREWAVE · ISLANDTRANSPORT · PIQBLADE -
TURBULENCE - APEX - Active/passive Exfiltration [pdf]
This 2009 NSA presentation details APEX (Active/Passive Exfiltration), a TURBULENCE program component that combines passive collection infrastructure with active TAO implants to exfiltrate VPN and VoIP traffic from deep within target networks back to NSA collection systems. The system uses the FASHIONCLEFT protocol to tunnel captured packets through compromised routers and network devices, enabling decryption of VPN tunnels and collection of voice communications that would otherwise be invisible to passive surveillance.
Programs: TURBULENCE · TURMOIL · HAMMERSTEIN · HAMMERCHANT · FASHIONCLEFT · TUTELAGE · TURBINE · TRAFFICTHIEF · XKEYSCORE · ANALYTICS · PRESSUREWAVE · TOYGRIPPE · POISONNUT · FLAXENPRECEPT · FOGYNULL · FUNNELAPS · SHELLGREY · METROTUBE · VINYLSEAT · OLYMPUS · UNITEDRAKE · FIGBUILD · SURPASSPIN · ROOTKNOT · OPTICPINCH · SEAGULFARO · TREBLECLEF · CONVEY · PINWALE · SWEEPFORWARD · QUANTUM · KEYCARD · ASDF · TUBE · PUZZLECUBE · WEALTHYCLUSTER2 · COALSHOVEL · HAMMERMILL · ISLANDTRANSPORT · FASCIA · TURBINIE · APEX · PPF · AEG · FIP · SSO · PICARESQUE · PSP · IVE · PSC · CHIMNEYPOOL · CORESSC · FLASHHANDLE · IBRIDGE · CORALREEF · VAO · NUCLEON · PIQBLADE“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Gallagher, Ryan · Greenwald, Glenn -
TURMOIL GALLANTWAVE [pdf]
An NSA WikiInfo page describing TURMOIL GALLANTWAVE — a CES mission application hosted on TURMOIL that decrypts communications using Data Network Session Cipher (DNSC) technologies, such as SSL/TLS, by integrating with the LONGHAUL SCARLETFEVER key recovery service and forwarding decrypted sessions to XKEYSCORE for analyst access.
Programs: VALIANTSURF · XKEYSCORE · TURMOIL · GALLANTWAVE · LONGHAUL · TURBULENCE · BULLRUN · SCARLETFEVER · TUMULT · TUBE · UTT · BTUBE · FISHWAY · EXOPUMP · PURGE · SURGE · SCISSORS · PINWALE · TUSCARORA · NUCLEON · WDM · TURTLEPOWER · CONVEYANCE · ONEROOF · KEYCARD · SLIDETACKLE · POLARSTARKEY · TUMMS · CEMETERY · TEPIDTSUNAMI · PPF · ISLANDTRANSPORT -
TURMOIL VPN PROCESSING [pdf]
A TURMOIL VPN Processing technical briefing from October 2009 describing the full architecture for intercepting and decrypting IPSec VPN traffic within the TURMOIL passive collection platform — covering IKE/ESP protocol handling, five distinct data flow types, the Dell LPT hardware implementation, and live operational metrics showing over 8 million packets decrypted at Menwith Hill and 1.4 million at SMOKYSINK during a single week in October 2009.
-
TURMOIL/APEX/APEX High Level Description Document [pdf]
NSA WikiInfo page providing the high-level design description of APEX — the Active-Passive Integration capability integrating HAMMERMILL router implants with TURMOIL passive collection — enabling real-time exfiltration of targeted VPN (HAMMERSTEIN) and VoIP (HAMMERCHANT) traffic from compromised routers directly into NSA's passive collection and cryptanalytic attack infrastructure, with TURBINE providing automated command and control of the combined active-passive system.
Programs: TURMOIL · APEX · HAMMERMILL · HAMMERCHANT · HAMMERSTEIN · FASHIONCLEFT · TURBINE · TOYGRIPPE · METROTUBE · CHIMNEYPOOL · PIQBLADE · KEYCARD · FASCIA · ISLANDTRANSPORT · PRESSUREWAVE · ASDF · CONVEYANCE · TURBULENCE -
User's Guide For PRISM Skype Collection - August 2012 [pdf]
An NSA analyst user guide for PRISM Skype collection, explaining how to task Skype selectors, locate collected content across PINWALE, NUCLEON and MARINA, interpret common collection artefacts, and troubleshoot issues with video synchronisation, timestamp discrepancies and incomplete file transfers — covering peer-to-peer, in/out and conference call collection modes from PRISM coverage that began in February 2011.
-
VALIANTSURF (VS): Capability Levels [pdf]
A capability status document for VALIANTSURF — NSA's programme for large-scale IPSec VPN decryption integrated with TURMOIL passive collection and LONGHAUL key recovery — defining five capability levels from basic key recovery through full hardware-accelerated on-site decryption with XKEYSCORE integration, and showing deployment status across named collection sites.
-
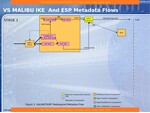
VS MALIBU IKE And ESP Metadata Flows [pdf]
A TOP SECRET four-slide architecture document describing MALIBU — NSA's system for intercepting and decrypting IPSec VPN traffic at the point where it crosses monitored internet cables — showing how intercepted VPN connections are processed, cryptographic keys recovered, traffic decrypted and results delivered to analysts, with separate diagrams for metadata collection, software decryption, full exploitation and survey modes.