Tracking Targets Through Proxies & Anonymizers
Open PDFDocument date: -
Pages: 25
Genre: slides
Banner: TOP SECRET//COMINT//REL TO USA, FVEY
Classification: TOP SECRET SI
Dissemination: REL 5EYES
This NSA presentation details methods for tracking and de-anonymizing internet users who employ privacy tools like Tor, proxies, and VPN services such as AnchorFree's Hotspot Shield. The document explains how the agency reverse-engineers anonymization tools, creates "fingerprints" to identify their traffic in surveillance systems, and correlates encrypted connections to reveal users' real IP addresses and locations—acknowledging this work "makes for sad analysts" when targets successfully obscure their identities.
My notes
TOP SECRET//COMINT//REL TO USA, FVEY
Tracking Targets Through Proxies & Anonymizers
(and the air speed velocity of an unladen swallow)
Also known as:TTTPaAatasvoaus
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
CLASSIFICATION
- Classification of this briefing is:
TS//SI//REL 5EYES
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Agenda Items
- The issue at hand... (proxies, anonymizers & TOR, oh my!)
- What we do about, and how we approach, this issue...
- A couple examples of tracking targets through anonymizers (AnchorFree & Tor)
- Closing remarks and questions
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Up Front Caveat
Before we begin this briefing, I want to set the stage by saying that there is no silver bullet for tracking target communications through anonymizers. Any methodology set forth in this briefing requires both manual analysis and (generally) luck.
With that out of the way...
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
The issue at hand...(proxies, anonymizers & Tor, oh my!)
- Targets generally don't like to have their communications tracked by government agencies or filtered by national firewalls.
- If they are tech-savvy enough, they will use anonymizers to try to mask their real IP/ location.
- This generally makes for sad analysts. :(
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
What we do about the issue at hand...
- The only way to track communications through anonymizers is if you understand how those anonymizers work. If you don't know what the traffic looks like, how will you recognize it in SIGINT?
- Generally our process is as follows:
- Identify new proxy/anonymizer
- Research/use anonymizer, document what happens, what does traffic look like, what client traffic does it pass through(if any)?
- Create fingerprints in SIGINT to identify such proxy traffic
- Correlate proxy traffic with known target activity
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Anchorfree
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Anchorfree
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Anchorfree
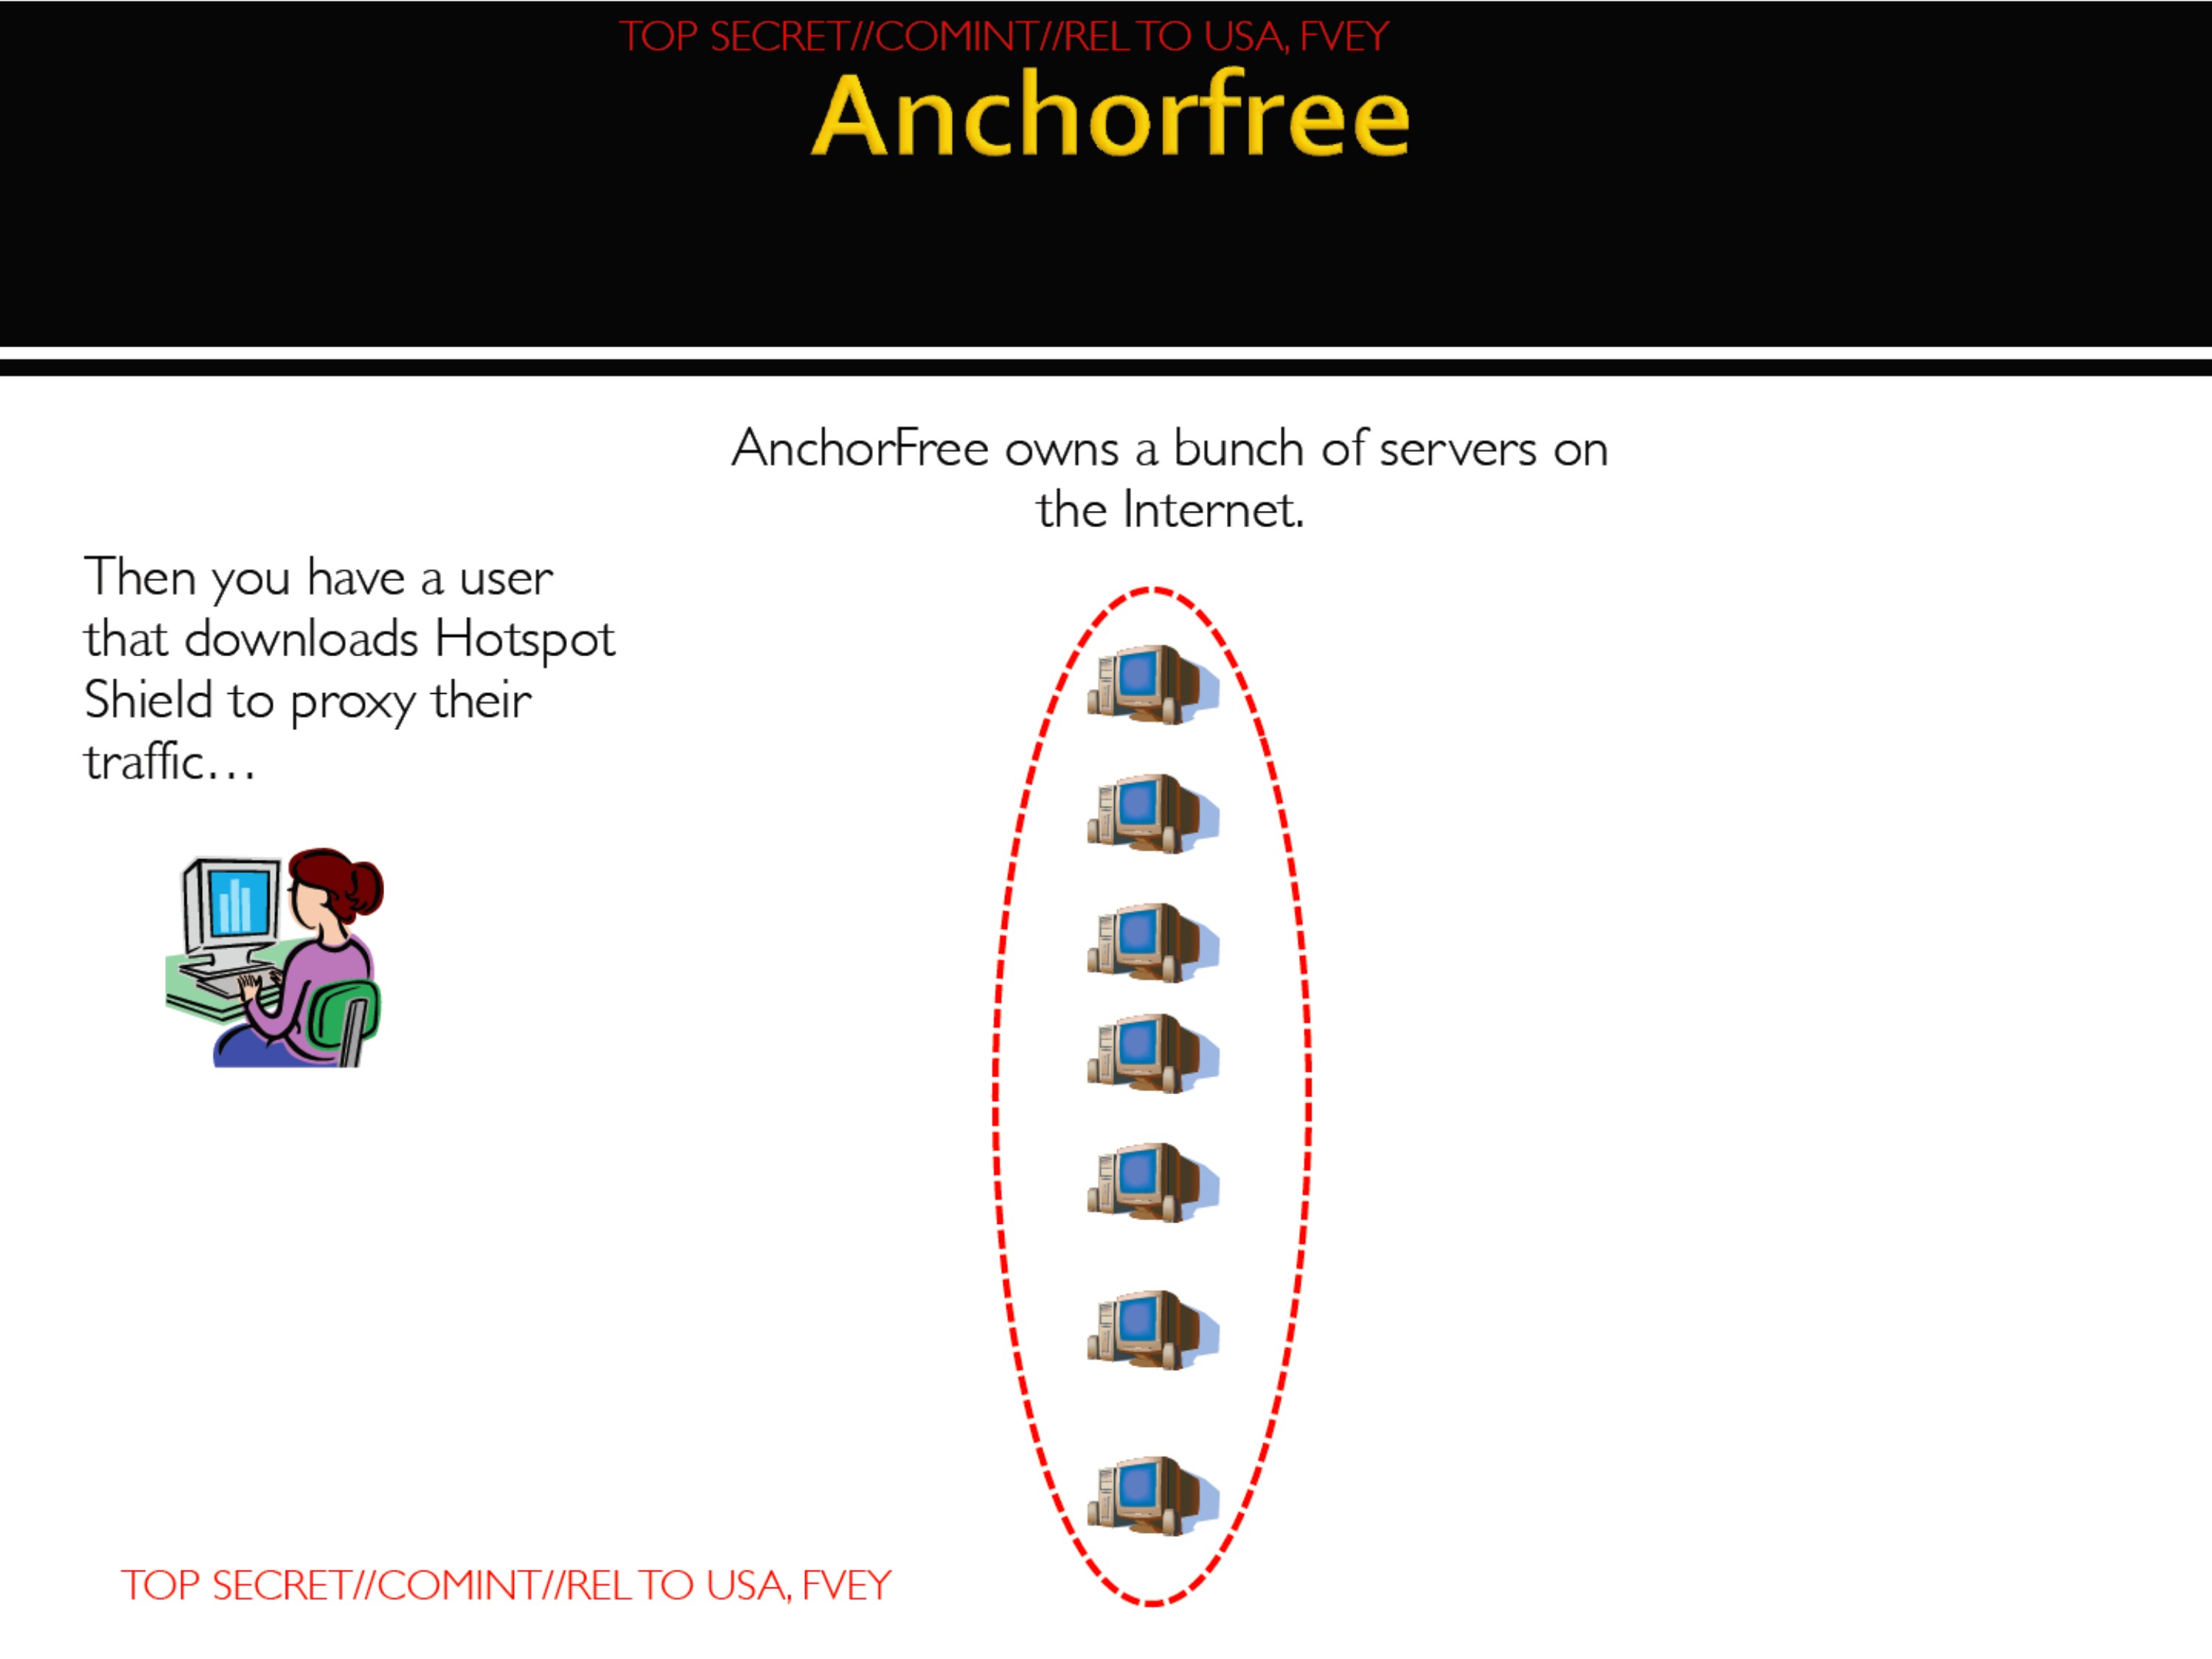
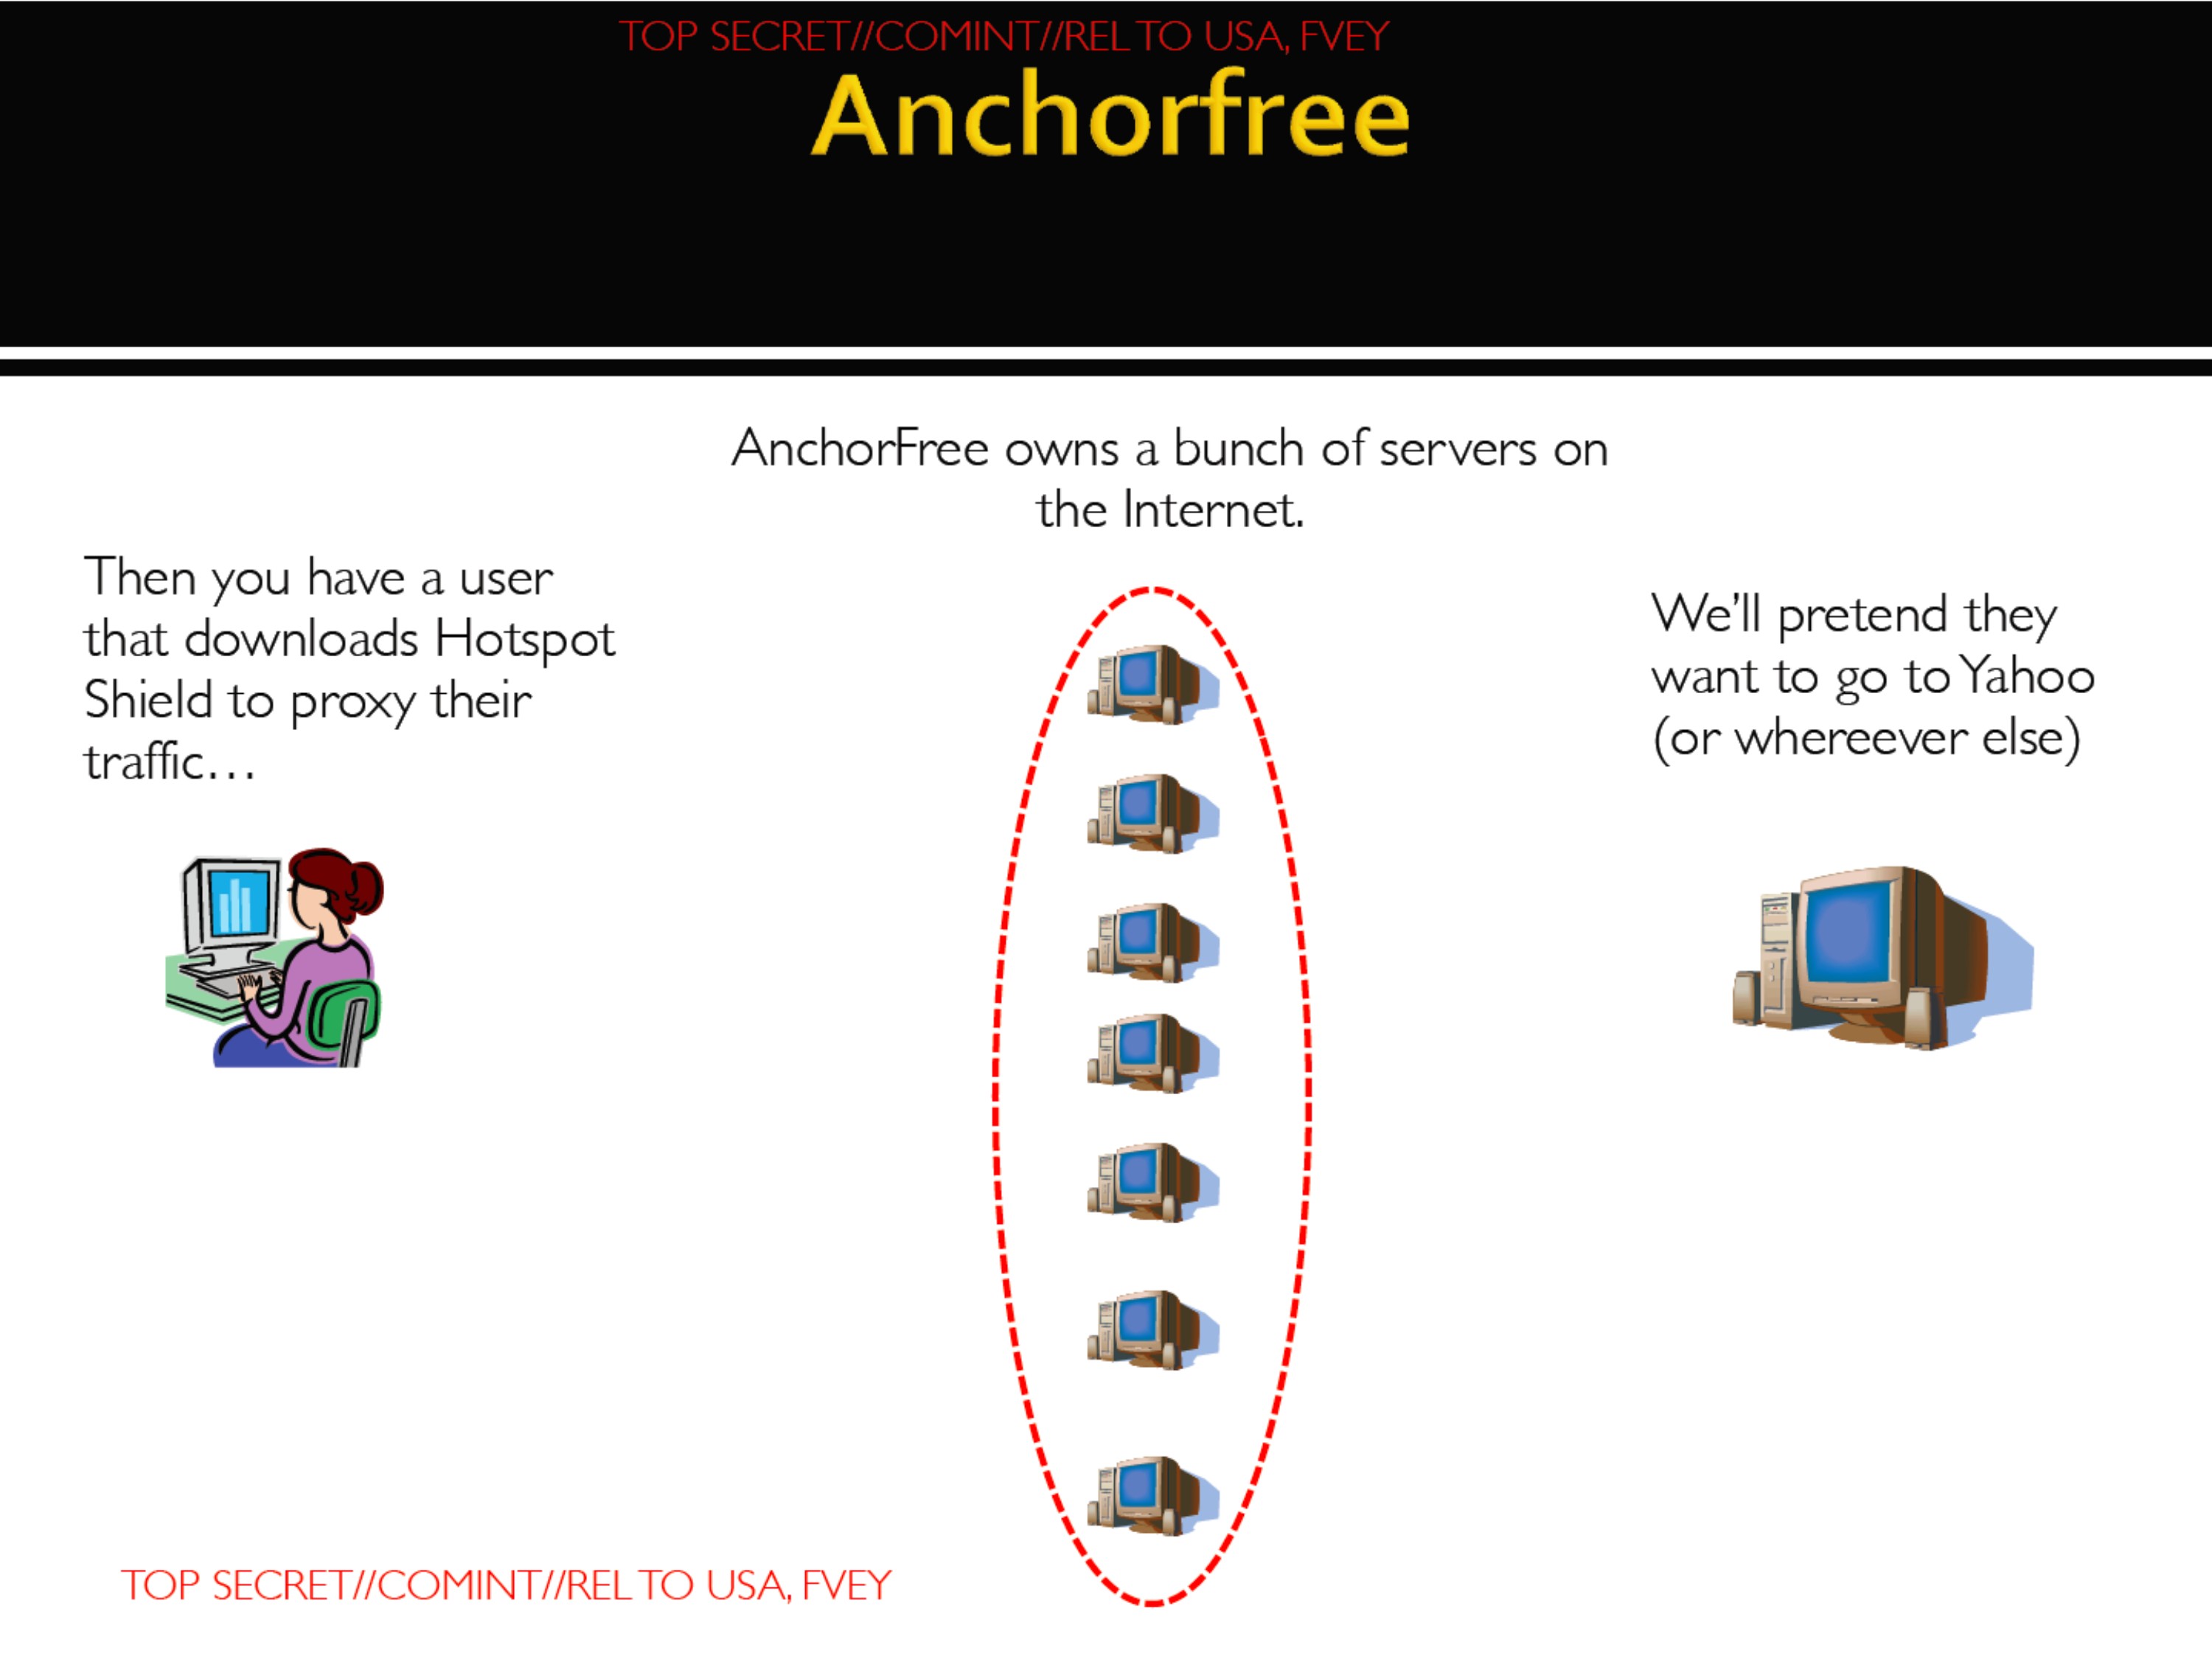
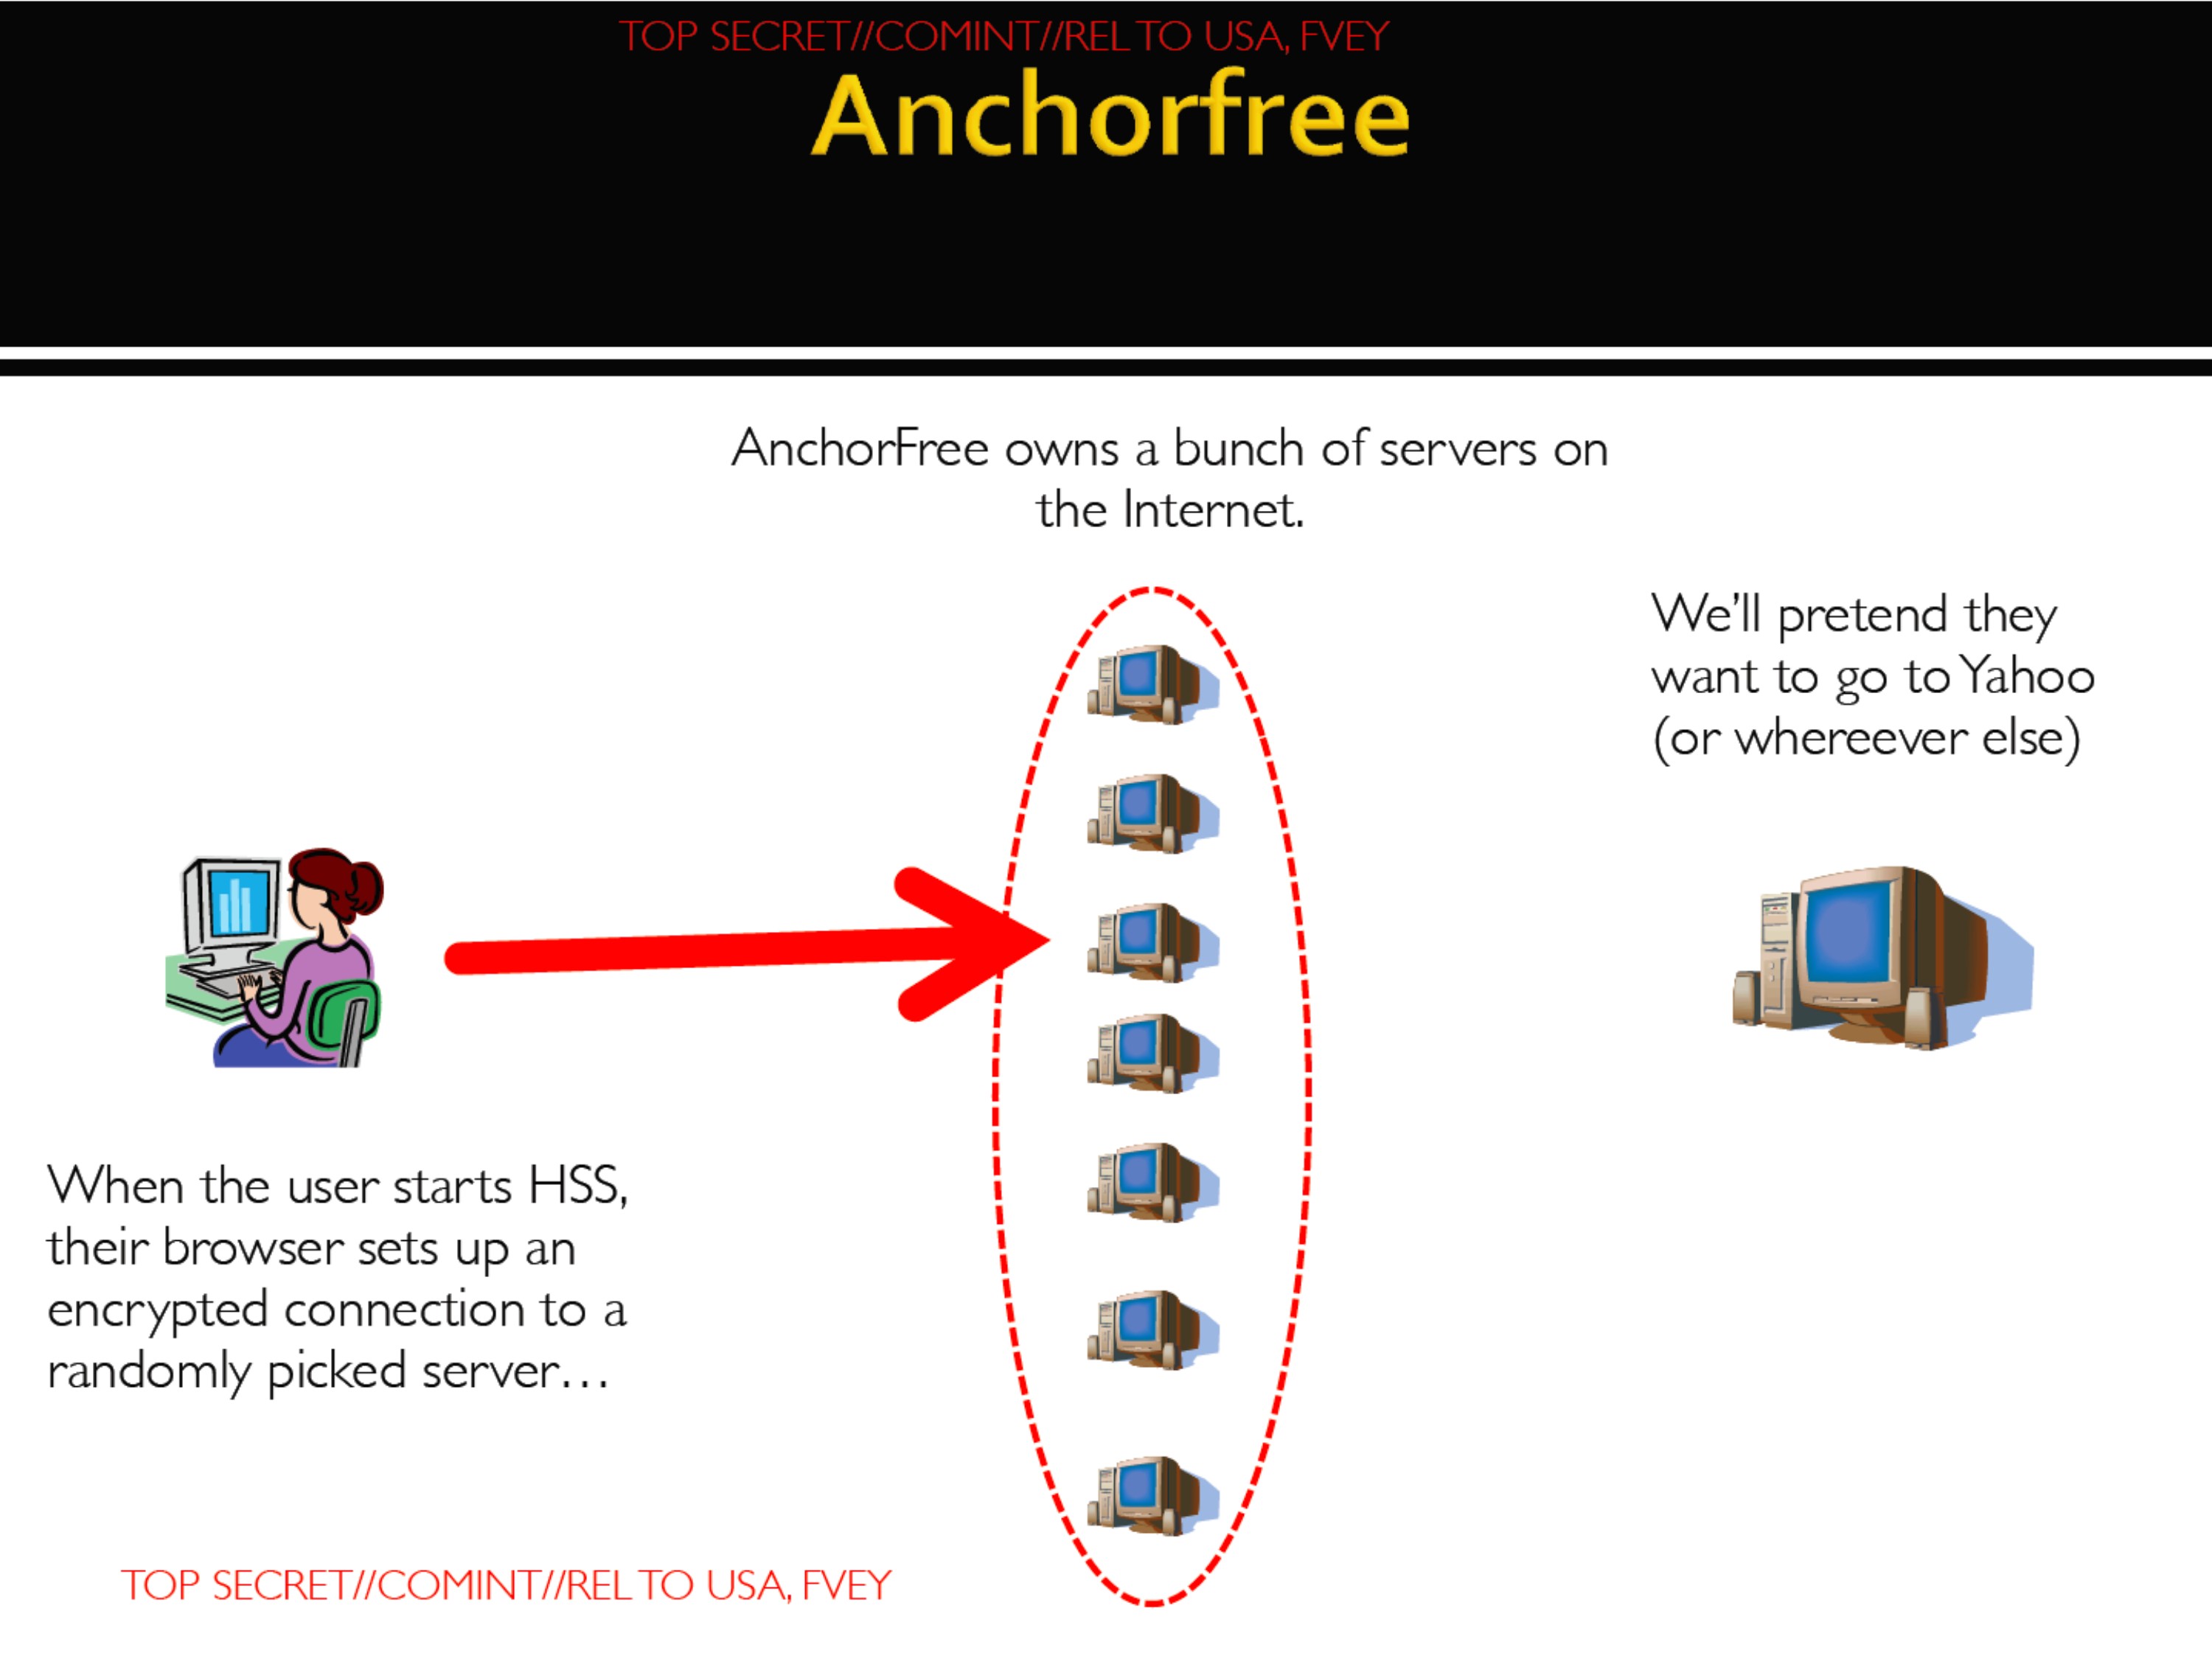
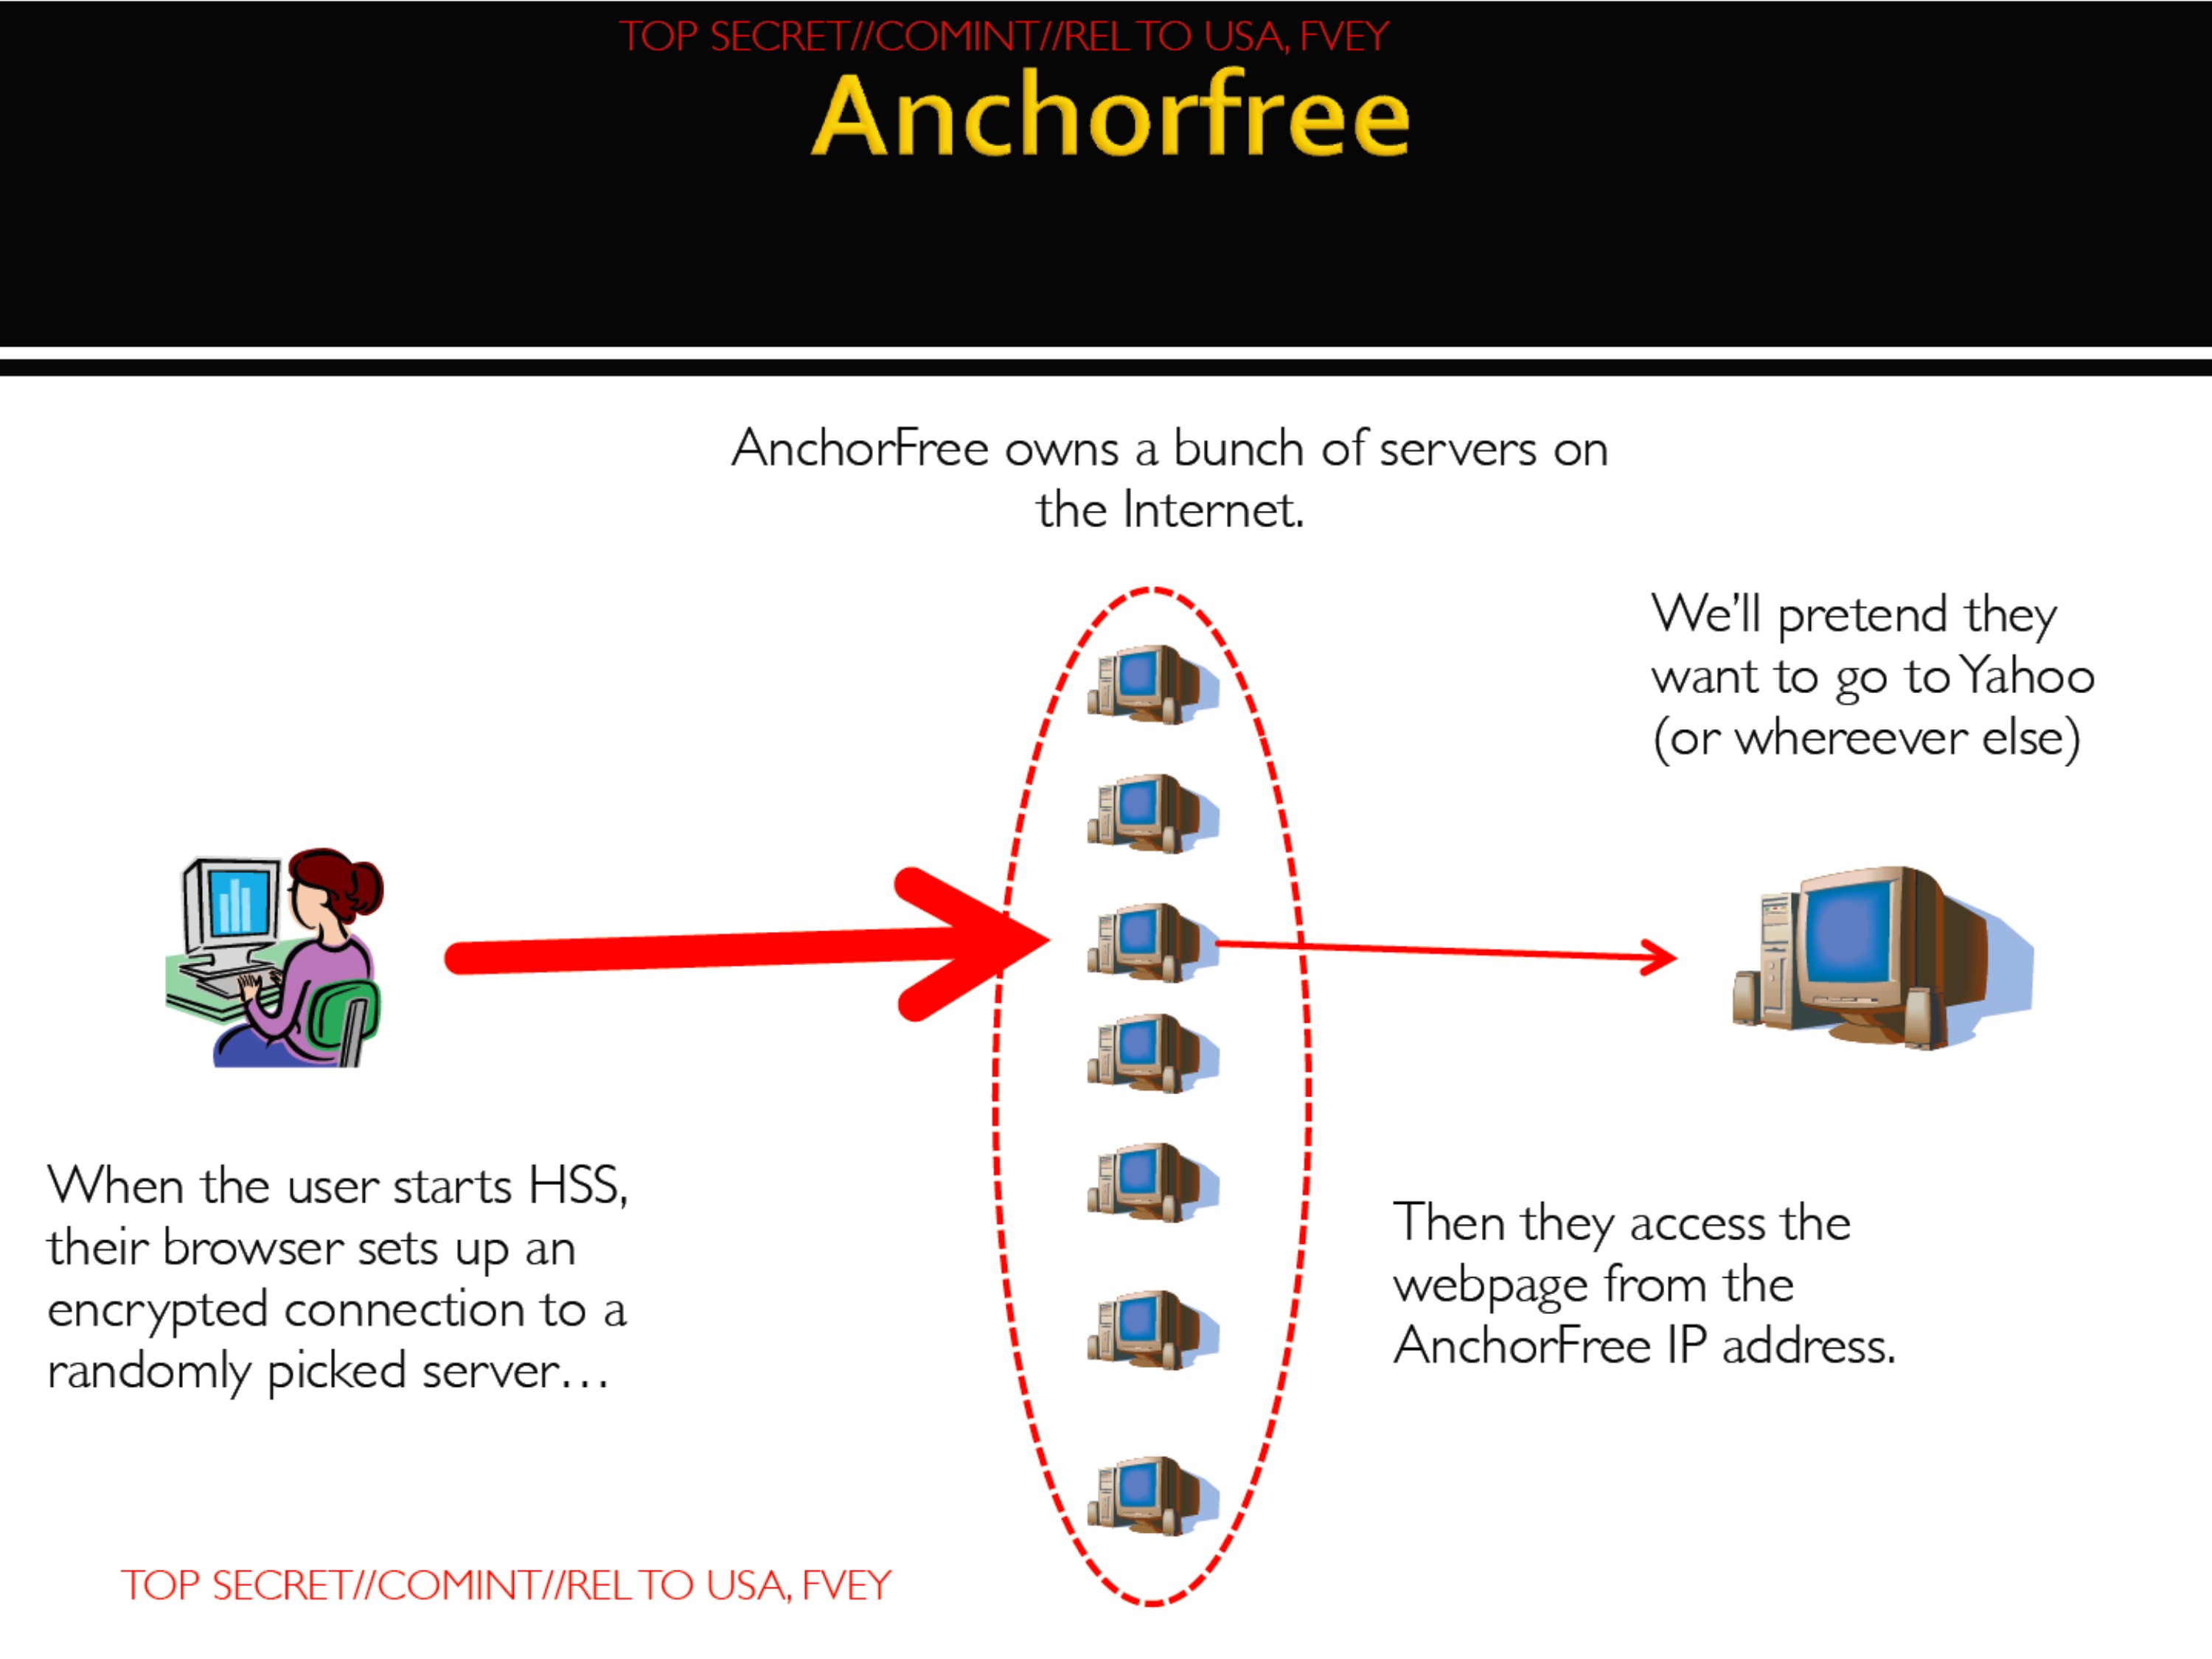
AnchorFree owns a bunch of servers on the Internet.
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Anchorfree
Then you have a user that downloads Hotspot Shield to proxy their traffic...
AnchorFree owns a bunch of servers on the Internet.
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Anchorfree
Then you have a user that downloads Hotspot Shield to proxy their traffic...
AnchorFree owns a bunch of servers on the Internet.
We'll pretend they want to go to Yahoo (or whereever else)
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Anchorfree
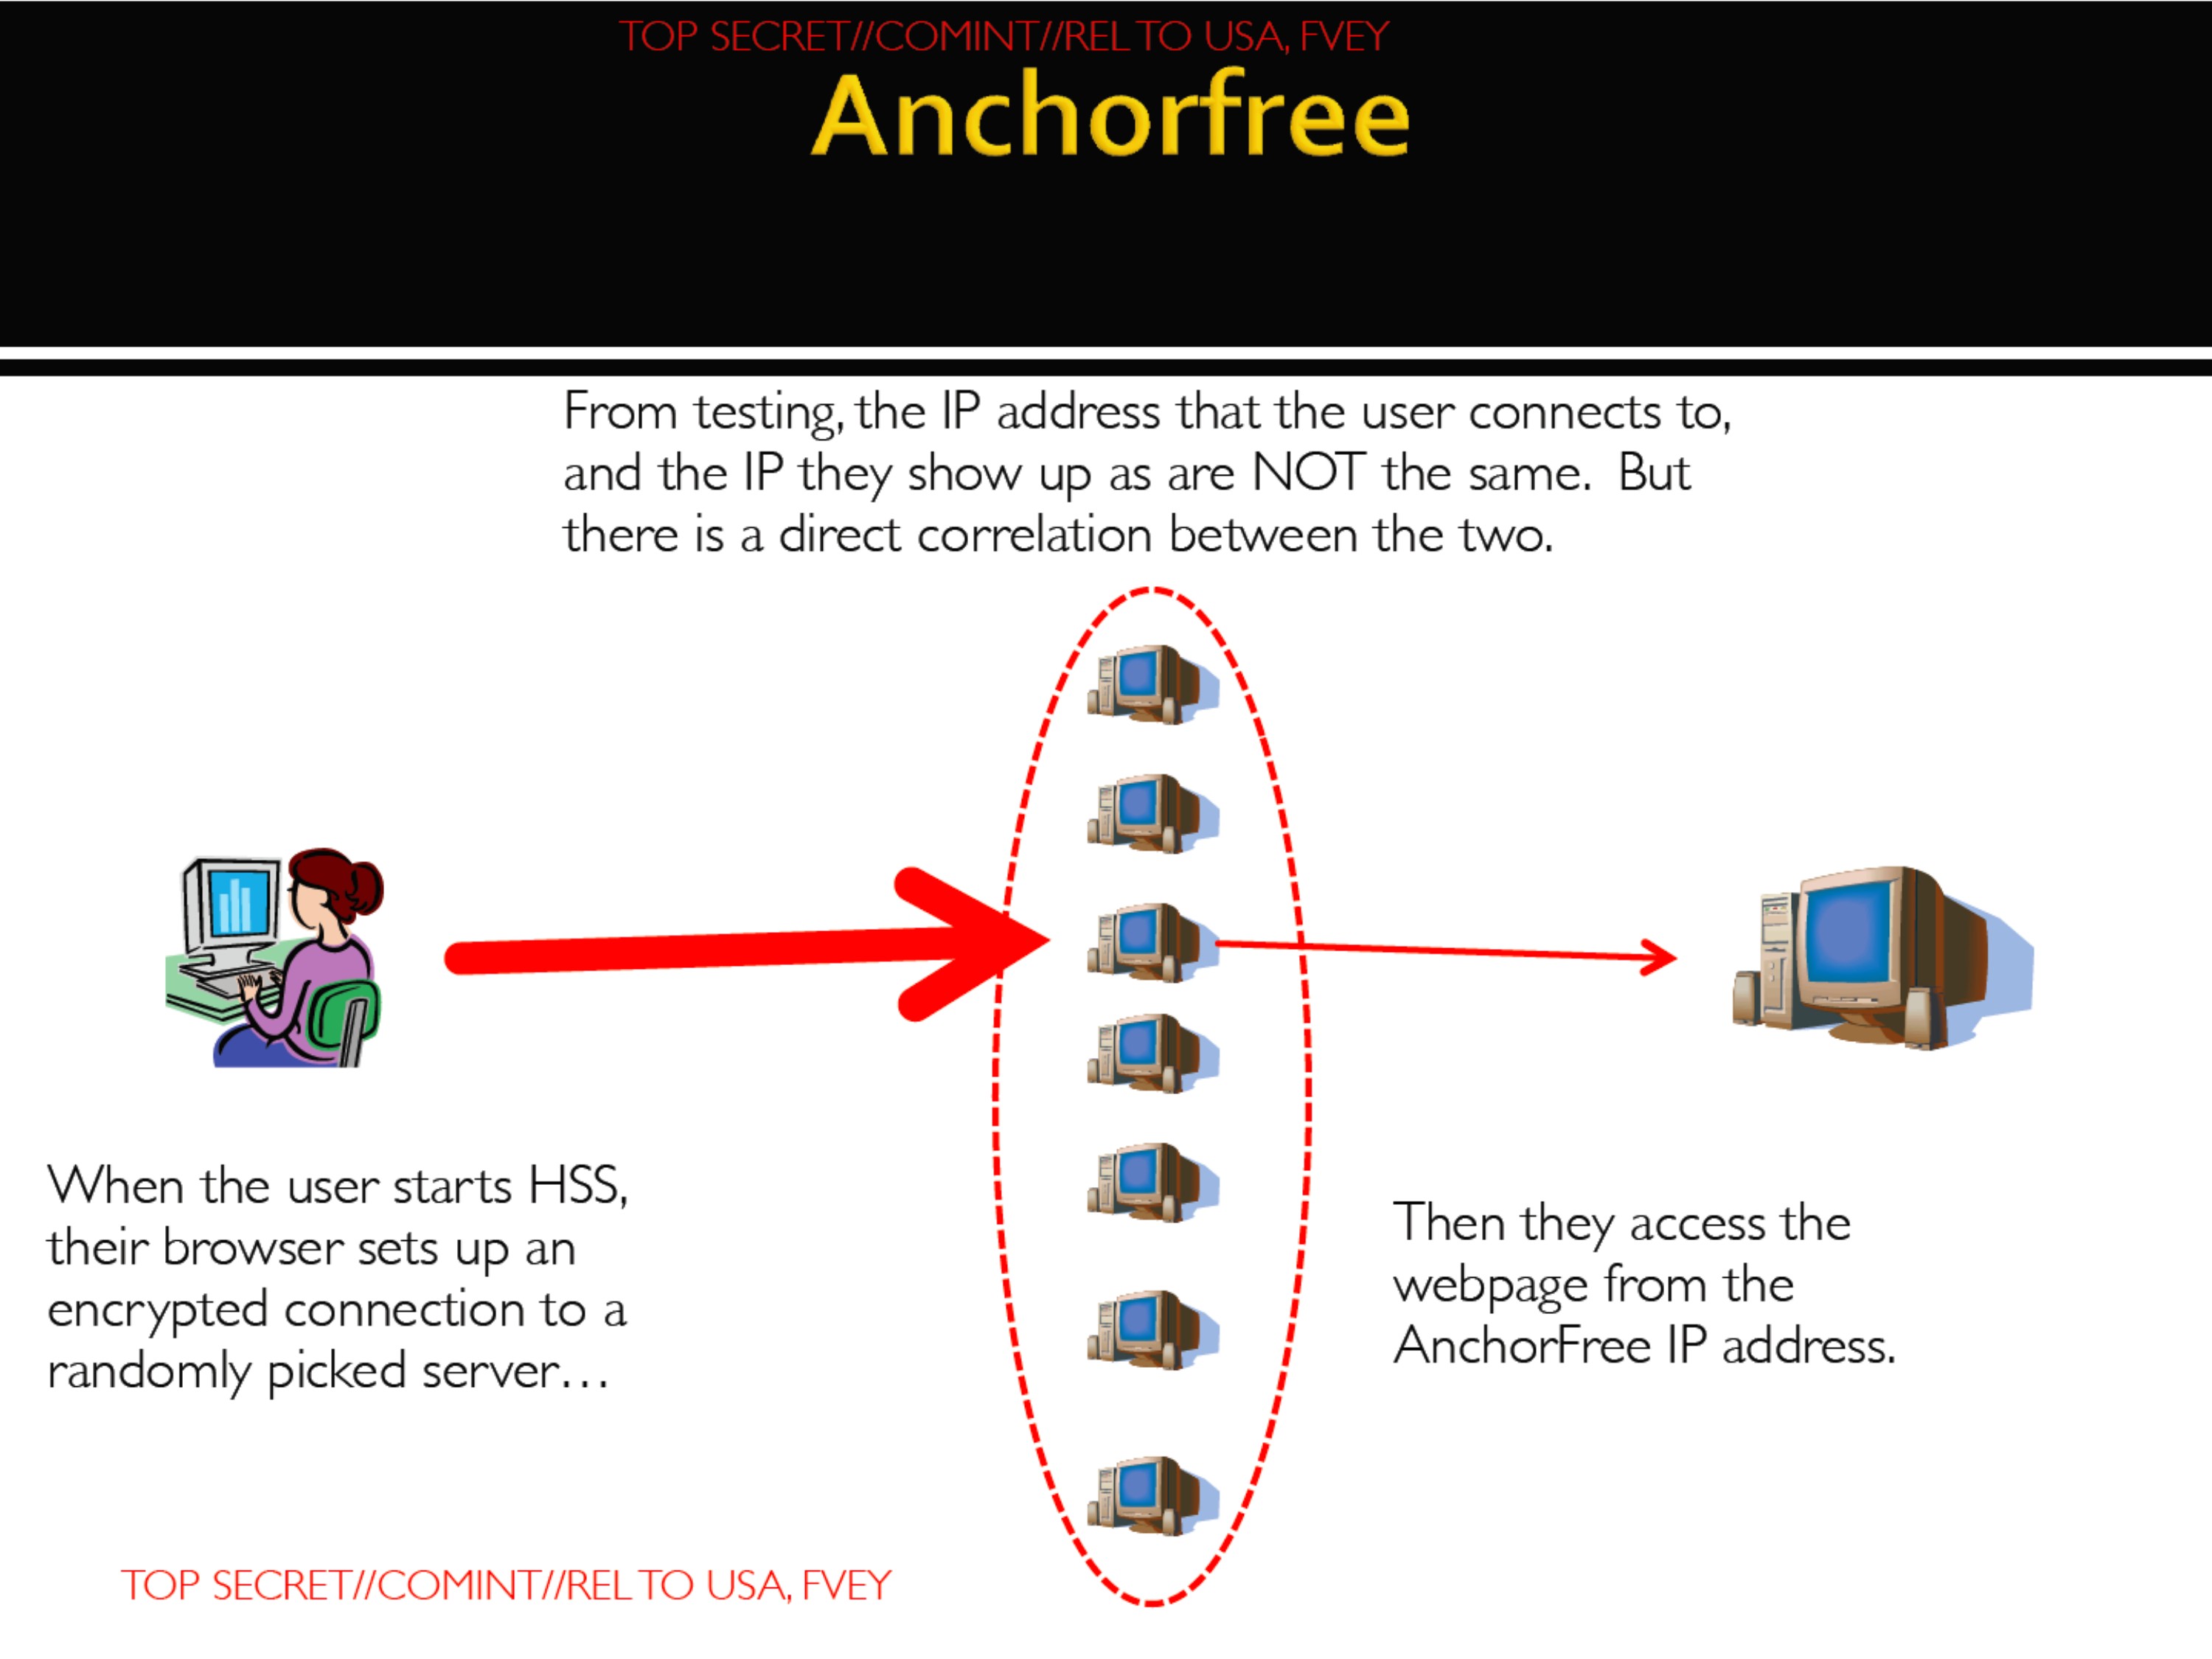
When the user starts HSS, their browser sets up an encrypted connection to a randomly picked server...
AnchorFree owns a bunch of servers on the Internet.
We'll pretend they want to go to Yahoo (or whereever else)
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Anchorfree
When the user starts HSS, their browser sets up an encrypted connection to a randomly picked server...
AnchorFree owns a bunch of servers on the Internet.
We'll pretend they want to go to Yahoo (or whereever else)
Then they access the webpage from the AnchorFree IP address.
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Anchorfree
From testing, the IP address that the user connects to, and the IP they show up as are NOT the same. But there is a direct correlation between the two.
When the user starts HSS, their browser sets up an encrypted connection to a randomly picked server...
Then they access the webpage from the AnchorFree IP address.
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
AnchorFree....so what?
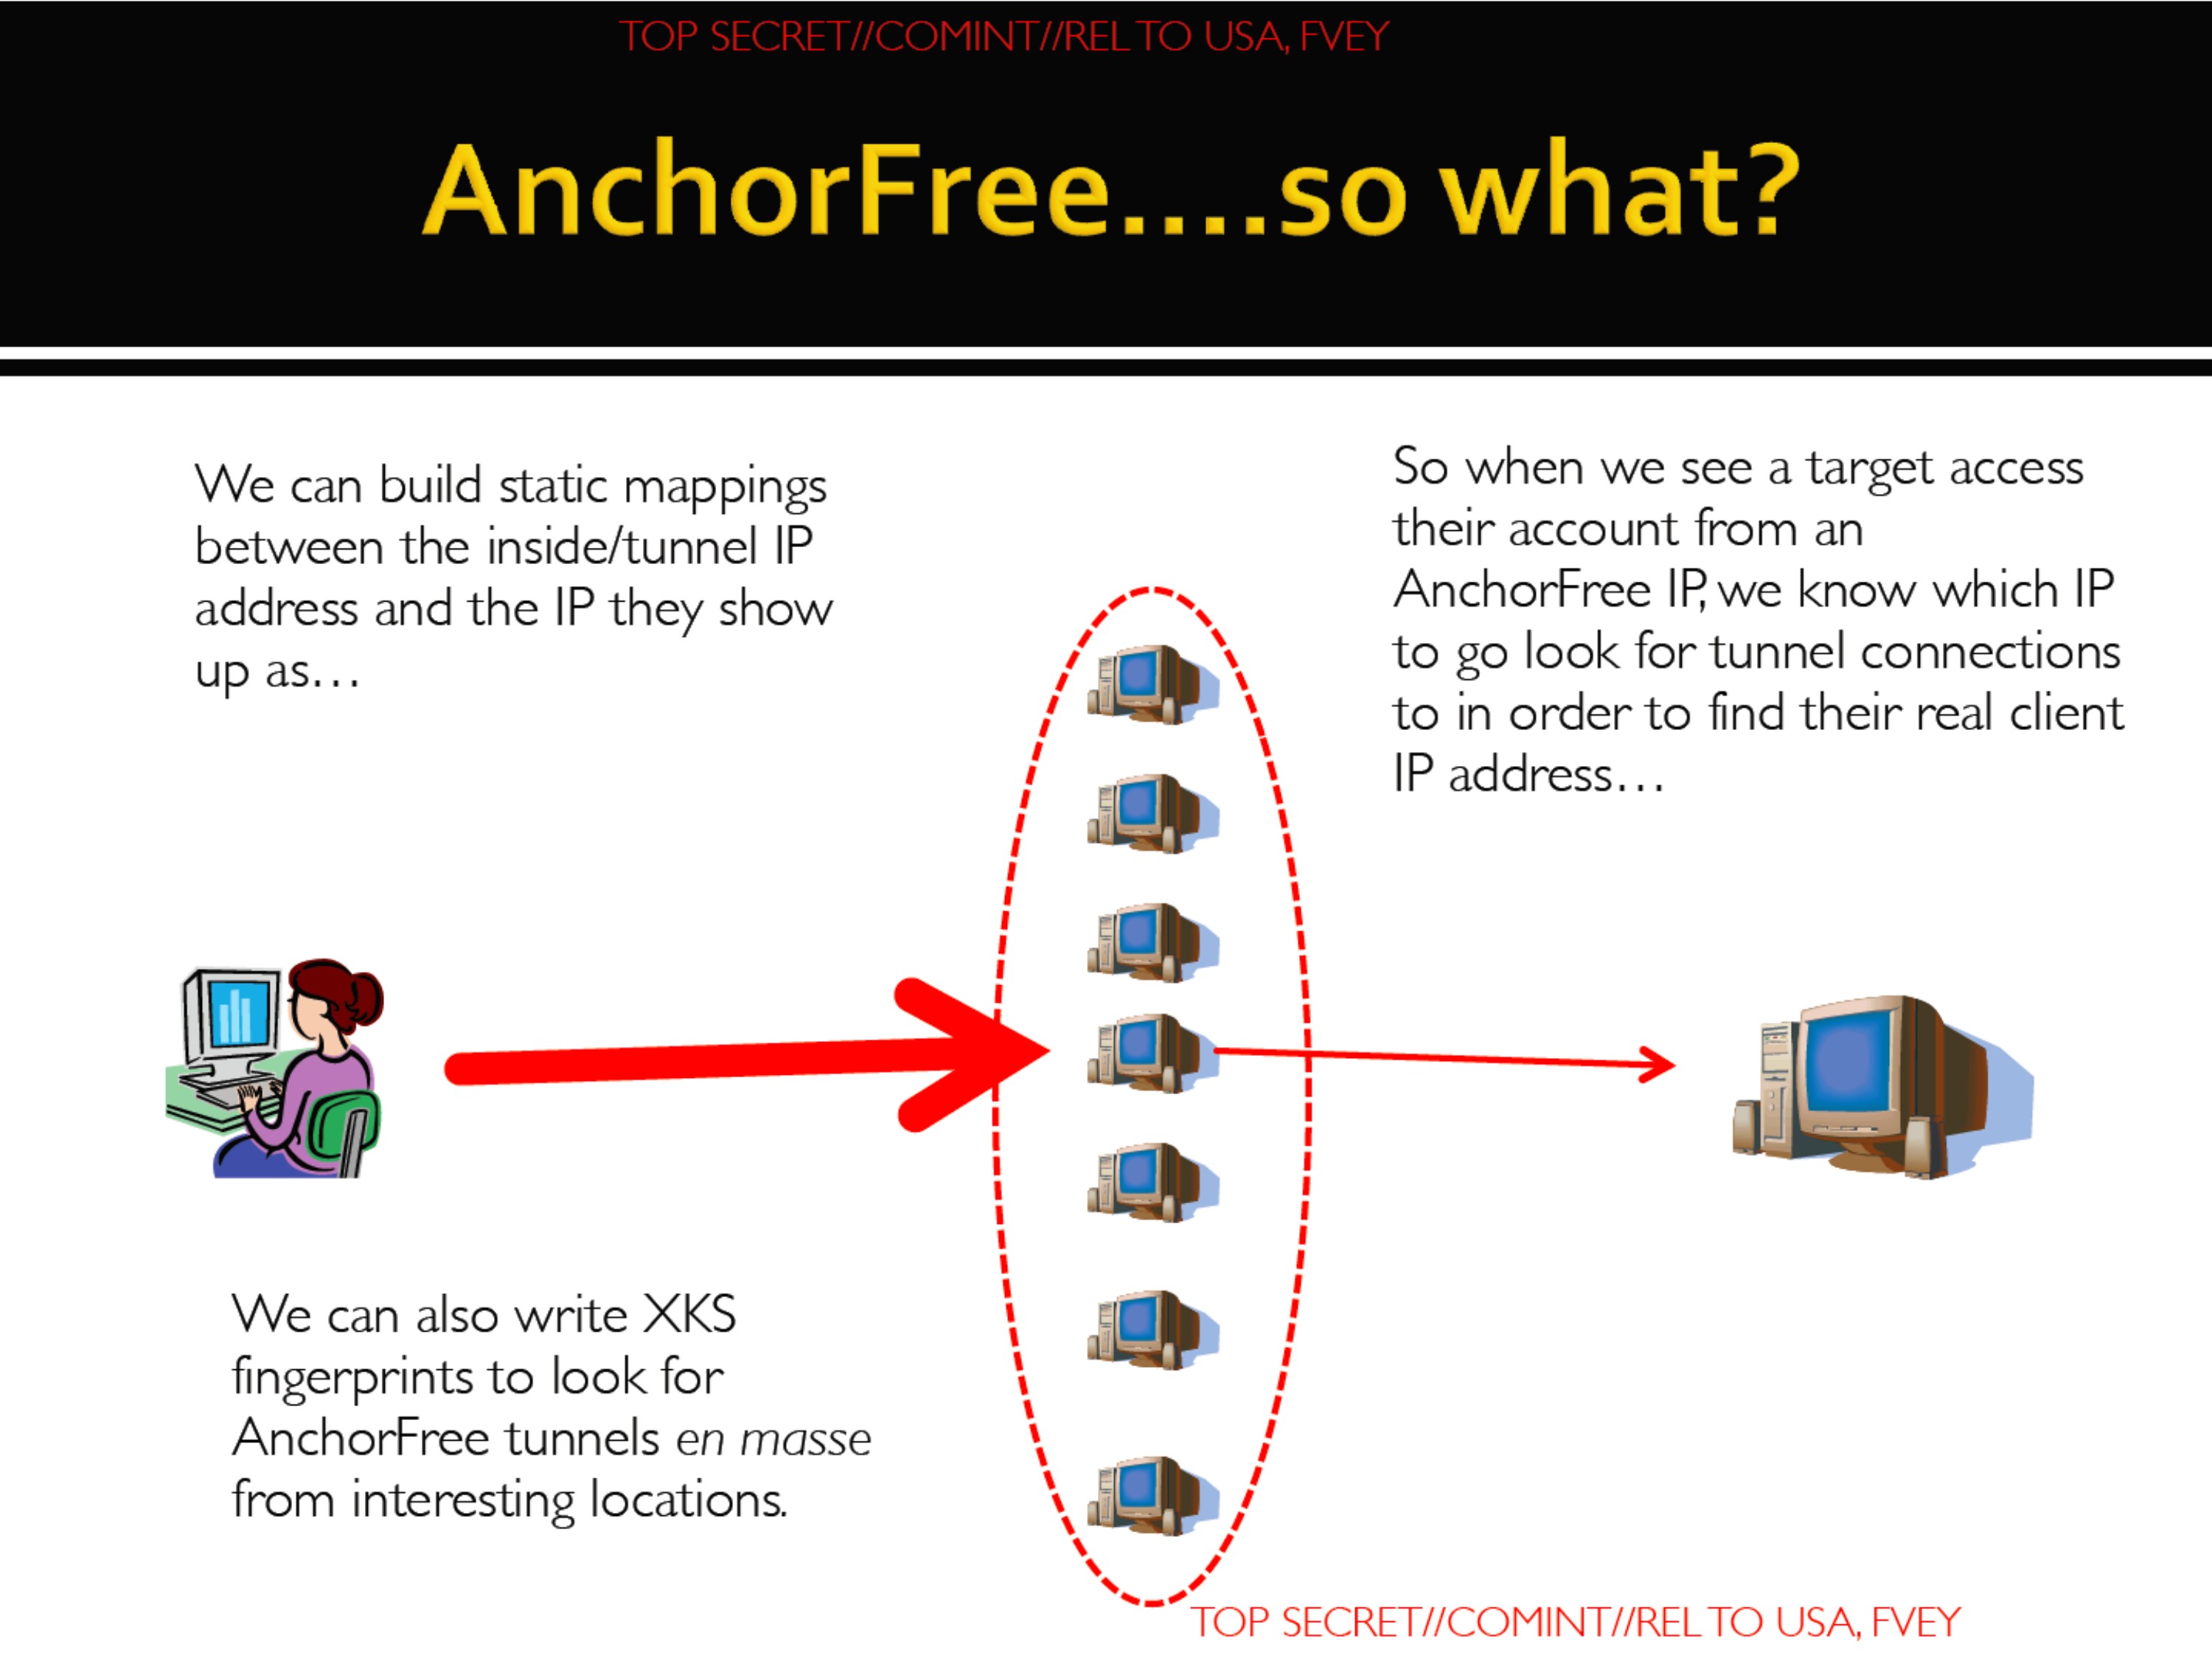
We can build static mappings between the inside/tunnel IP address and the IP they show up as...
So when we see a target access their account from an AnchorFree IP, we know which IP to go look for tunnel connections to in order to find their real client IP address...
We can also write XKS fingerprints to look for AnchorFree tunnels en masse from interesting locations.
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Tor
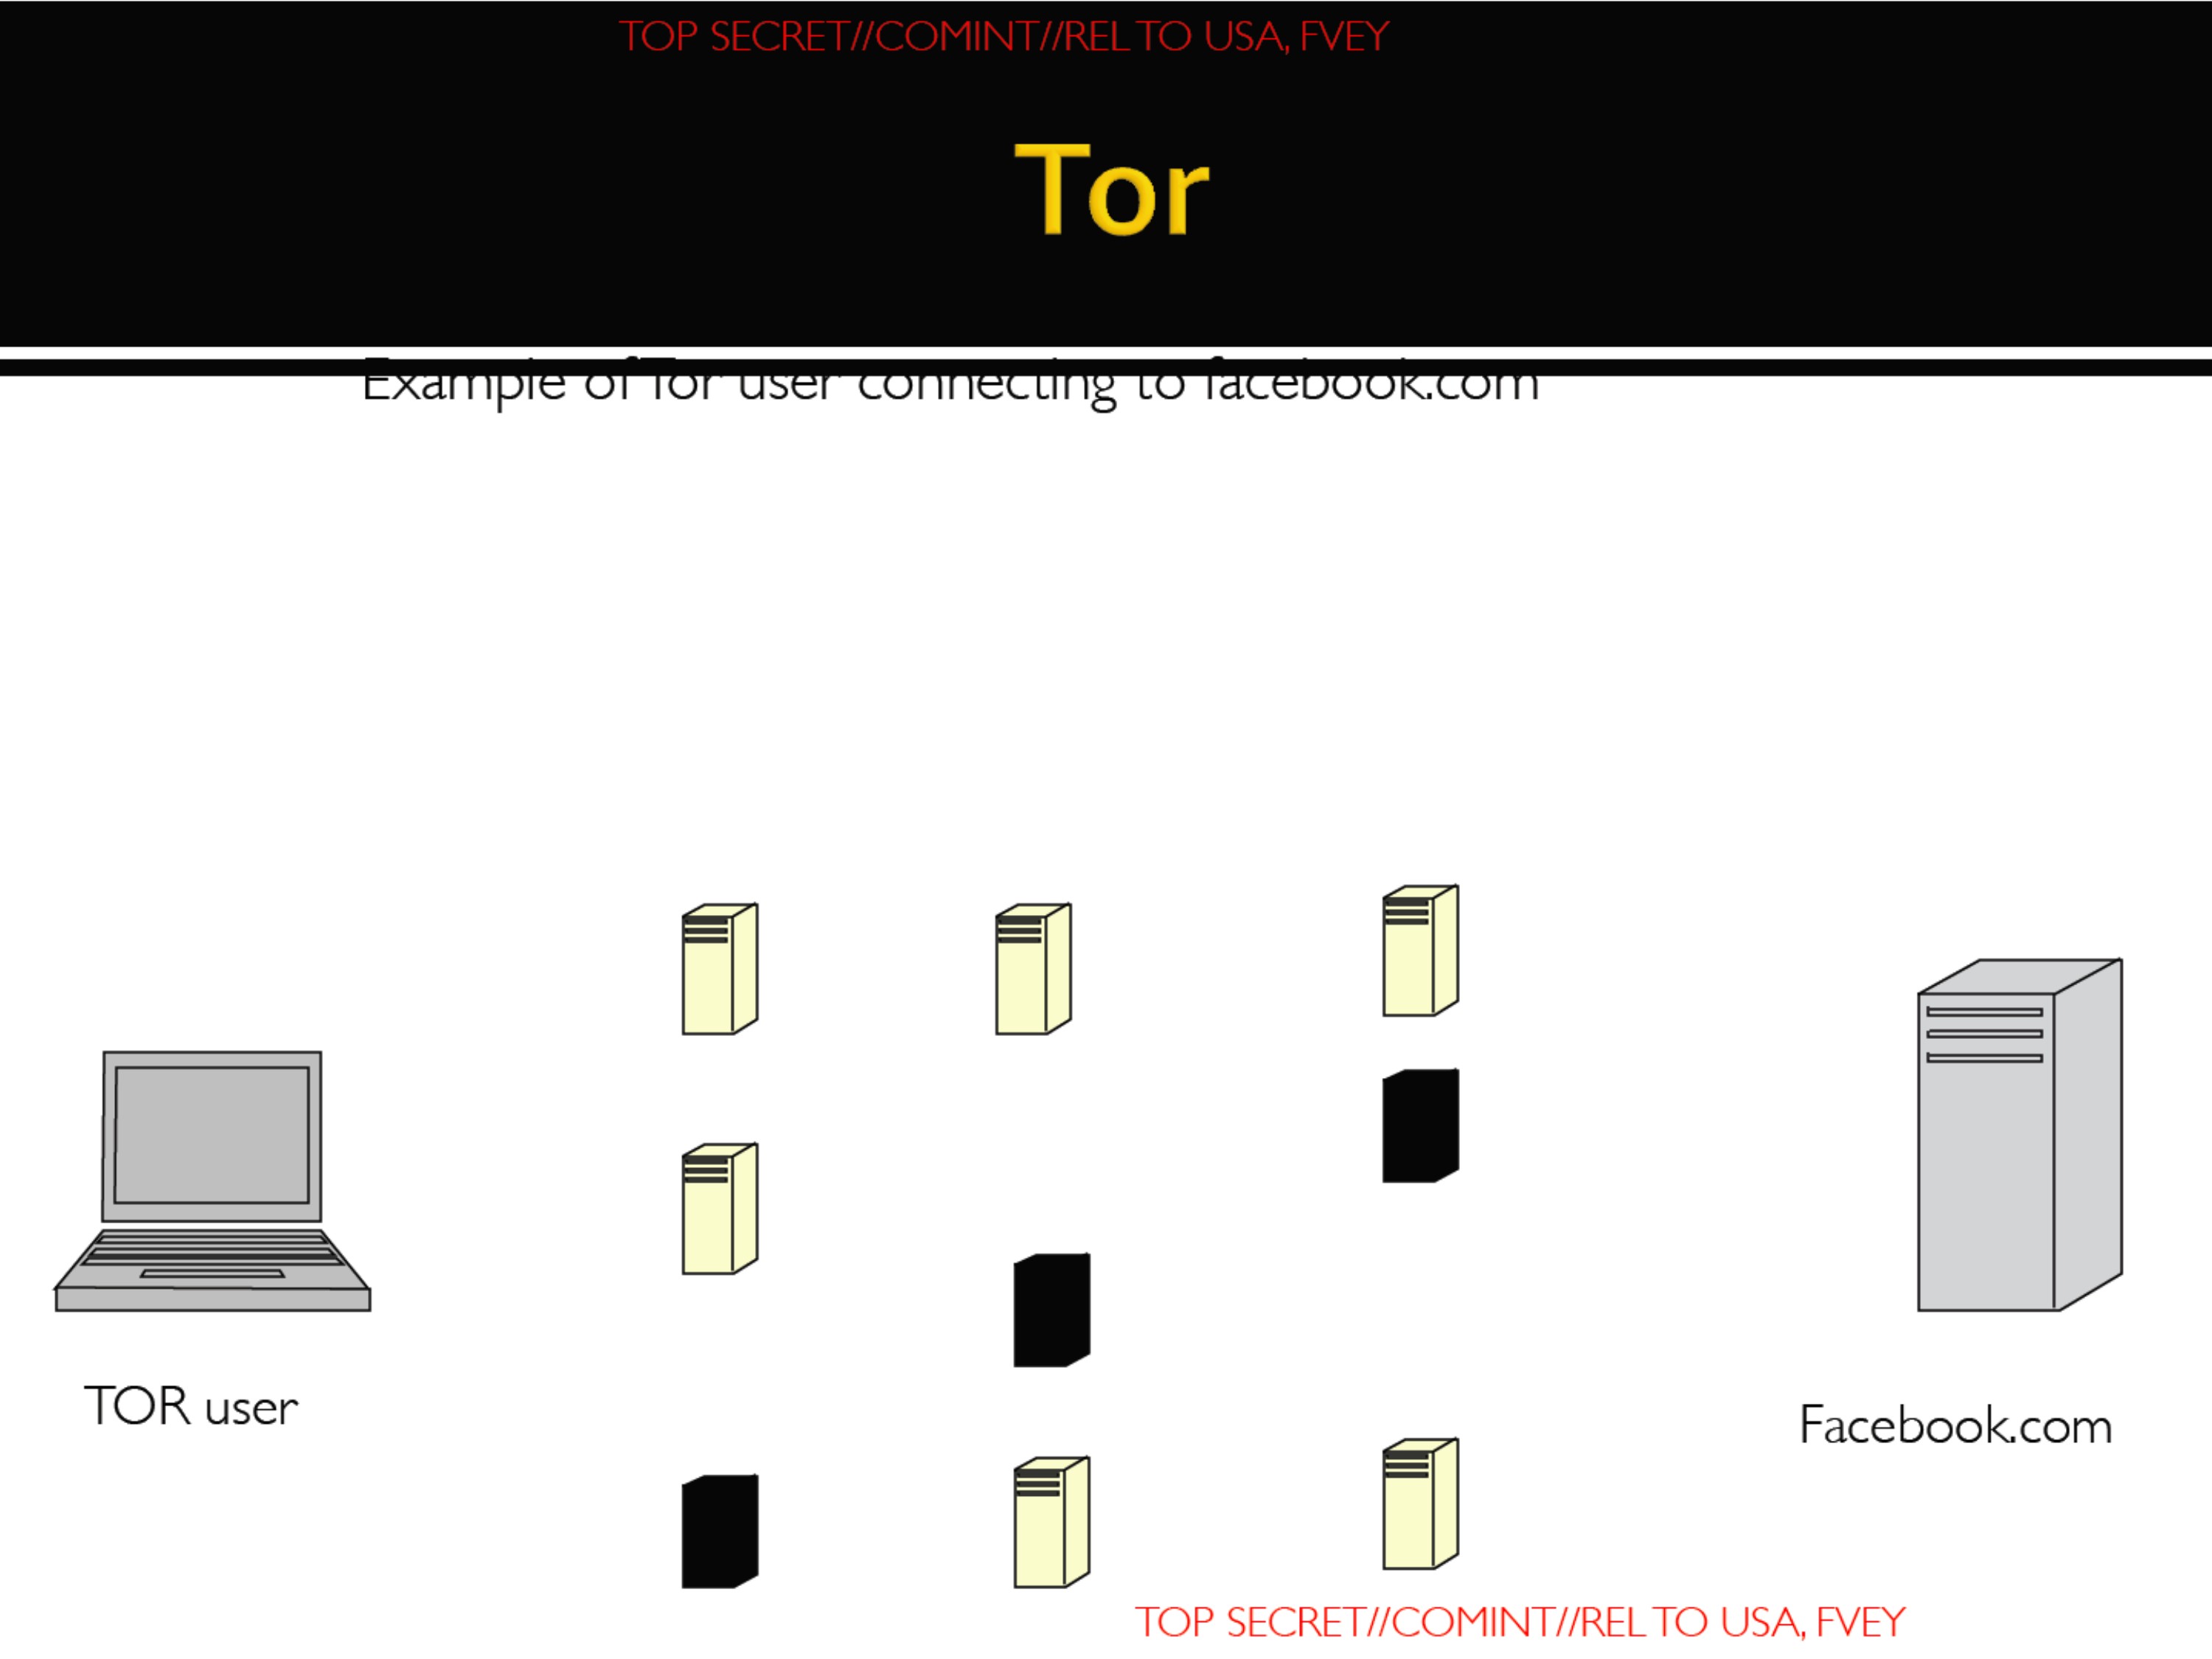
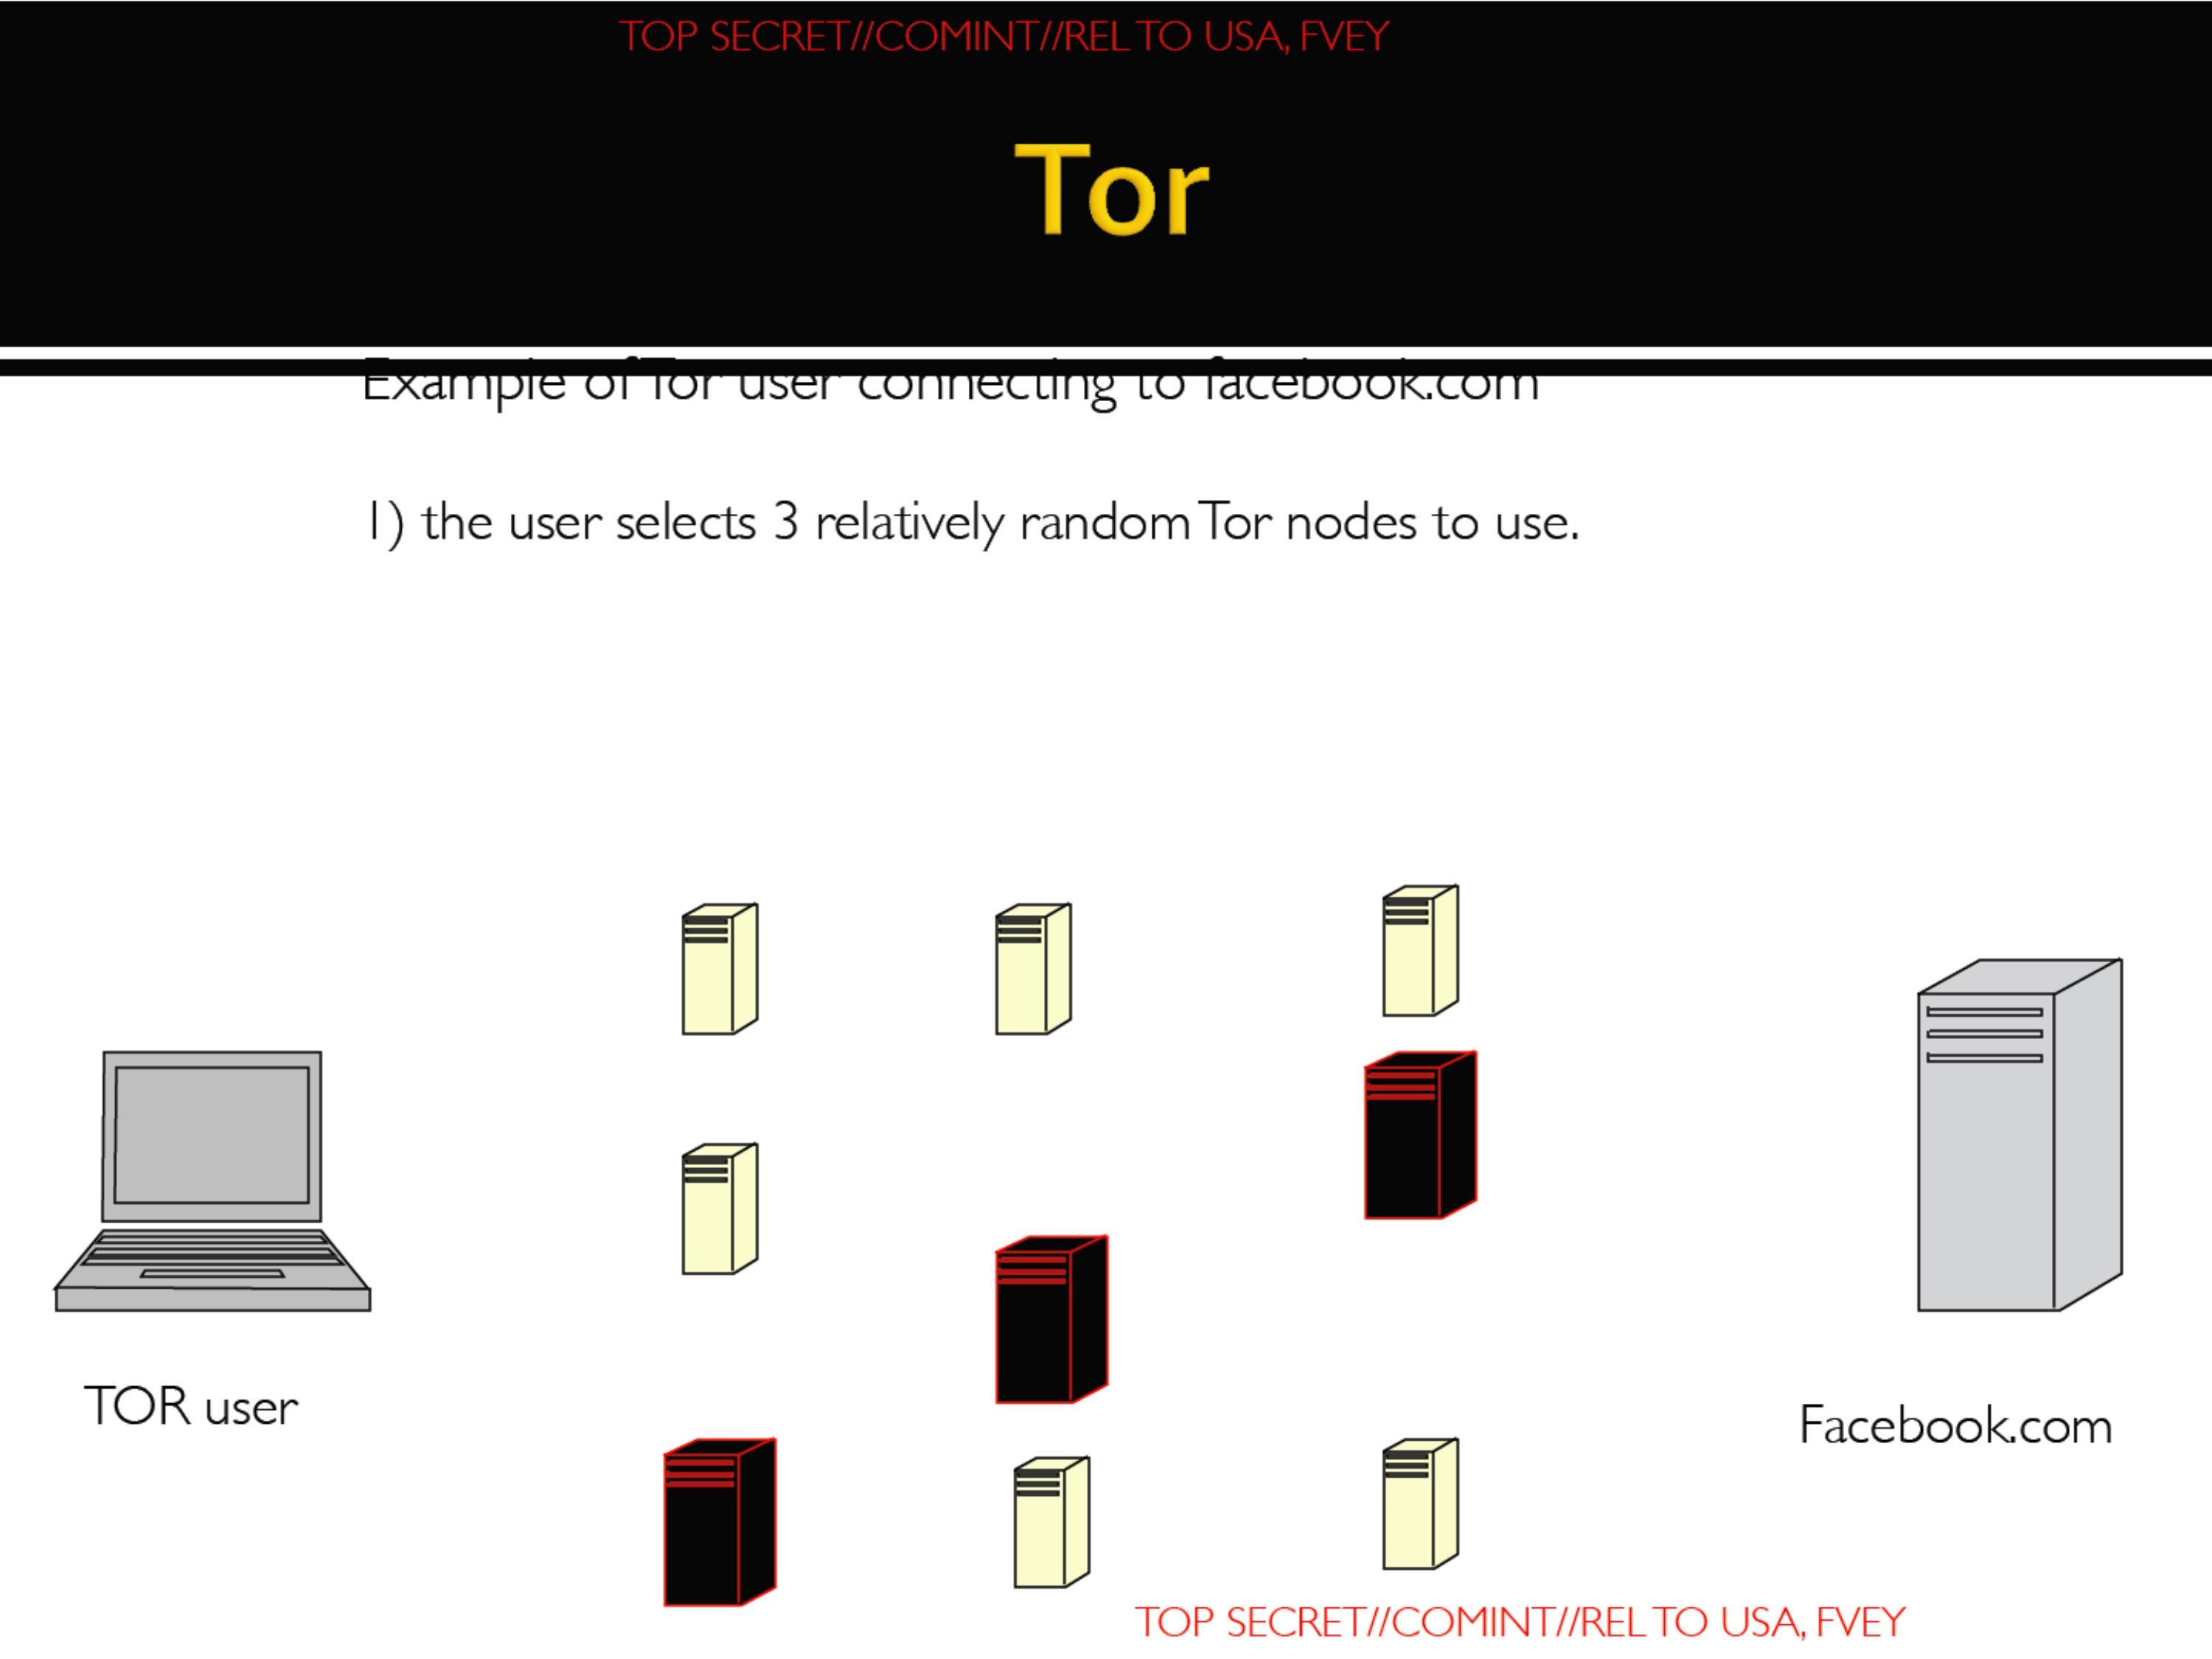
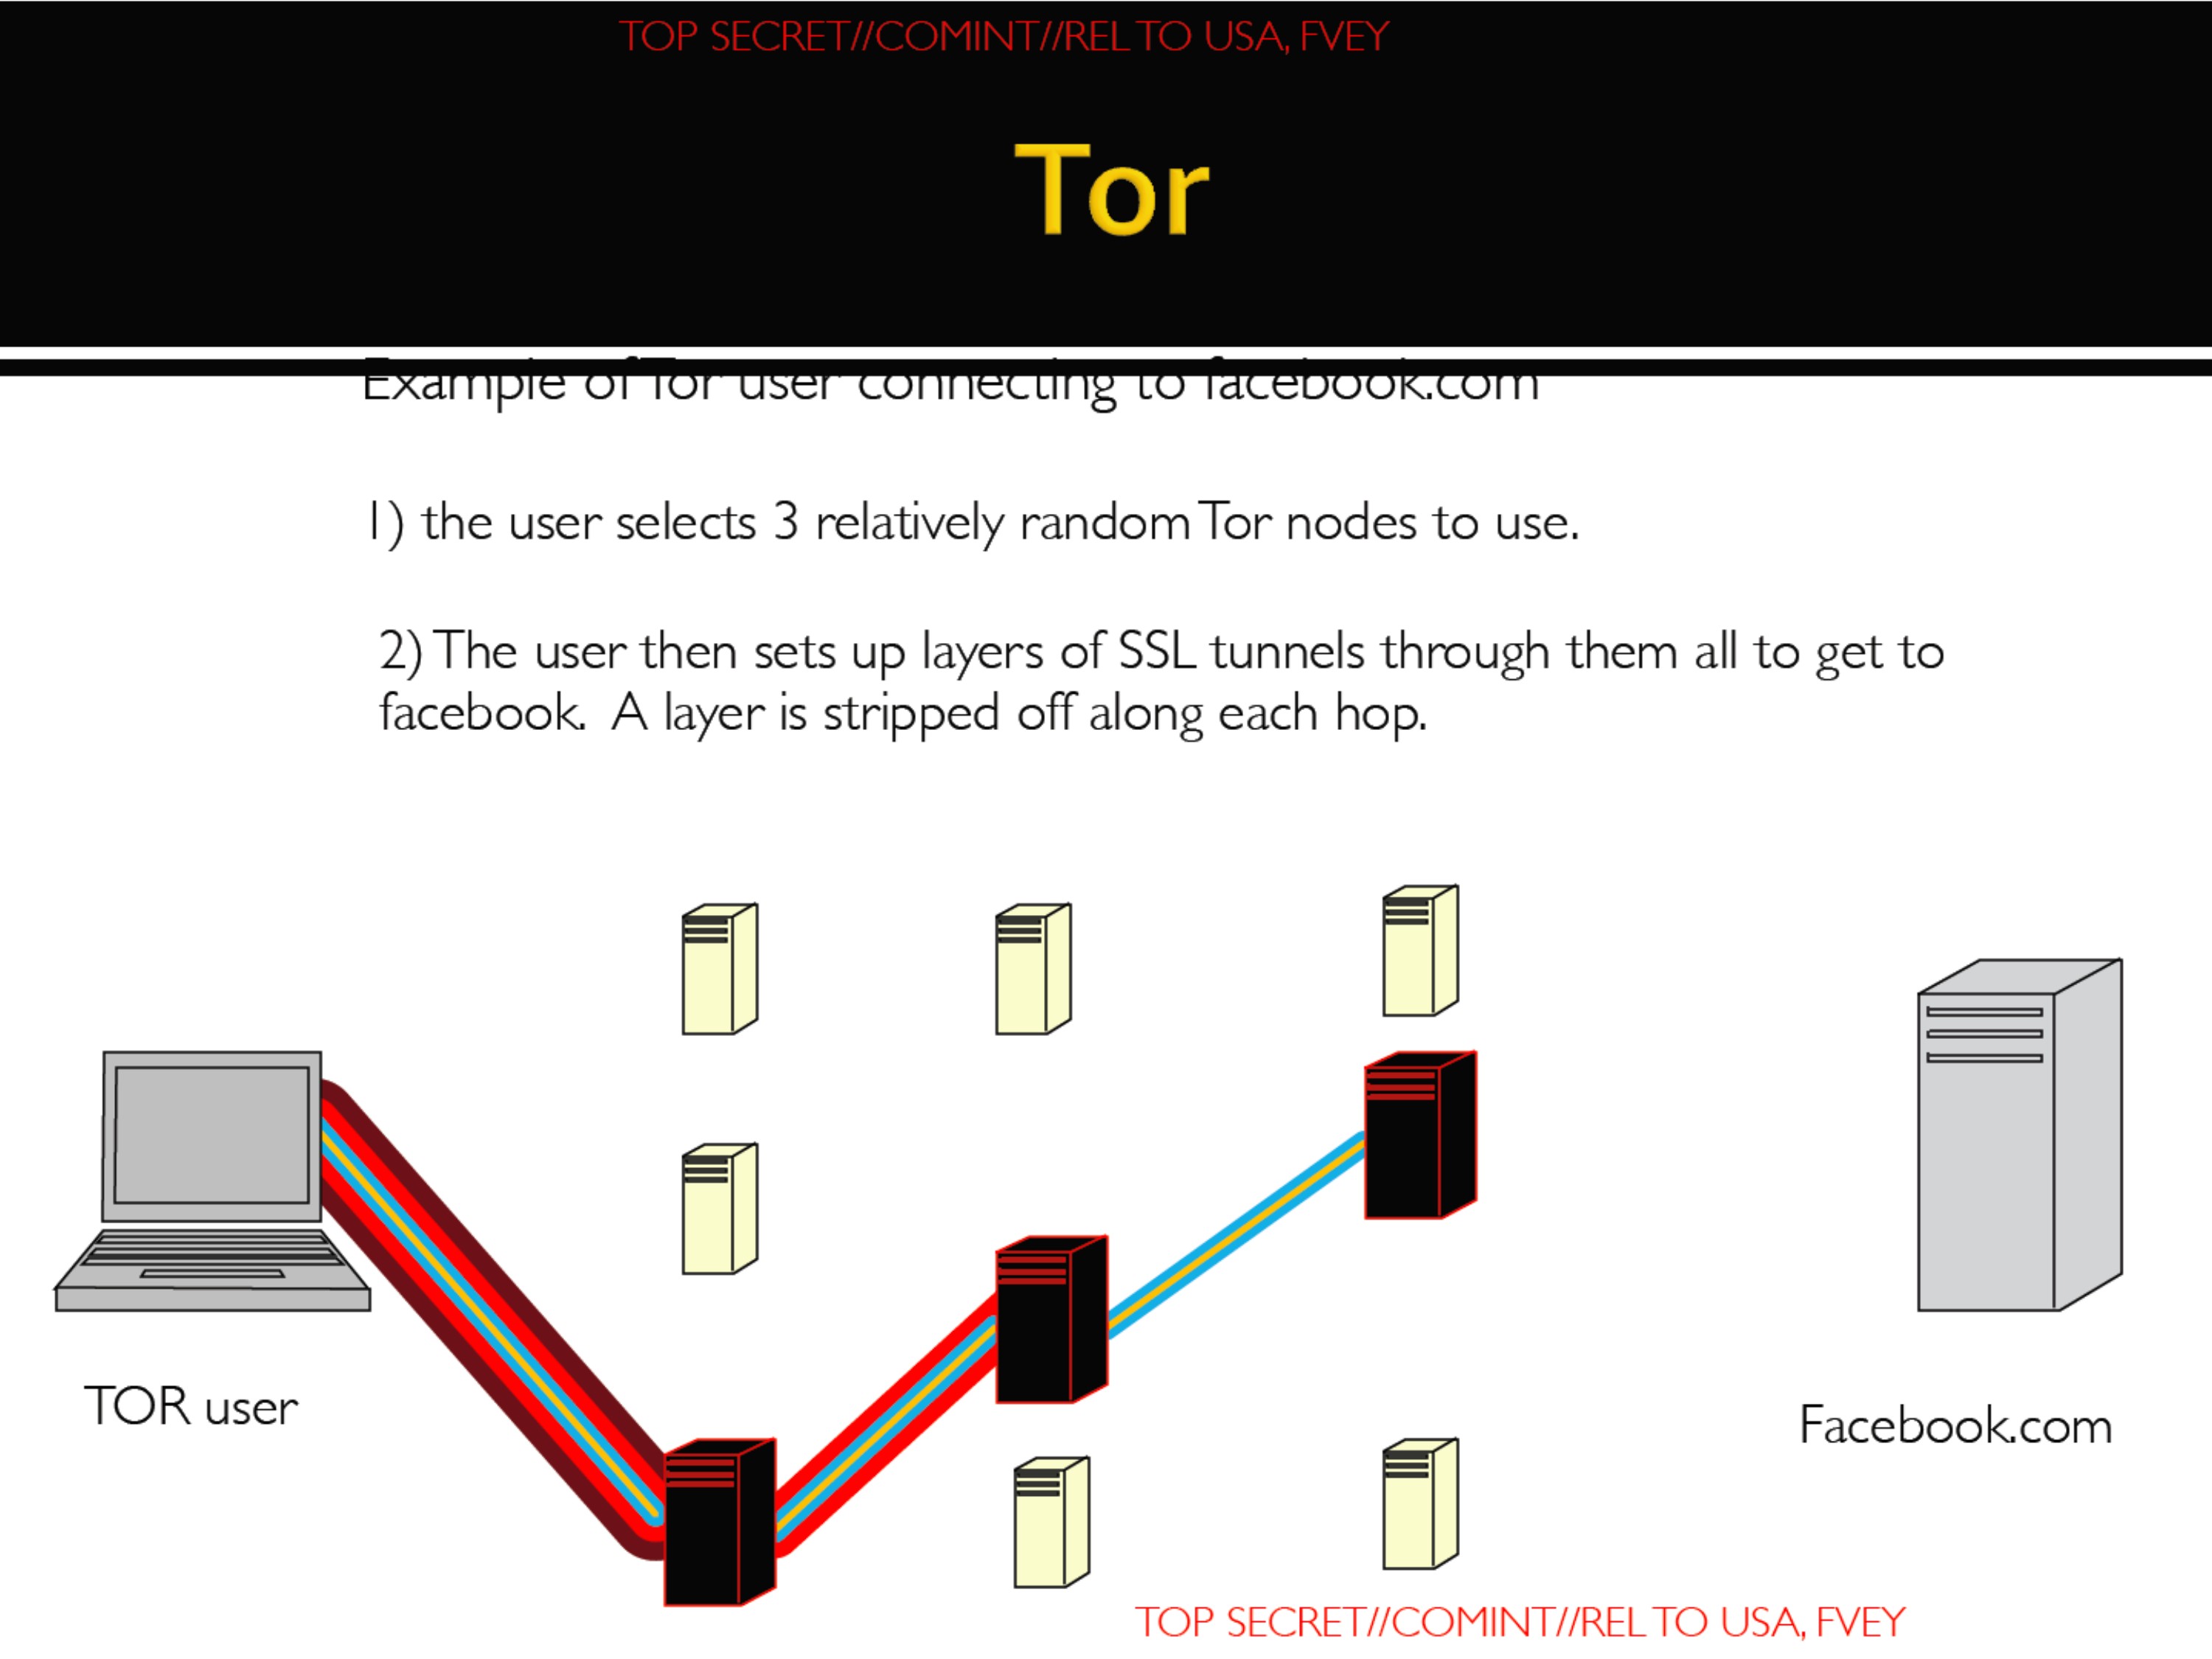
Example of Tor user connecting to facebook.com
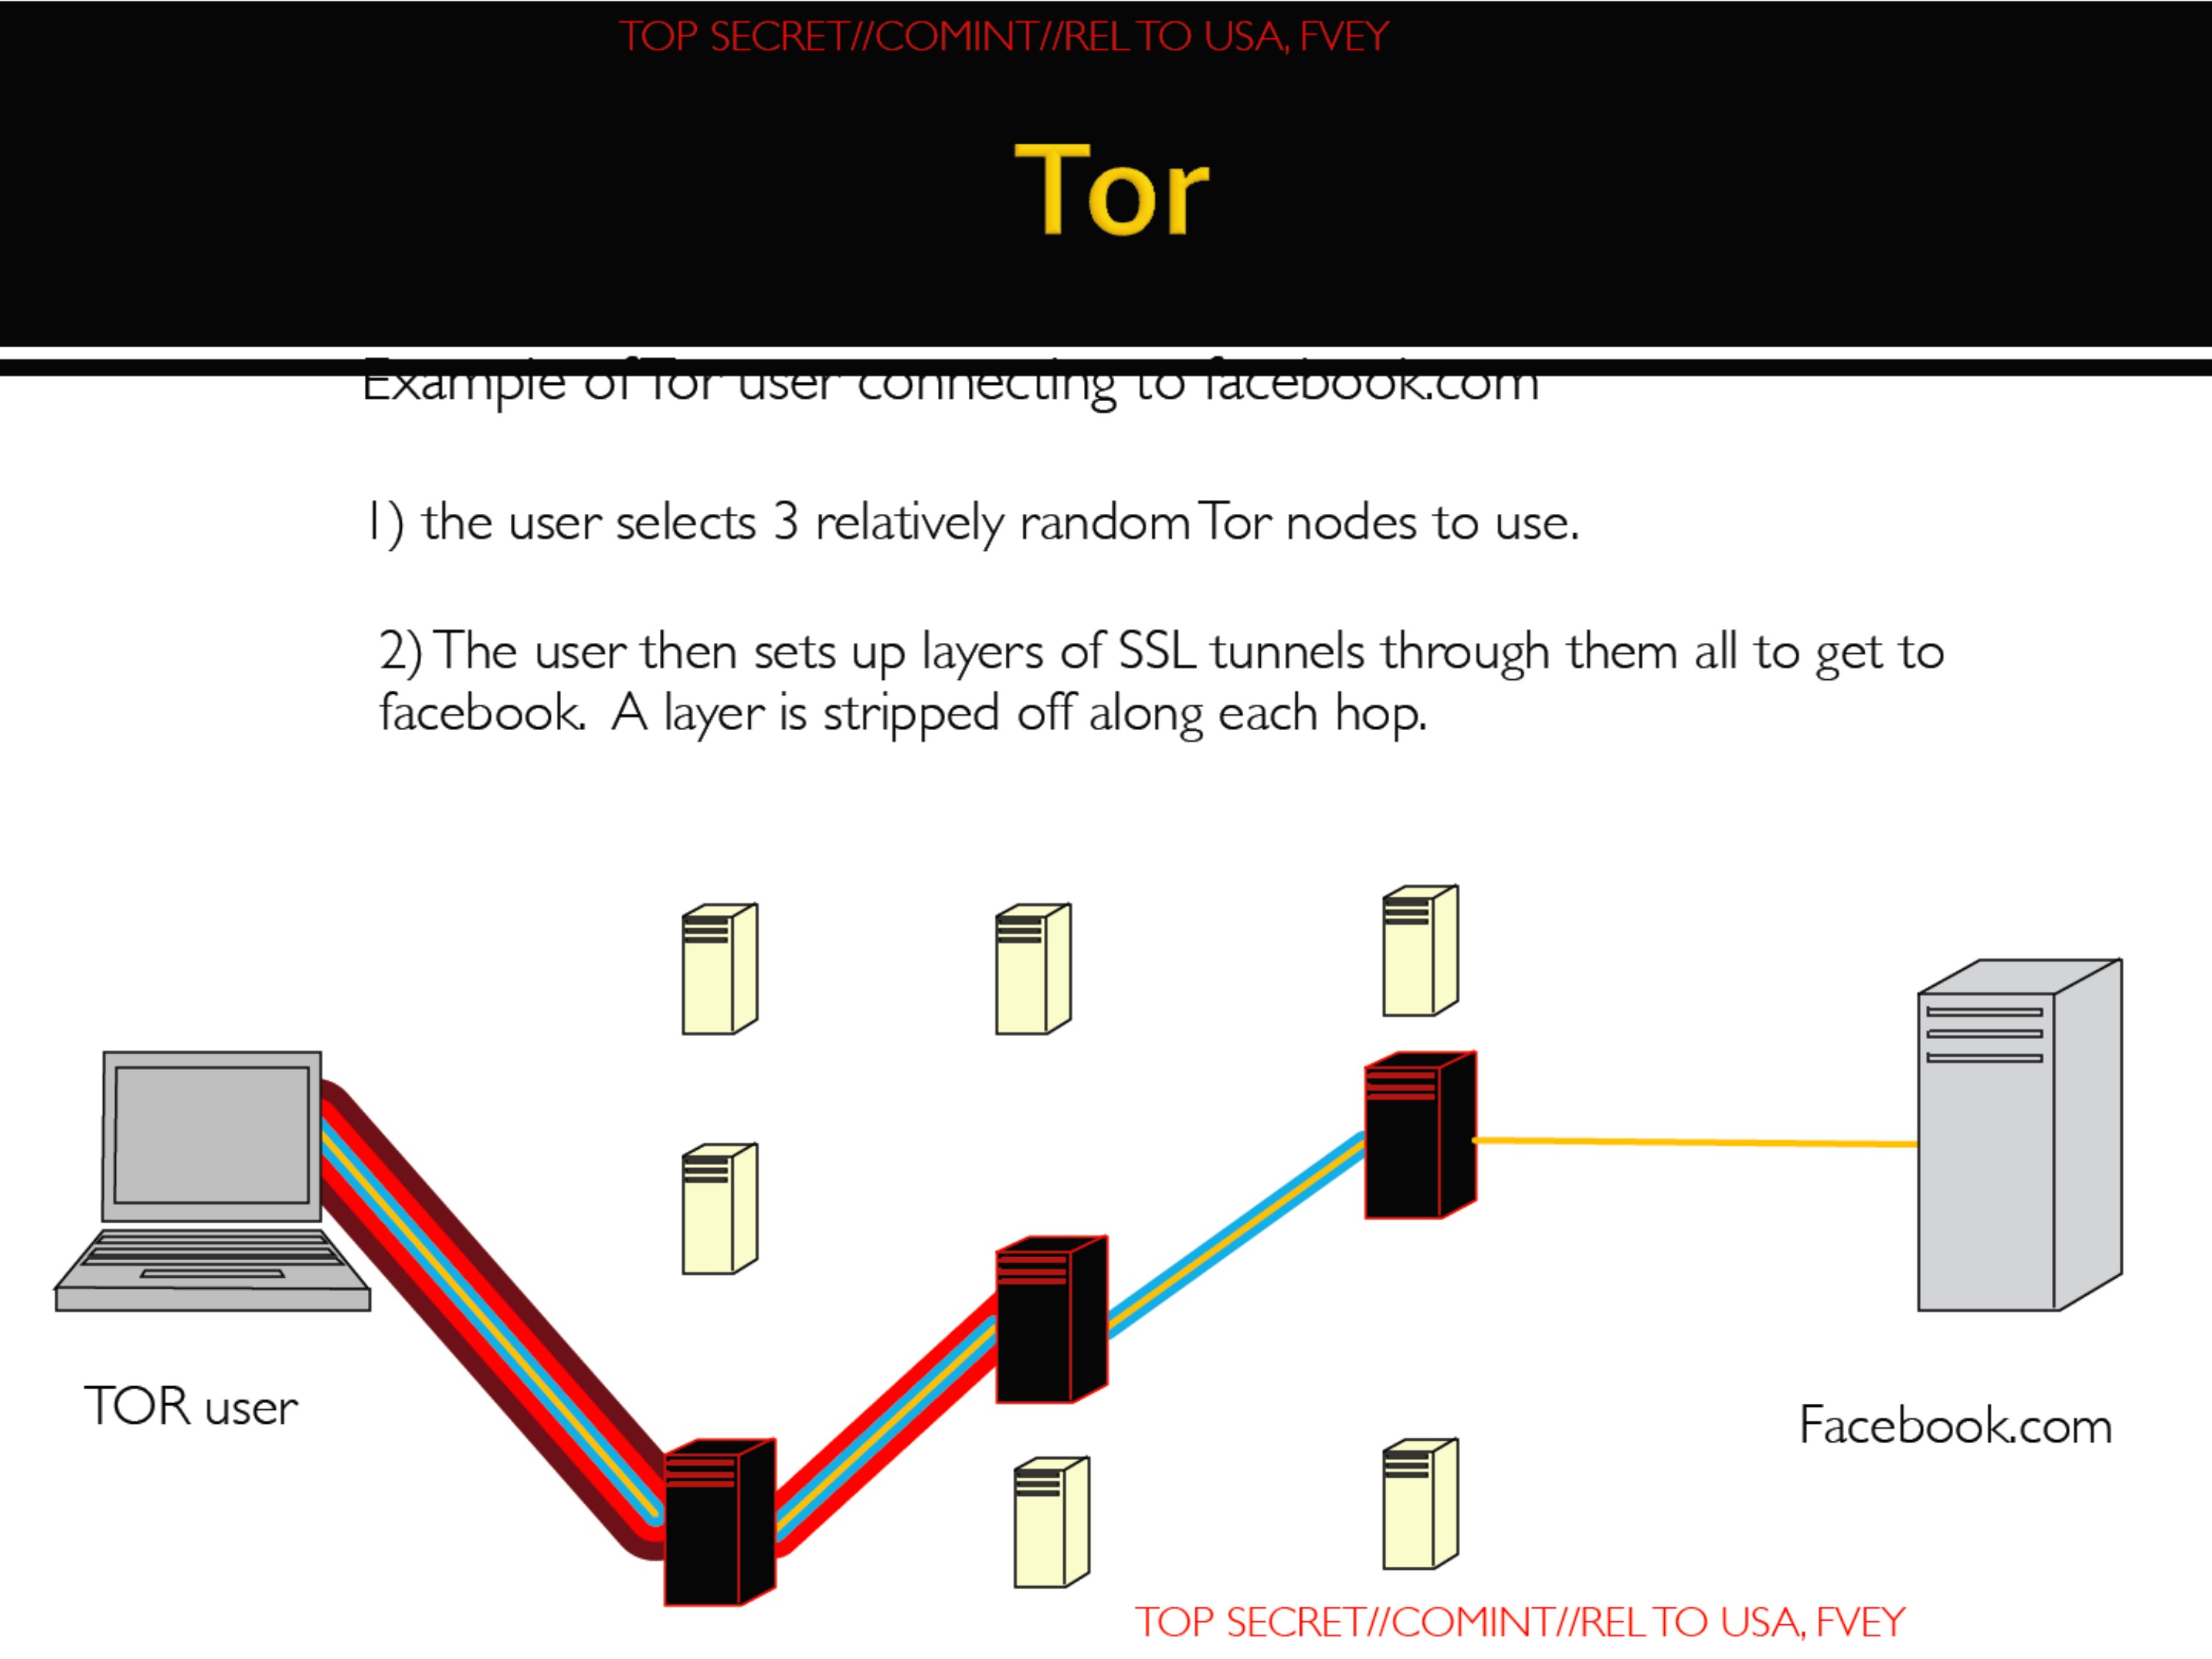
TOR user
Facebook.com
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Tor
Example of Tor user connecting to facebook.com
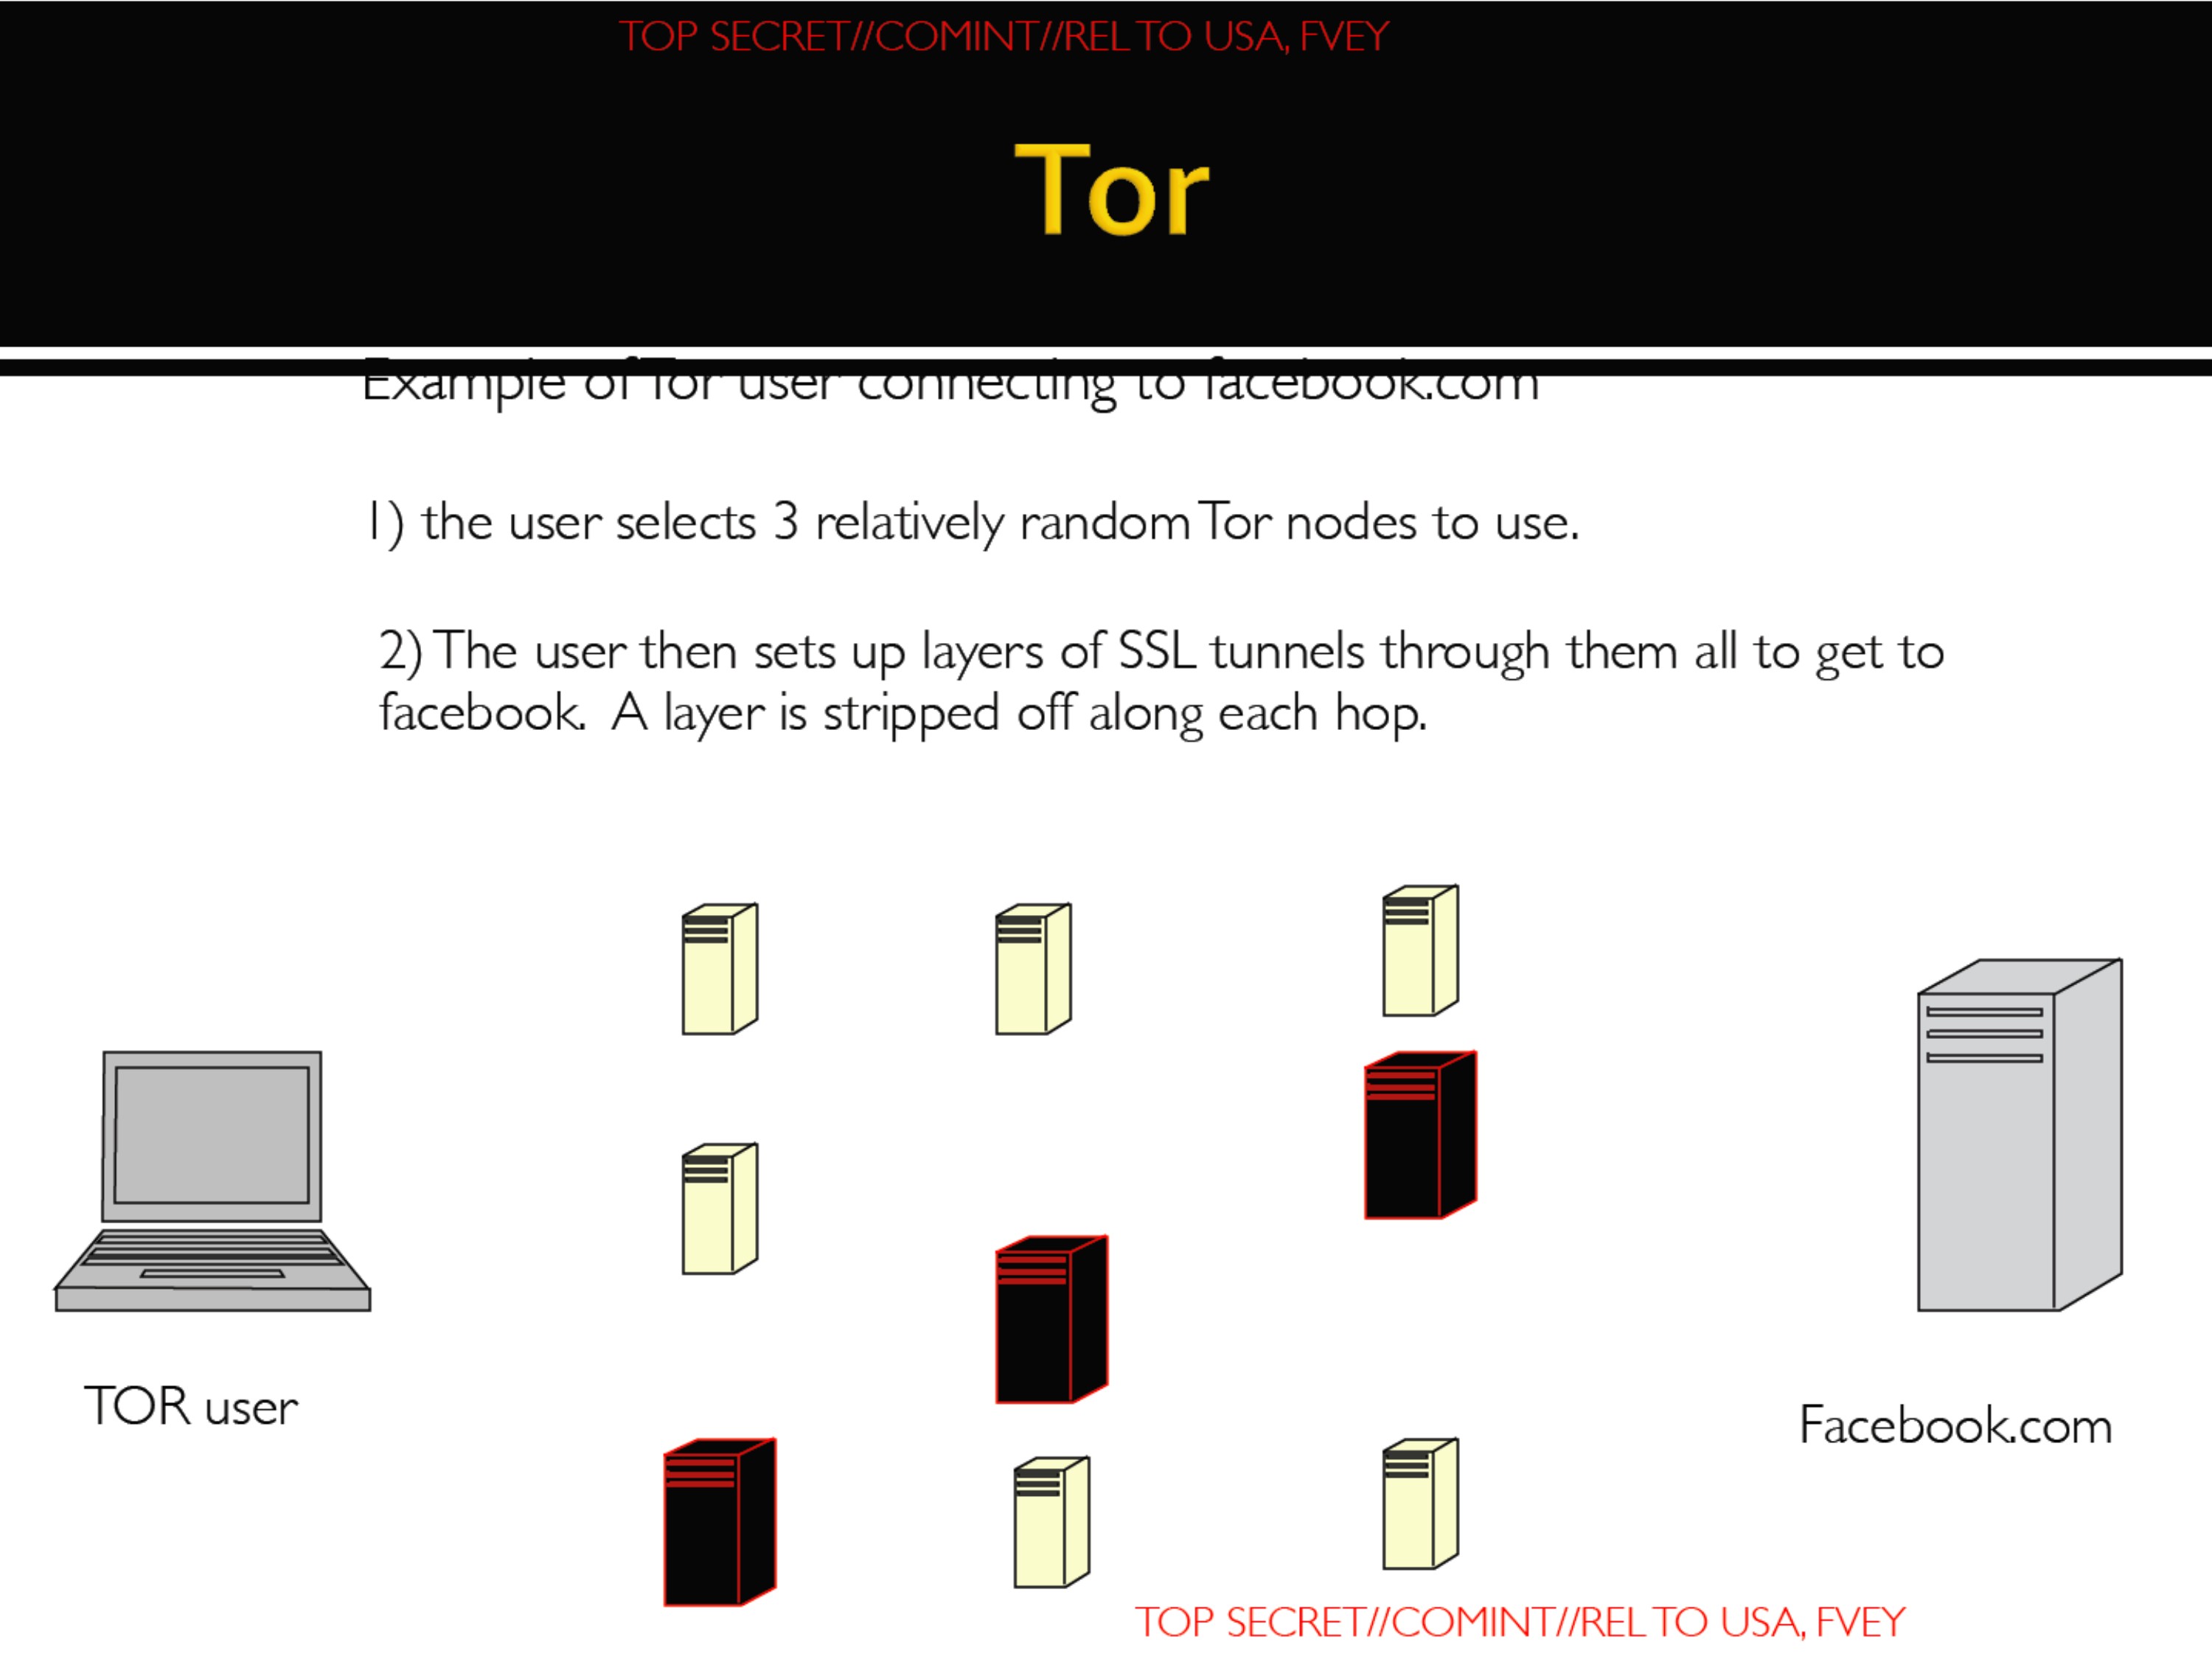
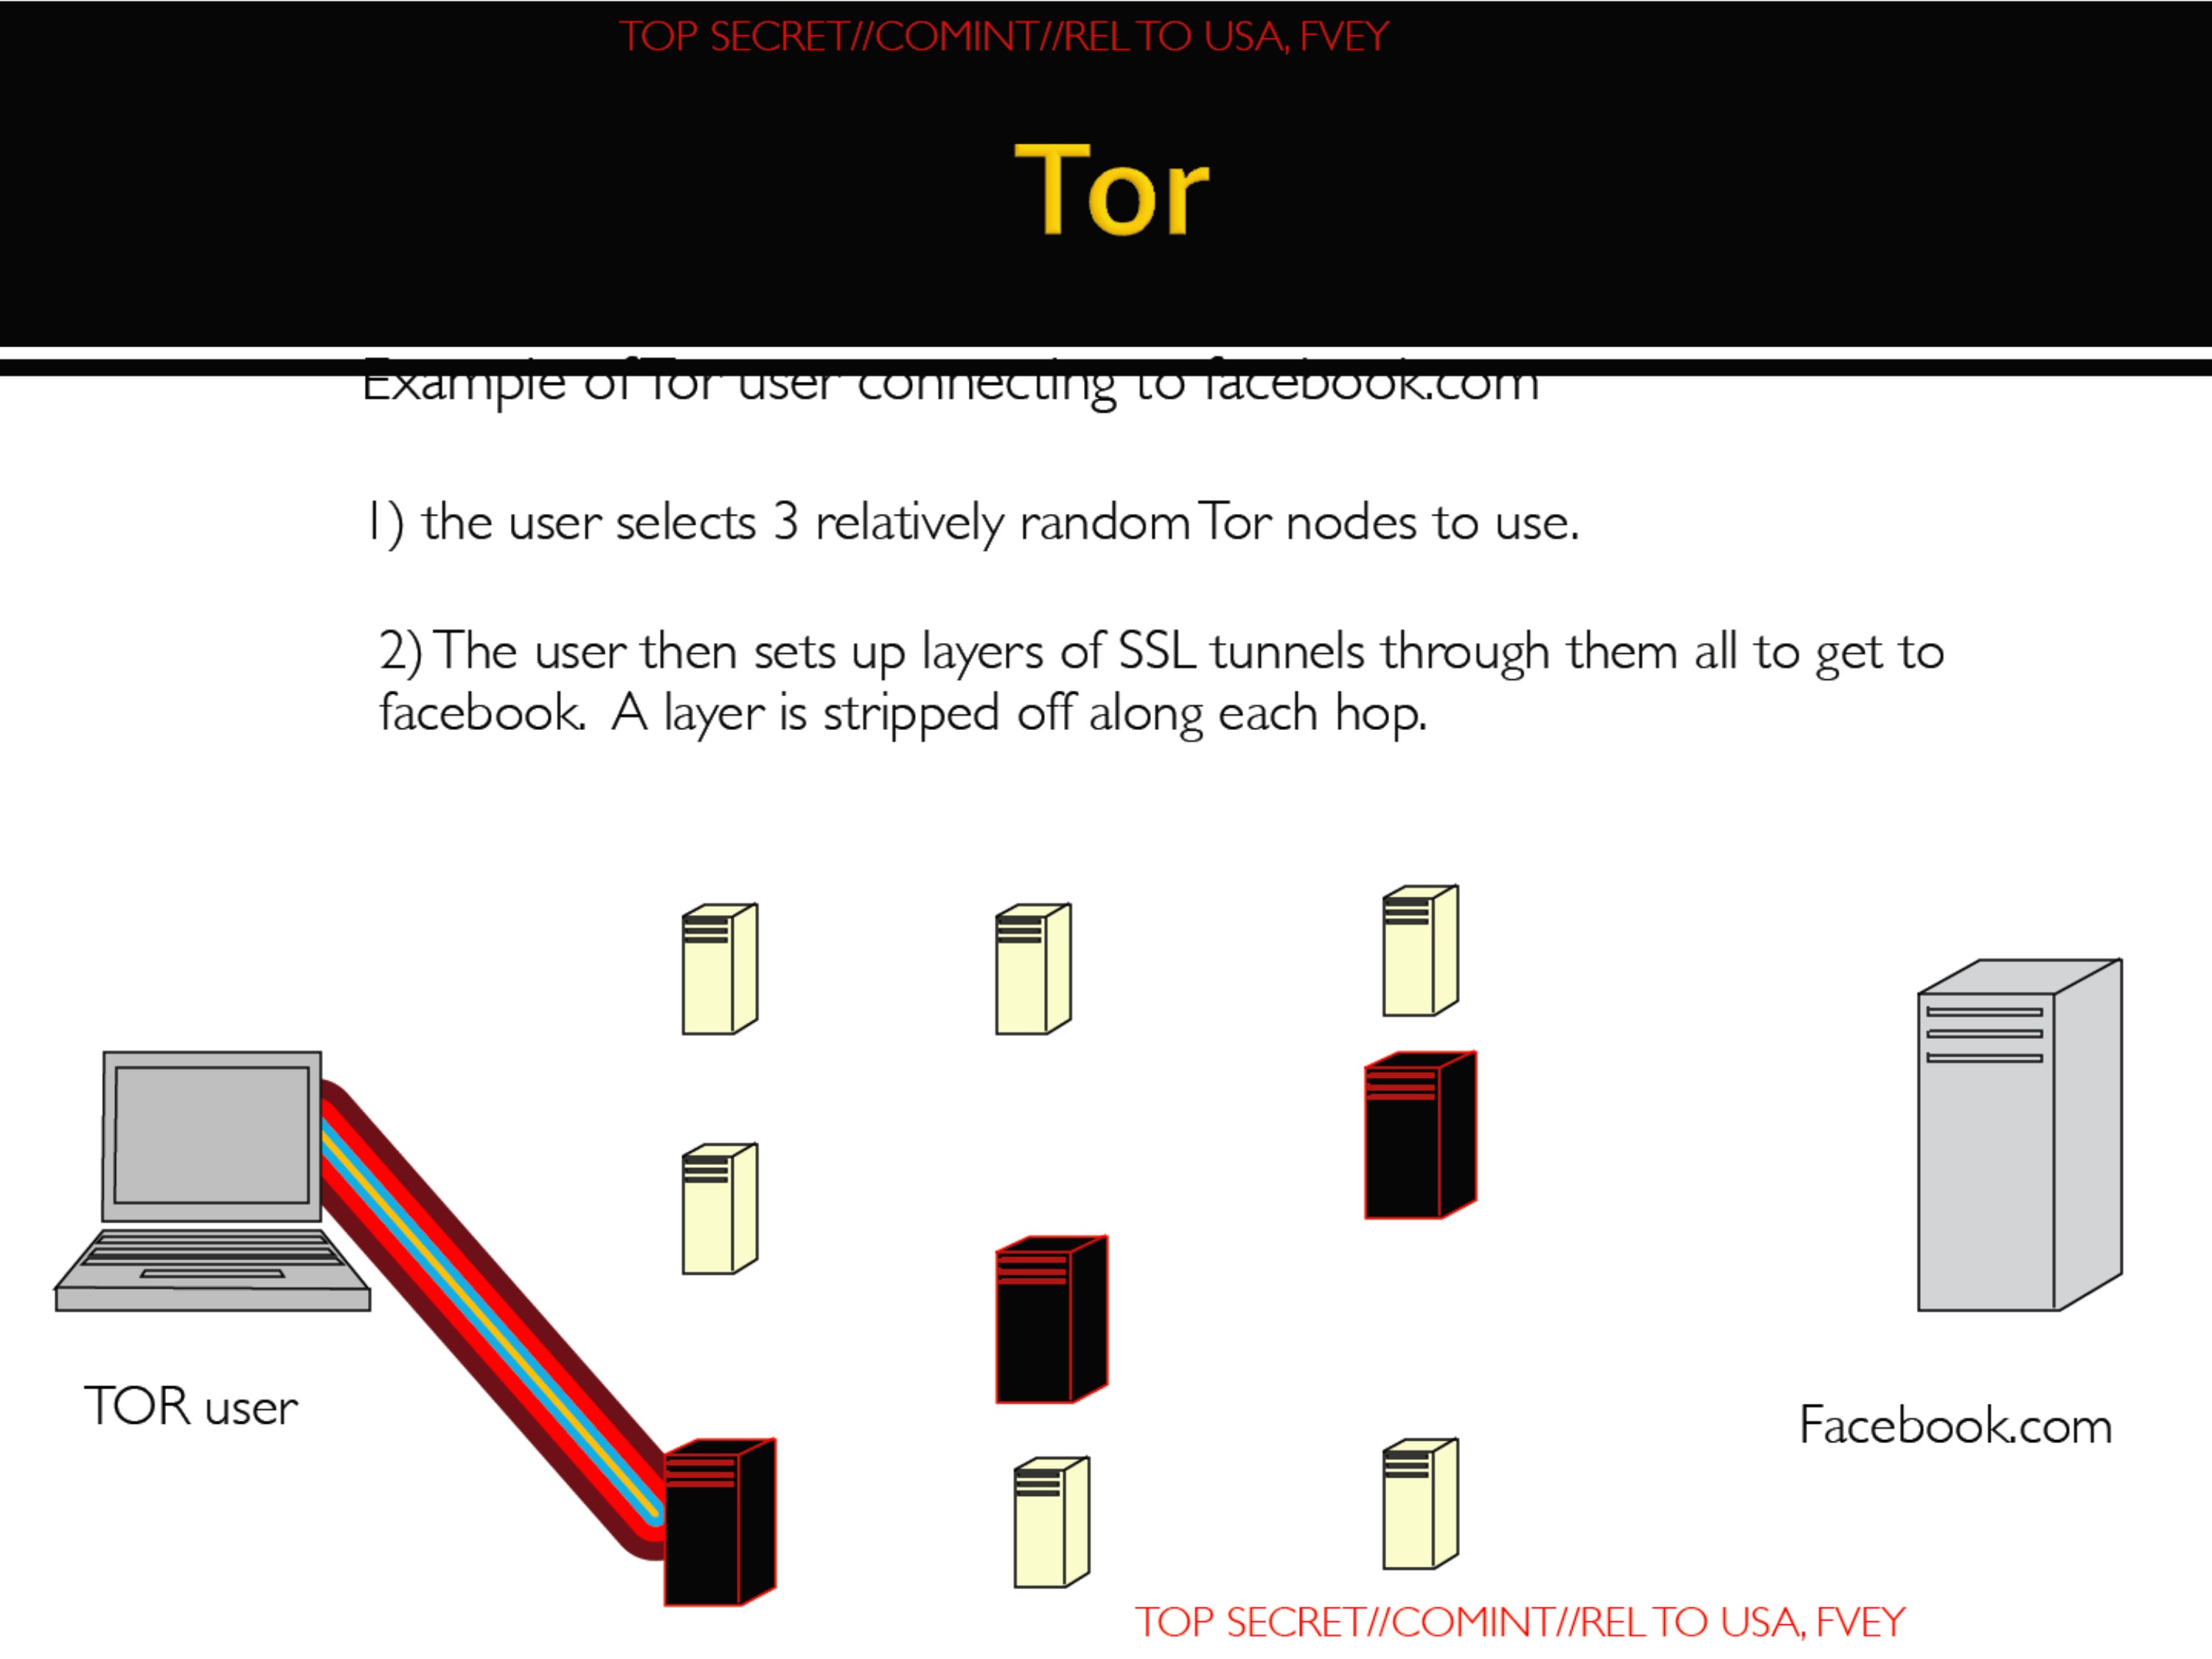
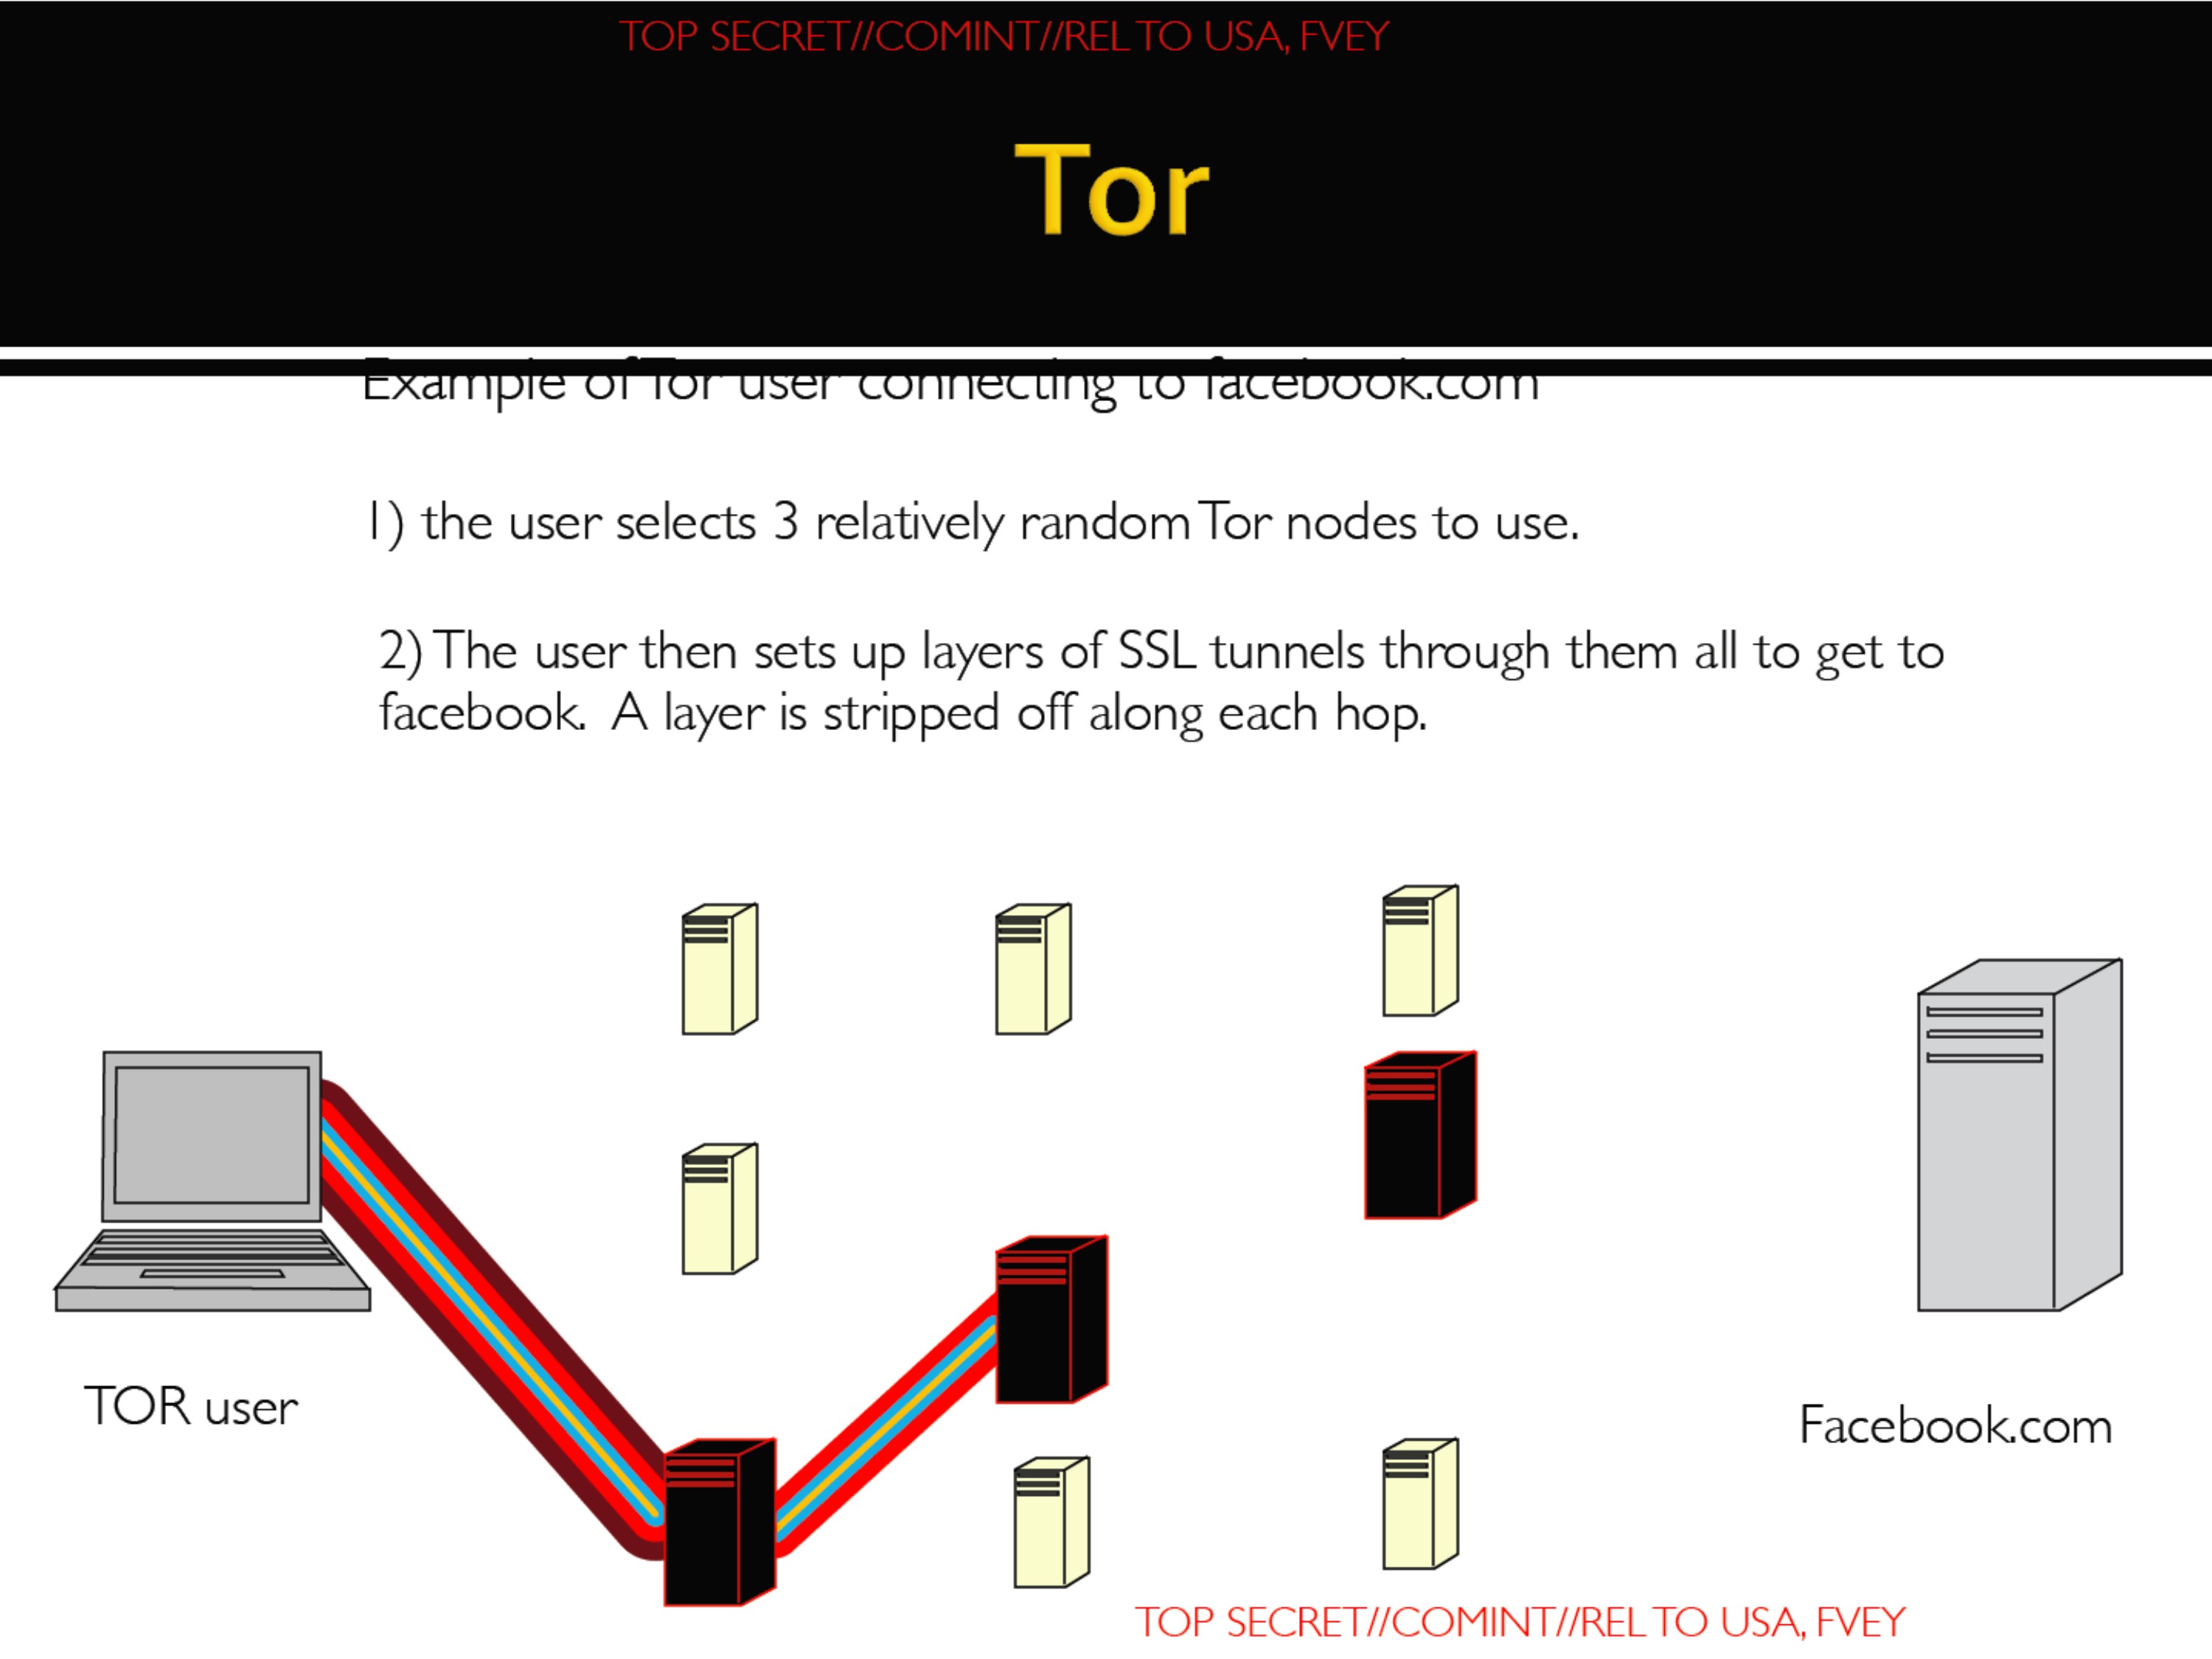
1) the user selects 3 relatively random Tor nodes to use.
TOR user
Facebook.com
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Tor
Example of Tor user connecting to facebook.com
1) the user selects 3 relatively random Tor nodes to use.
2) The user then sets up layers of SSL tunnels through them all to get to facebook. A layer is stripped off along each hop.
TOR user
Facebook.com
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Tor
Example of Tor user connecting to facebook.com
1) the user selects 3 relatively random Tor nodes to use.
2) The user then sets up layers of SSL tunnels through them all to get to facebook. A layer is stripped off along each hop.
TOR user
Facebook.com
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Tor
Example of Tor user connecting to facebook.com
1) the user selects 3 relatively random Tor nodes to use.
2) The user then sets up layers of SSL tunnels through them all to get to facebook. A layer is stripped off along each hop.
TOR user
Facebook.com
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Tor
Example of Tor user connecting to facebook.com
1) the user selects 3 relatively random Tor nodes to use.
2) The user then sets up layers of SSL tunnels through them all to get to facebook. A layer is stripped off along each hop.
TOR user
Facebook.com
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Tor
Example of Tor user connecting to facebook.com
1) the user selects 3 relatively random Tor nodes to use.
2) The user then sets up layers of SSL tunnels through them all to get to facebook. A layer is stripped off along each hop.
TOR user
Facebook.com
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Interesting tidbits about Tor
- TOR uses SSL tunnels for encryption, we are able to identify what their SSL certificates look like (which allows us to identify Tor circuits in SIGINT).
- GOLDENFORTIN dataset and exit node traffic
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
And now for something completely different...
- A lot of research we do on anonymizers consists of open source research:
- The Interwebz (forums, RFC's, 2010 Circumvention Tool Usage Report, etc)
- Trial and Error / Wireshark
- Basically RTFM'ing about how stuff works and translating that to the SIGINT system.
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Contact Info
TOP SECRET//COMINT//REL TO USA, FVEY
TOP SECRET//COMINT//REL TO USA, FVEY
Questions?
NOBODY EXPECTS THE SPANISH INQUISITION!!!!
TOP SECRET//COMINT//REL TO USA, FVEY
Published in the Same Report
(2 documents)
-
Network Shaping 101 [pdf]
An NSA top-secret training presentation that uses Yemen as a case study to explain how to "shape" a nation's Internet traffic by exploiting Autonomous Systems, upstream providers, BGP routing, and physical link topology to redirect or collect communications. The slide deck walks through practical router/IP/link details, passive SIGINT collection points and limitations, and warns that many assumptions are fabricated for the lesson and that real-world capabilities and link behavior can vary.
-
Shaping Diagram [pdf]
This hand-drawn diagram detail an NSA methodology for intercepting and redirecting internet traffic. The approach involves manipulating data flows through a controlled fiber cable, leveraging Computer Network Exploitation (CNE) to capture and replicate target communications for SIGINT processing, all framed in a tongue-in-cheek, yet highly classified, presentation style.
Related Documents
-
Internet Anonymity 2011 [pdf]
A TOP SECRET NSA presentation from 2011 providing a comprehensive survey of Internet Anonymity Technologies (IAT) — covering HTTP proxies, VPN anonymity providers, multi-hop networks including Tor and JAP, anonymous remailers and circumvention tools — alongside NSA's capabilities and limitations against each, including XKEYSCORE fingerprints for VPN identification, the PARTNERSNIPPET Tor deanonymisation team, GOLDENFORTIN Netflow data, and a candid assessment that Tor offers "no passive exploitation."
Programs: FOXTRAIL · NKB · NACIRONIN · PONTENTPOTABLES · RONIN · XKEYSCORE · PARTNERSNIPPET · GOLDENFORTIN · SNAPEPeople: Heap, Austin -
Types of IAT - Advanced Open Source Multi-hop [pdf]
This top-secret NSA/GCHQ document provides a detailed technical overview of the Tor network, including how it works, its strengths as the “king of high secure, low-latency Internet anonymity,” methods for identifying Tor traffic, censorship-driven protocol obfuscation, and ongoing intelligence efforts to analyze, fingerprint, and exploit Tor through passive SIGINT and active research, including collaboration between US and UK agencies.
People: Appelbaum, Jacob -
XKeyscore rules [pdf]
XKeyscore fingerprint and plug-in source code targeting Tor and other anonymity tools — the rules NSA used to flag anyone connecting to Tor directory servers, requesting Tor bridges, visiting the Tor Project or Tails websites, or researching the Tails operating system — including code that specifically excludes Five Eyes users while fingerprinting everyone else, and a note describing Tails as "a comsec mechanism advocated by extremists on extremist forums."
“NSA targets the privacy-conscious” - ARD ↗ (2014-07-03) · Appelbaum, Jacob · Gibson, Aaron · Goetz, John · Kabisch, Volkmar · Kampf, Lena · Ryge, Leif -
Full Log vs HTTP [pdf]
This 2009 NSA training presentation explains the difference between using the "Full Log" and "HTTP Activity" queries in the XKEYSCORE surveillance system, showing analysts how to use both in tandem to gain a complete picture of a target's online activities, including identifying the use of anonymizing proxies.
-
AND THEY SAID TO THE TITANS: « WATCH OUT OLYMPIANS IN THE HOUSE! » [pdf]
This Top Secret CSEC “Olympia” document details a Canadian intelligence program that analyzed and tracked the Brazilian Ministry of Mines and Energy’s telecommunications, mapping IPs, servers, proxies, and mobile devices while automating data collection and network analysis to develop actionable intelligence. It outlines tools, workflows, and contacts used for surveillance, though the presentation does not explain the specific purpose of the operation.
Programs: OLYMPIA · QUOVA · PROMETHEUS · PEITHO · SLINGSHOT · LEVITATE · STRATOS · EVILOLIVE · GCHQ Geofusion · ATLAS · HYPERION · ATHENA · DANAUS · TIDALSURGE · BLACKPEARL · MARINA · STARSEARCH · PEPPERBOX · TRITON · PACKAGEDGOODS · ARK · TOYGRIPPE · FRIARTUCK · MASTERSHAKE · COEUS · STALKER · MAINWAY · FASCIA · SEDB · OCTSKYWARD · FASTBAT · TWINSERPENT · EONBLUE · DISHFIRE · GNDB“Read a CSEC document that was first acquired by Edward Snowden” - The Globe and Mail ↗ (2013-11-30) · “Ministério de Minas e Energia está na mira de espiões americanos e canadenses” - O Globo ↗ (2013-10-06) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Freeze, Colin · Bridi, Sônia · Greenwald, Glenn