Tag: malware 45 documents
Search documents matching “malware” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
HAPPY TRIGGER/LOVELY HORSE/Zool/TWO FACE – Open Source for Cyber Defence/Progress [pdf]
A TOP SECRET STRAP1 COMINT GCWiki page cataloguing GCHQ's open source intelligence gathering for cyber defence, listing approved and pending data sources fed into internal databases HAPPY TRIGGER, LOVELY HORSE, ZooL and TWO FACE, covering malware tracking, vulnerability intelligence, infrastructure mapping and domain monitoring.
Programs: HAPPYTRIGGER · LOVELYHORSE · TWOFACE · ZOOL · XKEYSCORE · POSITIVEPONY · NETPLATE · HIDDENSPOTLIGHT · SNORT · FOXTRAIL · REFRIEDCHICKEN · GEOFUSION · GLOBALSURGE · SHORTFALL · JTRIG · BIRDSEED · BIRDSTRIKE · MARBLEPOLLSPeople: Stewart, Joe -
HIDDENSALAMANDER - Alerting and Characterization of Botnet Activity in TURMOIL [pdf]
This NSA briefing describes HIDDENSALAMANDER, a TURMOIL component that detects, tracks, and characterizes botnet command-and-control traffic on passive collection sensors worldwide, generating enriched metadata about bot herders, infected machines, attack commands, and malware families while providing low-latency defensive alerts when botnet activity involves high-value targets or protected networks. The system extends beyond traditional signature matching by decrypting Zeus RC4-encrypted traffic, extracting payload details like target IPs and DDoS commands, tracking C2 servers across multiple sessions, and categorizing botnet lifecycle stages (configuration, infection, reconnaissance, C&C communication, attack, exfiltration) to support both offensive attribution and defensive response.
Programs: HIDDENSALAMANDER · TURMOIL · CLOUDSHIELD · NETEZZA · TUTELAGE · GMPLACE · RONIN · CYBERCLOUD · MARINA · GHOSTMACHINE · QBOT · ASDF · MARIPOSA · XKEYSCORE · GOGADGET · TURQI · TRAFFICTHIEF · FALLOUT · POUNDSAND · BLUESMOKE · AEG · TURNABOUT · QUANTUMBOT -
HIMR Data Mining Research Problem Book [pdf]
This document is a research roadmap created by GCHQ for the Heilbronn Institute for Mathematical Research (HIMR). Its purpose is to guide long-term mathematical and data-mining research that could improve signals intelligence (SIGINT) capabilities. It outlines key research problems, datasets, and collaboration plans between intelligence agencies and academic researchers. The main goal is to develop new algorithms and mathematical tools to analyze extremely large communications datasets produced by modern surveillance systems.
Programs: CLOUD · DISTILLERY · DISCOVER · PRESTON · LECKWITH · TERRAIN · BROADOAK · NGE · FIVEALIVE · CHARTBREAKER · FIRSTCONTACT · GEOFUSION · RADONSHARPEN-B · PRIMETIME · HIDDENOTTER · BAKERSDOZEN · CLASP · SALTYOTTER · BIRCH · SOLIDINK · FLUIDINK · MAMBA · GRINNINGROACH · PIRATECAREBEAR · AUTOASSOC · CROUCHINGSQUIRREL · HRMAP · KACHINA · SQUEAL · QUESTA · METEORSHOWER · SUNSTORM · GOLDMINE · HAGERAWEL · WOODY · BUZZ · SILVERLIBRARY · SILVERLINING · VALHALLA · MOUNTMCKINLEY · SEPANG · BLACKHOLE · SALAMANCA · HAGELAWEL · LUCKYSTRIKE · SPIKYROCK · MYOFIBRIL · INJUNCTION · PSYCHICSALMON · RAGINGBULLFROG · ROBOTICFISH · TIMIDTOAD · AURA · CARBONCOPY · CASK · CHORDAL · CRAN · INSTINCT · MADFORGE · SWAMP · VOLSUNGA · WHITERAVEN · MVR · PPF · JTRIG · MAPREDUCE · MAILORDERPeople: Tukey, John -
Industrial-Scale Exploitation [pdf]
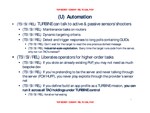
This top-secret NSA document details the operational philosophy behind the TURBINE system's transition to "industrial-scale exploitation." By integrating with both active and passive sensors, TURBINE automates the delivery of malware and the maintenance of network implants, specifically targeting routers and server-side code execution.
-
Intellipedia – BIOS Threats [pdf]
This from an internal wiki for the U.S. intelligence community, titled “BIOS Threats” details the use of malicious BIOS implants as a means of achieving persistent system compromise for cyber espionage and attack purposes. It discusses the history, technical challenges, detection limitations, and global development of BIOS-based malware by both state and non-state actors, including U.S. and Chinese cyber units.
-
Is there "fifth party" collection? [pdf]
This NSA internal Q&A forum discussion reveals "fifth party collection"—where the NSA passively intercepts data from one intelligence service (South Korea) that has compromised another service's (North Korea) computer network exploitation operations, creating a three-layer chain where NSA exploits Actor One's access to Actor Two's CNE activities against shared targets. The thread provides concrete examples including NSA leveraging South Korean implants on North Korean officials' computers (who themselves were conducting CNE operations) and stealing zero-day exploits from unidentified foreign intelligence services by passively monitoring their successful attacks.
-
NDIST — GCHQ’s Developing Cyber Defence Mission [pdf]
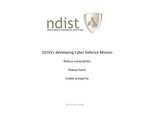
GCHQ’s NDIST sets out a developing cyber defence mission to reduce vulnerability and harm while enabling prosperity, centered on building a global-level picture of strategic threats and sharing intelligence with allies. The team anchors this work in massive telemetry, claiming roughly 100 million malware events collected per day to drive situational awareness.
-
Notes for Dutch SIGINT/Cyber Analytic Exchange [pdf]
This document provides top-secret notes between the NSA and the Dutch intelligence services (AIVD and MIVD). This document outlines a significant restructuring of the Dutch intelligence community, including the creation of a unified SIGINT and Cyber Division and a Single Point of Contact (SPOC) at AIVD headquarters in Zoetermeer. The briefing details the operational challenges of the newly formed National Cyber Security Center (NCSC), the development of the National Detection Network (NDN) for cyber sensors, and the shared technical interests between the two nations regarding malware detection, Tor (The Onion Router) exploitation, and the analysis of web forums via Computer Network Exploitation (CNE).
Programs: TUTELAGE -
NSA Intelligence Relationship with Sweden [pdf]
A 2013 NSA information paper documenting the agency's long-standing intelligence partnership with Sweden's signals intelligence service FRA, covering joint collection on Russian targets, counterterrorism, cryptanalysis, and cyber defense — a relationship kept classified due to Sweden's official political neutrality.
-
NSA QUANTUM Tasking Techniques for the R&T Analyst [pdf]
A classified NSA training presentation, prepared by Booz Allen Hamilton, walking analysts step-by-step through how to secretly hack into a target's computer by hijacking their everyday internet traffic — exploiting platforms like Yahoo and Facebook to silently inject malware without the target's knowledge.
Programs: QUANTUM · QUANTUMTHEORY · QUANTUMNATION · VALIDATOR · COMMONDEER · SEASONEDMOTH · SMOTH · MARINA · FOXACID · RADIUS · QUANTUMBISCUIT · ALTEREGO · DOGCOLLAR · FOREMAN · ANCHORY · BRUTUS · REACTOR · SPARKLEPONY · WINDCHASER · YACHTSHOP · MUTANTBROTH · FOXSEARCH · WHITELIST · SSO · PSC -
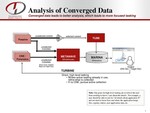
NSA Technology Directorate Analysis of Converged Data [pdf]
This document outlines the strategic integration of passive and active signals intelligence (SIGINT) to create a more efficient surveillance loop. The document centers on TURBINE, an intelligent command-and-control system designed to manage a massive network of malware implants (Computer Network Exploitation or CNE). The primary goal is to automate the extraction of data from targeted machines, effectively "converging" traditional passive collection with active hacking to refine intelligence tasking.
-
Pay attention to that man behind the curtain: Discovering aliens on CNE infrastructure [pdf]
CSEC briefing from 2010 outlines Canada’s counter–computer network exploitation efforts to detect, analyze, and pursue foreign and friendly cyber actors operating on shared CNE infrastructure. It details tools, methods, and a case study showing how hidden implants and overlapping state-sponsored operations were uncovered and attributed.
Programs: SNOWGLOBE · WARRIORPRIDE · DAREDEVIL · SLIPSTREAM · CHORDFLIER · NAMEDROPPER · WORMWOOD · REPLICANTFARM · OBELIX · SHEPHERD · CARBON · ALOOFNESS · REGBACKUP · DOGHOUSE · WALKER · CHOCOPOP · BLAZINGANGEL · WINDO · QUIVERINGSQUAB · DIESELRATTLE · CYDLL · CIVETCAT · WIDOWKEY · LASEX · PULLEDPORK · MAKERSMARK · FANNER · SEEDSPHERE · BYZANTINE · VOYEUR · SUPERDRAKE · GOSSIPGIRL · WATERMARK · DOURMAGNUM -
Project CAMBERDADA [pdf]
NSA presentation on Project CAMBERDADA, a programme that intercepts emails sent to antivirus companies reporting new malware, uses SIGINT collection to monitor antivirus vendor communications, and identifies opportunities to repurpose malware before vendors detect it — listing 23 antivirus companies from around the world as targets, with Kaspersky as the primary focus.
People: Picard, François -
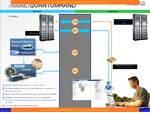
QUANTUMHAND [pdf]
This slide describes QUANTUMHAND, a specialized "Man-on-the-Side" (MOTS) attack used by the NSA's Tailored Access Operations (TAO) to infect targets visiting Facebook. The document outlines an automated process where the NSA's surveillance infrastructure, TURMOIL and TURBINE, detects a target's connection to Facebook and "races" against the legitimate Facebook server to deliver a malicious response first. This "winning the race" allows the NSA to redirect the user to a TAO server that attempts to deploy malware "implants" on the target's computer.
-
QUANTUMINSERT [pdf]
This top-secret NSA presentation provides a step-by-step visual walkthrough of a man-on-the-side (MOTS) attack. This technique allows the NSA to covertly redirect a target's web browser to a malicious server in order to install a malware implant. The diagrams illustrate the interaction between the NSA's global surveillance sensors (TURMOIL) and its automated command-and-control system (TURBINE), demonstrating how the agency exploits the fundamental "race condition" of the internet to compromise a target.
-
QUANTUMTHEORY (2010 SIGINT Development Conference) [pdf]
This 2010 NSA presentation reveals QUANTUMTHEORY, a suite of "man-on-the-side" network attack technologies that enable real-time injection and manipulation of TCP/IP connections through passive surveillance infrastructure. The system encompasses multiple specialized attack techniques including HTML redirection, DNS hijacking, botnet takeover, and database injection, deployed at Five Eyes surveillance sites worldwide.
Programs: QUANTUMTHEORY · TRAFFICTHIEF · TURMOIL · TURBINE · QUANTUM · NINJANIC · ISLANDTRANSPORT · SURPLUSHANGER · DAREDEVIL · STRAIGHTBIZARRE · QUANTUMINSERT · QUANTUMSKY · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMDNS · QUANTUMBOT2 · QUANTUMCOPPER · QUANTUMMUSH · HUFFMUSH · QUANTUMSPIM · QUANTUMSQUEEL · QUANTUMSQUIRREL · INCENSOR · SMOKEYSINK · SARATOGA · QUANTUMDEFENSE · TURBULENCE“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
Seminar: Threats to Computer Systems SIDtoday [pdf]
CIA senior adviser Brian Shaw will lead a seminar about “an invisible subculture” that “exists to take advantage of computer networks for nefarious purposes including vandalism, crime, or espionage.”
Marking: CONFIDENTIALPeople: Shaw, BrianThe Intercept ↗ (2018-03-01) -
SNOWGLOBE: From Discovery to Attribution [pdf]
This document describes how CSEC identified and analyzed the SNOWGLOBE intrusion set, using passive collection, implant reverse engineering, and infrastructure analysis to attribute the campaign with moderate confidence to a French intelligence service targeting Iranian and international scientific, diplomatic, and political organizations.
Programs: SNOWGLOBE · WARRIORPRIDE · REPLICANTFARM · SNOWBALL · SNOWMAN · EONBLUE · SPECIALSOURCE · CANDLEGLOWPeople: Roshal, Alexander“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “Quand les Canadiens partent en chasse de « Babar »” - Le Monde ↗ (2014-03-21) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Follorou, Jacques · Untersinger, Martin -
SPINALTAP, Tracking Courier Use of Secure Digital Cards, and QUANTUMFALCON [pdf]
Three NSA presentations published as a single file. SPINALTAP, from Menwith Hill Station, extracts selectors from TAO, SFC and GCHQ endpoint accesses and translates them into XKEYSCORE fingerprints so that machines held by active operations can be recognised again in passive collection. Tracking Courier Use of Secure Digital Cards, from the NSA SIGINT Forensics Center, uses volume serial numbers and volume labels to identify SD cards and USB media that carry no USB controller, and reports identification information for 36 devices not seized during the UBL raid. QUANTUMFALCON summarises selector activity to triage targets for QUANTUM operations: see the Der Spiegel article The Digital Arms Race: NSA Preps America for Future Battle, 17 January 2015.
Programs: AARDVARKSTAKE · ABSOLINEDELTA · ACRIDMINI · AFTERBOOTSOLE · AFTERCLIFFDIVE · AFTERDOGHOUSE · AFTERGASSTATION · AFTERLASTTEAM · AFTERRICHGEAR · AFTERSHORTRUN · AFTERTANKERTRUCK · AFTERTREEFORM · AFTERWAYBACK · AFTERWINDBLOWN · AFTERYARDARM · ANCIENTBREW · APACHERIVER · ARMOREDCONDOR · ASDF · ATOMICCANNON · ATOMICFIREBALL · ATOMICFOG · ATOMICMONKEY · ATOMICPUNCH · ATOMICSTRIKE · AZTECTOMB · BACKSNARF · BEDOUINSTRIKE · BEEFCAKE · BLACK ALCHEMY · BLACKAMETHYST · BLACKMESA · BLOODDIAMOND · BROKENTHOUGHT · BULLETTOOTH · CAFFEINECRASH · CHOCOLATESHIP · COBALTGUPPY · COCOAMELTDOWN · CRISPWARE · CRYPTICSENTINEL · CUDDLYBADGER · CYGNUSOLOR · DANDERSPRITZ · DARKFIRE · DARKHELMET · DARKINTENT · DARKRAVEN · DARKRAZOR · DARKSCREW · DARKTHUNDER · DEADDRUMMER · DEPUTYSHIP · DETASSELJANICE · DIRTDIVER · DISTORTAFFECT · DOUBLETAP · DRINKMINT · DRINKMINTAA · DRUMBEAT · EDITIONHAZE · EFFABLELAMBDA · ELECTRONSWORD · EMPTYMOCHA · FIREBRUSH · FIREEATER · FIRESWAMP · FOXACID · FOXBASE · FRANTICDANCER · FREEACIDRAIN · FREEAIRFARE · FREEARCADEZONE · FREEBACKGAMMON · FREEBADFIBER · FREEBADRENT · FREEBALLROOM · FREEBATTLEZONE · FREEBEACHTREE · FREEBIGBOSS · FREEBITTERCLOUD · FREEBLACKCLOUD · FREEBLOODYWOLF · FREEBLOWNTURBO · FREEBLUEMAT · FREEBRASSBRUSH · FREEBUTTERCLOUD · UTT · FREECANALLOCK · FREECANESUGAR · FREECATBOX · FREECEMENTBLOCK · FREECHERRYCOLA · FREECHESSBOARD · FREECLEARTAPE · FREECOLDTEA · FREECORNHUSK · FREECORNMAZE · FREECREEKMOOR · FREECRUSHEDDISK · FREEDARKSUIT · FREEDATALOSS · FREEDEADBATTERY · FREEDETOURSIGN · FREEDIRTYTRICK · FREEDISCOVERY · FREEDISKBRAKE · FREEDOGCRATE · FREEDOMECUPOLA · FREEDOVETAIL · FREEEMUFARM · FREEENERGYTAX · FREEFAMILYTIE · FREEFASTCAR · FREEFIBERBOARD · FREEFILEDELETE · FREEFLATFIBER · FREEFLOWCHART · FREEFLOWERPEOPLE · FREEFRIEZEFRESCO · FREEGEMSTONE · FREEGLASSTUBE · FREEGLUESTRIP · FREEHAVEFUN · FREEHOMEBASE · FREEHOOKHANDLE · FREEHOOPDREAM · FREEJETFUEL · FREEKIDPOOL · FREEKINGSPAWN · FREEKNOCKOUT · FREELANDLINE · FREELEADSHOT · FREELEADSINGER · FREELIFERAFT · FREELIKESAME · FREELINEDOWN · FREELOLLYPOP · FREEMARBLEBASIN · FREEMETALCRATE · FREEMETALFILE · FREEMETALSHARD · FREEMINETUNNEL · FREEMINTJELLY · FREENAVYBLUE · FREENIGHTTRAIN · FREEOBLIQUECASE · FREEOILLEAK · FREEOILPAINT · FREEOLDBIKE · FREEOUTRUN · FREEPAINTBALL · FREEPICKLEBRINE · FREEPINEPLANK · FREEPLASTICCASE · FREEPONGPLAYER · FREEPOSTMARK · FREEPOWERFAILURE · FREEPUFFYCLOUD · FREEPULLCHAIN · FREERAINCLOUD · FREERAVENTICKET · FREEREDBEER · FREEREDERASER · FREEREDMARKER · FREEREDSHIRT · FREEREDSTAIN · FREERIDEAROUND · FREERIGHTWHALE · FREERIPPINGBLADE · FREEROCKSONG · FREESAFEKEY · FREESALTTRUCK · FREESASHCORD · FREESCHOOLLOCKER · FREESCREENDOOR · FREESEADADDY · FREESHORTCARD · FREESHORTPASS · FREESINEWAVE · FREESLOWFAST · FREESMALLSPACE · FREESMOKESCREEN · FREESNOWCLOUD · FREESNOWSHOVEL · FREESPACEFLIGHT · FREESPEEDTRAP · FREESTATEWARD · FREESTONESHIP · FREESTORAGEROOM · FREETANKSTAND · FREETESTSHEET · FREETHUNDERCLOUD · FREETICKETBOOTH · FREETIMELEGEND · FREETIMESHARE · FREETINYTANK · FREETRICKYKICK · FREETROUTSTREAM · FREETRUEPINBALL · FREETWINBEE · FREEVINYLMESH · FREEWARRIORPAINT · FREEWATERBED · FREEWATERGLASS · FREEWATERTANK · FREEWATERTOWER · FREEWAVECREST · FREEWAYPOINT · FREEWHEELCOVER · FREEWHEELNUT · FREEWINDCLOUD · FREEWINDSHEAR · FREEWOODENSTICK · FURRYEWOK · GHOSTMACHINE · GMPLACE · GOODMONKEY · HAMMERBROTHERS · HASTYCOBRA · HORSEWRAP · ICEBLOCK · IMPUREHOLSTER · INDEPENDENCEPIE · INQUIRY · JAVAFRESCO · JEALOUSJOKER · JEEPFLEA · JEEPFLEAMARKET · JOLLYROGER · KIDSHIPAA · KOOPATROOPA · KUKRISTEEL · LIQUIDSTEEL · LUTEUSASTRO · MAGNUMOPUS · MAGNUMOPUSCC · MARINA · MAXRANKLE · MICEFUR · MIDNIGHTSCORPION · MILKSTEAK · MIRACLEMAX · MUSHROOMKINGDOM · NAPALAN · NATIVEFLORA · OBSCUREBLAZE · OFFICELINEBACKER · OFFICEQUARTERBACK · OPTIMUSPRIME · PARLAYBUFFET · PHANTOMSTARFISH · PLUMREVOLVER · PRETZELDOG · QBISCUIT · QDIRK · QUANTUM · QUANTUMBISCUIT · QUANTUMDIRK · QUANTUMFALCON · REACTOR · ROLLEDHAT · SANDPALACE · SCARFSLOOP · SHADYNINJA · SHAKEWEIGHT · SHATTEREDSHIELD · SILENTTONGUES · SILLYBUNNY · SILVERJUMP · SKYJACKBRAD · SLYNINJA · SLYSNOW · SLYWIZARD · SNAPKEY · SPARTANFURY · SPIKEYFARM · SPINALTAP · STARPROC · STEELSKY · STEELSKYDELTA · STEELSKYECHO · STEELSKYFOXTROT · STEELSKYGOLF · STONEHENGE · STRAITLACED · SWITCHDOWN · SWITCHDOWNIRAW · SWITCHDOWNIRBR · SWITCHDOWNIRCD · THIEVESQUARTER · TOADYTEAL · TOTALDAGGER · TOXICSNOW · TROPICALSTORM · UMBRAGESPIDER · UNITEDRAKE · UPPERMUTANT · VALIDATOR · VEILEDMAGIC · WATERCASKET · WATERWINGS · WAXCHIP · WICKEDAMP · WILDCHOCOBO · WITHEREDFRUIT · WOLFACID · WOLFACIDANISE · WOLFACIDARGON · WOLFACIDBARIUM · WOLFACIDCHILI · WOLFACIDIODINE · WOLFACIDIRON · WOLFACIDJUPITER · WOLFACIDLEAD · WOLFACIDPRECIOUS · WOLFACIDTIN · WOLFACIDURANIUM · WOLFACIDZINC · XKEYSCORE · YELLOWFAN · MUSCULAR · INCENSER · DANCINGOASIS · MAPREDUCE“Documents Reveal Top NSA Hacking Unit” - Der Spiegel ↗ (2013-12-29) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Appelbaum, Jacob · Poitras, Laura · Rosenbach, Marcel · Stöcker, Christian · Schindler, Jörg · Stark, Holger · Gallagher, Ryan · Greenwald, Glenn · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
The FASHIONCLEFT Protocol [pdf]
This October 2008 NSA technical specification details FASHIONCLEFT, the encryption and exfiltration protocol used by TAO implants to securely tunnel captured network packets from compromised devices back to the NSA's Common Data Receptor using layered RSA and RC6 encryption with authentication. The document addresses technical integration challenges of implementing FASHIONCLEFT packet reception within TURMOIL's passive collection infrastructure, particularly cache buffering requirements and metadata handling for exfiltrated traffic.
Programs: FASHIONCLEFT · FOGYNULL · FUNNELAPS · SHELLGREY · TURMOIL · SURPASSPIN · PUZZLECUBE · FLASHHANDLE · HAMMERCHANT · AEG · PPF · ISLANDTRANSPORT