NDIST — GCHQ’s Developing Cyber Defence Mission
Open PDFDocument date: -
Pages: 3
Genre: slides
Banner: TOP SECRET 5EYES
Classification: TOP SECRET STRAP 1
Dissemination: 5EYES
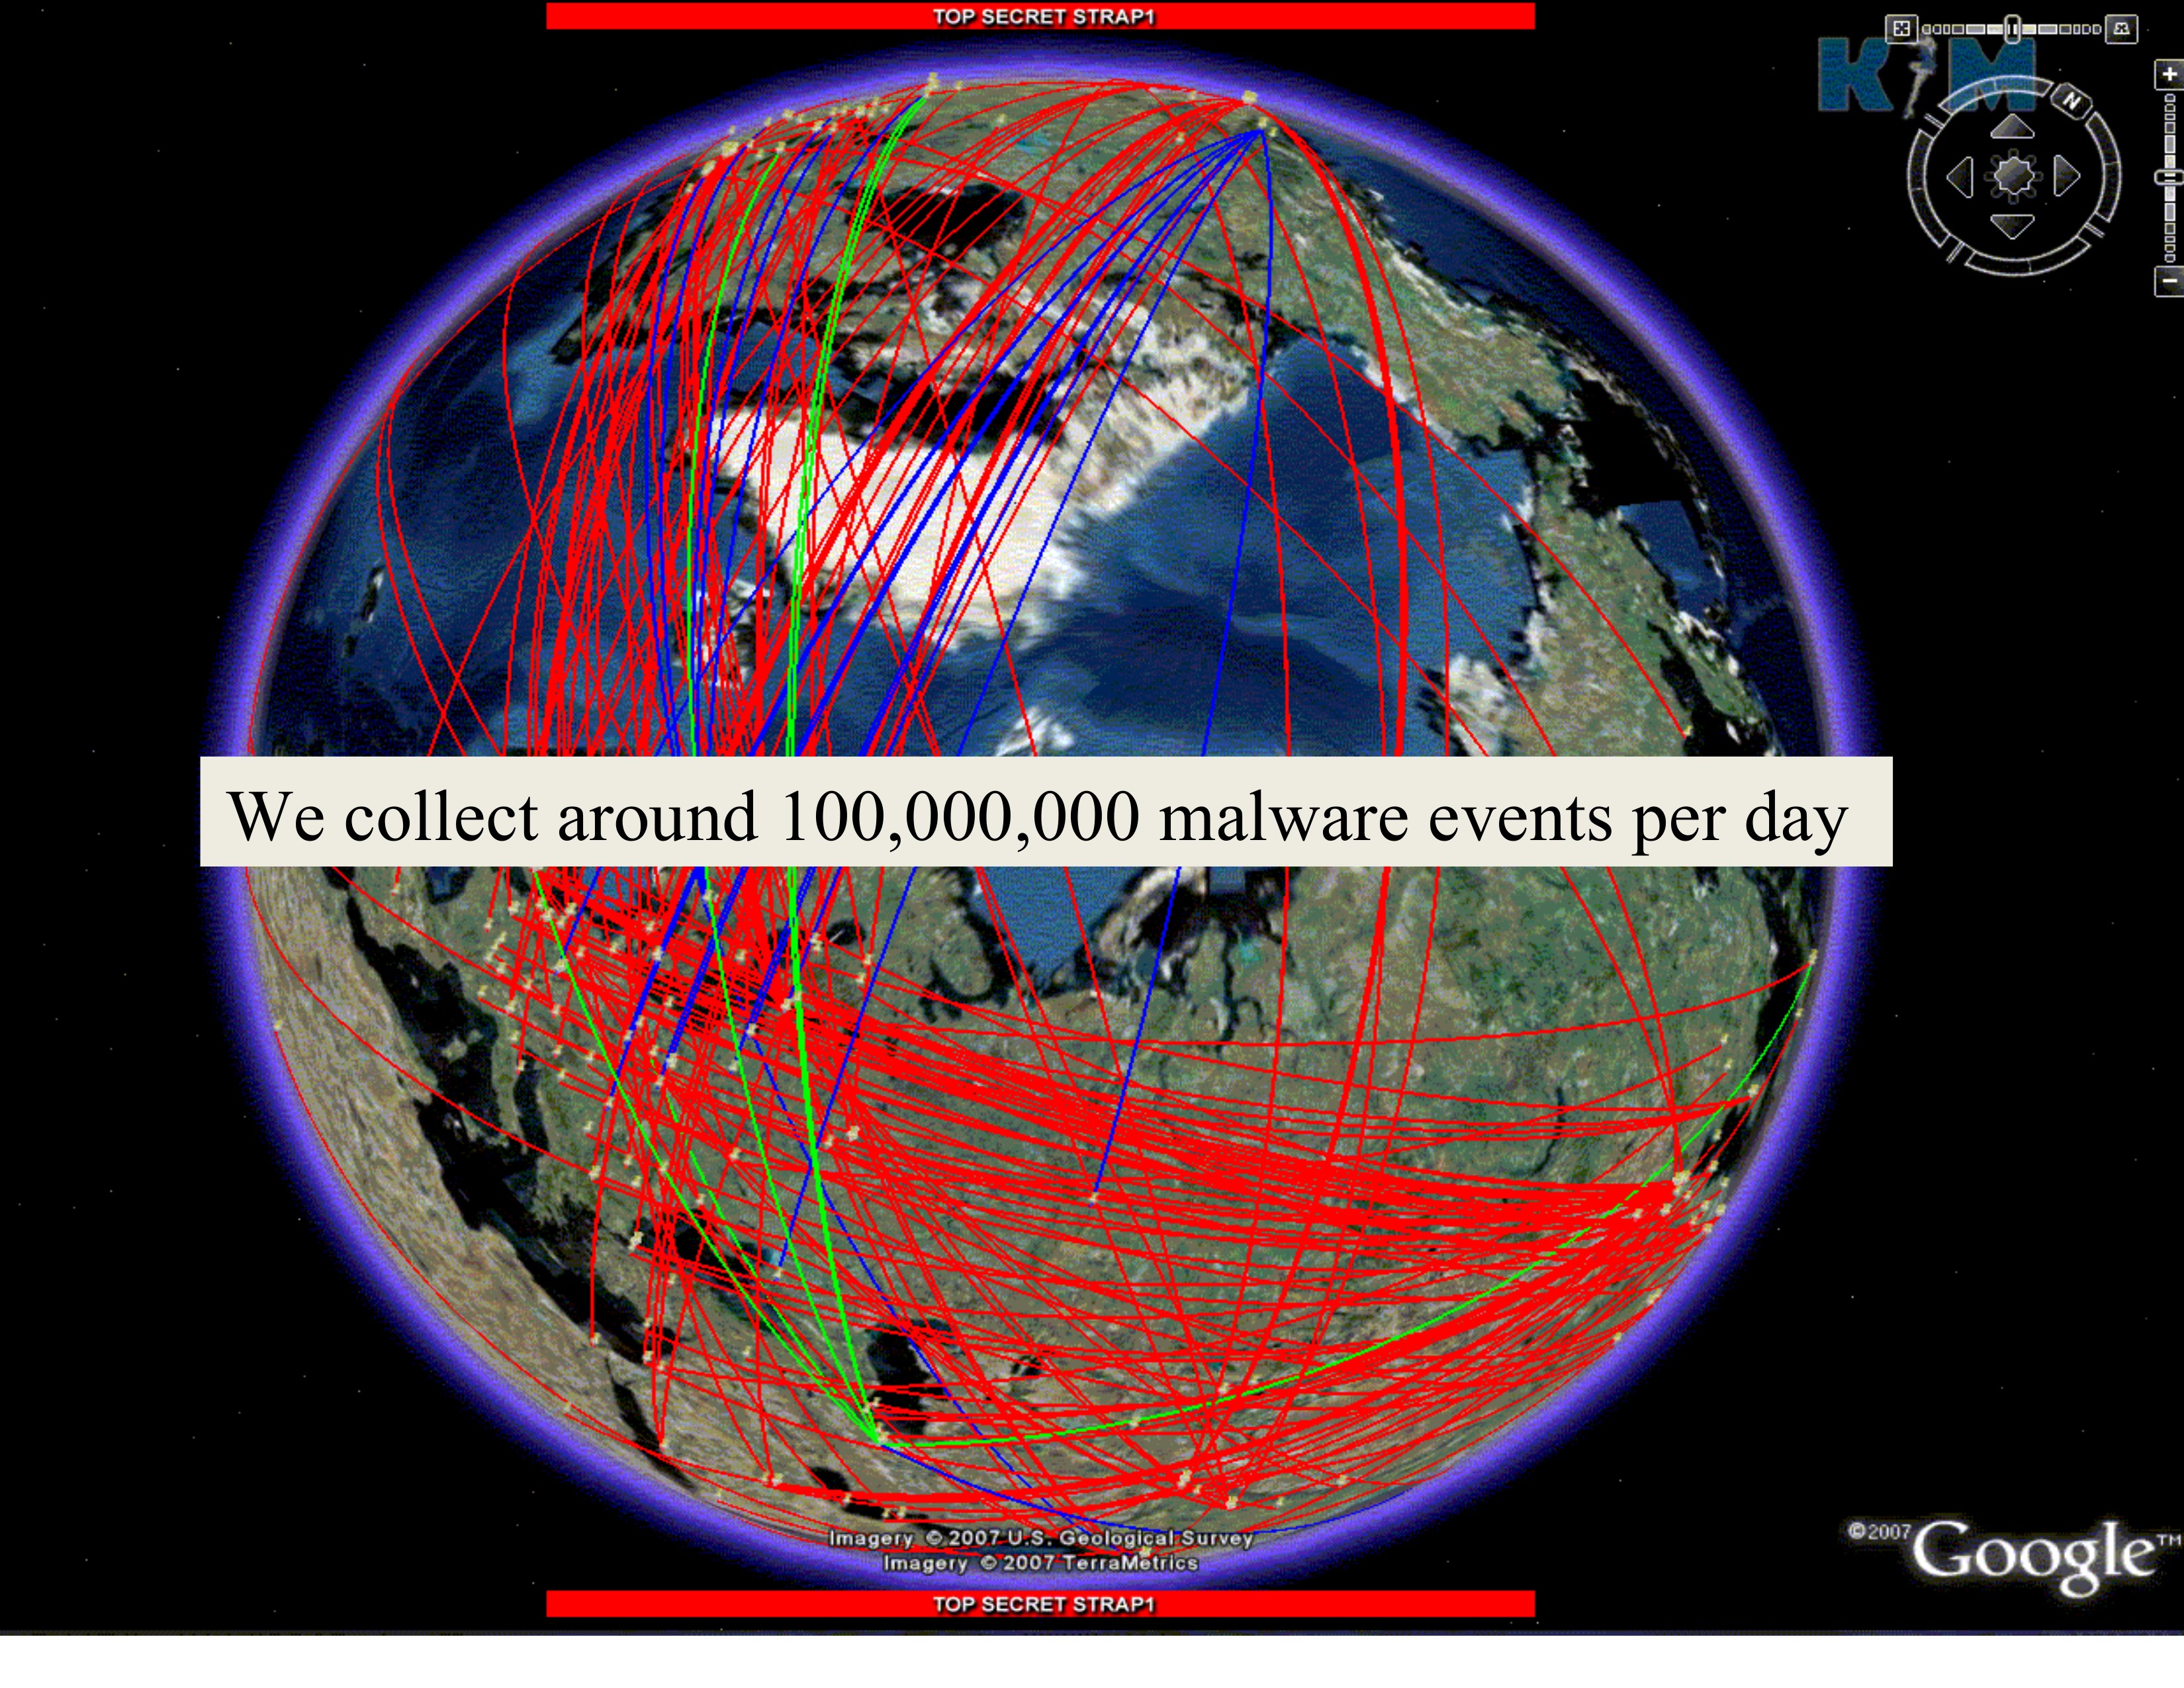
GCHQ’s NDIST sets out a developing cyber defence mission to reduce vulnerability and harm while enabling prosperity, centered on building a global-level picture of strategic threats and sharing intelligence with allies. The team anchors this work in massive telemetry, claiming roughly 100 million malware events collected per day to drive situational awareness.
My notes
ndist
network defence intelligence & security team
GCHQ's developing Cyber Defence Mission
Reduce vulnerability
Reduce harm
Enable prosperity
TOP SECRET 5EYES
The Cyber Defence Mission
Support national situational awareness
- Supporting UK partners, to build a national level picture of the most significant and strategic threats against the UK
Support international partners
- provide international partners (both 2nd and 3rd party) with intelligence that will help them build an appropriate national level picture of the most significant and strategic threats
TOP SECRET 5EYES
TOP SECRET STRAP1
We collect around 100,000,000 malware events per day
Imagery © 2007 U.S. Geological Survey
Imagery © 2007 TerraMetrics
©2007 Google™
TOP SECRET STRAP1
Published in the Same Report
(2 documents)
-
Kaspersky User-Agent Strings [pdf]
This September 2008 NSA technical report reveals that the agency discovered Kaspersky antivirus software's user-agent strings contain encoded serial numbers and can function as unique machine identifiers, allowing tracking of individual computers running the Russian security software across intercepted network traffic collected through the YACHTSHOP surveillance program.
-
Project CAMBERDADA [pdf]
NSA presentation on Project CAMBERDADA, a programme that intercepts emails sent to antivirus companies reporting new malware, uses SIGINT collection to monitor antivirus vendor communications, and identifies opportunities to repurpose malware before vendors detect it — listing 23 antivirus companies from around the world as targets, with Kaspersky as the primary focus.
People: Picard, François

Related Documents
-
-
Cyber Defence Operations Legal Policy [pdf]
GCHQ's internal wiki laying out the legal plumbing for its Cyber Defence Operations (formerly NDIST)—detailing warrant types (RIPA, ISA, CNE), data retention schedules, targeting rules for UK/Five Eyes infrastructure, XKEYSCORE query protocols, and the bureaucratic hoops analysts must jump through to search attacker IPs, fingerprint UK networks, and share malware intelligence without tripping over location/nationality safeguards or commercial sensitivities.
Programs: JTRIG · SPAY · GORDIANKNOT · CHORDAL · DISCOVER · EVENTS · CASPORT · XKEYSCORE · CONTENT CLOUD · SQUEAL · MIRAGE · MUTANTBROTH · ANXIOUS · HALTERHITCH · BROADOAK · DONKEYKONG · ZOOL · PALANTIR · OVERLINK · RT · GATEKEEPER · IRONHAND · HARUSPEX · B3M · LOOKINGGLASS · GOLDENEYE · BLAZINGSADDLES · MOONRAKER · TRITON -
Software Reverse Engineering – GCHQ [pdf]
GCHQ’s Network Defence unit runs software reverse engineering across both malicious and commercial code to map vulnerabilities, validate security claims, and feed CESG’s advice on electronic attack. Malicious code is fair game, but commercial RE hinges on GCHQ’s ISA s5 SRE warrant (GPW/1160), with local authorisers and audits—after a documented lapse in 2008 was retro‑authorised.
Marking: TOP SECRET -
Welcome to the Mission Driven Access Workshop - GCHQ Bude [pdf]
This document, sourced from a Mission Driven Access (MDA) Workshop at GCHQ Bude, outlines a strategic intelligence shift toward South American targets. It identifies a historical underperformance in monitoring Brazil and highlights the Foreign Office's urgent need for intelligence to counter growing regional support for Argentina regarding the Falkland Islands dispute.
Marking: CONFIDENTIAL -
HAPPY TRIGGER/LOVELY HORSE/Zool/TWO FACE – Open Source for Cyber Defence/Progress [pdf]
A TOP SECRET STRAP1 COMINT GCWiki page cataloguing GCHQ's open source intelligence gathering for cyber defence, listing approved and pending data sources fed into internal databases HAPPY TRIGGER, LOVELY HORSE, ZooL and TWO FACE, covering malware tracking, vulnerability intelligence, infrastructure mapping and domain monitoring.
Programs: HAPPYTRIGGER · LOVELYHORSE · TWOFACE · ZOOL · XKEYSCORE · POSITIVEPONY · NETPLATE · HIDDENSPOTLIGHT · SNORT · FOXTRAIL · REFRIEDCHICKEN · GEOFUSION · GLOBALSURGE · SHORTFALL · JTRIG · BIRDSEED · BIRDSTRIKE · MARBLEPOLLSPeople: Stewart, Joe