Country: Taiwan 17 documents
Search documents matching “Taiwan” →Countries mentioned in each document. A country may be mentioned directly (e.g., France) or inferred from a related reference, such as a city (Paris -> France) or a domain name (.fr -> France).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Approved SIGINT Partners [pdf]
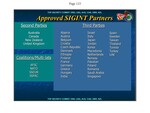
A Foreign Affairs Directorate slide listing NSA's approved SIGINT partners: the four Second Parties, 33 Third Parties from Algeria to the United Arab Emirates, and the coalitions AFSC, NATO, SSEUR and SSPAC. This is document is from Fiscal Year 2013 "Foreign Partner Review."
-
Bad guys are everywhere, good guys are somewhere! [pdf]
A classified NSA NTOC presentation describing TREASURE MAP — the agency's near real-time global internet mapping platform — which combines open source, commercial, covert, and SIGINT data to chart every device, router, and autonomous system on the internet, including through 13 covert servers secretly planted in unwitting data centers across 18 countries spanning Asia, Europe, Russia, Africa, and South America, with networks marked in red indicating active SIGINT collection access points across at least 20 major telecommunications providers on three continents including allied nations' state-owned carriers.
Programs: TREASUREMAP · PACKAGEDGOODS · SOCIALSTAMP · SEASIDEFERRY · ARK · CAIDA · RUSTICBAGGAGE · PACKAGEDGOODS-GTR · PACKAGEDGOODS-SERVER · BLACKPEARL · LEAKYFAUCET · HYDROCASTLE · MASTERSHAKE · S-TRICKLER · TOYGRIPPE · DISCOROUTE · VITALAIR2 · IPGEOTRAP · JOLLYROGER · TUTELAGE · BYZANTINEHADES · XKEYSCORE · RADIUS · TACACS -
Close Access SIGADS [pdf]
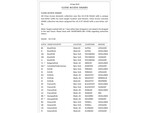
A 10 September 2010 NSA reference list of Close Access SIGADs revealing the codenames, locations and collection methods used to bug the embassies and UN missions of 38 targets — including US allies France, Italy, Greece, Japan, India, Mexico, South Korea and the EU — through implants, computer-screen capture, hard-drive imaging and electromagnetic emanation collection, most conducted against diplomatic facilities in Washington DC and New York.
Programs: KATEEL · POCOMOKE · MERCED · BANISTER · PERDIDO · MAGOTHY · BLACKFOOT · WABASH · NAVARRO · POWELL · KLONDIKE · NASHUA · OSAGE · OSWAYO · BRUNEAU · HEMLOCK · MULBERRY · ALAMITO · FLEMING · DOBIE · SULPHUR · REQUETTE · YUKON · WESTPORT · NAVAJO · PANTHER · LIFESAVER · HIGHLANDS · VAGRANT · MINERALIZ · DROPMIRE · PBX · MAGNETIC · OCEAN · GENIE · BLACKHEART · CRYPTOENABLED · CUSTOMS · DEWSWEEPER · RADON · MINERALIZE · COOP · STARRUBY · TRASHINT“No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “Espionnage de la NSA : la diplomatie française était sur écoute aux Etats-Unis” - Le Monde ↗ (2013-10-22) · “Da qui ci spiano gli americani” - L'Espresso ↗ (2013-12-05) · Greenwald, Glenn · Follorou, Jacques · Maurizi, Stefania -
DEFIANTWARRIOR and the NSA's Use of Bots [pdf]
This TOP SECRET NSA presentation from 2010 documents the DEFIANTWARRIOR effort to identify, seize, and operate botnets using SIGINT-enabled infrastructure, detailing both early failures and subsequent operational successes. The document reveals how bot herding was integrated into broader offensive cyber and intelligence collection strategies across the Five Eyes.
Programs: DEFIANTWARRIOR · OLYMPUS · UNITEDRAKE · TURBULENCE · QUANTUMBOT · TURMOIL · TURBINE · SNIPERS · XKEYSCORE · INCENSER · STELLABLUE · SMOKYSINK · STOVEPIPES · ISLANDTRANSPORT · FESTIVEWRAPPER · FREEFLOW · PRESSUREWAVE · HANGARSURPLUS · SURPLUSHANGER · WAITAUTO · DEEPFRIEDPIG · SEAGULLFARO · COLOSSUS · STORMPIG · YELLPIG · PASTEPIG · SHOUTPIG · ZORPIG · MAILORDER · TREASUREMAP · MARINA · WARNVOLCANO · STRAITBIZARRE · BOTINSTANCES · PUZZLECUBE · SEEKER · SURPLUSHANGAR -
EP-3E Collision: Cryptologic Damage Assessment and Incident Review [pdf]
A joint US Navy and NSA report from July 2001, prepared three months after a US spy plane was forced to land in China, assessing how far surveillance sources and methods were compromised and reviewing the emergency destruction that failed to prevent it. Damage to tactical SIGINT against the PRC is rated medium and overall SIGINT damage low, with the greatest loss the LUNCHBOX PROFORMA processor and MARTES signals analysis tools; COMSEC damage is rated low because keying material was superseded within 15 hours.
Programs: LUNCHBOX · MARTES · NICKELBACK · SENSOR PACER · PROFORMA · HULTEC · STRUM · TEXTA · RASIN · CRITIC · KLIEGLIGHT · XBIT · BLACKMAGIC · NOIWON · ZIRCON · MIDB · EOB-LITE · NIMROD · ARIEL · COBRA BALL · COMBAT SENT · RIVET JOINT · SEABOOT · SETTEE · KAMPUS · DRUID · RORIPA · MARKHAM · FOREJUDGE · SAM HEARTBURN · NOVELETTE · RSBN · BEGGAR HAWK · BEGGAR SHADOW · CAPSULE JACK · DISTANT WIND · DISTANT SENT · CHILING · RIBBED · UNACCENTED · SLIPSTICK · SIERRA ONEPeople: Meals, Charlie -
FAD FY 12 CCP Funding of Partners [pdf]
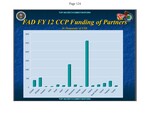
A Foreign Affairs Directorate slide showing Combined Cryptologic Program funding of foreign partners in fiscal year 2012, in thousands of dollars, across fifteen countries including Canada, Israel, Japan, Jordan, Pakistan, Taiwan and Thailand.
-
GCHQ - PCS Harvesting [pdf]
A TOP SECRET STRAP1 report details how GCHQ industrialized the theft of GSM subscriber authentication keys (Ki) by automating trawls of bulk “C2C” content to extract IMSI/Ki pairs from emails and FTP transfers between SIM personalisation centers and mobile operators. It shows the program scaling key harvesting across networks and countries, complementing computer network exploitation against core mobile infrastructure to suppress billing and lift authentication secrets.
-
Guidelines for the classification of NSA SIGINT details (1945-1967) [pdf]
This document is an NSA classification guide that defines how and why historical SIGINT material from 1945–1967 remains classified, in many cases for 75 years. It systematically explains which intelligence activities, targets, partnerships, and technical methods must stay protected because they still reveal sensitive sources, methods, and diplomatic equities.
-
Intellipedia – BIOS Threats [pdf]
This from an internal wiki for the U.S. intelligence community, titled “BIOS Threats” details the use of malicious BIOS implants as a means of achieving persistent system compromise for cyber espionage and attack purposes. It discusses the history, technical challenges, detection limitations, and global development of BIOS-based malware by both state and non-state actors, including U.S. and Chinese cyber units.
-
Internet Anonymity 2011 [pdf]
A TOP SECRET NSA presentation from 2011 providing a comprehensive survey of Internet Anonymity Technologies (IAT) — covering HTTP proxies, VPN anonymity providers, multi-hop networks including Tor and JAP, anonymous remailers and circumvention tools — alongside NSA's capabilities and limitations against each, including XKEYSCORE fingerprints for VPN identification, the PARTNERSNIPPET Tor deanonymisation team, GOLDENFORTIN Netflow data, and a candid assessment that Tor offers "no passive exploitation."
Programs: FOXTRAIL · NKB · NACIRONIN · PONTENTPOTABLES · RONIN · XKEYSCORE · PARTNERSNIPPET · GOLDENFORTIN · SNAPEPeople: Heap, Austin -
JORDAN-BELGIUM [pdf]
2008 GCHQ report documenting the interception of a Jordan–Belgium satellite telecommunications link, through which British intelligence monitored call traffic and identified tasked surveillance targets including the Turkish foreign ministry, Palestinian Authority figures and Israeli MK Ahmad Tibi, along with other hits on Kurdish leadership, diplomats, and Jordanian government offices such as the Royal Protocol Office. The published copies redact different entries. Der Spiegel's and The Intercept's show the Turkish and Kurdish ones, Le Monde's (version 8BBAC) the Palestinian and Jordanian ones.
People: Tibi, Ahmad“Turkey Is 'Partner and Target' for the NSA” - Der Spiegel ↗ (2014-08-31) · “How the NSA Helped Turkey Kill Kurdish Rebels” - The Intercept ↗ (2014-08-31) · “L’Autorité palestinienne et la Jordanie espionnées par les services américains et britanniques” - Le Monde ↗ (2016-12-07) · Poitras, Laura · Rosenbach, Marcel · Sontheimer, Michael · Stark, Holger · Follorou, Jacques -
List of foreign governments and organizations authorized for surveillance [pdf]
This exhibit lists the 193 foreign governments as well as foreign factions, political organizations and other entities that were part of a 2010 certification approved by the Foreign Intelligence Surveillance Court. These are the entities about which the NSA may conduct surveillance, for the purpose of gathering foreign intelligence. Each year a new certification must be approved by the court to permit such surveillance under Section 702 of the FISA Amendments Act.
-
NAC BUDE Partnership - SATELLITE TELEPORT KNOWLEDGE (GCHQ) [pdf]
A top secret GCHQ Network Analysis Centre document from GCHQ Bude detailing comprehensive intelligence profiles of three German satellite teleport operators — Stellar, Ce-Tel, and IABG — including their network infrastructure, router configurations, IP ranges, employee identities, satellite customers, and login credentials, compiled to identify access chokepoints for SIGINT collection against German IP transit infrastructure.
People: Steffen, Christian · Sommer, Christoph · Fares, Ali · Grave, Richard · Steffen, Simona · Skaletz, Oliver -
NIOC MARYLAND ADVANCED COMPUTER NETWORK OPERATIONS COURSE [pdf]
Programs: GENIE · HAWKEYE · EINSTEIN · TUTELAGE · NEPTUNETHUNDER · BLINDDATE · HAPPYHOUR · NITESTAND · WAITAUTO · MATCHCRIMP -
Persistence and Collaboration Thwart Criminals on the High Seas SIDtoday [pdf]
This SIDtoday document describes a successful operation in which NSA Hawaii's Maritime Analysis Support Team (HMAST) and other agencies helped track and interdict the illegal fishing vessel Da Cheng (formerly Shun Li No. 6), which was engaged in high seas drift net (HSDN) fishing, a practice harmful to marine ecosystems. The coordinated effort, involving the U.S. Coast Guard and SIGINT support, led to the vessel's boarding and the discovery of illegal catch, though the document emphasizes that ongoing efforts are necessary to combat this illegal activity.
-
Tracking Targets on Online Social Networks [pdf]
A TOP SECRET NSA presentation from September 2009 describing XKeyscore techniques for tracking targets across online social networks — covering OSN selector types, six categories of target OSN activity ranked by intelligence value, username and HTTP activity query methods, and specific XKeyscore AppIDs for Facebook and Twitter — noting that counterterrorism targets had been observed using over 50 social networks as of late 2008.
Programs: XKEYSCORE“XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Marquis-Boire, Morgan · Greenwald, Glenn · Lee, Micah -
United States SIGINT System January 2007 Strategic Mission List [pdf]
This 2007 list of the National Security Agency’s major missions illustrates the sweep of the agency’s goals for signals intelligence (Sigint) or electronic eavesdropping, which include not only such obvious targets as terrorist groups and Iran’s nuclear program, but the diplomacy and economic policy of friendly countries.