Country: Czech Republic 20 documents
Search documents matching “Czech Republic” →Countries mentioned in each document. A country may be mentioned directly (e.g., France) or inferred from a related reference, such as a city (Paris -> France) or a domain name (.fr -> France).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Afghanistan Coalition Dissemination Brief to Senior Leadership Forum [pdf]
This document ooutlines the structure, goals, and challenges of multinational signals intelligence (SIGINT) collaboration in Afghanistan as of 2009. It reveals how the U.S. and its intelligence-sharing allies (notably the 5 Eyes, 9 Eyes, and 14 Eyes) coordinated SIGINT collection, decryption, analysis, and dissemination across NATO and coalition forces.
“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
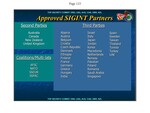
Approved SIGINT Partners [pdf]
A Foreign Affairs Directorate slide listing NSA's approved SIGINT partners: the four Second Parties, 33 Third Parties from Algeria to the United Arab Emirates, and the coalitions AFSC, NATO, SSEUR and SSPAC. This is document is from Fiscal Year 2013 "Foreign Partner Review."
-
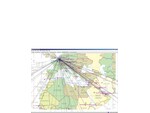
Belgacom connections [pdf]
A "Belgacom connections" map lays out the carrier’s sprawling roaming and backbone interconnects, precisely the arteries GCHQ wanted to get access into. Under Operation Socialist GCHQ successfully gained access to Belgacom’s infrastructure, including internal employee computers and encrypted and unencrypted streams of private communications handled by the company.
Programs: CARBONROD“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
Broadcast/Internet Radio Exploitation and Analysis, 6th November 2009, GCHQ [pdf]
This GCHQ report analyzes 6.68 million internet radio listening events collected over three months in 2009, detailing global broadcasting patterns, user behaviors, and specifically examining Islamic radio stations and Pakistan-UK connections for potential radicalization intelligence, while recommending integration with bulk surveillance databases like KARMA POLICE for enhanced user profiling.
-
Classification Guide Title/Number: Cuban Missile Crisis, 10-18 [pdf]
A 2008 NSA classification guide governing what may be disclosed about the agency's SIGINT activity during the Cuban Missile Crisis, showing that elements of 1960s collection against Cuba and the USSR were still controlled decades later.
-
DAPINO GAMMA Gemalto Yuaawaa Wiki [pdf]
This document details the identification of Yuaawaa, a secure file-sharing service sold and used by Gemalto employees, and assesses several of these employees as potential future intelligence targets. Key individuals are noted based on their roles, locations, and observed activities, such as sending PGP-encrypted files.
-
Driver 1: Worldwide SIGINT/Defense Cryptologic Platform [pdf]
A 2012 NSA management presentation slide revealing the agency's global surveillance architecture across five categories of access — covert cable taps, regional collection sites, computer network exploitation implants, foreign satellite collection, and third-party liaison relationships — including a list of cities hosting clandestine collection operations and confirmation of over 50,000 worldwide malware implants.
Programs: STELLAR · SOUNDER · SNICK · MOONPENNY · LADYLOVE · INDRA · IRONSAND · JACKKNIFE · CARBOY · TIMBERLINE“NSA infected 50,000 computer networks with malicious software” - NRC ↗ (2013-11-23) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Boon, Floor · Derix, Steven · Modderkolk, Huib · Greenwald, Glenn -
GCHQ - PCS Harvesting [pdf]
A TOP SECRET STRAP1 report details how GCHQ industrialized the theft of GSM subscriber authentication keys (Ki) by automating trawls of bulk “C2C” content to extract IMSI/Ki pairs from emails and FTP transfers between SIM personalisation centers and mobile operators. It shows the program scaling key harvesting across networks and countries, complementing computer network exploitation against core mobile infrastructure to suppress billing and lift authentication secrets.
-
Internet Anonymity 2011 [pdf]
A TOP SECRET NSA presentation from 2011 providing a comprehensive survey of Internet Anonymity Technologies (IAT) — covering HTTP proxies, VPN anonymity providers, multi-hop networks including Tor and JAP, anonymous remailers and circumvention tools — alongside NSA's capabilities and limitations against each, including XKEYSCORE fingerprints for VPN identification, the PARTNERSNIPPET Tor deanonymisation team, GOLDENFORTIN Netflow data, and a candid assessment that Tor offers "no passive exploitation."
Programs: FOXTRAIL · NKB · NACIRONIN · PONTENTPOTABLES · RONIN · XKEYSCORE · PARTNERSNIPPET · GOLDENFORTIN · SNAPEPeople: Heap, Austin -
JFK Assassination Records Classification/Declassification Guide Number: 385-00 [pdf]
A 2000 NSA guide setting what may be released from records responsive to the President John F. Kennedy Assassination Records Collection Act of 1992, keeping intercept details classified at SECRET//SI or TOP SECRET//SI while declassifying the fact of Cuban and Soviet collection.
Programs: SERAFINPeople: Kennedy, John F. -
List of foreign governments and organizations authorized for surveillance [pdf]
This exhibit lists the 193 foreign governments as well as foreign factions, political organizations and other entities that were part of a 2010 certification approved by the Foreign Intelligence Surveillance Court. These are the entities about which the NSA may conduct surveillance, for the purpose of gathering foreign intelligence. Each year a new certification must be approved by the court to permit such surveillance under Section 702 of the FISA Amendments Act.
-
OP HIGHLAND FLING - Event Log [pdf]
A TOP SECRET operational event log from GCHQ's GCWiki documenting a January 2011 operation targeting Gemalto employees in France, Poland and elsewhere, using MUTANT BROTH cookie analysis, Facebook credentials, LinkedIn profiles and Computer Network Exploitation to identify and implant targets as part of the operation to steal SIM card encryption keys.
-
OSINT FUSION PROJECT [pdf]
A TOP SECRET//COMINT//REL TO USA, FVEY presentation by Lockheed Martin's Intelligence and Global Solutions division describing the OSINT Fusion Project — a programme to collect and weaponise open source intelligence from hacker forums, malicious email traffic, botnet data and commercial threat feeds to generate XKEYSCORE fingerprints for CNE targeting and fourth party collection.
-
Project CAMBERDADA [pdf]
NSA presentation on Project CAMBERDADA, a programme that intercepts emails sent to antivirus companies reporting new malware, uses SIGINT collection to monitor antivirus vendor communications, and identifies opportunities to repurpose malware before vendors detect it — listing 23 antivirus companies from around the world as targets, with Kaspersky as the primary focus.
People: Picard, François -
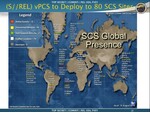
SCS sites [pdf]
A TOP SECRET map from an SCS SIGDEV briefing, dated 13 August 2010, showing the global presence of the Special Collection Service — the joint CIA/NSA embassy-based interception unit — at some 80 sites worldwide, published (briefly unredacted) by Der Spiegel alongside its Merkel/Berlin embassy reporting, naming the specific cities where covert intercept posts operated, including Berlin, Frankfurt, Moscow, Beijing, Tehran and dozens more.
Programs: VPCS -
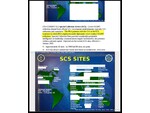
SCS SITES [pdf]
This 2004 NSA document maps the global footprint of the Special Collection Service (SCS), the joint NSA–CIA program that conducts covert signals-intelligence collection from U.S. embassies and consulates abroad under diplomatic cover, prized for intercepting "leadership communications" from within national capitals. Effective January 2002, it lists roughly 65 active, survey, and future SCS sites worldwide.
-
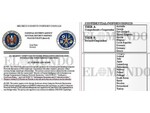
Sharing Computer Network Operations Cryptologic Information with Foreign Partners [pdf]
The document is a secret NSA/CSS policy outlining guidelines for sharing Computer Network Operations (CNO) cryptologic information with foreign partners, including rules for cooperation in CNE and CND within existing intelligence relationships. The “Purpose and Scope” section on the first page appears to be unpublished elsewhere, while the Tier A and Tier B country lists match those publicly revealed in sources like Glenn Greenwald’s No Place to Hide.
“El CNI facilitó el espionaje masivo de EEUU a España” - El Mundo ↗ (2013-10-30) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Greenwald, Glenn · Aranda, Germán -
SNOWGLOBE: From Discovery to Attribution [pdf]
This document describes how CSEC identified and analyzed the SNOWGLOBE intrusion set, using passive collection, implant reverse engineering, and infrastructure analysis to attribute the campaign with moderate confidence to a French intelligence service targeting Iranian and international scientific, diplomatic, and political organizations.
Programs: SNOWGLOBE · WARRIORPRIDE · REPLICANTFARM · SNOWBALL · SNOWMAN · EONBLUE · SPECIALSOURCE · CANDLEGLOWPeople: Roshal, Alexander“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “Quand les Canadiens partent en chasse de « Babar »” - Le Monde ↗ (2014-03-21) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Follorou, Jacques · Untersinger, Martin -
Tracking Targets on Online Social Networks [pdf]
A TOP SECRET NSA presentation from September 2009 describing XKeyscore techniques for tracking targets across online social networks — covering OSN selector types, six categories of target OSN activity ranked by intelligence value, username and HTTP activity query methods, and specific XKeyscore AppIDs for Facebook and Twitter — noting that counterterrorism targets had been observed using over 50 social networks as of late 2008.
Programs: XKEYSCORE“XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Marquis-Boire, Morgan · Greenwald, Glenn · Lee, Micah -
What Your Mother Never Told You About SIGDEV Analysis [pdf]
An NSA presentation covering VPN signals development tradecraft and the prototype DARKSUNRISE VPN analytics tool — describing how analysts use DISCOROUTE, BLACKPEARL, TOYGRIPPE, NKB, RONIN and GNETWORK GNOME to map target VPN networks from router configuration data, with live screenshots of DARKSUNRISE's SHADOWNET interface showing IPSec VPN connections associated with Pakistani, Afghan and other targets collected through MUSCULAR (DS-200B).
Programs: TOYGRIPPE · DISCOROUTE · BLACKPEARL · GNETWORKGNOME · NKB · RONIN · XKEYSCORE · TREASUREMAP · RENOIR · ROYALNET · GNOME · ASDF · DARKSUNRISE · SHADOWNET · WEALTHYCLUSTER · MUSCULAR · CASPORT · CUE · BLACKSAND · DANCINGOASIS · BLACKBEACH · POTLUCK · SSO · DNIPRESENTER · TNS · BLACKPEAL · ROADBED · TROPICNET · SILVERZEPHYR · SITESTORE