Country: China 103 documents
Search documents matching “China” →Countries mentioned in each document. A country may be mentioned directly (e.g., France) or inferred from a related reference, such as a city (Paris -> France) or a domain name (.fr -> France).
Graphs
By document date (10 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Entry From SSO News [pdf]
This document discusses the initial operational capability of MONKEYROCKET, a non-Western Internet anonymization service developed as part of the OAKSTAR program, aimed at supporting counter-terrorism efforts. As of July 2012, the system was forwarding metadata to backend repositories, with a significant user base of around 16,000, primarily from countries like Iran and China. The service is expected to grow in usage, generating about 2,000 events per day.
-
EP-3E Collision: Cryptologic Damage Assessment and Incident Review [pdf]
A joint US Navy and NSA report from July 2001, prepared three months after a US spy plane was forced to land in China, assessing how far surveillance sources and methods were compromised and reviewing the emergency destruction that failed to prevent it. Damage to tactical SIGINT against the PRC is rated medium and overall SIGINT damage low, with the greatest loss the LUNCHBOX PROFORMA processor and MARTES signals analysis tools; COMSEC damage is rated low because keying material was superseded within 15 hours.
Programs: LUNCHBOX · MARTES · NICKELBACK · SENSOR PACER · PROFORMA · HULTEC · STRUM · TEXTA · RASIN · CRITIC · KLIEGLIGHT · XBIT · BLACKMAGIC · NOIWON · ZIRCON · MIDB · EOB-LITE · NIMROD · ARIEL · COBRA BALL · COMBAT SENT · RIVET JOINT · SEABOOT · SETTEE · KAMPUS · DRUID · RORIPA · MARKHAM · FOREJUDGE · SAM HEARTBURN · NOVELETTE · RSBN · BEGGAR HAWK · BEGGAR SHADOW · CAPSULE JACK · DISTANT WIND · DISTANT SENT · CHILING · RIBBED · UNACCENTED · SLIPSTICK · SIERRA ONEPeople: Meals, Charlie -
ESOC: Report on the experiences of one NSA worker [pdf]
A NSA intelligence analysis intern details their 2007 temporary assignment to the European Security Operations Center (ESOC), where they successfully established a new signals intelligence (SIGINT) mission targeting Angola's energy sector. The author describes the end-to-end process from initial research and target development to successful collection and the first intelligence product.
-
Exploiting Foreign Lawful Intercept (LI) Roundtable [pdf]
Top-secret PowerPoint presentation, "Exploiting Foreign Lawful Intercept Roundtable," highlights the agency’s strategy to exploit vulnerabilities in lawful intercept systems from telecom companies, such as Ericsson, Motorola, and Nokia, in countries like Mexico, Indonesia, and Egypt. The presentation also discusses NSA's use of various "Fingerprints" for identifying data and its collaboration with industry players and foreign lawful intercept systems.
“A Death in Athens” - The Intercept ↗ (2015-09-28) · “Americans and Greeks started the 2004 wiretaps together” - Kathimerini ↗ (2015-09-29) · Bamford, James · Petropoulos, Aggelos -
Final Agenda - HR DIETMAR B - Director SIGINT Analysis and Production German Federal Intelligence Service, 30 April - 1 May 2013 [pdf]
This document presents the final agenda for a visit by Hr. Dietmar B., the Director of SIGINT Analysis and Production from the German Federal Intelligence Service (BND), scheduled for April 30 to May 1, 2013. The agenda details key discussions and meetings with various officials from the NSA, focusing on strategic planning and areas of mutual interest in intelligence collaboration.
-
FINAL Agenda SWEDUSA [pdf]
Detailed list of points and participants in the summit meeting between the top brass of the FRA and the NSA in April 2013.
Programs: TURTLEPOWER · TURMOIL · XKEYSCORE · WINTERLIGHT · QUANTUM · PARTNERMALL · VIVIAN · NAPA-3 · GCE · SSO -
FOXACID SOP for Operational Management of FOXACID Infrastructure (Draft) [pdf]
This document is an NSA standard operating procedure (SOP) manual detailing how to manage and operate the FOXACID system, which delivers malware to targets through tools like SECONDDATE and BADDECISION. It provides technical instructions for tracking, deploying, and maintaining covert web-based infections used in global cyber operations.
Programs: FOXACID · FOXSEARCH · WAITAUTO · RAISEBED · FORRESTPLACE · FOXHelp · PUZZLECUBE · YACHTSHOP · SECONDDATE · MAGIC SQUIRREL · MAGICBEAN · FINKCOAT · FRUGALSHOT · QUANTUM · FERRETCANNON · BEACHHEAD · OLYMPUS · UNITERAKE · DIRESCALLOP · DEEPFREEZE · FINKDIFFERENT · DISABLEVALOR · VALIDATOR · MISTYVEAL · UNITEDRAKE · PEDDLE CHEAP · PKTWENCH · FORESTPLACE · FOXCONTACT · EASYHOOKUP · DEMENTIAWHEEL · CASTLECREEK · ROCHELP · QUANTUMINSERT · FABULOUSFABLE · WATCHER · FROZENGAZE · FABFAB · DARKFIRE · CRYPTICSENTINEL · DARKHELMET · PSP · WILLOWVIXEN -
FY 2013 Congressional Budget Justification, Volume I, National Intelligence Program Summary, February 2012 [pdf]
This document outlines the $52.6 billion “black budget,” detailing the structure, priorities, successes, and shortcomings of the 16 U.S. intelligence agencies. It reveals unprecedented insight into funding allocations, operations, and intelligence gaps—including the CIA’s dominant role, expanding cyber operations, and persistent challenges in areas such as North Korea and counterterrorism—while emphasizing the tension between secrecy and public accountability.
-
GCHQ - PCS Harvesting [pdf]
A TOP SECRET STRAP1 report details how GCHQ industrialized the theft of GSM subscriber authentication keys (Ki) by automating trawls of bulk “C2C” content to extract IMSI/Ki pairs from emails and FTP transfers between SIM personalisation centers and mobile operators. It shows the program scaling key harvesting across networks and countries, complementing computer network exploitation against core mobile infrastructure to suppress billing and lift authentication secrets.
-
GCHQ Ministry Stakeholder Relationships Spreadsheets [pdf]
This document details GCHQ's strategic engagement and intelligence support across various UK government departments (e.g., Bank of England, FCO, MoJ, DECC) for 2008-2009, covering areas from economic stability and national security to social policy and infrastructure protection. Each departmental overview outlines specific GCHQ objectives, current headline issues, areas of impact, and intelligence products provided.
People: King, Mervyn · Gieve, John · Bailey, Andrew · Allen, Stuart · Brown, Gordon · Haywood, Jeremy · Fletcher, Tom · Catsaras, Nick · King, Simon · Cavanagh, Matt · Jacobs, Michael · Forsyth, Justin · Wood, Stuart · Hepburn, Eric · Groves, John · O'Donnell, Gus · Hannigan, Robert · McDonald, Simon · Cunliffe, Jon · Allen, Alex · Dowse, Tim · Wright, Chris · Grey, Sue · Johnson, Chris · Styles, Roger · Aldred, Margaret · Cleveland, Alexis · Taylor, Michael · Blears, Hazel · Housden, Peter · Scholefield, Susan · Williams, David · Freeman, Jonathan · Hasan, Jenan · Greaves, Daniel · Boyle, Louise · Whiting, Ed · Pyott, Ian · Usher, Peter · Balls, Ed · Bell, David · Gough, Hermione · Gibbens, Nigel · Anderson, Rodney · Anderson, Michael · Lebrecht, Andy · Cowan, Richard · Derwent, Henry · Dodwell, Chris · Thompson, Jan · Nixon, Tony · Perfect, Trevor · Miliband, Ed · O'Donnell, Rory · Wallace, Moira · Ruddock, Joan · O'Brien, Mike · White, Graham · Neve, John · Benn, Hilary · Ghosh, Helen · Alexander, Douglas · Shafik, Minouche · Lowcock, Mark · Fish, Dave · Warmington, Beverley · Manuel, Marcus · Wardell, Sue · Drummond, Jim · Conway, Gordon · Hendrie, Barb · Leigh, Andy · Dick, Kenny · Leith, Jennifer · Tilbrook, Richard · Kenningham, Andrew · Crawford, Patrick · Havelock, David · Welsh, Gordon · Gotts, Roger · Faulkner, Anthony · Johnson, Alan · Taylor, Hugh · Donaldson, Liam · Harper, David · Beavan, Penny · Ritchie, Judith · Woodall, Mike · Brain, Leon · Eckles, Graeme · McCarthy, Kraig · Eldon, Stuart · Sawers, John · Gass, Simon · Brinkley, Robert · Jenkins, John · Prentice, Christopher · Pringle, Anne · Ehrman, William · Sedwill, Mark · Phillipson, Antony · Noble, Andrew · Bethlehem, Daniel · Thomson, Adam · Johnston, Paul · Davenport, Michael · Rankin, John · Roberts, Colin · Wightman, Scott · Bronnert, Deborah · Bowman, Vicky · Hitchens, Tim · Wood, Adam · Manley, Simon · Choudhury, Anwar · Cowper-Coles, Sherard · Mather, Tony · Fraser, Simon · Grant, Mark Lyall · Leslie, Mariot · Gould, Matthew · MacFarland, David · Hickey, Stephen · Brooker, Catherine · Merron, Gillian · Flint, Caroline · Malloch-Brown · Rammell, Bill · Ricketts, Peter · Miliband, David · Sants, Hector · Robinson, Philip -
GCSB has identified an MFA data link [pdf]
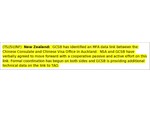
A short extract from an April 2013 NSA document recording that GCSB had identified a Chinese Ministry of Foreign Affairs data link between the Chinese Consulate and the Chinese Visa Office in Auckland, and that NSA and GCSB had verbally agreed to mount a joint passive and active operation against it.
“Leaked papers reveal NZ plan to spy on China for US” - The New Zealand Herald ↗ (2015-04-19) · “New Zealand Plotted Hack on China With NSA” - The Intercept ↗ (2015-04-18) · Fisher, David · Gallagher, Ryan · Hager, Nicky -
GRIMPLATE - First Steps Toward Identifying Adversarial Use of BitTorrent [pdf]
This document outlines the NSA's GRIMPLATE program, which was developed to monitor and analyze BitTorrent traffic on the Department of Defense's NIPRnet to identify potentially malicious activity. The program focuses on crawling the Distributed Hash Table (DHT) of BitTorrent networks to gather data on file-sharing nodes and peer connections, in order to detect and mitigate threats while building a case for halting unauthorized P2P usage on secure networks.
-
Guidelines for the classification of NSA SIGINT details (1945-1967) [pdf]
This document is an NSA classification guide that defines how and why historical SIGINT material from 1945–1967 remains classified, in many cases for 75 years. It systematically explains which intelligence activities, targets, partnerships, and technical methods must stay protected because they still reveal sensitive sources, methods, and diplomatic equities.
-
HIMR Data Mining Research Problem Book [pdf]
This document is a research roadmap created by GCHQ for the Heilbronn Institute for Mathematical Research (HIMR). Its purpose is to guide long-term mathematical and data-mining research that could improve signals intelligence (SIGINT) capabilities. It outlines key research problems, datasets, and collaboration plans between intelligence agencies and academic researchers. The main goal is to develop new algorithms and mathematical tools to analyze extremely large communications datasets produced by modern surveillance systems.
Programs: CLOUD · DISTILLERY · DISCOVER · PRESTON · LECKWITH · TERRAIN · BROADOAK · NGE · FIVEALIVE · CHARTBREAKER · FIRSTCONTACT · GEOFUSION · RADONSHARPEN-B · PRIMETIME · HIDDENOTTER · BAKERSDOZEN · CLASP · SALTYOTTER · BIRCH · SOLIDINK · FLUIDINK · MAMBA · GRINNINGROACH · PIRATECAREBEAR · AUTOASSOC · CROUCHINGSQUIRREL · HRMAP · KACHINA · SQUEAL · QUESTA · METEORSHOWER · SUNSTORM · GOLDMINE · HAGERAWEL · WOODY · BUZZ · SILVERLIBRARY · SILVERLINING · VALHALLA · MOUNTMCKINLEY · SEPANG · BLACKHOLE · SALAMANCA · HAGELAWEL · LUCKYSTRIKE · SPIKYROCK · MYOFIBRIL · INJUNCTION · PSYCHICSALMON · RAGINGBULLFROG · ROBOTICFISH · TIMIDTOAD · AURA · CARBONCOPY · CASK · CHORDAL · CRAN · INSTINCT · MADFORGE · SWAMP · VOLSUNGA · WHITERAVEN · MVR · PPF · JTRIG · MAPREDUCE · MAILORDERPeople: Tukey, John -
HR DIETMAR B - Director SIGINT Analysis and Production German Federal Intelligence Service, 30 April - 1 May 2013 [pdf]
This draft agenda outlines scheduled meetings and presentations for a collaboration event between the German Federal Intelligence Service (BND) and the NSA, held from April 30 to May 1, 2013. The agenda details various discussions on SIGINT analysis, data acquisition, and counterterrorism efforts, showcasing the active engagement between the two intelligence communities.
Programs: SSOPeople: Alexander, Keith B. -
Intelligently filtering your data: Brazil and Mexico case studies [pdf]
These documents reveal that the NSA conducted targeted surveillance operations against high-profile Brazilian and Mexican figures, including President Dilma Rousseff and presidential candidate Enrique Peña Nieto, using advanced contact-graph filtering and data analysis techniques to extract relevant intelligence from intercepted communications. These documents show how NSA analysts systematically developed intelligence on foreign leaders during election periods and diplomatic activities, framing it as “target development,” but in practice enabling deep political espionage under the guise of analytical innovation.
“Veja os documentos ultrassecretos que comprovam espionagem a Dilma” - O Globo ↗ (2013-09-02) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Greenwald, Glenn -
Intellipedia – Air Gapped Network Threats [pdf]
This document from an internal wiki for the U.S. intelligence community, surveys threats to so-called air-gapped systems, arguing that supply-chain compromises, physical implants (BIOS, KVMs, peripherals), infected removable media, and enabled wireless/emanations present realistic paths for adversaries to bridge isolated networks. It assesses likelihoods and attack vectors (including insider help and CDS/guard exploitation), highlights specific historic incidents (Agent.BTZ/MAKERSMARK), and recommends strict removable-media policies, TEMPEST countermeasures, and rigorous cross-domain guard protections to mitigate the risk.
People: Witte, Griff · Warren, Peter · Streeter, Michael · Watson, Paul · Louchard, Bjørn · Crawford, George · Rudge, David · Terrazas, Michael -
Intellipedia – BIOS Threats [pdf]
This from an internal wiki for the U.S. intelligence community, titled “BIOS Threats” details the use of malicious BIOS implants as a means of achieving persistent system compromise for cyber espionage and attack purposes. It discusses the history, technical challenges, detection limitations, and global development of BIOS-based malware by both state and non-state actors, including U.S. and Chinese cyber units.
-
Intellipedia – Supply Chain Cyber Threats [pdf]
This document on Supply Chain Cyber Threats, from an internal wiki for the U.S. intelligence community, outlines vulnerabilities in hardware and firmware components such as power supplies, NICs, RAID controllers, GPUs, and peripheral devices that could be exploited by adversaries through the supply chain. It details assessments from U.S. intelligence agencies (CIA, DIA, FBI, CYBERCOM) highlighting risks from foreign companies, insider threats, and malicious modifications that could compromise critical U.S. government and military systems.
Programs: A-SPACE -
Internet Anonymity 2011 [pdf]
A TOP SECRET NSA presentation from 2011 providing a comprehensive survey of Internet Anonymity Technologies (IAT) — covering HTTP proxies, VPN anonymity providers, multi-hop networks including Tor and JAP, anonymous remailers and circumvention tools — alongside NSA's capabilities and limitations against each, including XKEYSCORE fingerprints for VPN identification, the PARTNERSNIPPET Tor deanonymisation team, GOLDENFORTIN Netflow data, and a candid assessment that Tor offers "no passive exploitation."
Programs: FOXTRAIL · NKB · NACIRONIN · PONTENTPOTABLES · RONIN · XKEYSCORE · PARTNERSNIPPET · GOLDENFORTIN · SNAPEPeople: Heap, Austin