Tag: packet analysis 6 documents
Search documents matching “packet analysis” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
HIDDENSALAMANDER - Alerting and Characterization of Botnet Activity in TURMOIL [pdf]
This NSA briefing describes HIDDENSALAMANDER, a TURMOIL component that detects, tracks, and characterizes botnet command-and-control traffic on passive collection sensors worldwide, generating enriched metadata about bot herders, infected machines, attack commands, and malware families while providing low-latency defensive alerts when botnet activity involves high-value targets or protected networks. The system extends beyond traditional signature matching by decrypting Zeus RC4-encrypted traffic, extracting payload details like target IPs and DDoS commands, tracking C2 servers across multiple sessions, and categorizing botnet lifecycle stages (configuration, infection, reconnaissance, C&C communication, attack, exfiltration) to support both offensive attribution and defensive response.
Programs: HIDDENSALAMANDER · TURMOIL · CLOUDSHIELD · NETEZZA · TUTELAGE · GMPLACE · RONIN · CYBERCLOUD · MARINA · GHOSTMACHINE · QBOT · ASDF · MARIPOSA · XKEYSCORE · GOGADGET · TURQI · TRAFFICTHIEF · FALLOUT · POUNDSAND · BLUESMOKE · AEG · TURNABOUT · QUANTUMBOT -
Mobile Apps Checkpoint Meeting Archives [pdf]
This GCHQ document tracks project checkpoints from December 2009 to July 2010, focusing on the rollout and operationalization of mobile apps, TERRAIN system upgrades, GTP/GRX access, and converged event processing. Key themes include coordinating multi-team dependencies, addressing technical gaps in handset and app data characterization, and ensuring timely delivery of milestones like MIP-1.
Programs: TERRAIN · PRESTON · XKEYSCORE · BEGAL · TAMING PASTRIES · MILKWHITE · MVR · SOCIAL ANTHROPOID · INTEGER SPIN · MUTANT BROTH · GEO FUSION · MARBLED GEKO · BLACKHOLE · ACTOR ACTION · TRAFFICMASTER · HARD ASSOC · MIRTF · HEARTBEAT · SILVER LINING · GREENHEART · EREPO · MAGLITE · POKERFACE · BOSTROM · MIDDLESEX GREEN · ENCHANTERSS · HAUSTORIUM · SALAMANCA · BROADOAK · MONKEY PUZZLE · TACHO · EREPO GAMMA · NINJA · PEBBLE BED · GOLDEN EYE · STRAPROC · STARPROC · LOOKING GLASS · SORCERER · SOCIAL ANIMAL · GTE · NGE · PPF · IIB · UDAQ · MES · TERRAINS · CCDF · SINO · GDR · OSDS · LECKWITH -
Network Shaping 101 [pdf]
An NSA top-secret training presentation that uses Yemen as a case study to explain how to "shape" a nation's Internet traffic by exploiting Autonomous Systems, upstream providers, BGP routing, and physical link topology to redirect or collect communications. The slide deck walks through practical router/IP/link details, passive SIGINT collection points and limitations, and warns that many assumptions are fabricated for the lesson and that real-world capabilities and link behavior can vary.
-
Tor - 2006 CES Summer Program [pdf]
The following document is a 2006 research paper produced for the NSA's "Cryptanalysis and Exploitation Services" office. It lays out the technical features of Tor and proposes a number of theoretical and practical attacks, some of which the NSA developed and used in subsequent years. Among other things, the paper describes an NSA-written adaptation of Tor, "indistinguishable from an original Tor client," which enables the NSA to gather intelligence inside the network. It also describes two kinds of "denial of service" attacks against Tor, code-named Coil and Flower, which are used to divert would-be anonymous communications into open channels.
Programs: MJOLNIR -
TURMOIL IPSEC VPN SESSIONIZATION [pdf]
An NSA technical specification document describing how TURMOIL detects and sessionizes IPSec VPN protocol traffic — covering the six IPSec protocol stacks targeted for collection, the specific keyword and bitmask patterns used by the Atomic Event Generator to identify each packet type at wire speed, and the sessionization parameters used to group related packets into coherent sessions for downstream processing.
-
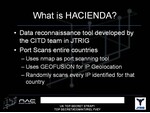
What is HACIENDA? [pdf]
This document details HACIENDA, a large-scale reconnaissance tool used by GCHQ and the Five Eyes alliance to perform automated port scanning and vulnerability mapping across entire nations. It outlines the technical process of identifying and exploiting network infrastructure, specifically for the purpose of discovering Operational Relay Boxes (ORBs) to facilitate covert "Computer Network Exploitation" (CNE).