Tag: Denial of Service 6 documents
Search documents matching “Denial of Service” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Behavioural Science Support for JTRIG’S Effects and Online HUMINT Operations [pdf]
A top‑secret 2011 paper by psychologist Mandeep K. Dhami operationalizes behavioral science for GCHQ’s JTRIG, turning social‑psychology playbooks into a menu of cyber “effects” and online HUMINT to discredit, deceive, disrupt, and deter targets. It recommends training, profiling, measurement, and a bespoke ethics code to systematize influence operations across social platforms and covert personas.
Marking: TOP SECRETPrograms: JTRIGPeople: Dhami, Mandeep K. · Wortley, Richard · Mazerolle, Lorraine · Hall, Gordon C. Nagayama · Barongan, Christy · Mann, Ian · Maio, Gregory R. · Haddock, Geoffrey · Lewicki, Roy J. · McAllister, Daniel J. · Bies, Robert J. · Kahle, Lynn R. · Kim, Chung-Hyun · Horowitz, Leonard M. · Strack, Stephen · Hogg, Michael A. · Vaughan, Graham M. · Garcia-Retamero, Rocio · Forgas, Joseph P. · Cooper, Joel · Crano, William D. · Fiske, Susan T. · Gilbert, Daniel T. · Lindzey, Gardner · Mandel, David R. · Clow, Kenneth E. · Baack, Donald E. · Cialdini, Robert B. · Bachmann, Reinhard · Zaheer, Akbar · Adams, Barbara D. · Sartori, Jessica A. · Yun, Minwoo · Hirsch, Andrew Von · Bottoms, Anthony E. · Burney, Elizabeth · Wikstrom, P-O · Tunnell, Kenneth D. · Piquero, Alex R. · Tibbets, Stephen G. · Snook, Brent · Eastwood, Joseph · Gendreau, Paul · Goggin, Claire · Cullen, R. M. · Kavanagh, Jennifer M. · Smith, Peter B. · Bond, Michael Harris · Slovic, Paul · Knol, Anne B. · Slottje, Pauline · Sluijs, Jeroen P. van der · Savage, Leonard J. · Postmes, Tom · Spears, Russell · Sakhel, Khaled · Groot, Daphne de · Pettigrew, Thomas Fraser · Tropp, Linda R. · Newman, Graeme R. · Mischel, Walter · Miller, Michael D. · Brunner, C. Cryss · McDaniels, Timothy L. · Marcus, Aaron · Perez, Angel · Lee, Eun-Ju · Knight, Frank H. · King, Sara B. · Payne, John W. · Johnson, Eric · Hui, Pan · Buchegger, Sonja · Huffaker, David A. · Furby, Lita · Beyth-Marom, Ruth · Freilich, Joshua D. · Chermak, Steven M. · Fischhoff, Baruch · Lichtenstein, Sarah · Derby, Steven L. · Keeney, Ralph · Felson, Marcus · Clarke, Ronald V. · Wallsten, Thomas S. · Crandall, David · Cosley, Dan · Huttenlocher, Daniel · Kleinberg, Jon · Suri, Siddharth · Carroll, John · Weaver, Frances · Becker, Gary S.“Britain Used Spy Team to Shape Latin American Public Opinion on Falklands” - The Intercept ↗ (2015-04-02) · “Controversial GCHQ Unit Engaged in Domestic Law Enforcement, Online Propaganda, Psychology Research” - The Intercept ↗ (2015-06-22) · “#EspiadosPorLosIngleses: los nuevos documentos de Snowden revelan un plan de espionaje de Gran Bretaña en Argentina por Malvinas” - Todo Noticias ↗ (2015-04-02) · Fishman, Andrew · Greenwald, Glenn -
-
JTRIG tools and techniques [pdf]
This document is an internal GCHQ wiki page from July 2012 detailing the capabilities of GCHQ’s Joint Threat Research Intelligence Group (JTRIG). It serves as an internal "Chinese menu" or catalog of digital tools and techniques used for engineering, intelligence collection, and "effects" (offensive operations).
Programs: JTRIG · CERBERUS · JTRIG RADIANTSPLENDOUR · ALLIUMARCH · ASTRALPROJECTION · TWILIGHTARROW · SPICEISLAND · POISONARROW · FRUITBOWL · NUTALLERGY · BERRYTWISTER · BERRYTWISTER+ · FORESTWARRIOR · JAZZFUSION · BRANDYSNAP · WINDFARM · BOMBAYROLL · COUNTRYFILE · TECHNOVIKING · JAZZFUSION+ · BUMBLEBEEDANCE · AIRBAG · EXPOW · AXLEGREASE · PODRACE · WATCHTOWER · REAPER · DIALd · DIRTYDEVIL · AIRWOLF · ANCESTRY · BEARTRAP · BIRDSONG · BIRDSTRIKE · BUGSY · DANCINGBEAR · DEVILSHANDSHAKE · DRAGON'SSNOUT · EXCALIBUR · FATYAK · FUSEWIRE · GLASSBACK · GODFATHER · GOODFELLA · HACIENDA · GEOFUSION · GLOBALSURGE · ICE · INSPECTOR · LANDINGPARTY · VIKINGPILLAGE · MINIATUREHERO · MOUTH · MUSTANG · PHOTONTORPEDO · RESERVOIR · SEBACIUM · SILVERSPECTER · SODAWATER · SPRINGBISHOP · DIRTYRAT · SYLVESTER · TANNER · TRACERFIRE · VIEWER · TOPHAT · ANGRYPIRATE · ARSONSAM · BUMPERCAR+ · BOMBBAY · BADGER · BURLESQUE · CANNONBALL · CLEANSWEEP · CLUMSYBEEKEEPER · CHINESEFIRECRACKER · BUMPERCAR · CONCRETEDONKEY · DEERSTALKER · GATEWAY · GAMBIT · GESTATOR · GLITTERBALL · IMPERIALBARGE · PITBULL · POISONEDDAGGER · PREDATORSFACE · ROLLINGTHUNDER · SCARLETEMPEROR · SCRAPHEAPCHALLENGE · SERPENTSTONGUE · SILENTMOVIE · SILVERBLADE · SILVERFOX · SILVERLORD · SKYSCRAPER · SLIPSTREAM · STEALTHMOOSE · SUNBLOCK · SWAMPDONKEY · TORNADOALLEY · UNDERPASS · VIPERSTONGUE · WARPATH · HOMEPORTAL · CYBERCOMMANDCONSOLE · NAMEJACKER · BABYLON · CRYOSTAT · ELATE · PRIMATE · JEDI · JILES · MIDDLEMAN · OUTWARD · TANGLEFOOT · SCREAMINGEAGLE · SLAMMER · EARTHLING · NEWPIN · BYSTANDER · CONDUIT · QUINCY · BEARSCRAPE · SFL · SNOOPY · MOBILEHOOVER · NEVIS · CHANGELING · HAVOK · MIRAGE · SHADOWCAT · SPACEROCKET · RANA · LUMP · GURKHASSWORD · CRINKLECUT · SHORTFALL · DEADPOOL · HUSK · LONGSHOT · MOLTEN-MAGMA · NIGHTCRAWLER · PISTRIX · WURLITZER -
New CNO Capability Poised to Help Counter IEDs, Geolocate Terrorists SIDtoday [pdf]
A new capability allows for denial-of-service attacks against High Power Cordless Phone (HPCP) networks and geolocation of high value targets. HPCP networks are frequently used by insurgents in Iraq and Afghanistan as a way to trigger IEDs.
The Intercept ↗ (2018-08-15) -
Offsensive Session: the Boundaries and Against Hacktivism [pdf]
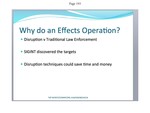
GCHQ slides on “effects” operations against hacktivists: disruption in place of traditional law enforcement, denial-of-service attacks on key communications outlets during Op WEALTH in summer 2011, and a disruption playbook of infiltration, ruse, set-piece, false-flag, false-rescue, disruption and sting operations.
-
Slides Describe Mission Involving Huawei [pdf]
This document details an NSA-led strategic initiative to target Huawei due to its dominance in global telecommunications infrastructure. The operation (codenamed "Shotgiant") aims to exploit Huawei hardware to maintain access to target communications while investigating the company’s potential role in facilitating People’s Republic of China (PRC) signals intelligence and supply chain subversion.