Banner: TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL 37 documents
Search documents matching “TOP SECRET//COMINT//REL TO USA, AUS, CAN, GBR, NZL” →The marking line each document prints.
Graphs
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Advanced HTTP Activity Analysis [pdf]
This NSA training document from 2009 teaches intelligence analysts how to analyze HTTP internet traffic and exploit it using the XKEYSCORE surveillance system to monitor and identify internet users globally.
“XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Marquis-Boire, Morgan · Greenwald, Glenn · Lee, Micah -
BYZANTINE HADES: An Evolution of Collection [pdf]
A classified NSA SIGINT briefing from 2010 describes “BYZANTINE HADES,” a collection of Chinese computer network exploitation activities, with a focus on the BYZANTINE CANDOR actor set and U.S. efforts to analyze, attribute, and counter those intrusions. The document details targeting patterns, technical tradecraft, and a TAO-led counterintelligence operation that successfully penetrated the attackers’ infrastructure and personal systems.
Programs: BYZANTINEHADES · BYZANTINECANDOR · BYZANTINERAPTOR · BYZANTINEANCHOR · BISHOPKNIGHT · BYZANTINEVIKING · MAVERICKCHURCH · BISHOP · BYZANTINETRACE · DIESELRATTLE · BYZANTINEFOOTHOLD · BYZANTINEPRAIRIE · SEEDSPHERE · CARBONPEPTIDE · TITANRAIN · PINWALE · XKEYSCORE · CROSSBONES · TUNINGFORK · ARROWECLIPSE · CUTEBOY · POPROCKS · BYZANTINE -
Center for Content Extraction - Content Extraction Analytics, SIGDEV End-to-End Demo [pdf]
This document is a technical showcase demonstrating the capabilities of an NSA content‑extraction program, using political leaders and diplomatic figures (such as Angela Merkel) as illustrative examples. It presents how automated language technology can extract, organize, and scale intelligence data from intercepted material.
Programs: MARINA · CYBERTRANS · PAINTBALL · SYNAPSE · NYMROD · THUNDERCLOUD · JOURNEYMAN · GOLDENRETRIEVER · SOCIOPATH · LEXHOUND · HERESYITCH · HLT · TKB · EKS -
CNE Analysis in XKEYSCORE [pdf]
This document is an NSA training presentation from October 2009 demonstrating how XKEYSCORE integrates with Computer Network Exploitation (CNE) operations, allowing analysts to search and analyze data extracted from compromised computers including keystrokes, browser history, registry files, documents, emails, and directory structures collected through implants like UNITEDRAKE and OLYMPUS.
Programs: XKEYSCORE · OLYMPUS · UNITEDRAKE · PINWALE · TUNINGFORK · TURBOCHASER · MARINA · JOLLYROGER · TREASUREMAP · TURBINE · PRESSUREWAVE · MAD · TUCKER · EXPANDINGPULLY · UNIX · SEARCHLIGHT · KEYLOGGER · PILBEAM · FOXACID · WAYTIDE · SHADOWQUEST · SEAGULLFARO · DARKHELMET · LUTEUSICARUS · FOGGYBOTTOM · GREENCHAOS · RADIUS · NKB · VALIDATOR -
Cyber Integration [pdf]
The leaked 2012 GCHQ JTRIG presentation detail a wide range of offensive cyber and influence operations designed to “deny, disrupt, degrade, and deceive” targets, including hackers, foreign governments, companies, and individuals. Tactics include hacking, DDOS attacks, disinformation, honey traps, credential harvesting, and psychological operations, reflecting a shift from traditional surveillance to active disruption and manipulation campaigns.
“Exclusive: Snowden Docs Show British Spies Used Sex and 'Dirty Tricks'” - NBC News ↗ (2014-02-07) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Cole, Matthew · Esposito, Richard · Schone, Mark · Greenwald, Glenn -
Driver 1: Worldwide SIGINT/Defense Cryptologic Platform [pdf]
A 2012 NSA management presentation slide revealing the agency's global surveillance architecture across five categories of access — covert cable taps, regional collection sites, computer network exploitation implants, foreign satellite collection, and third-party liaison relationships — including a list of cities hosting clandestine collection operations and confirmation of over 50,000 worldwide malware implants.
Programs: STELLAR · SOUNDER · SNICK · MOONPENNY · LADYLOVE · INDRA · IRONSAND · JACKKNIFE · CARBOY · TIMBERLINE“NSA infected 50,000 computer networks with malicious software” - NRC ↗ (2013-11-23) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Boon, Floor · Derix, Steven · Modderkolk, Huib · Greenwald, Glenn -
FOXACID SOP for Operational Management of FOXACID Infrastructure (Draft) [pdf]
This document is an NSA standard operating procedure (SOP) manual detailing how to manage and operate the FOXACID system, which delivers malware to targets through tools like SECONDDATE and BADDECISION. It provides technical instructions for tracking, deploying, and maintaining covert web-based infections used in global cyber operations.
Programs: FOXACID · FOXSEARCH · WAITAUTO · RAISEBED · FORRESTPLACE · FOXHelp · PUZZLECUBE · YACHTSHOP · SECONDDATE · MAGIC SQUIRREL · MAGICBEAN · FINKCOAT · FRUGALSHOT · QUANTUM · FERRETCANNON · BEACHHEAD · OLYMPUS · UNITERAKE · DIRESCALLOP · DEEPFREEZE · FINKDIFFERENT · DISABLEVALOR · VALIDATOR · MISTYVEAL · UNITEDRAKE · PEDDLE CHEAP · PKTWENCH · FORESTPLACE · FOXCONTACT · EASYHOOKUP · DEMENTIAWHEEL · CASTLECREEK · ROCHELP · QUANTUMINSERT · FABULOUSFABLE · WATCHER · FROZENGAZE · FABFAB · DARKFIRE · CRYPTICSENTINEL · DARKHELMET · PSP · WILLOWVIXEN -
GALLANTWAVE [pdf]
NSA presentation describing GALLANTWAVE — a LONGHAUL capability for VPN decryption — specifically its scaling architecture to handle increased collection volumes and a peering mechanism allowing partner agencies to share single-sided VPN key exchange events so that LONGHAUL can complete decryption attempts that would otherwise fail due to one-sided collection.
-
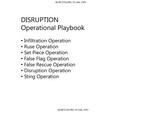
GCHQ - DISRUPTION Operational Playbook [pdf]
A JTRIG “Disruption Operational Playbook” outlines GCHQ’s online covert action toolkit to discredit people and companies, manipulate narratives, and execute false flag, sting, and infiltration operations across targets. It’s a blunt handbook for the four D’s—deny, disrupt, degrade, deceive—translating psychological warfare into clickable tactics on social platforms and forums.
Programs: JTRIG -
GCHQ Cyber Operations Against Anonymous and Hacktivist Groups [pdf]
The leaked 2012 GCHQ presentation reveals that the agency’s JTRIG unit conducted offensive cyber operations against Anonymous and other hacktivist groups, including DDOS attacks (codenamed “Rolling Thunder”), online infiltration, and covert intelligence collection to disrupt their communications and identify key members.
-
GCSB access, XKEYSCORE [pdf]
4 p.These documents confirm that GCSB's Waihopai base (IRONSAND) provides Five Eyes partners, including the UK, with both "strong selected data" and a "full-take feed" of communications from the South Pacific via the NSA's XKEYSCORE system, confirming New Zealand's deep integration into the U.S.-led surveillance network despite facing internal issues with GCSB analysts accessing their own national data within NSA databases.
-
GCSB SIGINT Development Quarterly Report [pdf]
This GCSB quarterly report from July 2009 provides a Top Secret review of major telecommunications developments in the South West Pacific, focusing on the intelligence challenges posed by competitive deregulation and new infrastructure projects, while also detailing GCSB's efforts to enhance its collection capabilities, including the fine-tuning of GSM collection in the Solomon Islands, supporting DSD analyses in Fiji, and preparing for full-take XKEYSCORE data sharing with allies.
“New Zealand Spies on Neighbors in Secret "Five Eyes" Global Surveillance” - The Intercept ↗ (2015-03-04) · “Snowden revelations / The price of the Five Eyes club: Mass spying on friendly nations” - The New Zealand Herald ↗ (2015-03-04) · “New Zealand Spy Data Shared With Bangladeshi Human Rights Abusers” - The Intercept ↗ (2015-04-15) · “Secret documents shine light on GCSB spying in Bangladesh” - The New Zealand Herald ↗ (2015-04-16) · Gallagher, Ryan · Hager, Nicky -
Getting Close to the Adversary – Forward-based Defense with QFIRE (June 3, 2011) [pdf]
This document describes the QFIRE project which is designed to give the NSA a global, low-latency platform for “forward-based defense”, enabling real-time detection and manipulation of Internet traffic close to its source. By co-locating passive sensors (TURMOIL), decision logic (TURBINE), and injection capabilities, QFIRE can rapidly reset connections, redirect targets for exploitation, inject malicious payloads, and even seize control of botnets. It operates as part of the broader QUANTUMTHEORY architecture, leveraging both cooperative and non-cooperative infrastructure worldwide to enable CNE/CND/CNA effects with minimal delay.
Programs: QFIRE · QUANTUMTHEORY · TURBULENCE · TURMOIL · TURBINE · TUTELAGE · QUANTUM · QUANTUMSKY · QUANTUMINSERT · QUANTUMBOT · QUANTUMCOPPER · STRAIGHTBIZARRE · BLINDDATE · TUMULT · ISLANDTRANSPORT · SURPLUSHANGAR · MIDDLEMAN · SCSnet · WEALTHYCLUSTER · SSO -
HTTP Activity vs User Activity [pdf]
This NSA training document from June 2009 explains the distinction between HTTP Activity (general web browsing data) and User Activity (communications metadata from specific protocols like webmail and chat) within the XKEYSCORE surveillance system, demonstrating through Iranian examples how analysts combine both search types to develop comprehensive intelligence on targets.
Programs: XKEYSCORE · MARINA · FOXTRAIL · DECODEORDAIN · YACHTSHOP · BRUTUS · WINDCHASER · NKB · UIS · STARPROC -
Huawei - Social Network Analysis [pdf]
This document describes Social Network Analysis targeting top leadership at Huawei. By tracking the email selectors of CEO Ren Zhengfei and Chairwoman Sun Yafang, the agency mapped their professional and personal connections.
“NSA: Imperiale Visionen” - Der Spiegel ↗ (2014-03-23) · Rosenbach, Marcel · Stark, Holger · Zand, Bernhard -
Introduction to Context Sensitive Scanning with X-KEYSCORE Fingerprints [pdf]
This May 2010 NSA training document introduces XKEYSCORE's context-sensitive scanning capabilities using "fingerprints"—customizable detection rules that allow analysts to surgically target specific types of Internet traffic without needing prior knowledge of email addresses or other strong selectors, using over 70 unique contexts to identify patterns in communications and behaviors.
-
Introduction to XKS Application IDs and Fingerprints [pdf]
This August 2009 NSA training document introduces XKEYSCORE's Application IDs (AppIDs) and Fingerprints system, explaining how metadata tags are automatically applied to intercepted sessions to identify and categorize different types of Internet traffic, applications, and behaviors, evolving through four generations from simple keyword matching to sophisticated code-based metadata extraction.
-
Kaspersky User-Agent Strings [pdf]
This September 2008 NSA technical report reveals that the agency discovered Kaspersky antivirus software's user-agent strings contain encoded serial numbers and can function as unique machine identifiers, allowing tracking of individual computers running the Russian security software across intercepted network traffic collected through the YACHTSHOP surveillance program.
-
Peeling Back the Layers of TOR with EGOTISTICALGIRAFFE [pdf]
An NSA Tailored Access Operations presentation describing EGOTISTICALGIRAFFE and EGOTISTICALGOAT — Firefox browser exploits targeting Tor Browser Bundle users — covering fingerprinting Tor users via the TorButton BuildID, the EGOTISTICALGOAT type confusion vulnerability in Firefox's E4X implementation enabling remote code execution, and the FINKDIFFERENT/FUNNELOUT callback infrastructure used to exfiltrate data from exploited targets.
Programs: EGOTISTICALGIRAFFE · EGOTISTICALGOAT · ERRONEOUSINGENUITY · ERIN · EGGO · FINKDIFFERENT · FIDI · EGGI · FUNNELOUT -
Project CAMBERDADA [pdf]
NSA presentation on Project CAMBERDADA, a programme that intercepts emails sent to antivirus companies reporting new malware, uses SIGINT collection to monitor antivirus vendor communications, and identifies opportunities to repurpose malware before vendors detect it — listing 23 antivirus companies from around the world as targets, with Kaspersky as the primary focus.
People: Picard, François