Tag: Computer Network Exploitation 143 documents
Search documents matching “Computer Network Exploitation” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By document date (11 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
CNE Analysis in XKEYSCORE [pdf]
This document is an NSA training presentation from October 2009 demonstrating how XKEYSCORE integrates with Computer Network Exploitation (CNE) operations, allowing analysts to search and analyze data extracted from compromised computers including keystrokes, browser history, registry files, documents, emails, and directory structures collected through implants like UNITEDRAKE and OLYMPUS.
Programs: XKEYSCORE · OLYMPUS · UNITEDRAKE · PINWALE · TUNINGFORK · TURBOCHASER · MARINA · JOLLYROGER · TREASUREMAP · TURBINE · PRESSUREWAVE · MAD · TUCKER · EXPANDINGPULLY · UNIX · SEARCHLIGHT · KEYLOGGER · PILBEAM · FOXACID · WAYTIDE · SHADOWQUEST · SEAGULLFARO · DARKHELMET · LUTEUSICARUS · FOGGYBOTTOM · GREENCHAOS · RADIUS · NKB · VALIDATOR -
CNE End Point Requirements [pdf]
This NSA/GCHQ document outlines comprehensive requirements for an endpoint surveillance systems that enables analysts to systematically identify intelligence collection needs and discover appropriate tools for data extraction from compromised computers. The framework covers capabilities for remote data collection, cross-platform intelligence integration, query functions, tasking procedures, and visualization tools across implanted networks.
Programs: STARGATE · LOOKING GLASS · QUANTUM · GOLDENEYE · XKEYSCORE · MARINA · JTRIG · BROADOAK · UTT · GLOBALREACH · GLOBALSURGE · THUGGEE · EREPO · DANCINGBEAR · HAUSTORIUM · SHAREOWN · MUTANTBROTH · MOONRAKER · CARBONROD · RUFFLE · ROCKOPERA · QUINCEY · ECLIPSE · MUGSHOT · HIGHNOTE · UDAQ2 · EKB · TURBINE · ACNO · FLAMECARPET · FUMECUPBOARD · JACKPOT · SLIPSTREAM · B13B · PSC · QUINCY · DAREDEVIL · ROADBED -
CNE EndPoint Project Load [pdf]
The CNE EndPoint Project Load document lists multiple GCHQ exploitation projects, with “PFENNING ALPHA” targeting Flag Telecom’s network. It notes automated pulls of router monitoring webpages, collection of performance statistics, and ongoing efforts to gain further access points within Reliance’s infrastructure, while other projects and targets remain redacted.
Programs: PFENNING ALPHA · BURRITO ALPHA · GLADDY IOTA · HEADRESS IOTA · HEADRESS KAPPA · HEADRESS NU · HEADRESS OMICRON · GLADDY CHI · EREPO · RELIANCE · GTE“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
CNE Presence in CT10 Status Report [pdf]
A TOP SECRET NSA status report from April 2008 describing how a counterterrorism analysis team began importing data from the agency's hacking operations into their tracking system — specifically logs from FOXACID, an NSA tool that infects targets' computers mainly through their web browsers — enabling real-time alerts when new targets were successfully hacked, with plans to expand into tracking four named surveillance implants (VALIDATOR, UNITEDRAKE, OLYMPUS and STRAITBIZARRE) as they phone home to NSA servers for instructions and stolen data.
-
CNO Core Secrets Security Structure [pdf]
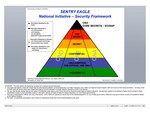
A 3-slide NSA presentation outlining the classification architecture of Sentry Eagle, a national cyber operations initiative, showing how its most sensitive components — covering network hacking, encryption sabotage, and covert industry relationships — are locked behind ECI and SAP designations accessible only to a tiny circle of government officials.
Programs: SENTRYEAGLE · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL -
CNO Core Secrets Slide Slices [pdf]
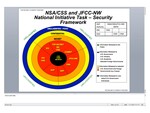
This document outlines the Security Framework for a joint national initiative between the NSA/CSS and JFCC-NW, detailing the highly compartmented structure used to protect cyber and intelligence secrets. It utilizes a concentric security framework diagram to visualize the layers of sensitivity, placing the most critical technical capabilities at the absolute center of the intelligence community's protection.
Programs: SENTRY-EAGLE · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL -
Collaboration in Overdrive: A CNE Success SIDtoday [pdf]
A collaboration between several NSA departments achieved, for the first time, Computer Network Exploitation against "Turkish leadership."
Programs: CMAP“Turkey Is 'Partner and Target' for the NSA” - Der Spiegel ↗ (2014-08-31) · “How the NSA Helped Turkey Kill Kurdish Rebels” - The Intercept ↗ (2014-08-31) · The Intercept ↗ (2019-05-29) · Poitras, Laura · Rosenbach, Marcel · Sontheimer, Michael · Stark, Holger -
COMPUTER NETWORK OPERATIONS - GENIE [pdf]
A TOP SECRET Congressional Budget Justification entry for the NSA/CSS GENIE project — the Tailored Access Operations programme underpinning all endpoint Computer Network Operations — requesting $651.7 million and 1,870 military and civilian positions for FY2013, with plans to maintain 85,000-96,000 implant points-of-presence worldwide and 9,000-10,000 active accesses, including $25.1 million for covert purchase of software vulnerabilities and a $3.4 million supply chain implant operation targeting al-Qaeda.
-
Computer-Network Exploitation Successes South of the Border [pdf]
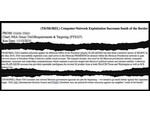
Pena Nieto's predecessor as president, Felipe Calderon, was also targeted. This image shows an excerpt from an NSA document classified as "top secret," from November 2010. The National Security Agency (NSA) has a division for particularly difficult cases. Called "Tailored Access Operations," or TAO for short, this department devises special methods for special targets. In May 2010, the division reported mission accomplished. A report classified as "top secret" said: "TAO successfully exploited a key mail server in the Mexican Presidencia domain within the Mexican Presidential network to gain first-ever access to President Felipe Calderon's public email account." According to the NSA, this email domain was also used by cabinet members, and contained "diplomatic, economic and leadership communications which continue to provide insight into Mexico's political system and internal stability."
Programs: FLATLIQUID -
CSEC Cyber Threat Capabilities [pdf]
This document details CSEC’s full-spectrum cyber operations architecture, integrating SIGINT and IT Security to conduct both defensive and offensive activities under the guise of “information superiority.” While early sections emphasize detection, anomaly analysis, and collaboration with Five Eyes partners, later portions reveal active measures including network infiltration (implant deployment), command-and-control tracking, traffic manipulation and redirection, DNS interference, and potential disruption or deception operations—illustrating CSEC’s capacity not only to defend Canadian networks but also to surveil, exploit, and influence foreign and domestic digital infrastructure.
Programs: EONBLUE · CYBERDMZ · SEEDSPHERE · PHOTONICPRISM · SPECIALSOURCE · SUPERDRAKE · DARKSPACE · QUANTUM · MANDATE · STREAMING SENTRY · SSO · TKB · COVENANT -
CSEC Cyber Threat Detection [pdf]
This document details the Communications Security Establishment’s (CSEC) cyber threat detection and intelligence infrastructure, including systems like EONBLUE, CROSSBOW, CRUCIBLE, and LODESTONE, which enable passive monitoring, anomaly detection, and botnet identification through metadata and deep packet inspection. It outlines how CSEC integrates SIGINT, cryptanalysis, and network forensics to detect and mitigate cyber intrusions using both SIGINT and domestic sensors, while collaborating with Five Eyes partners to enhance Canada’s cyber defense and situational awareness. The presentation is duplicated from page 7 onwards - one of the duplicated slide has internal CSE comments.
Programs: EONBLUE · SPECIALSOURCE · WARRANTEDACCESS · COVENANT · SEEDSPHERE · DIESELRATTLE · SIENNABLUE · DOWNGRADE · CROSSBOW · CRUCIBLE · LODESTONE -
CSEC SIGINT Cyber Discovery: Summary of the current effort [pdf]
This document provides a overview of the Communications Security Establishment Canada (CSEC) cyber operations, detailing its SIGINT, CNE (Computer Network Exploitation), and cyber counterintelligence programs, including tools like WARRIORPRIDE, REPLICANTFARM, and EONBLUE for threat detection, anomaly discovery, and metadata production. It outlines operational procedures, analytic methodologies, and collaborative frameworks with domestic and Five Eyes partners for sharing intelligence, tipping/cueing, and integrating cyber and traditional counterintelligence efforts.
Programs: REPLICANTFARM · SLIPSTREAM · WARRIORPRIDE · DAREDEVIL · CHORDFLIER · NAMEDROPPER · WORMWOOD · OBELIX · SHEPHERD · CARBON · REGBACKUP · DOGHOUSE · WALKER · ALOOFNESS · BLAZINGANGEL · TINYWEB · QUIVERINGSQUAB · WINDO · DIESELRATTLE · WIDOWKEY · CIVETCAT · WINBEE · SSLINST · PULLEDPORK · EONBLUE · SNIFFLE · QUANTUM · XKEYSCORE · HALTERHITCH · FASTFLUX · DEADSEA · NSPACES · PPF · SSO · TKB“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “Communication Security Establishment's cyberwarfare toolbox revealed” - CBC News ↗ (2015-03-23) · “Documents Reveal Canada’s Secret Hacking Tactics” - The Intercept ↗ (2015-03-23) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Seglins, Dave · Hildebrandt, Amber · Pereira, Michael · Greenwald, Glenn · Gallagher, Ryan -
Cyber Defence Operations Legal Policy [pdf]
GCHQ's internal wiki laying out the legal plumbing for its Cyber Defence Operations (formerly NDIST)—detailing warrant types (RIPA, ISA, CNE), data retention schedules, targeting rules for UK/Five Eyes infrastructure, XKEYSCORE query protocols, and the bureaucratic hoops analysts must jump through to search attacker IPs, fingerprint UK networks, and share malware intelligence without tripping over location/nationality safeguards or commercial sensitivities.
Programs: JTRIG · SPAY · GORDIANKNOT · CHORDAL · DISCOVER · EVENTS · CASPORT · XKEYSCORE · CONTENT CLOUD · SQUEAL · MIRAGE · MUTANTBROTH · ANXIOUS · HALTERHITCH · BROADOAK · DONKEYKONG · ZOOL · PALANTIR · OVERLINK · RT · GATEKEEPER · IRONHAND · HARUSPEX · B3M · LOOKINGGLASS · GOLDENEYE · BLAZINGSADDLES · MOONRAKER · TRITON -
DEFIANTWARRIOR and the NSA's Use of Bots [pdf]
This TOP SECRET NSA presentation from 2010 documents the DEFIANTWARRIOR effort to identify, seize, and operate botnets using SIGINT-enabled infrastructure, detailing both early failures and subsequent operational successes. The document reveals how bot herding was integrated into broader offensive cyber and intelligence collection strategies across the Five Eyes.
Programs: DEFIANTWARRIOR · OLYMPUS · UNITEDRAKE · TURBULENCE · QUANTUMBOT · TURMOIL · TURBINE · SNIPERS · XKEYSCORE · INCENSER · STELLABLUE · SMOKYSINK · STOVEPIPES · ISLANDTRANSPORT · FESTIVEWRAPPER · FREEFLOW · PRESSUREWAVE · HANGARSURPLUS · SURPLUSHANGER · WAITAUTO · DEEPFRIEDPIG · SEAGULLFARO · COLOSSUS · STORMPIG · YELLPIG · PASTEPIG · SHOUTPIG · ZORPIG · MAILORDER · TREASUREMAP · MARINA · WARNVOLCANO · STRAITBIZARRE · BOTINSTANCES · PUZZLECUBE · SEEKER · SURPLUSHANGAR -
DNE, DNI, and CNE (repost) SIDtoday [pdf]
(Repost) Explanation of the differences between Digital Network Exploitation, Digital Network Intelligence, and Computer Network Exploitation: DNE is extracting intelligence from a device on the global network; DNI is the intelligence produced by DNE; and CNE is hacking end-point devices (mentions “subtly weakening encryption”). Article acknowledges that “our targets communications are increasingly buried by millions of non-target communications.”
The Intercept ↗ (2016-08-10) -
Driver 1: Worldwide SIGINT/Defense Cryptologic Platform [pdf]
A 2012 NSA management presentation slide revealing the agency's global surveillance architecture across five categories of access — covert cable taps, regional collection sites, computer network exploitation implants, foreign satellite collection, and third-party liaison relationships — including a list of cities hosting clandestine collection operations and confirmation of over 50,000 worldwide malware implants.
Programs: STELLAR · SOUNDER · SNICK · MOONPENNY · LADYLOVE · INDRA · IRONSAND · JACKKNIFE · CARBOY · TIMBERLINE“NSA infected 50,000 computer networks with malicious software” - NRC ↗ (2013-11-23) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Boon, Floor · Derix, Steven · Modderkolk, Huib · Greenwald, Glenn -
Exceptionally Controlled Information Compartments (January 2013) [pdf]
This document, dated January 2013, provides a list of Exceptionally Controlled Information (ECI) compartments utilized by the NSA and its Five Eyes partners. This document categorizes highly sensitive intelligence programs by their codenames, three-letter trigraphs, and the specific organizations responsible for them. The primary organizations listed include TAO, NCSC, and CES. These compartments represent the highest level of information security, designed to restrict access to sensitive technical data and specific intelligence sources even among individuals with high-level security clearances.
Programs: AMBULANT · APERIODIC · AUNTIE · BLACKANT · BLACKAXE · BLACKBALL · BLACKCLOUD · BLACKHOLE · BLACKJACK · BLACKTIE · BLACKVULTURE · BLACKWIDOW · BOXWOOD · CELESTIALGLOBE · CHIEFDOM · CLICKUMBER · CRIMSONREGENT · CRIMSTONSTEAL · CRUMPET · DECKSTOP · DEVILFISH · DIXIESPRING · DOMINATE · FASTIDIOUS · FIRESCREEN · FIRSTDOWN · FISSURESALUTE · FLYLEAF · FORBIDDEN · FORBORNE · FOXHEAT · FREELUNCH · FROTHYTWOPACK · FURTIVERELIANCE · GOLDENCALF · HELLFIRE · HISTORY · HYSSOP · INVEIGH · KESSELRUN · LIGHTNINGTHIEF · LITTLECROWN · LONGSERPENT · MAGICSTROKE · MERCURYTAO · MUSICBOX · NITEHAWK · OCELLUS · PAINTEDEAGLE · PAWLEYS · PAWNSHOP · PENDLETON · PENDRAGON · PERKYAUTUMN · PHENYLDOUR · PICARESQUE · PICAROON · PIEDMONT · PITCHFORD · PLACEBO · POMPANO · PRESSURETWIN · REDHARVEST · REEFPOINT · REFRACTOR · REVELRY · RIVERROAD · RUBIOUS · SAILWINDS · SCABBARD · SILVERCLOUD · SINKGOAL · STAIRWELL · STARCHART · SUITESWIVEL · TRICKSHOT · WAXOFF · WHIPGENIE -
Expanding TAO's Operational Capabilities Out to the CCs SIDtoday [pdf]
NSA Cryptologic Centers in Hawaii, Texas, and Georgia can now conduct Computer Network Exploitation.
The Intercept ↗ (2019-05-29) -
Expeditionary Access Operations: NSA’s Close Access Network Exploitation Program [pdf]
The document describes NSA/TAO’s Expeditionary Access Operations (EAO, S3283), a deployable arm that conducts human-enabled Close Access Network Exploitation (CNE) worldwide—using techniques from physical implants and gifted/compromised laptops to wireless injection tools (e.g., BLINDDATE, NITESTAND) and Wi-Fi geolocation—to support tactical customers like SOCOM, DIA, and task forces in Afghanistan, Iraq, and elsewhere. It details organization, tools, operational theaters (Bagram, Kabul, Kandahar, Stuttgart, Texas, etc.), specific operations (IRONPERSISTENCE, CLIMBINGSHIRT), and plans to formalize partnerships with USCYBERCOM and expand expeditionary CANO capabilities.
Programs: NITESTAND · HAPPY HOUR · BADDECISION · MASTERSHAKE · IRONPERSISTENCE · CLIMBINGSHIRT · BLINDDATE -
Exploiting Terrorists' Passwords SIDtoday [pdf]
The SIGINT Forensics Lab discovered that computer disks seized by the government not only contain intelligence, but are also a "rich source of passwords and related information." Researchers created special tools and harvested "hundreds of thousands of occurrences of passwords," which they used to attack encrypted files.
Programs: JUMBLEDPETPeople: O'Hara, MikeThe Intercept ↗ (2016-12-07)