Publication year: 2014 283 documents
Search documents matching “2014” →When a publisher first published each document. If a document is published multiple times, only the oldest one is used here.
Graphs
By document date (12 years)
By published date (6 years)
Sort: Title
Documents
-
POISONNUT [pdf]
NSA Wiki page describing POISONNUT — also known as the VPN Attack Orchestrator (VAO) — a LONGHAUL cryptologic exploitation service for IPSec VPN decryption that has existed in various forms since 2003, serving clients including TURMOIL, WEALTHYCLUSTER and the Transform Engine emulator via ISLANDTRANSPORT with ISLANDHIDEAWAY encryption.
Programs: POISONNUT · TURMOIL · WEALTHYCLUSTER · ISLANDTRANSPORT · ISLANDHIDEAWAY · LONGHAUL · OAKLEY · SCARLETFEVER · PICARESQUE · VALIANTSURF -
PRISM (US-984XN) expanded its impact [pdf]
FY2012 figures for PRISM: 24,096 end-product reports (up 27 percent), the most-cited SIGAD in first-party reporting at 15.1 percent, 1,477 reports cited in the President's Daily Brief, tasked selectors up 32 percent to 45,406, and taskable e-mail domains expanded from 40 to 22,000.
Programs: PRISM -
PRISM Olympic Option [pdf]
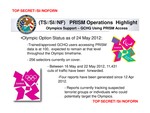
A May 2012 NSA operational highlight revealing that Britain's GCHQ was given access to the NSA's PRISM surveillance system during the London Olympics, with 100 trained British operatives secretly monitoring 256 targets and intercepting over 11,000 communications in a single week.
-
Private Networks are Important [pdf]
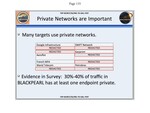
A slide arguing that many targets use private networks — Google's infrastructure, the SWIFT network, Gazprom, Aeroflot, the French foreign ministry, Warid Telecom and Petrobras — with a survey finding that 30 to 40 percent of BLACKPEARL traffic has at least one private endpoint.
Programs: BLACKPEARL -
Psychology: A New Kind of SIGDEV [pdf]
This document presents a detailed approach to integrating human sciences—such as psychology, sociology, anthropology, economics, and political science—into intelligence operations. It highlights the use of tools like SIGINT, HUMINT, and covert online monitoring to understand and shape human behavior, influence networks, and assess socio-cultural dynamics. The focus is on using real-time data analytics, including tracking social media interactions, to optimize intelligence gathering and strategic influence.
Programs: JTRIG · HSOC · SQUEAKY DOLPHIN · DISTILLERY · AIRWOLF · ANTICRISISGIRL · SPLUNK · STREAMINGANALYTICS · HOLLOWPOINT · FIREANT · GTE“Snowden Documents Reveal Covert Surveillance and Pressure Tactics Aimed at WikiLeaks and Its Supporters” - The Intercept ↗ (2014-02-18) · “Snowden docs reveal British spies snooped on YouTube and Facebook” - NBC News ↗ (2014-01-27) · Greenwald, Glenn · Gallagher, Ryan · Esposito, Richard · Cole, Matthew · Schone, Mark -
PTC Glossary [pdf]
This GCWiki PTC Glossary excerpt defines SIGINT-related telecom terms—IMEI, IMSI, INMARSAT—and documents internal collection systems (e.g., INCENSER at Bude) and targeting notes (which identifiers are useful for targeting and which are not). It’s a technical reference for signals analysts describing selectors, collection sources, and operational caveats.
“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
Quadrennial Intelligence Review Final Report, 2009 [pdf]
This 2009 strategic review from the Director of National Intelligence outlines potential future operating concepts for the US Intelligence Community, including "safe bets" like mass data analysis (Sentient Enterprise) and controversial "strategic hedges" such as using clandestine cyber operations to acquire proprietary technology from foreign corporations to benefit US industry (Technology Acquisition by All Means).
People: Shedd, David R. -
QUANTUMHAND [pdf]
This slide describes QUANTUMHAND, a specialized "Man-on-the-Side" (MOTS) attack used by the NSA's Tailored Access Operations (TAO) to infect targets visiting Facebook. The document outlines an automated process where the NSA's surveillance infrastructure, TURMOIL and TURBINE, detects a target's connection to Facebook and "races" against the legitimate Facebook server to deliver a malicious response first. This "winning the race" allows the NSA to redirect the user to a TAO server that attempts to deploy malware "implants" on the target's computer.
-
QUANTUMINSERT [pdf]
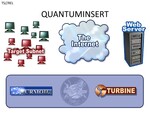
This top-secret NSA presentation provides a step-by-step visual walkthrough of a man-on-the-side (MOTS) attack. This technique allows the NSA to covertly redirect a target's web browser to a malicious server in order to install a malware implant. The diagrams illustrate the interaction between the NSA's global surveillance sensors (TURMOIL) and its automated command-and-control system (TURBINE), demonstrating how the agency exploits the fundamental "race condition" of the internet to compromise a target.
-
QUANTUMTHEORY (2010 SIGINT Development Conference) [pdf]
This 2010 NSA presentation reveals QUANTUMTHEORY, a suite of "man-on-the-side" network attack technologies that enable real-time injection and manipulation of TCP/IP connections through passive surveillance infrastructure. The system encompasses multiple specialized attack techniques including HTML redirection, DNS hijacking, botnet takeover, and database injection, deployed at Five Eyes surveillance sites worldwide.
Programs: QUANTUMTHEORY · TRAFFICTHIEF · TURMOIL · TURBINE · QUANTUM · NINJANIC · ISLANDTRANSPORT · SURPLUSHANGER · DAREDEVIL · STRAIGHTBIZARRE · QUANTUMINSERT · QUANTUMSKY · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMDNS · QUANTUMBOT2 · QUANTUMCOPPER · QUANTUMMUSH · HUFFMUSH · QUANTUMSPIM · QUANTUMSQUEEL · QUANTUMSQUIRREL · INCENSOR · SMOKEYSINK · SARATOGA · QUANTUMDEFENSE · TURBULENCE“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
RAMPART-A Project Overview [pdf]
This document is a 2010 project overview of RAMPART-A, a highly unconventional NSA special access program dedicated to tapping high-capacity international fiber-optic cables at global "congestion points." Through clandestine bilateral partnerships, the NSA installs U.S. equipment on foreign soil to intercept massive volumes of transit data, providing the agency with a unique vantage point that covers virtually every country in the world.
Programs: RAMPART-A · RAMPART-T · SMOKYSINK · AZUREPHOENIX · SPINNERET · TRANQUIL · MOONLIGHTPATH · FIREBIRD · FALCONSTRIKE · DULCIMER · REDHARVEST · FLASHMARK · CONDORSPEAK · TURMOIL · SSO“How Secret Partners Expand NSA’s Surveillance Dragnet” - The Intercept ↗ (2014-06-18) · “NSA ‘third party’ partners tap the Internet backbone in global surveillance program” - Dagbladet Information ↗ (2014-06-19) · Gallagher, Ryan · Geist, Anton · Gjerding, Sebastian · Moltke, Henrik · Poitras, Laura · Jensen, Kristian -
RAMPART-A Sites [pdf]
This document specifies the data throughput and operational constraints of five key RAMPART-A interception sites, including the implementation of the "DNI Throttle" to manage data volume. It also defines the "Support Hub" model for managing signals tasking and explains the role of the REDHARVEST compartment in restricting which analysts can view specific digital network categories.
Programs: RAMPART-A · AZUREPHOENIX · MOONLIGHTPATH · SPINNERET · SMOKYSINK · FIREBIRD · XKEYSCORE · PINWALE · REDHARVEST · CADENCE“How Secret Partners Expand NSA’s Surveillance Dragnet” - The Intercept ↗ (2014-06-18) · “NSA ‘third party’ partners tap the Internet backbone in global surveillance program” - Dagbladet Information ↗ (2014-06-19) · Gallagher, Ryan · Geist, Anton · Gjerding, Sebastian · Moltke, Henrik · Poitras, Laura -
RECEIPT OF FUNDS [pdf]
In 2003 and 2004, the Israelis were pressuring the NSA to agree to a massively expanded intelligence-sharing relationship called “Gladiator.” As part of that process, Israel wanted the Americans to pay hundreds of millions of dollars to fund Israeli activities. The specific proposed “Gladiator” agreement appears never to have been consummated, derailed by Israeli demands that the U.S. bear the full cost, but documents in the Snowden archive pertaining to those negotiations contain what appear to be two receipts for one or more payments of $500,000 in cash to Israeli officials for unspecified purposes.
Programs: GLADIATOR -
Regions [pdf]
A classified GCHQ document listing 63 undersea and terrestrial cables accessible to British intelligence, with landing locations across the UK coastline and capacity figures in gigabits per second, forming part of the Snowden archive documents published by Süddeutsche Zeitung revealing Cable & Wireless/Gerontic's cooperation with GCHQ.
“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
Report about Operation Doody - The Child of the Neighbor Shot By Accident [pdf]
This Dynamic Target Storyboard documents a 7 Feb 2011 UK AH‑64 engagement (Op STEN TAKAY) against “Obj DOODY” (Mullah Niaz Muhammed, IS3673), a JPEL mid‑level Taliban commander, which culminated in an AGM‑114 miss that may have killed a local child and wounded another civilian, and a follow‑on 30mm strafing run that wounded the target.
People: Muhammed, Mullah Niaz -
Research & Technology – Penetrating Hard Targets [pdf]
The NSA’s “Penetrating Hard Targets” program aims at developing a cryptologically useful quantum computer capable of breaking strong encryption systems, including those protecting global financial and government communications. Conducted under the U.S. intelligence “black budget,” the program focuses on quantum physics research, engineering studies, and experimental milestones such as achieving dynamical decoupling and quantum control on semiconductor qubits, which are foundational for scaling to larger systems. A related initiative, “Owning the Net,” explores quantum communication technologies to develop new Quantum Key Distribution (QKD) attacks and assess the security of emerging encryption methods.
-
Running Strategic Analytics Affecting Europe and Africa [pdf]
This Top Secret presentation from the NSA ECC (European Cryptologic Center) outlines the strategic challenges and technical methodology for conducting signal intelligence operations across Europe and Africa. It emphasizes a critical reliance on "Second Party" partnerships, particularly with the UK's GCHQ, and details the use of mass surveillance tools like XKEYSCORE to track terrorism, smuggling, and human trafficking networks.
Programs: XKEYSCORE · RTRG · DISTILLERY · CLOUD · GHOSTMACHINE · NIAGARAFILES · WHIZBANG · MAPREDUCE -
SCARLETFEVER [pdf]
NSA WikiInfo page describing SCARLETFEVER — the second LONGHAUL cryptanalytic capability, a message-driven cryptologic exploitation service for DNSC (Data Network Session Cipher) traffic serving clients including TURMOIL, WEALTHYCLUSTER and the TEe, communicating via ISLANDTRANSPORT with ISLANDHIDEAWAY encryption.
Programs: SCARLETFEVER · LONGHAUL · TURMOIL · WEALTHYCLUSTER · TEE · ISLANDTRANSPORT · ISLANDHIDEAWAY · POISONNUT · PICARESQUE -
Secure Sockets Layer (SSL) / Transport Layer Security (TLS) [pdf]
A classified NSA Network Security Products training presentation providing a comprehensive technical overview of SSL/TLS protocol mechanics and NSA's exploitation approaches, including observed usage statistics from intercepted traffic, RSA key exchange decryption methodology, exploitation of the Debian OpenSSL RNG weakness, and the practical challenges of decrypting millions of SSL sessions per day at scale.
Programs: SCARLETFEVER -
Sentry Eagle Brief Sheet [pdf]
A classified NSA/JFCC-NW briefing document formally inducting cleared personnel into Sentry Eagle — the agency's most sensitive umbrella program protecting core secrets about its cyber operations — and enumerating, tier by tier, what the NSA conceals about its covert industry partnerships, encryption sabotage, network hacking, computer network defense, and human intelligence relationships.
Programs: SENTRYEAGLE · SPARECHANGE · WHIPGENIE · AUNTIE · AMBULANT · OPALESCE · REVELRY · REFRACTOR · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL · BLUESASH · TAREX