Program: JTRIG 33 documents
Search documents matching “JTRIG” →Codenames and programs recorded for each document.
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Mobile Networks in My NOC World [pdf]
This TOP SECRET STRAP 2 GCHQ document outlines the “MyNOC” operations, a specialized Network Operations Centre used by the UK’s GCHQ to coordinate cyber exploitation of international mobile and telecom infrastructure, with a particular focus on Belgacom’s GRX network under “Operation Socialist” (OP SOCIALIST). It details operational planning, toolsets, personnel roles, network mapping, QUANTUM INSERT targeting, and successful infiltration strategies that enabled CNE (Computer Network Exploitation) access to key Belgacom systems and staff infrastructure.
Programs: HIGHNOTE · COPPERHEAD · NEXUS · CADDIS · BRENT · RUSSETT PHONE · CERBERUS · E-BEAM · PIA · JEDI · WYLEKEY · INTERACTION · EREPO · QUANTUM · WOODCUTTER · MUTANT BROTH · QUANTUM INSERT · NRTA · MERION ZETA · JTRIG · A-SPACE · GEOFUSION“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · “Britain's GCHQ Hacked Belgian Telecoms Firm” - Der Spiegel ↗ (2013-09-20) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
OP HIGHLAND FLING - Event Log [pdf]
A TOP SECRET operational event log from GCHQ's GCWiki documenting a January 2011 operation targeting Gemalto employees in France, Poland and elsewhere, using MUTANT BROTH cookie analysis, Facebook credentials, LinkedIn profiles and Computer Network Exploitation to identify and implant targets as part of the operation to steal SIM card encryption keys.
-
Operational Engineering November 2010 [pdf]
This internal GCHQ briefing from late 2010 documents the Events Product Centre's suite of bulk internet and communications surveillance tools — including IMMINGLE, SALAMANCA, SOCIAL ANTHROPOID, MUTANT BROTH, KARMA POLICE, SAMUEL PEPYS and GUIDING LIGHT — covering scaling targets, new data sources, and operational capabilities across telephony, webmail, instant messaging, social media, GPRS and VoIP collection.
Programs: EVENTS · IMMINGLE · SALAMANCA · GUIDINGLIGHT · B3M · HARDASSOC · MAINWAY · THUGGEE · FASCIA · HAUSTORIUM · FIRESTORM · TERRAIN · SHAREOWN · ESCHAR · BRIO · INFINITEMONKEY · KARMAPOLICE · MARBLEDGECKO · MEMORYHOLE · MUTANTBROTH · SAMUELPEPYS · SOCIALANIMAL · SOCIALANTHROPOID · HEARTBEAT · SANTHROPOID · LEAKYGATEWAYS · GTPTUNNEL · LUSTRE · GLASSBACK · COLLATERAL · HRMAP · SWORDPLAY · BROADOAK · REFORMER · ARTEMIS · MERLOT · CONTRAOCTAVE · CRYINGFOWL · CULTWEAVE · SAMDYCE · GCQUERY · BLAZZINGSADDLES · EREPO · JTRIG · SOUNDER -
Operational Legalities – GCHQ Powerpoint Presentation [pdf]
GCHQ’s “Operational Legalities” deck is an internal compliance playbook that translates the UK’s surveillance laws into day‑to‑day SIGINT procedure—drilling staff on authorisation, necessity, and proportionality, and walking through warrants, targeting justifications, database queries, dissemination, and oversight. Half slides and half speaker notes, it shows how analysts are trained to document, audit, and defend operations under ISA, RIPA, HRA, and WTA while navigating edge cases like location, nationality, second‑party constraints, and “indirect targeting.”
-
Psychology: A New Kind of SIGDEV [pdf]
This document presents a detailed approach to integrating human sciences—such as psychology, sociology, anthropology, economics, and political science—into intelligence operations. It highlights the use of tools like SIGINT, HUMINT, and covert online monitoring to understand and shape human behavior, influence networks, and assess socio-cultural dynamics. The focus is on using real-time data analytics, including tracking social media interactions, to optimize intelligence gathering and strategic influence.
Programs: JTRIG · HSOC · SQUEAKY DOLPHIN · DISTILLERY · AIRWOLF · ANTICRISISGIRL · SPLUNK · STREAMINGANALYTICS · HOLLOWPOINT · FIREANT · GTE“Snowden Documents Reveal Covert Surveillance and Pressure Tactics Aimed at WikiLeaks and Its Supporters” - The Intercept ↗ (2014-02-18) · “Snowden docs reveal British spies snooped on YouTube and Facebook” - NBC News ↗ (2014-01-27) · Greenwald, Glenn · Gallagher, Ryan · Esposito, Richard · Cole, Matthew · Schone, Mark -
Pull Steering Group Minutes [pdf]
A top secret STRAP1 GCHQ PullThrough Steering Group meeting record from February 2008 documenting the approval process for five surveillance and intelligence prototypes including KARMA POLICE — the mass internet browsing profiling system — alongside ORB FINDER for CNE operational relay box identification, SALTY OTTER for cross-media timing analysis, MOOSE MILK for telephone kiosk surveillance, and LIGHTWOOD for email address extraction used by JTRIG.
Programs: MYOFIBRIL · SALTYOTTER · PRIMETIME · KARMAPOLICE · ORBFINDER · MOOSEMILK · LIGHTWOOD · JTRIG · MERAPEAK · MONTEVISTA · KED -
SDSG Integrated Analytics Workshop (14 Oct 2011) [pdf]
This document is a summary of a workshop held by the SIGINT Development Steering Group (SDSG) on October 14, 2011, evaluating and comparing the strengths, weaknesses, and potential use of advanced analytics tools, specifically Palantir and Mamba, for intelligence analysis. It discusses the tools' capabilities in data integration, collaboration, and visualization, along with concerns about security, usability, and the risks of relying on commercial software.
Marking: SECRET -
SEBACIUM - GCWiki [pdf]
This GCWiki document outlines SEBACIUM, a suite of tools developed for monitoring and exploiting peer-to-peer (P2P) networks, particularly eMule and BitTorrent, to track and target users sharing or downloading specific content, such as extremist material, for intelligence and operational purposes. It also details various tools within the system, including DIRTY RAT for tracking file-sharing activities and PLAGUE RAT for altering search results in P2P networks.
-
The Art of Deception: Training for a New Generation of Online Covert Operations [pdf]
A top-secret JTRIG training deck lays out how GCHQ turns social science into operational tradecraft for online covert action—blending online HUMINT, strategic influence, and disruption/CNA—while “building cyber magicians” through a formal accreditation program. The curriculum operationalizes deception, persuasion, and group dynamics into false flags, ruses, and reputation attacks aimed at producing real-world “effects.”
Programs: JTRIGPeople: Robert-Houdin, Jean · Maskelyne, Jasper · Mulholland, John · Fishburne, Tom · Robles, Arturo · Teller -
TOR deanonymisation research (MIP) [pdf]
A TOP SECRET GCHQ wiki page documenting the research task on Tor deanonymisation — the project page linking the entry-exit correlation attack described in the OPC-MCR presentation to its formal research output, confirming the attack was successfully documented in OPC-M/TECH.B/61, presented at SANAR11, and planned for prototyping in the REMATION II workshop.
-
Tor Hidden Services - How Hidden is 'Hidden'? [pdf]
A TOP SECRET GCHQ presentation analysing the security of Tor hidden services — covering the hidden service protocol architecture, possible exploitation vectors including the Coil Attack against introduction points, a beaconing pattern discovered in idle hidden services, and the HOMING TROLL bridge discovery capability — concluding that hidden services are "near impossible" to deanonymise but noting several research avenues including PRESTON integration.
-
Tor: Overview of Existing Techniques [pdf]
A TOP SECRET GCHQ presentation summarising existing Tor exploitation techniques and 2012/13 plans documenting GCHQ's Tor-related programmes, naming QUICK ANT, HOMING TROLL, NEWTONS CRADLE, TRIBAL CARNEM, EPIC FAIL, THEMP, NATURAL SELECTION and HAKIM alongside the MCR deanonymisation research, traffic shaping, hidden service investigation and bridge discovery work.
Programs: HOMINGTROLL · NEWTONSCRADLE · JTRIG · TRIBALCARNEM · EPICFAIL · QUICKANT · NATURALSELECTION · REMATION · HAKIM · THEMP -
What is HACIENDA? [pdf]
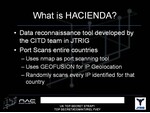
This document details HACIENDA, a large-scale reconnaissance tool used by GCHQ and the Five Eyes alliance to perform automated port scanning and vulnerability mapping across entire nations. It outlines the technical process of identifying and exploiting network infrastructure, specifically for the purpose of discovering Operational Relay Boxes (ORBs) to facilitate covert "Computer Network Exploitation" (CNE).