Classification: TOP SECRET 536 documents
Search documents matching “TOP SECRET” →Each document's classification level, as component values. If a document contains multiple classifications, the highest is used here.
Graphs
By document date (14 years)
By Banner
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Verizon forced to hand over telephone data – full court ruling [pdf]
A top secret FISC order requiring Verizon to produce all telephony metadata — call records, IMSI/IMEI numbers, call duration and routing — for all calls within the US and between the US and abroad, on a daily ongoing basis, to the NSA.
“NSA collecting phone records of millions of Verizon customers daily” - The Guardian ↗ (2013-06-06) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Greenwald, Glenn -
Virtual Private Network Transform Engine Emulator [pdf]
An NSA WikiInfo page describing the Transform Engine Emulator (TEe) — a software tool that replicates at NSA headquarters the same VPN decryption pipeline that runs on deployed field collection systems, allowing encrypted VPN traffic forwarded back to headquarters to be broken using the same key recovery infrastructure, specifically by combining the VULCANDEATHGRIP and POISONNUT components.
-
Virtual Teaming Pays Off SIDtoday [pdf]
This SIDtoday document describes the successful formation of a "virtual team" between NSA Georgia and the UK's Joint Service Signal Unit (JSSU) Digby to enhance surveillance and intelligence collection efforts against Lebanese and Palestinian security forces. This collaboration, initiated in July 2008, allowed for continuous real-time monitoring, with the team providing three reports to national-level policymakers and military commanders, demonstrating the efficiency and effectiveness of cross-national teamwork in intelligence operations.
-
VISIT PRÉCIS - Hr. Dietmar B Director SIGINT Analysis and Production German Federal Intelligence Service (BND) [pdf]
This April 2013 NSA briefing document prepares leadership for a visit by BND Director of SIGINT Analysis and Production Dietmar B[REDACTED] and German intelligence officials for the third Strategic Planning Conference, focusing on expanding NSA-BND cooperation in counterterrorism, cyber defense, Special Source access programs, and providing XKEYSCORE technology to Germany's domestic intelligence service BfV.
People: Fritsche, Klaus-Dieter -
Voice Fax User Group Minutes December 2010 [pdf]
This GCHQ document is a NSA/GCHQ meeting record from December 2010 detailing the deployment of voice analytics, including speech activity detection, speaker identification, and language identification, integrated with tools like Google Earth to map locations of target communications. It outlines ongoing and planned speaker ID operations against specific targets, including militant leaders and foreign officials, demonstrating the operational use of voice recognition for intelligence collection and geolocation.
-
Voice Fax User Group Minutes March 2009 [pdf]
The document is a TOP SECRET GCHQ meeting record from March 2009 detailing updates to B14/MCS voice analytics systems, including new language identification (LID) models for Pashto, Dari, Brahui, and Baluchi languages and a first-pass speaker ID (SID) system for General Kiyani of Pakistan. It also highlights operational successes, such as improved reporting on Iraq's Vice President Adil ’Abd-al-Mahdi, which enhanced GCHQ’s reputation with NSA and reduced unnecessary workload for linguists.
-
Voice Fax Users Group Minutes October 2008 [pdf]
The document is a TOP SECRET GCHQ report on the deployment of a 5-way speaker identification (SID) system targeting high-level individuals in the Afghan narcotics trade. It highlights operational success, including the identification of new phone numbers for a principal target leading to his arrest in Jakarta, and outlines plans to rebuild the system to target the remaining four narcotics barons.
-
Voice/Fax User Group Minutes of September 2008 meeting [pdf]
Page 3 of 7 of the minutes of GCHQ's Voice/Fax User Group (VFUG), September 2008: plans for data-quality testing, a request that linguists flag "Pick Your Own Number" calls in the B3M voice database, and the B14/MCS team's update on the Diariser and on speaker and language identification. The Intercept's PDF shows only the speaker ID section; the rest of the page is in the file (see the archive comment).
-
VOIP in XKEYSCORE [pdf]
A TOP SECRET XKeyscore training presentation from 2009 describing how the system intercepts internet phone calls — automatically matching the call setup information (who is calling whom) with the actual voice data even when they travel through different countries and collection sites, then decoding the audio into playable recordings that analysts can listen to through Windows Media Player.
-
VPN SigDev Basics [pdf]
A TOP SECRET VPN signals development training presentation from NSA's OTTERCREEK team introducing analysts to the six-stage workflow for discovering, assessing and exploiting VPN traffic — covering TOYGRIPPE, XKEYSCORE, DISCOROUTE and other repositories with live interface screenshots showing Iranian-German IPSec traffic and UNAMI (UN Assistance Mission for Iraq) router configurations containing pre-shared keys, including a Cuban VPN pre-shared key recovered in plaintext from a compromised router.
Programs: BLEAKINQUIRY · DISCOROUTE · TOYGRIPPE · MARINA · MASTERSHAKE · NKB · PINWALE · RENOIR · TREASUREMAP · TUNINGFORK · XKEYSCORE · GOLDPOINT · PILBEAM · RADIUS · CREAKSTILE · MAILORDER · ROADBED · DROPBOX · PPF -
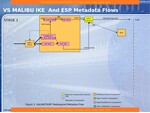
VS MALIBU IKE And ESP Metadata Flows [pdf]
A TOP SECRET four-slide architecture document describing MALIBU — NSA's system for intercepting and decrypting IPSec VPN traffic at the point where it crosses monitored internet cables — showing how intercepted VPN connections are processed, cryptographic keys recovered, traffic decrypted and results delivered to analysts, with separate diagrams for metadata collection, software decryption, full exploitation and survey modes.
-
Web Forum Exploitation using XKEYSCORE [pdf]
A TOP SECRET XKeyscore training presentation from 2009 describing how NSA analysts exploit web forum traffic — revealing that US-hosted web forums under FISA warrants are subject to full-take collection of all traffic, and demonstrating XKeyscore queries for extracting forum posts, private messages, system administrator activity and encrypted communications including traffic using "Mujahideen Secrets 2.0" encryption software.
-
What Does the Death of Usama bin Laden Mean? SIDtoday [pdf]
A 2011 NSA SIDtoday interview with SID's Associate Deputy Director for Counterterrorism assessing the significance of Osama bin Laden's death, revealing that NSA played a central role in identifying his compound and providing force-protection support during the SEAL raid, while also disclosing that bin Laden had been invisible to SIGINT since 1998.
Programs: SCQAWK -
What is HACIENDA? [pdf]
This document details HACIENDA, a large-scale reconnaissance tool used by GCHQ and the Five Eyes alliance to perform automated port scanning and vulnerability mapping across entire nations. It outlines the technical process of identifying and exploiting network infrastructure, specifically for the purpose of discovering Operational Relay Boxes (ORBs) to facilitate covert "Computer Network Exploitation" (CNE).
-
What Your Mother Never Told You About SIGDEV Analysis [pdf]
An NSA presentation covering VPN signals development tradecraft and the prototype DARKSUNRISE VPN analytics tool — describing how analysts use DISCOROUTE, BLACKPEARL, TOYGRIPPE, NKB, RONIN and GNETWORK GNOME to map target VPN networks from router configuration data, with live screenshots of DARKSUNRISE's SHADOWNET interface showing IPSec VPN connections associated with Pakistani, Afghan and other targets collected through MUSCULAR (DS-200B).
Programs: TOYGRIPPE · DISCOROUTE · BLACKPEARL · GNETWORKGNOME · NKB · RONIN · XKEYSCORE · TREASUREMAP · RENOIR · ROYALNET · GNOME · ASDF · DARKSUNRISE · SHADOWNET · WEALTHYCLUSTER · MUSCULAR · CASPORT · CUE · BLACKSAND · DANCINGOASIS · BLACKBEACH · POTLUCK · SSO · DNIPRESENTER · TNS · BLACKPEAL · ROADBED · TROPICNET · SILVERZEPHYR · SITESTORE -
What’s the worst that could happen? [pdf]
This GCHQ document from March 2010 presents a checklist of factors analysts should consider before going ahead with an operation to infiltrate a communications network, by physical or other means.
-
Who's Who in Afghanistan? SIDtoday [pdf]
This SIDtoday document outlines the structure and organization of U.S. and NATO forces in Afghanistan, detailing the roles of various military and intelligence units, including NSA's deployment of Cryptologic Services Groups (CSGs) and Cryptologic Support Teams (CSTs) to support counterterrorism and tactical operations. It also highlights key NSA locations in Afghanistan, such as Kabul, Bagram, and Kandahar, where NSA personnel provide SIGINT support to U.S. and coalition forces, contributing to intelligence fusion, targeting, and operational support.
People: McChrystal, Stanley -
Why TARMAC? [pdf]
A Menwith Hill slide making the case for TARMAC, citing the station's growing FORNSAT mission, its SHAREDVISION work, difficult-signals collection and ASPHALT, a “collect it all” proof-of-concept system.
-
Wireless LAN / CNE Tool Training Course and Evaluation [pdf]
This document is a slide deck introducing a "Close Access" NSA training course to "familiarize, educate, and certify students in the operational usage" of various computer network exploitation tools.
-
WOLFRAMITE Encryption Attack [pdf]
The "WOLFRAMITE Encryption Attack" is a GCHQ strategic annex from March 2011 detailing a joint effort with the NSA to compromise the A5/3 encryption standard. The document outlines a specialized research and development program aimed at scaling up handset exploitation and securing funding—estimated at approximately £4 million—to prototype a functional decryption attack against modern mobile broadband security.