Agency: NSA National Security Agency (US) 557 documents
Search documents matching “NSA” →The agency that WROTE each document.
Graphs
By document date (13 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
PINWALE: Transnational DNI Training [pdf]
This presentation is a classified NSA training guide on PINWALE, a SIGINT database used for the storage, retrieval, and analysis of intercepted digital network intelligence (DNI) communications. It outlines system capabilities, query creation, search tools, and interfaces such as NEXUS, UIS, and AGILITY, explaining how analysts search, retrieve, and analyze both content and metadata — including FISA-partitioned data — within the Five Eyes intelligence framework.
-
POISONNUT [pdf]
NSA Wiki page describing POISONNUT — also known as the VPN Attack Orchestrator (VAO) — a LONGHAUL cryptologic exploitation service for IPSec VPN decryption that has existed in various forms since 2003, serving clients including TURMOIL, WEALTHYCLUSTER and the Transform Engine emulator via ISLANDTRANSPORT with ISLANDHIDEAWAY encryption.
Programs: POISONNUT · TURMOIL · WEALTHYCLUSTER · ISLANDTRANSPORT · ISLANDHIDEAWAY · LONGHAUL · OAKLEY · SCARLETFEVER · PICARESQUE · VALIANTSURF -
PRC Information Warfare & Huawei [pdf]
This NSA intelligence briefing on Huawei analyzes Huawei’s global telecommunications presence and its potential links to the People’s Liberation Army (PLA) and Chinese government intelligence activities. It highlights concerns that Huawei’s international market expansion — including its subcontracted 2008 upgrade of the TAT-14 transatlantic cable carrying U.S. and defense communications — could be exploited by China for signals intelligence (SIGINT) purposes.
People: Chávez, Hugo -
Presentation on the spying program PRISM and ECC's participation [pdf]
This presentation provides statistics on the PRISM surveillance program, detailing intelligence reporting and target tasking across various NSA units and partners from 2011 to 2013. The data reveals that while not the top producer by volume, the European Cryptologic Center (ECC) was the most proportionally reliant on PRISM, which constituted over half of its intelligence output.
-
Presidential Policy Directive/PPD-20 [pdf]
Eighteen-page presidential memo reveals how Barack Obama has ordered intelligence officials to draw up a list of potential overseas targets for US cyber attacks.
-
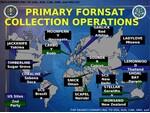
PRIMARY FORNSAT COLLECTION OPERATIONS [pdf]
This document is a TOP SECRET NSA/CSS slide mapping the global locations of primary FORNSAT (foreign satellite) collection operations, showing U.S. and second-party ground stations used to intercept satellite communications worldwide. It illustrates the geographic spread and allied integration of NSA satellite surveillance infrastructure rather than specific technical capabilities.
-
PRISM (US-984XN) expanded its impact [pdf]
FY2012 figures for PRISM: 24,096 end-product reports (up 27 percent), the most-cited SIGAD in first-party reporting at 15.1 percent, 1,477 reports cited in the President's Daily Brief, tasked selectors up 32 percent to 45,406, and taskable e-mail domains expanded from 40 to 22,000.
Programs: PRISM -
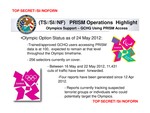
PRISM Olympic Option [pdf]
A May 2012 NSA operational highlight revealing that Britain's GCHQ was given access to the NSA's PRISM surveillance system during the London Olympics, with 100 trained British operatives secretly monitoring 256 targets and intercepting over 11,000 communications in a single week.
-
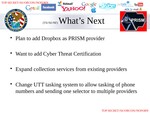
PRISM planning slide (PRISM briefing 1) [pdf]
A PRISM slide headed 'What's Next': plans to add Dropbox as a PRISM provider, add a cyber threat certification, expand collection from existing providers, and change the UTT tasking system to allow phone-number tasking.
-
PRISM tasking slide (PRISM briefing 2) [pdf]
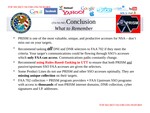
A PRISM slide headed 'Conclusion: What to Remember'. It says PRISM is among the most valuable NSA accesses, recommends tasking all DNI and DNR selectors to FAA 702 where they meet the criteria, and recommends Rules-Based Tasking in UTT so that PRISM and upstream SSO accesses both get the selectors.
-
PRISM/US-984XN Overview [pdf]
A 2013 NSA training presentation revealing that major U.S. tech companies — including Google, Facebook, Apple, Microsoft, and Skype — secretly gave the NSA direct access to their servers, allowing the agency to collect users' emails, chats, photos, and files in real time, with the FBI acting as intermediary.
Programs: PRISM · FAIRVIEW · STORMBREW · BLARNEY · OAKSTAR · UTT · PRINTAURA · PINWALE · NUCLEON · TRAFFICTHIEF · SCISSORS · MARINA · MAINWAY · FALLOUT · CONVEYANCE · REPRISMFISA · SSO“U.S., British intelligence mining data from nine U.S. Internet companies in broad secret program” - The Washington Post ↗ (2013-06-06) · “NSA Prism program taps in to user data of Apple, Google and others” - The Guardian ↗ (2013-06-07) · “L'ampleur de l'espionnage mondial par la NSA” - Le Monde ↗ (2013-10-21) · “NSA files decoded: Edward Snowden's surveillance revelations explained” - The Guardian ↗ (2013-11-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “Dark Mirror: Edward Snowden and the American Surveillance State” - Penguin Press ↗ (2020-05-19) · Gellman, Barton · Poitras, Laura · Greenwald, Glenn · MacAskill, Ewen · Untersinger, Martin · Dance, Gabriel -
PRISM/US-984XN Overview [pdf]
Blurry screengrabs from the "PRISM/US-984XN Overview" slide deck shown on the Fantástico O Globo broadcast. This document contains slides that are not incldued in the slides published by The Washington Post, The Guardian, Le Monde, and others.
-
Private Networks are Important [pdf]
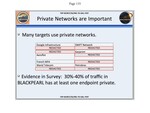
A slide arguing that many targets use private networks — Google's infrastructure, the SWIFT network, Gazprom, Aeroflot, the French foreign ministry, Warid Telecom and Petrobras — with a survey finding that 30 to 40 percent of BLACKPEARL traffic has at least one private endpoint.
Programs: BLACKPEARL -
PROJECT BULLRUN Classification Guide [pdf]
This BULLRUN classification guide outlines the NSA’s highly secretive methods for undermining and exploiting encryption technologies through a combination of cryptanalysis, industry collaboration, covert implants, and network exploitation. It specifies strict classification protocols for capabilities against protocols like TLS/SSL, VPNs, VoIP, and webmail, emphasizing secrecy around sources, methods, and industry partnerships that make commercial encryption systems deliberately vulnerable.
Programs: BULLRUN · APERIODIC · AMBULANT · AUNTIE · PAINTEDEAGLE · PAWLEYS · PITCHFORD · PENDLETON · PICARESQUE · PIEDMONT“Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · “N.S.A. Able to Foil Basic Safeguards of Privacy on Web” - The New York Times ↗ (2013-09-05) · “Revealed: The NSA's Secret Campaign to Crack, Undermine Internet Security” - ProPublica ↗ (2013-09-05) · Ball, James · Borger, Julian · Greenwald, Glenn · Perlroth, Nicole · Larson, Jeff · Shane, Scott -
Project CAMBERDADA [pdf]
NSA presentation on Project CAMBERDADA, a programme that intercepts emails sent to antivirus companies reporting new malware, uses SIGINT collection to monitor antivirus vendor communications, and identifies opportunities to repurpose malware before vendors detect it — listing 23 antivirus companies from around the world as targets, with Kaspersky as the primary focus.
People: Picard, François -
Project SANDSTORM [pdf]
This document shortly describes Project SANDSTORM, part of the Active Sigint Enabling Passive Geolocation (ASEPG) program at Menwith Hill, which uses Wi-Fi signal characterization and satellite-based Overhead capabilities to geolocate high-value targets, with geolocations of under 100 meters expected even for low-power signals in denied areas. It focuses on actively enabling SIGINT to track targets via 802.11 wireless networks.
-
QUANTUM Shooter SBZ Notes [pdf]
An NSA WikiInfo technical reference page describing the QUANTUM shooter infrastructure — covering how compromised internet hosts are configured with STRAITBIZARRE implants using FELONYCROWBAR and Deployed Node Documents, the CHIMNEYPOOL/FRIEZERAMP communications architecture linking shooters to TURBINE via SURPLUSHANGAR and HANGARSURPLUS diodes, and GCHQ's distinct MHS shooter configuration that suppresses callbacks entirely.
Programs: QUANTUM · QUANTUMSHOOTER · FREEFLOW · CHIMNEYPOOL · FELONYCROWBAR · STRAITBIZARRE · SURPLUSHANGAR · HANGARSURPLUS · PASSAGEHILL · FORESTPLACE · FUSSYKEEL · FINGERGNOME · FROZENEARTH · FRIEZERAMP · ISLANDTRANSPORT · GENIE · MIDDLEMAN · WEBSNIPERGATEWAY · WAITAUTO · ZOMBIEARMY · FIPTRIX · TURBINE -
QUANTUMHAND [pdf]
This slide describes QUANTUMHAND, a specialized "Man-on-the-Side" (MOTS) attack used by the NSA's Tailored Access Operations (TAO) to infect targets visiting Facebook. The document outlines an automated process where the NSA's surveillance infrastructure, TURMOIL and TURBINE, detects a target's connection to Facebook and "races" against the legitimate Facebook server to deliver a malicious response first. This "winning the race" allows the NSA to redirect the user to a TAO server that attempts to deploy malware "implants" on the target's computer.
-
QUANTUMINSERT [pdf]
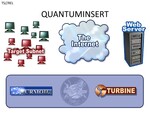
This top-secret NSA presentation provides a step-by-step visual walkthrough of a man-on-the-side (MOTS) attack. This technique allows the NSA to covertly redirect a target's web browser to a malicious server in order to install a malware implant. The diagrams illustrate the interaction between the NSA's global surveillance sensors (TURMOIL) and its automated command-and-control system (TURBINE), demonstrating how the agency exploits the fundamental "race condition" of the internet to compromise a target.
-
QUANTUMTHEORY (2010 SIGINT Development Conference) [pdf]
This 2010 NSA presentation reveals QUANTUMTHEORY, a suite of "man-on-the-side" network attack technologies that enable real-time injection and manipulation of TCP/IP connections through passive surveillance infrastructure. The system encompasses multiple specialized attack techniques including HTML redirection, DNS hijacking, botnet takeover, and database injection, deployed at Five Eyes surveillance sites worldwide.
Programs: QUANTUMTHEORY · TRAFFICTHIEF · TURMOIL · TURBINE · QUANTUM · NINJANIC · ISLANDTRANSPORT · SURPLUSHANGER · DAREDEVIL · STRAIGHTBIZARRE · QUANTUMINSERT · QUANTUMSKY · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMDNS · QUANTUMBOT2 · QUANTUMCOPPER · QUANTUMMUSH · HUFFMUSH · QUANTUMSPIM · QUANTUMSQUEEL · QUANTUMSQUIRREL · INCENSOR · SMOKEYSINK · SARATOGA · QUANTUMDEFENSE · TURBULENCE“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael