Tag: IAD 10 documents
Search documents matching “IAD” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Agenda for the visit of BSI Vice President Andreas Könen to the NSA [pdf]
An NSA visit schedule for Andreas Könen, Vice President of Germany's Federal Office for Information Security (BSI), covering briefings on NSA's Information Assurance Directorate, the FISHBOWL secure smartphone programme and the National Information Assurance Partnership — notable for being releasable to France but not Germany despite the visitor being a senior German government official.
Programs: FISHBOWLPeople: Könen, Andreas -
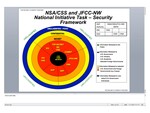
CNO Core Secrets Slide Slices [pdf]
This document outlines the Security Framework for a joint national initiative between the NSA/CSS and JFCC-NW, detailing the highly compartmented structure used to protect cyber and intelligence secrets. It utilizes a concentric security framework diagram to visualize the layers of sensitivity, placing the most critical technical capabilities at the absolute center of the intelligence community's protection.
Programs: SENTRY-EAGLE · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL -
Cooperation between the NSA and BND [pdf]
Comprehensive internal summary of the history and current state of cooperation between the NSA and BND
Programs: RT-RGPeople: Schindler, Gerhard -
Cryptographic Modernization (CryptoMod) Classification Guide 3-9 [pdf]
A partial NSA/CSS classification guide for the Cryptographic Modernisation (CryptoMod) programme — establishing classification levels for information about NSA's transition of US cryptographic products to modern algorithms, Positive Access Control parameters, software signing, and the association of specific algorithms with critical year and life-of-use assessments.
-
Cyber Paper Japan NSA DFS [pdf]
This January 2013 NSA memo from SUSLAJ (Special U.S. Liaison Activity Japan) details Japan’s effort to rapidly launch a SIGINT-enabled cyber defense initiative and a new 100-person “Cybercom” by April 2013. It describes tensions between reformist elements like CIRO (Cabinet Intelligence and Research Office) and more conservative ones like the DFS (Directorate for SIGINT) and MOD Internal Bureau, with struggles in policy, information sharing, and workforce training. The memo shows Japan seeking NSA’s technical help — including at the MALLARD FORNSAT site — while rushing to deliver malware signatures and sign new information-sharing agreements. The NSA viewed Japan as responsive but too focused on short-term results rather than long-term cyber workforce development.
Programs: MALLARD“The Untold Story of Japan's Secret Spy Agency” - The Intercept ↗ (2018-05-19) · “日本の諜報 スクープ 最高機密ファイル” - NHK ↗ (2018-05-19) · Gallagher, Ryan -
DFS and NSA partnership [pdf]
DFS the NSA Sister Organization. This document outlines a high-level visit by Japan’s Directorate for Signals Intelligence (DFS), described as NSA’s “sister organization,” to the NSA/CSS headquarters in early 2013. The purpose was to strengthen their decades-long partnership, focusing on SIGINT-enabled cyber capabilities, training, and mutual understanding of each agency’s role in cyber defense.
People: Alexander, Keith B.“The Untold Story of Japan's Secret Spy Agency” - The Intercept ↗ (2018-05-19) · “日本の諜報 スクープ 最高機密ファイル” - NHK ↗ (2018-05-19) · Gallagher, Ryan -
DGSE and ANSSI Delegation to NSA (April 2013), cyberattacks [pdf]
This Top Secret NSA visit précis details the April 12, 2013 meeting between senior French cyber officials Bernard Barbier (DGSE) and Patrick Pailloux (ANSSI) and NSA leadership to discuss and seek U.S. assistance in attributing May 2012 cyberattacks on the French Presidential network. The document outlines the visit agenda, background tensions over French media accusations of U.S. involvement, and NSA’s plan to emphasize cyber defense cooperation while carefully navigating potential diplomatic sensitivities.
-
Is There a Sustainable Ops Tempo in S2? How Can Analysts Deal with the Flood of Collection? SIDtoday [pdf]
The NSA's Deputy Director for Analysis and Production discusses the unsustainable operational tempo caused by overwhelming data collection volumes, advocating for "Analytic Modernization" that would shift from treating SIGINT as "radioactive" NSA-only material to sharing raw intelligence with other agencies for collaborative exploitation.
Programs: A-SPACE -
Mixing SIGINT and Information Assurance SIDtoday [pdf]
The signals intelligence director gives an update on some major changes to the Information Assurance Directorate. Two organizations within IAD have combined to create the new NSA Threat Operations Center for "detecting unauthorized activity, attacks, intrusions, and other threats to DoD's vital computer networks." A new position was created to liaison between IAD and SID.
The Intercept ↗ (2017-04-24) -
Project CAMBERDADA [pdf]
NSA presentation on Project CAMBERDADA, a programme that intercepts emails sent to antivirus companies reporting new malware, uses SIGINT collection to monitor antivirus vendor communications, and identifies opportunities to repurpose malware before vendors detect it — listing 23 antivirus companies from around the world as targets, with Kaspersky as the primary focus.
People: Picard, François