Introduction to WLAN / 802.11 Active CNE Operations
Open PDFDocument date: 2010-12-15
Pages: 17
Genre: slides
Banner: TOP SECRET//COMINT//NOFORN
Classification: TOP SECRET SI COMINT
Dissemination: NOFORN
This NSA powerpoint introduces computer network exploitation (CNE) criteria and assesment as well as active CNE operations. It also introduces the FOXACID program, which is a program to deliver content based exploits to web browsers.
My notes
TOP SECRET//COMINT//NOFORN
CLOSE ACCESS
Introduction to WLAN / 802.11 Active CNE Operations
December 15-16, 2010
TOP SECRET//COMINT//NOFORN
TOP SECRET//COMINT//NOFORN
CLOSE ACCESS
Classification
The overall classification of this presentation is
TOP SECRET//COMINT//NOFORN
All slides and materiels contained in this presentation should be considered classified TS//SI//NF
(unless otherwise noted)
TOP SECRET//COMINT//NOFORN
TOP SECRET//COMINT//NOFORN
CLOSE ACCESS
Section Overview
- Passive to Active Operations
- WLAN CNE Criteria / Assessment
- Active CNE Operations
- Introduction to FOXACID
TOP SECRET//COMINT//NOFORN
TOP SECRET//COMINT//NOFORN
CLOSE ACCESS
At The End...
You should be able to....
- Identify Criteria for CNE Assessment.
- List the Active CNE Operational Process
- Describe the purpose of FOXACID.
TOP SECRET//COMINT//NOFORN
TOP SECRET//COMINT//NOFORN
CLOSE ACCESS
Passive to Active Operations
- Primary Goal: To enable on-net access to target networks via off-net capabilities.
- Prerequisite: We need to find the network of interest in order to target it.
- Procedure: Conduct passive survey to locate network, then perform active op.
- Solution: Utilize BLINDDATE and the appropriate plug-in solution(s).
TOP SECRET//COMINT//NOFORN
TOP SECRET//COMINT//NOFORN
CLOSE ACCESS
Passive to Active Operations
- Successful operation of BLINDDATE is essential to correct usage of plug-ins.
- Two types of plug-ins exist:
- Analysis Tool Aids
- Active CNE Tools
- We will focus on Active CNE Tools:
- NIGHTSTAND
- HAPPYHOUR
TOP SECRET//COMINT//NOFORN
TOP SECRET//COMINT//NOFORN
CLOSE ACCESS
Active CNE Assessment
- BLINDDATE used as both a survey and vulnerability analysis tool for 802.11 networks.
- Operator needs to know what vulnerabilities, or criteria, to look for in order to utilize the correct Active CNE Tool (if any)
- We will focus primarily on criteria necessary to carry out NIGHTSTAND (NS) and BADDECISION (BDN) operations.
TOP SECRET//COMINT//NOFORN
TOP SECRET//COMINT//NOFORN
CLOSE ACCESS
Major Assessment Criteria
- Clients
- A client is a prerequisite: If no clients are on the target network, there's nothing to do yet.
- Security
- Encryption setting (Open, WEP, WPA, WPA2) dictates which capability can be used (if any).
- Signal Strength
- SNR dictates whether we can perform a successful active CNE operation.
TOP SECRET//COMINT//NOFORN
TOP SECRET//COMINT//NOFORN
CLOSE ACCESS
Active CNE Operations
- What is our end goal?
- Provide on-net access via off-net means.
- How do we do that?
- Redirect the target to the TAO infrastructure.
- How do we do that?
- Inject payload destined for the target client.
TOP SECRET//COMINT//NOFORN
TOP SECRET//COMINT//NOFORN
CLOSE ACCESS
Active CNE Operations
- What does that do exactly?
- Forces the target to covertly contact a FOXACID server.
- What is FOXACID suppose to do?
- Perform vulnerability analysis and exploitation of the target (if possible).
TOP SECRET//COMINT//NOFORN
TOP SECRET//COMINT//NOFORN
CLOSE ACCESS
Introduction to FOXACID
- FOXACID is the cover term for a DNT/ROC project to deliver content based exploits (CBE) to web browsers.
- The greatest vulnerability to your computer: your web browser.
TOP SECRET//COMINT//NOFORN
TOP SECRET//COMINT//NOFORN
CLOSE ACCESS
Introduction to FOXACID
- FOXACID Servers sit on Internet.
- Publicly addressable, DNS resolved.
- Utilizes whitelist for security, filtering.
- Requires specially crafted URL tag to contact FA Servers (FOXACID Tag).
TOP SECRET//COMINT//NOFORN
TOP SECRET//COMINT//NOFORN
CLOSE ACCESS
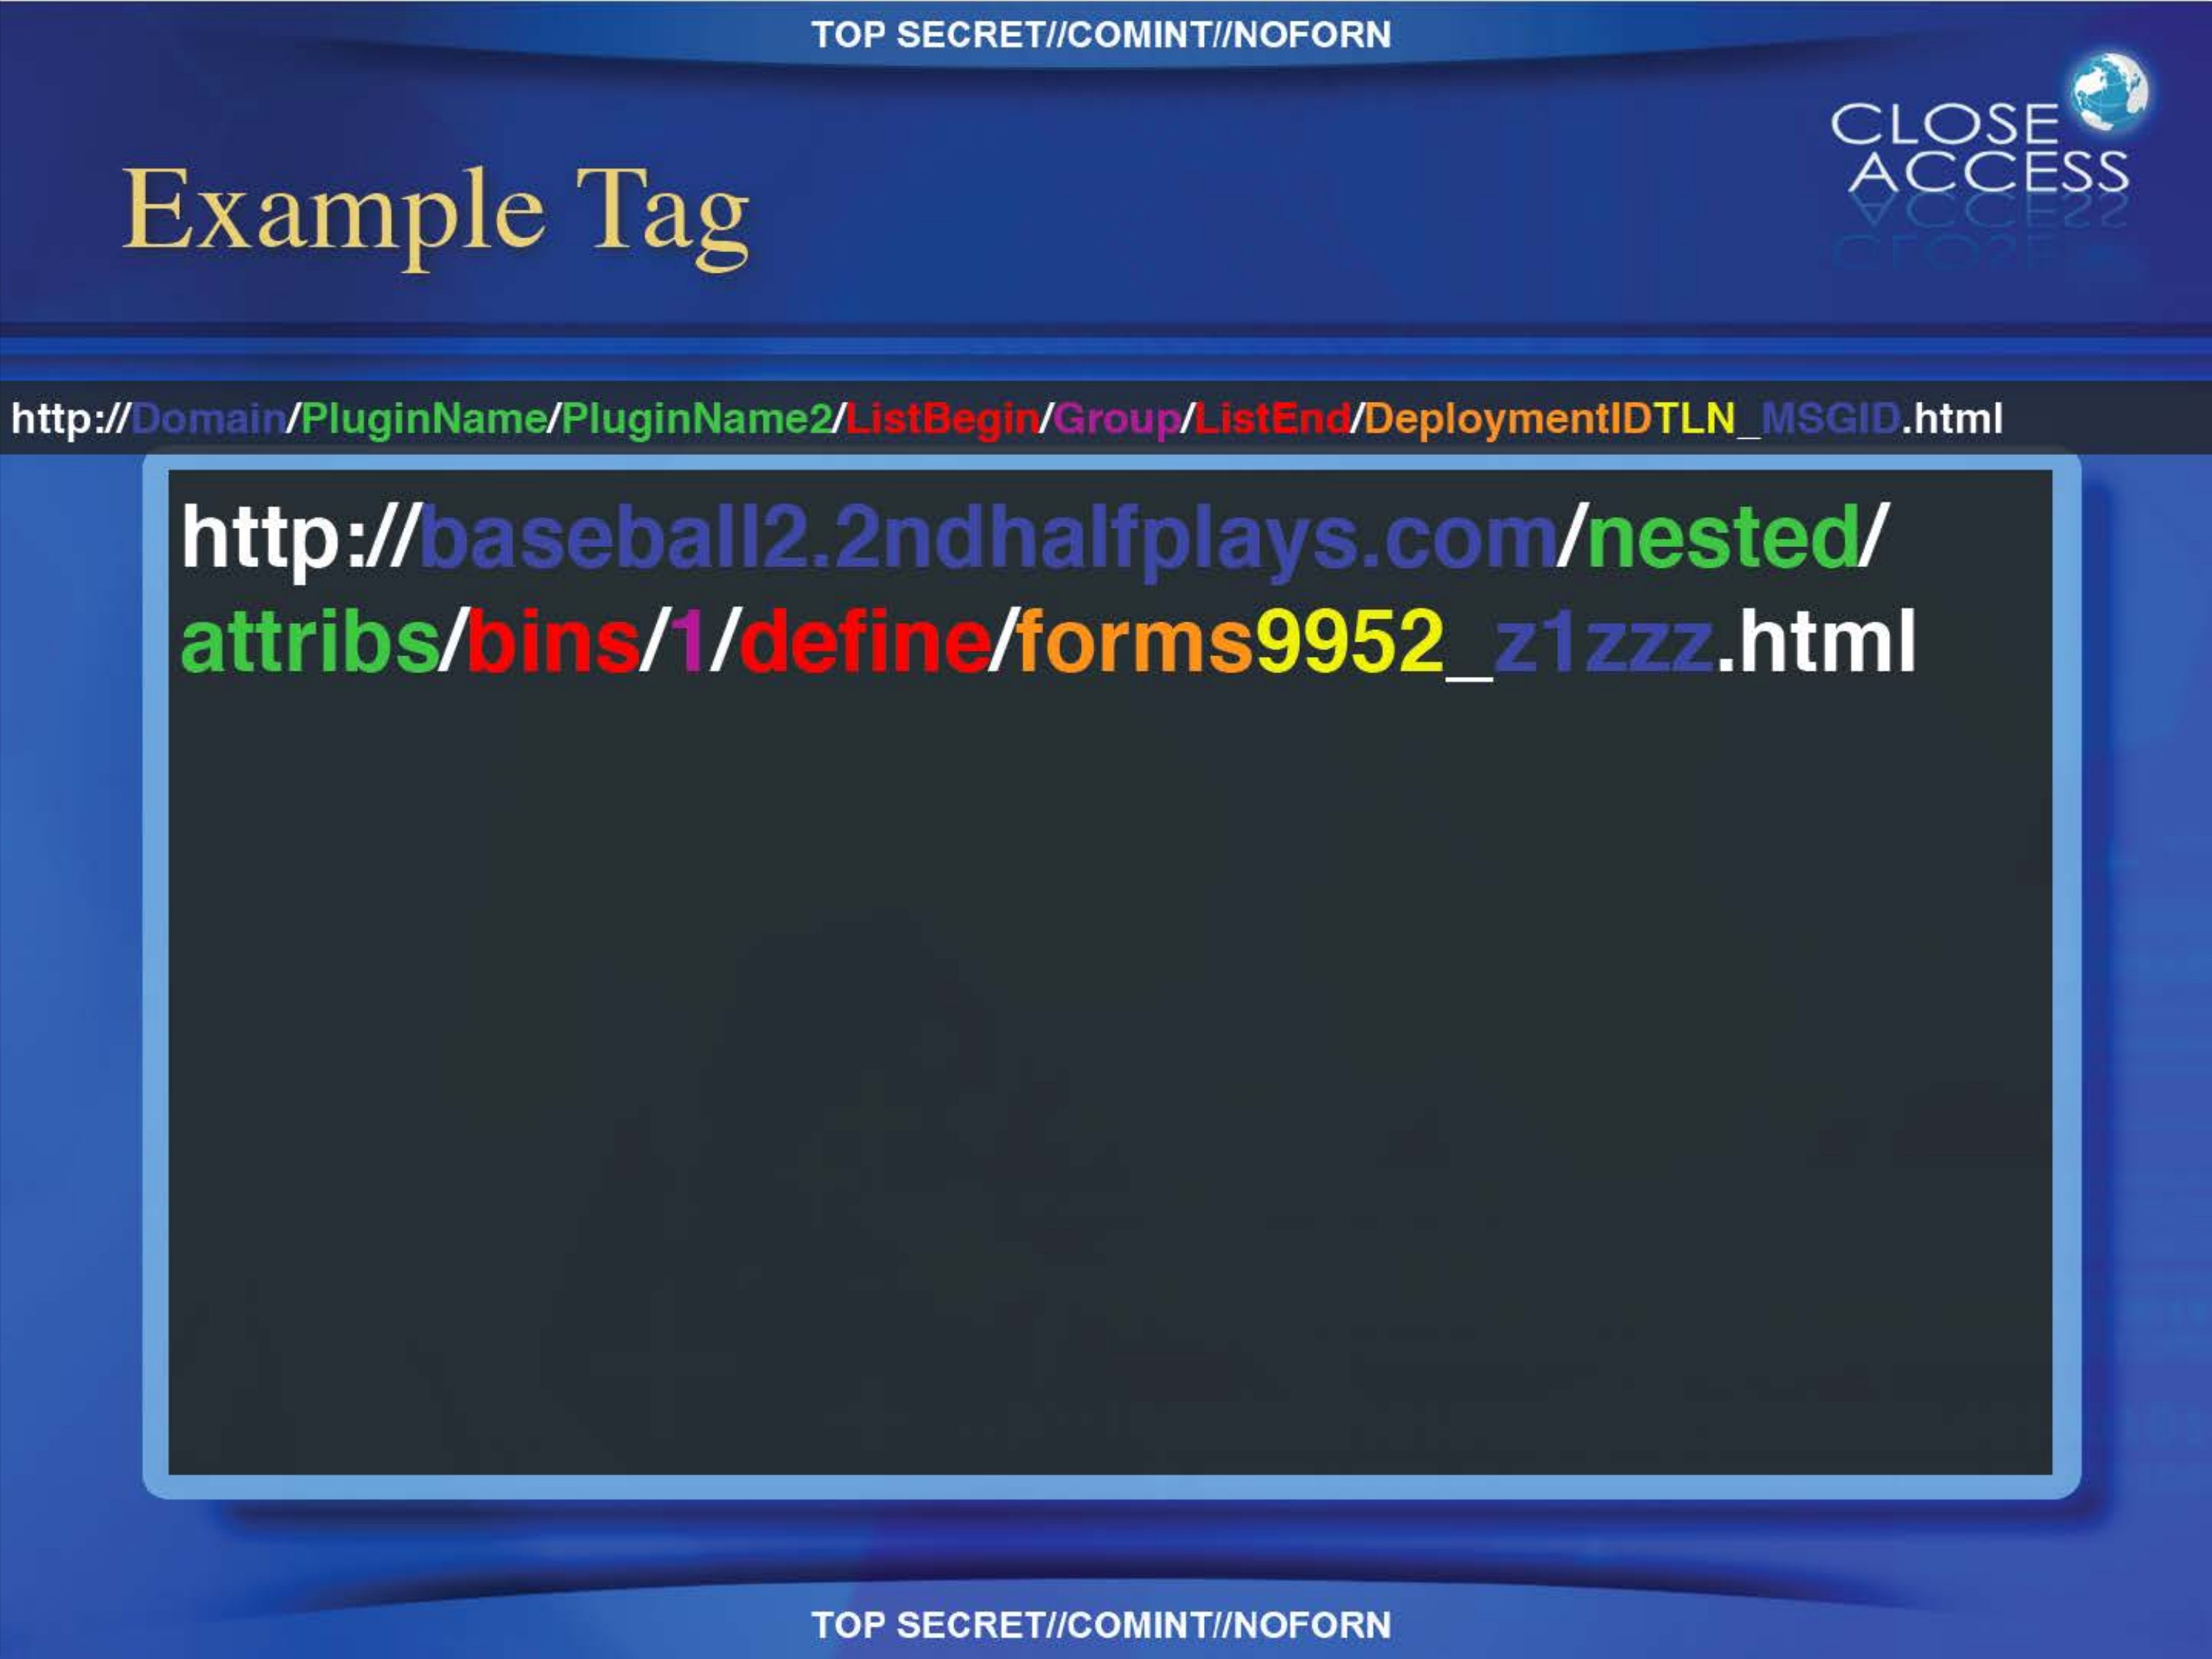
Example Tag
http://Domain/PluginName/PluginName2/ListBegin/Group/ListEnd/DeploymentIDTLN_MSGID.html

http://baseball2.2ndhalfplays.com/nested/attribs/bins/1/define/forms9952_z1zzz.html
TOP SECRET//COMINT//NOFORN
TOP SECRET//COMINT//NOFORN
CLOSE ACCESS
FOXACID Tags
- Designed to look ambiguous.
- Unique for a particular target / operation.
- All fields in the tag denote something special...
TOP SECRET//COMINT//NOFORN
TOP SECRET//COMINT//NOFORN
CLOSE ACCESS
Redirection to FOXACID
- A FOXACID Tag is a special URL pointing to a particular FOXACID Server.
- Contacting the FA Server will (hopefully) result in the contactor being exploited.
- We want the target to be exploited.
- How do we redirect the target to the FOXACID Server without being noticed.
- Use NIGHTSTAND or BADDECISION
TOP SECRET//COMINT//NOFORN
TOP SECRET//COMINT//NOFORN
CLOSE ACCESS
The End.
Questions?
TOP SECRET//COMINT//NOFORN
Published in the Same Report
(7 documents)
-
Wireless LAN / CNE Tool Training Course and Evaluation [pdf]
This document is a slide deck introducing a "Close Access" NSA training course to "familiarize, educate, and certify students in the operational usage" of various computer network exploitation tools.
-
Introduction to BADDECISION [pdf]
This presentation details the use of the NSA program BADDECISION, which is a computer network exploitation tool (CNE) that uses a frame injection technique to redirect the target client to a FOXACID server.
-
Expeditionary Access Operations: NSA’s Close Access Network Exploitation Program [pdf]
The document describes NSA/TAO’s Expeditionary Access Operations (EAO, S3283), a deployable arm that conducts human-enabled Close Access Network Exploitation (CNE) worldwide—using techniques from physical implants and gifted/compromised laptops to wireless injection tools (e.g., BLINDDATE, NITESTAND) and Wi-Fi geolocation—to support tactical customers like SOCOM, DIA, and task forces in Afghanistan, Iraq, and elsewhere. It details organization, tools, operational theaters (Bagram, Kabul, Kandahar, Stuttgart, Texas, etc.), specific operations (IRONPERSISTENCE, CLIMBINGSHIRT), and plans to formalize partnerships with USCYBERCOM and expand expeditionary CANO capabilities.
Programs: NITESTAND · HAPPY HOUR · BADDECISION · MASTERSHAKE · IRONPERSISTENCE · CLIMBINGSHIRT · BLINDDATE -
FOXACID Overall Briefing [pdf]
FOXACID is the NSA's exploit server infrastructure designed to gain "initial access" to target computers by tricking them into visiting malicious websites through spam emails, man-in-the-middle attacks, or split-second packet injection techniques that redirect legitimate web traffic. The document reveals how the agency has evolved from low-success spam operations (less than 1% success rate) to sophisticated "QUANTUM" techniques that achieve up to 80% success rates by exploiting web browsers through services like Yahoo and Facebook, allowing the NSA to compromise any target whose web traffic passes through monitored network chokepoints—with the chilling assessment that "if we can get the target to visit us in some sort of web browser, we can probably own them."
Programs: FOXACID · WILLOWVIXEN · GENUINEDRAFT · SECONDDATE · QUANTUMTHEORY · TURMOIL · TURBINE · WEBSNIPER · QUANTUMINSERT · QUANTUMBISCUIT · QUANTUMDIRK · QUANTUM · VALIDATOR · OLYMPUS · MISTYVEAL · SSO · STRAIGHTBIZARRE · ISLANDTRANSPORT -
FOXACID SOP for Operational Management of FOXACID Infrastructure (Draft) [pdf]
This document is an NSA standard operating procedure (SOP) manual detailing how to manage and operate the FOXACID system, which delivers malware to targets through tools like SECONDDATE and BADDECISION. It provides technical instructions for tracking, deploying, and maintaining covert web-based infections used in global cyber operations.
Programs: FOXACID · FOXSEARCH · WAITAUTO · RAISEBED · FORRESTPLACE · FOXHelp · PUZZLECUBE · YACHTSHOP · SECONDDATE · MAGIC SQUIRREL · MAGICBEAN · FINKCOAT · FRUGALSHOT · QUANTUM · FERRETCANNON · BEACHHEAD · OLYMPUS · UNITERAKE · DIRESCALLOP · DEEPFREEZE · FINKDIFFERENT · DISABLEVALOR · VALIDATOR · MISTYVEAL · UNITEDRAKE · PEDDLE CHEAP · PKTWENCH · FORESTPLACE · FOXCONTACT · EASYHOOKUP · DEMENTIAWHEEL · CASTLECREEK · ROCHELP · QUANTUMINSERT · FABULOUSFABLE · WATCHER · FROZENGAZE · FABFAB · DARKFIRE · CRYPTICSENTINEL · DARKHELMET · PSP · WILLOWVIXEN -
SSO news excerpts [pdf]
These SSO news exceprts describe the successful deployment of QUANTUMTHEORY and QUANTUMINSERT capabilities by the NSA’s Tailored Access Operations (TAO) team, in collaboration with Special Source Operations (SSO), to exploit high-value targets, including key figures in the Haqqani network. Using a combination of signal case notations and real-time exploitation via QUANTUMHAND, TAO was able to implant malicious software on the target's computer, enabling further intelligence collection and exploitation.
Programs: QUANTUMTHEORY · QUANTUM · QUANTUMINSERT · FOXACID · DANCINGOASIS · FOXCONTACT · VALIDATOR · SARATOGA · TURMOIL · QUANTUMHAND · SSOPeople: Haqqani, Badruddin -
SIGINT Development Support II Program Management Review, 24 April 2013 (select slides) [pdf]
These selected slides briefly celebrate two NSA “success stories”: penetrating Pakistan’s Green Line infrastructure with SECONDDATE-enabled implants, and seizing country-wide leverage over Lebanon’s internet backbone through Ogero to siphon off Hezbollah-related data. It shows how U.S. intelligence treated supposedly inaccessible national networks as targets to be shaped, exploited, and folded into its global surveillance machine. See extra slide in "NSA Supply Chain Attack From PMR 4-24-13" https://theintercept.com/document/2019/01/24/nsa-supply-chain-attack-from-pmr-4-24-13/
Programs: MONSTERMIND · CHELSEABLUE · SECONDDATE · QUANTUM · REXKWONDO · STORMBREW · XKEYSCORE · MARINA · HAMMERCORE · HAMREX · CADENCE · HAMMERSTEIN · SSO


Related Documents
-
Introduction to BADDECISION [pdf]
This presentation details the use of the NSA program BADDECISION, which is a computer network exploitation tool (CNE) that uses a frame injection technique to redirect the target client to a FOXACID server.
-
Wireless LAN / CNE Tool Training Course and Evaluation [pdf]
This document is a slide deck introducing a "Close Access" NSA training course to "familiarize, educate, and certify students in the operational usage" of various computer network exploitation tools.
-
Expeditionary Access Operations: NSA’s Close Access Network Exploitation Program [pdf]
The document describes NSA/TAO’s Expeditionary Access Operations (EAO, S3283), a deployable arm that conducts human-enabled Close Access Network Exploitation (CNE) worldwide—using techniques from physical implants and gifted/compromised laptops to wireless injection tools (e.g., BLINDDATE, NITESTAND) and Wi-Fi geolocation—to support tactical customers like SOCOM, DIA, and task forces in Afghanistan, Iraq, and elsewhere. It details organization, tools, operational theaters (Bagram, Kabul, Kandahar, Stuttgart, Texas, etc.), specific operations (IRONPERSISTENCE, CLIMBINGSHIRT), and plans to formalize partnerships with USCYBERCOM and expand expeditionary CANO capabilities.
Programs: NITESTAND · HAPPY HOUR · BADDECISION · MASTERSHAKE · IRONPERSISTENCE · CLIMBINGSHIRT · BLINDDATE -
FOXACID SOP for Operational Management of FOXACID Infrastructure (Draft) [pdf]
This document is an NSA standard operating procedure (SOP) manual detailing how to manage and operate the FOXACID system, which delivers malware to targets through tools like SECONDDATE and BADDECISION. It provides technical instructions for tracking, deploying, and maintaining covert web-based infections used in global cyber operations.
Programs: FOXACID · FOXSEARCH · WAITAUTO · RAISEBED · FORRESTPLACE · FOXHelp · PUZZLECUBE · YACHTSHOP · SECONDDATE · MAGIC SQUIRREL · MAGICBEAN · FINKCOAT · FRUGALSHOT · QUANTUM · FERRETCANNON · BEACHHEAD · OLYMPUS · UNITERAKE · DIRESCALLOP · DEEPFREEZE · FINKDIFFERENT · DISABLEVALOR · VALIDATOR · MISTYVEAL · UNITEDRAKE · PEDDLE CHEAP · PKTWENCH · FORESTPLACE · FOXCONTACT · EASYHOOKUP · DEMENTIAWHEEL · CASTLECREEK · ROCHELP · QUANTUMINSERT · FABULOUSFABLE · WATCHER · FROZENGAZE · FABFAB · DARKFIRE · CRYPTICSENTINEL · DARKHELMET · PSP · WILLOWVIXEN -
CNE Analysis in XKEYSCORE [pdf]
This document is an NSA training presentation from October 2009 demonstrating how XKEYSCORE integrates with Computer Network Exploitation (CNE) operations, allowing analysts to search and analyze data extracted from compromised computers including keystrokes, browser history, registry files, documents, emails, and directory structures collected through implants like UNITEDRAKE and OLYMPUS.
Programs: XKEYSCORE · OLYMPUS · UNITEDRAKE · PINWALE · TUNINGFORK · TURBOCHASER · MARINA · JOLLYROGER · TREASUREMAP · TURBINE · PRESSUREWAVE · MAD · TUCKER · EXPANDINGPULLY · UNIX · SEARCHLIGHT · KEYLOGGER · PILBEAM · FOXACID · WAYTIDE · SHADOWQUEST · SEAGULLFARO · DARKHELMET · LUTEUSICARUS · FOGGYBOTTOM · GREENCHAOS · RADIUS · NKB · VALIDATOR
