Tag: vulnerability analysis 9 documents
Search documents matching “vulnerability analysis” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Black Budget: Cryptanalysis & Exploitation Services – Analysis of Target Systems [pdf]
This document is a budget justification for the NSA's Cryptanalysis & Exploitation Services project, which develops capabilities to defeat commercial encryption systems, exploit emerging communications technologies, and conduct vulnerability analysis against both foreign and domestic security products.
“The CIA Campaign to Steal Apple's Secrets” - The Intercept ↗ (2015-03-10) · Scahill, Jeremy · Begley, Josh -
Cyber Network Defence R&D Activities [pdf]
A September 2010 CSEC briefing to the Five Eyes 5IARC conference on cyber defence R&D, giving the full PONY EXPRESS email attachment scanning architecture and the PHOTONIC PRISM sensor, with speaker notes in which the presenter concedes CSEC does little research of its own.
Marking: SECRETPrograms: PHOTONICPRISM · PONYEXPRESS · SLIPSTREAM · POPQUIZ · 8BALL · SNORT · POPEYESEAR · FLOWPONY · SMTPPONY · MAILPONY · METAPONY · SCANPONY · AGGPONY · SYNCPONY · POOLTABLE · POOLCUE · CORNERPOCKET · TONTO · MULASSES · MULVAL · ASSETRANK · JNDMS · ARMOUR · SWAD · MINISSL · SSLFUZZER · N3C · N3 · CTEC · DCITS · 5IARC -
Full-Spectrum Cyber Effects [pdf]
The leaked 2012 GCHQ JTRIG “Full-Spectrum Cyber Effects” presentation outlines the UK’s offensive cyber capabilities, detailing strategies to destroy, deny, degrade, disrupt, deceive, and influence targets across digital and physical domains. It describes a wide range of operations—from network attacks, spoofing, and psychological operations on social media to hotel surveillance (Royal Concierge), mobile tracking, and advanced vulnerability exploitation—demonstrating how GCHQ integrates cyber operations, intelligence, and information warfare on a global scale.
Programs: JTRIG · SALAMANCA · RADIUS · ROYAL CONCIERGE · BLACKHOLE · GUILTY SPARK · MIDDLESEX GREEN · PPF · HOTWIRE -
Introduction to BADDECISION [pdf]
This presentation details the use of the NSA program BADDECISION, which is a computer network exploitation tool (CNE) that uses a frame injection technique to redirect the target client to a FOXACID server.
-
Introduction to WLAN / 802.11 Active CNE Operations [pdf]
This NSA powerpoint introduces computer network exploitation (CNE) criteria and assesment as well as active CNE operations. It also introduces the FOXACID program, which is a program to deliver content based exploits to web browsers.
-
OP HIGHLAND FLING - Event Log [pdf]
A TOP SECRET operational event log from GCHQ's GCWiki documenting a January 2011 operation targeting Gemalto employees in France, Poland and elsewhere, using MUTANT BROTH cookie analysis, Facebook credentials, LinkedIn profiles and Computer Network Exploitation to identify and implant targets as part of the operation to steal SIM card encryption keys.
-
TECA Product Centre — Wiki [pdf]
The TECA Product Centre is a GCHQ unit, within the Technical Enabling Covert Access group (TEA), whose mission is to develop and exploit specialist technologies and physical access methods to gain intelligence or SIGINT access where conventional methods fail. It works closely with SIS (MI6) on technical operations and deployment, offering bespoke managed services rather than direct products.
-
Types of IAT - Advanced Open Source Multi-hop [pdf]
This top-secret NSA/GCHQ document provides a detailed technical overview of the Tor network, including how it works, its strengths as the “king of high secure, low-latency Internet anonymity,” methods for identifying Tor traffic, censorship-driven protocol obfuscation, and ongoing intelligence efforts to analyze, fingerprint, and exploit Tor through passive SIGINT and active research, including collaboration between US and UK agencies.
People: Appelbaum, Jacob -
What is HACIENDA? [pdf]
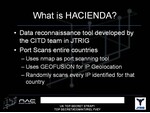
This document details HACIENDA, a large-scale reconnaissance tool used by GCHQ and the Five Eyes alliance to perform automated port scanning and vulnerability mapping across entire nations. It outlines the technical process of identifying and exploiting network infrastructure, specifically for the purpose of discovering Operational Relay Boxes (ORBs) to facilitate covert "Computer Network Exploitation" (CNE).