Tag: data exfiltration 27 documents
Search documents matching “data exfiltration” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Access Breakdown [pdf]
This GCHQ document provides a technical breakdown of surveillance access points showing 11 different interception sites (with codenames like DONNINGTON, LATUS, SCEPTRE) accessing various undersea cables including Flag, Apollo North/South, BT, Cable & Wireless (C&W), SMW-3, Solas, and Verizon, totaling 541 10-gigabit connections representing 5,410 gigabits of surveillance capacity across the network.
Programs: DONNINGTON · LATUS · SCEPTRE · PRESCOTT · GIBUS · KIRKISTOWN · MONDELLO · LINNELL · CATEGORY · KNAPWEED · ELAPSE · BROKER“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
Access: Vision 2013 [pdf]
This July 2010 GCHQ strategic document outlines the agency's vision for 2013 to create "the world's biggest SIGINT engine" with access to 800 10-gigabit connections (up from existing capacity), expanding overseas operations to 60% while reducing UK-based to 40%, and developing new capabilities including computer network exploitation (CNE), exfiltration, beaconry, geolocation, and collection of "Internet Pocket Litter" like cookies and browsing data. The strategy emphasizes "scale and pace," "balance," and "agility" while claiming to operate within legal frameworks of "necessity, proportionality and authorisation," and highlights partnerships with second and third parties to access "intractable and hard targets."
Marking: SECRET -
Analytic Challenges from Active-Passive Integration [pdf]
This NSA presentation examines metadata attribution challenges arising when active TAO implants exfiltrate traffic through passive TURMOIL collection infrastructure, creating conflicts where intercepted data carries dual classification markings, case notations, and legal authorities from both collection systems. The briefing highlights how existing databases and analytic tools were not designed to handle traffic with two simultaneous sets of metadata parameters, requiring enterprise-wide solutions to consistently attribute and track actively-shaped intelligence collection.
Programs: BRAVENICKEL · HAMMERMILL · APEX · MARINA · TURMOIL · PRESSUREWAVE · METROTUBE · TOYGRIPPE · HAMMERSTEIN · HAMMERSTONE · METAWAVE · TURBULENCE · SSO -
Analytic Challenges from Active-Passive Integration [pdf]
This NSA briefing addresses the technical and administrative friction caused by "shaping" operations. Shaping occurs when an active malware implant, typically situated on network infrastructure like a router, copies specific data streams and redirects them past a passive surveillance sensor such as TURMOIL. While this ensures the capture of data that might otherwise be missed, it creates a "double metadata" conflict where a single piece of intelligence carries two competing sets of identifiers: one from the active Tailored Access Operations (TAO) implant and another from the passive collection site. The document tasks analysts with finding a way to reconcile these source notations to ensure the data remains searchable and legally compliant within legacy databases.
Programs: BRAVENICKEL · HAMMERMILL · APEX · TURMOIL · HAMMERSTONE · PRESSUREWAVE · METROTUBE · TOYGRIPPE · TURBULENCE · METAWAVE · MARINA · SSO · CONVEYANCE · NUCLEON · FASCIA · HAMMERCHANT -
AZTECTOMB32 DMW Install and ESH Package [pdf]
This document is a top-secret NSA internal project log detailing restrictions on installing new implants on machines running Kaspersky 2010+ due to the software’s cloud functionality, which prevents safe deployment of NSA malware. It records the suspension and eventual closure of a project (AZTECTOMB32/DEMENTIAWHEEL) that would have targeted such systems.
-
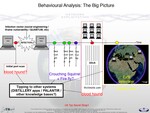
Behavioural Analysis: The Big Picture (Palantir could be used as part of a CNE) [pdf]
This diagram from GCHQ outlines the lifecycle of a CNE and identifies where Palantir fits into the intelligence workflow. The slide, titled "Behavioural Analysis: The Big Picture," illustrates a timeline of network exploitation from the initial infection of a target host to the eventual exfiltration of data. Crucially, it positions Palantir as a key "knowledge base" used for "Tipping to other systems." This indicates that Palantir’s software was used to aggregate data from successful hacks, allowing analysts to visualize connections and pivot (or "tip") that information toward further surveillance or offensive operations.
-
BYZANTINE HADES: An Evolution of Collection [pdf]
A classified NSA SIGINT briefing from 2010 describes “BYZANTINE HADES,” a collection of Chinese computer network exploitation activities, with a focus on the BYZANTINE CANDOR actor set and U.S. efforts to analyze, attribute, and counter those intrusions. The document details targeting patterns, technical tradecraft, and a TAO-led counterintelligence operation that successfully penetrated the attackers’ infrastructure and personal systems.
Programs: BYZANTINEHADES · BYZANTINECANDOR · BYZANTINERAPTOR · BYZANTINEANCHOR · BISHOPKNIGHT · BYZANTINEVIKING · MAVERICKCHURCH · BISHOP · BYZANTINETRACE · DIESELRATTLE · BYZANTINEFOOTHOLD · BYZANTINEPRAIRIE · SEEDSPHERE · CARBONPEPTIDE · TITANRAIN · PINWALE · XKEYSCORE · CROSSBONES · TUNINGFORK · ARROWECLIPSE · CUTEBOY · POPROCKS · BYZANTINE -
Cable Master List [pdf]
This GCHQ document is a comprehensive master list of undersea fiber optic cables tracked for surveillance purposes, including both cables with UK landing points and international cables without UK connections, detailing technical specifications, ownership, capacity data, and code names for telecommunications partner companies that provided the intelligence agency with surveillance access.
Programs: PINNAGE · PFENNINGALPHA · NIGELLA · REMEDY · HIASCO · GERONTIC · SCEPTRE · PRESCOTT · KIRKISTOWN · LINNELL · CATEGORY · DACRON · KNAPWEED · ELAPSE · VITREOUS · LITTLE · STREETCAR · GIBBUS · VISAGE · LATUS · NUMDAH“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
Cables we do not currently have good access [pdf]
This GCHQ document, titled "Cables we do not currently have good access," lists numerous undersea fiber-optic cables along with their active data capacity ("Lit Capacity"), indicating the substantial portion of global telecommunications infrastructure where the agency lacks adequate surveillance access, in contrast to other internal reports detailing cables it successfully monitors.
“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
Chinese Exfiltrate Sensitive Military Technology [pdf]
This TOP SECRET NSA SIGINT development briefing describes large-scale Chinese cyber espionage that exfiltrated sensitive U.S. military technologies and inflicted extensive operational, financial, and strategic damage on Department of Defense systems. The document emphasizes both the scale of losses and the role of SIGINT in detecting, understanding, and mitigating adversary malware.
Programs: BYZANTINEHADES -
CNE Analysis in XKEYSCORE [pdf]
This document is an NSA training presentation from October 2009 demonstrating how XKEYSCORE integrates with Computer Network Exploitation (CNE) operations, allowing analysts to search and analyze data extracted from compromised computers including keystrokes, browser history, registry files, documents, emails, and directory structures collected through implants like UNITEDRAKE and OLYMPUS.
Programs: XKEYSCORE · OLYMPUS · UNITEDRAKE · PINWALE · TUNINGFORK · TURBOCHASER · MARINA · JOLLYROGER · TREASUREMAP · TURBINE · PRESSUREWAVE · MAD · TUCKER · EXPANDINGPULLY · UNIX · SEARCHLIGHT · KEYLOGGER · PILBEAM · FOXACID · WAYTIDE · SHADOWQUEST · SEAGULLFARO · DARKHELMET · LUTEUSICARUS · FOGGYBOTTOM · GREENCHAOS · RADIUS · NKB · VALIDATOR -
DEFIANTWARRIOR and the NSA's Use of Bots [pdf]
This TOP SECRET NSA presentation from 2010 documents the DEFIANTWARRIOR effort to identify, seize, and operate botnets using SIGINT-enabled infrastructure, detailing both early failures and subsequent operational successes. The document reveals how bot herding was integrated into broader offensive cyber and intelligence collection strategies across the Five Eyes.
Programs: DEFIANTWARRIOR · OLYMPUS · UNITEDRAKE · TURBULENCE · QUANTUMBOT · TURMOIL · TURBINE · SNIPERS · XKEYSCORE · INCENSER · STELLABLUE · SMOKYSINK · STOVEPIPES · ISLANDTRANSPORT · FESTIVEWRAPPER · FREEFLOW · PRESSUREWAVE · HANGARSURPLUS · SURPLUSHANGER · WAITAUTO · DEEPFRIEDPIG · SEAGULLFARO · COLOSSUS · STORMPIG · YELLPIG · PASTEPIG · SHOUTPIG · ZORPIG · MAILORDER · TREASUREMAP · MARINA · WARNVOLCANO · STRAITBIZARRE · BOTINSTANCES · PUZZLECUBE · SEEKER · SURPLUSHANGAR -
FASHIONCLEFT - Interface Control Document (15 June 2009) [pdf]
This 2009 NSA Interface Control Document provides comprehensive technical specifications for FASHIONCLEFT, the protocol that acts as a covert shipping system enabling TAO malware implants to send stolen network data back to NSA collection servers with minimal computer processing requirements—using multiple encryption layers (RSA-1024 and RC6-128) to disguise the traffic as it travels across the internet while allowing NSA's Common Data Receptor to reassemble and authenticate the original intercepted packets. The document details how implants make modified copies of captured network traffic (changing destination addresses to point toward NSA instead of legitimate recipients), apply various levels of encryption or scrambling ("munging") depending on how powerful the infected computer is, attach metadata instructions explaining how to reconstruct the original packets, and use pattern-matching algorithms to ensure NSA systems can identify which stolen packets belong to which collection operation.
Programs: FASHIONCLEFT · FLAXENPRECEPT · SHELLGREY · SURPASSPIN · SEAGULLFARO · ROOTKNOT · FIGBUILD · OPTICPINCH · VINYLSEAT · OLYMPUS · UNITEDRAKE · HOGTECH · SWEEPFORWARD · CONVEY · PINWALE · TREBLECLEF · FOGYNULL · FUNNELAPS · FLASHHANDLE -
Fourth Party Opportunities [pdf]
This presentation document explains how NSA identifies, prioritizes, and exploits “fourth party” opportunities by passively or actively leveraging foreign computer network exploitation operations, including victim stealing and tool repurposing, to collect intelligence without initiating original intrusions.
Programs: VOYEUR · UIS · PINWALE · YNKE · TUNINGFORK · DIRTSHED · SEEKER · CLOUD · ABR · SILVERBOLT · DEADSEA · XKEYSCORE · BYZANTINERAPTOR · HAWALA · ZEBEDEE · DATAFLURRY · ECLECTICPLOT · HAPPYFOOT · BLUESMOKE · CROSSBONES2 · CYBERQUEST · VICDB · PLAIDDIANA · TRANSGRESSION -
Industrial-Scale Exploitation [pdf]
This top-secret NSA document details the operational philosophy behind the TURBINE system's transition to "industrial-scale exploitation." By integrating with both active and passive sensors, TURBINE automates the delivery of malware and the maintenance of network implants, specifically targeting routers and server-side code execution.
-
Moving Data Through Disconnected Networks - Delay-Tolerant Networking and the IC [pdf]
This June 2012 NSA Laboratory for Telecommunications Sciences presentation details Delay-Tolerant Networking (DTN) applications for surveillance operations, including covert communications in denied areas, data exfiltration from isolated networks, unwitting data mules, and integration with TAO's CHIMNEYPOOL implant framework. The document reveals R4 development of FUZZYLINT, an ultra-lightweight DTN implementation designed to enable multi-hop exfiltration from implants without requiring direct physical access.
People: Vahdat, Amin · Becker, David · Juang, Philo · Oki, Hidekazu · Wang, Yong · Martonosi, Margaret · Peh, Li-Shiuan · Rubenstein, Daniel · Grossglauser, Matthias · Tse, David N. C. · Fall, Kevin · Shah, Rahul C. · Roy, Sumit · Jain, Sushant · Brunette, Waylon · Lindgren, Anders · Doria, Avri · Schelen, Olov · Small, Tara · Haas, Zygmunt J. · Zhao, Wenrui · Ammar, Mostafa · Zegura, Ellen · Ginzboorg, Philip · Kärkkäinen, Teemu · Nagata, Akira · Lenders, Vincent · Legendre, Franck · May, Martin · Karlsson, Gunnar · Du, Bowei · Demmer, Michael · Brewer, Eric · Ott, Jörg · Pitkänen, Mikko Juhani · Han, Bo · Hui, Pan -
Network Shaping 101 [pdf]
An NSA top-secret training presentation that uses Yemen as a case study to explain how to "shape" a nation's Internet traffic by exploiting Autonomous Systems, upstream providers, BGP routing, and physical link topology to redirect or collect communications. The slide deck walks through practical router/IP/link details, passive SIGINT collection points and limitations, and warns that many assumptions are fabricated for the lesson and that real-world capabilities and link behavior can vary.
-
NSA ANT Catalog [pdf]
The NSA ANT catalog is a leaked confidential collection of sophisticated surveillance and hacking tools developed by the agency’s Tailored Access Operations unit (TAO), detailing hardware and software implants capable of covertly infiltrating computers, networks, and mobile devices. It revealed the NSA’s ability to conduct remote surveillance, implant malware, and maintain persistent access to targeted systems without users’ knowledge.
Programs: IRONCHEF · PROTOSS · STRONGMITE · GECKO II · STRAITBIZARRE · WAGONBED · UNITEDRAKE · DEITYBOUNCE · ARKSTREAM · TUNING FORK · GODSURGE · FLUXBABBITT · JETPLOW · BANANAGLEE · HALLUXWATER · TURBOPANDA · FEEDTROUGH · ZESTYLEAK · GOURMETTROUGH · SOUFFLETROUGH · HEADWATER · HAMMERMILL · HIT · SIERRAMONTANA · VALIDATOR · SCHOOLMONTANA · STUCCOMONTANA · CTX4000 · PHOTOANGLO · LOUDAUTO · ANGRYNEIGHBOR · NIGHTWATCHER · VIEWPLATE · LFS-2 · TAWDRYYARD · RAGEMASTER · CROSSBEAM · CHIMNEYPOOL · ROCKYKNOB · CANDYGRAM · CYCLONE Hx9 · TYPHON · EBSR · LANDSHARK · ENTOURAGE · HOLLOWPOINT · GALAXY · GENESIS · NEBULA · TYPHON HX · WATERWITCH · NIGHTSTAND · SPARROW II · BLINDDATE · DROPOUTJEEP · ARTEMIS · DROPMIRE · STRAITBIZZARE · FREEFLOW · TURBULENCE · GOPHERSET · MONKEYCALENDAR · TOTECHASER · TOTEGHOSTLY · PICASSO · TOTEGHOSTLY 2.0 · FRIEZERAMP · GENIE · VAGRANT · GOTHAM · SURLYSPAWN · GINSU · BULLDOZER · KONGUR · OMNIGAT · IRATEMONK · SERUM · SLICKERVICAR · RETURNSPRING · WISTFULTOLL · JIMSQ · SEAGULLFARO · SWAP · SNEAKERNET · TWISTEDKILT · HOWLERMONKEY · SUTURESAILOR · YELLOWPIN · CONJECTURE · SPECULATION · JUNIORMINT · MAESTRO · MAESTRO-II · SOMBERKNAVE · OLYMPUS · TRINITY · COTTONMOUTH-I · COTTONMOUTH-II · TURBINE · COTTONMOUTH-III · FIREWALK · DANDERSPRITZ -
NSA Technology Directorate Analysis of Converged Data [pdf]
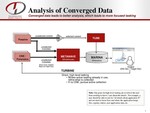
This document outlines the strategic integration of passive and active signals intelligence (SIGINT) to create a more efficient surveillance loop. The document centers on TURBINE, an intelligent command-and-control system designed to manage a massive network of malware implants (Computer Network Exploitation or CNE). The primary goal is to automate the extraction of data from targeted machines, effectively "converging" traditional passive collection with active hacking to refine intelligence tasking.
-
Sentry Eagle Brief Sheet [pdf]
A classified NSA/JFCC-NW briefing document formally inducting cleared personnel into Sentry Eagle — the agency's most sensitive umbrella program protecting core secrets about its cyber operations — and enumerating, tier by tier, what the NSA conceals about its covert industry partnerships, encryption sabotage, network hacking, computer network defense, and human intelligence relationships.
Programs: SENTRYEAGLE · SPARECHANGE · WHIPGENIE · AUNTIE · AMBULANT · OPALESCE · REVELRY · REFRACTOR · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL · BLUESASH · TAREX