Tag: data exfiltration 27 documents
Search documents matching “data exfiltration” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Shaping Diagram [pdf]
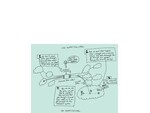
This hand-drawn diagram detail an NSA methodology for intercepting and redirecting internet traffic. The approach involves manipulating data flows through a controlled fiber cable, leveraging Computer Network Exploitation (CNE) to capture and replicate target communications for SIGINT processing, all framed in a tongue-in-cheek, yet highly classified, presentation style.
-
SIGINT Development Support II Program Management Review, 24 April 2013 (select slides) [pdf]
These selected slides briefly celebrate two NSA “success stories”: penetrating Pakistan’s Green Line infrastructure with SECONDDATE-enabled implants, and seizing country-wide leverage over Lebanon’s internet backbone through Ogero to siphon off Hezbollah-related data. It shows how U.S. intelligence treated supposedly inaccessible national networks as targets to be shaped, exploited, and folded into its global surveillance machine. See extra slide in "NSA Supply Chain Attack From PMR 4-24-13" https://theintercept.com/document/2019/01/24/nsa-supply-chain-attack-from-pmr-4-24-13/
Programs: MONSTERMIND · CHELSEABLUE · SECONDDATE · QUANTUM · REXKWONDO · STORMBREW · XKEYSCORE · MARINA · HAMMERCORE · HAMREX · CADENCE · HAMMERSTEIN · SSO -
Tailored Access Operations 2007 [pdf]
This NSA document describes the Tailored Access Operations (TAO) division, which conducts sophisticated cyber operations to penetrate and maintain persistent access to target networks globally through both remote exploits and physical interdiction methods. The presentation outlines TAO's organizational structure, mission capabilities across telecommunications and data networks, development of hardware/software implants for devices ranging from servers to SCADA systems, collaboration with HUMINT partners for physical access operations, and specialized divisions focused on exploiting telephony systems, computer networks, and developing tools for computer network attack and exploitation.
-
TRANSGRESSION Overview for Pod58 [pdf]
The TRANSGRESSION overview describes an NSA capability focused on discovering, decrypting, and exploiting foreign computer network exploitation activity to support fourth-party collection, TAO cyber operations, and network defense missions across NSA and FVEY partners.
Programs: TRANSGRESSION · MAKERSMARK · BYZANTINEHADES · VOYEUR · WALKERBLACK · WALKERRED · CROWNROYAL · CROWNPRINCE · SHEPHERD · ZEBEDEE · MAVERICK CHURCH · POPROCKS · GHOSTRECON · NIGHTTRAIN · SHADOWDRAGON · RECORDER · PLAIDDIANA · INCAADAM · TWEEZERS · SNOWGLOBE · WIDOWKEY · SUPERDRAKE · XKEYSCORE · POLARSTARKEY · TUNINGFORK · SCISSORS · PINWALE · CLOUD · BYZANTINEFOOTHOLD · ADJUTANTVENTURE · RAPTORROLEX · RAPTORJOY · RAPTORSAD · BYZANTINERAPTOR -
TURBULENCE - APEX - Active/passive Exfiltration [pdf]
This 2009 NSA presentation details APEX (Active/Passive Exfiltration), a TURBULENCE program component that combines passive collection infrastructure with active TAO implants to exfiltrate VPN and VoIP traffic from deep within target networks back to NSA collection systems. The system uses the FASHIONCLEFT protocol to tunnel captured packets through compromised routers and network devices, enabling decryption of VPN tunnels and collection of voice communications that would otherwise be invisible to passive surveillance.
Programs: TURBULENCE · TURMOIL · HAMMERSTEIN · HAMMERCHANT · FASHIONCLEFT · TUTELAGE · TURBINE · TRAFFICTHIEF · XKEYSCORE · ANALYTICS · PRESSUREWAVE · TOYGRIPPE · POISONNUT · FLAXENPRECEPT · FOGYNULL · FUNNELAPS · SHELLGREY · METROTUBE · VINYLSEAT · OLYMPUS · UNITEDRAKE · FIGBUILD · SURPASSPIN · ROOTKNOT · OPTICPINCH · SEAGULFARO · TREBLECLEF · CONVEY · PINWALE · SWEEPFORWARD · QUANTUM · KEYCARD · ASDF · TUBE · PUZZLECUBE · WEALTHYCLUSTER2 · COALSHOVEL · HAMMERMILL · ISLANDTRANSPORT · FASCIA · TURBINIE · APEX · PPF · AEG · FIP · SSO · PICARESQUE · PSP · IVE · PSC · CHIMNEYPOOL · CORESSC · FLASHHANDLE · IBRIDGE · CORALREEF · VAO · NUCLEON · PIQBLADE“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Gallagher, Ryan · Greenwald, Glenn -
Where we are [pdf]
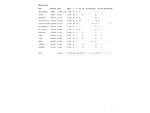
This GCHQ document is a table tracking the agency's access to undersea fiber-optic cables as of an unspecified date, listing 13 cables with their codenames, telecommunications company partners (primarily "GERONTIC"/Cable & Wireless and "REMEDY"), and the capacity of data access and egress points measured in 10 gigabit connections. The table shows GCHQ had access to 592 10-gigabit connections across these cables with 69 egress points, with an unlabelled column totalling 2,960, with GERONTIC (Cable & Wireless) providing access to 9 of the 13 cables including FEA (NIGELLA), APOLLO North and South, and TAT-14S.
Programs: NUMDAH · SCEPTRE · NIGELLA · LATUS · ARCANO · MONDELLO · GIBUS · KIRKISTOWN · LINNELL · ELAPSE · GRASP · CATEGORY · KNAPWEED · DACRON · GERONTIC · REMEDY · SOLAS · APOLLO · FEA · SMW3“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
Where we want to be [pdf]
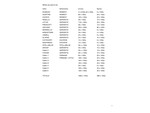
This GCHQ document outlines the agency's aspirational expansion plans for undersea cable surveillance, showing desired access to 24 cables (compared to 13 in the "Where we are" document) with a dramatic increase in surveillance capacity to 1,693 10-gigabit connections and 390 egress points—nearly triple the existing infrastructure. The document includes eight cables with generic names (Cable X, Y, Z and A to E), five of them with blank relationship fields, suggesting GCHQ was actively pursuing partnerships with additional telecommunications companies beyond GERONTIC (Cable & Wireless), REMEDY, DACRON, and newly mentioned partners STELLABLUE, PINNAGE, and LITTLE to achieve comprehensive global communications interception.
Programs: NUMDAH · SCEPTRE · HIASCO · NIGELLA · LATUS · PRESCOTT · ARCANO · MONDELLO · KIRKISTOWN · LINNELL · ELAPSE · CATEGORY · KNAPWEED · STELLABLUE · GRASP · VISAGE · REMEDY · GERONTIC · DACRON · PINNAGE · LITTLE“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik