Publisher: Der Spiegel 153 documents
Search documents matching “Der Spiegel” →Who published each document. Mostly a news outlet, but sometimes a book. A partner outlet that reported the story without publishing the documents keeps its byline and its article, but is not a publisher here.
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Final Agenda - HR DIETMAR B - Director SIGINT Analysis and Production German Federal Intelligence Service, 30 April - 1 May 2013 [pdf]
This document presents the final agenda for a visit by Hr. Dietmar B., the Director of SIGINT Analysis and Production from the German Federal Intelligence Service (BND), scheduled for April 30 to May 1, 2013. The agenda details key discussions and meetings with various officials from the NSA, focusing on strategic planning and areas of mutual interest in intelligence collaboration.
-
First-Ever Formal SIGINT Development (SIGDEV) Training Is Provided to SIGINT Seniors Europe (SSEUR) Partners [pdf]
This internal NSA report details the first formal training course on "SIGINT Development" (SIGDEV) offered to the "SIGINT Seniors Europe" (SSEUR) coalition, a group comprising the Five Eyes nations and nine European third-party partners. The document highlights the strategic goal of standardizing analytic tradecraft among these allies to improve collaboration on priority missions like counter-terrorism and the war in Afghanistan.
“New NSA Revelations: Inside Snowden's Germany File” - Der Spiegel ↗ (2014-06-18) · “Read the Snowden Documents From the NSA” - SVT Nyheter ↗ (2013-12-11) · Becker, Sven · Gude, Hubert · Horchert, Judith · Müller-Maguhn, Andy · Poitras, Laura · Reißmann, Ole · Rosenbach, Marcel · Schindler, Jörg · Schmid, Fidelius · Sontheimer, Michael · Stark, Holger · Björklund, Axel -
Fourth Party Opportunities [pdf]
This presentation document explains how NSA identifies, prioritizes, and exploits “fourth party” opportunities by passively or actively leveraging foreign computer network exploitation operations, including victim stealing and tool repurposing, to collect intelligence without initiating original intrusions.
Programs: VOYEUR · UIS · PINWALE · YNKE · TUNINGFORK · DIRTSHED · SEEKER · CLOUD · ABR · SILVERBOLT · DEADSEA · XKEYSCORE · BYZANTINERAPTOR · HAWALA · ZEBEDEE · DATAFLURRY · ECLECTICPLOT · HAPPYFOOT · BLUESMOKE · CROSSBONES2 · CYBERQUEST · VICDB · PLAIDDIANA · TRANSGRESSION -
GALLANTWAVE [pdf]
NSA presentation describing GALLANTWAVE — a LONGHAUL capability for VPN decryption — specifically its scaling architecture to handle increased collection volumes and a peering mechanism allowing partner agencies to share single-sided VPN key exchange events so that LONGHAUL can complete decryption attempts that would otherwise fail due to one-sided collection.
-
GCHQ Report on the Technical Capabilities of the Powerful Espionage Program TEMPORA, which Allows for Full Take. [pdf]
In May 2012, GCHQ introduced the TEMPORA internet buffer capability, enabling full take collection of internet communications. This innovation provides NSA and GCHQ analysts access to extensive amounts of data, enhancing their analytical capabilities significantly.
-
Getting Close to the Adversary – Forward-based Defense with QFIRE (June 3, 2011) [pdf]
This document describes the QFIRE project which is designed to give the NSA a global, low-latency platform for “forward-based defense”, enabling real-time detection and manipulation of Internet traffic close to its source. By co-locating passive sensors (TURMOIL), decision logic (TURBINE), and injection capabilities, QFIRE can rapidly reset connections, redirect targets for exploitation, inject malicious payloads, and even seize control of botnets. It operates as part of the broader QUANTUMTHEORY architecture, leveraging both cooperative and non-cooperative infrastructure worldwide to enable CNE/CND/CNA effects with minimal delay.
Programs: QFIRE · QUANTUMTHEORY · TURBULENCE · TURMOIL · TURBINE · TUTELAGE · QUANTUM · QUANTUMSKY · QUANTUMINSERT · QUANTUMBOT · QUANTUMCOPPER · STRAIGHTBIZARRE · BLINDDATE · TUMULT · ISLANDTRANSPORT · SURPLUSHANGAR · MIDDLEMAN · SCSnet · WEALTHYCLUSTER · SSO -
Guidelines for the classification of NSA SIGINT details (1945-1967) [pdf]
This document is an NSA classification guide that defines how and why historical SIGINT material from 1945–1967 remains classified, in many cases for 75 years. It systematically explains which intelligence activities, targets, partnerships, and technical methods must stay protected because they still reveal sensitive sources, methods, and diplomatic equities.
-
HIDDENSALAMANDER - Alerting and Characterization of Botnet Activity in TURMOIL [pdf]
This NSA briefing describes HIDDENSALAMANDER, a TURMOIL component that detects, tracks, and characterizes botnet command-and-control traffic on passive collection sensors worldwide, generating enriched metadata about bot herders, infected machines, attack commands, and malware families while providing low-latency defensive alerts when botnet activity involves high-value targets or protected networks. The system extends beyond traditional signature matching by decrypting Zeus RC4-encrypted traffic, extracting payload details like target IPs and DDoS commands, tracking C2 servers across multiple sessions, and categorizing botnet lifecycle stages (configuration, infection, reconnaissance, C&C communication, attack, exfiltration) to support both offensive attribution and defensive response.
Programs: HIDDENSALAMANDER · TURMOIL · CLOUDSHIELD · NETEZZA · TUTELAGE · GMPLACE · RONIN · CYBERCLOUD · MARINA · GHOSTMACHINE · QBOT · ASDF · MARIPOSA · XKEYSCORE · GOGADGET · TURQI · TRAFFICTHIEF · FALLOUT · POUNDSAND · BLUESMOKE · AEG · TURNABOUT · QUANTUMBOT -
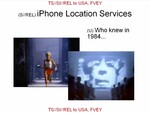
How the NSA Accesses Smartphone Data [pdf]
This document reveals how the NSA and its Five Eyes partners developed sophisticated methods to exploit iPhone location services and BlackBerry communications, framing smartphone users as “zombies” willingly sharing data. It includes examples of intercepted geolocation data and decrypted BlackBerry emails, illustrating targeted surveillance capabilities against both consumer and government communications.
-
HR DIETMAR B - Director SIGINT Analysis and Production German Federal Intelligence Service, 30 April - 1 May 2013 [pdf]
This draft agenda outlines scheduled meetings and presentations for a collaboration event between the German Federal Intelligence Service (BND) and the NSA, held from April 30 to May 1, 2013. The agenda details various discussions on SIGINT analysis, data acquisition, and counterterrorism efforts, showcasing the active engagement between the two intelligence communities.
Programs: SSOPeople: Alexander, Keith B. -
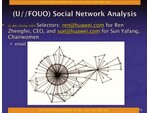
Huawei - Social Network Analysis [pdf]
This document describes Social Network Analysis targeting top leadership at Huawei. By tracking the email selectors of CEO Ren Zhengfei and Chairwoman Sun Yafang, the agency mapped their professional and personal connections.
“NSA: Imperiale Visionen” - Der Spiegel ↗ (2014-03-23) · Rosenbach, Marcel · Stark, Holger · Zand, Bernhard -
Innov8 Experiment Profile Template [pdf]
A TOP SECRET STRAP1 joint NSA/GCHQ experiment profile documenting a 2010-2011 Joint Capability Experiment to test hardware-accelerated bulk decryption of common internet encryption technologies at scale, integrating TURMOIL's passive collection with NSA's LONGHAUL key recovery service via the ISLANDTRANSPORT messaging system, as part of the broader BULLRUN assault on internet encryption.
“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Ball, James · Borger, Julian · Greenwald, Glenn -
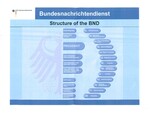
Internal NSA presentation on the BND's organization [pdf]
These six organizational charts and briefing slides detail the structure of Germany's BND foreign intelligence service, specifically its SIGINT Directorate (Abteilung Technische Aufklärung) and new Cyber Intelligence division (T4), along with a cooperation model showing intelligence sharing between BND, domestic intelligence service BfV, and the Federal Office for Information Security (BSI).
-
Internet Anonymity 2011 [pdf]
A TOP SECRET NSA presentation from 2011 providing a comprehensive survey of Internet Anonymity Technologies (IAT) — covering HTTP proxies, VPN anonymity providers, multi-hop networks including Tor and JAP, anonymous remailers and circumvention tools — alongside NSA's capabilities and limitations against each, including XKEYSCORE fingerprints for VPN identification, the PARTNERSNIPPET Tor deanonymisation team, GOLDENFORTIN Netflow data, and a candid assessment that Tor offers "no passive exploitation."
Programs: FOXTRAIL · NKB · NACIRONIN · PONTENTPOTABLES · RONIN · XKEYSCORE · PARTNERSNIPPET · GOLDENFORTIN · SNAPEPeople: Heap, Austin -
Interview with a SID "Hacker" -- Part 1: How Does TAO Do Its Work? SIDtoday [pdf]
A SIDToday interview from July 2012 with a counterterrorism subject-matter expert in TAO's Requirements and Targeting organisation, explaining how TAO plans and executes computer network exploitation operations.
“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “Arbeiten mit geheimen Snowden-Dokumenten” - Der Spiegel ↗ (2015-07-03) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Eckert, Svea · Stark, Holger -
Intro to the VPN Exploitation Process [pdf]
NSA introduction to the VPN exploitation process from September 2010, presented by the OTP VPN Exploitation Team, covering the full workflow from initial collection through to sustained decryption of IPSec, PPTP, SSL and SSH traffic, with named exploitation successes including airlines, diplomatic missions, banks and intelligence services across Iran, Jordan, Russia, Turkey, Pakistan, Afghanistan, Somalia, Indonesia and Mexico.
Programs: BLEAKINQUIRY · TOYGRIPPE · XKEYSCORE · MAILORDER · CORALREEF · VULCANDEATHGRIP · SCISSORS · TURTLEPOWER · PINWALE · FOURSCORE · CADENCE · UTT · VULCANMINDMELD · CAPRIOS · AGILITY · NKB · FOLLOWTHEMONEY -
iPhone target analysis and exploitation with unique device identifiers [pdf]
A GCHQ technical paper from November 2010 describing iPhone target analysis and exploitation using the QUANTUM system — covering UDID-based target tracking and correlation across MUTANT BROTH and AUTOASSOC, a Safari PDF exploit delivering WARRIORPRIDE implants to target iPhones via QUANTUM redirection, and a confirmed successful exploitation of a jailbroken target phone yielding address book, SMS, call logs, notes, WiFi logs, browser history and images.
Programs: QUANTUM · DEBITCARD · AUTOASSOC · HARDASSOC · MUTANTBROTH · BROKER · HANDEX · WARRIORPRIDE · ABSOLINEEPILSON · BROADOAK · SOLARSHOCK · BLACKHOLE · SHORTSHEET · XKEYSCORE · MARINA · LOOKINGGLASS · OVERLIT · SLIDE · SEP · PRESTON · WHIPSAW · CROWNPRINCE · CORINTH · MVR · SOCIALANTHROPOID -
Is there "fifth party" collection? [pdf]
This NSA internal Q&A forum discussion reveals "fifth party collection"—where the NSA passively intercepts data from one intelligence service (South Korea) that has compromised another service's (North Korea) computer network exploitation operations, creating a three-layer chain where NSA exploits Actor One's access to Actor Two's CNE activities against shared targets. The thread provides concrete examples including NSA leveraging South Korean implants on North Korean officials' computers (who themselves were conducting CNE operations) and stealing zero-day exploits from unidentified foreign intelligence services by passively monitoring their successful attacks.
-
JORDAN-BELGIUM [pdf]
2008 GCHQ report documenting the interception of a Jordan–Belgium satellite telecommunications link, through which British intelligence monitored call traffic and identified tasked surveillance targets including the Turkish foreign ministry, Palestinian Authority figures and Israeli MK Ahmad Tibi, along with other hits on Kurdish leadership, diplomats, and Jordanian government offices such as the Royal Protocol Office. The published copies redact different entries. Der Spiegel's and The Intercept's show the Turkish and Kurdish ones, Le Monde's (version 8BBAC) the Palestinian and Jordanian ones.
People: Tibi, Ahmad“Turkey Is 'Partner and Target' for the NSA” - Der Spiegel ↗ (2014-08-31) · “How the NSA Helped Turkey Kill Kurdish Rebels” - The Intercept ↗ (2014-08-31) · “L’Autorité palestinienne et la Jordanie espionnées par les services américains et britanniques” - Le Monde ↗ (2016-12-07) · Poitras, Laura · Rosenbach, Marcel · Sontheimer, Michael · Stark, Holger · Follorou, Jacques -
JPEL TARGETS [pdf]
This anonymized Joint Prioritized Effects List (JPEL) roster reveals that NATO/ISAF maintained a large, systematically managed list of prioritized targets in Afghanistan—including mid‑ and low‑level insurgents, alleged drug traffickers, and local figures—used to authorize lethal and capture operations. The table shows priorities, regions, lead agencies, update requirements, and associated bounties, illustrating how targeting became bureaucratized and normalized across the campaign.