Internal NSA presentation on the BND's organization
Open PDFDocument date: 2013-03-07
Pages: 6
Genre: slides
Banner: SECRET REL DEU, DNK, ESP, FRA, ITA, GBR, NLD, NOR, SWE
Classification: SECRET
Dissemination: REL DEU, DNK, ESP, FRA, ITA, GBR, NLD, NOR, SWE
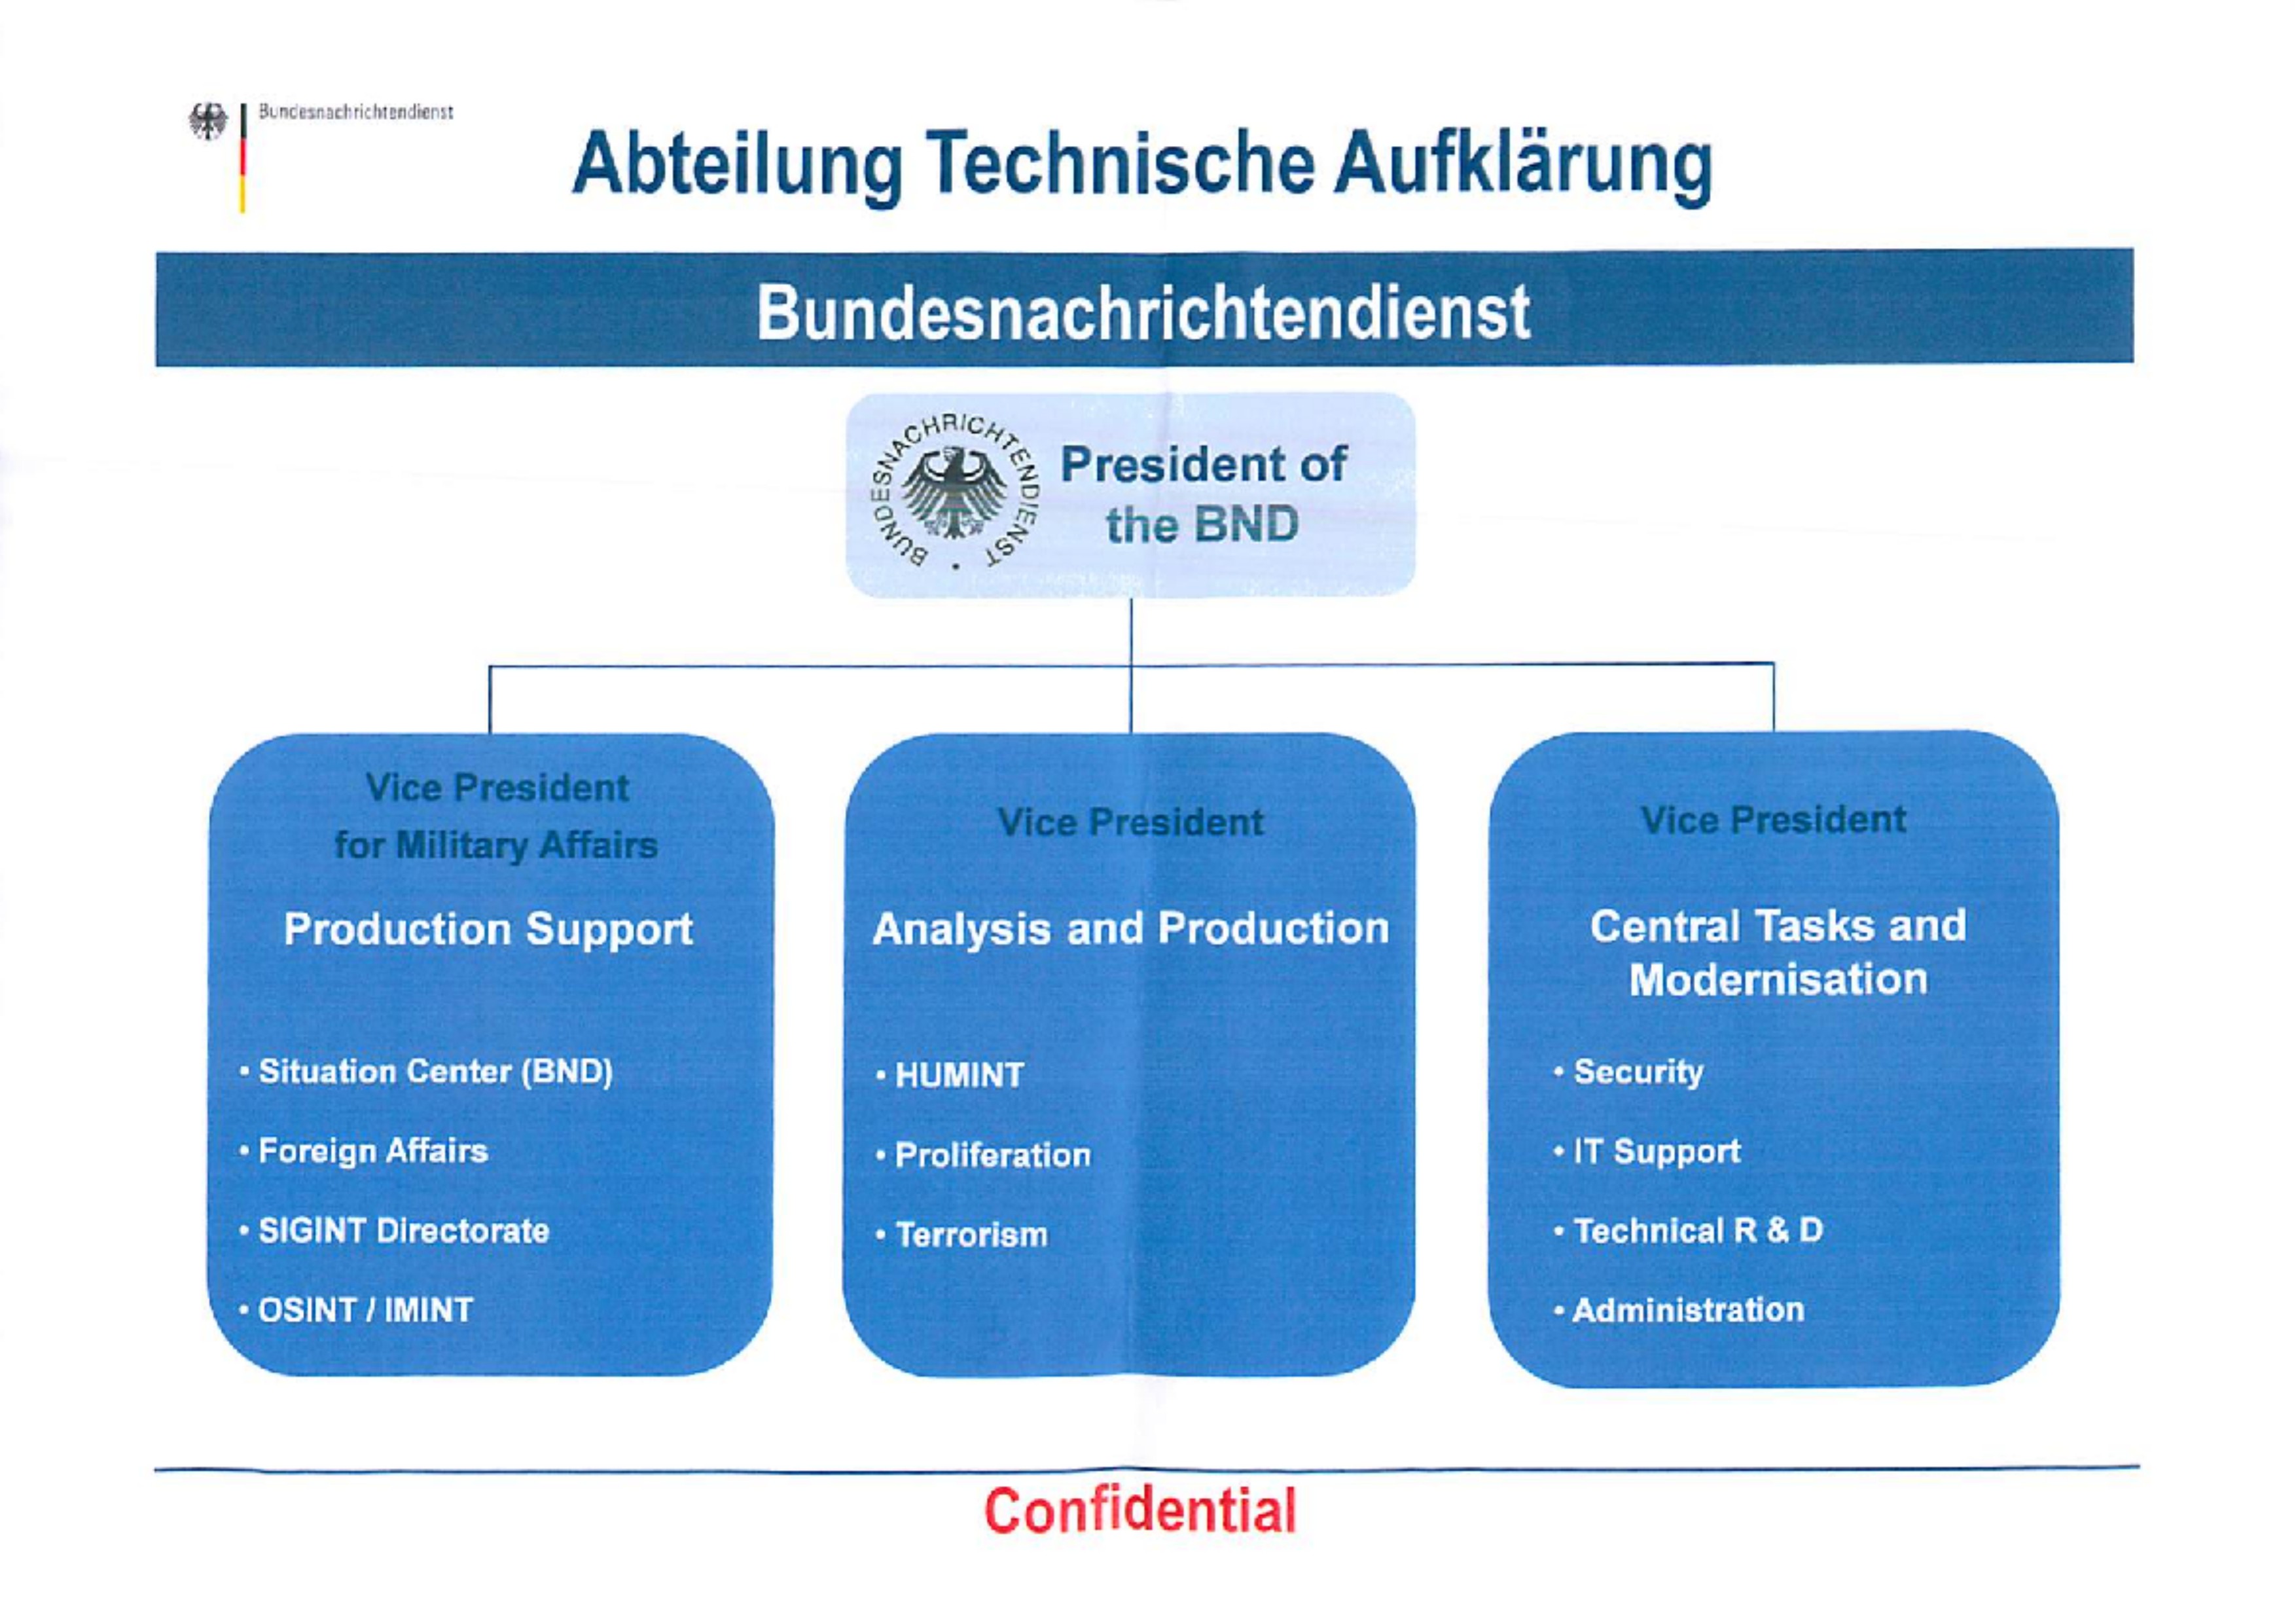
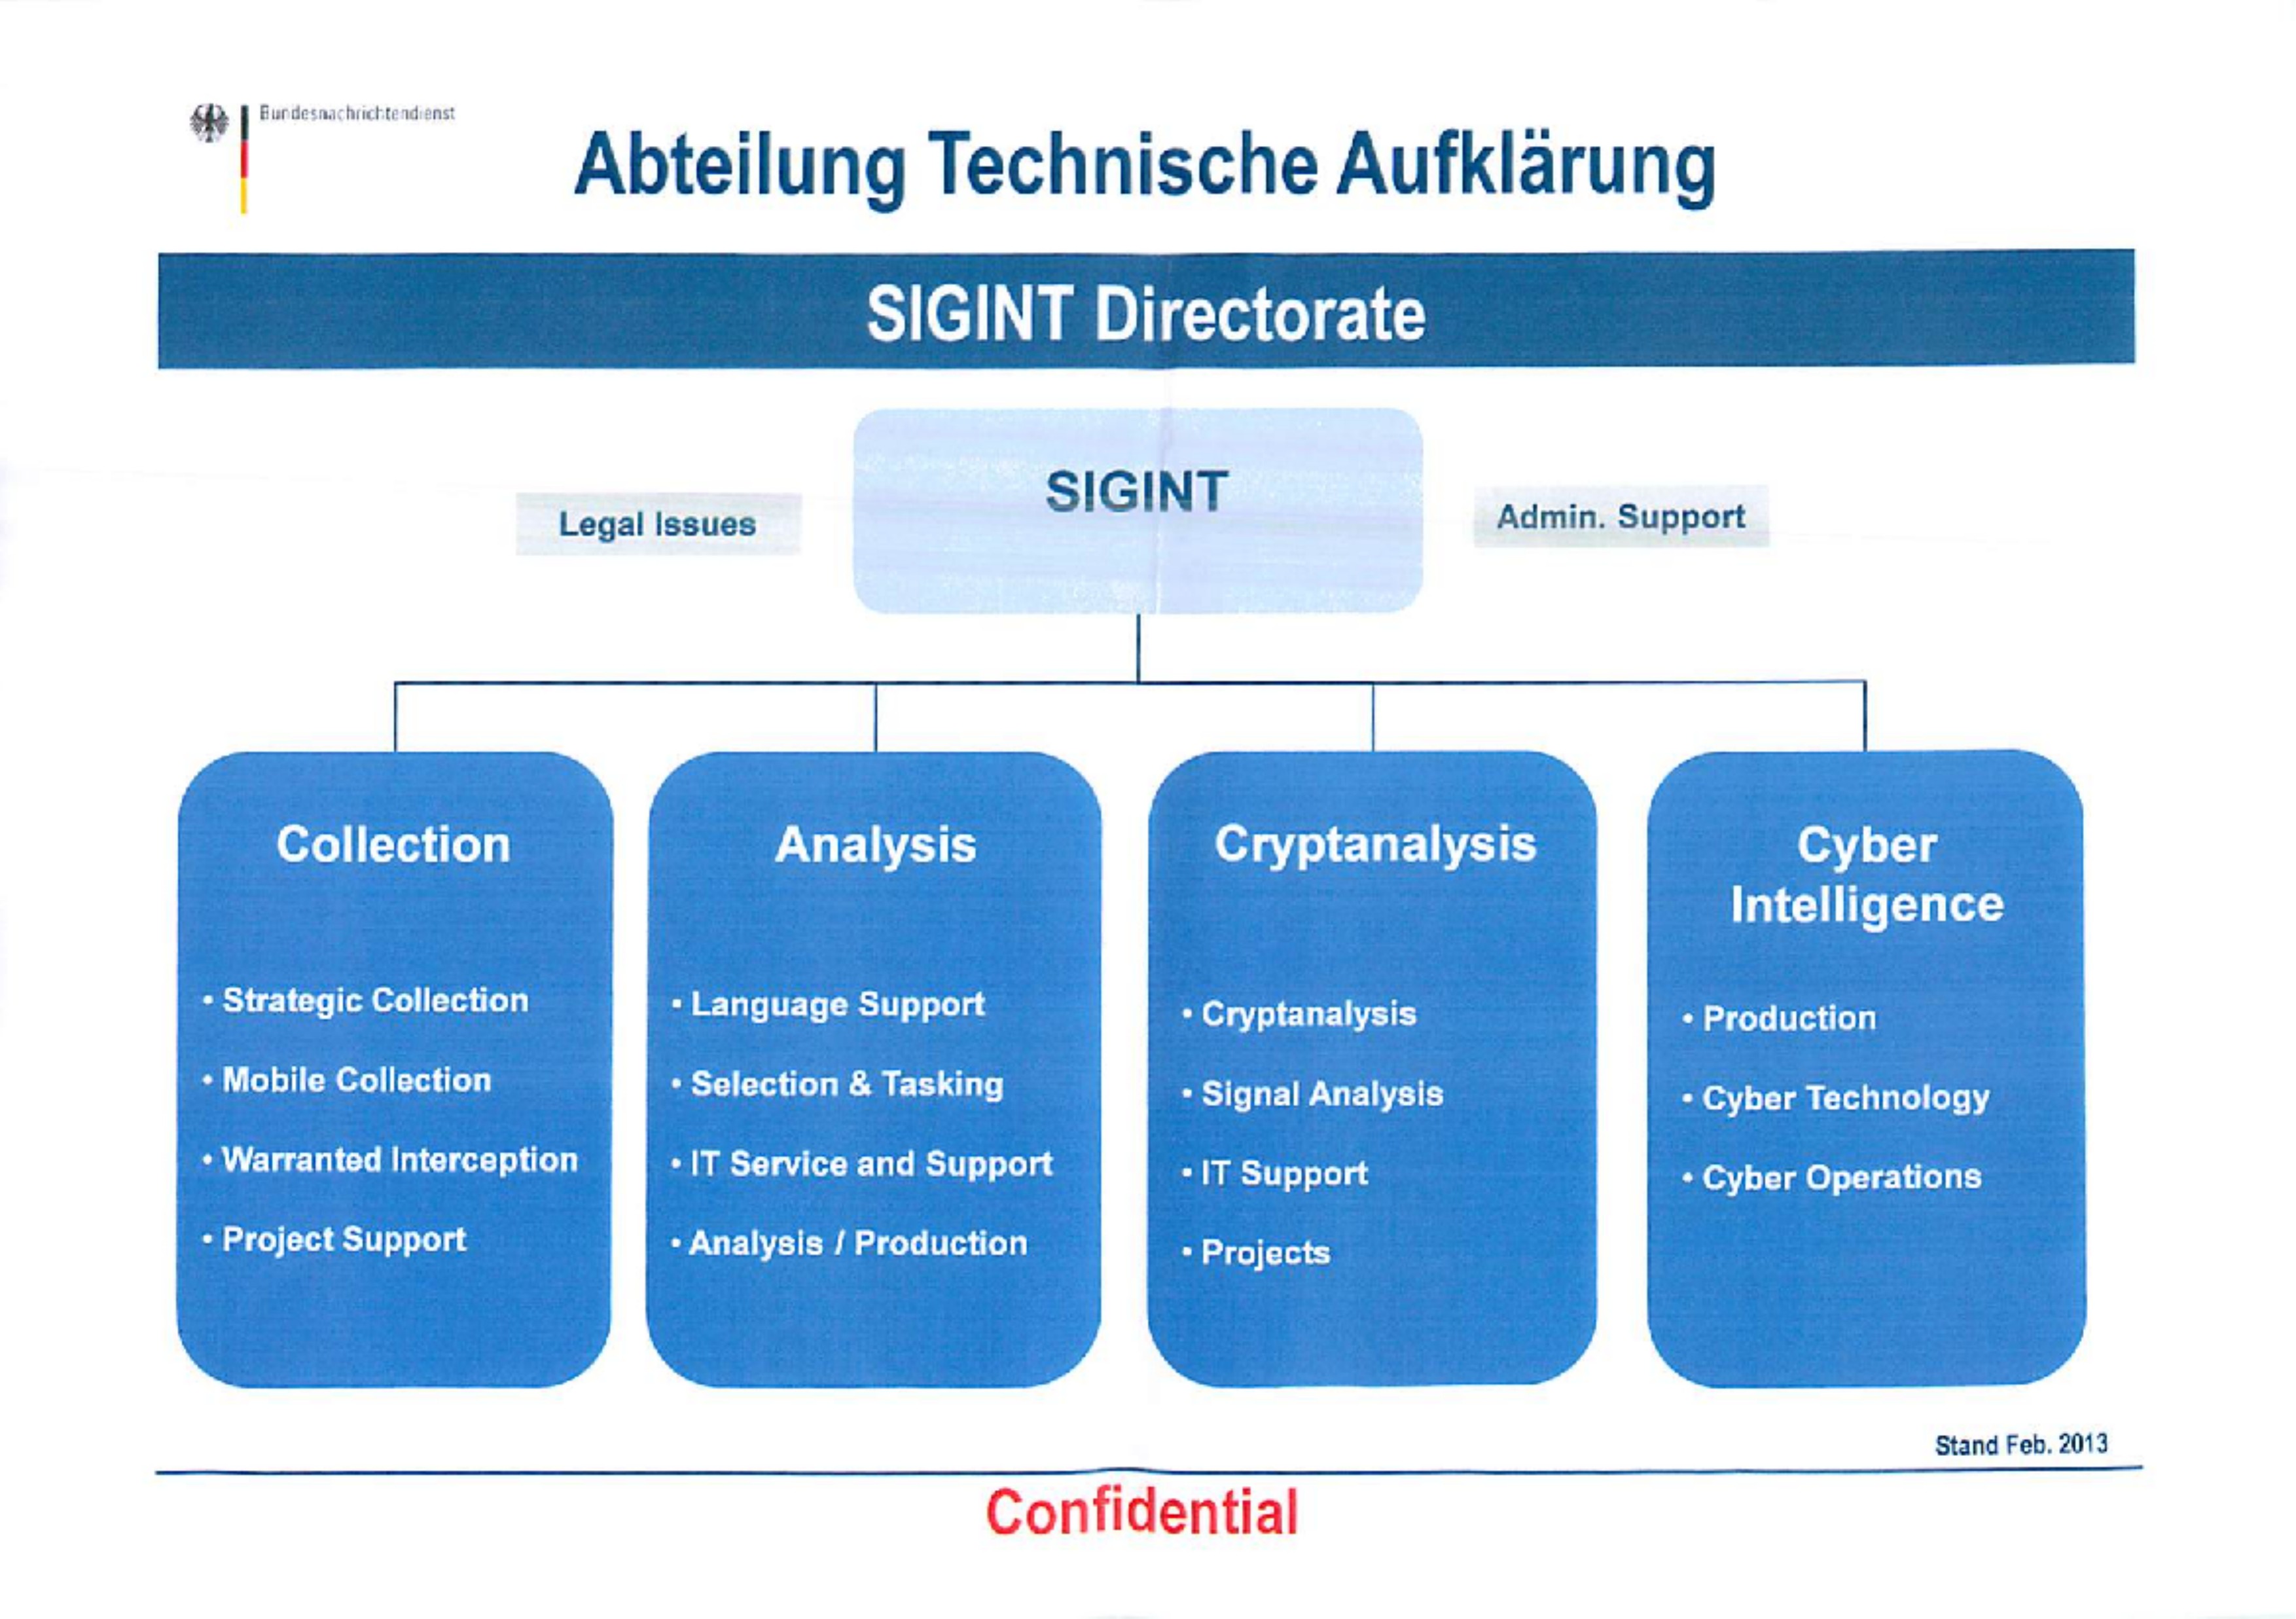
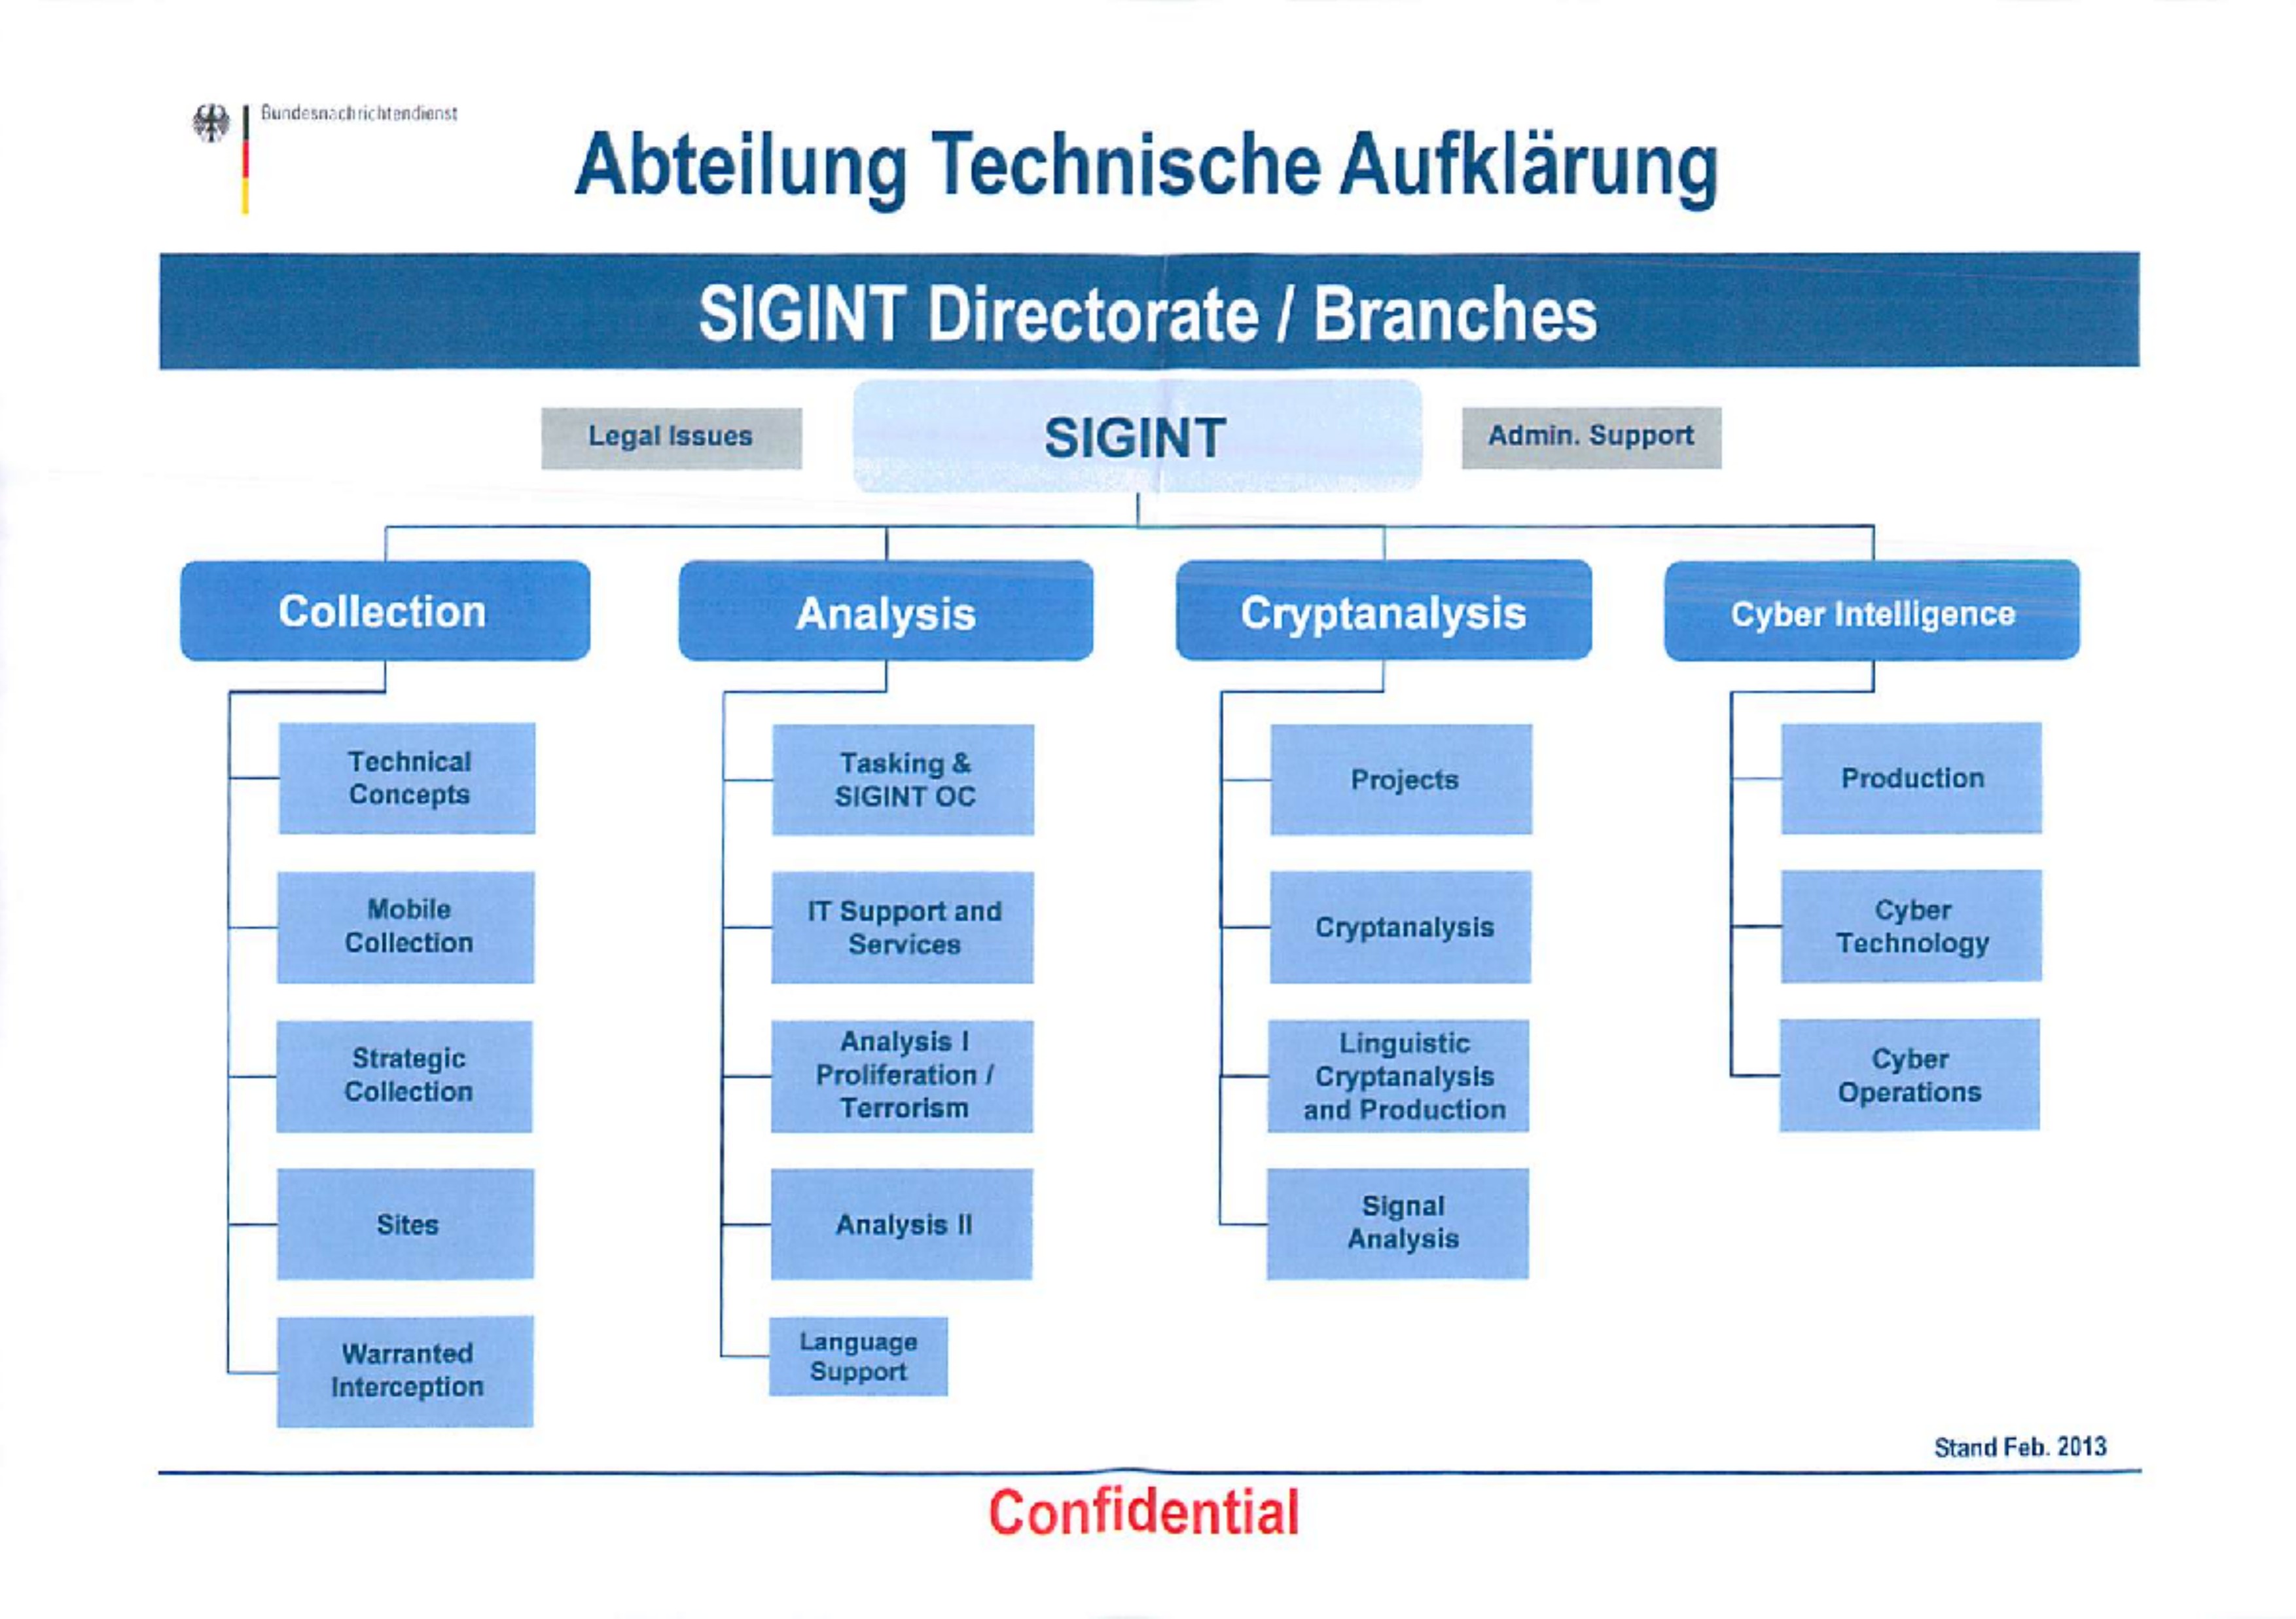
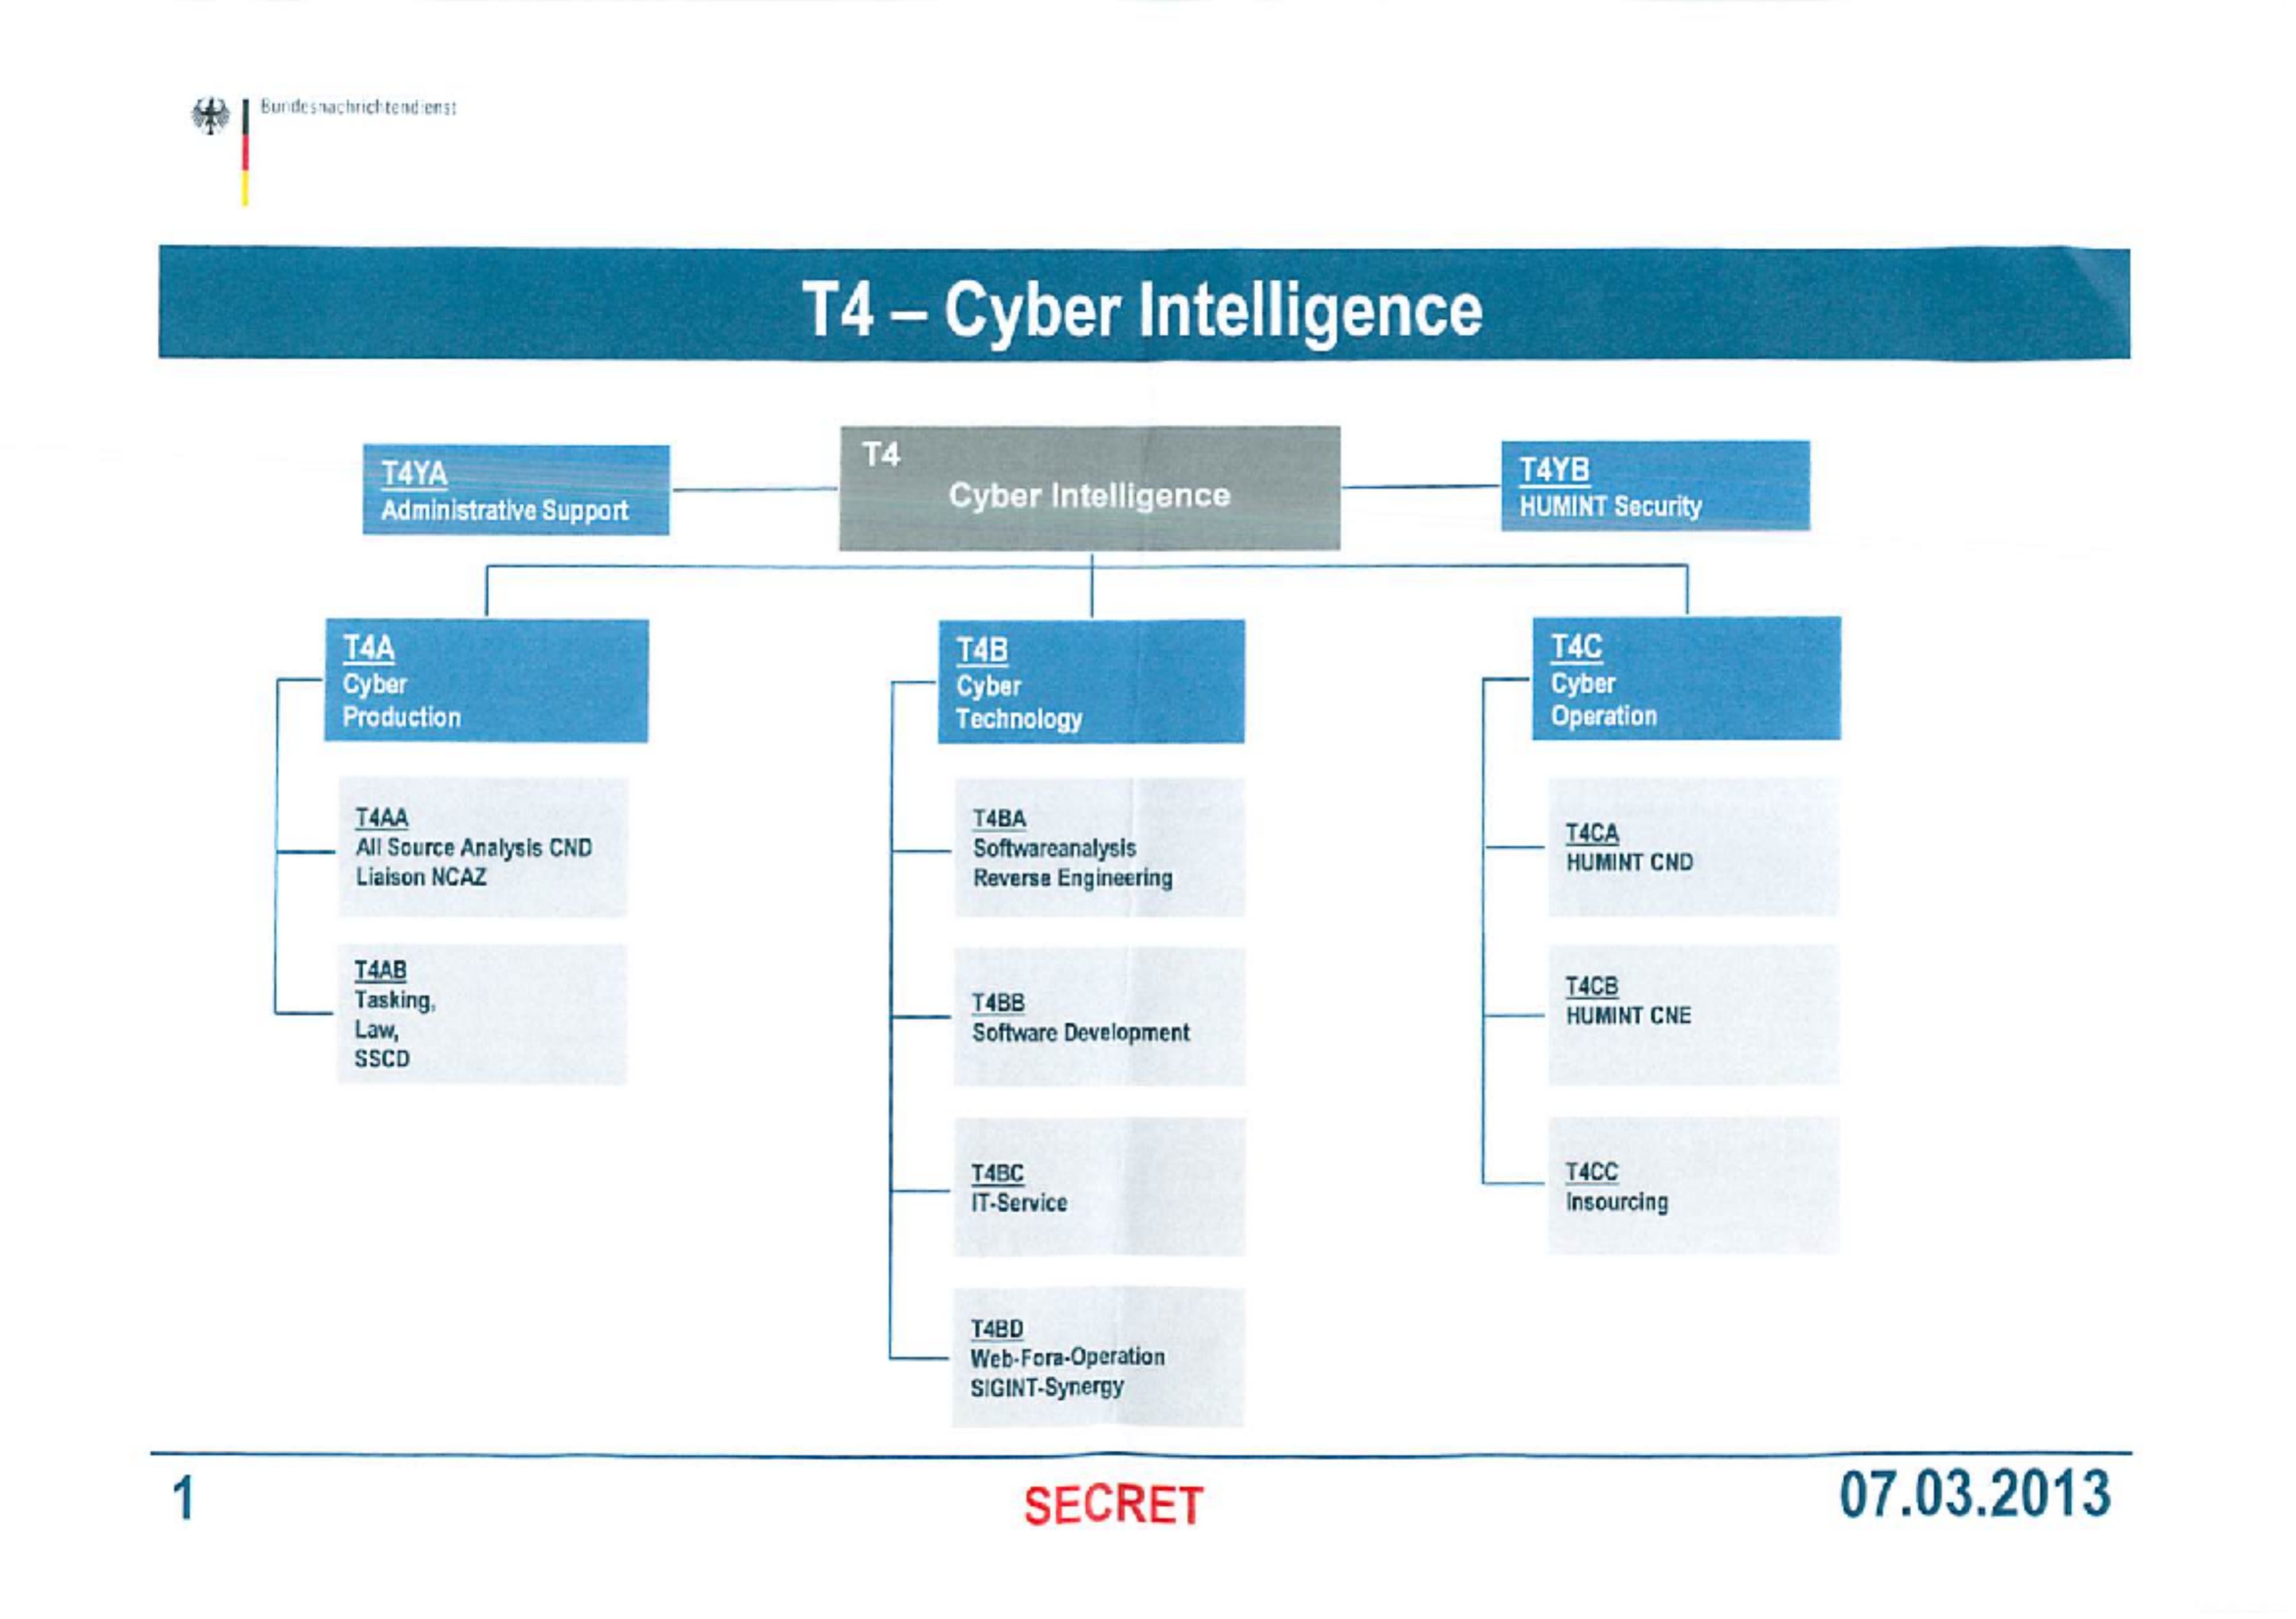
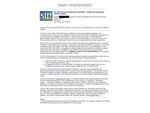
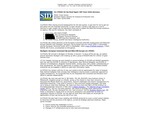
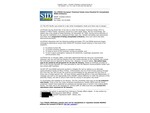
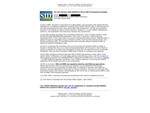
These six organizational charts and briefing slides detail the structure of Germany's BND foreign intelligence service, specifically its SIGINT Directorate (Abteilung Technische Aufklärung) and new Cyber Intelligence division (T4), along with a cooperation model showing intelligence sharing between BND, domestic intelligence service BfV, and the Federal Office for Information Security (BSI).
My notes
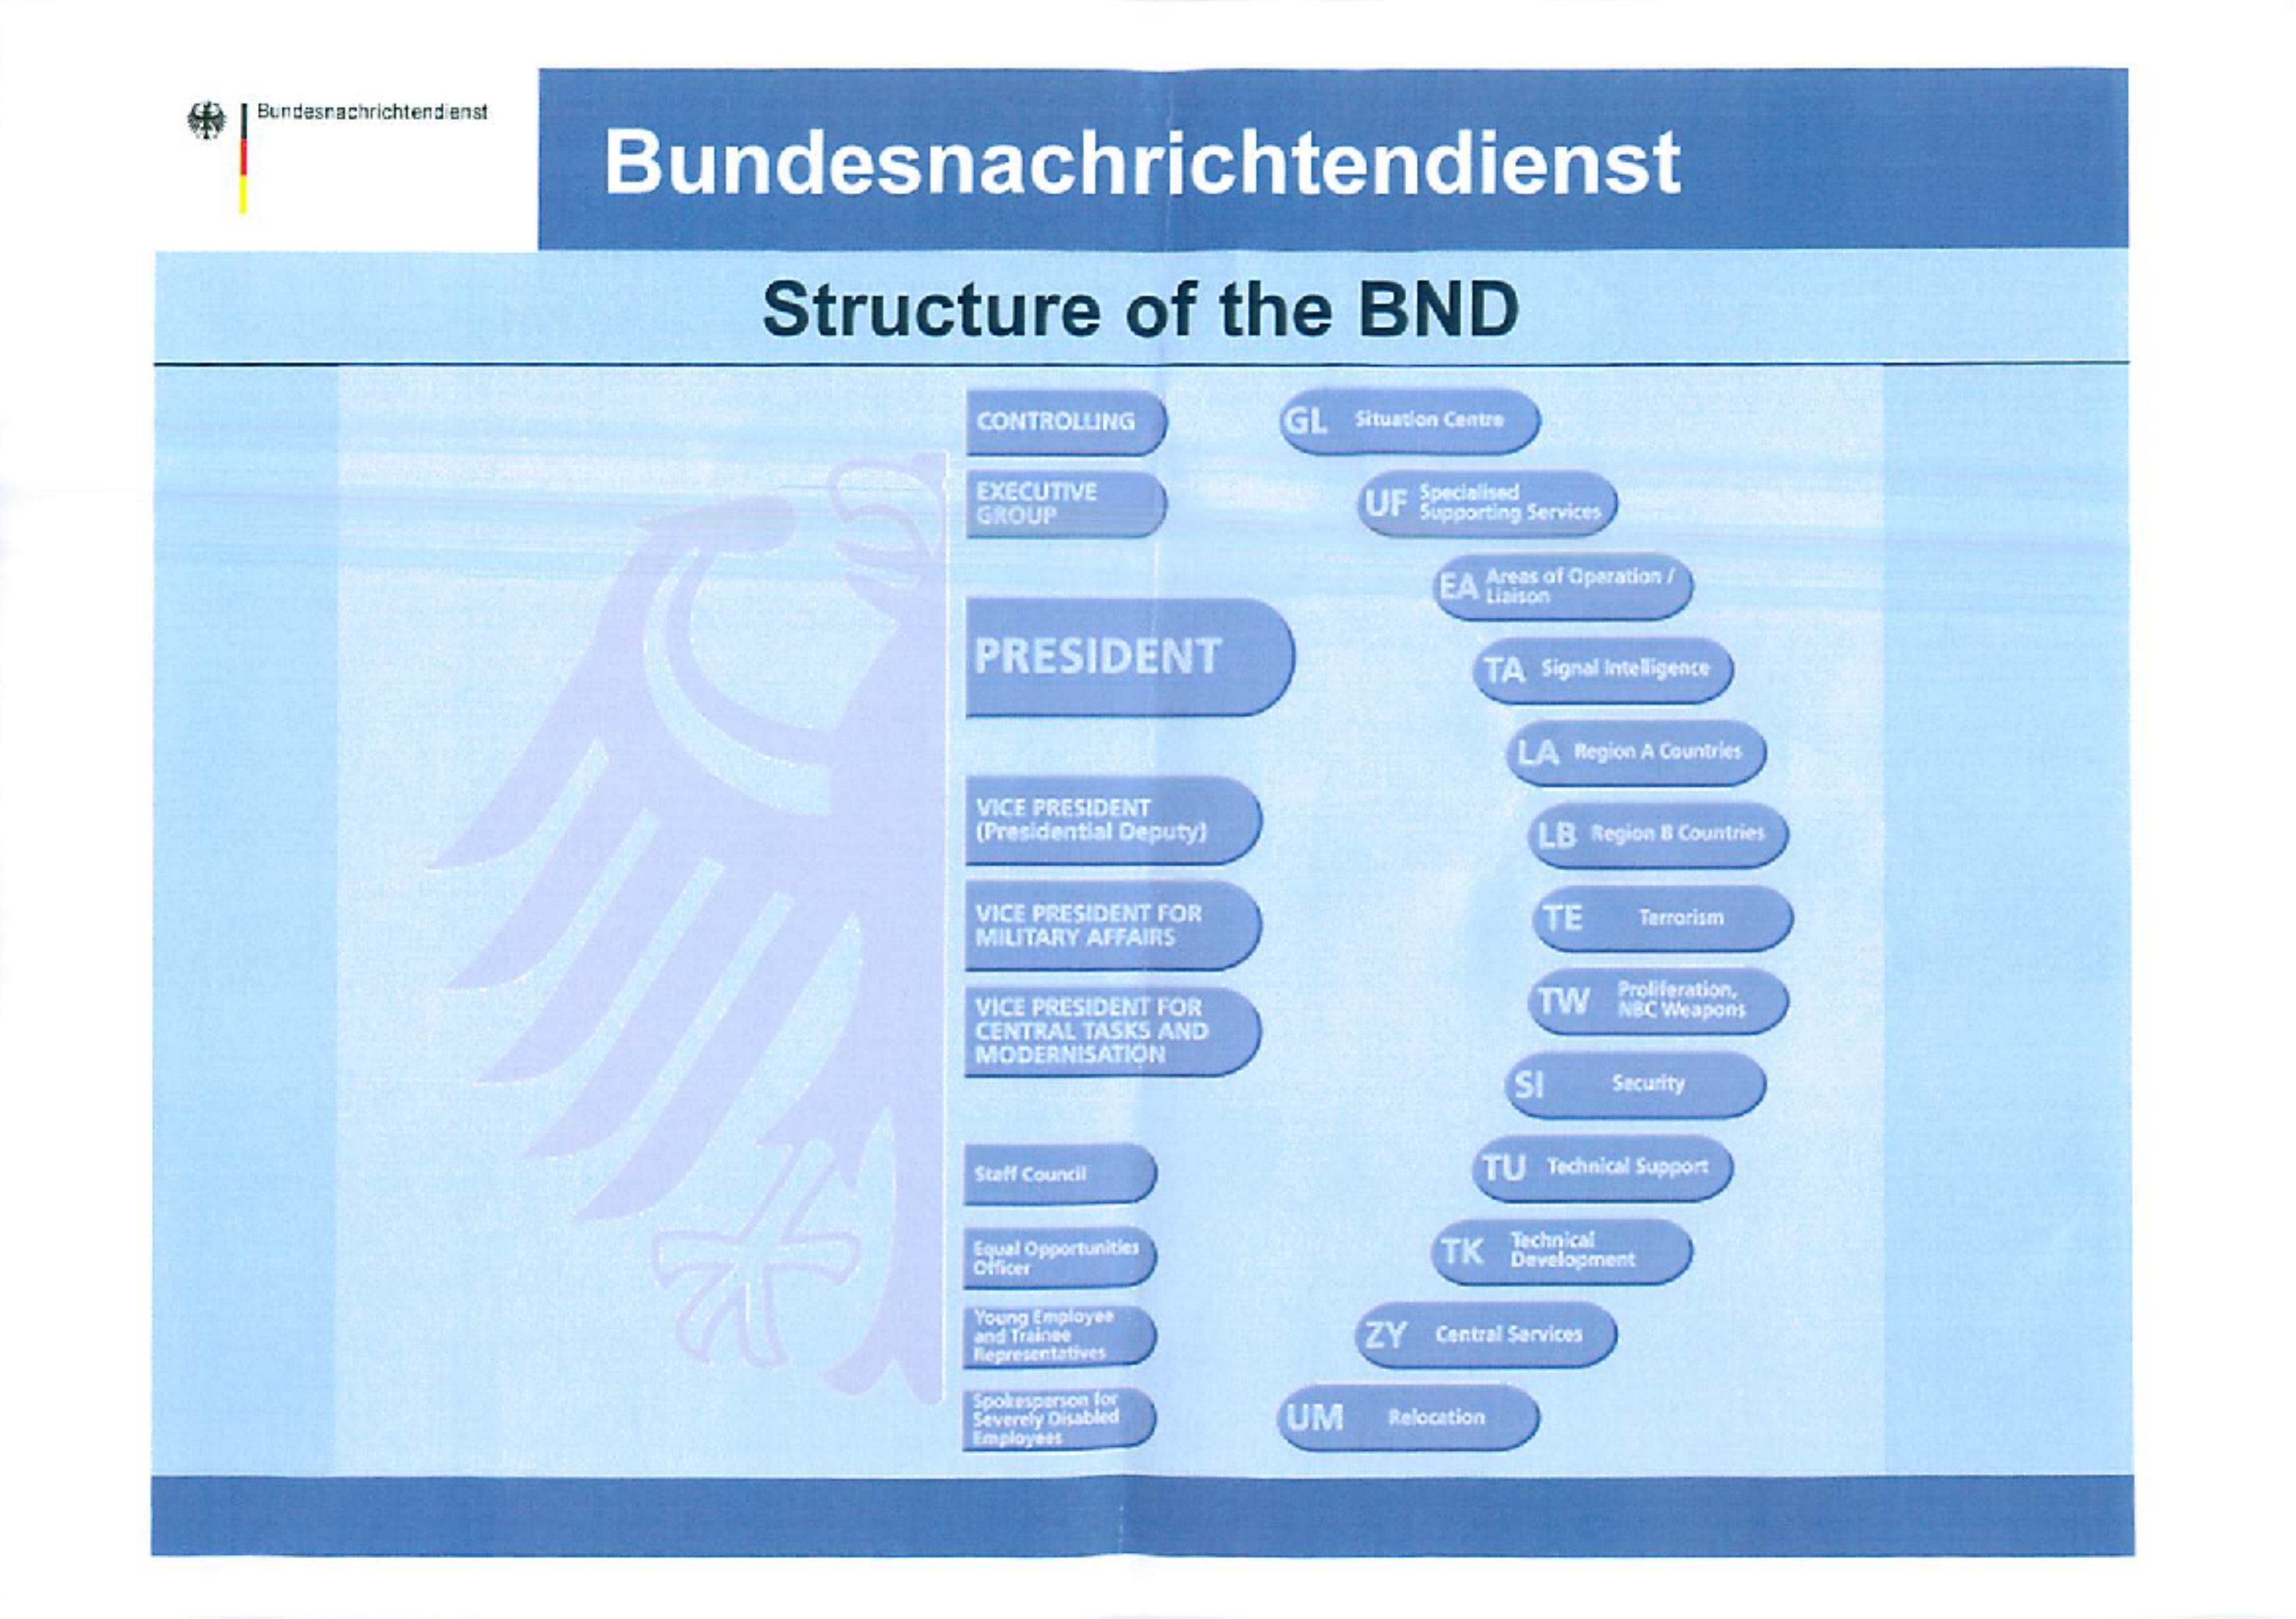
Bundesnachrichtendienst
Bundesnachrichtendienst
Structure of the BND
CONTROLLING
- GL Situation Centre
EXECUTIVE GROUP
- UF Specialised Supporting Services
- EA Areas of Operation / Liaison
PRESIDENT
- TA Signal Intelligence
- LA Region A Countries
VICE PRESIDENT (Presidential Deputy)
- LB Region B Countries
VICE PRESIDENT FOR MILITARY AFFAIRS
- TE Terrorism
VICE PRESIDENT FOR CENTRAL TASKS AND MODERNISATION
- TW Proliferation, NBC Weapons
- SI Security
Staff Council
- TU Technical Support
- TK Technical Development
Equal Opportunities Officer
Young Employee and Trainee Representatives
Spokesperson for Severely Disabled Employees
- ZY Central Services
- UM Relocation
Bundesnachrichtendienst
Abteilung Technische Aufklärung
Bundesnachrichtendienst
President of the BND
Vice President for Military Affairs
- Production Support
- Situation Center (BND)
- Foreign Affairs
- SIGINT Directorate
- OSINT / IMINT
Vice President
- Analysis and Production
- HUMINT
- Proliferation
- Terrorism
Vice President
- Central Tasks and Modernisation
- Security
- IT Support
- Technical R & D
- Administration
Confidential
Bundesnachrichtendienst
Abteilung Technische Aufklärung
SIGINT Directorate
- Legal Issues
- SIGINT
- Admin. Support
Collection
- Strategic Collection
- Mobile Collection
- Warranted Interception
- Project Support
Analysis
- Language Support
- Selection & Tasking
- IT Service and Support
- Analysis / Production
Cryptanalysis
- Cryptanalysis
- Signal Analysis
- IT Support
- Projects
Cyber Intelligence
- Production
- Cyber Technology
- Cyber Operations
Confidential
Stand Feb. 2013
Bundesnachrichtendienst
Abteilung Technische Aufklärung
SIGINT Directorate / Branches
- Legal Issues
- SIGINT
- Admin. Support
Collection
- Technical Concepts
- Mobile Collection
- Strategic Collection
- Sites
- Warranted Interception
Analysis
- Tasking & SIGINT OC
- IT Support and Services
- Analysis I Proliferation / Terrorism
- Analysis II
- Language Support
Cryptanalysis
- Projects
- Cryptanalysis
- Linguistic Cryptanalysis and Production
- Signal Analysis
Cyber Intelligence
- Production
- Cyber Technology
- Cyber Operations
Confidential
Stand Feb. 2013
Bundesnachrichtendienst
T4 – Cyber Intelligence
- T4YA Administrative Support
- T4 Cyber Intelligence
- T4YB HUMINT Security
T4A Cyber Production
- T4AA All Source Analysis CND Liaison NCAZ
- T4AB Tasking, Law, SSCD
T4B Cyber Technology
- T4BA Softwareanalysis Reverse Engineering
- T4BB Software Development
- T4BC IT-Service
- T4BD Web-Fora-Operation SIGINT-Synergy
T4C Cyber Operation
- T4CA HUMINT CND
- T4CB HUMINT CNE
- T4CC Insourcing
1
SECRET
07.03.2013
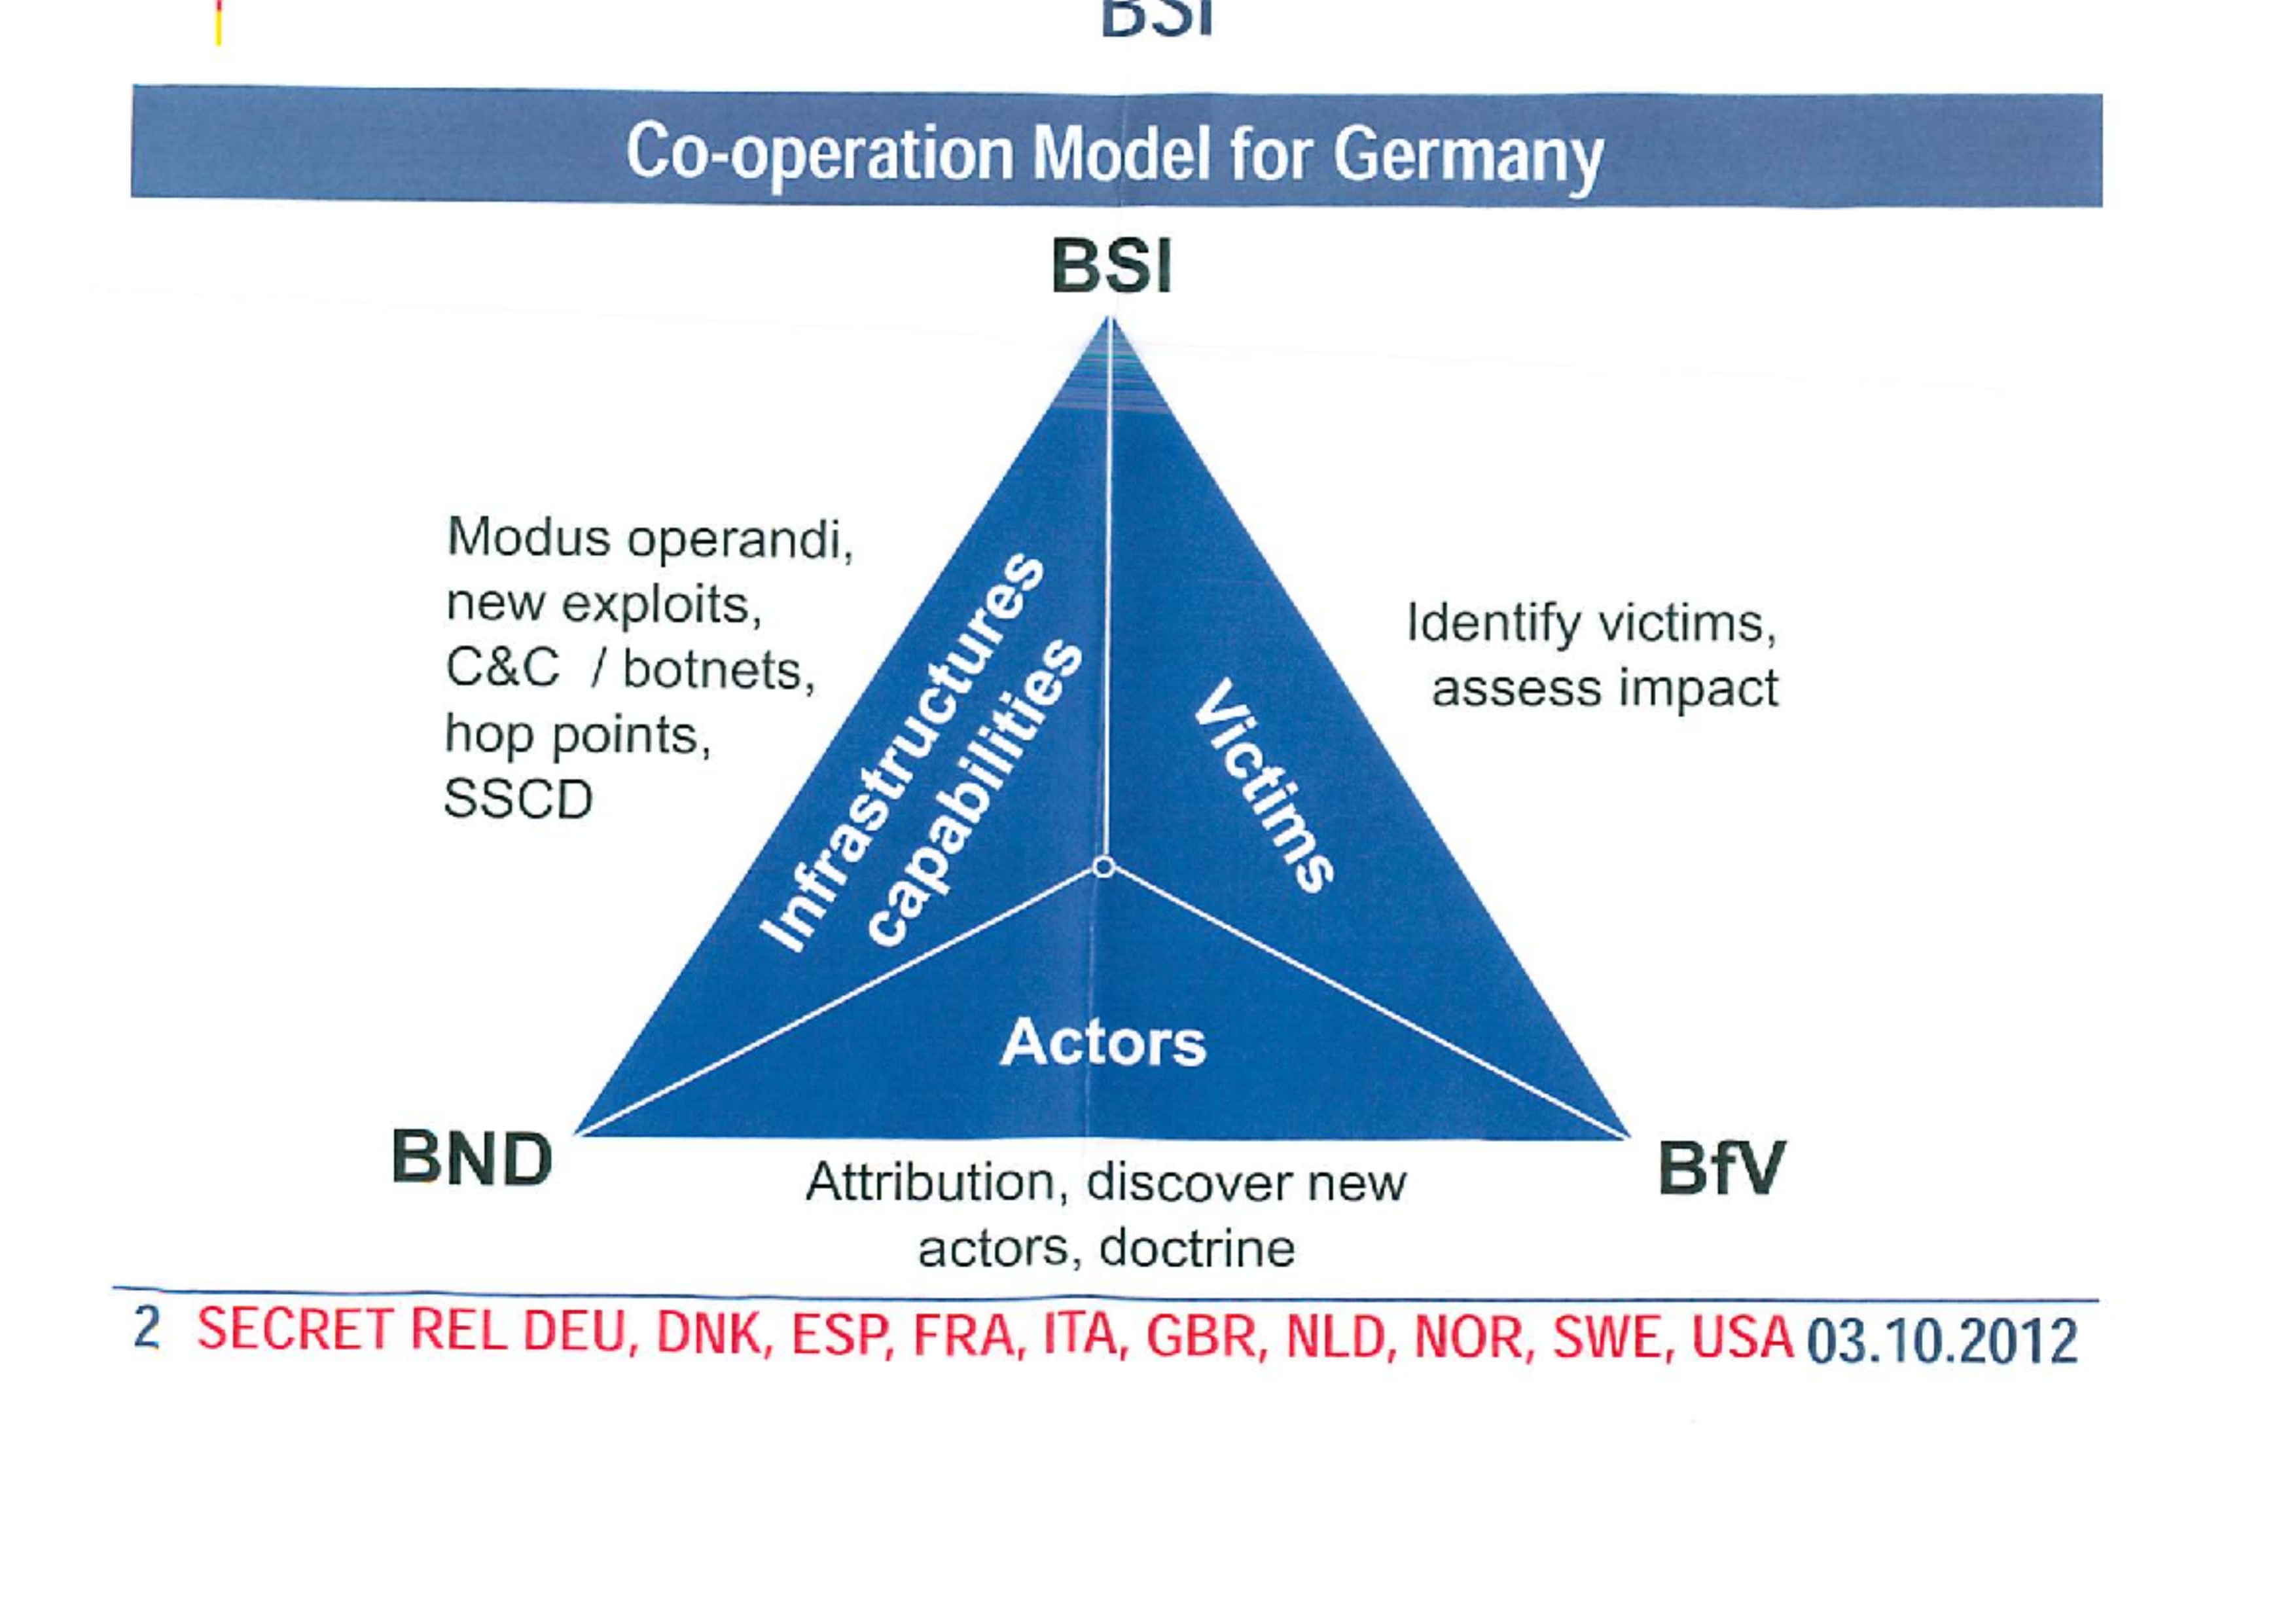
BSI
Co-operation Model for Germany
BSI
- Infrastructures capabilities
- Modus operandi, new exploits, C&C / botnets, hop points, SSCD
- Victims
- Identify victims, assess impact
- Actors
- Attribution, discover new actors, doctrine
BND
BfV
2 SECRET REL DEU, DNK, ESP, FRA, ITA, GBR, NLD, NOR, SWE, USA 03.10.2012
Published in the Same Report
(10 of 27 documents)
-
SID Around the World: The Rheinland SIDtoday [pdf]
An NSA couple worked at locations in Germany’s Rheinland and enjoyed local cuisine and European travel.
“The NSA in Germany: Snowden's Documents Available for Download” - Der Spiegel ↗ (2014-06-18) · The Intercept ↗ (2016-05-16) -
European Security Center to Begin Operations SIDtoday [pdf]
SIGINT operations in support of U.S. Army Europe and European Command will start at a facility in Darmstadt, Germany, in April 2004.
Marking: SECRET“The NSA in Germany: Snowden's Documents Available for Download” - Der Spiegel ↗ (2014-06-18) · The Intercept ↗ (2016-12-07) -
A Little Bad Aibling Nostalgia SIDtoday [pdf]
With the closing of Bad Aibling Station in Germany, some BA veterans post a list of nostalgic recollections from working there.
“The NSA in Germany: Snowden's Documents Available for Download” - Der Spiegel ↗ (2014-06-18) · The Intercept ↗ (2016-12-07) -
Forward Production at NCEUR — Inside the Customers' Decision Space SIDtoday [pdf]
Beginning in 2003, a team of NSA counterterrorism analysts based at NSA/CSS Europe began a dedicated project to support counterterrorism efforts in North Africa. The team collected signals intelligence, which they distributed to U.S. European Command and U.S. ambassadors, who then transmitted this information to governments in Mali, Algeria, and Mauritania. They believe this effort was "responsible for the capture or kill of over 40 terrorists."
“The NSA in Germany: Snowden's Documents Available for Download” - Der Spiegel ↗ (2014-06-18) · The Intercept ↗ (2017-09-13) -
On the Road Again: SID Team Visits Germany SIDtoday [pdf]
A Signals Intelligence Directorate team visits NSA sites in Germany.
Marking: CONFIDENTIAL“The NSA in Germany: Snowden's Documents Available for Download” - Der Spiegel ↗ (2014-06-18) · The Intercept ↗ (2018-08-15) -
European Technical Center Area Checked for Unexploded WWII Ordnance SIDtoday [pdf]
The European Technical Center area in Mainz, Germany, was closed for a day while investigators checked what seemed to be — but wasn’t — unexploded Word War II ordnance.
“The NSA in Germany: Snowden's Documents Available for Download” - Der Spiegel ↗ (2014-06-18) · The Intercept ↗ (2018-08-15) -
German, NSA SIGINTers Share DNI Processing Knowledge SIDtoday [pdf]
A delegation from Germany’s Federal Intelligence Service visits Fort Meade, Maryland, to learn about the NSA’s “packet level” selection and filtering of internet-based traffic, which is opposite to the approach used by the Germans.
“The NSA in Germany: Snowden's Documents Available for Download” - Der Spiegel ↗ (2014-06-18) · The Intercept ↗ (2018-08-15) -
The European Security Center to Become the 'ESOC' SIDtoday [pdf]
The European Security Center in Darmstadt, Germany will expand to become the European Security Operations Center; additional civilian NSA staff will join existing Army staff. The ESOC's primary responsibilities will be targets in Africa.
“The NSA in Germany: Snowden's Documents Available for Download” - Der Spiegel ↗ (2014-06-18) · The Intercept ↗ (2019-05-29) -
NSAers Make First-Ever Visit to FORNSAT Collection Site in Schöningen, Germany SIDtoday [pdf]
The BND (German Federal Intelligence Service) has a base at Schoningen, where they collect different types of mobile communications (satellite, fax, and GSM), many of which they share with their NSA counterparts. NSA visited to compare notes, and requested copies of some of the Germans' software tools--which had "features that surpass US SIGINT capabilities--for call chaining and metadata analysis.
“The NSA in Germany: Snowden's Documents Available for Download” - Der Spiegel ↗ (2014-06-18) · The Intercept ↗ (2019-05-29) -
BOUNDLESSINFORMANT Overview [pdf]
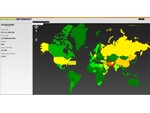
World map view from the Boundless Informant program, with "CNE" (Computer Network Exploitation) selected from the dropdown.
Programs: BOUNDLESSINFORMANT
Related Documents
-
Cooperation between the NSA and BND [pdf]
Comprehensive internal summary of the history and current state of cooperation between the NSA and BND
Programs: RT-RGPeople: Schindler, Gerhard -
Sharing Computer Network Operations Cryptologic Information with Foreign Partners [pdf]
The document is a secret NSA/CSS policy outlining guidelines for sharing Computer Network Operations (CNO) cryptologic information with foreign partners, including rules for cooperation in CNE and CND within existing intelligence relationships. The “Purpose and Scope” section on the first page appears to be unpublished elsewhere, while the Tier A and Tier B country lists match those publicly revealed in sources like Glenn Greenwald’s No Place to Hide.
“El CNI facilitó el espionaje masivo de EEUU a España” - El Mundo ↗ (2013-10-30) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Greenwald, Glenn · Aranda, Germán -
Sentry Eagle Brief Sheet [pdf]
A classified NSA/JFCC-NW briefing document formally inducting cleared personnel into Sentry Eagle — the agency's most sensitive umbrella program protecting core secrets about its cyber operations — and enumerating, tier by tier, what the NSA conceals about its covert industry partnerships, encryption sabotage, network hacking, computer network defense, and human intelligence relationships.
Programs: SENTRYEAGLE · SPARECHANGE · WHIPGENIE · AUNTIE · AMBULANT · OPALESCE · REVELRY · REFRACTOR · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL · BLUESASH · TAREX -
HIDDENSALAMANDER - Alerting and Characterization of Botnet Activity in TURMOIL [pdf]
This NSA briefing describes HIDDENSALAMANDER, a TURMOIL component that detects, tracks, and characterizes botnet command-and-control traffic on passive collection sensors worldwide, generating enriched metadata about bot herders, infected machines, attack commands, and malware families while providing low-latency defensive alerts when botnet activity involves high-value targets or protected networks. The system extends beyond traditional signature matching by decrypting Zeus RC4-encrypted traffic, extracting payload details like target IPs and DDoS commands, tracking C2 servers across multiple sessions, and categorizing botnet lifecycle stages (configuration, infection, reconnaissance, C&C communication, attack, exfiltration) to support both offensive attribution and defensive response.
Programs: HIDDENSALAMANDER · TURMOIL · CLOUDSHIELD · NETEZZA · TUTELAGE · GMPLACE · RONIN · CYBERCLOUD · MARINA · GHOSTMACHINE · QBOT · ASDF · MARIPOSA · XKEYSCORE · GOGADGET · TURQI · TRAFFICTHIEF · FALLOUT · POUNDSAND · BLUESMOKE · AEG · TURNABOUT · QUANTUMBOT -
Getting Close to the Adversary – Forward-based Defense with QFIRE (June 3, 2011) [pdf]
This document describes the QFIRE project which is designed to give the NSA a global, low-latency platform for “forward-based defense”, enabling real-time detection and manipulation of Internet traffic close to its source. By co-locating passive sensors (TURMOIL), decision logic (TURBINE), and injection capabilities, QFIRE can rapidly reset connections, redirect targets for exploitation, inject malicious payloads, and even seize control of botnets. It operates as part of the broader QUANTUMTHEORY architecture, leveraging both cooperative and non-cooperative infrastructure worldwide to enable CNE/CND/CNA effects with minimal delay.
Programs: QFIRE · QUANTUMTHEORY · TURBULENCE · TURMOIL · TURBINE · TUTELAGE · QUANTUM · QUANTUMSKY · QUANTUMINSERT · QUANTUMBOT · QUANTUMCOPPER · STRAIGHTBIZARRE · BLINDDATE · TUMULT · ISLANDTRANSPORT · SURPLUSHANGAR · MIDDLEMAN · SCSnet · WEALTHYCLUSTER · SSO