Publication year: 2014 265 documents
Search documents matching “2014” →When a publisher first published each document. If a document is published multiple times, only the oldest one is used here.
Graphs
By document date (12 years)
By published date (4 years)
Sort: Title
Documents
-
Elegant Chaos: collect it all, exploit it all [pdf]
This document outlines a classified project, "Elegant CHAOS," focused on advanced signals intelligence (SIGINT) collection, processing, and analysis using cutting-edge technologies like automated surveys and modems. It highlights goals such as real-time data analysis, collaboration with international partners, and integration with cloud-based platforms to manage massive data. See also the document with notes (by GCHQ): "Elegant-Chaos-collect-it-all-exploit-it-all-plus"
Programs: ELEGANTCHAOS · ASPHALT · ASPHALT-A · ASPHALT-A-PLUS · STORMFORCE · DARKQUEST · TORUS · XKEYSCORE · MHS CLOUD · TURMOIL · TARMAC · ASDF · SLR · POPQUIZ · WEALTHYCLUSTER2 · TRAVELLINGWAVE · BILBOBADGER · DRINKYBIRD · GLOBETROTTER · MASTERSHAKE · REST · TRAFFICTHIEF · VENUSAFFECT · FOGHORN · MATCHMAKER · ROADBED · MOONPENNY · AMULETSTELLAR · CLOUD · WEALTHYCLUSTER · MVR · TINT · IPGEOTRAP · MARINA · PLUS -
Email Address vs User Activity [pdf]
This 2009 NSA training presentation explains how to use the XKEYSCORE system to search raw SIGINT, detailing the differences between the "Email Address" query, which finds email addresses in full content, and the more flexible "User Activity" query, which can search for selectors like cookies, usernames, and phone numbers.
“XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Marquis-Boire, Morgan · Greenwald, Glenn · Lee, Micah -
ESOC: Report on the experiences of one NSA worker [pdf]
A NSA intelligence analysis intern details their 2007 temporary assignment to the European Security Operations Center (ESOC), where they successfully established a new signals intelligence (SIGINT) mission targeting Angola's energy sector. The author describes the end-to-end process from initial research and target development to successful collection and the first intelligence product.
-
Exceptionally Controlled Information Compartments (January 2013) [pdf]
This document, dated January 2013, provides a list of Exceptionally Controlled Information (ECI) compartments utilized by the NSA and its Five Eyes partners. This document categorizes highly sensitive intelligence programs by their codenames, three-letter trigraphs, and the specific organizations responsible for them. The primary organizations listed include TAO, NCSC, and CES. These compartments represent the highest level of information security, designed to restrict access to sensitive technical data and specific intelligence sources even among individuals with high-level security clearances.
Programs: AMBULANT · APERIODIC · AUNTIE · BLACKANT · BLACKAXE · BLACKBALL · BLACKCLOUD · BLACKHOLE · BLACKJACK · BLACKTIE · BLACKVULTURE · BLACKWIDOW · BOXWOOD · CELESTIALGLOBE · CHIEFDOM · CLICKUMBER · CRIMSONREGENT · CRIMSTONSTEAL · CRUMPET · DECKSTOP · DEVILFISH · DIXIESPRING · DOMINATE · FASTIDIOUS · FIRESCREEN · FIRSTDOWN · FISSURESALUTE · FLYLEAF · FORBIDDEN · FORBORNE · FOXHEAT · FREELUNCH · FROTHYTWOPACK · FURTIVERELIANCE · GOLDENCALF · HELLFIRE · HISTORY · HYSSOP · INVEIGH · KESSELRUN · LIGHTNINGTHIEF · LITTLECROWN · LONGSERPENT · MAGICSTROKE · MERCURYTAO · MUSICBOX · NITEHAWK · OCELLUS · PAINTEDEAGLE · PAWLEYS · PAWNSHOP · PENDLETON · PENDRAGON · PERKYAUTUMN · PHENYLDOUR · PICARESQUE · PICAROON · PIEDMONT · PITCHFORD · PLACEBO · POMPANO · PRESSURETWIN · REDHARVEST · REEFPOINT · REFRACTOR · REVELRY · RIVERROAD · RUBIOUS · SAILWINDS · SCABBARD · SILVERCLOUD · SINKGOAL · STAIRWELL · STARCHART · SUITESWIVEL · TRICKSHOT · WAXOFF · WHIPGENIE -
Expanding PRISM Sharing With FBI and CIA [pdf]
An SSO item describing two projects that widened PRISM sharing with the FBI and CIA: PRINTAURA software that compiles the tasked-selector list every two weeks for both agencies, and weekly operational PRISM news and guidance from the mission programme manager.
-
Exploiting Facebook traffic in the passive environment to obtain specific information [pdf]
A GCHQ Global Telecommunications Exploitation presentation on extracting information about Facebook users from passively collected traffic: why online social networks are a rich source, how Facebook's use of the Akamai content delivery network exposes a user's ID inside image URLs, and how profile and album images are then obtained through SPRING BISHOP, GODFATHER and JTRIG.
-
FAD FY 12 CCP Funding of Partners [pdf]
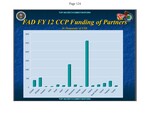
A Foreign Affairs Directorate slide showing Combined Cryptologic Program funding of foreign partners in fiscal year 2012, in thousands of dollars, across fifteen countries including Canada, Israel, Japan, Jordan, Pakistan, Taiwan and Thailand.
-
FAIRVIEW - Corp partner since 1985 [pdf]
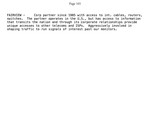
1 p.A note describing FAIRVIEW as a corporate partnership dating to 1985 that gives access to international cables, routers and switches through a US company which is also “aggressively involved in shaping traffic to run signals of interest past our monitors”.
Programs: FAIRVIEW -
Ferguson NSA Visit Précis [pdf]
This internal NSA "Visit Précis" from March 2013 details a high-level courtesy call between Ambassador Roy Ferguson of New Zealand and the Director of the NSA. The meeting's primary objective was to discuss proposed legislative changes to New Zealand’s intelligence community, focusing on increased oversight in the wake of public controversies.
Programs: FIRSTLIGHTPeople: Ferguson, Roy · Cusick, James M. · Inglis, Chris · Fleisch, Fran · Kagan, Edgard · Wolfenson, Hugh · Dotcom, Kim · Alexander, Keith B. -
Final Agenda - HR DIETMAR B - Director SIGINT Analysis and Production German Federal Intelligence Service, 30 April - 1 May 2013 [pdf]
This document presents the final agenda for a visit by Hr. Dietmar B., the Director of SIGINT Analysis and Production from the German Federal Intelligence Service (BND), scheduled for April 30 to May 1, 2013. The agenda details key discussions and meetings with various officials from the NSA, focusing on strategic planning and areas of mutual interest in intelligence collaboration.
-
FISA Amendments Act of 2008 Section 702 summary document [pdf]
This document summarizes the way the law works and describes the three types of certifications used to permit the surveillance, as well as targeting and minimization procedures. The three certification are for foreign governments, counterterrorism and WMD/proliferation.
-
FISA dataflow [pdf]
This document describes the technical SIGINT architecture for FISA data processing, specifically detailing how the RAGTIME/SQF partition and PALMCARTE system utilize unique case notations and metadata tools to route and track intercepted communications.
-
FISA judge's order authorizing surveillance of foreign governments and organizations [pdf]
With this order dated Aug. 19, 2010, John D. Bates, then-Chief Judge of the Foreign Intelligence Surveillance Court, approved an annual certification permitting the National Security Agency to conduct surveillance about 193 foreign governments, foreign factions, foreign-based political organizations and foreign entities such as the World Bank. Each year, a new certification must be approved by the court to permit such surveillance under Section 702 of the FISA Amendments Act.
Marking: SECRETPeople: Bates, John D. -
FISA recap [pdf]
This document is a Top Secret NSA "FISA Recap" spreadsheet detailing electronic surveillance conducted between 2005 and 2008. It tracks specific email accounts targeted under the Foreign Intelligence Surveillance Act, listing the responsible agencies (NSA, FBI, and CIA), their legal "Case Notation," and the duration of collection. Notably, the log includes prominent U.S. Persons and organizations, such as the Council on American-Islamic Relations (CAIR), and features a 2005 formatting guide that uses a racial slur as a placeholder for a target's identity.
Programs: SQF -
FOXACID Overall Briefing [pdf]
FOXACID is the NSA's exploit server infrastructure designed to gain "initial access" to target computers by tricking them into visiting malicious websites through spam emails, man-in-the-middle attacks, or split-second packet injection techniques that redirect legitimate web traffic. The document reveals how the agency has evolved from low-success spam operations (less than 1% success rate) to sophisticated "QUANTUM" techniques that achieve up to 80% success rates by exploiting web browsers through services like Yahoo and Facebook, allowing the NSA to compromise any target whose web traffic passes through monitored network chokepoints—with the chilling assessment that "if we can get the target to visit us in some sort of web browser, we can probably own them."
Programs: FOXACID · WILLOWVIXEN · GENUINEDRAFT · SECONDDATE · QUANTUMTHEORY · TURMOIL · TURBINE · WEBSNIPER · QUANTUMINSERT · QUANTUMBISCUIT · QUANTUMDIRK · QUANTUM · VALIDATOR · OLYMPUS · MISTYVEAL · SSO · STRAIGHTBIZARRE · ISLANDTRANSPORT -
Full-Spectrum Cyber Effects [pdf]
The leaked 2012 GCHQ JTRIG “Full-Spectrum Cyber Effects” presentation outlines the UK’s offensive cyber capabilities, detailing strategies to destroy, deny, degrade, disrupt, deceive, and influence targets across digital and physical domains. It describes a wide range of operations—from network attacks, spoofing, and psychological operations on social media to hotel surveillance (Royal Concierge), mobile tracking, and advanced vulnerability exploitation—demonstrating how GCHQ integrates cyber operations, intelligence, and information warfare on a global scale.
Programs: JTRIG · SALAMANCA · RADIUS · ROYAL CONCIERGE · BLACKHOLE · GUILTY SPARK · MIDDLESEX GREEN · PPF · HOTWIRE -
GALLANTWAVE [pdf]
NSA presentation describing GALLANTWAVE — a LONGHAUL capability for VPN decryption — specifically its scaling architecture to handle increased collection volumes and a peering mechanism allowing partner agencies to share single-sided VPN key exchange events so that LONGHAUL can complete decryption attempts that would otherwise fail due to one-sided collection.
-
GCHQ - DISRUPTION Operational Playbook [pdf]
A JTRIG “Disruption Operational Playbook” outlines GCHQ’s online covert action toolkit to discredit people and companies, manipulate narratives, and execute false flag, sting, and infiltration operations across targets. It’s a blunt handbook for the four D’s—deny, disrupt, degrade, deceive—translating psychological warfare into clickable tactics on social platforms and forums.
Programs: JTRIG -
GCHQ - OPTIC NERVE [pdf]
GCHQ’s OPTIC NERVE project built a web interface to display images from Yahoo webcam sessions captured via bulk, unselected interception, then used that stream for “proportionate” target discovery. The system sampled one frame every five minutes per feed, flagged the prevalence of nudity, and bolted on imperfect face-detection “censoring” alongside warnings about handling offensive material.
Programs: OPTICNERVE -
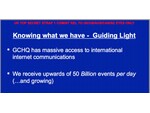
GCHQ access to international internet communications [pdf]
This document describes the scale of the agency's access to international internet communications, stating that GCHQ receives upwards of 50 billion events per day and that this volume is growing.
Programs: GUIDINGLIGHT“The US/UK Campaign to Demonize Social Media Companies as Terrorist Allies” - The Intercept ↗ (2014-11-26) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Greenwald, Glenn