FISA dataflow
Open PDFDocument date: -
Pages: 1
Genre: slides
Classification: -
Dissemination: -
This document describes the technical SIGINT architecture for FISA data processing, specifically detailing how the RAGTIME/SQF partition and PALMCARTE system utilize unique case notations and metadata tools to route and track intercepted communications.
My notes
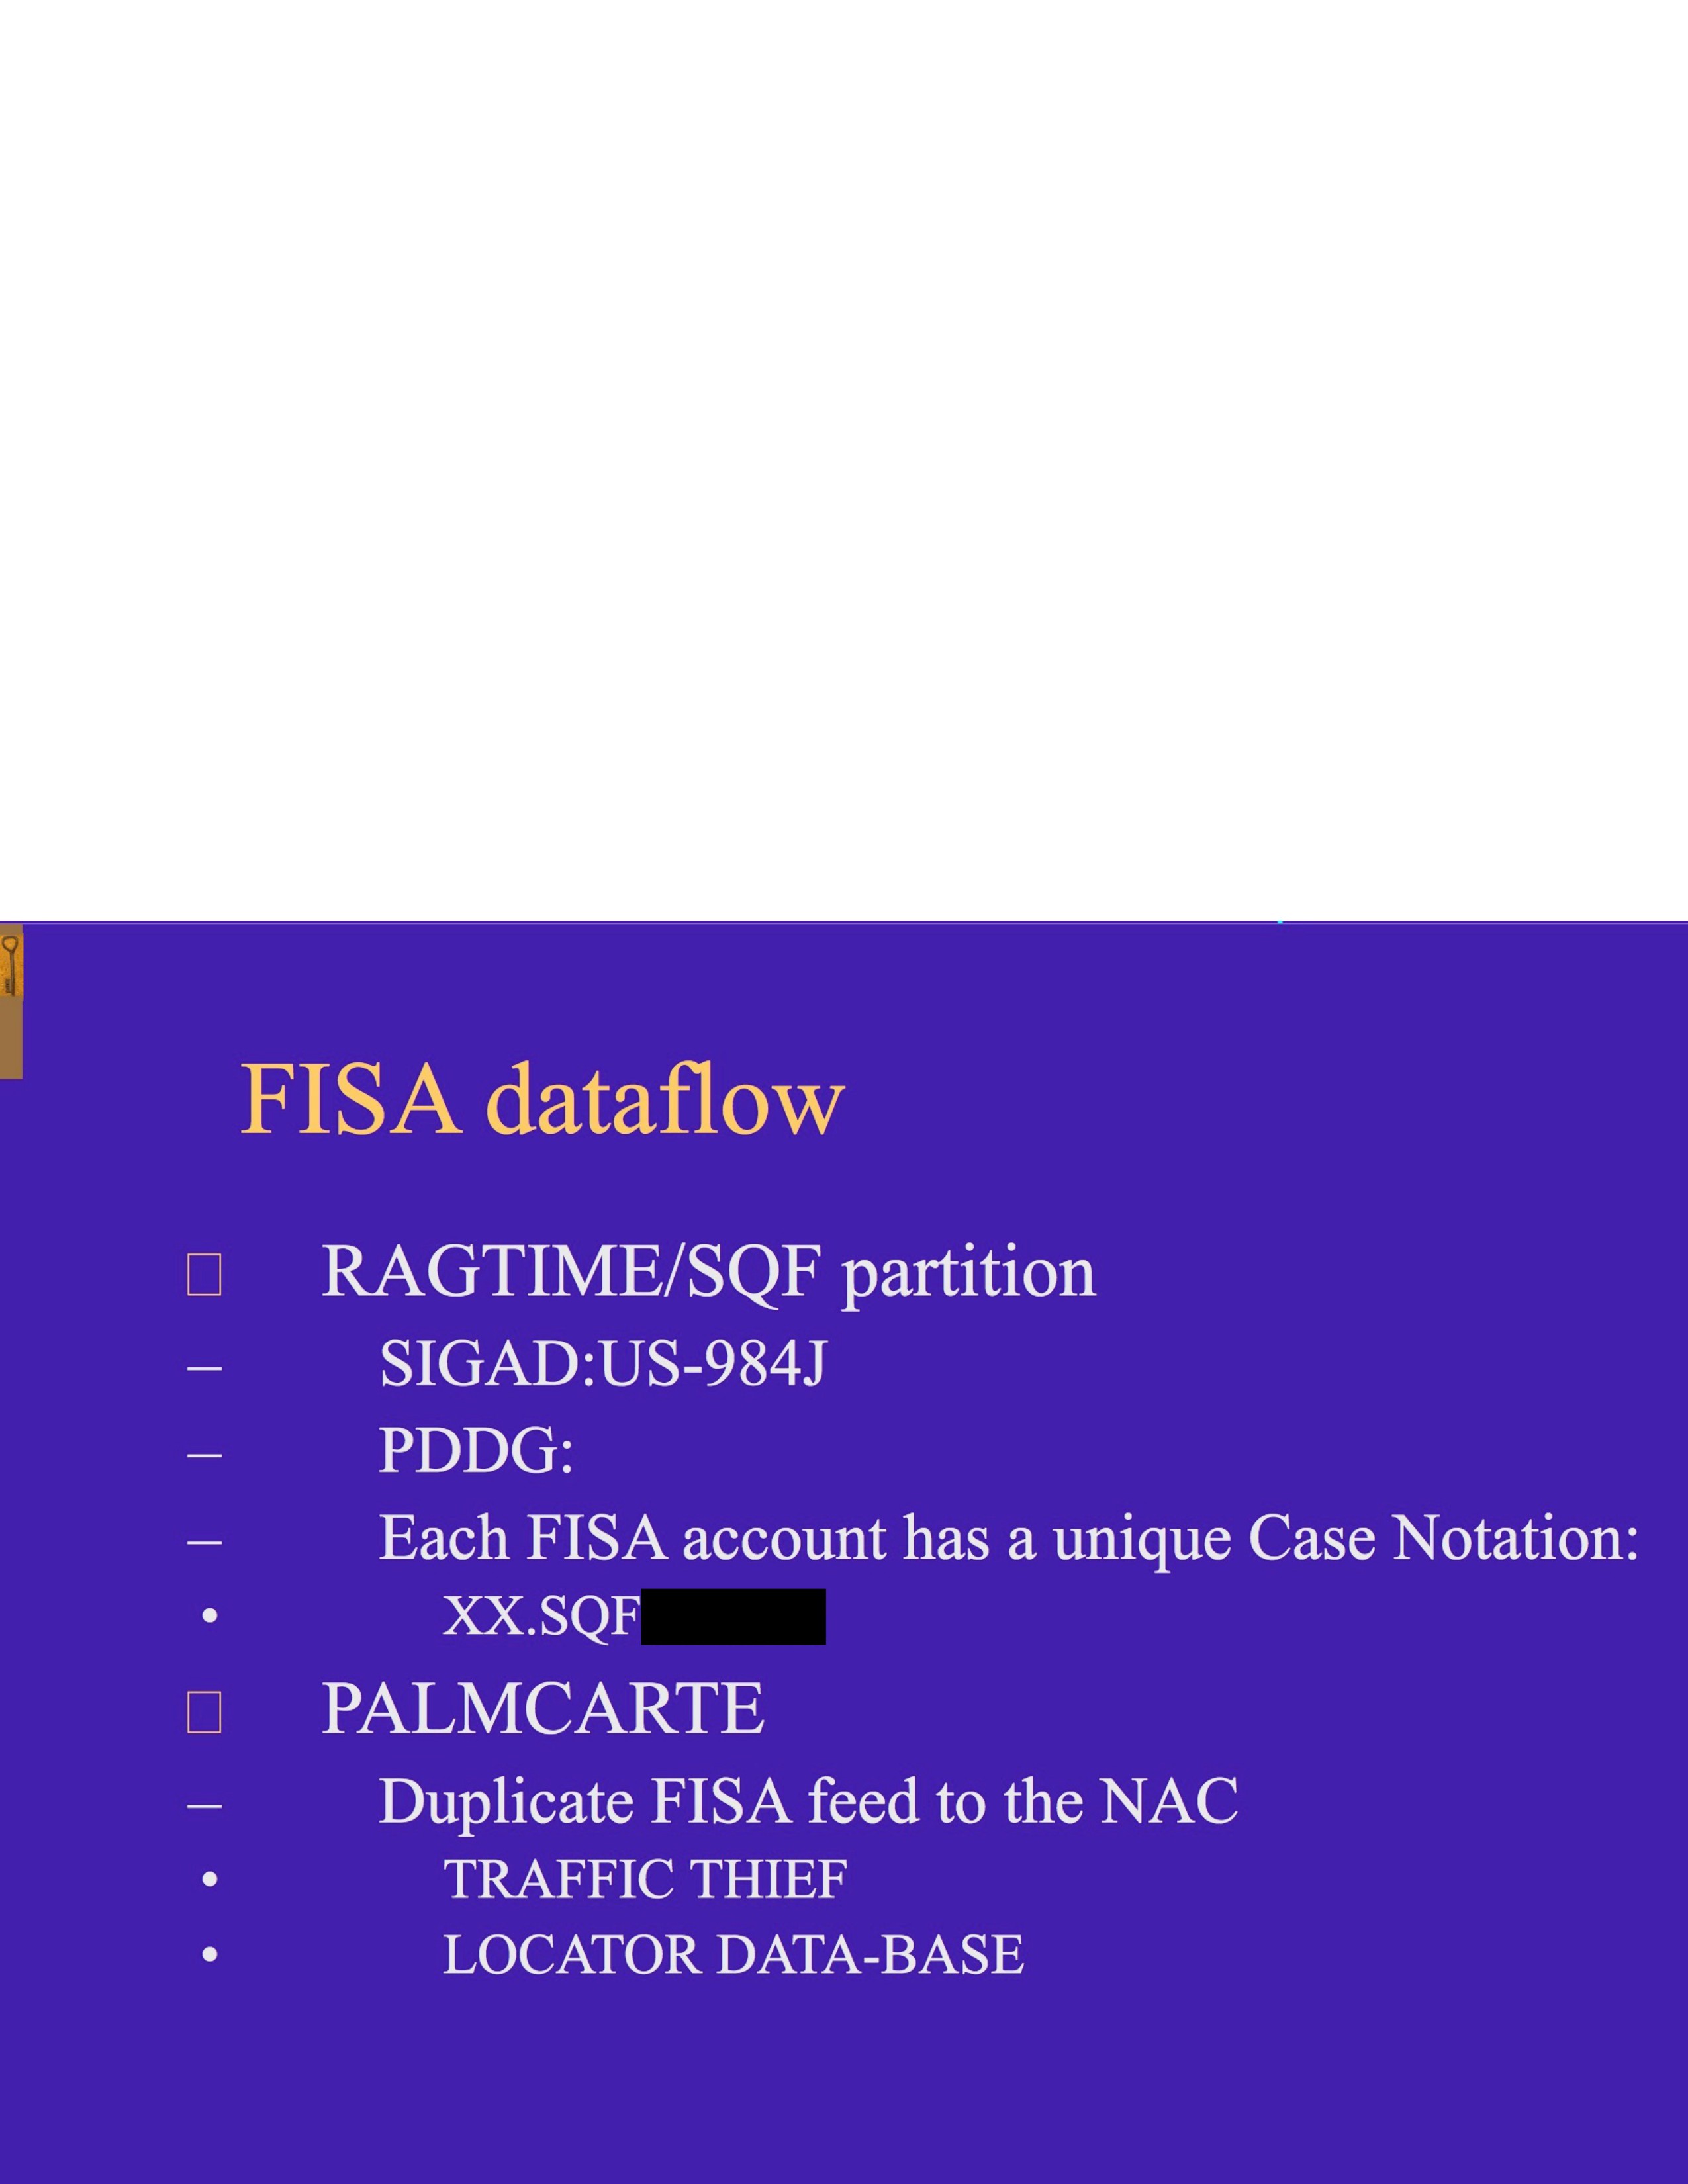
FISA dataflow
- RAGTIME/SQF partition
- SIGAD:US-984J
- PDDG:
- Each FISA account has a unique Case Notation:
- XX.SQF[REDACTED]
- PALMCARTE
- Duplicate FISA feed to the NAC
- TRAFFIC THIEF
- LOCATOR DATA-BASE
- Duplicate FISA feed to the NAC
Published in the Same Report
(1 documents)
-
FISA recap [pdf]
This document is a Top Secret NSA "FISA Recap" spreadsheet detailing electronic surveillance conducted between 2005 and 2008. It tracks specific email accounts targeted under the Foreign Intelligence Surveillance Act, listing the responsible agencies (NSA, FBI, and CIA), their legal "Case Notation," and the duration of collection. Notably, the log includes prominent U.S. Persons and organizations, such as the Council on American-Islamic Relations (CAIR), and features a 2005 formatting guide that uses a racial slur as a placeholder for a target's identity.
Programs: SQF
Related Documents
-
PINWALE: Transnational DNI Training [pdf]
This presentation is a classified NSA training guide on PINWALE, a SIGINT database used for the storage, retrieval, and analysis of intercepted digital network intelligence (DNI) communications. It outlines system capabilities, query creation, search tools, and interfaces such as NEXUS, UIS, and AGILITY, explaining how analysts search, retrieve, and analyze both content and metadata — including FISA-partitioned data — within the Five Eyes intelligence framework.
-
FISA recap [pdf]
This document is a Top Secret NSA "FISA Recap" spreadsheet detailing electronic surveillance conducted between 2005 and 2008. It tracks specific email accounts targeted under the Foreign Intelligence Surveillance Act, listing the responsible agencies (NSA, FBI, and CIA), their legal "Case Notation," and the duration of collection. Notably, the log includes prominent U.S. Persons and organizations, such as the Council on American-Islamic Relations (CAIR), and features a 2005 formatting guide that uses a racial slur as a placeholder for a target's identity.
Programs: SQF -
PRISM/US-984XN Overview [pdf]
A 2013 NSA training presentation revealing that major U.S. tech companies — including Google, Facebook, Apple, Microsoft, and Skype — secretly gave the NSA direct access to their servers, allowing the agency to collect users' emails, chats, photos, and files in real time, with the FBI acting as intermediary.
Programs: PRISM · FAIRVIEW · STORMBREW · BLARNEY · OAKSTAR · UTT · PRINTAURA · PINWALE · NUCLEON · TRAFFICTHIEF · SCISSORS · MARINA · MAINWAY · FALLOUT · CONVEYANCE · REPRISMFISA · SSO“U.S., British intelligence mining data from nine U.S. Internet companies in broad secret program” - The Washington Post ↗ (2013-06-06) · “NSA Prism program taps in to user data of Apple, Google and others” - The Guardian ↗ (2013-06-07) · “L'ampleur de l'espionnage mondial par la NSA” - Le Monde ↗ (2013-10-21) · “NSA files decoded: Edward Snowden's surveillance revelations explained” - The Guardian ↗ (2013-11-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “Dark Mirror: Edward Snowden and the American Surveillance State” - Penguin Press ↗ (2020-05-19) · Gellman, Barton · Poitras, Laura · Greenwald, Glenn · MacAskill, Ewen · Untersinger, Martin · Dance, Gabriel -
FAIRVIEW dataflow charts April 2012 [pdf]
This document outlines data flow diagrams that show how various types of sensitive communication, including voice, fax, and modem traffic, are handled through systems operated by the NSA and its partners. These partners include corporations, telecommunications companies, ISPs, and other entities involved in processing and managing the data through secure and classified channels. The document covers processing flows for various data types, metadata, and communications systems under NSA's control, detailing how data is routed, stored, and analyzed across different platforms and sites.
Programs: FAIRVIEW · SAGUARO · TURNSTILE · MESA · TITANPOINT · RIMROCK · MAILORDER · PINECONE · BLARNEY · STONEGATE · TINSEL · CONVEYANCE · FISHWAY · NUCLEON · PINWALE · SCISSORS · COURIERSKILL · DRIFTWOOD · ASDF · FALLOUT · MARINA · LOPERS · WEALTHYCLUSTER · PUPR · CLEARSIGHT · MIDFIELD · CADENCE · BUGCATCHER · WAYLAND · DESOTO · GATEKEEP · HIGHDECIBEL · XKEYSCORE · YANKEE · TOPROCK · FASCIA · DISHFIRE · SEAGULL · BIGDIPPER · CORPORATE · LILDIPPER · HAVASU · WEALTHYCLUSTER2 · RAGTIME · TUMULT · TATTOO · DARKTHUNDER · ICYTWINS · TML-STATUS · WATERFRONT · VULCANDEATHGRIP · STEELFLAUTA · UNITY · KEYCARD · UTT · BTUBE · ISLANDTRANSPORT · SSO · MAINWAY · SSDM · TUBE · TITANPOINTE · TURMOIL · VPCS“NSA Spying Relies on AT&T’s ‘Extreme Willingness to Help’” - ProPublica ↗ (2015-08-15) · “AT&T Helped U.S. Spy on Internet on a Vast Scale” - The New York Times ↗ (2015-08-15) · “Titanpointe: The NSA’s Spy Hub in New York, Hidden in Plain Sight” - The Intercept ↗ (2016-11-16) · Angwin, Julia · Larson, Jeff · Savage, Charlie · Moltke, Henrik · Poitras, Laura · Risen, James · Gallagher, Ryan -
FISA: Teaming with the FBI in the Global War on Terrorism SIDtoday [pdf]
The author describes being the first NSA employee integrated into the FBI unit responsible for the bureau’s data collected under the Foreign Intelligence Surveillance Act at the Digital Intercept Technology Unit at Quantico. The author is included in meetings with the “data providers.” Time-sensitive information from the FISA collection is sent to the NSA in a constant flow and provides up to 40 percent of the NSA’s counterterrorism reporting.
“NSA Secretly Helped Convict Defendants in U.S. Courts, Classified Documents Reveal” - The Intercept ↗ (2017-11-30) · The Intercept ↗ (2018-03-01) · Aaronson, Trevor