Publication year: 2014 265 documents
Search documents matching “2014” →When a publisher first published each document. If a document is published multiple times, only the oldest one is used here.
Graphs
By document date (12 years)
By published date (4 years)
Sort: Title
Documents
-
RECEIPT OF FUNDS [pdf]
In 2003 and 2004, the Israelis were pressuring the NSA to agree to a massively expanded intelligence-sharing relationship called “Gladiator.” As part of that process, Israel wanted the Americans to pay hundreds of millions of dollars to fund Israeli activities. The specific proposed “Gladiator” agreement appears never to have been consummated, derailed by Israeli demands that the U.S. bear the full cost, but documents in the Snowden archive pertaining to those negotiations contain what appear to be two receipts for one or more payments of $500,000 in cash to Israeli officials for unspecified purposes.
Programs: GLADIATOR -
Regions [pdf]
A classified GCHQ document listing 63 undersea and terrestrial cables accessible to British intelligence, with landing locations across the UK coastline and capacity figures in gigabits per second, forming part of the Snowden archive documents published by Süddeutsche Zeitung revealing Cable & Wireless/Gerontic's cooperation with GCHQ.
“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
Report about Operation Doody - The Child of the Neighbor Shot By Accident [pdf]
This Dynamic Target Storyboard documents a 7 Feb 2011 UK AH‑64 engagement (Op STEN TAKAY) against “Obj DOODY” (Mullah Niaz Muhammed, IS3673), a JPEL mid‑level Taliban commander, which culminated in an AGM‑114 miss that may have killed a local child and wounded another civilian, and a follow‑on 30mm strafing run that wounded the target.
People: Muhammed, Mullah Niaz -
Research & Technology – Penetrating Hard Targets [pdf]
The NSA’s “Penetrating Hard Targets” program aims at developing a cryptologically useful quantum computer capable of breaking strong encryption systems, including those protecting global financial and government communications. Conducted under the U.S. intelligence “black budget,” the program focuses on quantum physics research, engineering studies, and experimental milestones such as achieving dynamical decoupling and quantum control on semiconductor qubits, which are foundational for scaling to larger systems. A related initiative, “Owning the Net,” explores quantum communication technologies to develop new Quantum Key Distribution (QKD) attacks and assess the security of emerging encryption methods.
-
Running Strategic Analytics Affecting Europe and Africa [pdf]
This Top Secret presentation from the NSA ECC (European Cryptologic Center) outlines the strategic challenges and technical methodology for conducting signal intelligence operations across Europe and Africa. It emphasizes a critical reliance on "Second Party" partnerships, particularly with the UK's GCHQ, and details the use of mass surveillance tools like XKEYSCORE to track terrorism, smuggling, and human trafficking networks.
Programs: XKEYSCORE · RTRG · DISTILLERY · CLOUD · GHOSTMACHINE · NIAGARAFILES · WHIZBANG · MAPREDUCE -
SCARLETFEVER [pdf]
NSA WikiInfo page describing SCARLETFEVER — the second LONGHAUL cryptanalytic capability, a message-driven cryptologic exploitation service for DNSC (Data Network Session Cipher) traffic serving clients including TURMOIL, WEALTHYCLUSTER and the TEe, communicating via ISLANDTRANSPORT with ISLANDHIDEAWAY encryption.
Programs: SCARLETFEVER · LONGHAUL · TURMOIL · WEALTHYCLUSTER · TEE · ISLANDTRANSPORT · ISLANDHIDEAWAY · POISONNUT · PICARESQUE -
Secure Sockets Layer (SSL) / Transport Layer Security (TLS) [pdf]
A classified NSA Network Security Products training presentation providing a comprehensive technical overview of SSL/TLS protocol mechanics and NSA's exploitation approaches, including observed usage statistics from intercepted traffic, RSA key exchange decryption methodology, exploitation of the Debian OpenSSL RNG weakness, and the practical challenges of decrypting millions of SSL sessions per day at scale.
Programs: SCARLETFEVER -
Sentry Eagle Brief Sheet [pdf]
A classified NSA/JFCC-NW briefing document formally inducting cleared personnel into Sentry Eagle — the agency's most sensitive umbrella program protecting core secrets about its cyber operations — and enumerating, tier by tier, what the NSA conceals about its covert industry partnerships, encryption sabotage, network hacking, computer network defense, and human intelligence relationships.
Programs: SENTRYEAGLE · SPARECHANGE · WHIPGENIE · AUNTIE · AMBULANT · OPALESCE · REVELRY · REFRACTOR · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL · BLUESASH · TAREX -
Serving our customers [pdf]
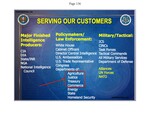
A briefing slide listing NSA's customers: the finished-intelligence producers (CIA, DIA, State/INR, NGA and the National Intelligence Council), policymakers and law enforcement from the White House to Congress and seven departments, and military users from the Joint Chiefs to NATO and UN forces.
-
Sharing Communications Metadata Across the U.S. Intelligence Community - ICREACH [pdf]
ICREACH is a "one-stop shopping" tool and federated query architecture that allows thousands of analysts across 23 U.S. agencies to search billions of communications metadata records. It consolidates telephony and digital network intelligence (DNI) from various sources—including NSA holdings, Second Party (Five Eyes) partners, and other IC databases like the CIA/FBI's PROTON—into a single, searchable interface. At its launch, the system increased shared metadata records from 50 billion to over 850 billion.
“How the NSA Built Its Own Secret Google” - The Intercept ↗ (2014-08-25) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Gallagher, Ryan · Greenwald, Glenn -
SHELLTRUMPET Processes its One Trillionth Metadata Record [pdf]
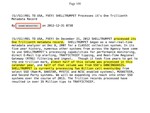
An SSO news item announcing that SHELLTRUMPET processed its one-trillionth metadata record on 21 December 2012 — almost half of that volume in 2012 alone — feeding TRAFFICTHIEF tipping and Real-Time Regional Gateway filtering from CLASSIC, DANCINGOASIS, RAMPART-M, OAKSTAR, MYSTIC, NCSC, MUSKETEER and Second Party systems.
Programs: SHELLTRUMPET · CLASSIC · TRAFFICTHIEF · RTRG · SSO · DANCINGOASIS · RAMPART-M · OAKSTAR · MYSTIC · NCSC · MUSKETEER -
SHENANIGANS operator SIDtoday [pdf]
A March 2013 TOP SECRET SIDToday article written by an operator of SHENANIGANS — an airborne NSA collection system carried on CIA drones — describing the VICTORYDANCE mission that mapped the Wi-Fi signature of nearly every major town in Yemen to geolocate the wireless devices of Al Qaeda in the Arabian Peninsula, including detail on the tool's operation and confirmation that NSA Washington, NSA Georgia, the Special Collection Service and the Utah Regional Operations Center provided SIGINT support to the 30 September 2011 strike that killed Anwar al-Awlaki.
Programs: SHENANIGANS -
Shift to Software Demodulation in Misawa Expands Collection, Saves Money SIDtoday [pdf]
This SIDtoday document details how the Misawa Security Operations Center (MSOC) has implemented a software demodulation system called WORDGOPHER to process low-data-rate satellite signals. This shift to software-based processing allows MSOC to increase SIGINT collection, save millions of dollars by reducing reliance on expensive hardware demodulators, and improve overall mission efficiency.
“Japan Made Secret Deals With the NSA That Expanded Global Surveillance” - The Intercept ↗ (2017-04-24) · “アメリカに監視される日本 ~スノーデン“未公開ファイル”の衝撃” - NHK ↗ (2017-04-24) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Gallagher, Ryan · Ikegami, Akira · Greenwald, Glenn -
SIGDEV Conference 2012 - Making Things Measureable: Technology Trending Challenges and Approaches [pdf]
An NSA presentation from the 2012 SIGDEV Conference describing NSA's technology trending methodology — a framework for identifying which encryption and communications technologies targets are adopting, measuring the SIGINT risk they pose, and prioritising capabilities development responses — notable for containing the risk matrix that was later cited in Der Spiegel's December 2014 encryption investigation showing NSA's difficulty levels against specific technologies including Tor, TrueCrypt, OTR and ZRTP.
Programs: XKEYSCORE · SEEKER · BIONICTURTLE · JEMA · JOLLYROGER · MARINA · TUNINGFORK · STARPROC · MICROEXPANSE · ECHOBASE · PRISM · GMHALO · UTT · TKB · LAE · FAMT · WPMO · AMOD · FORTREND · GAMBIT · DATAEXPLORER · MYNOC -
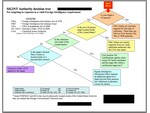
SIGINT Authority decision tree [pdf]
A one-page NSA training chart that walks an analyst from a targeting request to the legal authority that covers it, branching on whether the target is a US person, where the target is, where the collection site is, and whether the target is a Second Party citizen.
-
SIGINT Helps Hobble the Taleban by Cutting Off Their Livelihood SIDtoday [pdf]
This SIDtoday article (Feb 3, 2009) describes how SIGINT operations—led by NSA Georgia’s Southwest Asia Narcotics Division (FGS2F) with partners like NSAW and GCHQ—shifted counternarcotics efforts in Afghanistan from HUMINT to SIGINT, enabling real‑time targeting of traffickers and major seizures that disrupted Taliban funding. It credits SIGINT-driven support for large drug seizures, increased operational tempo, and the inclusion of traffickers on ISAF targeting lists.
-
SIGINT Strategy Threads 4 and 7 SIDtoday [pdf]
A TOP SECRET SIDToday article from September 2011 describing SIGINT Strategy Threads 4 and 7 — NSA's two classified programmes addressing the challenge of ubiquitous internet encryption — directing cleared analysts to BULLRUN-protected content covering capabilities against commercial webmail encryption used by CT targets and VPN traffic exploitation, with access requiring BULLRUN Community of Interest indoctrination.
-
SILVERZEPHYR FAA DNI Access Initiated at NSAW [pdf]
An SSO item on the OAKSTAR SILVERZEPHYR access beginning FAA DNI forwarding to NSAW on 5 November 2009 through a WealthyCluster2/Tellurian system at the partner's site, after a 12-day survey that identified over 200 new links, with snapshots examined from Brazil and Colombia.
-
SINIO Seminar: Turkish Presidential and Parliamentary Elections SIDtoday [pdf]
People: Erdoğan, Recep Tayyip“Turkey Is 'Partner and Target' for the NSA” - Der Spiegel ↗ (2014-08-31) · “How the NSA Helped Turkey Kill Kurdish Rebels” - The Intercept ↗ (2014-08-31) · Poitras, Laura · Rosenbach, Marcel · Sontheimer, Michael · Stark, Holger -
Slides Describe Mission Involving Huawei [pdf]
This document details an NSA-led strategic initiative to target Huawei due to its dominance in global telecommunications infrastructure. The operation (codenamed "Shotgiant") aims to exploit Huawei hardware to maintain access to target communications while investigating the company’s potential role in facilitating People’s Republic of China (PRC) signals intelligence and supply chain subversion.