Program: MARINA 56 documents
Search documents matching “MARINA” →Codenames and programs recorded for each document.
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
FASCIA: The NSA's huge trove of location records [pdf]
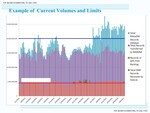
FASCIA is the National Security Agency's enormous database containing trillions of metadata records, many with device locations, that are collected from a variety of sources. This document shows the volume and types of device-location data collected by the agency.
“NSA tracking cellphone locations worldwide, Snowden documents show” - The Washington Post ↗ (2013-12-04) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Gellman, Barton · Soltani, Ashkan · Greenwald, Glenn -
Full Log vs HTTP [pdf]
This 2009 NSA training presentation explains the difference between using the "Full Log" and "HTTP Activity" queries in the XKEYSCORE surveillance system, showing analysts how to use both in tandem to gain a complete picture of a target's online activities, including identifying the use of anonymizing proxies.
-
HIDDENSALAMANDER - Alerting and Characterization of Botnet Activity in TURMOIL [pdf]
This NSA briefing describes HIDDENSALAMANDER, a TURMOIL component that detects, tracks, and characterizes botnet command-and-control traffic on passive collection sensors worldwide, generating enriched metadata about bot herders, infected machines, attack commands, and malware families while providing low-latency defensive alerts when botnet activity involves high-value targets or protected networks. The system extends beyond traditional signature matching by decrypting Zeus RC4-encrypted traffic, extracting payload details like target IPs and DDoS commands, tracking C2 servers across multiple sessions, and categorizing botnet lifecycle stages (configuration, infection, reconnaissance, C&C communication, attack, exfiltration) to support both offensive attribution and defensive response.
Programs: HIDDENSALAMANDER · TURMOIL · CLOUDSHIELD · NETEZZA · TUTELAGE · GMPLACE · RONIN · CYBERCLOUD · MARINA · GHOSTMACHINE · QBOT · ASDF · MARIPOSA · XKEYSCORE · GOGADGET · TURQI · TRAFFICTHIEF · FALLOUT · POUNDSAND · BLUESMOKE · AEG · TURNABOUT · QUANTUMBOT -
HTTP Activity in XKEYSCORE [pdf]
This training presentation from March 2009 provides NSA and Five Eyes analysts with detailed instructions on exploiting HTTP web browsing activity collected by XKEYSCORE, explaining how to differentiate client-to-server requests (GET/POST) from server-to-client responses, extract metadata like search terms, URLs, cookies, language, and browser types, and use this data to discover new surveillance targets, track individuals' online behavior, and conduct "pattern of life" analysis.
-
HTTP Activity vs User Activity [pdf]
This NSA training document from June 2009 explains the distinction between HTTP Activity (general web browsing data) and User Activity (communications metadata from specific protocols like webmail and chat) within the XKEYSCORE surveillance system, demonstrating through Iranian examples how analysts combine both search types to develop comprehensive intelligence on targets.
Programs: XKEYSCORE · MARINA · FOXTRAIL · DECODEORDAIN · YACHTSHOP · BRUTUS · WINDCHASER · NKB · UIS · STARPROC -
iPhone target analysis and exploitation with unique device identifiers [pdf]
A GCHQ technical paper from November 2010 describing iPhone target analysis and exploitation using the QUANTUM system — covering UDID-based target tracking and correlation across MUTANT BROTH and AUTOASSOC, a Safari PDF exploit delivering WARRIORPRIDE implants to target iPhones via QUANTUM redirection, and a confirmed successful exploitation of a jailbroken target phone yielding address book, SMS, call logs, notes, WiFi logs, browser history and images.
Programs: QUANTUM · DEBITCARD · AUTOASSOC · HARDASSOC · MUTANTBROTH · BROKER · HANDEX · WARRIORPRIDE · ABSOLINEEPILSON · BROADOAK · SOLARSHOCK · BLACKHOLE · SHORTSHEET · XKEYSCORE · MARINA · LOOKINGGLASS · OVERLIT · SLIDE · SEP · PRESTON · WHIPSAW · CROWNPRINCE · CORINTH · MVR · SOCIALANTHROPOID -
Is It the End of the SIGINT World as We Have Come to Know It? [pdf]
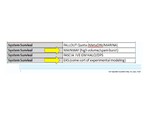
Two excerpts from a 2012 NSA presentation titled "Is It the End of the SIGINT World as We Have Come to Know It?" prepared by a member of the Large-Access Exploitation Group. The table excerpt lists MAINWAY among the systems at highest risk of being overwhelmed by the volume of data the agency was ingesting. The diagram excerpt shows MAINWAY feeding into the Graph-in-Memory (alongside WESTERNSTAR), illustrating how MAINWAY's continuous contact-chaining pushed its precomputed results into the in-memory graph database that analysts actually queried.
Programs: FALLOUT · METADNI · MARINA · MAINWAY · FASCIA · GMHALO · DPS · EKS · WESTERNSTAR · GRAPH-IN-MEMORY -
Legalities - GCHQ Databases eg Pilbeam, Salamanca, UDAQ etc [pdf]
This October 2007 GCHQ document outlines the legal authorization requirements for querying surveillance databases, revealing that GCHQ analysts can search their own databases (like PILBEAM, SALAMANCA, UDAQ) for metadata on anyone regardless of nationality without additional authorization, while NSA databases (like MARINA, MAINWAY, DISHFIRE) prohibit searches for Americans and other Five Eyes citizens but permit searches for UK persons.
-
LEVITATION and the FFU Hypothesis [pdf]
This document describes LEVITATION, a top-secret Canadian Communications Security Establishment (CSE) project that monitors millions of daily file uploads and downloads from free file-sharing sites to identify potential extremist activity. It details the program’s data collection methods, analytical workflow, use of partner databases, and examples of successful discoveries related to terrorist materials and hostage videos.
-
Menwith databases as of Aug 2008 [pdf]
This document outlines database access and SIGINT missions at Menwith Hill Station (MHS) as of August 2008, detailing the specific programs, language branches, and target development teams supported, including repositories like DISHFIRE, MAINWAY, and PINWALE. It also notes that U.S. personnel use the SIGINT Contact Center (SCC) process for access, with certain NOFORN restrictions, and lists additional analytic tools available to MHS analysts.
Marking: CONFIDENTIALPrograms: ASSOCIATION · DISHFIRE · HOMEBASE GEO · MAINWAY · NUCLEON · PINWALE · SPOTBEAM · XKEYSCORE · BANYAN · BROOMSTICK · CULTWEAVE II · MARINA · TRAFFICTHIEF · FASCIA · OCTSKYWARD · ROADBED · TUNNINGFORK · AGILITY · CADENCE · CONTRAOCTAVE · GAMUT · UTT · NKB · OCTAVE · PUZZLECUBE · TKB -
New Technique Geolocates Targets Active at Yemeni Cafes SIDtoday [pdf]
A 2010 NSA document from Menwith Hill Station details a new geolocation technique used in Yemen that combines HUMINT café surveys with SIGINT data — including RADIUS logs, passive collection tools, and TAO access — to track targets frequenting internet cafés linked to Al Qaeda. The method, integrating systems like MORK, WINDCHASER, MARINA, and SPARKLEPONY, enabled analysts to identify and monitor dozens of cafés and correlate user activity with high-priority targets.
Programs: GHOSTHUNTER · MORK · RADIUS · WINDCHASER · MARINA · XKEYSCORE · SPARKLEPONY · GHOSTWOLF · TELIR -
NSA QUANTUM Tasking Techniques for the R&T Analyst [pdf]
A classified NSA training presentation, prepared by Booz Allen Hamilton, walking analysts step-by-step through how to secretly hack into a target's computer by hijacking their everyday internet traffic — exploiting platforms like Yahoo and Facebook to silently inject malware without the target's knowledge.
Programs: QUANTUM · QUANTUMTHEORY · QUANTUMNATION · VALIDATOR · COMMONDEER · SEASONEDMOTH · SMOTH · MARINA · FOXACID · RADIUS · QUANTUMBISCUIT · ALTEREGO · DOGCOLLAR · FOREMAN · ANCHORY · BRUTUS · REACTOR · SPARKLEPONY · WINDCHASER · YACHTSHOP · MUTANTBROTH · FOXSEARCH · WHITELIST · SSO · PSC -
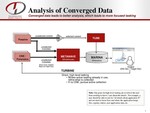
NSA Technology Directorate Analysis of Converged Data [pdf]
This document outlines the strategic integration of passive and active signals intelligence (SIGINT) to create a more efficient surveillance loop. The document centers on TURBINE, an intelligent command-and-control system designed to manage a massive network of malware implants (Computer Network Exploitation or CNE). The primary goal is to automate the extraction of data from targeted machines, effectively "converging" traditional passive collection with active hacking to refine intelligence tasking.
-
OAKSTAR Weekly Update - Program Highlights Week of: March 16-22, 2013 [pdf]
The document is a NSA weekly operations update from March 16-22, 2013, detailing technical issues, maintenance, and intelligence activities within the OAKSTAR and MONKEYROCKET programs—surveillance systems used for data collection. It notes collection outages, system adjustments, and that analysts were using MONKEYROCKET access to track Bitcoin transactions and investigate organized crime and cyber targets using e-currency for money laundering.
Programs: OAKSTAR · PRIMECANE · MONKEYROCKET · NIAGARAFILES · TRANSPORTORO · XKEYSCORE · REMEDY · MARINA · CLOUDRUNNER -
OAKSTAR Weekly Update - Program Highlights Week of: March 2-8, 2013 [pdf]
The document is a NSA weekly operations update from March 2-8, 2013, detailing technical issues, maintenance, and intelligence activities within the OAKSTAR and MONKEYROCKET programs—surveillance systems used for data collection. It notes collection outages, system adjustments, and that analysts were using MONKEYROCKET access to track Bitcoin transactions and investigate organized crime and cyber targets using e-currency for money laundering.
-
OAKSTAR Weekly Update - Program Highlights Week of: March 23-29, 2013 [pdf]
The document is a NSA weekly operations update from March 23-29, 2013, it details equipment handoffs, script tweaks to improve data flow, metadata collection metrics, and ongoing MONKEYROCKET use for tracking Bitcoin-related targets, including sharing detailed user and session data with analysts for intelligence purposes.
-
OAKSTAR Weekly Update - Program Highlights Week of: March 9-15, 2013 [pdf]
The document is a NSA weekly operations update from March 9-15, 2013, detailing technical issues, maintenance, and intelligence activities within the OAKSTAR and MONKEYROCKET programs—surveillance systems used for data collection. It notes collection outages, system adjustments, and that analysts were using MONKEYROCKET access to track Bitcoin transactions and investigate organized crime and cyber targets using e-currency for money laundering.
-
PRISM/US-984XN Overview [pdf]
A 2013 NSA training presentation revealing that major U.S. tech companies — including Google, Facebook, Apple, Microsoft, and Skype — secretly gave the NSA direct access to their servers, allowing the agency to collect users' emails, chats, photos, and files in real time, with the FBI acting as intermediary.
Programs: PRISM · FAIRVIEW · STORMBREW · BLARNEY · OAKSTAR · UTT · PRINTAURA · PINWALE · NUCLEON · TRAFFICTHIEF · SCISSORS · MARINA · MAINWAY · FALLOUT · CONVEYANCE · REPRISMFISA · SSO“U.S., British intelligence mining data from nine U.S. Internet companies in broad secret program” - The Washington Post ↗ (2013-06-06) · “NSA Prism program taps in to user data of Apple, Google and others” - The Guardian ↗ (2013-06-07) · “L'ampleur de l'espionnage mondial par la NSA” - Le Monde ↗ (2013-10-21) · “NSA files decoded: Edward Snowden's surveillance revelations explained” - The Guardian ↗ (2013-11-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “Dark Mirror: Edward Snowden and the American Surveillance State” - Penguin Press ↗ (2020-05-19) · Gellman, Barton · Poitras, Laura · Greenwald, Glenn · MacAskill, Ewen · Untersinger, Martin · Dance, Gabriel -
SID Oversight and Compliance [pdf]
Signals Intelligence Directorate (SID) oversight and compliance. A 2012 quarterly audit of the NSA's surveillance activities, which describes 865 violations by the NSA of the surveillance laws and its internal rules and regulations.
-
SIGDEV Conference 2012 - Making Things Measureable: Technology Trending Challenges and Approaches [pdf]
An NSA presentation from the 2012 SIGDEV Conference describing NSA's technology trending methodology — a framework for identifying which encryption and communications technologies targets are adopting, measuring the SIGINT risk they pose, and prioritising capabilities development responses — notable for containing the risk matrix that was later cited in Der Spiegel's December 2014 encryption investigation showing NSA's difficulty levels against specific technologies including Tor, TrueCrypt, OTR and ZRTP.
Programs: XKEYSCORE · SEEKER · BIONICTURTLE · JEMA · JOLLYROGER · MARINA · TUNINGFORK · STARPROC · MICROEXPANSE · ECHOBASE · PRISM · GMHALO · UTT · TKB · LAE · FAMT · WPMO · AMOD · FORTREND · GAMBIT · DATAEXPLORER · MYNOC