Journalist: Poitras, Laura 193 documents
Search documents matching “Poitras, Laura” →Journalists bylined on the stories that published these documents. Contributors credited without a byline are searchable but not listed here.
Graphs
By document date (11 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
SCS - Embassies and Consulates [pdf]
TOP SECRET Special Collection Service (SCS) documents about covert CIA/NSA spying sites operated from diplomatic facilities worldwide.
-
SCS sites [pdf]
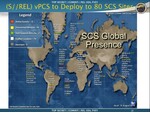
A TOP SECRET map from an SCS SIGDEV briefing, dated 13 August 2010, showing the global presence of the Special Collection Service — the joint CIA/NSA embassy-based interception unit — at some 80 sites worldwide, published (briefly unredacted) by Der Spiegel alongside its Merkel/Berlin embassy reporting, naming the specific cities where covert intercept posts operated, including Berlin, Frankfurt, Moscow, Beijing, Tehran and dozens more.
Programs: VPCS -
Secure Sockets Layer (SSL) / Transport Layer Security (TLS) [pdf]
A classified NSA Network Security Products training presentation providing a comprehensive technical overview of SSL/TLS protocol mechanics and NSA's exploitation approaches, including observed usage statistics from intercepted traffic, RSA key exchange decryption methodology, exploitation of the Debian OpenSSL RNG weakness, and the practical challenges of decrypting millions of SSL sessions per day at scale.
Programs: SCARLETFEVER -
Sentry Eagle Brief Sheet [pdf]
A classified NSA/JFCC-NW briefing document formally inducting cleared personnel into Sentry Eagle — the agency's most sensitive umbrella program protecting core secrets about its cyber operations — and enumerating, tier by tier, what the NSA conceals about its covert industry partnerships, encryption sabotage, network hacking, computer network defense, and human intelligence relationships.
Programs: SENTRYEAGLE · SPARECHANGE · WHIPGENIE · AUNTIE · AMBULANT · OPALESCE · REVELRY · REFRACTOR · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL · BLUESASH · TAREX -
SIGDEV Conference 2012 - Making Things Measureable: Technology Trending Challenges and Approaches [pdf]
An NSA presentation from the 2012 SIGDEV Conference describing NSA's technology trending methodology — a framework for identifying which encryption and communications technologies targets are adopting, measuring the SIGINT risk they pose, and prioritising capabilities development responses — notable for containing the risk matrix that was later cited in Der Spiegel's December 2014 encryption investigation showing NSA's difficulty levels against specific technologies including Tor, TrueCrypt, OTR and ZRTP.
Programs: XKEYSCORE · SEEKER · BIONICTURTLE · JEMA · JOLLYROGER · MARINA · TUNINGFORK · STARPROC · MICROEXPANSE · ECHOBASE · PRISM · GMHALO · UTT · TKB · LAE · FAMT · WPMO · AMOD · FORTREND · GAMBIT · DATAEXPLORER · MYNOC -
SIGINT Helps Hobble the Taleban by Cutting Off Their Livelihood SIDtoday [pdf]
This SIDtoday article (Feb 3, 2009) describes how SIGINT operations—led by NSA Georgia’s Southwest Asia Narcotics Division (FGS2F) with partners like NSAW and GCHQ—shifted counternarcotics efforts in Afghanistan from HUMINT to SIGINT, enabling real‑time targeting of traffickers and major seizures that disrupted Taliban funding. It credits SIGINT-driven support for large drug seizures, increased operational tempo, and the inclusion of traffickers on ISAF targeting lists.
-
SIGINT Strategy 2012-2016 [pdf]
This five-page document, written in 2012, is essentially a National Security Agency mission statement with broad goals, including a desire to push for changes in the law to provide the agency with expanded surveillance powers. It was written before Edward J. Snowden’s leaks, so it provides a glimpse at the thinking of agency officials before Mr. Snowden upset their political calculus.
People: Lynn, William J.“A Strategy for Surveillance Powers” - The New York Times ↗ (2013-11-22) · Risen, James · Poitras, Laura -
SIGINT Strategy Threads 4 and 7 SIDtoday [pdf]
A TOP SECRET SIDToday article from September 2011 describing SIGINT Strategy Threads 4 and 7 — NSA's two classified programmes addressing the challenge of ubiquitous internet encryption — directing cleared analysts to BULLRUN-protected content covering capabilities against commercial webmail encryption used by CT targets and VPN traffic exploitation, with access requiring BULLRUN Community of Interest indoctrination.
-
SINIO Seminar: Turkey and the Kurds SIDtoday [pdf]
A strategic seminar titled “Turkish Cross-Border Operations and Kurdish Intifada: Rhetoric or Reality?” will be held.
Marking: CONFIDENTIAL“Turkey Is 'Partner and Target' for the NSA” - Der Spiegel ↗ (2014-08-31) · “How the NSA Helped Turkey Kill Kurdish Rebels” - The Intercept ↗ (2014-08-31) · The Intercept ↗ (2018-08-15) · Poitras, Laura · Rosenbach, Marcel · Sontheimer, Michael · Stark, Holger -
SINIO Seminar: Turkish Presidential and Parliamentary Elections SIDtoday [pdf]
People: Erdoğan, Recep Tayyip“Turkey Is 'Partner and Target' for the NSA” - Der Spiegel ↗ (2014-08-31) · “How the NSA Helped Turkey Kill Kurdish Rebels” - The Intercept ↗ (2014-08-31) · Poitras, Laura · Rosenbach, Marcel · Sontheimer, Michael · Stark, Holger -
SINIO Summer 2003 Series of Strategic Intelligence Issue Seminars Begins with Tough Times for Turkey SIDtoday [pdf]
Announcement of a seminar on negative fallout from the Iraq War for Turkey and Turkey-U.S. relations.
Marking: CONFIDENTIAL“Turkey Is 'Partner and Target' for the NSA” - Der Spiegel ↗ (2014-08-31) · “How the NSA Helped Turkey Kill Kurdish Rebels” - The Intercept ↗ (2014-08-31) · The Intercept ↗ (2016-05-16) · Poitras, Laura · Rosenbach, Marcel · Sontheimer, Michael · Stark, Holger -
SNIPs of SIGINT [pdf]
A monthly notes entry from June 2012 by an NSA analyst on exchange at DSD Australia, describing two CNA/CNE tool development projects — PITIEDFOOL, a Windows file system destruction suite that kills the MFT and volume shadow copies and was successfully tested inside FUZZYEBOLA, and PANT SPARTY, an OpenSSH daemon backdoor granting covert root access while suppressing log entries — alongside a briefing to the US Ambassador to Australia on CNA/CNE work and TAO collaboration.
-
SNOWGLOBE: From Discovery to Attribution [pdf]
This document describes how CSEC identified and analyzed the SNOWGLOBE intrusion set, using passive collection, implant reverse engineering, and infrastructure analysis to attribute the campaign with moderate confidence to a French intelligence service targeting Iranian and international scientific, diplomatic, and political organizations.
Programs: SNOWGLOBE · WARRIORPRIDE · REPLICANTFARM · SNOWBALL · SNOWMAN · EONBLUE · SPECIALSOURCE · CANDLEGLOWPeople: Roshal, Alexander“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “Quand les Canadiens partent en chasse de « Babar »” - Le Monde ↗ (2014-03-21) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Follorou, Jacques · Untersinger, Martin -
SOMALGET (2012) [pdf]
This 2012 document provides an internal overview of SOMALGET, a sub-program of the MYSTIC surveillance project. It describes a radical shift in telephony intelligence: the move from "targeted" wiretapping to "full-take" nation-scale buffering. SOMALGET allows analysts to record 100% of a country's mobile phone audio and store it for a rolling period of 30 days. This capability, known as "retrospective retrieval," allows the NSA to listen to conversations that occurred before a person was even identified as a target. At the time of this writing, the program was fully operational in the Bahamas and one other redacted location(s).
-
Special Collection Service - Pacific SIGDEV Conference March 2011 [pdf]
This document is a TOP SECRET briefing describing the Special Collection Service (SCS)—its organizational structure, global posture and strategic partnerships—and how SCS leverages advanced SIGINT and cyber capabilities (microwave, cellular, satellite, VPN/Internet exploitation, tools like INTERQUAKE/Einstein/Castanet/Birdwatcher) from embassy/PoP sites to collect, analyze and support intelligence and covert operations. It also outlines SCS modernization goals (unified IT core, cloud/virtualization, expanded cyber presence), operational authorities and mission advantages for enabling both SIGINT and HUMINT activities. See also Spiegel's 2013 reporting based on the same presentation (back then they only published two slides from this presentation): https://www.spiegel.de/international/germany/cover-story-how-nsa-spied-on-merkel-cell-phone-from-berlin-embassy-a-930205.html
-
Special Source Collection - March 2013 [pdf]
A March 2013 NSA Special Source Operations briefing for the NSA Threat Operations Center outlining SSO's portfolio of surveillance programs, their legal authorities, and operational constraints — revealing that SSO accounts for approximately 60% of NSA content collection and 75% of metadata collection, and mapping all major collection programs across three access categories: foreign partner, corporate, and unilateral.
-
Special Source Operations [pdf]
This document provides an overview of the NSA’s Special Source Operations (SSO), characterizing the division as the premier "Cryptologic Provider" for intelligence derived from global high-capacity telecommunications. It outlines a three-tiered access portfolio—Corporate, Foreign, and Unilateral—designed to manage the "incredible challenge" of intercepting target communications across undersea fiber-optic cables that carry millions of simultaneous sessions.
Programs: RAMPART-A · WINDSTOP · BLARNEY · FAIRVIEW · STORMBREW · OAKSTAR · PRISM · RAMPART-I · RAMPART-T · SSO · RAMPART-X · ClanSIG · MYSTIC · LOPERS · WEALTHYCLUSTER-2 · DEEPDIVE · TURMOIL · FASCIA · PINWALE · MARINA · TRAFFICTHIEF · TWISTEDPATH · BLACKPEARL · ACS“How Secret Partners Expand NSA’s Surveillance Dragnet” - The Intercept ↗ (2014-06-18) · “NSA ‘third party’ partners tap the Internet backbone in global surveillance program” - Dagbladet Information ↗ (2014-06-19) · Gallagher, Ryan · Geist, Anton · Gjerding, Sebastian · Moltke, Henrik · Poitras, Laura -
Special Source Operations - Corporate Partner Access [pdf]
A classified NSA Special Source Operations briefing detailing the four major corporate partner surveillance programs — BLARNEY, FAIRVIEW, STORMBREW, and OAKSTAR — their legal authorities, collection access points, target lists, and funding profiles totaling nearly $480 million in FY2010, revealing the infrastructure through which the NSA taps U.S. telecommunications companies to intercept international fiber optic communications on American soil.
Programs: BLARNEY · FAIRVIEW · STORMBREW · OAKSTAR · LITHIUM · ARTIFICE · ROCKSALT · SERENADE · PINECONE · BRECKENRIDGE · TAHOE · SUNVALLEY · WHISTLER · KILLINGTON · COPPERMOUNTAIN · MAVERICK · CONUS · TURMOIL · UTT · STEELKNIGHT · SSO“Snowden document reveals key role of companies in NSA data collection” - The Guardian ↗ (2013-11-01) · “NSA files decoded: Edward Snowden's surveillance revelations explained” - The Guardian ↗ (2013-11-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “NSA Spying Relies on AT&T’s ‘Extreme Willingness to Help’” - ProPublica ↗ (2015-08-15) · “AT&T Helped U.S. Spy on Internet on a Vast Scale” - The New York Times ↗ (2015-08-15) · “Titanpointe: The NSA’s Spy Hub in New York, Hidden in Plain Sight” - The Intercept ↗ (2016-11-16) · MacAskill, Ewen · Rushe, Dominic · Dance, Gabriel · Greenwald, Glenn · Angwin, Julia · Larson, Jeff · Savage, Charlie · Moltke, Henrik · Poitras, Laura · Risen, James · Gallagher, Ryan -
Special Source Operations corporate overview [pdf]
A classified NSA training presentation providing an in-depth operational overview of the FAIRVIEW program — the agency's largest corporate partner surveillance program — detailing its collection capabilities, legal authorities, TAO shaping operations, targeting tools, and productivity statistics, while revealing that BLARNEY/PRISM was the single most productive SSO program in 2012 with 806 serialized product reports.
Programs: FAIRVIEW · BLARNEY · PRISM · RAMPART-A · RAMPART-I · RAMPART-X · RAMPART-T · RAMPART-M · DGO · WINDSTOP · MYSTIC · PINWALE · XKEYSCORE · TURMOIL · STORMBREW · OAKSTAR · OCTAVE · UTT · CADENCE · COWBOY · YANKEE · MAINWAY · TOYGRIPPE · BLACKPEARL · TWISTEDPATH · NUCLEON · DISHFIRE · SPYDER · CARBONFURY · NATIVEFLORA · UNICORNSANDWICH · CROSSEYEDBEAR · SCORCHERSIX · TROPICTHUNDER · DARKTHUNDER · STEELFLAUTA · RAGTIME · SWEETSMACK2 · SOURSMACK2 · EVILOLIVE · SCALEABLE · FLEXIBLE · MONKEYROCKET · SHIFTINGSHADOW · ORANGECRUSH · YACHTSHOP · ORANGEBLOSSOM · SILVERZEPHYR · BLUEZEPHYR · COBALTFALCON · RAGTIME-A · RAGTIME-C · SSO · SURREY“NSA Spying Relies on AT&T’s ‘Extreme Willingness to Help’” - ProPublica ↗ (2015-08-15) · “AT&T Helped U.S. Spy on Internet on a Vast Scale” - The New York Times ↗ (2015-08-15) · “The Wiretap Rooms: The NSA’s Hidden Spy Hubs in Eight U.S. Cities” - The Intercept ↗ (2018-06-25) · Angwin, Julia · Larson, Jeff · Savage, Charlie · Moltke, Henrik · Poitras, Laura · Risen, James · Gallagher, Ryan -
Special Source Operations Weekly - 14 March 2013 [pdf]
A March 2013 NSA Special Source Operations weekly briefing slide noting the activation of STORMBREW's Transit DNI metadata collection at the BRECKENRIDGE site on March 11, 2013, and announcing that content collection of SMTP traffic under Transit Authority began two days later.