Journalist: Poitras, Laura 193 documents
Search documents matching “Poitras, Laura” →Journalists bylined on the stories that published these documents. Contributors credited without a byline are searchable but not listed here.
Graphs
By document date (11 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Cable Master List [pdf]
This GCHQ document is a comprehensive master list of undersea fiber optic cables tracked for surveillance purposes, including both cables with UK landing points and international cables without UK connections, detailing technical specifications, ownership, capacity data, and code names for telecommunications partner companies that provided the intelligence agency with surveillance access.
Programs: PINNAGE · PFENNINGALPHA · NIGELLA · REMEDY · HIASCO · GERONTIC · SCEPTRE · PRESCOTT · KIRKISTOWN · LINNELL · CATEGORY · DACRON · KNAPWEED · ELAPSE · VITREOUS · LITTLE · STREETCAR · GIBBUS · VISAGE · LATUS · NUMDAH“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
Cables we do not currently have good access [pdf]
This GCHQ document, titled "Cables we do not currently have good access," lists numerous undersea fiber-optic cables along with their active data capacity ("Lit Capacity"), indicating the substantial portion of global telecommunications infrastructure where the agency lacks adequate surveillance access, in contrast to other internal reports detailing cables it successfully monitors.
“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
Case Studies of Integrated Cyber Operation Techniques [pdf]
Programs: AURORAVNC · TUTELAGE · QUANTUM · TURBINE · BOXINGRUMBLE · CLOUDSHIELD · PANDORASMAYHAM · TURMOIL · QUANTUMTHEORY · QUANTUMDNS · TAOSHOOTER · DEFIANTWARRIOR · QUANTUMINSERT · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMHAND · QUANTUMPHANTOM · QUANTUMSKY · QUANTUMCOPPER · QUANTUMSMACKDOWN · QUANTUMSANDMAN · FOXACID“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Gallagher, Ryan · Greenwald, Glenn -
Center for Content Extraction - Content Extraction Analytics, SIGDEV End-to-End Demo [pdf]
This document is a technical showcase demonstrating the capabilities of an NSA content‑extraction program, using political leaders and diplomatic figures (such as Angela Merkel) as illustrative examples. It presents how automated language technology can extract, organize, and scale intelligence data from intercepted material.
Programs: MARINA · CYBERTRANS · PAINTBALL · SYNAPSE · NYMROD · THUNDERCLOUD · JOURNEYMAN · GOLDENRETRIEVER · SOCIOPATH · LEXHOUND · HERESYITCH · HLT · TKB · EKS -
Chinese Exfiltrate Sensitive Military Technology [pdf]
This TOP SECRET NSA SIGINT development briefing describes large-scale Chinese cyber espionage that exfiltrated sensitive U.S. military technologies and inflicted extensive operational, financial, and strategic damage on Department of Defense systems. The document emphasizes both the scale of losses and the role of SIGINT in detecting, understanding, and mitigating adversary malware.
Programs: BYZANTINEHADES -
CLASSIFICATION GUIDE FOR CRYPTANALYSIS, 2-12 [pdf]
An NSA/CSS classification guide for cryptanalysis establishing the precise classification level for each type of information about NSA's capabilities to exploit commercial and indigenous encryption systems — from the unclassified acknowledgement that NSA exploits cryptographic devices, through to the Top Secret protection of cryptographic modifications made to commercial products to render them exploitable and industry relationships used to obtain cryptographic details.
“Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · “Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · Ball, James · Borger, Julian · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian -
CLASSIFICATION GUIDE FOR ECI PAWLEYS (PAW) [pdf]
This 2006 NSA classification guide outlines the protocols for ECI PAWLEYS (PAW). PAWLEYS is an Exceptionally Compartmented Information (ECI) category designed to protect clandestine operations—both physical (HUMINT) and digital (CNE)—specifically aimed at acquiring foreign cryptographic information and material. The document confirms that the NSA actively seeks to circumvent encryption through clandestine HUMINT and computer network access aimed at cryptographic information and material, rather than relying solely on traditional codebreaking.
Programs: PAWLEYS -
Classification Guide for FISA, the Protect America Act and the FISA Amendments Act [pdf]
The Foreign Intelligence Surveillance Act regulates spying for national security purposes on domestic soil. This guide lays out secrecy restrictions for various aspects of those programs. Among other things, it mentions the Large Content FISA order, a term that has not previously been disclosed.
-
CLASSIFICATION GUIDE FOR THE NSA/CSS TARGET EXPLOITATION (TAREX) PROGRAM [pdf]
A 2012 NSA/CSS classification guide for the TAREX program — the agency's clandestine human intelligence and close-access signals intelligence unit — establishing what information about TAREX's operations, locations, methodologies, and interagency relationships must be protected, revealing forward-based presences in Germany, South Korea, and Beijing, and confirming that TAREX personnel operate undercover at U.S. embassies worldwide.
Programs: TAREXPeople: Shea, Teresa H. -
CNE End Point Requirements [pdf]
This NSA/GCHQ document outlines comprehensive requirements for an endpoint surveillance systems that enables analysts to systematically identify intelligence collection needs and discover appropriate tools for data extraction from compromised computers. The framework covers capabilities for remote data collection, cross-platform intelligence integration, query functions, tasking procedures, and visualization tools across implanted networks.
Programs: STARGATE · LOOKING GLASS · QUANTUM · GOLDENEYE · XKEYSCORE · MARINA · JTRIG · BROADOAK · UTT · GLOBALREACH · GLOBALSURGE · THUGGEE · EREPO · DANCINGBEAR · HAUSTORIUM · SHAREOWN · MUTANTBROTH · MOONRAKER · CARBONROD · RUFFLE · ROCKOPERA · QUINCEY · ECLIPSE · MUGSHOT · HIGHNOTE · UDAQ2 · EKB · TURBINE · ACNO · FLAMECARPET · FUMECUPBOARD · JACKPOT · SLIPSTREAM · B13B · PSC · QUINCY · DAREDEVIL · ROADBED -
CNE EndPoint Project Load [pdf]
The CNE EndPoint Project Load document lists multiple GCHQ exploitation projects, with “PFENNING ALPHA” targeting Flag Telecom’s network. It notes automated pulls of router monitoring webpages, collection of performance statistics, and ongoing efforts to gain further access points within Reliance’s infrastructure, while other projects and targets remain redacted.
Programs: PFENNING ALPHA · BURRITO ALPHA · GLADDY IOTA · HEADRESS IOTA · HEADRESS KAPPA · HEADRESS NU · HEADRESS OMICRON · GLADDY CHI · EREPO · RELIANCE · GTE“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
CNE Presence in CT10 Status Report [pdf]
A TOP SECRET NSA status report from April 2008 describing how a counterterrorism analysis team began importing data from the agency's hacking operations into their tracking system — specifically logs from FOXACID, an NSA tool that infects targets' computers mainly through their web browsers — enabling real-time alerts when new targets were successfully hacked, with plans to expand into tracking four named surveillance implants (VALIDATOR, UNITEDRAKE, OLYMPUS and STRAITBIZARRE) as they phone home to NSA servers for instructions and stolen data.
-
CNO Core Secrets Security Structure [pdf]
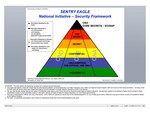
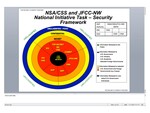
A 3-slide NSA presentation outlining the classification architecture of Sentry Eagle, a national cyber operations initiative, showing how its most sensitive components — covering network hacking, encryption sabotage, and covert industry relationships — are locked behind ECI and SAP designations accessible only to a tiny circle of government officials.
Programs: SENTRYEAGLE · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL -
CNO Core Secrets Slide Slices [pdf]
This document outlines the Security Framework for a joint national initiative between the NSA/CSS and JFCC-NW, detailing the highly compartmented structure used to protect cyber and intelligence secrets. It utilizes a concentric security framework diagram to visualize the layers of sensitivity, placing the most critical technical capabilities at the absolute center of the intelligence community's protection.
Programs: SENTRY-EAGLE · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL -
Collaboration in Overdrive: A CNE Success SIDtoday [pdf]
A collaboration between several NSA departments achieved, for the first time, Computer Network Exploitation against "Turkish leadership."
Programs: CMAP“Turkey Is 'Partner and Target' for the NSA” - Der Spiegel ↗ (2014-08-31) · “How the NSA Helped Turkey Kill Kurdish Rebels” - The Intercept ↗ (2014-08-31) · The Intercept ↗ (2019-05-29) · Poitras, Laura · Rosenbach, Marcel · Sontheimer, Michael · Stark, Holger -
Computer Network Exploitation (CNE) Classification Guide / 2-59 [pdf]
A NSA/TAO classification guide establishing the precise classification level for 41 categories of information about computer network exploitation operations — covering remote and physical subversion methods, CNE tools and techniques, supply chain operations, hardware implants, off-net field operations, zero-day vulnerabilities, and cryptographic material acquired through CNE.
“Core Secrets: NSA Saboteurs in China and Germany” - The Intercept ↗ (2014-10-10) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Maass, Peter · Poitras, Laura · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
COMPUTER NETWORK OPERATIONS - GENIE [pdf]
A TOP SECRET Congressional Budget Justification entry for the NSA/CSS GENIE project — the Tailored Access Operations programme underpinning all endpoint Computer Network Operations — requesting $651.7 million and 1,870 military and civilian positions for FY2013, with plans to maintain 85,000-96,000 implant points-of-presence worldwide and 9,000-10,000 active accesses, including $25.1 million for covert purchase of software vulnerabilities and a $3.4 million supply chain implant operation targeting al-Qaeda.
-
Computer-Network Exploitation Successes South of the Border [pdf]
Pena Nieto's predecessor as president, Felipe Calderon, was also targeted. This image shows an excerpt from an NSA document classified as "top secret," from November 2010. The National Security Agency (NSA) has a division for particularly difficult cases. Called "Tailored Access Operations," or TAO for short, this department devises special methods for special targets. In May 2010, the division reported mission accomplished. A report classified as "top secret" said: "TAO successfully exploited a key mail server in the Mexican Presidencia domain within the Mexican Presidential network to gain first-ever access to President Felipe Calderon's public email account." According to the NSA, this email domain was also used by cabinet members, and contained "diplomatic, economic and leadership communications which continue to provide insight into Mexico's political system and internal stability."
Programs: FLATLIQUID -
Cooperation between the NSA and BND [pdf]
Comprehensive internal summary of the history and current state of cooperation between the NSA and BND
Programs: RT-RGPeople: Schindler, Gerhard -
Crypt Discovery Joint Collaboration Activity 20 January 2011 [pdf]
A TOP SECRET NSA/GCHQ joint collaboration activity plan from January 2011 describing a research programme to understand and mitigate the threat that rising encryption adoption poses to target discovery and development — measuring encryption prevalence across SIGINT collection, assessing the impact on metadata-based targeting tradecraft, and developing new techniques for identifying targets behind encrypted traffic using a joint cloud environment fed by MUTANT BROTH, BEARDED PIGGY, KARMA POLICE, MEMORY HOLE, MARBLED GECKO, SOCIAL ANIMAL and ASDF metadata.
Marking: TOP SECRETPrograms: TICKETWINDOW · MUTANTBROTH · BEARDEDPIGGY · KARMAPOLICE · MEMORYHOLE · MARBLEDGECKO · SOCIALANIMAL · XKEYSCORE · ASDF“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “Profiled: From Radio to Porn, British Spies Track Web Users' Online Identities” - The Intercept ↗ (2015-09-25) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Gallagher, Ryan