Journalist: Gallagher, Ryan 212 documents
Search documents matching “Gallagher, Ryan” →Journalists bylined on the stories that published these documents. Contributors credited without a byline are searchable but not listed here.
Graphs
By document date (10 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
NSA/GCHQ/CSEC Network Tradecraft Advancement Team [pdf]
The "NSA/GCHQ/CSEC Network Tradecraft Advancement Team (NTAT) 2010" document describes a collaborative mission between the US, UK, and Canada to synchronize and advance SIGINT techniques. The NTAT focused on "Network Analysis Tradecraft," specifically integrating analysis tools such as IRASCIABLE RABBIT and TOYGRIPPE into CSEC's OLYMPIA and developing standardized "use cases" for tracking mobile networks and virtual private networks (VPNs).
-
NSA’s intelligence relationship with Australia [pdf]
This document summarizes the close intelligence partnership between the U.S. NSA and Australia’s Defence Signals Directorate (DSD), highlighting collaboration on cyber operations, SIGINT collection, and military support. It emphasizes Australia’s contributions through satellite access, geolocation, and terrorism-related communications, particularly in the Pacific region, while noting shared focus on China and joint participation in multinational intelligence coalitions.
-
NTAC Overview [pdf]
This document outlines the structure, mission, and operations of the U.K.’s National Technical Assistance Centre (NTAC), a GCHQ-controlled unit responsible for enabling and managing lawful interception of communications and decryption of data across national networks. It details NTAC’s integration into GCHQ, its key role in programs like MILKWHITE, its extensive interception capacity, and the technical and resource challenges it faces in adapting to evolving telecommunications technologies.
Marking: SECRET -
OP HIGHLAND FLING - Event Log [pdf]
A TOP SECRET operational event log from GCHQ's GCWiki documenting a January 2011 operation targeting Gemalto employees in France, Poland and elsewhere, using MUTANT BROTH cookie analysis, Facebook credentials, LinkedIn profiles and Computer Network Exploitation to identify and implant targets as part of the operation to steal SIM card encryption keys.
-
Operational Engineering November 2010 [pdf]
This internal GCHQ briefing from late 2010 documents the Events Product Centre's suite of bulk internet and communications surveillance tools — including IMMINGLE, SALAMANCA, SOCIAL ANTHROPOID, MUTANT BROTH, KARMA POLICE, SAMUEL PEPYS and GUIDING LIGHT — covering scaling targets, new data sources, and operational capabilities across telephony, webmail, instant messaging, social media, GPRS and VoIP collection.
Programs: EVENTS · IMMINGLE · SALAMANCA · GUIDINGLIGHT · B3M · HARDASSOC · MAINWAY · THUGGEE · FASCIA · HAUSTORIUM · FIRESTORM · TERRAIN · SHAREOWN · ESCHAR · BRIO · INFINITEMONKEY · KARMAPOLICE · MARBLEDGECKO · MEMORYHOLE · MUTANTBROTH · SAMUELPEPYS · SOCIALANIMAL · SOCIALANTHROPOID · HEARTBEAT · SANTHROPOID · LEAKYGATEWAYS · GTPTUNNEL · LUSTRE · GLASSBACK · COLLATERAL · HRMAP · SWORDPLAY · BROADOAK · REFORMER · ARTEMIS · MERLOT · CONTRAOCTAVE · CRYINGFOWL · CULTWEAVE · SAMDYCE · GCQUERY · BLAZZINGSADDLES · EREPO · JTRIG · SOUNDER -
OPULENT PUP Encryption Attack [pdf]
"OPULENT PUP encryption attack (GCHQ)" is a 2009 technical planning document from the British intelligence agency GCHQ. It outlines a "proof-of-concept demonstrator" for a new capability to intercept and decrypt GSM communications protected by the A5/3 algorithm, requiring a complete overhaul of the existing processing chain used for the older A5/1 standard.
Programs: OPULENTPUP -
PHANTOM PARROT [pdf]
This document discusses PHANTOM PARROT, a GTAC tool used for querying mobile phone data collected from individuals stopped at UK ports as part of the ITT Op WILDWAY initiative. The tool allows intelligence analysts to access phonebook, SMS, and call log data from these stops, which can be used for counter-terrorism efforts. Data is obtained under the Terrorism Act 2000, and the tool is part of a broader intelligence-gathering effort, eventually to be integrated into the LUCKY STRIKE project.
Programs: PHANTOM PARROT · WILDWAY · RANNOCH MOOR · LUCKY STRIKE · LOOKING GLASS · DISHFIRE · CORINTH · MOONRAKER · RUSSETT -
Pine Gap classification guide [pdf]
This document is a classification guide for NSA/CSS activities at the Joint Defense Facility Pine Gap (JDFPG) in Australia, outlining which information about the site, its SIGINT missions, organizational structure, and training is classified and at what level. It specifies that sensitive details, including the site’s SIGINT mission, Producer Designator Digraph, SIGAD, and support to military operations, are protected to safeguard national security and allied interests.
-
PRESTON Architecture [pdf]
The PRESTON architecture, centered on GCHQ’s PRESTON Processing system, is detailed across multiple views showing how the agency intercepts, processes, and stores communications. It outlines a sophisticated surveillance framework that integrates lawful interception, data processing, and analyst access, emphasizing covert monitoring and management of intercepted data.
Programs: PRESTON · FAST GROK · BOXSTER · MARMION · GENTIAN · TERRAIN · BLACKNIGHT · CORINTH · FARNDALE · SAMDYCE · B3M · VSLT · SAMBOK · HAUSTORIUM · FUNFAIR · Cheltenham · SALAMANCA · IIB · LOCHNVAR · MONACO · HOTLINE · Benhall · GDR · CE · BRIGHTON · ARSENIDE · SPQR · TACHO · TRAFFIC MASTER · KEYCARD · XKEYSCORE · COURIERSKILL · MONKEYPUZZLE · PILBEAM · GREENHEART · CCDF · GTE · CADENCE · TERRAINS · GCNET · HENCE -
PRESTON Business Processes [pdf]
The PRESTON Business Processes document outlines GCHQ’s internal workflows for authorizing, enabling, managing, and terminating communications interception, as well as producing intelligence from intercepted data. It defines the roles, responsibilities, and technical processes that support lawful interception operations within the PRESTON system.
-
PRESTON Study [pdf]
This GCHQ document details the PRESTON surveillance program, revealing that over a six-month period, 97% of intercepted communications—including calls, texts, and internet data—were not viewed by analysts despite being fully warranted, highlighting systemic challenges in processing and exploiting the vast volume of collected intelligence. It underscores the reliance on traditional PRESTON sources for events like the London G20, while noting gaps in data feeds from other repositories, reflecting both operational scale and limitations in effective oversight.
-
PRISM Olympic Option [pdf]
A May 2012 NSA operational highlight revealing that Britain's GCHQ was given access to the NSA's PRISM surveillance system during the London Olympics, with 100 trained British operatives secretly monitoring 256 targets and intercepting over 11,000 communications in a single week.
-
Project SANDSTORM [pdf]
This document shortly describes Project SANDSTORM, part of the Active Sigint Enabling Passive Geolocation (ASEPG) program at Menwith Hill, which uses Wi-Fi signal characterization and satellite-based Overhead capabilities to geolocate high-value targets, with geolocations of under 100 meters expected even for low-power signals in denied areas. It focuses on actively enabling SIGINT to track targets via 802.11 wireless networks.
-
Psychology: A New Kind of SIGDEV [pdf]
This document presents a detailed approach to integrating human sciences—such as psychology, sociology, anthropology, economics, and political science—into intelligence operations. It highlights the use of tools like SIGINT, HUMINT, and covert online monitoring to understand and shape human behavior, influence networks, and assess socio-cultural dynamics. The focus is on using real-time data analytics, including tracking social media interactions, to optimize intelligence gathering and strategic influence.
Programs: JTRIG · HSOC · SQUEAKY DOLPHIN · DISTILLERY · AIRWOLF · ANTICRISISGIRL · SPLUNK · STREAMINGANALYTICS · HOLLOWPOINT · FIREANT · GTE“Snowden Documents Reveal Covert Surveillance and Pressure Tactics Aimed at WikiLeaks and Its Supporters” - The Intercept ↗ (2014-02-18) · “Snowden docs reveal British spies snooped on YouTube and Facebook” - NBC News ↗ (2014-01-27) · Greenwald, Glenn · Gallagher, Ryan · Esposito, Richard · Cole, Matthew · Schone, Mark -
Pull Steering Group Minutes [pdf]
A top secret STRAP1 GCHQ PullThrough Steering Group meeting record from February 2008 documenting the approval process for five surveillance and intelligence prototypes including KARMA POLICE — the mass internet browsing profiling system — alongside ORB FINDER for CNE operational relay box identification, SALTY OTTER for cross-media timing analysis, MOOSE MILK for telephone kiosk surveillance, and LIGHTWOOD for email address extraction used by JTRIG.
Programs: MYOFIBRIL · SALTYOTTER · PRIMETIME · KARMAPOLICE · ORBFINDER · MOOSEMILK · LIGHTWOOD · JTRIG · MERAPEAK · MONTEVISTA · KED -
QFD BLACKHOLE Technology Behind INOC [pdf]
A UK SECRET STRAP2 COMINT ORCON GCHQ Applied Research presentation from March 2009 documenting the BLACK HOLE bulk data repository's scale and structure, and the suite of analytical tools — MUTANT BROTH, KARMA POLICE, INFINITE MONKEYS and MARBLED GECKO — built on top of it to answer specific intelligence questions about online presence, browsing activity, forum usage and geolocation searches.
Programs: BLACKHOLE · MESME · NETEZZA · CLOUDS · MUTANTBROTH · KARMAPOLICE · INFINITEMONKEYS · MARBLEDGECKO · GOOB · AUTOASSOC · PSOUP · SOCIALANIMAL · SAMUELPEPYS · MEMORYHOLE · HRMAP · PSOUPALERT · LAUGHINGHYENA -
Quantum – from GCHQ documents dates October 2012 [pdf]
Portion of a document from the NSA’s British equivalent, the GCHQ, in which Sweden is not mentioned, but it describes an example of how Quantum has been used to attack computers in an African country where the users have visited extremist websites.
-
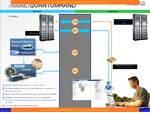
QUANTUMHAND [pdf]
This slide describes QUANTUMHAND, a specialized "Man-on-the-Side" (MOTS) attack used by the NSA's Tailored Access Operations (TAO) to infect targets visiting Facebook. The document outlines an automated process where the NSA's surveillance infrastructure, TURMOIL and TURBINE, detects a target's connection to Facebook and "races" against the legitimate Facebook server to deliver a malicious response first. This "winning the race" allows the NSA to redirect the user to a TAO server that attempts to deploy malware "implants" on the target's computer.
-
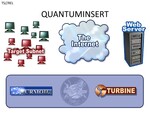
QUANTUMINSERT [pdf]
This top-secret NSA presentation provides a step-by-step visual walkthrough of a man-on-the-side (MOTS) attack. This technique allows the NSA to covertly redirect a target's web browser to a malicious server in order to install a malware implant. The diagrams illustrate the interaction between the NSA's global surveillance sensors (TURMOIL) and its automated command-and-control system (TURBINE), demonstrating how the agency exploits the fundamental "race condition" of the internet to compromise a target.
-
QUANTUMTHEORY (2010 SIGINT Development Conference) [pdf]
This 2010 NSA presentation reveals QUANTUMTHEORY, a suite of "man-on-the-side" network attack technologies that enable real-time injection and manipulation of TCP/IP connections through passive surveillance infrastructure. The system encompasses multiple specialized attack techniques including HTML redirection, DNS hijacking, botnet takeover, and database injection, deployed at Five Eyes surveillance sites worldwide.
Programs: QUANTUMTHEORY · TRAFFICTHIEF · TURMOIL · TURBINE · QUANTUM · NINJANIC · ISLANDTRANSPORT · SURPLUSHANGER · DAREDEVIL · STRAIGHTBIZARRE · QUANTUMINSERT · QUANTUMSKY · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMDNS · QUANTUMBOT2 · QUANTUMCOPPER · QUANTUMMUSH · HUFFMUSH · QUANTUMSPIM · QUANTUMSQUEEL · QUANTUMSQUIRREL · INCENSOR · SMOKEYSINK · SARATOGA · QUANTUMDEFENSE · TURBULENCE“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael