Country: Poland 24 documents
Search documents matching “Poland” →Countries mentioned in each document. A country may be mentioned directly (e.g., France) or inferred from a related reference, such as a city (Paris -> France) or a domain name (.fr -> France).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
BOUNDLESSINFORMANT, Poland [pdf]
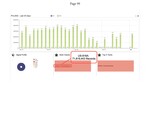
A BOUNDLESSINFORMANT signal profile for Poland over 30 days: 71,819,443 records from SIGAD US-916A via DRTBOX, with PCS, INMARSAT, MOIP, VSAT, HPCP, PSTN and DNI as the top techniques.
-
Afghanistan Coalition Dissemination Brief to Senior Leadership Forum [pdf]
This document ooutlines the structure, goals, and challenges of multinational signals intelligence (SIGINT) collaboration in Afghanistan as of 2009. It reveals how the U.S. and its intelligence-sharing allies (notably the 5 Eyes, 9 Eyes, and 14 Eyes) coordinated SIGINT collection, decryption, analysis, and dissemination across NATO and coalition forces.
“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
Approved SIGINT Partners [pdf]
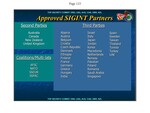
A Foreign Affairs Directorate slide listing NSA's approved SIGINT partners: the four Second Parties, 33 Third Parties from Algeria to the United Arab Emirates, and the coalitions AFSC, NATO, SSEUR and SSPAC. This is document is from Fiscal Year 2013 "Foreign Partner Review."
-
Bad guys are everywhere, good guys are somewhere! [pdf]
A classified NSA NTOC presentation describing TREASURE MAP — the agency's near real-time global internet mapping platform — which combines open source, commercial, covert, and SIGINT data to chart every device, router, and autonomous system on the internet, including through 13 covert servers secretly planted in unwitting data centers across 18 countries spanning Asia, Europe, Russia, Africa, and South America, with networks marked in red indicating active SIGINT collection access points across at least 20 major telecommunications providers on three continents including allied nations' state-owned carriers.
Programs: TREASUREMAP · PACKAGEDGOODS · SOCIALSTAMP · SEASIDEFERRY · ARK · CAIDA · RUSTICBAGGAGE · PACKAGEDGOODS-GTR · PACKAGEDGOODS-SERVER · BLACKPEARL · LEAKYFAUCET · HYDROCASTLE · MASTERSHAKE · S-TRICKLER · TOYGRIPPE · DISCOROUTE · VITALAIR2 · IPGEOTRAP · JOLLYROGER · TUTELAGE · BYZANTINEHADES · XKEYSCORE · RADIUS · TACACS -
Belgacom connections [pdf]
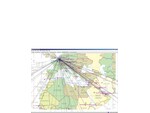
A "Belgacom connections" map lays out the carrier’s sprawling roaming and backbone interconnects, precisely the arteries GCHQ wanted to get access into. Under Operation Socialist GCHQ successfully gained access to Belgacom’s infrastructure, including internal employee computers and encrypted and unencrypted streams of private communications handled by the company.
Programs: CARBONROD“Operation Socialist: The Inside Story of How British Spies Hacked Belgium’s Largest Telco” - The Intercept ↗ (2014-12-13) · “Lees hier hoe de Britse geheime dienst GCHQ Belgacom aanviel” - NRC ↗ (2014-12-13) · “Britse geheime dienst bespioneerde jarenlang Belgacom-klanten” - De Standaard ↗ (2014-12-13) · Gallagher, Ryan · Modderkolk, Huib · Vanhecke, Nikolas · Eeckhaut, Mark -
Broadcast/Internet Radio Exploitation and Analysis, 6th November 2009, GCHQ [pdf]
This GCHQ report analyzes 6.68 million internet radio listening events collected over three months in 2009, detailing global broadcasting patterns, user behaviors, and specifically examining Islamic radio stations and Pakistan-UK connections for potential radicalization intelligence, while recommending integration with bulk surveillance databases like KARMA POLICE for enhanced user profiling.
-
DEFIANTWARRIOR and the NSA's Use of Bots [pdf]
This TOP SECRET NSA presentation from 2010 documents the DEFIANTWARRIOR effort to identify, seize, and operate botnets using SIGINT-enabled infrastructure, detailing both early failures and subsequent operational successes. The document reveals how bot herding was integrated into broader offensive cyber and intelligence collection strategies across the Five Eyes.
Programs: DEFIANTWARRIOR · OLYMPUS · UNITEDRAKE · TURBULENCE · QUANTUMBOT · TURMOIL · TURBINE · SNIPERS · XKEYSCORE · INCENSER · STELLABLUE · SMOKYSINK · STOVEPIPES · ISLANDTRANSPORT · FESTIVEWRAPPER · FREEFLOW · PRESSUREWAVE · HANGARSURPLUS · SURPLUSHANGER · WAITAUTO · DEEPFRIEDPIG · SEAGULLFARO · COLOSSUS · STORMPIG · YELLPIG · PASTEPIG · SHOUTPIG · ZORPIG · MAILORDER · TREASUREMAP · MARINA · WARNVOLCANO · STRAITBIZARRE · BOTINSTANCES · PUZZLECUBE · SEEKER · SURPLUSHANGAR -
FAD FY 12 CCP Funding of Partners [pdf]
A Foreign Affairs Directorate slide showing Combined Cryptologic Program funding of foreign partners in fiscal year 2012, in thousands of dollars, across fifteen countries including Canada, Israel, Japan, Jordan, Pakistan, Taiwan and Thailand.
-
GCHQ - PCS Harvesting [pdf]
A TOP SECRET STRAP1 report details how GCHQ industrialized the theft of GSM subscriber authentication keys (Ki) by automating trawls of bulk “C2C” content to extract IMSI/Ki pairs from emails and FTP transfers between SIM personalisation centers and mobile operators. It shows the program scaling key harvesting across networks and countries, complementing computer network exploitation against core mobile infrastructure to suppress billing and lift authentication secrets.
-
Guidelines for the classification of NSA SIGINT details (1945-1967) [pdf]
This document is an NSA classification guide that defines how and why historical SIGINT material from 1945–1967 remains classified, in many cases for 75 years. It systematically explains which intelligence activities, targets, partnerships, and technical methods must stay protected because they still reveal sensitive sources, methods, and diplomatic equities.
-
JORDAN-BELGIUM [pdf]
2008 GCHQ report documenting the interception of a Jordan–Belgium satellite telecommunications link, through which British intelligence monitored call traffic and identified tasked surveillance targets including the Turkish foreign ministry, Palestinian Authority figures and Israeli MK Ahmad Tibi, along with other hits on Kurdish leadership, diplomats, and Jordanian government offices such as the Royal Protocol Office. The published copies redact different entries. Der Spiegel's and The Intercept's show the Turkish and Kurdish ones, Le Monde's (version 8BBAC) the Palestinian and Jordanian ones.
People: Tibi, Ahmad“Turkey Is 'Partner and Target' for the NSA” - Der Spiegel ↗ (2014-08-31) · “How the NSA Helped Turkey Kill Kurdish Rebels” - The Intercept ↗ (2014-08-31) · “L’Autorité palestinienne et la Jordanie espionnées par les services américains et britanniques” - Le Monde ↗ (2016-12-07) · Poitras, Laura · Rosenbach, Marcel · Sontheimer, Michael · Stark, Holger · Follorou, Jacques -
-
List of foreign governments and organizations authorized for surveillance [pdf]
This exhibit lists the 193 foreign governments as well as foreign factions, political organizations and other entities that were part of a 2010 certification approved by the Foreign Intelligence Surveillance Court. These are the entities about which the NSA may conduct surveillance, for the purpose of gathering foreign intelligence. Each year a new certification must be approved by the court to permit such surveillance under Section 702 of the FISA Amendments Act.
-
OP HIGHLAND FLING - Event Log [pdf]
A TOP SECRET operational event log from GCHQ's GCWiki documenting a January 2011 operation targeting Gemalto employees in France, Poland and elsewhere, using MUTANT BROTH cookie analysis, Facebook credentials, LinkedIn profiles and Computer Network Exploitation to identify and implant targets as part of the operation to steal SIM card encryption keys.
-
ORANGECRUSH, part of the OAKSTAR program [pdf]
An SSO item reporting that ORANGECRUSH — the OAKSTAR access at a third-party partner site in Poland, known to the Poles only as BUFFALOGREEN — began forwarding metadata to NSA on 3 March and content on 25 March, with collection shared to Second Parties through TICKETWINDOW.
-
Partner Cables [pdf]
A classified table mapping which GCHQ cable interception programs had access to specific undersea fiber optic cables worldwide, revealing the codenames and access types — either Direct Cable Order or Indefeasible Right of Use/Landing Capacity — of seven surveillance programs across dozens of international cable systems, with Cable & Wireless (GERONTIC) providing access to the largest number.
“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
PRC Information Warfare & Huawei [pdf]
This NSA intelligence briefing on Huawei analyzes Huawei’s global telecommunications presence and its potential links to the People’s Liberation Army (PLA) and Chinese government intelligence activities. It highlights concerns that Huawei’s international market expansion — including its subcontracted 2008 upgrade of the TAT-14 transatlantic cable carrying U.S. and defense communications — could be exploited by China for signals intelligence (SIGINT) purposes.
People: Chávez, Hugo -
Project CAMBERDADA [pdf]
NSA presentation on Project CAMBERDADA, a programme that intercepts emails sent to antivirus companies reporting new malware, uses SIGINT collection to monitor antivirus vendor communications, and identifies opportunities to repurpose malware before vendors detect it — listing 23 antivirus companies from around the world as targets, with Kaspersky as the primary focus.
People: Picard, François -
Sharing Computer Network Operations Cryptologic Information with Foreign Partners [pdf]
The document is a secret NSA/CSS policy outlining guidelines for sharing Computer Network Operations (CNO) cryptologic information with foreign partners, including rules for cooperation in CNE and CND within existing intelligence relationships. The “Purpose and Scope” section on the first page appears to be unpublished elsewhere, while the Tier A and Tier B country lists match those publicly revealed in sources like Glenn Greenwald’s No Place to Hide.
“El CNI facilitó el espionaje masivo de EEUU a España” - El Mundo ↗ (2013-10-30) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Greenwald, Glenn · Aranda, Germán -
SNOWGLOBE: From Discovery to Attribution [pdf]
This document describes how CSEC identified and analyzed the SNOWGLOBE intrusion set, using passive collection, implant reverse engineering, and infrastructure analysis to attribute the campaign with moderate confidence to a French intelligence service targeting Iranian and international scientific, diplomatic, and political organizations.
Programs: SNOWGLOBE · WARRIORPRIDE · REPLICANTFARM · SNOWBALL · SNOWMAN · EONBLUE · SPECIALSOURCE · CANDLEGLOWPeople: Roshal, Alexander“The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · “Quand les Canadiens partent en chasse de « Babar »” - Le Monde ↗ (2014-03-21) · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael · Follorou, Jacques · Untersinger, Martin