Country: Pakistan 197 documents
Search documents matching “Pakistan” →Countries mentioned in each document. A country may be mentioned directly (e.g., France) or inferred from a related reference, such as a city (Paris -> France) or a domain name (.fr -> France).
Graphs
By document date (12 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
CSEC Surveillance of Travellers Through Airport Wi-Fi Tracking [pdf]
The leaked 2012 top secret CSEC presentation details a trial program that used airport Wi-Fi metadata to identify and track travellers’ devices across Canada and internationally, developing advanced “IP profiling” techniques to map movements through hotels, airports, and public hotspots. The program, conducted with NSA support, aimed to build powerful analytic tools for surveillance and real-time alerts within the Five Eyes intelligence network.
Marking: TOP SECRET -
DEFIANTWARRIOR and the NSA's Use of Bots [pdf]
This TOP SECRET NSA presentation from 2010 documents the DEFIANTWARRIOR effort to identify, seize, and operate botnets using SIGINT-enabled infrastructure, detailing both early failures and subsequent operational successes. The document reveals how bot herding was integrated into broader offensive cyber and intelligence collection strategies across the Five Eyes.
Programs: DEFIANTWARRIOR · OLYMPUS · UNITEDRAKE · TURBULENCE · QUANTUMBOT · TURMOIL · TURBINE · SNIPERS · XKEYSCORE · INCENSER · STELLABLUE · SMOKYSINK · STOVEPIPES · ISLANDTRANSPORT · FESTIVEWRAPPER · FREEFLOW · PRESSUREWAVE · HANGARSURPLUS · SURPLUSHANGER · WAITAUTO · DEEPFRIEDPIG · SEAGULLFARO · COLOSSUS · STORMPIG · YELLPIG · PASTEPIG · SHOUTPIG · ZORPIG · MAILORDER · TREASUREMAP · MARINA · WARNVOLCANO · STRAITBIZARRE · BOTINSTANCES · PUZZLECUBE · SEEKER · SURPLUSHANGAR -
EP-3E Collision: Cryptologic Damage Assessment and Incident Review [pdf]
A joint US Navy and NSA report from July 2001, prepared three months after a US spy plane was forced to land in China, assessing how far surveillance sources and methods were compromised and reviewing the emergency destruction that failed to prevent it. Damage to tactical SIGINT against the PRC is rated medium and overall SIGINT damage low, with the greatest loss the LUNCHBOX PROFORMA processor and MARTES signals analysis tools; COMSEC damage is rated low because keying material was superseded within 15 hours.
Programs: LUNCHBOX · MARTES · NICKELBACK · SENSOR PACER · PROFORMA · HULTEC · STRUM · TEXTA · RASIN · CRITIC · KLIEGLIGHT · XBIT · BLACKMAGIC · NOIWON · ZIRCON · MIDB · EOB-LITE · NIMROD · ARIEL · COBRA BALL · COMBAT SENT · RIVET JOINT · SEABOOT · SETTEE · KAMPUS · DRUID · RORIPA · MARKHAM · FOREJUDGE · SAM HEARTBURN · NOVELETTE · RSBN · BEGGAR HAWK · BEGGAR SHADOW · CAPSULE JACK · DISTANT WIND · DISTANT SENT · CHILING · RIBBED · UNACCENTED · SLIPSTICK · SIERRA ONEPeople: Meals, Charlie -
Excerpt of May 2008 NSA Afghanistan Dataflow Analysis [pdf]
The document outlines how the NSA’s Real Time Regional Gateway (RT-RG) in Afghanistan progressively expanded from late 2007 through 2008 to ingest massive amounts of GSM, VHF, HF, and telephony metadata from dozens of locations across Afghanistan, supplemented by third-party “dirtbox” collection from allied nations such as the Netherlands, Denmark, Norway, Germany, and Spain. It details the specific collection sites, data types, and timelines (SPIN 9, 10, 11, etc.), illustrating how partner contributions and multiple signals sources fed into the RT-RG system to enable real-time intelligence.
Programs: FOURCORNERS · FORTRESS · WARRIOR · ECHIDNA · CASSIEOPIA · KARUS · SOUNDER · SNICK · TEMPOWOLFE · CALYPSO · TATTERAN · AIRBORNE · LEAVEBEHIND · UDEAUS · NELEUS · CROSSHAIR · SSO · DRT · RIVET JOINT · VOICESAIL“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
Exploiting Foreign Lawful Intercept (LI) Roundtable [pdf]
Top-secret PowerPoint presentation, "Exploiting Foreign Lawful Intercept Roundtable," highlights the agency’s strategy to exploit vulnerabilities in lawful intercept systems from telecom companies, such as Ericsson, Motorola, and Nokia, in countries like Mexico, Indonesia, and Egypt. The presentation also discusses NSA's use of various "Fingerprints" for identifying data and its collaboration with industry players and foreign lawful intercept systems.
“A Death in Athens” - The Intercept ↗ (2015-09-28) · “Americans and Greeks started the 2004 wiretaps together” - Kathimerini ↗ (2015-09-29) · Bamford, James · Petropoulos, Aggelos -
Exploiting US/UK/CAN Phone Numbers -- In Compliance with USSID-18 Policy SIDtoday [pdf]
The NSA can now classify certain U.S. phone numbers as foreign, allowing them to be targeted. Such targeting may occur on a U.S. number if the phone number is “identified on foreign links” and if it is associated with a “Pick Your Own Number” internet service such as Vonage.
The Intercept ↗ (2018-08-15) -
Eye-Opening Experience in Haiti (part 1) SIDtoday [pdf]
An intelligence analysis intern was deployed to Haiti on a National Intelligence Support Team, which includes personnel from NSA, CIA, NGA, and DIA. There were operational challenges because the Marines on the ground had not requested the NIST deployment.
The Intercept ↗ (2017-04-24) -
Eye-Opening Experience in Haiti (part 2) SIDtoday [pdf]
The intelligence analysis intern deployed to Haiti describes how the SIGINT used by tactical forces on the ground is different from the product for most SID customers.
The Intercept ↗ (2017-04-24) -
F6, NSA Texas, and Yakima Research Station Collaborate on Venezuela Survey SIDtoday [pdf]
In the first in a series about SIGINT Development (SIGDEV) collaboration, the authors describe how three different departments worked together to develop new sources of signals intelligence on Venezuela. The Special Collection Service (F6), NSA Texas, and the Yakima Research Center worked on a remote survey that "uncovered dozens of links carrying traffic for Venezuelan targets of interest."
Programs: ESECSThe Intercept ↗ (2019-05-29) -
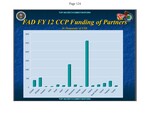
FAD FY 12 CCP Funding of Partners [pdf]
A Foreign Affairs Directorate slide showing Combined Cryptologic Program funding of foreign partners in fiscal year 2012, in thousands of dollars, across fifteen countries including Canada, Israel, Japan, Jordan, Pakistan, Taiwan and Thailand.
-
Finding and Querying Document Metadata [pdf]
This 2009 NSA training guide, created by Booz Allen Hamilton, explains how analysts can use the XKEYSCORE system to track targets by searching for "non-traditional selectors" embedded within documents, such as author names, company information, or even the hash values of company logos.
Programs: XKEYSCORE · TUNINGFORK · PINWALE · FOXACID · FOXBASE · CARBOY · CARDAMON · UNITEDRAKE · CADENCE -
FININT Tasking [pdf]
This document outlines GCHQ's financial intelligence (FININT) operations, detailing the use of tools like LUCKY STRIKE and LUCKY ESCAPE to search and fuse datasets from financial and travel sources. It also describes procedures for requesting financial checks on individuals and mentions the collection of bulk banking and credit card data from specific regions.
Programs: TRACFIN · LUCKY STRIKE · LUCKY ESCAPE · TAPERLAY · TMM · MOON RAKER · BROADOAK · FININTTRACKER · FINTOOLS · FOLLOWTHEMONEY · PLATINUMPLUS · RUSSETT -
Free File Uploaders [pdf]
This 2009 NSA training presentation for the XKEYSCORE system details how analysts can monitor Free File Uploader (FFU) websites like Zshare and RapidShare, which are difficult to track due to a lack of strong selectors. The guide introduces the "Web File Transfer" plug-in, a specialized tool designed to extract key metadata like original filenames and download/delete links from FFU web traffic.
-
Friedman Presentation: The US in Asia: The White House Roadmap SIDtoday [pdf]
The National Security Council senior director for Asia, a special assistant to the president, will speak about the administration's perspective on Asia.
The Intercept ↗ (2017-09-13) -
Full Log vs HTTP [pdf]
This 2009 NSA training presentation explains the difference between using the "Full Log" and "HTTP Activity" queries in the XKEYSCORE surveillance system, showing analysts how to use both in tandem to gain a complete picture of a target's online activities, including identifying the use of anonymizing proxies.
-
FY 2013 Congressional Budget Justification, Volume I, National Intelligence Program Summary, February 2012 [pdf]
This document outlines the $52.6 billion “black budget,” detailing the structure, priorities, successes, and shortcomings of the 16 U.S. intelligence agencies. It reveals unprecedented insight into funding allocations, operations, and intelligence gaps—including the CIA’s dominant role, expanding cyber operations, and persistent challenges in areas such as North Korea and counterterrorism—while emphasizing the tension between secrecy and public accountability.
-
-
-
FY2013 Congressional Budget Justification Bin Laden Excerpts [pdf]
This document includes excerpts from the 2013 National Intelligence Program budget justification describing the integrated intelligence community efforts that led to locating and raiding Osama bin Laden's compound, detailing contributions from NSA's signal intelligence, CIA's geolocation analysis, NGA's imagery modeling, and post-raid forensic DNA confirmation.
People: bin Laden, Osama -
GCHQ - PCS Harvesting [pdf]
A TOP SECRET STRAP1 report details how GCHQ industrialized the theft of GSM subscriber authentication keys (Ki) by automating trawls of bulk “C2C” content to extract IMSI/Ki pairs from emails and FTP transfers between SIM personalisation centers and mobile operators. It shows the program scaling key harvesting across networks and countries, complementing computer network exploitation against core mobile infrastructure to suppress billing and lift authentication secrets.