Country: Italy 81 documents
Search documents matching “Italy” →Countries mentioned in each document. A country may be mentioned directly (e.g., France) or inferred from a related reference, such as a city (Paris -> France) or a domain name (.fr -> France).
Graphs
By document date (11 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
CSEC Cyber Threat Capabilities [pdf]
This document details CSEC’s full-spectrum cyber operations architecture, integrating SIGINT and IT Security to conduct both defensive and offensive activities under the guise of “information superiority.” While early sections emphasize detection, anomaly analysis, and collaboration with Five Eyes partners, later portions reveal active measures including network infiltration (implant deployment), command-and-control tracking, traffic manipulation and redirection, DNS interference, and potential disruption or deception operations—illustrating CSEC’s capacity not only to defend Canadian networks but also to surveil, exploit, and influence foreign and domestic digital infrastructure.
Programs: EONBLUE · CYBERDMZ · SEEDSPHERE · PHOTONICPRISM · SPECIALSOURCE · SUPERDRAKE · DARKSPACE · QUANTUM · MANDATE · STREAMING SENTRY · SSO · TKB · COVENANT -
Driver 1: Worldwide SIGINT/Defense Cryptologic Platform [pdf]
A 2012 NSA management presentation slide revealing the agency's global surveillance architecture across five categories of access — covert cable taps, regional collection sites, computer network exploitation implants, foreign satellite collection, and third-party liaison relationships — including a list of cities hosting clandestine collection operations and confirmation of over 50,000 worldwide malware implants.
Programs: STELLAR · SOUNDER · SNICK · MOONPENNY · LADYLOVE · INDRA · IRONSAND · JACKKNIFE · CARBOY · TIMBERLINE“NSA infected 50,000 computer networks with malicious software” - NRC ↗ (2013-11-23) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Boon, Floor · Derix, Steven · Modderkolk, Huib · Greenwald, Glenn -
EP-3E Collision: Cryptologic Damage Assessment and Incident Review [pdf]
A joint US Navy and NSA report from July 2001, prepared three months after a US spy plane was forced to land in China, assessing how far surveillance sources and methods were compromised and reviewing the emergency destruction that failed to prevent it. Damage to tactical SIGINT against the PRC is rated medium and overall SIGINT damage low, with the greatest loss the LUNCHBOX PROFORMA processor and MARTES signals analysis tools; COMSEC damage is rated low because keying material was superseded within 15 hours.
Programs: LUNCHBOX · MARTES · NICKELBACK · SENSOR PACER · PROFORMA · HULTEC · STRUM · TEXTA · RASIN · CRITIC · KLIEGLIGHT · XBIT · BLACKMAGIC · NOIWON · ZIRCON · MIDB · EOB-LITE · NIMROD · ARIEL · COBRA BALL · COMBAT SENT · RIVET JOINT · SEABOOT · SETTEE · KAMPUS · DRUID · RORIPA · MARKHAM · FOREJUDGE · SAM HEARTBURN · NOVELETTE · RSBN · BEGGAR HAWK · BEGGAR SHADOW · CAPSULE JACK · DISTANT WIND · DISTANT SENT · CHILING · RIBBED · UNACCENTED · SLIPSTICK · SIERRA ONEPeople: Meals, Charlie -
First-Ever Formal SIGINT Development (SIGDEV) Training Is Provided to SIGINT Seniors Europe (SSEUR) Partners [pdf]
This internal NSA report details the first formal training course on "SIGINT Development" (SIGDEV) offered to the "SIGINT Seniors Europe" (SSEUR) coalition, a group comprising the Five Eyes nations and nine European third-party partners. The document highlights the strategic goal of standardizing analytic tradecraft among these allies to improve collaboration on priority missions like counter-terrorism and the war in Afghanistan.
“New NSA Revelations: Inside Snowden's Germany File” - Der Spiegel ↗ (2014-06-18) · “Read the Snowden Documents From the NSA” - SVT Nyheter ↗ (2013-12-11) · Becker, Sven · Gude, Hubert · Horchert, Judith · Müller-Maguhn, Andy · Poitras, Laura · Reißmann, Ole · Rosenbach, Marcel · Schindler, Jörg · Schmid, Fidelius · Sontheimer, Michael · Stark, Holger · Björklund, Axel -
Fourth Party Opportunities [pdf]
This presentation document explains how NSA identifies, prioritizes, and exploits “fourth party” opportunities by passively or actively leveraging foreign computer network exploitation operations, including victim stealing and tool repurposing, to collect intelligence without initiating original intrusions.
Programs: VOYEUR · UIS · PINWALE · YNKE · TUNINGFORK · DIRTSHED · SEEKER · CLOUD · ABR · SILVERBOLT · DEADSEA · XKEYSCORE · BYZANTINERAPTOR · HAWALA · ZEBEDEE · DATAFLURRY · ECLECTICPLOT · HAPPYFOOT · BLUESMOKE · CROSSBONES2 · CYBERQUEST · VICDB · PLAIDDIANA · TRANSGRESSION -
From the SID Mailbag: When To Mark Things 'COMINT' SIDtoday [pdf]
The COMINT (Communications Intelligence) classification marking, along with Special Intelligence, often refers to information derived from foreign communications. However, the marking can also be used for “SIGINT equities that support the production of Communications Intelligence.” For example, secret information-sharing arrangements with foreign governments are classified SI, because these relationships lead to the acquisition of foreign communications.
Programs: ITISThe Intercept ↗ (2018-03-01) -
GCHQ - PCS Harvesting [pdf]
A TOP SECRET STRAP1 report details how GCHQ industrialized the theft of GSM subscriber authentication keys (Ki) by automating trawls of bulk “C2C” content to extract IMSI/Ki pairs from emails and FTP transfers between SIM personalisation centers and mobile operators. It shows the program scaling key harvesting across networks and countries, complementing computer network exploitation against core mobile infrastructure to suppress billing and lift authentication secrets.
-
GOOOOAAAALLLL!!! -- World Cup Report from SUSLAG SIDtoday [pdf]
NSA kept a watchful eye during the soccer World Cup in Germany, providing "extended-hours support" to the hosts, and in coordination with a number of additional partner nations.
Programs: SISECT“The Powerful Global Spy Alliance You Never Knew Existed” - The Intercept ↗ (2018-03-01) · The Intercept ↗ (2019-05-29) · Gallagher, Ryan -
Guidelines for the classification of NSA SIGINT details (1945-1967) [pdf]
This document is an NSA classification guide that defines how and why historical SIGINT material from 1945–1967 remains classified, in many cases for 75 years. It systematically explains which intelligence activities, targets, partnerships, and technical methods must stay protected because they still reveal sensitive sources, methods, and diplomatic equities.
-
How NSA Is Prepared for the Winter Olympics (Which Kick Off Tomorrow) SIDtoday [pdf]
NSA is ready for yet another Olympics in the geographically challenging Italian alps. A SCIF has been set up and analyst deployed to Turin and the National Counterterrorism Center in Virginia. Though the Italians are deemed better at providing security than the Greeks were in Athens, NSA will be "monitoring host government communications to verify security planning, performance and sharing of threat information."
Programs: VOICESAILPeople: Bush, LauraThe Intercept ↗ (2018-08-15) -
Improving Our Capability to Collect Against the Thuraya Satellite SIDtoday [pdf]
An upgraded system targeting the Thuraya satellite phone network has been installed in 23 sites across Europe, the Middle East and Central Asia. On an average day the systems collected "over 500,000 call events", including "20,000 calls of potential interest to NSA analysts."
The Intercept ↗ (2019-05-29) -
InSIDer's View of History... A Lesson in Personal Accountability SIDtoday [pdf]
SID Chief of Staff Charles Berlin discloses something startling: "As many of you know, our forces in Iraq are dropping bombs on the strength of SIGINT alone." He says this while sharing a story of a commander who was concerned about culpability for war crimes.
The Intercept ↗ (2016-12-07) -
InSIDer's View of History... A Lesson in Personal Accountability (repost) SIDtoday [pdf]
(Repost) SID Chief of Staff Charles Berlin discloses something startling: "As many of you know, our forces in Iraq are dropping bombs on the strength of SIGINT alone." He says this while sharing a story of a commander who was concerned about culpability for war crimes.
The Intercept ↗ (2017-04-24) -
InSIDer's View of History: The Adventure Continues -- Evacuation from Belgrade SIDtoday [pdf]
Anecdote about being in Belgrade when an attempt at diplomacy failed, tensely evacuating the embassy, and fleeing the country the same day the U.S. started bombing Serbia. About $6 million worth of equipment was intentionally destroyed in "a little over six hours."
The Intercept ↗ (2016-12-07) -
Intelligence Need Released to Third Parties SIDtoday [pdf]
The NSA released its first-ever "intelligence need" ”” a request for assistance in collecting signals intelligence from Second and Third Party partners ”” in monitoring a specific information target relating to the Iraqi election. An Italian partner responded with an extensive report.
Programs: SISECTThe Intercept ↗ (2017-09-13) -
Intelligently filtering your data: Brazil and Mexico case studies [pdf]
These documents reveal that the NSA conducted targeted surveillance operations against high-profile Brazilian and Mexican figures, including President Dilma Rousseff and presidential candidate Enrique Peña Nieto, using advanced contact-graph filtering and data analysis techniques to extract relevant intelligence from intercepted communications. These documents show how NSA analysts systematically developed intelligence on foreign leaders during election periods and diplomatic activities, framing it as “target development,” but in practice enabling deep political espionage under the guise of analytical innovation.
“Veja os documentos ultrassecretos que comprovam espionagem a Dilma” - O Globo ↗ (2013-09-02) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Greenwald, Glenn -
Internal NSA presentation on the BND's organization [pdf]
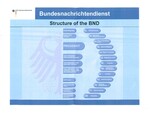
These six organizational charts and briefing slides detail the structure of Germany's BND foreign intelligence service, specifically its SIGINT Directorate (Abteilung Technische Aufklärung) and new Cyber Intelligence division (T4), along with a cooperation model showing intelligence sharing between BND, domestic intelligence service BfV, and the Federal Office for Information Security (BSI).
-
Internet Anonymity 2011 [pdf]
A TOP SECRET NSA presentation from 2011 providing a comprehensive survey of Internet Anonymity Technologies (IAT) — covering HTTP proxies, VPN anonymity providers, multi-hop networks including Tor and JAP, anonymous remailers and circumvention tools — alongside NSA's capabilities and limitations against each, including XKEYSCORE fingerprints for VPN identification, the PARTNERSNIPPET Tor deanonymisation team, GOLDENFORTIN Netflow data, and a candid assessment that Tor offers "no passive exploitation."
Programs: FOXTRAIL · NKB · NACIRONIN · PONTENTPOTABLES · RONIN · XKEYSCORE · PARTNERSNIPPET · GOLDENFORTIN · SNAPEPeople: Heap, Austin -
Interview with... Charlie Meals, Signals Intelligence Deputy Director SIDtoday [pdf]
In an interview, the deputy director describes his early days in the NSA's "weather shop," decrypting Soviet weather reports.
The Intercept ↗ (2017-04-24) -
List of foreign governments and organizations authorized for surveillance [pdf]
This exhibit lists the 193 foreign governments as well as foreign factions, political organizations and other entities that were part of a 2010 certification approved by the Foreign Intelligence Surveillance Court. These are the entities about which the NSA may conduct surveillance, for the purpose of gathering foreign intelligence. Each year a new certification must be approved by the court to permit such surveillance under Section 702 of the FISA Amendments Act.