Country: India 85 documents
Search documents matching “India” →Countries mentioned in each document. A country may be mentioned directly (e.g., France) or inferred from a related reference, such as a city (Paris -> France) or a domain name (.fr -> France).
Graphs
By document date (12 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
CROSSHAIR — Foreign Partners Filling HF/DF Gaps for the US SIDtoday [pdf]
The U.S. closed a number of High Frequency Direction-Finding sensor sites in the 1990s. To ensure they're able to track signals in areas that had previously been covered by now-shuttered stations, the Signals Intelligence Directorate worked with Second and Third Party partners to share resources and establish a global direction-finding network.
Programs: CROSSHAIR“Japan Made Secret Deals With the NSA That Expanded Global Surveillance” - The Intercept ↗ (2017-04-24) · “アメリカに監視される日本 ~スノーデン“未公開ファイル”の衝撃” - NHK ↗ (2017-04-24) · The Intercept ↗ (2017-09-13) · Gallagher, Ryan · Ikegami, Akira -
Cryptologic shore support [pdf]
The document describes the Maritime Cryptologic Integration Centres (MCICs), which provide global SIGINT support to naval, air, and land units. Three MCICs operate within U.S. Fleet Information Operation Centres, while the fourth, uniquely joint U.K.–U.S. (RN/USN), is at RAF Digby in Lincolnshire, responsible for 24/7 cryptologic support to U.K. and allied missions across the North Atlantic, Barents, Baltic, and Black Seas, as well as North and Sub-Saharan Africa.
Marking: CONFIDENTIAL -
CSEC Surveillance of Travellers Through Airport Wi-Fi Tracking [pdf]
The leaked 2012 top secret CSEC presentation details a trial program that used airport Wi-Fi metadata to identify and track travellers’ devices across Canada and internationally, developing advanced “IP profiling” techniques to map movements through hotels, airports, and public hotspots. The program, conducted with NSA support, aimed to build powerful analytic tools for surveillance and real-time alerts within the Five Eyes intelligence network.
Marking: TOP SECRET -
Discovery SIGINT Targeting Scenarios and Compliance [pdf]
This document is a top-secret NSA guidance manual detailing SIGINT targeting scenarios, compliance procedures, and legal guidance for querying foreign actors, malware, and potentially U.S.-linked systems, including considerations for minimizing incidental collection of U.S. persons’ communications. It outlines specific rules, approvals, and exceptions for using SIGINT tools, foreign intelligence tasks, and cases involving ambiguous or dual-use selectors like WikiLeaks, The Pirate Bay, and foreign actors operating through U.S. infrastructure.
-
Driver 1: Worldwide SIGINT/Defense Cryptologic Platform [pdf]
A 2012 NSA management presentation slide revealing the agency's global surveillance architecture across five categories of access — covert cable taps, regional collection sites, computer network exploitation implants, foreign satellite collection, and third-party liaison relationships — including a list of cities hosting clandestine collection operations and confirmation of over 50,000 worldwide malware implants.
Programs: STELLAR · SOUNDER · SNICK · MOONPENNY · LADYLOVE · INDRA · IRONSAND · JACKKNIFE · CARBOY · TIMBERLINE“NSA infected 50,000 computer networks with malicious software” - NRC ↗ (2013-11-23) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Boon, Floor · Derix, Steven · Modderkolk, Huib · Greenwald, Glenn -
EP-3E Collision: Cryptologic Damage Assessment and Incident Review [pdf]
A joint US Navy and NSA report from July 2001, prepared three months after a US spy plane was forced to land in China, assessing how far surveillance sources and methods were compromised and reviewing the emergency destruction that failed to prevent it. Damage to tactical SIGINT against the PRC is rated medium and overall SIGINT damage low, with the greatest loss the LUNCHBOX PROFORMA processor and MARTES signals analysis tools; COMSEC damage is rated low because keying material was superseded within 15 hours.
Programs: LUNCHBOX · MARTES · NICKELBACK · SENSOR PACER · PROFORMA · HULTEC · STRUM · TEXTA · RASIN · CRITIC · KLIEGLIGHT · XBIT · BLACKMAGIC · NOIWON · ZIRCON · MIDB · EOB-LITE · NIMROD · ARIEL · COBRA BALL · COMBAT SENT · RIVET JOINT · SEABOOT · SETTEE · KAMPUS · DRUID · RORIPA · MARKHAM · FOREJUDGE · SAM HEARTBURN · NOVELETTE · RSBN · BEGGAR HAWK · BEGGAR SHADOW · CAPSULE JACK · DISTANT WIND · DISTANT SENT · CHILING · RIBBED · UNACCENTED · SLIPSTICK · SIERRA ONEPeople: Meals, Charlie -
Exploiting US/UK/CAN Phone Numbers -- In Compliance with USSID-18 Policy SIDtoday [pdf]
The NSA can now classify certain U.S. phone numbers as foreign, allowing them to be targeted. Such targeting may occur on a U.S. number if the phone number is “identified on foreign links” and if it is associated with a “Pick Your Own Number” internet service such as Vonage.
The Intercept ↗ (2018-08-15) -
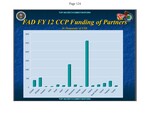
FAD FY 12 CCP Funding of Partners [pdf]
A Foreign Affairs Directorate slide showing Combined Cryptologic Program funding of foreign partners in fiscal year 2012, in thousands of dollars, across fifteen countries including Canada, Israel, Japan, Jordan, Pakistan, Taiwan and Thailand.
-
Friedman Presentation: The US in Asia: The White House Roadmap SIDtoday [pdf]
The National Security Council senior director for Asia, a special assistant to the president, will speak about the administration's perspective on Asia.
The Intercept ↗ (2017-09-13) -
GCHQ - PCS Harvesting [pdf]
A TOP SECRET STRAP1 report details how GCHQ industrialized the theft of GSM subscriber authentication keys (Ki) by automating trawls of bulk “C2C” content to extract IMSI/Ki pairs from emails and FTP transfers between SIM personalisation centers and mobile operators. It shows the program scaling key harvesting across networks and countries, complementing computer network exploitation against core mobile infrastructure to suppress billing and lift authentication secrets.
-
GCHQ Intelligence Production Head Outlines Present and Future Priorities SIDtoday [pdf]
According to a talk recently given at NSA's UK base in Menwith Hill, counterterrorism absorbs most (30%) of GCHQ's resources. Afghanistan and China are given increasing attention, while Russia gets less. Long term, GCHQ foresees challenges in keeping up with the internet and "huge amounts of data", while peace is expected in Iraq.
People: Ashton, JonThe Intercept ↗ (2019-05-29) -
GCSB SIGINT Development Quarterly Report [pdf]
This GCSB quarterly report from July 2009 provides a Top Secret review of major telecommunications developments in the South West Pacific, focusing on the intelligence challenges posed by competitive deregulation and new infrastructure projects, while also detailing GCSB's efforts to enhance its collection capabilities, including the fine-tuning of GSM collection in the Solomon Islands, supporting DSD analyses in Fiji, and preparing for full-take XKEYSCORE data sharing with allies.
“New Zealand Spies on Neighbors in Secret "Five Eyes" Global Surveillance” - The Intercept ↗ (2015-03-04) · “Snowden revelations / The price of the Five Eyes club: Mass spying on friendly nations” - The New Zealand Herald ↗ (2015-03-04) · “New Zealand Spy Data Shared With Bangladeshi Human Rights Abusers” - The Intercept ↗ (2015-04-15) · “Secret documents shine light on GCSB spying in Bangladesh” - The New Zealand Herald ↗ (2015-04-16) · Gallagher, Ryan · Hager, Nicky -
Guide to Using Contexts in XKS Fingerprints [pdf]
This technical guide explains how NSA analysts use "contexts" within XKEYSCORE fingerprints to create highly targeted surveillance queries by restricting searches to specific scopes (e.g., web searches, document bodies, geographic locations), enabling precision targeting such as finding "all people in Kabul performing web searches on Jihad" while avoiding the overwhelming noise of broader keyword searches.
-
IMT Changes: Fewer, All Full-Time SIDtoday [pdf]
Eighteen months after its inception, the Issue Management Team program is changing. There will be fewer teams, but all the new IMTs will be full-time positions.
The Intercept ↗ (2017-04-24) -
Intelligently filtering your data: Brazil and Mexico case studies [pdf]
These documents reveal that the NSA conducted targeted surveillance operations against high-profile Brazilian and Mexican figures, including President Dilma Rousseff and presidential candidate Enrique Peña Nieto, using advanced contact-graph filtering and data analysis techniques to extract relevant intelligence from intercepted communications. These documents show how NSA analysts systematically developed intelligence on foreign leaders during election periods and diplomatic activities, framing it as “target development,” but in practice enabling deep political espionage under the guise of analytical innovation.
“Veja os documentos ultrassecretos que comprovam espionagem a Dilma” - O Globo ↗ (2013-09-02) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Greenwald, Glenn -
Internet Anonymity 2011 [pdf]
A TOP SECRET NSA presentation from 2011 providing a comprehensive survey of Internet Anonymity Technologies (IAT) — covering HTTP proxies, VPN anonymity providers, multi-hop networks including Tor and JAP, anonymous remailers and circumvention tools — alongside NSA's capabilities and limitations against each, including XKEYSCORE fingerprints for VPN identification, the PARTNERSNIPPET Tor deanonymisation team, GOLDENFORTIN Netflow data, and a candid assessment that Tor offers "no passive exploitation."
Programs: FOXTRAIL · NKB · NACIRONIN · PONTENTPOTABLES · RONIN · XKEYSCORE · PARTNERSNIPPET · GOLDENFORTIN · SNAPEPeople: Heap, Austin -
Interns Now Contributing from Day One SIDtoday [pdf]
An intelligence analysis intern recounts how, due to high volumes of data, he was thrown right into “prosecuting critical targets within weeks of arriving” and learned that the Signals Intelligence Directorate is “not quite satellites, but not really Dilbert either.”
Marking: TOP SECRETPrograms: FOLLOWTHEMONEYThe Intercept ↗ (2018-08-15) -
INTOLERANT – Who Else Is Targeting Your Target? Collecting Data Stolen by Hackers – SIDtoday SIDtoday [pdf]
A TOP SECRET SIDToday article from Menwith Hill Station describing how NSA and CSEC discovered and began exploiting INTOLERANT — a sophisticated email-stealing hacking operation targeting Indian diplomats, Central Asian diplomats, Chinese human rights defenders, Tibetan pro-democracy activists, Uighur activists and European officials — by intercepting the stolen emails as they transited satellite links, a technique internally called "fourth party collection" or "outsourcing SIGINT."
Programs: INTOLERANT -
Intro to the VPN Exploitation Process [pdf]
NSA introduction to the VPN exploitation process from September 2010, presented by the OTP VPN Exploitation Team, covering the full workflow from initial collection through to sustained decryption of IPSec, PPTP, SSL and SSH traffic, with named exploitation successes including airlines, diplomatic missions, banks and intelligence services across Iran, Jordan, Russia, Turkey, Pakistan, Afghanistan, Somalia, Indonesia and Mexico.
Programs: BLEAKINQUIRY · TOYGRIPPE · XKEYSCORE · MAILORDER · CORALREEF · VULCANDEATHGRIP · SCISSORS · TURTLEPOWER · PINWALE · FOURSCORE · CADENCE · UTT · VULCANMINDMELD · CAPRIOS · AGILITY · NKB · FOLLOWTHEMONEY -
JORDAN-BELGIUM [pdf]
2008 GCHQ report documenting the interception of a Jordan–Belgium satellite telecommunications link, through which British intelligence monitored call traffic and identified tasked surveillance targets including the Turkish foreign ministry, Palestinian Authority figures and Israeli MK Ahmad Tibi, along with other hits on Kurdish leadership, diplomats, and Jordanian government offices such as the Royal Protocol Office. The published copies redact different entries. Der Spiegel's and The Intercept's show the Turkish and Kurdish ones, Le Monde's (version 8BBAC) the Palestinian and Jordanian ones.
People: Tibi, Ahmad“Turkey Is 'Partner and Target' for the NSA” - Der Spiegel ↗ (2014-08-31) · “How the NSA Helped Turkey Kill Kurdish Rebels” - The Intercept ↗ (2014-08-31) · “L’Autorité palestinienne et la Jordanie espionnées par les services américains et britanniques” - Le Monde ↗ (2016-12-07) · Poitras, Laura · Rosenbach, Marcel · Sontheimer, Michael · Stark, Holger · Follorou, Jacques