Classification: STRAP 1 107 documents
Search documents matching “STRAP 1” →Each document's classification level, as component values. If a document contains multiple classifications, the highest is used here.
Graphs
By Banner
Refine (combine with another filter, via search)
Sort: Title
Documents
-
A potential technique to deanonymise users of the TOR network [pdf]
A TOP SECRET GCHQ research presentation describing a traffic correlation attack against Tor — using cumulative packet counts observed simultaneously at a controlled exit node and at SIGINT collection points near a target's guard node to deanonymise Tor users without breaking the encryption — with GTE and JTRIG having adapted owned exit nodes to collect the required data for live deployment.
-
A potential technique to deanonymise users of the TOR network [pdf]
The GCHQ technical report documenting the entry-exit traffic correlation attack against Tor — providing the complete mathematical specification, test methodology, experimental results and software reference implementation, with distribution to NSA R1, NSA R4, NSA CES, CSE, DSD, SEQUOIA, ICTR, JTRIG, TEA, GTE and multiple OPC divisions.
-
Access to the future [pdf]
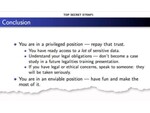
The conclusion slide excerpt of a GCHQ presentation on TEMPORA, telling analysts they are in a "privileged" and "enviable" position with ready access to a great deal of sensitive data, and to "have fun and make the most of it".
Programs: TEMPORA -
AFRICAN INBOUND DVB-S2 CARRIER [pdf]
2009 GCHQ report documents the survey and tasking of an African inbound satellite data carrier (DVB-S2) carrying internet traffic from Nigerian, Kenyan, and Zambian ISPs, intercepted via the TERRAIN collection suite. Among the identified targets were Israeli diplomatic and defense-related selectors — including the Israeli Prime Minister, an Israeli UAV/drone entity, and the Israeli embassies in Abuja (Nigeria) and Nairobi (Kenya) — as well as the Palestinian Authority embassy to Belgium.
-
AIRHANDLER missions Feb 2010 [pdf]
A communications survey in Helmand Province (Jan–Feb 2010) mapped line-of-sight and satellite activity to support allied operations. Between July and December 2009, RAF Digby conducted 148 AIRHANDLER drone surveillance missions, generating 363 intelligence reports.
Programs: AIRHANDLER -
APPARITION/GHOSTHUNTER TASKING INFO [pdf]
The document details how the NSA’s and GCHQ’s GHOSTHUNTER and APPARITION systems, based primarily at Menwith Hill Station, are used to geolocate VSAT satellite modems for both real-time operational support and strategic intelligence. It explains tasking priorities, coordination processes, and how geolocation results are shared through systems like Mastershake to support surveillance and capture/kill missions.
Programs: APPARITION · GHOSTHUNTER · SOUNDER · CARD · LADYLOVE · JACKNIFE · MOONPENNY · CARBOY · MASTERSHAKE · TRYST -
Assessment of Intelligence Opportunity - Juniper [pdf]
This document reveals that GCHQ, with NSA cooperation, developed capabilities to exploit vulnerabilities in 13 Juniper NetScreen firewall models and was expanding efforts to target Juniper’s broader JUNOS-based products for intelligence collection. It highlights the agencies’ strategic focus on maintaining access to critical network infrastructure globally, leveraging Juniper’s widespread use in high-priority countries.
Programs: HEADRESSNU -
Behavioural Analysis: The Big Picture (Palantir could be used as part of a CNE) [pdf]
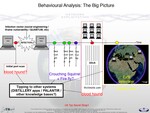
This diagram from GCHQ outlines the lifecycle of a CNE and identifies where Palantir fits into the intelligence workflow. The slide, titled "Behavioural Analysis: The Big Picture," illustrates a timeline of network exploitation from the initial infection of a target host to the eventual exfiltration of data. Crucially, it positions Palantir as a key "knowledge base" used for "Tipping to other systems." This indicates that Palantir’s software was used to aggregate data from successful hacks, allowing analysts to visualize connections and pivot (or "tip") that information toward further surveillance or offensive operations.
-
BLACK HOLE ANALYTICS, ADD/SD briefing, September 2009 [pdf]
This September 2009 GCHQ briefing describes the BLACK HOLE analytics infrastructure and Next Generation Events (NGE) project, which planned to scale from ~8 10-gigabit connections to ~200 10Gs by March 2011, storing intercepted data in massive flat-file repositories at Benhall and Bude before loading it into "Question Focused Dataset" (QFD) databases that power surveillance tools like MUTANT BROTH, KARMA POLICE, INFINITE MONKEYS, and others. The document outlines how "probes" extract Target Detection Identifiers (TDIs) from intercepted data feeds, store them in BLACK HOLE repositories, then enable analysts to profile targets' online activities, create social networks, investigate websites and forums, track web searches and Google Earth usage, and perform large-scale data mining across internet and telephony data.
Programs: BLACKHOLE · MUTANTBROTH · AUTOASSOC · INFINITEMONKEYS · KARMAPOLICE · SOCIALANIMAL · HRMAP · MEMORYHOLE · MARBLEDGECKO · HARDASSOC · SAMUELPEPYS · BLAZINGSADDLES · TELLURIAN · BUFFER · DISTILLERY · LOOKINGGLASS · NGEPeople: bin Laden, Osama -
Blazing Saddles [pdf]
This document describes BLAZING SADDLES, a GCHQ program designed to massively scale the storage and analysis of bulk internet surveillance data through multiple specialized databases that track website visits, online identities, communications patterns, and geolocation queries across the global internet population.
Programs: BLAZINGSADDLES · BLACKHOLE · SOCIALANTHROPOID · AUTOASSOC · HRMAP · INFINITEMONKEYS · KARMAPOLICE · MARBLEDGECKO · MUTANTBROTH · MEMORYHOLE · SAMUELPEPYS · SOCIALANIMAL · HAUSTORIUM · GOLDENAXE · NGE -
Bude Sigint Development Report [pdf]
GCHQ Bude SIGINT Development report fragment listing four "hits" from a satellite communication path, naming EU Commissioner Joaquin Almunia, French energy company Total (Total E and P), French defense contractor Thales (Thales Freight and Logistics), and the UN Institute for Disarmament Research (UNIDIR) as targets flagged in the agency's target database.
Programs: DRUMROLL -
BULLRUN [pdf]
A GCHQ TOP SECRET STRAP1 briefing presentation on BULLRUN — summarising the programme's purpose, the network security technologies it targets, the sensitivities surrounding cryptanalytic capabilities, and the access control framework protecting both technical details and the "fact of" capability — notable for explicitly naming three ECIs protecting the technical underpinnings: PICARESQUE, PAWLEYS and AMBULANT.
-
BULLRUN CoI - Briefing Sheet [pdf]
A GCHQ briefing sheet introducing the BULLRUN Community of Interest — the access control framework protecting Five Eyes capabilities to defeat encryption across TLS/SSL, HTTPS, SSH, VPNs, IPSec, encrypted chat and encrypted VoIP — covering the classification structure, handling procedures and protective marking guidance for intelligence derived from cryptanalytic exploitation.
“N.S.A. Able to Foil Basic Safeguards of Privacy on Web” - The New York Times ↗ (2013-09-05) · “Revealed: The NSA's Secret Campaign to Crack, Undermine Internet Security” - ProPublica ↗ (2013-09-05) · “Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · Perlroth, Nicole · Larson, Jeff · Shane, Scott · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian -
CNE End Point Requirements [pdf]
This NSA/GCHQ document outlines comprehensive requirements for an endpoint surveillance systems that enables analysts to systematically identify intelligence collection needs and discover appropriate tools for data extraction from compromised computers. The framework covers capabilities for remote data collection, cross-platform intelligence integration, query functions, tasking procedures, and visualization tools across implanted networks.
Programs: STARGATE · LOOKING GLASS · QUANTUM · GOLDENEYE · XKEYSCORE · MARINA · JTRIG · BROADOAK · UTT · GLOBALREACH · GLOBALSURGE · THUGGEE · EREPO · DANCINGBEAR · HAUSTORIUM · SHAREOWN · MUTANTBROTH · MOONRAKER · CARBONROD · RUFFLE · ROCKOPERA · QUINCEY · ECLIPSE · MUGSHOT · HIGHNOTE · UDAQ2 · EKB · TURBINE · ACNO · FLAMECARPET · FUMECUPBOARD · JACKPOT · SLIPSTREAM · B13B · PSC · QUINCY · DAREDEVIL · ROADBED -
CNE EndPoint Project Load [pdf]
The CNE EndPoint Project Load document lists multiple GCHQ exploitation projects, with “PFENNING ALPHA” targeting Flag Telecom’s network. It notes automated pulls of router monitoring webpages, collection of performance statistics, and ongoing efforts to gain further access points within Reliance’s infrastructure, while other projects and targets remain redacted.
Programs: PFENNING ALPHA · BURRITO ALPHA · GLADDY IOTA · HEADRESS IOTA · HEADRESS KAPPA · HEADRESS NU · HEADRESS OMICRON · GLADDY CHI · EREPO · RELIANCE · GTE“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
COMET NEWS (March 2010) [pdf]
This document is a March 2010 edition of the COMET NEWS newsletter, a high-level GCHQ publication designed to inform targeting teams about the latest capabilities and successful operations within the "Overhead" satellite constellation. It specifically highlights a coordinated GCHQ and US overhead (OH) effort to intercept high-priority military and leadership communications from Argentina, utilizing specialized US satellite assets and geolocation techniques to map digital microwave emitters.
Programs: COMET“Britain Used Spy Team to Shape Latin American Public Opinion on Falklands” - The Intercept ↗ (2015-04-02) · “#EspiadosPorLosIngleses: los nuevos documentos de Snowden revelan un plan de espionaje de Gran Bretaña en Argentina por Malvinas” - Todo Noticias ↗ (2015-04-02) · Fishman, Andrew · Greenwald, Glenn -
Communications Capability Development Programme [pdf]
The Communications Capability Development (CCD) Programme (formerly the Intercept Modernisation Programme, IMP) was a Home Office–led effort to maintain the U.K.’s lawful interception and communications data capabilities amid changing technologies, emphasizing that law enforcement faced a “significant decline” without new measures. GCHQ supported CCD with technical expertise and interim services like MILKWHITE Enrichment, while stressing that CCD was politically contentious, technically complex, and required legislation to mandate data retention by U.K. network operators.
-
Contact chaining [pdf]
A secret GCHQ Applied Research presentation describing how the agency's analysts use automated tools to map out a surveillance target's social network — starting with a known email address or phone number, then scoring and ranking every person that target communicates with to identify the most "suspicious" or strongly connected contacts, using twelve different relationship types including direct calls, shared locations, timing patterns, equipment sharing and calling profile similarity.
Programs: CARPAT · PRIME TIME · SNAPDRAGON · MoaG · SORTING FRIENDS · CHART BREAKER · MAMBA · CONTACTLENS · FLEXIMART · PSOUP · IMMINGLE -
Content-Metadata Matrix [pdf]
GCHQ's internal taxonomy sorts intercepted data into "content" or "metadata" to determine what can be searched without individual warrants—email subject lines, full URLs, and buddy lists fall on opposite sides of the line, enabling analysts to mine massive troves of IP addresses, phone numbers, location data, and browsing history with just a few keystrokes and a brief justification.
-
Cyber Defence Operations Legal Policy [pdf]
GCHQ's internal wiki laying out the legal plumbing for its Cyber Defence Operations (formerly NDIST)—detailing warrant types (RIPA, ISA, CNE), data retention schedules, targeting rules for UK/Five Eyes infrastructure, XKEYSCORE query protocols, and the bureaucratic hoops analysts must jump through to search attacker IPs, fingerprint UK networks, and share malware intelligence without tripping over location/nationality safeguards or commercial sensitivities.
Programs: JTRIG · SPAY · GORDIANKNOT · CHORDAL · DISCOVER · EVENTS · CASPORT · XKEYSCORE · CONTENT CLOUD · SQUEAL · MIRAGE · MUTANTBROTH · ANXIOUS · HALTERHITCH · BROADOAK · DONKEYKONG · ZOOL · PALANTIR · OVERLINK · RT · GATEKEEPER · IRONHAND · HARUSPEX · B3M · LOOKINGGLASS · GOLDENEYE · BLAZINGSADDLES · MOONRAKER · TRITON