Tag: offensive cyber operations 22 documents
Search documents matching “offensive cyber operations” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Access: Vision 2013 [pdf]
This July 2010 GCHQ strategic document outlines the agency's vision for 2013 to create "the world's biggest SIGINT engine" with access to 800 10-gigabit connections (up from existing capacity), expanding overseas operations to 60% while reducing UK-based to 40%, and developing new capabilities including computer network exploitation (CNE), exfiltration, beaconry, geolocation, and collection of "Internet Pocket Litter" like cookies and browsing data. The strategy emphasizes "scale and pace," "balance," and "agility" while claiming to operate within legal frameworks of "necessity, proportionality and authorisation," and highlights partnerships with second and third parties to access "intractable and hard targets."
Marking: SECRET -
Bad guys are everywhere, good guys are somewhere! [pdf]
A classified NSA NTOC presentation describing TREASURE MAP — the agency's near real-time global internet mapping platform — which combines open source, commercial, covert, and SIGINT data to chart every device, router, and autonomous system on the internet, including through 13 covert servers secretly planted in unwitting data centers across 18 countries spanning Asia, Europe, Russia, Africa, and South America, with networks marked in red indicating active SIGINT collection access points across at least 20 major telecommunications providers on three continents including allied nations' state-owned carriers.
Programs: TREASUREMAP · PACKAGEDGOODS · SOCIALSTAMP · SEASIDEFERRY · ARK · CAIDA · RUSTICBAGGAGE · PACKAGEDGOODS-GTR · PACKAGEDGOODS-SERVER · BLACKPEARL · LEAKYFAUCET · HYDROCASTLE · MASTERSHAKE · S-TRICKLER · TOYGRIPPE · DISCOROUTE · VITALAIR2 · IPGEOTRAP · JOLLYROGER · TUTELAGE · BYZANTINEHADES · XKEYSCORE · RADIUS · TACACS -
CSEC Cyber Threat Capabilities [pdf]
This document details CSEC’s full-spectrum cyber operations architecture, integrating SIGINT and IT Security to conduct both defensive and offensive activities under the guise of “information superiority.” While early sections emphasize detection, anomaly analysis, and collaboration with Five Eyes partners, later portions reveal active measures including network infiltration (implant deployment), command-and-control tracking, traffic manipulation and redirection, DNS interference, and potential disruption or deception operations—illustrating CSEC’s capacity not only to defend Canadian networks but also to surveil, exploit, and influence foreign and domestic digital infrastructure.
Programs: EONBLUE · CYBERDMZ · SEEDSPHERE · PHOTONICPRISM · SPECIALSOURCE · SUPERDRAKE · DARKSPACE · QUANTUM · MANDATE · STREAMING SENTRY · SSO · TKB · COVENANT -
FINAL Agenda SWEDUSA [pdf]
Detailed list of points and participants in the summit meeting between the top brass of the FRA and the NSA in April 2013.
Programs: TURTLEPOWER · TURMOIL · XKEYSCORE · WINTERLIGHT · QUANTUM · PARTNERMALL · VIVIAN · NAPA-3 · GCE · SSO -
FOXACID SOP for Operational Management of FOXACID Infrastructure (Draft) [pdf]
This document is an NSA standard operating procedure (SOP) manual detailing how to manage and operate the FOXACID system, which delivers malware to targets through tools like SECONDDATE and BADDECISION. It provides technical instructions for tracking, deploying, and maintaining covert web-based infections used in global cyber operations.
Programs: FOXACID · FOXSEARCH · WAITAUTO · RAISEBED · FORRESTPLACE · FOXHelp · PUZZLECUBE · YACHTSHOP · SECONDDATE · MAGIC SQUIRREL · MAGICBEAN · FINKCOAT · FRUGALSHOT · QUANTUM · FERRETCANNON · BEACHHEAD · OLYMPUS · UNITERAKE · DIRESCALLOP · DEEPFREEZE · FINKDIFFERENT · DISABLEVALOR · VALIDATOR · MISTYVEAL · UNITEDRAKE · PEDDLE CHEAP · PKTWENCH · FORESTPLACE · FOXCONTACT · EASYHOOKUP · DEMENTIAWHEEL · CASTLECREEK · ROCHELP · QUANTUMINSERT · FABULOUSFABLE · WATCHER · FROZENGAZE · FABFAB · DARKFIRE · CRYPTICSENTINEL · DARKHELMET · PSP · WILLOWVIXEN -
Full-Spectrum Cyber Effects [pdf]
The leaked 2012 GCHQ JTRIG “Full-Spectrum Cyber Effects” presentation outlines the UK’s offensive cyber capabilities, detailing strategies to destroy, deny, degrade, disrupt, deceive, and influence targets across digital and physical domains. It describes a wide range of operations—from network attacks, spoofing, and psychological operations on social media to hotel surveillance (Royal Concierge), mobile tracking, and advanced vulnerability exploitation—demonstrating how GCHQ integrates cyber operations, intelligence, and information warfare on a global scale.
Programs: JTRIG · SALAMANCA · RADIUS · ROYAL CONCIERGE · BLACKHOLE · GUILTY SPARK · MIDDLESEX GREEN · PPF · HOTWIRE -
FY 2013 Congressional Budget Justification, Volume I, National Intelligence Program Summary, February 2012 [pdf]
This document outlines the $52.6 billion “black budget,” detailing the structure, priorities, successes, and shortcomings of the 16 U.S. intelligence agencies. It reveals unprecedented insight into funding allocations, operations, and intelligence gaps—including the CIA’s dominant role, expanding cyber operations, and persistent challenges in areas such as North Korea and counterterrorism—while emphasizing the tension between secrecy and public accountability.
-
GCHQ - DISRUPTION Operational Playbook [pdf]
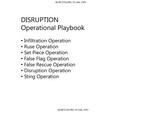
A JTRIG “Disruption Operational Playbook” outlines GCHQ’s online covert action toolkit to discredit people and companies, manipulate narratives, and execute false flag, sting, and infiltration operations across targets. It’s a blunt handbook for the four D’s—deny, disrupt, degrade, deceive—translating psychological warfare into clickable tactics on social platforms and forums.
Programs: JTRIG -
GCHQ Cyber Operations Against Anonymous and Hacktivist Groups [pdf]
The leaked 2012 GCHQ presentation reveals that the agency’s JTRIG unit conducted offensive cyber operations against Anonymous and other hacktivist groups, including DDOS attacks (codenamed “Rolling Thunder”), online infiltration, and covert intelligence collection to disrupt their communications and identify key members.
-
Interview with a SID "Hacker" -- Part 2: Hacker Culture and Worker Retention SIDtoday [pdf]
A SIDtoday internal NSA newsletter interview with a redacted TAO employee discussing hacker culture within the agency's offensive cyber unit, worker retention challenges, and the team's role in operations including the raid that killed Osama bin Laden.
Programs: SCQAWKPeople: bin Laden, Osama -
Iran – Current Topics, Interaction with GCHQ [pdf]
This NOFORN top secret April 2013 NSA document, shows how Iran significantly improved its offensive cyber capabilities by learning from cyberattacks against it, such as the April 2012 attack on its own oil industry, subsequently launching its own destructive attacks against Saudi Aramco and U.S. financial institutions.
-
Legal issues UK regarding Sweden and Quantum [pdf]
An internal NSA document from April 2013 that describes the status of the relationship with a number of partners. It takes up a three-party agreement regarding the hacker programme Quantum, between the Swedish FRA, American NSA and British GCHQ, initiated by NSA chief Keith Alexander. The document shows that the project has so far resulted in a “proof of concept” – i.e., the system works, but it has not yet generated any substantial intelligence results. It also shows that the GCHQ are doubtful about continuing in the project because of restrictions in British legislation, but that the NSA’s intention all along has been to carry out the project with the Swedish FRA rather than GCHQ.
Programs: QUANTUM -
National Intelligence Estimate 2009 Global Cyber Threat – Supply Chain Excerpts [pdf]
These Supply Chain Excerpts from the 2009 National Intelligence Estimate, assesses that the U.S. faces a growing cyber threat from state actors, particularly Russia and China, who have the capability and strategic intent to exploit or disrupt U.S. and allied information systems. It emphasizes vulnerabilities from supply chains, insider threats, and technology trends that favor offensive operations, while noting the difficulty of detecting and fully defending against these sophisticated cyber threats.
-
Network Shaping 101 [pdf]
An NSA top-secret training presentation that uses Yemen as a case study to explain how to "shape" a nation's Internet traffic by exploiting Autonomous Systems, upstream providers, BGP routing, and physical link topology to redirect or collect communications. The slide deck walks through practical router/IP/link details, passive SIGINT collection points and limitations, and warns that many assumptions are fabricated for the lesson and that real-world capabilities and link behavior can vary.
-
Presidential Policy Directive/PPD-20 [pdf]
Eighteen-page presidential memo reveals how Barack Obama has ordered intelligence officials to draw up a list of potential overseas targets for US cyber attacks.
-
Quantum – from GCHQ documents dates October 2012 [pdf]
Portion of a document from the NSA’s British equivalent, the GCHQ, in which Sweden is not mentioned, but it describes an example of how Quantum has been used to attack computers in an African country where the users have visited extremist websites.
-
QUANTUMTHEORY CT Successes [pdf]
This document details a successful NSA counterterrorism cyber operation in which analysts used QUANTUM techniques to deploy the UNITEDRAKE implant—equipped with keylogging and USB collection tools—against Al-Qaeda coordinator Muhsin al-Fadhli in Iran, even after detecting Kaspersky antivirus software on the target system. The operation yielded significant intelligence on Al-Qaeda communications, document forgery activities, and associated operatives.
Programs: QUANTUMTHEORY · ANCIENTBREW · VALIDATOR · QUANTUM · QUANTUMCOWBOY · UNITEDRAKE · GROK · SALVAGERABBITPeople: al-Fadhli, Muhsin -
Sentry Eagle Brief Sheet [pdf]
A classified NSA/JFCC-NW briefing document formally inducting cleared personnel into Sentry Eagle — the agency's most sensitive umbrella program protecting core secrets about its cyber operations — and enumerating, tier by tier, what the NSA conceals about its covert industry partnerships, encryption sabotage, network hacking, computer network defense, and human intelligence relationships.
Programs: SENTRYEAGLE · SPARECHANGE · WHIPGENIE · AUNTIE · AMBULANT · OPALESCE · REVELRY · REFRACTOR · SENTRYHAWK · SENTRYFALCON · SENTRYOSPREY · SENTRYRAVEN · SENTRYCONDOR · SENTRYOWL · BLUESASH · TAREX -
SIGINT Development Support II Program Management Review, 24 April 2013 (select slides) [pdf]
These selected slides briefly celebrate two NSA “success stories”: penetrating Pakistan’s Green Line infrastructure with SECONDDATE-enabled implants, and seizing country-wide leverage over Lebanon’s internet backbone through Ogero to siphon off Hezbollah-related data. It shows how U.S. intelligence treated supposedly inaccessible national networks as targets to be shaped, exploited, and folded into its global surveillance machine. See extra slide in "NSA Supply Chain Attack From PMR 4-24-13" https://theintercept.com/document/2019/01/24/nsa-supply-chain-attack-from-pmr-4-24-13/
Programs: MONSTERMIND · CHELSEABLUE · SECONDDATE · QUANTUM · REXKWONDO · STORMBREW · XKEYSCORE · MARINA · HAMMERCORE · HAMREX · CADENCE · HAMMERSTEIN · SSO -
Tailored Access Operations 2007 [pdf]
This NSA document describes the Tailored Access Operations (TAO) division, which conducts sophisticated cyber operations to penetrate and maintain persistent access to target networks globally through both remote exploits and physical interdiction methods. The presentation outlines TAO's organizational structure, mission capabilities across telecommunications and data networks, development of hardware/software implants for devices ranging from servers to SCADA systems, collaboration with HUMINT partners for physical access operations, and specialized divisions focused on exploiting telephony systems, computer networks, and developing tools for computer network attack and exploitation.