Tag: Section 702 26 documents
Search documents matching “Section 702” →Free-text subjects the curators added. Unlike the other axes these are not necessarily from the documents' own vocabulary, so they are the loosest thing to browse by (and the most forgiving).
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
FAA702 Glossary - Section 702 of the Fisa Amendments Act (FAA) [pdf]
This document outlines NSA rules under Section 702 of the FISA Amendments Act, which prohibit directly targeting U.S. persons or individuals inside the U.S., but quietly note a 2011 rule change allowing analysts to use U.S. person identifiers to query data already collected under 702—pending internal oversight. This effectively establishes a “backdoor search” capability enabling warrantless searches of Americans’ communications stored in NSA databases. Section 702 also gives the NSA authority to target without warrant the communications of foreign targets.
-
FISA Amendments Act of 2008 Section 702 summary document [pdf]
This document summarizes the way the law works and describes the three types of certifications used to permit the surveillance, as well as targeting and minimization procedures. The three certification are for foreign governments, counterterrorism and WMD/proliferation.
-
Minimization Procedures Used By The National Security Agency In Connection With Acquisitions Of Foreign Intelligence, Information Pursuant To Section 702 Of The Foreign Intelligence Court Surveillance Act Of 1978 [pdf]
The NSA’s Section 702 minimization rules expose how the agency can collect, keep, and use Americans’ communications without warrants, despite claiming to target only foreigners. While the document sets out procedures for handling U.S. data, it includes broad loopholes—like keeping “inadvertently” collected domestic messages for years, sharing unfiltered data with the FBI, CIA, and even foreign governments, and giving NSA analysts wide discretion over who gets surveilled—all under secret FISA Court approval.
People: Holder, Eric H. Jr. -
Procedures Used By The National Security Agency For Targeting Non-United States Persons Reasonably Believed To Be Located Outside The United States To Acquire Foreign Intelligence Court Information Pursuant To Section 702 Of The Foreign Intelligence Surveillance Act Of 1978 [pdf]
The NSA’s 2009 Section 702 targeting procedures lay out how analysts decide who can be surveilled without a warrant, supposedly limiting spying to foreigners abroad. In reality, the rules give the agency wide latitude to presume people are foreign, rely on vague “totality of the circumstances” tests, and allow broad technical methods like IP filters and metadata checks. Oversight is mostly internal and after-the-fact, creating significant potential for U.S. communications to be swept up with little accountability.
People: Holder, Eric H. Jr. -
Attention, SIGINT Analysts: E.O. 12333 Transit Communications -- What Are They? SIDtoday [pdf]
This SIDtoday article clarifies the difference between NSA's longstanding authority to collect "transit communications" and FISA Amendment Act (FAA) Section 702 authorizations. The Office of Special Source Operations (SSO) manages these transit communications under various programs like US-990, US-983, and US-3273.
Programs: SSO -
DNI, attorney general certify surveillance targets 'reasonably believed' to be outside U.S. [pdf]
In this document, the director of national intelligence and the attorney general certify that there are procedures in place to ensure that surveillance conducted under Section 702 of the FISA Amendments Act will be limited to targeting people "reasonably believed to be located outside the United States." They state that the foreign intelligence to be collected "concerns foreign powers" as defined by statute. The list of foreign powers is in Exhibit F.
-
FAA Certification Renewals with Caveats [pdf]
This NSA document shows that after the FISA Court found NSA’s upstream internet collection unconstitutional and illegal, the agency’s response was less about reform and more about finding technical and procedural workarounds to keep surveillance running as usual. While the court ordered changes within 30 days, NSA officials planned to sequester and filter “higher-risk” data to appease the judge—not halt collection—revealing a mindset focused on preserving operations rather than addressing legal violations.
-
FAA702 comms memo [pdf]
This document details NSA's response to concerns raised by the FISA Court over the collection of non-targeted data in FAA-702 upstream collection. To mitigate the risk of continued acquisition, NSA is implementing temporary measures, including cautionary banners and updated processes, to prevent misuse of data that may not be directly related to tasked selectors.
People: Shea, Teresa H. -
FISA judge's order authorizing surveillance of foreign governments and organizations [pdf]
With this order dated Aug. 19, 2010, John D. Bates, then-Chief Judge of the Foreign Intelligence Surveillance Court, approved an annual certification permitting the National Security Agency to conduct surveillance about 193 foreign governments, foreign factions, foreign-based political organizations and foreign entities such as the World Bank. Each year, a new certification must be approved by the court to permit such surveillance under Section 702 of the FISA Amendments Act.
Marking: SECRETPeople: Bates, John D. -
How the NSA verifies a target's location [pdf]
This is an excerpt from a transcript of National Security Agency training videos that describe how to verify the location of a targeted device. It explains how the NSA monitors different types of mobile signaling information known as HLR and VLR registrations in order to locate individuals. It also makes clear that the agency is able to use location tracking to ascertain whether a target is in the United States.
-
How to tell if a target is 'foreign' [pdf]
The document describes a human intelligence (HUMINT) report indicating that a specific intelligence target, identified by a Foreign Source ID, is located outside the U.S., including details such as email, telephone number, and mobile network type, with checks confirming no U.S. roaming over a 60-day period. It illustrates the use of HUMINT to corroborate foreign location data for surveillance purposes.
-
List of foreign governments and organizations authorized for surveillance [pdf]
This exhibit lists the 193 foreign governments as well as foreign factions, political organizations and other entities that were part of a 2010 certification approved by the Foreign Intelligence Surveillance Court. These are the entities about which the NSA may conduct surveillance, for the purpose of gathering foreign intelligence. Each year a new certification must be approved by the court to permit such surveillance under Section 702 of the FISA Amendments Act.
-
Lobban NSA Visit Précis [pdf]
This document is a formal briefing for a April 2013 visit by GCHQ Director Sir Iain Lobban to the NSA. The visit aimed to reinforce the Five Eyes partnership by discussing sensitive topics including supervised access to FAA Section 702 data ("Triage 2.0"), coordinated cyber and SIGINT strategies for Syria and Iran, and the implementation of the Global Collaboration Environment (GCE).
-
Microsoft releases new service, affects FAA 702 collection [pdf]
An SSO item on Microsoft's new outlook.com service encrypting web chat from 31 July 2012 and cutting off FAA 702 collection, and on the surveillance solution Microsoft built with the FBI, which went live on 12 December 2012 and needed no change to UTT tasking.
-
New FAA702 Certification in the Works - Cyber Threat [pdf]
A 23 March 2012 SSO article on a draft FAA 702 certification for cyber threats. It would let analysts task selectors tied to malicious cyber activity without attributing them to a foreign government or terrorist group, and would codify tasking of IP addresses and code strings through PRISM and the upstream accesses.
-
NSA Cyber Timeline (Some Key SSO Cyber Milestone Dates Since Fall 2005) [pdf]
A one-page NSA SSO timeline of cyber-related milestones from fall 2005 to late 2012: CNCI implementation, the Protect America Act and FISA Amendments Act certifications, TURMOIL and XKEYSCORE deployments, and the August 2012 Iranian DDoS attack on Saudi Aramco.
Programs: TURMOIL · SSO · BLUESNORT · DANCINGOASIS · MADCAPOCELOT · TURBULENCE · XKEYSCORE · WEALTHYCLUSTER -
NSA director's affidavit on foreign surveillance [pdf]
The affidavit was submitted in support of the 2010 certification concerning foreign governments, factions and other entities. In it, Alexander states that pursuant to the certification, NSA seeks to acquire foreign intelligence information concerning foreign powers. The list of foreign powers is in Exhibit F.
People: Alexander, Keith B. -
NSA target package [pdf]
This 2011 target package focuses on Muhammad Tahir Shahzad (alias Abu Hamza), a Pakistan-based bomb builder and Al-Qaeda facilitator. The document was produced by the Counter IED Analysis Integration Cell (CAIC) at the NSA. Notably, the document credits the tracking of Shahzad’s 60+ digital selectors with the eventual capture of high-value targets, including himself and Bali bombing suspect Umar Patek. The accompanying Washington Post investigation uses this specific case to highlight the massive scale of "incidental collection." While Shahzad was a valid foreign target under Section 702 of the FISA Amendments Act (FAA), the investigation revealed that for every legitimate target like him, the NSA intercepted nine "non-targeted" users—many of whom were Americans—capturing deeply personal photos, medical records, and private correspondence.
-
PRISM tasking slide (PRISM briefing 2) [pdf]
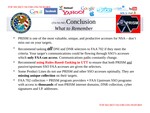
A PRISM slide headed 'Conclusion: What to Remember'. It says PRISM is among the most valuable NSA accesses, recommends tasking all DNI and DNR selectors to FAA 702 where they meet the criteria, and recommends Rules-Based Tasking in UTT so that PRISM and upstream SSO accesses both get the selectors.
-
PRISM/US-984XN Overview [pdf]
A 2013 NSA training presentation revealing that major U.S. tech companies — including Google, Facebook, Apple, Microsoft, and Skype — secretly gave the NSA direct access to their servers, allowing the agency to collect users' emails, chats, photos, and files in real time, with the FBI acting as intermediary.
Programs: PRISM · FAIRVIEW · STORMBREW · BLARNEY · OAKSTAR · UTT · PRINTAURA · PINWALE · NUCLEON · TRAFFICTHIEF · SCISSORS · MARINA · MAINWAY · FALLOUT · CONVEYANCE · REPRISMFISA · SSO“U.S., British intelligence mining data from nine U.S. Internet companies in broad secret program” - The Washington Post ↗ (2013-06-06) · “NSA Prism program taps in to user data of Apple, Google and others” - The Guardian ↗ (2013-06-07) · “L'ampleur de l'espionnage mondial par la NSA” - Le Monde ↗ (2013-10-21) · “NSA files decoded: Edward Snowden's surveillance revelations explained” - The Guardian ↗ (2013-11-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · “Dark Mirror: Edward Snowden and the American Surveillance State” - Penguin Press ↗ (2020-05-19) · Gellman, Barton · Poitras, Laura · Greenwald, Glenn · MacAskill, Ewen · Untersinger, Martin · Dance, Gabriel