Publisher: The Intercept 489 documents
Search documents matching “The Intercept” →Who published each document. Mostly a news outlet, but sometimes a book. A partner outlet that reported the story without publishing the documents keeps its byline and its article, but is not a publisher here.
Graphs
By document date (14 years)
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
PINWALE: Transnational DNI Training [pdf]
This presentation is a classified NSA training guide on PINWALE, a SIGINT database used for the storage, retrieval, and analysis of intercepted digital network intelligence (DNI) communications. It outlines system capabilities, query creation, search tools, and interfaces such as NEXUS, UIS, and AGILITY, explaining how analysts search, retrieve, and analyze both content and metadata — including FISA-partitioned data — within the Five Eyes intelligence framework.
-
PRC Information Warfare & Huawei [pdf]
This NSA intelligence briefing on Huawei analyzes Huawei’s global telecommunications presence and its potential links to the People’s Liberation Army (PLA) and Chinese government intelligence activities. It highlights concerns that Huawei’s international market expansion — including its subcontracted 2008 upgrade of the TAT-14 transatlantic cable carrying U.S. and defense communications — could be exploited by China for signals intelligence (SIGINT) purposes.
People: Chávez, Hugo -
PRESTON Architecture [pdf]
The PRESTON architecture, centered on GCHQ’s PRESTON Processing system, is detailed across multiple views showing how the agency intercepts, processes, and stores communications. It outlines a sophisticated surveillance framework that integrates lawful interception, data processing, and analyst access, emphasizing covert monitoring and management of intercepted data.
Programs: PRESTON · FAST GROK · BOXSTER · MARMION · GENTIAN · TERRAIN · BLACKNIGHT · CORINTH · FARNDALE · SAMDYCE · B3M · VSLT · SAMBOK · HAUSTORIUM · FUNFAIR · Cheltenham · SALAMANCA · IIB · LOCHNVAR · MONACO · HOTLINE · Benhall · GDR · CE · BRIGHTON · ARSENIDE · SPQR · TACHO · TRAFFIC MASTER · KEYCARD · XKEYSCORE · COURIERSKILL · MONKEYPUZZLE · PILBEAM · GREENHEART · CCDF · GTE · CADENCE · TERRAINS · GCNET · HENCE -
PRESTON Business Processes [pdf]
The PRESTON Business Processes document outlines GCHQ’s internal workflows for authorizing, enabling, managing, and terminating communications interception, as well as producing intelligence from intercepted data. It defines the roles, responsibilities, and technical processes that support lawful interception operations within the PRESTON system.
-
PRESTON Study [pdf]
This GCHQ document details the PRESTON surveillance program, revealing that over a six-month period, 97% of intercepted communications—including calls, texts, and internet data—were not viewed by analysts despite being fully warranted, highlighting systemic challenges in processing and exploiting the vast volume of collected intelligence. It underscores the reliance on traditional PRESTON sources for events like the London G20, while noting gaps in data feeds from other repositories, reflecting both operational scale and limitations in effective oversight.
-
PRISM Olympic Option [pdf]
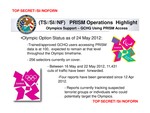
A May 2012 NSA operational highlight revealing that Britain's GCHQ was given access to the NSA's PRISM surveillance system during the London Olympics, with 100 trained British operatives secretly monitoring 256 targets and intercepting over 11,000 communications in a single week.
-
Project CAMBERDADA [pdf]
NSA presentation on Project CAMBERDADA, a programme that intercepts emails sent to antivirus companies reporting new malware, uses SIGINT collection to monitor antivirus vendor communications, and identifies opportunities to repurpose malware before vendors detect it — listing 23 antivirus companies from around the world as targets, with Kaspersky as the primary focus.
People: Picard, François -
Project SANDSTORM [pdf]
This document shortly describes Project SANDSTORM, part of the Active Sigint Enabling Passive Geolocation (ASEPG) program at Menwith Hill, which uses Wi-Fi signal characterization and satellite-based Overhead capabilities to geolocate high-value targets, with geolocations of under 100 meters expected even for low-power signals in denied areas. It focuses on actively enabling SIGINT to track targets via 802.11 wireless networks.
-
Psychology: A New Kind of SIGDEV [pdf]
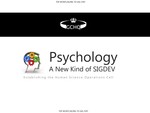
This document presents a detailed approach to integrating human sciences—such as psychology, sociology, anthropology, economics, and political science—into intelligence operations. It highlights the use of tools like SIGINT, HUMINT, and covert online monitoring to understand and shape human behavior, influence networks, and assess socio-cultural dynamics. The focus is on using real-time data analytics, including tracking social media interactions, to optimize intelligence gathering and strategic influence.
Programs: JTRIG · HSOC · SQUEAKY DOLPHIN · DISTILLERY · AIRWOLF · ANTICRISISGIRL · SPLUNK · STREAMINGANALYTICS · HOLLOWPOINT · FIREANT · GTE“Snowden Documents Reveal Covert Surveillance and Pressure Tactics Aimed at WikiLeaks and Its Supporters” - The Intercept ↗ (2014-02-18) · “Snowden docs reveal British spies snooped on YouTube and Facebook” - NBC News ↗ (2014-01-27) · Greenwald, Glenn · Gallagher, Ryan · Esposito, Richard · Cole, Matthew · Schone, Mark -
Pull Steering Group Minutes [pdf]
A top secret STRAP1 GCHQ PullThrough Steering Group meeting record from February 2008 documenting the approval process for five surveillance and intelligence prototypes including KARMA POLICE — the mass internet browsing profiling system — alongside ORB FINDER for CNE operational relay box identification, SALTY OTTER for cross-media timing analysis, MOOSE MILK for telephone kiosk surveillance, and LIGHTWOOD for email address extraction used by JTRIG.
Programs: MYOFIBRIL · SALTYOTTER · PRIMETIME · KARMAPOLICE · ORBFINDER · MOOSEMILK · LIGHTWOOD · JTRIG · MERAPEAK · MONTEVISTA · KED -
QFD BLACKHOLE Technology Behind INOC [pdf]
A UK SECRET STRAP2 COMINT ORCON GCHQ Applied Research presentation from March 2009 documenting the BLACK HOLE bulk data repository's scale and structure, and the suite of analytical tools — MUTANT BROTH, KARMA POLICE, INFINITE MONKEYS and MARBLED GECKO — built on top of it to answer specific intelligence questions about online presence, browsing activity, forum usage and geolocation searches.
Programs: BLACKHOLE · MESME · NETEZZA · CLOUDS · MUTANTBROTH · KARMAPOLICE · INFINITEMONKEYS · MARBLEDGECKO · GOOB · AUTOASSOC · PSOUP · SOCIALANIMAL · SAMUELPEPYS · MEMORYHOLE · HRMAP · PSOUPALERT · LAUGHINGHYENA -
Quadrennial Intelligence Review Final Report, 2009 [pdf]
This 2009 strategic review from the Director of National Intelligence outlines potential future operating concepts for the US Intelligence Community, including "safe bets" like mass data analysis (Sentient Enterprise) and controversial "strategic hedges" such as using clandestine cyber operations to acquire proprietary technology from foreign corporations to benefit US industry (Technology Acquisition by All Means).
People: Shedd, David R. -
QUANTUMHAND [pdf]
This slide describes QUANTUMHAND, a specialized "Man-on-the-Side" (MOTS) attack used by the NSA's Tailored Access Operations (TAO) to infect targets visiting Facebook. The document outlines an automated process where the NSA's surveillance infrastructure, TURMOIL and TURBINE, detects a target's connection to Facebook and "races" against the legitimate Facebook server to deliver a malicious response first. This "winning the race" allows the NSA to redirect the user to a TAO server that attempts to deploy malware "implants" on the target's computer.
-
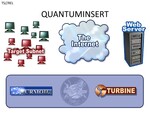
QUANTUMINSERT [pdf]
This top-secret NSA presentation provides a step-by-step visual walkthrough of a man-on-the-side (MOTS) attack. This technique allows the NSA to covertly redirect a target's web browser to a malicious server in order to install a malware implant. The diagrams illustrate the interaction between the NSA's global surveillance sensors (TURMOIL) and its automated command-and-control system (TURBINE), demonstrating how the agency exploits the fundamental "race condition" of the internet to compromise a target.
-
QUANTUMTHEORY (2010 SIGINT Development Conference) [pdf]
This 2010 NSA presentation reveals QUANTUMTHEORY, a suite of "man-on-the-side" network attack technologies that enable real-time injection and manipulation of TCP/IP connections through passive surveillance infrastructure. The system encompasses multiple specialized attack techniques including HTML redirection, DNS hijacking, botnet takeover, and database injection, deployed at Five Eyes surveillance sites worldwide.
Programs: QUANTUMTHEORY · TRAFFICTHIEF · TURMOIL · TURBINE · QUANTUM · NINJANIC · ISLANDTRANSPORT · SURPLUSHANGER · DAREDEVIL · STRAIGHTBIZARRE · QUANTUMINSERT · QUANTUMSKY · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMDNS · QUANTUMBOT2 · QUANTUMCOPPER · QUANTUMMUSH · HUFFMUSH · QUANTUMSPIM · QUANTUMSQUEEL · QUANTUMSQUIRREL · INCENSOR · SMOKEYSINK · SARATOGA · QUANTUMDEFENSE · TURBULENCE“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
QUANTUMTHEORY CT Successes [pdf]
This document details a successful NSA counterterrorism cyber operation in which analysts used QUANTUM techniques to deploy the UNITEDRAKE implant—equipped with keylogging and USB collection tools—against Al-Qaeda coordinator Muhsin al-Fadhli in Iran, even after detecting Kaspersky antivirus software on the target system. The operation yielded significant intelligence on Al-Qaeda communications, document forgery activities, and associated operatives.
Programs: QUANTUMTHEORY · ANCIENTBREW · VALIDATOR · QUANTUM · QUANTUMCOWBOY · UNITEDRAKE · GROK · SALVAGERABBITPeople: al-Fadhli, Muhsin -
RAMPART-A Project Overview [pdf]
This document is a 2010 project overview of RAMPART-A, a highly unconventional NSA special access program dedicated to tapping high-capacity international fiber-optic cables at global "congestion points." Through clandestine bilateral partnerships, the NSA installs U.S. equipment on foreign soil to intercept massive volumes of transit data, providing the agency with a unique vantage point that covers virtually every country in the world.
Programs: RAMPART-A · RAMPART-T · SMOKYSINK · AZUREPHOENIX · SPINNERET · TRANQUIL · MOONLIGHTPATH · FIREBIRD · FALCONSTRIKE · DULCIMER · REDHARVEST · FLASHMARK · CONDORSPEAK · TURMOIL · SSO“How Secret Partners Expand NSA’s Surveillance Dragnet” - The Intercept ↗ (2014-06-18) · “NSA ‘third party’ partners tap the Internet backbone in global surveillance program” - Dagbladet Information ↗ (2014-06-19) · Gallagher, Ryan · Geist, Anton · Gjerding, Sebastian · Moltke, Henrik · Poitras, Laura · Jensen, Kristian -
RAMPART-A Sites [pdf]
This document specifies the data throughput and operational constraints of five key RAMPART-A interception sites, including the implementation of the "DNI Throttle" to manage data volume. It also defines the "Support Hub" model for managing signals tasking and explains the role of the REDHARVEST compartment in restricting which analysts can view specific digital network categories.
Programs: RAMPART-A · AZUREPHOENIX · MOONLIGHTPATH · SPINNERET · SMOKYSINK · FIREBIRD · XKEYSCORE · PINWALE · REDHARVEST · CADENCE“How Secret Partners Expand NSA’s Surveillance Dragnet” - The Intercept ↗ (2014-06-18) · “NSA ‘third party’ partners tap the Internet backbone in global surveillance program” - Dagbladet Information ↗ (2014-06-19) · Gallagher, Ryan · Geist, Anton · Gjerding, Sebastian · Moltke, Henrik · Poitras, Laura -
Re: Ehsanul Sadequee FISA Request [pdf]
This NSA email chain from April 2006 shows NSA analysts urgently requesting FBI FISA authorization documents for Ehsanul Sadequee so they could conduct a "TAO operation" (Tailored Access Operations hack) to retrieve a file he had shared, racing against the FBI's impending arrest which would invalidate their surveillance authority. The emails reveal the NSA's dependence on FBI-obtained FISA warrants to justify their operations and their need to complete the hack before Sadequee's arrest made their authorization "invalid."
Programs: CADENCEPeople: Sadequee, Ehsanul Islam -
Real-Time Regional Gateway (RT-RG) [pdf]
This document from GCHQ details the NSA's Real-Time Regional Gateway (RT-RG), a system designed to provide tactical military users with near-instantaneous SIGINT (signals intelligence) support by integrating and analyzing data from multiple sources. It outlines the system’s applications, benefits, and challenges, particularly in enhancing the speed and efficiency of intelligence delivery to military operations in regions like Afghanistan, and highlights its impact on collaboration with GCHQ.
Programs: RT-RG · RT-10 · GOLDMINER · VOICESAIL · GEOT · SHARKFINN · CELLEX · SORTINGLEAD · GREMIO · IMMERGO · HERRICK · AIRHANDLER · TIPPERS · PASHTOVOICE · VIPERFOCUS · SKS · GEOFUSION · EVENTS“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin