Dissemination control: REL TO USA, FVEY 107 documents
Search documents matching “REL TO USA, FVEY” →Handling controls assessed for each document, as component values. If a document contains multiple disseminations, the most restrictive is used here.
Graphs
By Banner
By Classification
Refine (combine with another filter, via search)
Sort: Title
Documents
-
TEC Successfully Installs BOTANICREALTY at LADYLOVE (USJ-799) [pdf]
This document outlines technical advancements in NSA surveillance, specifically the deployment of the "BOTANICREALTY" tool at LADYLOVE (USJ-799) to intercept encrypted video feeds, and details the 2007 annual report of the "Joint SIGINT Activity" (JSA), a collaborative operation between the NSA and the German BND. The report highlights massive increases in data collection, including the daily flow of 330,000 SMS messages into the DISHFIRE database and the development of new tools for VoIP analysis.
Programs: BOTANICREALTY · SALTYDOGS · UNCANNY · LADYLOVE · HIGHPRIDE · TROPICPUMA · NORMALRUN · DISHFIRE · FASCIA · JUGGERNAUT · SSO -
Template:POISONNUT Product [pdf]
An NSA WikiInfo page describing the POISONNUT ESP attack scheduling component — the internal software element responsible for determining whether a VPN key recovery attack can proceed, submitting it to the cryptanalytic processing infrastructure, correlating responses, and marking each attack attempt as successful or failed.
Programs: POISONNUT -
The Art of Deception: Training for a New Generation of Online Covert Operations [pdf]
A top-secret JTRIG training deck lays out how GCHQ turns social science into operational tradecraft for online covert action—blending online HUMINT, strategic influence, and disruption/CNA—while “building cyber magicians” through a formal accreditation program. The curriculum operationalizes deception, persuasion, and group dynamics into false flags, ruses, and reputation attacks aimed at producing real-world “effects.”
Programs: JTRIGPeople: Robert-Houdin, Jean · Maskelyne, Jasper · Mulholland, John · Fishburne, Tom · Robles, Arturo · Teller -
The collection challenge [pdf]
A slide stating the collection problem in one line: “Collection is outpacing our ability to ingest, process and store to the ‘norms’ to which we have become accustomed.”
-
The FASHIONCLEFT Protocol [pdf]
This October 2008 NSA technical specification details FASHIONCLEFT, the encryption and exfiltration protocol used by TAO implants to securely tunnel captured network packets from compromised devices back to the NSA's Common Data Receptor using layered RSA and RC6 encryption with authentication. The document addresses technical integration challenges of implementing FASHIONCLEFT packet reception within TURMOIL's passive collection infrastructure, particularly cache buffering requirements and metadata handling for exfiltrated traffic.
Programs: FASHIONCLEFT · FOGYNULL · FUNNELAPS · SHELLGREY · TURMOIL · SURPASSPIN · PUZZLECUBE · FLASHHANDLE · HAMMERCHANT · AEG · PPF · ISLANDTRANSPORT -
The Role of National Interests, Money, and Egos [pdf]
Slides on standards-setting as an instrument of power, arguing bluntly that the Western world and especially the United States gained influence and money by drafting the earlier standards that shaped today's Internet.
-
THIEVING MAGPIE: Using on-board GSM/GPRS services to track targets [pdf]
A GCHQ capability-development presentation on THIEVING MAGPIE, which uses the on-board GSM/GPRS services airlines offer to track targets in flight: comms backhauled over Inmarsat BGAN and collected via SOUTHWINDS, registration events tied to a flight number or callsign in near real time, events for BlackBerry handsets with their PINs and associated e-mail addresses, and content tasked into datastores with unselected traffic to XKEYSCORE.
“US and Britain refine their ability to tap into airline passenger’s mobile phones while they are in the air” - Le Monde ↗ (2016-12-07) · “American and British Spy Agencies Targeted In-Flight Mobile Phone Use” - The Intercept ↗ (2016-12-07) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Follorou, Jacques · Greenwald, Glenn -
Tracking Targets on Online Social Networks [pdf]
A TOP SECRET NSA presentation from September 2009 describing XKeyscore techniques for tracking targets across online social networks — covering OSN selector types, six categories of target OSN activity ranked by intelligence value, username and HTTP activity query methods, and specific XKeyscore AppIDs for Facebook and Twitter — noting that counterterrorism targets had been observed using over 50 social networks as of late 2008.
Programs: XKEYSCORE“XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Marquis-Boire, Morgan · Greenwald, Glenn · Lee, Micah -
TRAFFICTHIEF Readme [pdf]
A SECRET XKeyscore configuration manual describing TRAFFICTHIEF — NSA's corporate alerting and tipping system that receives real-time events from XKeyscore when targets are actively communicating, enriches them with geolocation data and immediately alerts analysts — covering socket and MAILORDER configuration methods for both Five Eyes and NOFORN tip streams.
-
TRANSGRESSION Overview for Pod58 [pdf]
The TRANSGRESSION overview describes an NSA capability focused on discovering, decrypting, and exploiting foreign computer network exploitation activity to support fourth-party collection, TAO cyber operations, and network defense missions across NSA and FVEY partners.
Programs: TRANSGRESSION · MAKERSMARK · BYZANTINEHADES · VOYEUR · WALKERBLACK · WALKERRED · CROWNROYAL · CROWNPRINCE · SHEPHERD · ZEBEDEE · MAVERICK CHURCH · POPROCKS · GHOSTRECON · NIGHTTRAIN · SHADOWDRAGON · RECORDER · PLAIDDIANA · INCAADAM · TWEEZERS · SNOWGLOBE · WIDOWKEY · SUPERDRAKE · XKEYSCORE · POLARSTARKEY · TUNINGFORK · SCISSORS · PINWALE · CLOUD · BYZANTINEFOOTHOLD · ADJUTANTVENTURE · RAPTORROLEX · RAPTORJOY · RAPTORSAD · BYZANTINERAPTOR -
TURMOIL GALLANTWAVE [pdf]
An NSA WikiInfo page describing TURMOIL GALLANTWAVE — a CES mission application hosted on TURMOIL that decrypts communications using Data Network Session Cipher (DNSC) technologies, such as SSL/TLS, by integrating with the LONGHAUL SCARLETFEVER key recovery service and forwarding decrypted sessions to XKEYSCORE for analyst access.
Programs: VALIANTSURF · XKEYSCORE · TURMOIL · GALLANTWAVE · LONGHAUL · TURBULENCE · BULLRUN · SCARLETFEVER · TUMULT · TUBE · UTT · BTUBE · FISHWAY · EXOPUMP · PURGE · SURGE · SCISSORS · PINWALE · TUSCARORA · NUCLEON · WDM · TURTLEPOWER · CONVEYANCE · ONEROOF · KEYCARD · SLIDETACKLE · POLARSTARKEY · TUMMS · CEMETERY · TEPIDTSUNAMI · PPF · ISLANDTRANSPORT -
TURMOIL VPN PROCESSING [pdf]
A TURMOIL VPN Processing technical briefing from October 2009 describing the full architecture for intercepting and decrypting IPSec VPN traffic within the TURMOIL passive collection platform — covering IKE/ESP protocol handling, five distinct data flow types, the Dell LPT hardware implementation, and live operational metrics showing over 8 million packets decrypted at Menwith Hill and 1.4 million at SMOKYSINK during a single week in October 2009.
-
TURMOIL/APEX/APEX High Level Description Document [pdf]
NSA WikiInfo page providing the high-level design description of APEX — the Active-Passive Integration capability integrating HAMMERMILL router implants with TURMOIL passive collection — enabling real-time exfiltration of targeted VPN (HAMMERSTEIN) and VoIP (HAMMERCHANT) traffic from compromised routers directly into NSA's passive collection and cryptanalytic attack infrastructure, with TURBINE providing automated command and control of the combined active-passive system.
Programs: TURMOIL · APEX · HAMMERMILL · HAMMERCHANT · HAMMERSTEIN · FASHIONCLEFT · TURBINE · TOYGRIPPE · METROTUBE · CHIMNEYPOOL · PIQBLADE · KEYCARD · FASCIA · ISLANDTRANSPORT · PRESSUREWAVE · ASDF · CONVEYANCE · TURBULENCE -
TUTELAGE 411 [pdf]
TUTELAGE is a SIGINT-driven cyber defense and counterintelligence platform that enables NSA to observe, intercept, redirect, block, and manipulate adversary network activity at DoD gateways, transforming intrusion response from post-incident reporting into real-time mitigation and intelligence generation.
Programs: TUTELAGE · CYBERQUEST · XKEYSCORE · GNOMEVISION · POPQUIZ · BISHOPKNIGHT · BLACKENERGY · BLINDMARKSMEN · BYZANTINEFOOTHOLD · BYZANTINEVIKING · CARBONPEPTIDE · CONFICKER · DANCING PANDA · DISCOVERY · GNOMEFISHER · MAKERSMARK · MAVERICKCHURCH · NATIVEDANCER · WEASELWAGGLE · SUBTLESNOW · WIDOWKEY · ZEUS · GHOSTMACHINE · PANDORASMAYHEM · TURBINE · QUANTUM · BYZANTINEHADES · AMULETSTELLAR · TURNABOUT -
Types of IAT - Advanced Open Source Multi-hop [pdf]
This top-secret NSA/GCHQ document provides a detailed technical overview of the Tor network, including how it works, its strengths as the “king of high secure, low-latency Internet anonymity,” methods for identifying Tor traffic, censorship-driven protocol obfuscation, and ongoing intelligence efforts to analyze, fingerprint, and exploit Tor through passive SIGINT and active research, including collaboration between US and UK agencies.
People: Appelbaum, Jacob -
User-agents: Why and How and How to [pdf]
A TOP SECRET NSA training presentation from 2010 teaching analysts how to use browser user-agent strings — the identifying information your web browser automatically sends to every website you visit — to track surveillance targets across the internet, link their known email activity to their anonymous web browsing, and identify opportunities for hacking their computers based on their operating system and software versions.
-
UTT Configuration READ ME [pdf]
A SECRET XKeyscore configuration manual describing how to set up the Unified Targeting Tool — NSA's centralised system for pushing surveillance selectors from analysts to field site collection systems worldwide — revealing the complete data flow from analyst targeting request through MAILORDER transport to XKeyscore ingestion, including a forwarding domain table showing how intercepted data is routed to all Five Eyes partners (NSA, GCHQ, CSE, DSD, GCSB) and third parties.
Programs: UTT · TURBULENCE · XKEYSCORE · MAILORDER · SSDM · FISHWAY · SCISSORS · PINWALE · TRAFFICTHIEF -
VALIANTSURF [pdf]
An NSA WikiInfo page for VALIANTSURF — the coverterm for NSA's IPSec VPN decryption capability within the TURMOIL collection platform — describing the four data flow types for intercepting and breaking encrypted VPN traffic, the full deployment roster across collection sites including Menwith Hill, SMOKYSINK, MUSCULAR, CROSSCUT and others, and the architectural taxonomy of the VALIANTSURF programme including its MALIBU and WAIMEA processing architectures and their relationship to LONGHAUL, POISONNUT and GALLANTWAVE.
Programs: VALIANTSURF · TURMOIL · TURBULENCE · HOOKED · HOOKEDHAND · CINDER · CINDERASH · CINDERTRACK · SCARLETFEVER · LONGHAUL · FALLOUT · TOYGRIPPE · PICARESQUE · XKEYSCORE · PRESSUREWAVE · ASDF · MAILORDER · TUBE · KEYCARD · POISONNUT · ISLANDHIDEAWAY · ISLANDTRANSPORT · EXOPUMP · CORALREEF · PINWALE · TUSCARORA · ONEROOF · CONVEYANCE · TURTLEPOWER · WDM · CADENCE · UTT · SCISSORS · FISHWAY · BTUBE · DNCA · ROMULANALE · GALLANTWAVE · ROMULANGAWK · ROMULANGOWL · MALIBU · WAIMEA · WAIMEAVISAGE · ROMULANVISAGE · WAIMEAVISE · ROMULANVISE · APEX · METROTUBE · MADFORGE · JSORCERER · CROSSCUT · CIET · LATTICE · STARQUAKE · SARATOGA · MUSCULAR · SMOKYSINK · SLACKKEY · TUMMS · PURGE · SURGE · NUCLEON · SPAGIC · PPF · SOAP · TUMULT · FIP · PIQBLADE · DEEPDIVE · IBRIDGE -
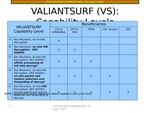
VALIANTSURF (VS): Capability Levels [pdf]
A capability status document for VALIANTSURF — NSA's programme for large-scale IPSec VPN decryption integrated with TURMOIL passive collection and LONGHAUL key recovery — defining five capability levels from basic key recovery through full hardware-accelerated on-site decryption with XKEYSCORE integration, and showing deployment status across named collection sites.
-
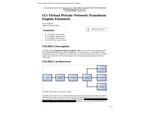
Virtual Private Network Transform Engine Emulator [pdf]
An NSA WikiInfo page describing the Transform Engine Emulator (TEe) — a software tool that replicates at NSA headquarters the same VPN decryption pipeline that runs on deployed field collection systems, allowing encrypted VPN traffic forwarded back to headquarters to be broken using the same key recovery infrastructure, specifically by combining the VULCANDEATHGRIP and POISONNUT components.