Classification: TOP SECRET 823 documents
Search documents matching “TOP SECRET” →Each document's classification level, as component values. If a document contains multiple classifications, the highest is used here.
Graphs
By document date (14 years)
By published date (9 years)
By Banner
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Targeting Rationale (TAR) [pdf]
An NSA document describing how analysts should explain their targeting decisions under the FISA Amendments Act.
-
Tasking of SCALAWAG [pdf]
An NSA Special Source Operations memo describing bandwidth and latency problems caused by the SCALAWAG bulk voice collection program, and introducing the RETRO Tool — a capability allowing analysts to reach back up to 30 days into a buffer of recorded phone calls from an entire country to retrieve audio that was never individually targeted.
Programs: SCALAWAG · DOUBLEARROW · UTT · OCTAVE · NUCLEON · RETROSPECTIVE · RETROTOOL · RETRO · FASCIA · SSO -
TCB Jamboree 2010 Abstracts [pdf]
This document discusses a 2010 CIA-hosted conference on trusted computing technologies, specifically focusing on security measures such as bypassing disk access for covert execution of code. It highlights a demonstration of Northrop Grumman Xetron's "Orca" system, which enables covert launching of Windows executables without writing to disk, circumventing personal security products that monitor disk activity for malicious software.
-
TCB Jamboree 2011 Abstracts [pdf]
This document discusses a 2011 CIA-hosted conference 2011 TCB Jamboree, focusing on research into emerging security technologies, their vulnerabilities, and methods for exploiting or circumventing trusted computing architectures. The event featured presentations—many redacted—on hardware and software security topics, including processor analysis, driver‑signing forensics, and other advanced techniques relevant to intelligence operations.
-
TCB Jamboree 2012 [pdf]
This document describes a 2012 TCB Jamboree conference highlighting research into security weaknesses in Apple technologies, including analysis of Apple A4/A5 processors and methods for targeting the MacOS and iOS software‑development ecosystem. The focus is on understanding and exploiting architectural or tooling vulnerabilities rather than user‑level devices, all presented in a high‑level research context.
-
TCB Jamboree 2012 [pdf]
1 p.A TOP SECRET//SI//NOFORN entry from NSA's internal WikiInfo-NF wiki describing the CIA Trusted Computing Base Jamboree — an annual conference hosted by CIA's Emerging Technologies Branch within the Information Operations Center, bringing together CIA analysts and contractors conducting research for the TCB programme, with NSA invited to participate through its own counterpart TCB programme.
“The CIA Campaign to Steal Apple's Secrets” - The Intercept ↗ (2015-03-10) · Scahill, Jeremy · Begley, Josh -
Team Re-establishes Crucial Collection in Iraq SIDtoday [pdf]
After they noticed a significant drop in intercepted mobile phone calls prior to a major military operation in Fallujah, the Special Collection Service realized that the cellular network had changed, and they had consequently lost a significant intelligence source. SCS took emergency measures to try to regain access to the signals.
People: Green, ChrisThe Intercept ↗ (2017-09-13) -
TEC Successfully Installs BOTANICREALTY at LADYLOVE (USJ-799) [pdf]
This document outlines technical advancements in NSA surveillance, specifically the deployment of the "BOTANICREALTY" tool at LADYLOVE (USJ-799) to intercept encrypted video feeds, and details the 2007 annual report of the "Joint SIGINT Activity" (JSA), a collaborative operation between the NSA and the German BND. The report highlights massive increases in data collection, including the daily flow of 330,000 SMS messages into the DISHFIRE database and the development of new tools for VoIP analysis.
Programs: BOTANICREALTY · SALTYDOGS · UNCANNY · LADYLOVE · HIGHPRIDE · TROPICPUMA · NORMALRUN · DISHFIRE · FASCIA · JUGGERNAUT · SSO -
TECA Product Centre — Wiki [pdf]
The TECA Product Centre is a GCHQ unit, within the Technical Enabling Covert Access group (TEA), whose mission is to develop and exploit specialist technologies and physical access methods to gain intelligence or SIGINT access where conventional methods fail. It works closely with SIS (MI6) on technical operations and deployment, offering bespoke managed services rather than direct products.
-
Technology that Identifies People by the Sound of Their Voices SIDtoday [pdf]
Voice matching technology developed by the Massachusetts Institute of Technology helped the FBI confirm that an individual the bureau had interrogated in Iraq was not a particular terrorist. Voice matching was also used to identify Saddam Hussein, Osama bin Laden, and Al Qaeda leader Ayman al-Zawahiri across recordings. It was also applied in an “insider threat” effort to identify potential NSA leakers.
People: Cusmariu, Adolf · Hakim, Abu · al-Zawahiri, Ayman · bin Laden, Osama · Hussein, Saddam · Pelton, Ron -
Telecomm Customers Can Now Pick Their Own Phone Numbers -- What Does It Mean for SIGINT? SIDtoday [pdf]
Pick-Your-Own-Number is a new feature made possible by VoIP providers such as Vonage, and as of 2004 rapidly gaining in popularity. Now that this phenomenon is taking off, it means that phone numbers no longer reliably correspond to the country of the subscriber. "Theoretically," the author writes, "Usama bin Laden could be using a U.S.-based number while located in Afghanistan!" This has legal complications for NSA, because they need to be able to spy on international targets, but USSID-18 regulations forbid them from spying on domestic targets. The author suggests that NSA could partner with law enforcement agencies, such as FBI, to target domestic phone numbers using the domestic surveillance law known as the Communications Assistance for Law Enforcement Act.
People: bin Laden, OsamaThe Intercept ↗ (2017-04-24) -
Template:POISONNUT Product [pdf]
An NSA WikiInfo page describing the POISONNUT ESP attack scheduling component — the internal software element responsible for determining whether a VPN key recovery attack can proceed, submitting it to the cryptanalytic processing infrastructure, correlating responses, and marking each attack attempt as successful or failed.
Programs: POISONNUT -
TEMPORA -- "The World's Largest XKEYSCORE" -- Is Now Available to Qualified NSA Users [pdf]
This document announces expanded NSA analyst access to TEMPORA, GCHQ’s massive XKEYSCORE‑based internet buffer, positioning it as the largest single XKEYSCORE data source in existence. It promotes TEMPORA as a high‑value discovery and development platform for large‑scale internet surveillance.
-
Temporary SCS Site Established for Presidential Visit to India; Threats to President Reported SIDtoday [pdf]
In preparation for President George W. Bush’s first visit to India, a temporary Special Collection Service site has been set up in Hyderabad. A letter intercepted by Indian intelligence indicates a potential terrorist attack, and “predominately Muslim and Left Wing groups” plan demonstrations.
People: Bush, George W.The Intercept ↗ (2018-08-15) -
The 'Regruntlement' of a SIGINT Collector SIDtoday [pdf]
A jaded veteran signals intelligence collection officer found himself reinvigorated after a 17-month tour at the National Security Operations Center, where he was assigned to a Navy unit and served on duty during many key events in the war on terror, including the first night of the U.S. invasion of Iraq.
The Intercept ↗ (2017-09-13) -
The 'Regruntlement' of a SIGINT Collector (repost) SIDtoday [pdf]
(Repost) A jaded veteran signals intelligence collection officer found himself reinvigorated after a 17-month tour at the National Security Operations Center, where he was assigned to a Navy unit and served on duty during many key events in the war on terror, including the first night of the U.S. invasion of Iraq.
The Intercept ↗ (2017-09-13) -
The Analyst Cockpit SIDtoday [pdf]
Announcement of beta test of a new desktop dashboard for analysts.
The Intercept ↗ (2016-05-16) -
The Answer Is... Peer to Peer File Sharing SIDtoday [pdf]
In 2004, BitTorrent traffic was responsible for two-thirds of all traffic on the internet, and BitTorrent wasn't even the most popular peer-to-peer file-sharing tool. The File-sharing Analysis and Vulnerability Assessment (FAVA) pod began researching P2P tools and protocols, such as BitTorrent, DirectConnect, eDonkey, KaZaA, and several others, to develop methods to search this traffic for intelligence. "We have developed the capability to decrypt and decode both KaZaA and eDonkey traffic to determine which files are being shared, and what queries are being performed."
Marking: TOP SECRETPeople: Spears, BritneyThe Intercept ↗ (2017-09-13) -
The collection challenge [pdf]
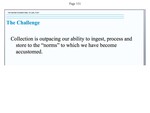
A slide stating the collection problem in one line: “Collection is outpacing our ability to ingest, process and store to the ‘norms’ to which we have become accustomed.”
-
The Collection Strategies and Requirements Center SIDtoday [pdf]
Describes the functions of the Collection Strategies and Requirements Center within Data Acquisition. It served as the “focal point for Data Acquisition for Operation Iraqi Freedom.”
The Intercept ↗ (2016-08-10)