Classification: TOP SECRET 536 documents
Search documents matching “TOP SECRET” →Each document's classification level, as component values. If a document contains multiple classifications, the highest is used here.
Graphs
By document date (14 years)
By Banner
Refine (combine with another filter, via search)
Sort: Title
Documents
-
PROFILING SSL AND ATTRIBUTING PRIVATE NETWORKS [pdf]
A TOP SECRET GCHQ presentation introducing two prototype cloud analytics — FLYING PIG, a knowledge base for investigating TLS/SSL traffic at scale across approximately 20 billion events per week, and HUSH PUPPY, a tool for attributing private network traffic to identifiable organisations — with live interface screenshots demonstrating queries against mail.ru infrastructure and operational successes including identification of the Afghan Ministry of Defence network and a foreign Ministry of Foreign Affairs VSAT network.
Programs: FLYINGPIG · HUSHPUPPY · QUICKANT · GEOFUSION · LEGIONJADE · LEGIONRUBY · MAKERSMARK · XKEYSCORE · NOSEYPARKER“Prying Eyes: Inside the NSA's War on Internet Security” - Der Spiegel ↗ (2014-12-28) · “'Brasil é um grande alvo', diz jornalista sobre vigilância dos EUA” - O Globo ↗ (2013-07-07) · Appelbaum, Jacob · Gibson, Aaron · Grothoff, Christian · Müller-Maguhn, Andy · Poitras, Laura · Sontheimer, Michael · Stöcker, Christian · Greenwald, Glenn · Kaz, Roberto · Casado, José -
PROJECT BULLRUN Classification Guide [pdf]
This BULLRUN classification guide outlines the NSA’s highly secretive methods for undermining and exploiting encryption technologies through a combination of cryptanalysis, industry collaboration, covert implants, and network exploitation. It specifies strict classification protocols for capabilities against protocols like TLS/SSL, VPNs, VoIP, and webmail, emphasizing secrecy around sources, methods, and industry partnerships that make commercial encryption systems deliberately vulnerable.
Programs: BULLRUN · APERIODIC · AMBULANT · AUNTIE · PAINTEDEAGLE · PAWLEYS · PITCHFORD · PENDLETON · PICARESQUE · PIEDMONT“Revealed: how US and UK spy agencies defeat internet privacy and security” - The Guardian ↗ (2013-09-05) · “N.S.A. Able to Foil Basic Safeguards of Privacy on Web” - The New York Times ↗ (2013-09-05) · “Revealed: The NSA's Secret Campaign to Crack, Undermine Internet Security” - ProPublica ↗ (2013-09-05) · Ball, James · Borger, Julian · Greenwald, Glenn · Perlroth, Nicole · Larson, Jeff · Shane, Scott -
Project CAMBERDADA [pdf]
NSA presentation on Project CAMBERDADA, a programme that intercepts emails sent to antivirus companies reporting new malware, uses SIGINT collection to monitor antivirus vendor communications, and identifies opportunities to repurpose malware before vendors detect it — listing 23 antivirus companies from around the world as targets, with Kaspersky as the primary focus.
People: Picard, François -
Psychology: A New Kind of SIGDEV [pdf]
This document presents a detailed approach to integrating human sciences—such as psychology, sociology, anthropology, economics, and political science—into intelligence operations. It highlights the use of tools like SIGINT, HUMINT, and covert online monitoring to understand and shape human behavior, influence networks, and assess socio-cultural dynamics. The focus is on using real-time data analytics, including tracking social media interactions, to optimize intelligence gathering and strategic influence.
Programs: JTRIG · HSOC · SQUEAKY DOLPHIN · DISTILLERY · AIRWOLF · ANTICRISISGIRL · SPLUNK · STREAMINGANALYTICS · HOLLOWPOINT · FIREANT · GTE“Snowden Documents Reveal Covert Surveillance and Pressure Tactics Aimed at WikiLeaks and Its Supporters” - The Intercept ↗ (2014-02-18) · “Snowden docs reveal British spies snooped on YouTube and Facebook” - NBC News ↗ (2014-01-27) · Greenwald, Glenn · Gallagher, Ryan · Esposito, Richard · Cole, Matthew · Schone, Mark -
PTC Glossary [pdf]
This GCWiki PTC Glossary excerpt defines SIGINT-related telecom terms—IMEI, IMSI, INMARSAT—and documents internal collection systems (e.g., INCENSER at Bude) and targeting notes (which identifiers are useful for targeting and which are not). It’s a technical reference for signals analysts describing selectors, collection sources, and operational caveats.
“Vodafone – der lange Arm des britischen Geheimdienstes?” - WDR ↗ (2014-11-20) · “Spy cable revealed: how telecoms firm worked with GCHQ” - Channel 4 ↗ (2014-11-20) · “Der lange Arm des Geheimdienstes?” - NDR ↗ (2014-11-21) · “Snowden-Leaks: How Vodafone-Subsidiary Cable & Wireless Aided GCHQ’s Spying Efforts” - Süddeutsche Zeitung ↗ (2014-11-25) · Restle, Georg · White, Geoff · Strozyk, Jan · Moltke, Henrik · Poitras, Laura · Obermaier, Frederik -
Pull Steering Group Minutes [pdf]
A top secret STRAP1 GCHQ PullThrough Steering Group meeting record from February 2008 documenting the approval process for five surveillance and intelligence prototypes including KARMA POLICE — the mass internet browsing profiling system — alongside ORB FINDER for CNE operational relay box identification, SALTY OTTER for cross-media timing analysis, MOOSE MILK for telephone kiosk surveillance, and LIGHTWOOD for email address extraction used by JTRIG.
Programs: MYOFIBRIL · SALTYOTTER · PRIMETIME · KARMAPOLICE · ORBFINDER · MOOSEMILK · LIGHTWOOD · JTRIG · MERAPEAK · MONTEVISTA · KED -
QUANTUM Shooter SBZ Notes [pdf]
An NSA WikiInfo technical reference page describing the QUANTUM shooter infrastructure — covering how compromised internet hosts are configured with STRAITBIZARRE implants using FELONYCROWBAR and Deployed Node Documents, the CHIMNEYPOOL/FRIEZERAMP communications architecture linking shooters to TURBINE via SURPLUSHANGAR and HANGARSURPLUS diodes, and GCHQ's distinct MHS shooter configuration that suppresses callbacks entirely.
Programs: QUANTUM · QUANTUMSHOOTER · FREEFLOW · CHIMNEYPOOL · FELONYCROWBAR · STRAITBIZARRE · SURPLUSHANGAR · HANGARSURPLUS · PASSAGEHILL · FORESTPLACE · FUSSYKEEL · FINGERGNOME · FROZENEARTH · FRIEZERAMP · ISLANDTRANSPORT · GENIE · MIDDLEMAN · WEBSNIPERGATEWAY · WAITAUTO · ZOMBIEARMY · FIPTRIX · TURBINE -
QUANTUMHAND [pdf]
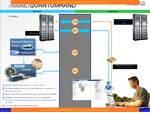
This slide describes QUANTUMHAND, a specialized "Man-on-the-Side" (MOTS) attack used by the NSA's Tailored Access Operations (TAO) to infect targets visiting Facebook. The document outlines an automated process where the NSA's surveillance infrastructure, TURMOIL and TURBINE, detects a target's connection to Facebook and "races" against the legitimate Facebook server to deliver a malicious response first. This "winning the race" allows the NSA to redirect the user to a TAO server that attempts to deploy malware "implants" on the target's computer.
-
QUANTUMINSERT [pdf]
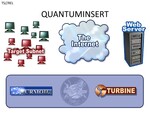
This top-secret NSA presentation provides a step-by-step visual walkthrough of a man-on-the-side (MOTS) attack. This technique allows the NSA to covertly redirect a target's web browser to a malicious server in order to install a malware implant. The diagrams illustrate the interaction between the NSA's global surveillance sensors (TURMOIL) and its automated command-and-control system (TURBINE), demonstrating how the agency exploits the fundamental "race condition" of the internet to compromise a target.
-
QUANTUMTHEORY (2010 SIGINT Development Conference) [pdf]
This 2010 NSA presentation reveals QUANTUMTHEORY, a suite of "man-on-the-side" network attack technologies that enable real-time injection and manipulation of TCP/IP connections through passive surveillance infrastructure. The system encompasses multiple specialized attack techniques including HTML redirection, DNS hijacking, botnet takeover, and database injection, deployed at Five Eyes surveillance sites worldwide.
Programs: QUANTUMTHEORY · TRAFFICTHIEF · TURMOIL · TURBINE · QUANTUM · NINJANIC · ISLANDTRANSPORT · SURPLUSHANGER · DAREDEVIL · STRAIGHTBIZARRE · QUANTUMINSERT · QUANTUMSKY · QUANTUMBOT · QUANTUMBISCUIT · QUANTUMDNS · QUANTUMBOT2 · QUANTUMCOPPER · QUANTUMMUSH · HUFFMUSH · QUANTUMSPIM · QUANTUMSQUEEL · QUANTUMSQUIRREL · INCENSOR · SMOKEYSINK · SARATOGA · QUANTUMDEFENSE · TURBULENCE“How the NSA Plans to Infect ‘Millions’ of Computers with Malware” - The Intercept ↗ (2014-03-12) · “The Digital Arms Race: NSA Preps America for Future Battle” - Der Spiegel ↗ (2015-01-17) · Gallagher, Ryan · Greenwald, Glenn · Appelbaum, Jacob · Gibson, Aaron · Guarnieri, Claudio · Müller-Maguhn, Andy · Poitras, Laura · Rosenbach, Marcel · Ryge, Leif · Schmundt, Hilmar · Sontheimer, Michael -
QUANTUMTHEORY CT Successes [pdf]
This document details a successful NSA counterterrorism cyber operation in which analysts used QUANTUM techniques to deploy the UNITEDRAKE implant—equipped with keylogging and USB collection tools—against Al-Qaeda coordinator Muhsin al-Fadhli in Iran, even after detecting Kaspersky antivirus software on the target system. The operation yielded significant intelligence on Al-Qaeda communications, document forgery activities, and associated operatives.
Programs: QUANTUMTHEORY · ANCIENTBREW · VALIDATOR · QUANTUM · QUANTUMCOWBOY · UNITEDRAKE · GROK · SALVAGERABBITPeople: al-Fadhli, Muhsin -
RAMPART-A Project Overview [pdf]
This document is a 2010 project overview of RAMPART-A, a highly unconventional NSA special access program dedicated to tapping high-capacity international fiber-optic cables at global "congestion points." Through clandestine bilateral partnerships, the NSA installs U.S. equipment on foreign soil to intercept massive volumes of transit data, providing the agency with a unique vantage point that covers virtually every country in the world.
Programs: RAMPART-A · RAMPART-T · SMOKYSINK · AZUREPHOENIX · SPINNERET · TRANQUIL · MOONLIGHTPATH · FIREBIRD · FALCONSTRIKE · DULCIMER · REDHARVEST · FLASHMARK · CONDORSPEAK · TURMOIL · SSO“How Secret Partners Expand NSA’s Surveillance Dragnet” - The Intercept ↗ (2014-06-18) · “NSA ‘third party’ partners tap the Internet backbone in global surveillance program” - Dagbladet Information ↗ (2014-06-19) · Gallagher, Ryan · Geist, Anton · Gjerding, Sebastian · Moltke, Henrik · Poitras, Laura · Jensen, Kristian -
RAMPART-A Sites [pdf]
This document specifies the data throughput and operational constraints of five key RAMPART-A interception sites, including the implementation of the "DNI Throttle" to manage data volume. It also defines the "Support Hub" model for managing signals tasking and explains the role of the REDHARVEST compartment in restricting which analysts can view specific digital network categories.
Programs: RAMPART-A · AZUREPHOENIX · MOONLIGHTPATH · SPINNERET · SMOKYSINK · FIREBIRD · XKEYSCORE · PINWALE · REDHARVEST · CADENCE“How Secret Partners Expand NSA’s Surveillance Dragnet” - The Intercept ↗ (2014-06-18) · “NSA ‘third party’ partners tap the Internet backbone in global surveillance program” - Dagbladet Information ↗ (2014-06-19) · Gallagher, Ryan · Geist, Anton · Gjerding, Sebastian · Moltke, Henrik · Poitras, Laura -
Real Life Stats from GPRS work [pdf]
GCHQ’s TOP SECRET briefing touts real-time interception of diplomats’ smartphone traffic at the 2009 G20—especially BlackBerry—feeding live messages and newly discovered selectors to analysts and UK ministers to shape summit outcomes. It’s a snapshot of summit espionage turned into a policy tool: exploit the smartphone dependence of foreign delegations, deliver actionable SIGINT on demand.
“GCHQ intercepted foreign politicians' communications at G20 summits” - The Guardian ↗ (2013-06-16) · “For the NSA, espionage was a means to strengthen the US position in climate negotiations” - Dagbladet Information ↗ (2014-01-30) · MacAskill, Ewen · Davies, Nick · Hopkins, Nick · Borger, Julian · Ball, James · Gjerding, Sebastian · Geist, Anton · Moltke, Henrik · Poitras, Laura -
Real-Time Regional Gateway (RT-RG) [pdf]
This document from GCHQ details the NSA's Real-Time Regional Gateway (RT-RG), a system designed to provide tactical military users with near-instantaneous SIGINT (signals intelligence) support by integrating and analyzing data from multiple sources. It outlines the system’s applications, benefits, and challenges, particularly in enhancing the speed and efficiency of intelligence delivery to military operations in regions like Afghanistan, and highlights its impact on collaboration with GCHQ.
Programs: RT-RG · RT-10 · GOLDMINER · VOICESAIL · GEOT · SHARKFINN · CELLEX · SORTINGLEAD · GREMIO · IMMERGO · HERRICK · AIRHANDLER · TIPPERS · PASHTOVOICE · VIPERFOCUS · SKS · GEOFUSION · EVENTS“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
Real-Time Regional Gateway Cloud Analytics for Forward Users [pdf]
This document outlines the NSA’s Real-Time Regional Gateway (RT-RG) program, a global cloud-based signals intelligence system designed to provide near real-time data analysis and targeting support for military and intelligence operations. It details the transition to scalable cloud architectures such as GHOSTMACHINE and Cloudbase, enabling massive data retention, exploitation, advanced geolocation, and automated analytics for tracking high-value targets across multiple theaters, including Afghanistan, Iraq, and the Horn of Africa.
Programs: RT-RG · GOLDMINER · GEOT · AGENTLOGIC · SHARKFINN · SKS · PANOPTICON · DRT · CIDNE · JUGGERNAUT · LOPERS · TALIS · MATTERHORN · AIRHANDLER · LYCANTHROPE · VOICESAIL · RETURNSPRING · SORTINGLEAD · GHOSTMACHINE · GMROYALE · GMREGAL · GMGEIST · GMIDEA · GMTOTE · GMPEN · GMPAC · GMCALM · GMMATE · GMAPPLE · GMCAVE · GMPEACH · GMDEN · GMMOUNT · GMALAMO · GMLIGHT · GMBALTIC · GMPLACE · GMPARK · GMHALO · GMCARBON · DRAGONFIRE · DOMEEXPOSE · GIANTSQUID · MAINWAY · FURIOUSCHAINSAW · SHARKFURY · NIAGARAFILES · SHARKQUERY · SHARKDOCS · OCTAVE · UTT · BEDDOWN · CHEEKYMONKEY · LAYERCAKE · CYBERTRANS · GMSEMINOLE · GMGULF · GMZILLA · HLT · JEMA · NEVIS · SEDB · CLOUDBASE · MAPREDUCE · CASPORT · WAVELEGAL“Mission Creep: How the NSA’s Game-Changing Targeting System Built for Iraq and Afghanistan Ended Up on the Mexico Border” - The Intercept ↗ (2019-05-29) · “Norges hemmelige krig i Afghanistan” - NRK ↗ (2019-05-29) · Moltke, Henrik · Skille, Øyvind Bye · Døvik, Olav · Hansen, Ståle Ellingsgard · Fjørtoft, Martin -
Report on an XKeyscore training session at the ECC / Dagger Complex [pdf]
This 2012 report details a highly successful XKEYSCORE (XKS) "Circuit Training" event at the European Cryptologic Center (ECC) in Germany, which dramatically increased analyst usage of the powerful SIGINT tool. The training, which used a "speed dating" format and gamification, helped analysts overcome their intimidation and led to significant intelligence discoveries.
-
Report on Architectural Risk 2012 - Summary [pdf]
This 2012 GCHQ report identifies that a historical under-investment in IT architecture has created significant risk, especially with new challenges like massive data growth, cyber defense, and increased partnering. The document recommends immediate, prioritized investment in big data strategies, integrated analytics frameworks, and security services to address the strain on the system.
Programs: BLACKHOLE -
Research & Technology – Penetrating Hard Targets [pdf]
The NSA’s “Penetrating Hard Targets” program aims at developing a cryptologically useful quantum computer capable of breaking strong encryption systems, including those protecting global financial and government communications. Conducted under the U.S. intelligence “black budget,” the program focuses on quantum physics research, engineering studies, and experimental milestones such as achieving dynamical decoupling and quantum control on semiconductor qubits, which are foundational for scaling to larger systems. A related initiative, “Owning the Net,” explores quantum communication technologies to develop new Quantum Key Distribution (QKD) attacks and assess the security of emerging encryption methods.
-
Rocoto: Implanting the iPhone [pdf]
A top secret abstract from the CIA's 2010 Trusted Computing Base Jamboree conference, describing a Johns Hopkins University Applied Physics Laboratory presentation on efforts to create intelligence community exploitation tools for the iPhone 3G, including analysis of its firmware security architecture and leveraging community jailbreak methods for signals intelligence purposes.
“The CIA Campaign to Steal Apple's Secrets” - The Intercept ↗ (2015-03-10) · Scahill, Jeremy · Begley, Josh