Classification: SI 265 documents
Search documents matching “SI” →Each document's classification level, as component values. If a document contains multiple classifications, the highest is used here.
Graphs
By Banner
Refine (combine with another filter, via search)
Sort: Title
Documents
-
Lobban NSA Visit Précis [pdf]
This document is a formal briefing for a April 2013 visit by GCHQ Director Sir Iain Lobban to the NSA. The visit aimed to reinforce the Five Eyes partnership by discussing sensitive topics including supervised access to FAA Section 702 data ("Triage 2.0"), coordinated cyber and SIGINT strategies for Syria and Iran, and the implementation of the Global Collaboration Environment (GCE).
-
Location Cookies [pdf]
These slides contain excerpts from an April 2013 National Security Agency presentation detailing signal surveillance techniques and successes. They reveal that the NSA and its British counterpart, Government Communications Headquarters (GCHQ), use a Google-specific tracking cookie to pinpoint targets for hacking.
-
Longest Shifts: Working Overtime in Pursuit of SIGINT (part 2: conclusion) SIDtoday [pdf]
To mark Labor Day, SIDtoday shared stories from NSA personnel about their longest shifts. The accounts highlighted the dedication, stress, and sacrifice involved in supporting critical SIGINT operations, from intense 48-hour shifts during military operations to working long hours in extreme conditions like snowstorms or following major events like 9/11.
People: Blum, H. Steven -
LONGHAUL [pdf]
An NSA WikiInfo page for LONGHAUL — the centralised end-to-end attack orchestration and key recovery service that sits at the heart of NSA's capability to break encrypted internet traffic, receiving cryptanalytic data from field collection systems, coordinating attacks against VPN and SSL/TLS encryption through child projects POISONNUT and SCARLETFEVER, and returning recovered keys to deployed CA Servers at collection sites worldwide.
Programs: LONGHAUL · MAILORDER · CASPORT · GECC · VIVIDDREAM · TURMOIL · WEALTHYCLUSTER · TUTELAGE · EINSTEIN · ISLANDTRANSPORT · HADOOP · NINJACOVE · JST · CST · VMM · VDG · ORDC · SCB · ISLANDHIDEAWAY · TURBULENCE · POISONNUT · SCARLETFEVER · HEROICSAND · PLATINUMRING · GALLANTWAVE · JEDIMINDTRICK · CHAOTICSTORMTROOPER · CORALREEF · SCUBADIVER2 · TERRACOTTA · HBASE · SCALA · MAPREDUCE · COALCAR · STOCKCAR · BEACHHEAD · MIDRIFT · WOLVERINESTAKE · NSP · PURGE · SURGE · C2DP · DOORS · HUDSON -
Manhunting Timeline 2008 - Intellipedia [pdf]
This document is an archived Intellipedia entry titled "Manhunting Timeline 2008," a collaborative wiki used by the U.S. Intelligence Community to track high-value targeting operations. It catalogs a global series of assassinations, captures, and military strikes against state officials and militant leaders, ranging from the arrest of the "Merchant of Death" to clandestine naval commando operations.
Programs: LORAINAPeople: Sulayman, Muhammad · al-Masri, Abu Khabab · Mursi, Midhat · Karadžić, Radovan · Ayrow, Aden Hashi · Ayro, Aden Hashi Farah · Nuristani, Mohammad Tamim · Hekmatyar, Gulbuddin · Khan, Kashmir · Bout, Viktor · Bush, George W. · Obama, Barack · Jones, James L. · Nabhan, Saleh Ali Saleh · Musharraf, Pervez · Kayani, Ashfaq Parvez · Kulick, Amir · bin Laden, Osama · Sarkozy, Nicolas -
Manhunting Timeline 2010 [pdf]
The Intellipedia manhunting timeline for 2010, recording the United States urging Australia, the United Kingdom and Germany on 10 August to consider criminal charges against WikiLeaks founder Julian Assange — described as focusing the legal element of national power on Assange and the network supporting WikiLeaks.
-
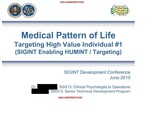
Medical Pattern of Life - Targeting High Value Individual #1 - (SIGINT Enabling HUMINT / Targeting) [pdf]
This presentation dates from June 2010 and outlines a highly specialized intelligence strategy: using a target's medical needs as a "geospatial beacon" to bypass traditional security measures. In this context, High Value Individual #1 (HVI #1) refers to Osama bin Laden (UBL), and the document details a plan to track him via his suspected chronic kidney disease and related medical supplies.
People: bin Laden, Osama -
Menwith continues successful counterterrorism survey along Af-Pak border [pdf]
Menwith Hill Station (MHS) conducted a counterterrorism surveillance operation along the Afghanistan-Pakistan border using the DARKSIDE collection system, successfully intercepting and processing microwave communications to gather actionable intelligence on terrorist activities. The operation, enhanced by Phase II hardware and coordinated with regional target offices, allowed dynamic capture and analysis of multiple signals to support ongoing counterterrorism efforts.
-
Metadata-Driven Drone Strikes SIDtoday [pdf]
These documents describe the NSA and CIA’s use of geolocation technology, particularly via UAV-mounted systems like GILGAMESH and VICTORYDANCE, to track mobile devices for targeted drone strikes, including operations that killed U.S. citizen Anwar Nasser Aulaqi. These programs rely heavily on signals intelligence rather than human confirmation, raising concerns about reliability, civilian casualties, and the accuracy of targeting. See also: SIDtoday/documents/2005/2005-01-18_SIDToday_-_New_Tactical_Collection_System_Joins_the_War_on_Terroris
-
MHS Leverages XKS for QUANTUM Against Yahoo and Hotmail [pdf]
This document describes a technical study conducted at Menwith Hill Station (MHS) in the UK. The study used XKEYSCORE (XKS) to evaluate the feasibility of launching QUANTUMTHEORY "man-on-the-side" attacks against users of Yahoo and Hotmail. Analysts developed a specialized Map/Reduce analytic called DRAGGABLEKITTEN to perform deep packet analysis on bulk internet traffic. The study concluded that 90% of Yahoo sessions and 50% of Hotmail sessions contained the specific technical "keywords" (such as unique cookies or headers) within a single data packet required to trigger a successful automated injection of malware.
-
Microsoft releases new service, affects FAA 702 collection [pdf]
An SSO item on Microsoft's new outlook.com service encrypting web chat from 31 July 2012 and cutting off FAA 702 collection, and on the surveillance solution Microsoft built with the FBI, which went live on 12 December 2012 and needed no change to UTT tasking.
-
Mission Management Success Stories [pdf]
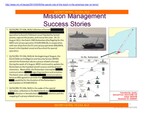
This document details a joint intelligence operation between the NSA and the Dutch Defense Intelligence and Security Service (MIVD) targeting Somali piracy. This document outlines how the NSA provided the Dutch flagship HMS Rotterdam with specialized intercept capabilities during Operation OCEAN SHIELD in 2012. This collaboration directly facilitated a successful special operation on 13 August 2012, which resulted in the rescue of a hijacked Pakistani vessel's crew and the capture of several pirates.
-
MYSTIC [pdf]
These excerpts provide foundational details on the MYSTIC program, including its inception in 2009 and its structural organization. It defines MYSTIC as a program managed by the Special Source Operations (SSO) division, focusing on "embedded collection systems" within foreign wireless and mobile networks. The document confirms a deceptive operational model: the equipment is overtly installed to provide "commercial services" for telecommunications companies, while its secret purpose is to provide SIGINT (Signals Intelligence) to U.S. agencies.
-
NCTC Current Status of Major Terrorism Figures [pdf]
A TOP SECRET joint HUMINT–COMINT status report from June 2008 summarizes the whereabouts and threat posture of senior al‑Qaida leaders, highlighting Usama bin Ladin, Ayman al‑Zawahiri, and a key courier assessed as critical to locating them. The document reflects U.S. intelligence tracking priorities just three years before bin Ladin’s death.
-
Net Defense from Encrypted Communications [pdf]
A NSA Technology Directorate briefing from February 2012 describing BLUESNORT — a capability that repurposes GALLANTWAVE's SSL/TLS decryption pipeline for network defence, re-injecting decrypted traffic into TURMOIL Stage 1 Prime where BLUESNORT detects malware and other malicious activity — representing description of NSA using its own bulk decryption infrastructure for cyber defence as well as intelligence collection.
-
New Contact-Chaining Procedures to Allow Better, Faster Analysis SIDtoday [pdf]
The SIGINT Management Directive 424 briefing (Jan 2011) announces a major procedural shift at the NSA, allowing analysts to conduct contact chaining and large-scale metadata analysis from any selector, regardless of nationality or location. This change removes prior restrictions on U.S. data, enabling more powerful social network mapping for foreign intelligence purposes.
Programs: GATEKEEPER -
New FAA702 Certification in the Works - Cyber Threat [pdf]
A 23 March 2012 SSO article on a draft FAA 702 certification for cyber threats. It would let analysts task selectors tied to malicious cyber activity without attributing them to a foreign government or terrorist group, and would codify tasking of IP addresses and code strings through PRISM and the upstream accesses.
-
New Operations Building at MHS Completed, Fit-Up Begins SIDtoday [pdf]
A 2011 NSA internal report describes the completion of “Project Phoenix” at Menwith Hill Station in the UK — a new operations building featuring a state-of-the-art data center, auditorium, and collaborative office spaces designed to enhance mission resilience, technological capacity, and training infrastructure. The project marks a major modernization effort, expanding Menwith Hill’s operational footprint and preparing it to support new intelligence systems and missions.
-
New RT-RG Overview Video Available on NSANet SIDtoday [pdf]
The NSA's Meade Operations Center released a 10-minute video overview of the Real-Time Regional Gateway (RT-RG), a tool suite designed for forward-deployed analysts. The suite enables faster access to real-time metadata and reporting, improving tactical support for military operations, with new functionalities being developed for use in Afghanistan and beyond.
-
New Skype Stored Comms Capability For PRISM [pdf]
An SSO item on PRISM's new Skype stored-communications capability — buddy lists, credit card details, call data records and account information — with roughly 2,000 Skype selectors sent for FBI adjudication on 29 March 2013 and over 2,800 reports issued from PRISM Skype collection since April 2011.