Reported Documents (810 total)
Documents published alongside news reporting on the Snowden disclosures.
Sort: Title
Documents
-
Digint Narrative [pdf]
This Digint Programme (2010 draft) outlines MI5’s plan to strengthen its ability to collect and exploit digital intelligence, addressing the growing challenge of massive internet-based data and the risk of missing critical insights. It emphasizes collaboration with GCHQ, NTAC, and other agencies to build strategic capabilities, improve exploitation of collected data, and expand coverage for counterterrorism and national security.
Marking: UK SECRETPrograms: IMP -
Discovery SIGINT Targeting Scenarios and Compliance [pdf]
This document is a top-secret NSA guidance manual detailing SIGINT targeting scenarios, compliance procedures, and legal guidance for querying foreign actors, malware, and potentially U.S.-linked systems, including considerations for minimizing incidental collection of U.S. persons’ communications. It outlines specific rules, approvals, and exceptions for using SIGINT tools, foreign intelligence tasks, and cases involving ambiguous or dual-use selectors like WikiLeaks, The Pirate Bay, and foreign actors operating through U.S. infrastructure.
-
DNI, attorney general certify surveillance targets 'reasonably believed' to be outside U.S. [pdf]
In this document, the director of national intelligence and the attorney general certify that there are procedures in place to ensure that surveillance conducted under Section 702 of the FISA Amendments Act will be limited to targeting people "reasonably believed to be located outside the United States." They state that the foreign intelligence to be collected "concerns foreign powers" as defined by statute. The list of foreign powers is in Exhibit F.
-
DNI101 [pdf]
This TOP SECRET training guide, "DNI 101," provides a workflow for Digital Network Intelligence analysts on how to investigate a target's email address, detailing the specific tools, databases, and methodology used, and stressing the critical difference between initial open-source/classified research and the active "targeting" of raw SIGINT repositories like XKEYSCORE, PINWALE, and MARINA.
Programs: NKB · FOXTRAIL · FOREMAN · PINWALE · LIONHEART · XKEYSCORE · DISHFIRE · MARINA · MECWEB · MAINWAY · TRAFFICTHIEF · MAUI · ANCHORY · M3 · INTELLINK · HOMEBASE · PROTON · UTT · CADENCE · SPEEDBUMP · TUNINGFORK · MASTERSHAKE · BLACKPEARL · JACKSPARROW · ROADBED · STORYDUTY · LIONROAR · DOPHONE · UIS -
DoD 2011 Strategy for Operating in Cyberspace – Supply Chain Excerpts [pdf]
The classified 2011 Department of Defense strategy warns that U.S. reliance on foreign manufacturing—especially from countries like China—creates major cybersecurity risks, including the potential insertion of malicious hardware or software into critical systems. It outlines a government-wide plan to mitigate these supply chain vulnerabilities through coordinated policies, risk management strategies, and collaboration with industry.
-
Does NSA Look Different from the Outside? What's in Store for SIGINT Analysis and Production? -- An Interview with Wayne Murphy SIDtoday [pdf]
In this SIDtoday interview with Wayne Murphy, the Assistant Deputy Director for Analysis & Production (S2) at NSA, he reflects on his career and vision for the future of SIGINT analysis and production. Having returned to NSA after a stint at the FBI, Murphy provides valuable insights into the importance of collaboration, both within the intelligence community and between intelligence agencies and operational teams.
Programs: ASPACE -
Driver 1: Worldwide SIGINT/Defense Cryptologic Platform [pdf]
A 2012 NSA management presentation slide revealing the agency's global surveillance architecture across five categories of access — covert cable taps, regional collection sites, computer network exploitation implants, foreign satellite collection, and third-party liaison relationships — including a list of cities hosting clandestine collection operations and confirmation of over 50,000 worldwide malware implants.
Programs: STELLAR · SOUNDER · SNICK · MOONPENNY · LADYLOVE · INDRA · IRONSAND · JACKKNIFE · CARBOY · TIMBERLINE“NSA infected 50,000 computer networks with malicious software” - NRC ↗ (2013-11-23) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Boon, Floor · Derix, Steven · Modderkolk, Huib · Greenwald, Glenn -
DROPMIRE on the Cryptofax at the EU Embassy D.C. [pdf]
This document reveals that the NSA secretly targeted EU diplomatic communications through a program called DROPMIRE, which involved placing surveillance implants on encrypted fax machines at the EU Embassy in Washington, D.C. This operation was part of a broader effort to spy on 38 foreign embassies and missions—including allies such as France, Italy, and Greece—to gain inside knowledge of policy debates and diplomatic positions.
Programs: DROPMIRE -
DSD’s Risky Metadata Sharing: Australian Citizens’ Privacy Jeopardized in 5-Eyes Surveillance [pdf]
The document reveals that in 2008, Australia’s Defence Signals Directorate (DSD) was willing to share bulk, unselected, unminimised metadata about ordinary citizens with its 5-Eyes partners, including sensitive medical, legal, and religious information.
Marking: SECRET -
DTX 600 Load Sharing Carriers R.O.W (via UK) to IRAQ plus RLEs [pdf]
A GCHQ informal report dated 15 October 2008 on IRAQ/UK load sharing DTX600 carriers and their return link ends, with redacted JSS7 hits and technical details of four carriers.
“Turkey Is 'Partner and Target' for the NSA” - Der Spiegel ↗ (2014-08-31) · “How the NSA Helped Turkey Kill Kurdish Rebels” - The Intercept ↗ (2014-08-31) · Poitras, Laura · Rosenbach, Marcel · Sontheimer, Michael · Stark, Holger -
ECI WHIPGENIE Classification Guide [pdf]
A 2004 NSA classification guide for ECI WHIPGENIE, covering the agency's Special Source Operations relationships with US corporate partners for cable collection and domestic wire access, including FISA-warranted collection and FBI-assisted compelled and cooperative partnerships.
Programs: WHIPGENIE · FAIRVIEW · STORMBREW · BLARNEY · POWERPLANT · TUMBRIL · WEALTHYCLUSTER · RAGTIME · PLUS · YELLOWSTONE · SSO -
Elegant Chaos: collect it all, exploit it all [pdf]
This document outlines a classified project, "Elegant CHAOS," focused on advanced signals intelligence (SIGINT) collection, processing, and analysis using cutting-edge technologies like automated surveys and modems. It highlights goals such as real-time data analysis, collaboration with international partners, and integration with cloud-based platforms to manage massive data. See also the document with notes (by GCHQ): "Elegant-Chaos-collect-it-all-exploit-it-all-plus"
Programs: ELEGANTCHAOS · ASPHALT · ASPHALT-A · ASPHALT-A-PLUS · STORMFORCE · DARKQUEST · TORUS · XKEYSCORE · MHS CLOUD · TURMOIL · TARMAC · ASDF · SLR · POPQUIZ · WEALTHYCLUSTER2 · TRAVELLINGWAVE · BILBOBADGER · DRINKYBIRD · GLOBETROTTER · MASTERSHAKE · REST · TRAFFICTHIEF · VENUSAFFECT · FOGHORN · MATCHMAKER · ROADBED · MOONPENNY · AMULETSTELLAR · CLOUD · WEALTHYCLUSTER · MVR · TINT · IPGEOTRAP · MARINA · PLUS -
Elegant Chaos: collect it all, exploit it all (plus notes) [pdf]
GCHQ/NSA presentation describing ELEGANT CHAOS — an automated system at the Menwith Hill Station satellite interception facility that scores and ranks thousands of intercepted satellite signals by intelligence value, automatically deciding which ones deserve collection resources based on criteria like geographic location, target network hits, technology type and Computer Network Operations interest — built to implement the station's directive to "Sniff it All, Know it All, Collect it All, Process it All, Exploit it All, Partner it All" as collection capacity scaled from 100 signals to a planned 3,000 simultaneous intercepts.
Programs: ELEGANTCHAOS · ASPHALT · ASPHALT-A · ASPHALT-A-PLUS · STORMFORCE · DARKQUEST · TORUS · XKEYSCORE · MHS CLOUD · TURMOIL · TARMAC · ASDF · SLR · POPQUIZ · WEALTHYCLUSTER2 · TRAVELLINGWAVE · BILBOBADGER · DRINKYBIRD · GLOBETROTTER · MASTERSHAKE · REST · TRAFFICTHIEF · VENUSAFFECT · FOGHORN · MATCHMAKER · ROADBED · MOONPENNY · WHIZBANG · CLOUDBASE · APLUS · MAILORDER · CROSSBONES · AMULET STELLAR · MVR · TINT · WEALTHYCLUSTER · IPGEOTRAP · MARINA · CLOUD · PLUS -
ELINT Analysts - Overcome by Overload? Help is Here with IM&S SIDtoday [pdf]
A 2011 NSA SIDtoday article announcing the Initial Operational Capability of the ELINT Modernization Information Management and Storage system, designed to give analysts worldwide unified access to five years of ELINT reports and raw data from an expanding range of traditional and non-traditional collection platforms.
-
Email Address vs User Activity [pdf]
This 2009 NSA training presentation explains how to use the XKEYSCORE system to search raw SIGINT, detailing the differences between the "Email Address" query, which finds email addresses in full content, and the more flexible "User Activity" query, which can search for selectors like cookies, usernames, and phone numbers.
“XKEYSCORE: NSA’s Google for the World’s Private Communications” - The Intercept ↗ (2015-07-01) · “No Place to Hide” - Metropolitan Books ↗ (2014-05-13) · Marquis-Boire, Morgan · Greenwald, Glenn · Lee, Micah -
Email from GCHQ to NSA about targeting realms in MONKEY PUZZLE [pdf]
Email from GCHQ's MONKEY PUZZLE development team to NSA clarifying that the system only supports deploying targeting for four specific selector realms: emailAddr, google, msnpassport, and yahoo, while still accepting other realms into the system pool.
Marking: SECRET -
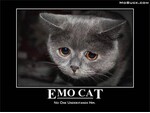
EMO CAT [pdf]
A cat meme from the January 2013 slide deck titled "SSO Collection Optimization." The slide has a glum Russian Blue cat captioned "Emo Cat — No One Understands Him." The meme is a cultural fingerprint how the NSA's analysts weren't men in black but Reddit- and DEF CON–style geeks, also later confirmed by Snowden's and former analyst Alan Tu's descriptions of the agency's informal, meme-saturated internal culture.
-
Entries From Sample SSO Accesses [pdf]
This document reveals that OAKSTAR is a covert NSA program involving corporate partnerships to access global internet traffic, while MONKEYROCKET, a sub-program of OAKSTAR, specifically targets foreign internet traffic from the Middle East, Europe, South America, and Asia for surveillance, with data funneled to the NSA’s European Technical Center for further analysis. It also notes that the data collected is stored in the YANKEE partition for processing.
-
Entry From SSO News [pdf]
This document discusses the initial operational capability of MONKEYROCKET, a non-Western Internet anonymization service developed as part of the OAKSTAR program, aimed at supporting counter-terrorism efforts. As of July 2012, the system was forwarding metadata to backend repositories, with a significant user base of around 16,000, primarily from countries like Iran and China. The service is expected to grow in usage, generating about 2,000 events per day.
-
Entry From SSODictionary v1.0 [pdf]
This document outlines a pending access point for MONKEYROCKET under the OAKSTAR program, focusing on full-take data collection from selected counter-terrorism (CT) targets using a non-Western anonymous browsing service. The collection will include user data, such as billing information and IP addresses, and support NSA's long-term strategy targeting terrorism and other criminal activities, with data gathered under Executive Order 12333. The system used for collection will be vPCS or XKS, and the operation is codenamed "THUNDERISLAND."